Routing Protocols
The Routing Protocols section contains the following topics:
The Routing Protocols section contains the following topics:
You configure Layer 3 MTU on Layer 3 interfaces and SVIs using the mtu command within interface configuration mode.
(config)# interface ethernet 1/1
(config-if-Et1/1)# mtu 1492
MTU is independently configurable on all routable interfaces. The switch supports MTU sizes ranging from 68 to 9214 bytes. The default MTU size is 1500 bytes.
The no mtu and default mtu commands restore the interface MTU to the default value by removing the corresponding mtu command from running-config.
mtu command and it does not appear in the
Interface Configuration Mode.The show interfaces command displays the MTU configured on the L3 interface (ethernet 1/1), as shown in the following example. The IP MTU represents the interface's Layer 3 MTU value.
switch(config-if-Et9/1)# show interfaces ethernet 1/1
...
  IP MTU 1600 bytes , BW 100000000 kbit
  Full-duplex, 100Gb/s over 4 lanes, auto negotiation: off, uni-link: n/a
...Routing transmits network layer data packets over connected independent subnets. Each subnet is assigned an IP address range and each device on the subnet is assigned an IP address from that range.
Connected subnets have IP address ranges that do not overlap. A router is a network device connecting multiple subnets. Routers forward inbound packets to the subnet whose address range includes the packets’ destination address.
IPv4 and IPv6 are Internet layer protocols that define packet-switched inter-networking, including source-to-destination datagram transmission across multiple networks. The switch supports IP version 4 (IPv4) and IP version 6 (IPv6).
IPv6 is described by RFC 2460: Internet Protocol, Version 6 (IPv6) Specification. RFC 2463 describes ICMPv6 for IPv6. ICMPv6 is a core protocol of the Internet Protocol suite.
Internet Protocol version 6 (IPv6) consists ofa communications protocol used for relaying network packets across a set of connected networks using the Internet Protocol suite. EOS assigns a 128 bit IP address that identifies its network location to each network device.
Example
d28e:0000:0000:0000:0234:812f:61ed:4419
d28e:0:0:0:234:812f:61ed:4419
d28e::234:812f:61ed:4419
IPv6 addresses typically denote a 64-bit network prefix and a 64-bit host address.
Unicast addressing defines a one-to-one association between the destination address and a network endpoint. Each destination address uniquely identifies a single receiver endpoint. Anycast addressing defines a one-to-one-of-many association, for example, packets to a single member of a group of potential receivers identified by the same destination address.
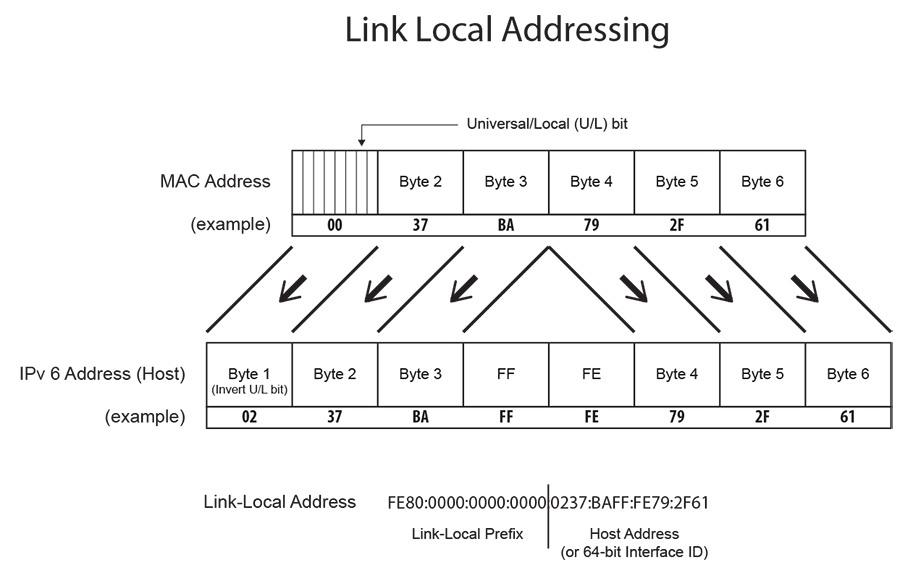
Multicast addressing defines a one-to-many association. Packets simultaneously route from a single sender to multiple endpoints in a single transmission. The network replicates packets as required by network links that contain a recipient endpoint. EOS assigns one multicast address to an interface for each multicast group of an interface.
A solicited-node multicast address consists of an IPv6 multicast address whose scope extends only to the link to the directly connected interface. All IPv6 hosts have at least one address per interface. Neighbor Discovery Protocol uses solicited-node multicast addresses to obtain Layer 2 link-layer addresses of other nodes.
Dynamic Host Configuration Protocol (DHCP) snooping is a Layer 2 feature that is configured on LAN switches. The Arista EOS switch supports Option-37 insertion that allows relay agents to provide remote-id information in DHCP request packets. DHCP servers use this information to determine the originating port of DHCP requests and associate a corresponding IP address to that port. DHCP servers use port information to track host location and IP address usage by authorized physical ports.
DHCP snooping uses the information option (Option-37) to include the switch MAC address (router-id) along with the physical interface name and VLAN number (remote-id) in DHCP packets. After adding the information to the packet, the DHCP relay agent forwards the packet to the DHCP server as specified by the DHCP protocol.
IPv6 Duplicate Address Detection Proxy ensures that all IPv6 addresses assigned on a network segment are unique. After a host verifies the uniqueness of the IPv6 address, it enables DAD on the network.
However, if two network segments cannot communicate with each other, IPv6 DAD cannot perform and duplicate addresses may be assigned to the same interface. To prevent this, a proxy for IPv6 hosts must be assigned on the network and it responds on behalf of the address owner when the address already exists.
The ipv6 unicast-routing command enables the forwarding of IPv6 unicast packets. When routing is enabled, the switch attempts to deliver inbound packets to destination addresses by forwarding them to interfaces or next hop addresses specified by the IPv6 routing table.
Example
switch(config)# ipv6 unicast-routing
switch(config)#The ipv6 route command creates an IPv6 static route to a destination with an IPv6 prefix, and the source uses an IPv6 address or a routable interface port. When multiple routes exist to a destination prefix, the route with the lowest administrative distance takes precedence.
y default, EOS assigns an administrative distance of1 to static routes.
Assigning a higher administrative distance to a static route allows dynamic routing data to override the static route. For example, an OSPF intra-area route, with a default distance of 110, overrides a static route with a distance value of 200.
Example
switch(config)# ipv6 route 10:23:31:00:01:32:93/24 vlan 300
switch(config)#
The default route denotes the packet forwarding rule that takes effect if no other route exists for a specified IPv6 address. EOS sends all packets without destinations in the routing table to the destination specified by the default route.
The IPv6 default route source uses ::/0 as an IP address. EOS refers to the default route destination as the default gateway.
Example
switch(config)# ipv6 route ::/0 fd7a:629f:52a4:fe61::2
switch(config)#IPv6 static routes support link-local next hop addresses on point-to-point interfaces, but in deployments that rely on Zero Touch Provisioning (ZTP) to activate switches with static routes, specifying link-local addresses in configuration templates becomes challenging. Link-Local addresses vary per switch and interface and does not allow the use of a single template across multiple deployments.
EOS supports automatic discovery of link-local next-hop using the IPv6 Router Advertisements to discover the neighbor link-local address and use it as the next-hop for the static routes. Configuring this feature enables simpler and more scalable ZTP deployment and eliminates the need to specify link-local addresses in configuration templates.
Use the following command to enable automatic link-local next-hop discovery on a specified point-to-point interface, Ethernet 1:
switch(config)# ipv6 route 2001:db8:100::/6 next-hop auto p2p Ethernet1
switch(config)#Multiple routes configured to the same destination with the same administrative distance comprise an Equal Cost Multi-Path (ECMP) route. The switch spreads outbound traffic across all ECMP route paths equally and assigns the same tag value to each path. Commands that change the tag value of any ECMP path change the tag value of all paths in the ECMP.
Resilient ECMP is available for IPv6 routes. Equal Cost Multipath Routing (ECMP) and Load Sharing describes resilient ECMP. The ipv6 hardware fib ecmp resilience command implements IPv6 resilient ECMP.
Example
switch(config)# ipv6 hardware fib ecmp resilience 2001:db8:0::/64 capacity 5 redundancy 3
switch(config)#The ipv6 enable command enables IPv6 in the Configuration Mode if it does not have a configured IPv6 address. It also configures the interface with an IPv6 address.
The no ipv6 enable command disables IPv6 on an interface not configured with an IPv6 address. This command does not disable interfaces configured with an IPv6 address.
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 enable
switch(config-vl200)#The ipv6 address command enables IPv6 in the Interface Configuration Mode, assigns a global IPv6 address to the interface, and defines the prefix length. Routable interfaces support this command. Multiple global IPv6 addresses can be assigned to an interface. EOS supports Stateless Address Auto Configuration (SLAAC).
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 address 10:23:31::1:32:93/64
switch(config-if-Vl200)#switch(config)#interface vlan 200
switch(config-if-vl200)#ipv6 address auto-config
switch(config-if-vl200)#The RFC 2461 defines IPv6 Neighbor Discovery. IPv6 Stateless Address Autoconfiguration is described by RFC 2462.
The following sections describe Neighbor Discovery configuration tasks.
The ipv6 nd reachable-time command specifies the time period that EOS includes in the reachable time field of Router Advertisements (RAs) sent from the configuration mode interface. The reachable time defines the period that a remote IPv6 node becomes reachable after a reachability confirmation event.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd reachable-time 25000
switch(config-if-Vl200)# show active
   interface Vlan200
   ipv6 address fd7a:4321::1/64
   ipv6 nd reachable-time 25000
switch(config-if-Vl200)#The ipv6 nd ra interval command configures the interval between IPv6 RA transmissions from the configuration mode interface.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra interval 60
switch(config-if-Vl200)# show active
interface Vlan200
   ipv6 nd ra interval 60
switch(config-if-Vl200)#
The ipv6 nd ra lifetime command specifies the value EOS places in the router lifetime field of IPv6 RAs sent from the IPv6 interface.
If you configure the value as 0, IPv6 peers connected to the specified interface remove the switch from the lists of default routers. Values greater than 0 indicate the time in seconds that peers should keep the router on their default router lists without receiving further RAs from the switch. Unless set to 0, the router lifetime value should be equal to or exceed the interval between unsolicited RAs sent on the interface.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra lifetime 2700
switch(config-if-Vl200)# show active
interface Vlan200
   ipv6 nd ra lifetime 2700
switch(config-if-Vl200)#
The ipv6 nd prefix command configures neighbor discovery router advertisement prefix inclusion for RAs sent from the configuration mode interface.
By default, all prefixes configured as IPv6 addresses are advertised in the interface’s RAs. The ipv6 nd prefix command with the no-advertise option prevents advertising of the specified prefix without affecting the advertising of other prefixes specified as IPv6 addresses. When an interface configuration includes at least one ipv6 nd prefix command that enables prefix advertising, RAs advertise only prefixes specified through ipv6 nd prefix commands.
Commands enabling prefix advertising also specify the advertised valid and preferred lifetime periods. Default periods are 2,592,000 (valid) and 604,800 (preferred) seconds.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd prefix 3012:D678::/64 1296000
switch(config-if-Vl200)#The ipv6 nd ra disabled command suppress IPv6 RA transmissions on the configuration mode interface. By default, only unsolicited RAs that are transmitted periodically are suppressed. The all option configures the switch to suppress all RAs, including those responding to a router solicitation.
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 nd ra disabled all
switch(config-vl200)#The ipv6 nd ra mtu suppress command suppresses the router advertisement MTU option on the IPv6 interface. The MTU option causes an identical MTU value to advertise from all nodes on a link. By default, EOS does not suppress the router advertisement MTU option.
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 nd ra mtu suppress
switch(config-vl200)#
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd managed-config-flag
switch(config-if-Vl200)#switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd other-config-flag
switch(config-if-Vl200)#The IPv6 Router Preference protocol supports an extension to RA messages for communicating default router preferences and more specific routes from routers to hosts. This provides assistance to hosts when selecting a router. RFC 4191 describes the IPv6 Router Preference Protocol.
The ipv6 nd router-preference command specifies the value that the switch enters in the Default Router Preference (DRP) field of RAs sent from the IPv6 interface. The default field entry value is medium.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd router-preference medium
switch(config-if-Vl200)#Unicast Reverse Path Forwarding (uRPF) verifies the accessibility of source IP addresses in forwarded packets from the switch. Unicast Reverse Path Forwarding (uRPF) describes uRPF. Enable uRPF for IPv6 packets entering the IPv6 interface using the ipv6 verify command.
Example
switch(config)# interface vlan 100
switch(config-if-Vl100)# ipv6 verify unicast source reachable-via rx allow-default
switch(config-if-Vl100)# show active
interface Vlan100
ipv6 verify unicast source reachable-via rx allow-default
switch(config-if-Vl100)#Configure IPv6 DAD on an interface, and add an IPv6 address on the interface. Then enable IPv6 on the interface. You can configure this in conjunction with IPv6 ND Proxy.
Example Configuration
switch(config-if-Et1/1# ipv6 nd dad proxy
switch(config-if-Et1/1# ipv6 address 2001:db8:1::/64
switch(config-if-Et1/1# ipv6 enableswitch(config-if-Et1/1# ipv6 nd cache expire 1800switch# show ipv6 nd dad interface
Ethernet1
ipv6 nd proxy prefix connected
ipv6 nd dad proxy
ipv6 address 2001:db8:3::/64The ipv6 dhcp snooping command enables DHCP snooping globally on the switch. DHCP snooping provides a Layer 2 feature that can be configured on LAN switches. Arista switches support Option-37 insertion that allows relay agents to provide remote-ID information in DHCP request packets.
switch(config)# ipv6 dhcp snooping
switch(config)# ipv6 dhcp snooping remote-id option
switch(config)# ipv6 dhcp snooping vlan <vlan|vlan-range>switch(config)# ipv6 dhcp snooping
switch(config)# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
2789-2790
DHCPv6 Snooping is operational on following VLANs:
2789
Insertion of Option-37 is enabledUse the show rib route ipv6 command to view the IPv6 Routing Information Base (RIB) information.
Example
switch# show rib route ipv6 bgp
VRF name: default, VRF ID: 0xfe, Protocol: bgp
Codes: C - Connected, S - Static, P - Route Input
B - BGP, O - Ospf, O3 - Ospf3, I - Isis
> - Best Route, * - Unresolved Nexthop
L - Part of a recursive route resolution loop
B 2001:10:1::/64 [200/42]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100::/64 [200/200]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100:1::/64 [200/0]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100:2::/64 [200/42]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
switch#The show ipv6 route command displays routing table entries in the Forwarding Information Base (FIB), including static routes, routes to directly connected networks, and dynamically learned routes. Multiple equal cost paths to the same prefix display contiguously as a block, with the destination prefix displayed only on the first line.
Example
switch> show ipv6 route fd7a:3418:52a4:fe18::/64
IPv6 Routing Table - 77 entries
Codes: C - connected, S - static, K - kernel, O - OSPF, B - BGP, R - RIP, A -
Aggregate
O fd7a:3418:52a4:fe18::/64 [10/20]
via f180::21c:73ff:fe00:1319, Vlan3601
via f180::21c:73ff:fe00:1319, Vlan3602
via f180::21c:73ff:fe00:1319, Vlan3608
via f180::21c:73ff:fe0f:6a80, Vlan3610
via f180::21c:73ff:fe00:1319, Vlan3611
switch>The show ipv6 route age command displays the IPv6 route age to the specified IPv6 address or prefix.
Example
switch> show ipv6 route 2001::3:0/11 age
IPv6 Routing Table - 74 entries
Codes: C - connected, S - static, K - kernel, O - OSPF, B - BGP, R - RIP, A -
Aggregate
C 2001::3:0/11 age 00:02:34
switch>Example
switch# show ipv6 route host
R - receive F - FIB, A - attached
F ::1 to cpu
A fee7:48a2:0c11:1900:400::1 on Vlan102
R fee7:48a2:0c11:1900:400::2 to cpu
F fee7:48a2:0c11:1a00::b via fe80::21c:73ff:fe0b:a80e on Vlan3902
R fee7:48a2:0c11:1a00::17 to cpu
F fee7:48a2:0c11:1a00::20 via fe80::21c:73ff:fe0b:33e on Vlan3913
F fee7:48a2:0c11:1a00::22 via fe80::21c:73ff:fe01:5fe1 on Vlan3908
via fe80::21c:73ff:fe01:5fe1 on Vlan3902
switch#The show ipv6 route summary command displays the current number of routes of the IPv6 routing table in summary format.
Example
switch> show ipv6 route summary
Route Source Number Of Routes
------------------ ----------------
connected 2
static 0
ospf 5
bgp 7
isis 0
internal 1
attached 0
aggregate 2
Total Routes 17
switch>The ipv6 dhcp relay always-on command enables the switch DHCP IPv6 Relay Agent globally regardless of the DHCP IPv6 Relay Agent status on any interface. EOS enables DHCP IPv6 Relay Agent by default if at least one routable interface has an ipv6 dhcp relay destination statement.
Example
switch(config)# ipv6 dhcp relay always-on
switch(config)#The ipv6 dhcp relay destination command enables the DHCP IPv6 Relay Agent function and specifies the client message destination address on an interface.
Example
switch(config)# interface ethernet 4
switch(config-if-Et4)# ipv6 dhcp relay destination 2001:0db8:0:1::1
switch(config-if-Et4)#
The ipv6 dhcp relay option link-layer address command enables the DHCPv6 relay agent to configure the Client Link Layer Address option to solicit and request messages. In other words, the command enables the Client Link Layer Address option (79) in the Global Configuration Mode. The no ipv6 dhcp relay option link-layer address command disables the link layer address option (79) in the Global Configuration Mode.
Example
switch(config)# ipv6 dhcp relay option link-layer addressThe DHCPv6 Relay Option 37 allows a DHCPv6 relay agent to insert a Remote-ID option (Option 37) into DHCPv6 messages. This option provides the DHCPv6 server with information about the client's location, such as the MAC address of the relay agent, the ingress interface, and the VLAN ID. This is useful for network administrators to track the origin of DHCP requests and to enforce policies based on the client's location.
switch(config)# ipv6 dhcp relay option remote-id format %m:%h:%p switch# show ip dhcp relay
DHCP relay is active
DHCPv6 relay remote ID option (37) encoding format: MAC address:hostname:interface name
switch(config-if-Et4)# exit
switch(config)# clear ipv6 dhcp relay counters
switch(config)#switch(config)# interface ethernet 4
switch(config-if-Et4)# clear ipv6 dhcp relay counters
switch(config)#
The show ip dhcp relay command displays the status of DHCP relay agent parameters on the switch and each interface where at least one feature parameter is listed. The command displays the status for both global and interface configurations.
Example
switch(config)# interface ethernet 1/2
switch(config-if-Et1/2)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCPv6 Relay Link-layer Address Option (79) is disabled
DHCP Smart Relay is disabled
Interface: Ethernet1/2
DHCP Smart Relay is disabled
DHCP servers: 1::1
2001:db8:0:1::1
switch(config-if-Et1/2)#The show ipv6 dhcp relay counters command displays the number of DHCP packets received, forwarded, or dropped on the switch and on all interfaces enabled as DHCP relay agents.
Example
switch> show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Ethernet4 | 207 148 0 | 4 days, 19:54:24 ago
switch>TCP MSS Clamping limits the value of the Maximum Segment Size (MSS) in the TCP header of TCP SYN packets transiting a specified Ethernet or tunnel interface. Setting the MSS ceiling can avoid IP fragmentation in tunnel scenarios by ensuring that the MSS is low enough to account for the extra overhead of GRE and tunnel outer IP headers. Use TCP MSS Clamping when connecting through a GRE tunnel to cloud providers that require asymmetric routing.
When configuring MSS clamping on an interface, if the TCP MSS value in a SYN packet transiting that interface exceeds the configured ceiling limit, the configured limit overwrites the TCP MSS value, and the TCP checksum recomputes and updates.
By default, the software datapath handles TCP MSS Clamping. However, the hardware configuration can support the process to minimize possible packet loss and reduce the number of TCP sessions that the switch can establish per second.
Set the TCP MSS Ceiling limit on an interface using command tcp mss ceiling ipv6. This also enables TCP MSS Clamping on the switch.
switch(config)# interface ethernet 26
switch(config-if-Et5)# no switchport
switch(config-if-Et5)# tcp mss ceiling ipv6 1436 egress
switch(config-if-Et5)#The clear ipv6 dhcp relay counters command resets the DHCP relay counters. If you do not specify a port, the command clears the counters for the switch and for all interfaces. Otherwise, the command clears the counter for the specified interface.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 dhcp relay counters [port]
Parameters
Example
switch(config)# show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Ethernet4 | 207 148 0 | 4 days, 19:54:24 ago
switch(config)# interface ethernet 4
switch(config-if-Et4)# clear ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 380 380 0 | 4 days, 21:19:17 ago
All Resp | 281 281 0 |
| |
Ethernet4 | 0 0 0 |4 days, 21:18:30 ago
These commands clear all DHCP relay counters on the switch.
switch(config-if-Et4)# exit
switch(config)# clear ipv6 dhcp relay counters
switch(config)# show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|-------------
All Req | 0 0 0 | 0:00:03 ago
All Resp | 0 0 0 |
| |
Ethernet4 | 0 0 0 | 0:00:03 ago
switch(config)#The clear ipv6 dhcp snooping counters command resets the DHCP snooping packet counters.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 dhcp snooping counters [counter_type]
switch# clear ipv6 dhcp snooping counters
switch# show ipv6 dhcp snooping counters
| Dhcpv6 Request Pkts | Dhcpv6 Reply Pkts |
Vlan | Rcvd Fwdd Drop | Rcvd Fwdd Drop | Last Cleared
-----|------ ------ -------|------ ----- ------|-------------
2789 | 1 1 0 | 1 1 0 | 0:03:09 agoswitch# clear ipv6 dhcp snooping counters debug
switch# show ipv6 dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 1 1
Forwarded 1 1
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Remote-ID Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 0:04:29 agoThe clear ipv6 neighbors command removes the specified dynamic IPv6 neighbor discovery cache entries. Commands that do not specify an IPv6 address remove all dynamic entries for the listed interface. Commands that do not specify an interface remove all dynamic entries.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 neighbors [port][dynamic_ipv6]
Example
switch# clear ipv6 neighbors vlan 200
switch#The ipv6 address command assigns a global IPv6 address to the IPv6 interface, and defines the prefix length. Routable interfaces support this command. Multiple global IPv6 addresses can be assigned to an interface. The IPv6 address or prefix can be supplied manually, or configured using Stateless Address Auto Configuration.
The no ipv6 address and default ipv6 address commands remove the IPv6 address assignment from the configuration mode interface by deleting the corresponding ipv6 address command from running-config. If the command does not include an address, all address assignments are removed from the interface. IPv6 remains enabled on the interface after the removal of all IPv6 addresses only ifipv6 enable command is configured on the interface.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 address [ ipv6_address | ipv6_prefix | auto-config ]
no ipv6 address { ipv6_address | ipv6_prefix | auto-config }
default ipv6 address { ipv6_address | ipv6_prefix | auto-config }
Parameter
ipv6_address - Specify the IPv6 address to assign to the interface.
ipv6_prefix - Specify the IPv6 prefix assigned to the interface (CIDR notation).
auto-config - Use SLAAC auto-configuration.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 address 10:23:31:00:01:32:93/64
switch(config-if-Vl200)#The iv6p dhcp relay always-on command enables the switch DHCP relay agent on the switch regardless of the DHCP relay agent status on any interface. By default, the DHCP relay agent is enabled only if at least one routable interface is configured with an ipv6 dhcp relay destination statement.
The no ipv6 dhcp relay always-on and default ipv6 dhcp relay always-on commands remove the ipv6 dhcp relay always-on command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay always-on
no ipv6 dhcp relay always-on
default ipv6 dhcp relay always-on
Exampleswitch(config)# ipv6 dhcp relay always-on
switch(config)#The ipv6 dhcp relay destination command enables the DHCPv6 relay agent and sets the destination address on the configuration mode interface.
The no ipv6 dhcp relay destination and default ipv6 dhcp relay destination commands remove the corresponding ipv6 dhcp relay destination command from running-config. When the commands do not list an IPv6 address, all ipv6 dhcp relay destination commands are removed from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 dhcp relay destination [ipv6_addr][source-address ipv6_addr]
no ipv6 dhcp relay destination [ipv6_addr]
default ipv6 dhcp relay destination [ipv6_addr]
Guidelines
If the source-address parameter is specified, then the DHCP client receives an IPv6 address from the subnet of source IP address. The source-address must be one of the configured addresses on the interface.
Example
switch(config)# interface ethernet 4
switch(config-if-Et4)# ipv6 dhcp relay destination 2001:0db8:0:1::1
switch(config-if-Et4)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCPv6 Relay Link-layer Address Option (79) is disabled
DHCP Smart Relay is disabled
Interface: Ethernet4
DHCP Smart Relay is disabled
DHCP servers: 1::1
2001:db8:0:1::1
switch(config-if-Et4)#The ipv6 dhcp relay option link-layer address command enables the DHCPv6 relay agent to configure the client link layer address option to solicit and request messages. In other words, the command enables the link layer address option (79) in the global configuration mode.
The no ipv6 dhcp relay option link-layer address command disables the link layer address option (79) in the global configuration mode.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay option link-layer address
no ipv6 dhcp relay option link-layer address
default ipv6 dhcp relay option link-layer address
Example
switch(config)# ipv6 dhcp relay option link-layer addressThe ipv6 dhcp relay option command configures DHCPv6 Relay Option 37, Remote-ID, to add the MAC address, interface ID or name, and hostname as the remote-id format. The no version of the command removes the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay option remote-id format {%m:%h:%p | %m:%i | %m:%p}
no ipv6 dhcp relay option remote-id format {%m:%h:%p | %m:%i | %m:%p}
Example
switch(config)# ipv6 dhcp relay option remote-id format %m:%h:%p The ipv6 enable command enables IPv6 on the configuration mode interface. Assigning an IPv6 address to an interface also enables IPv6 on the interface.
The no ipv6 enable and default ipv6 enable command remove the corresponding ipv6 enable command from running-config. This action disables IPv6 on interfaces that are not configured with an IPv6 address.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 enable
no ipv6 enable
default ipv6 enable
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 enable
switch(config-vl200)#The ipv6 hardware fib aggregate-address command specifies the routing table repository of specified IPv6 route.
By default, routes that are created statically through the CLI or dynamically through routing protocols are initially stored in software routing tables, then entered in the hardware routing table by the routing agent. This command prevents the entry of the specified route into the hardware routing table. Specified routes that are in the hardware routing table are removed by this command. Specific routes that are encompassed within the specified route prefix are affected by this command.
The no ipv6 hardware fib aggregate-address and default ipv6 hardware fib aggregate-address commands remove the restriction from the hardware routing table for the specified routes by removing the corresponding ipv6 hardware fib aggregate-address command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 hardware fib aggregate-address ipv6_prefix summary-only software-forward
no ipv6 hardware fib aggregate-address ipv6_prefix
default ipv6 hardware fib aggregate-address ipv6_prefix
Parameters
ipv6_prefix IPv6 prefix that is restricted from the hardware routing table (CIDR notation).
Example
switch(config)# ipv6 hardware fib aggregate-address fd77:4890:5313:ffed::/64
summary-only software-forward
switch(config)# show ipv6 hardware fib aggregate-address
Codes: S - Software Forwarded
S fd77:4890:5313:ffed::/64
switch(config)#The ip hardware fib ecmp resilience command configures a fixed number of next hop entries in the hardware ECMP table for the specified IPv6 address prefix. In addition to specifying the maximum number of next hop addresses that the table can contain for the prefix, the command introduces a redundancy factor that allows duplication of each next hop address. The fixed table space for the address is the maximum number of next hops multiplied by the redundancy factor.
The default method of adding or removing next hop entries when required by the active hashing algorithm leads to inefficient management of the ECMP table, which can result in the rerouting of packets to different next hops that breaks TCP packet flows. Implementing fixed table entries for a specified IP address allows data flows that are hashed to a valid next hop number to remain intact. Additionally, traffic is evenly distributed over a new set of next hops.
The no ip hardware fib ecmp resilience and default ip hardware fib ecmp resilience commands restore the default hardware ECMP table management by removing the ip hardware fib ecmp resilience command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 hardware fib ecmp resilience net_prfx capacity nhop_max redundancy duplicates
no ipv6 hardware fib ecmp resilience net_addr
default ipv6 hardware fib ecmp resilience net_addr
Example
switch(config)# ipv6 hardware fib ecmp resilience 2001:db8:0::/64 capacity 5 redundancy 3The ipv6 hardware fib nexthop-index command deterministically selects the next hop used for ECMP routes. By default, routes that are created statically through the CLI or dynamically through routing protocols are initially stored in software routing tables, then entered in the hardware routing table by the routing agent. This command specifies the method of creating an index-offset number that points to the next hop from the list of the route’s ECMP next hops.
The command specifies the number of bits that comprise the prefix offset. The prefix offset is set to the prefix when the command specifies a prefix size larger than the prefix. If the command specifies an prefix size of zero, the prefix-offset is also zero and the index-offset is set to the next hop index.
When the index-offset is greater than the number of next hops in the table, the position of the next hop is the remainder of the division of the index-offset by the number of next hop entries.
The no ipv6 hardware fib nexthop-index and default ipv6 hardware fib nexthop-index commands remove the specified nexthop used for ECMP routes by removing the ipv6 hardware fib nexthop-index command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 hardware fib nexthop nxthop_index [PREFIX]
no ipv6 hardware fib nexthop
default ipv6 hardware fib nexthop
Example
switch(config)# ipv6 hardware fib nexthop-index 5 prefix-bits 10
switch> show ip
IP Routing : Enabled
IP Multicast Routing : Disabled
VRRP: Configured on 0 interfaces
IPv6 Unicast Routing : Enabled
IPv6 ECMP Route support : False
IPv6 ECMP Route nexthop index: 5
IPv6 ECMP Route num prefix bits for nexthop index: 10
switch>The ipv6 hardware fib optimize prefixes command in the Global Configuration Mode reserves IPv6 optimized prefixes on the default and non-default VRFs.
The no version of the command explicitly removes the configuration from the running-config on the switch.
Command Mode
Global Configuration
Command Syntax
ip hardware fib optimize vrf vrf_name prefixes minimum count num_prefixes
no ip hardware fib optimize vrf vrf_name prefixes minimum count num_prefixes
Example
switch(config)# ipv6 hardware fib optimize vrf green prefixes minimum count 35
! Please restart the SandL3Unicast agent to reserve space for optimized FIB prefixesIPv6 DAD Proxy can be configured on an interface, and you must configure an IPv6 address on the interface and then enable IPv6 on the interface. You can configure this in conjunction with IPv6 ND Proxy.
Command Mode
Interface-Ethernet Configuration
Command Syntax
ipv6 nd dad proxy
Example
switch(config-if-Et1/1#ipv6 nd dad proxy
switch(config-if-Et1/1#ipv6 address 2001:db8:1::/64
switch(config-if-Et1/1#ipv6 enable
The ipv6 nd managed-config-flag command causes the managed address configuration flag to be set in IPv6 RA packets transmitted from the configuration mode interface.
The no ipv6 nd managed-config-flag and default ipv6 nd managed-config-flag commands restore the default setting where the managed address configuration flag is not set in IPv6 RA packets transmitted by the interface by removing the corresponding ipv6 nd managed-config-flag command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd managed-config-flag
no ipv6 nd managed-config-flag
default ipv6 nd managed-config-flag
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd managed-config-flag
switch(config-if-Vl200)#The ipv6 nd ns-interval command configures the interval between IPv6 Neighbor Solicitation (NS) transmissions from the configuration mode interface.
The no ipv6 nd ns-interval and default ipv6 nd ns-interval commands return the IPv6 NS transmission interval for the configuration mode interface to the default value of 1000 milliseconds by removing the corresponding ipv6 nd ns-interval command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ns-interval period
no ipv6 nd ns-interval
default ipv6 nd ns-interval
Parameter
period interval in milliseconds between successive IPv6 neighbor solicitation transmissions. Values range from 1000 to 4294967295. The default period is 1000 milliseconds.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ns-interval 30000
switch(config-if-Vl200)#The ipv6 nd other-config-flag command configures the configuration mode interface to send IPv6 RAs with the other stateful configuration flag set.
The no ipv6 nd other-config-flag and default ipv6 nd other-config-flag commands restore the default setting by removing the corresponding ipv6 nd other-config-flag command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd other-config-flag
no ipv6 nd other-config-flag
default ipv6 nd other-config-flag
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd other-config-flag
switch(config-if-Vl200)#The ipv6 nd prefix command configures neighbor discovery Router Advertisements (RAs) prefix inclusion for RAs sent from the configuration mode interface.
By default, all prefixes configured as IPv6 addresses are advertised in the interface’s RAs. The ipv6 nd prefix command with the no-advertise option prevents advertising of the specified prefix without affecting the advertising of other prefixes specified as IPv6 addresses. When an interface configuration includes at least one ipv6 nd prefix command that enables prefix advertising, RAs advertise only prefixes specified through ipv6 nd prefix commands.
Commands enabling prefix advertising also specify the advertised valid and preferred lifetime periods. Default periods are 2,592,000 (valid) and 604,800 (preferred) seconds.
The no ipv6 nd prefix and default ipv6 nd prefix commands remove the corresponding ipv6 nd prefix command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd prefix ipv6_prefix LIFETIME [FLAGS]
ipv6 nd prefix ipv6_prefix no-advertise
no ipv6 nd prefix ipv6_prefix
default ipv6 nd prefix ipv6_prefix
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd prefix 3012:D678::/64 1296000The ipv6 nd ra disabled command suppress IPv6 Router Advertisement (RA) transmissions on the configuration mode interface. By default, only unsolicited RAs that are transmitted periodically are suppressed. The all option configures the switch to suppress all RAs, including those responding to a router solicitation.
The no ipv6 nd ra disabled and default ipv6 nd ra disabled commands restore the transmission of RAs on the configuration mode interface by deleting the corresponding ipv6 nd ra disabled command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra disabled [SCOPE]
no ipv6 nd ra disabled
default ipv6 nd ra disabled
Parameters
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 nd ra disabled all
switch(config-vl200)#The ipv6 nd ra dns-server command configures the IPv6 address of a preferred Recursive DNS Server (RDNSS) for the command mode interface to include in its neighbor-discovery Router Advertisements (RAs). Including RDNSS information in RAs provides DNS server configuration for connected IPv6 hosts without requiring DHCPv6.
Multiple servers can be configured on the interface by using the command repeatedly. A lifetime value for the RDNSS can optionally be specified with this command, and overrides any default value configured for the interface using the ipv6 nd ra dns-servers lifetime command.
The no ipv6 nd ra dns-server and default ipv6 nd ra dns-server commands remove the corresponding ipv6 nd ra dns-server command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuratio
Command Syntax
ipv6 nd ra dns-server ipv6_addr SERVER_LIFE
no ipv6 nd ra dns-server ipv6_addr
default ipv6 nd ra dns-server ipv6_addr
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra dns-server 2001:0db8:0:1::1 lifetime 300
switch(config-if-Vl200)#The ipv6 nd ra dns-servers lifetime command sets the default value that the configuration mode interface uses for the lifetime of any Recursive DNS Server (RDNSS) configured on the interface. A lifetime value set for an individual RDNSS overrides this value. The lifetime value is the maximum amount of time after a route advertisement packet is sent that the RDNSS referenced in the packet may be used for name resolution.
The no ipv6 nd ra dns-servers lifetime and default ipv6 nd ra dns-servers lifetime commands remove the default lifetime value from the interface by removing the corresponding ipv6 nd ra dns-servers lifetime command from running-config. When there is no default RDNSS lifetime value configured on the interface, an RDNSS without a custom lifetime value will default to 1.5 times the RA interval configured on the interface. A lifetime of zero seconds means that the RDNSS must not be used for name resolution.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra dns-servers lifetime period
no ipv6 nd ra dns-servers lifetime
default ipv6 nd ra dns-servers lifetime
Parameters
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra dns-servers lifetime 350
switch(config-if-Vl200)#The ipv6 nd ra dns-suffix command creates a DNS Search List (DNSSL) for the command mode interface to include in its neighbor-discovery Router Advertisements as defined in RFC 6106 . The DNSSL contains the domain names of DNS suffixes for IPv6 hosts to append to short, unqualified domain names for DNS queries.
Multiple DNS domain names can be added to the DNSSL by using the command repeatedly. A lifetime value for the DNSSL can optionally be specified with this command, and overrides any default value configured for the interface using the ipv6 nd ra dns-suffixes lifetime command.
The no ipv6 nd ra dns-suffix and default ipv6 nd ra dns-suffix commands remove the corresponding ipv6 nd ra dns-suffix command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra dns-suffix domain SUFFIX_LIFE
no ipv6 nd ra dns-suffix ipv6_addr
default ipv6 nd ra dns-suffix ipv6_addr
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra dns-suffix test.com lifetime 300
switch(config-if-Vl200)#The ipv6 nd ra dns-suffixes lifetime command sets the default value that the configuration mode interface uses for the lifetime of any DNS Search List (DNSSL) configured on the interface. A lifetime value set for an individual DNSSL overrides this value. The lifetime value is the maximum amount of time after a route advertisement packet is sent that the DNSSL included in the packet may be used for name resolution.
The no ipv6 nd ra dns-suffixes lifetime and default ipv6 nd ra dns-suffixes lifetime commands remove the default lifetime value from the interface by removing the corresponding ipv6 nd ra dns-suffixes lifetime command from running-config. When there is no default DNSSL lifetime value configured on the interface, a DNSSL without a custom lifetime value will default to 1.5 times the RA interval configured on the interface. A lifetime of zero seconds means that the DNSSL must not be used for name resolution.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra dns-suffixes lifetime period
no ipv6 nd ra dns-suffixes lifetime
default ipv6 nd ra dns-suffixes lifetime
Parameters
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra dns-suffixes lifetime 350
switch(config-if-Vl200)#The ipv6 nd ra hop-limit command sets a suggested hop-limit value to be included in Router Advertisement (RA) packets. The hop-limit value is to be used by attached hosts in outgoing packets.
The no ipv6 nd ra hop-limit and default ipv6 nd ra hop-limit commands remove the corresponding ipv6 nd ra hop-limit command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra hop-limit quantity
no ipv6 nd ra hop-limit lifetime
default ipv6 nd ra hop-limit lifetime
Parameters
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra hop-limit
switch(config-if-Vl200)#The ipv6 nd ra interval command configures the interval between IPv6 Router Advertisement transmissions from the configuration mode interface.
The no ipv6 nd ra interval and default ipv6 nd ra interval commands return the IPv6 RA transmission interval for the configuration mode interface to the default value of 200 seconds by removing the corresponding ipv6 nd ra interval command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra interval [SCALE] ra_period [minimum_period]
no ipv6 nd ra interval
default ipv6 nd ra interval
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra interval 60
switch(config-if-Vl200)# show active
interface Vlan200
ipv6 nd ra interval 60
switch(config-if-Vl200)#The ipv6 nd ra lifetime command specifies the value that the switch places in the router lifetime field of IPv6 Router Advertisements sent from the configuration mode interface.
If the value is set to 0, IPv6 peers connected to the specified interface will remove the switch from their lists of default routers. Values greater than 0 indicate the time in seconds that peers should keep the router on their default router lists without receiving further RAs from the switch. Unless the value is 0, the router lifetime value should be equal to or greater than the interval between unsolicited RAs sent on the interface.
The no ipv6 nd ra lifetime and default ipv6 nd ra lifetime commands return the IPv6 RA lifetime data entry filed for the configuration mode interface to the default value of 1800 seconds by removing the corresponding ipv6 nd ra lifetime command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra lifetime ra_lifetime
no ipv6 nd ra lifetime
default ipv6 nd ra lifetime
Parameters
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd ra lifetime 2700
switch(config-if-Vl200)# show active
interface Vlan20
ipv6 nd ra lifetime 2700
switch(config-if-Vl200)#The ipv6 nd ra mtu suppress command suppresses the Router Advertisement (RA) MTU option on the configuration mode interface. The MTU option causes an identical MTU value to be advertised by all nodes on a link. By default, the RA MTU option is not suppressed.
The no ipv6 nd ra mtu suppress and default ipv6 nd ra mtu suppress commands restores the MTU option setting to enabled by for the configuration mode interface by removing the corresponding ipv6 nd ra mtu suppress command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd ra mtu suppress
no ipv6 nd ra mtu suppress
default ipv6 nd ra mtu suppress
Example
switch(config)# interface vlan 200
switch(config-vl200)# ipv6 nd ra mtu suppress
switch(config-vl200)#The ipv6 nd ra rx accept default-route command configures the interface to accept the default gateway information from the Router Advertisement (RA) in the interface configuration. EOS disables this parameter by default. The no and default versions of the command disables the feature.
Command Mode
Interface Configuration Mode
Command Syntax
ipv6 nd ra rx accept default
Example
switch(config)# interface Ethernet3/1
switch(config-if-Et3/1) ipv6 nd ra rx accept default-route
The ipv6 nd reachable-time command specifies the time period that the switch includes in the reachable time field of RAs sent from the configuration mode interface. The reachable time defines the period that a remote IPv6 node is considered reachable after a reachability confirmation event.
RAs that advertise zero seconds indicate that the router does not specify a reachable time. The default advertisement value is 0 seconds. The switch reachability default period is 30 seconds.
The no ipv6 nd reachable-time and default ipv6 nd reachable-time commands restore the entry of the default value (0) in RAs sent from the configuration mode interface by deleting the corresponding ipv6 nd reachable-time command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd reachable-time period
no ipv6 nd reachable-time
default ipv6 nd reachable-time
Parameter
period Reachable time value (milliseconds). Value ranges from 0 to 4294967295. Default is 0.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd reachable-time 25000
interface Vlan200
ipv6 address fd7a:4321::1/64
ipv6 nd reachable-time 25000
switch(config-if-Vl200)#The ipv6 nd router-preference command specifies the value that the switch enters in the Default Router Preference (DRP) field of Router Advertisements (RAs) that it sends from the configuration mode interface. The default field entry value is medium.
The no ipv6 nd router-preference and default ipv6 nd router-preference commands restore the switch to enter the default DRP field value of medium in RAs sent from the configuration mode interface by deleting the corresponding ipv6 nd router-preference command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 nd router-preference [RANK [high | low | medium]]
no ipv6 nd router-preference
default ipv6 nd router-preference
Parameters
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ipv6 nd router-preference medium
switch(config-if-Vl200)#The ipv6 neighbor cache persistent command restores the IPv6 neighbor cache after reboot.
The no ipv6 neighbor cache persistent and default ipv6 neighbor cache persistent commands remove the ARP cache persistant configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 neighbor cache persistent
no ipv6 neighbor cache persistent
default ipv6 neighbor cache persistent
Example
switch(config)# ipv6 neighbor cache persistent
switch(config)#The ipv6 neighbor command creates an IPv6 neighbor discovery cache static entry. The command converts pre-existing dynamic cache entries for the specified address to static entries.
The no ipv6 neighbor and default ipv6 neighborcommands remove the specified static entry from the IPV6 neighbor discovery cache and delete the corresponding ipv6 neighbor command from running-config. These commands do not affect any dynamic entries in the cache.
Command Mode
Global Configuration
Command Syntax
ipv6 neighbor ipv6_addr PORT mac_addr
no ipv6 neighbor ipv6_address PORT
default ipv6 neighbor ipv6_addr PORT
Example
switch(config)# ipv6 neighbor 3100:4219::3EF2 vlan 200 0100.4EA1.B100
switch(config)#The ipv6 route command creates an IPv6 static route. The destination is a IPv6 prefix; the source is an IPv6 address or a routable interface port. When multiple routes exist to a destination prefix, the route with the lowest administrative distance takes precedence.
By default, the administrative distance assigned to static routes is 1. Assigning a higher administrative distance to a static route configures it to be overridden by dynamic routing data. For example, a static route with a distance value of 200 is overridden by OSPF intra-area routes, which have a default distance of 110.
Multiple routes that are configured to the same destination with the same administrative distance comprise an Equal Cost Multi-Path (ECMP) route. The switch attempts to spread outbound traffic across all ECMP route paths equally. All ECMP paths are assigned the same tag value; commands that change the tag value of any ECMP path change the tag value of all paths in the ECMP.
The no ipv6 route and default ipv6 route commands delete static routes by removing the corresponding ipv6 route statements from running-config. Commands not including a source delete all statements to the destination. Only statements with parameters that match specified command arguments are deleted. Parameters that are not in the command line are not evaluated.
Command Mode
Global Configuration
Command Syntax
ipv6 route dest_prefix next-hop [distance][tag_opt][rt_name]
no ipv6 route dest_prefix [nexthop_addr][distance]
default ipv6 route dest_prefix [nexthop_addr][distance]
Example
switch(config)# ipv6 route 10:23:31:00:01:32:93/24 vlan 300The ipv6 unicast-routing command enables the forwarding of IPv6 unicast packets. When routing is enabled, the switch attempts to deliver inbound packets to destination addresses by forwarding them to interfaces or next hop addresses specified by the IPv6 routing table.
The no ipv6 unicast-routing and default ip ipv6 unicast-routing commands disable IPv6 unicast routing by removing the ipv6 unicast-routing command from running-config. Dynamic routes added by routing protocols are removed from the routing table. Static routes are preserved by default; the delete-static-routes option removes static entries from the routing table.
IPv6 unicast routing is disabled by default.
Command Mode
Global Configuration
Command Syntax
ipv6 unicast-routing
no ipv6 unicast-routing [DELETE_ROUTES]
default ipv6 unicast-routing [DELETE_ROUTES]
Parameters
Example
switch(config)# ipv6 unicast-routing
switch(config)#The ipv6 verify command configures Unicast Reverse Path Forwarding (uRPF) for inbound IPv6 packets on the configuration mode interface. uRPF verifies the accessibility of source IP addresses in packets that the switch forwards.
The no ipv6 verify and default ipv6 verify commands disable uRPF on the configuration mode interface by deleting the corresponding ipv6 verify command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 verify unicast source reachable-via RPF_MODE
no ipv6 verify unicast
default ipv6 verify unicast
Parameters
Guidelines
The first IPv6 uRPF implementation briefly disables IPv6 unicast routing. Subsequent ip verify commands on any interface do not disable IPv6 routing.
Example
switch(config)# interface vlan 100
switch(config-if-Vl100)# ipv6 verify unicast source reachable-via rx allow-default
switch(config-if-Vl100)# show active
 interface Vlan100
   ipv6 verify unicast source reachable-via rx allow-default
switch(config-if-Vl100)#The ipv6 dhcp snooping command enables DHCP snooping globally on the switch.
The no ipv6 dhcp snooping and default ipv6 dhcp snooping commands disable global DHCP snooping by removing the ipv6 dhcp snooping command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
no ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
default ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
Examples
switch(config)# ipv6 dhcp snooping
switch(config)# ipv6 dhcp snooping remote-id option
switch(config)# ipv6 dhcp snooping vlan <vlan|vlan-range>switch(config)# ipv6 dhcp snooping
switch(config)# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
2789-2790
DHCPv6 Snooping is operational on following VLANs:
2789
Insertion of Option-37 is enabledThe pim ipv6 sparse-mode command enables PIM Sparse Mode (PIM-SM) and IGMP (router mode) on the configuration mode interface.
The no pim ipv6 sparse-mode and default pim ipv6 sparse-mode commands restore the default PIM and IGMP (router mode) settings of disabled on the configuration mode interface by removing the pim ipv6 sparse-mode command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel
Configuration Interface-VLAN Configuration
Command Syntax
pim ipv6 sparse-mode
no pim ipv6
no pim ipv6 sparse-mode
default pim ipv6
default pim ipv6 sparse-mode
Example
switch(config)# interface vlan 4
switch(config-if-Vl4)# pim ipv6 sparse-mode
switch(config-if-Vl4)#The show ipv6 dhcp relay counters command displays the number of DHCP packets received, forwarded, or dropped on the switch and on all interfaces enabled as DHCP relay agents.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp relay counters
Example
switch> show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Ethernet4 | 207 148 0 | 4 days, 19:54:24 ago
switch> The show ipv6 dhcp snooping command displays information about the DHCP snooping configuration.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping
Example
switch# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
2789-2790
DHCPv6 Snooping is operational on following VLANs:
2789
Insertion of Option-37 is enabledThe show ipv6 dhcp snooping counters command displays counters that track the quantity of DHCP request and reply packets that the switch receives. Data is either presented for each VLAN or aggregated for all VLANs with counters for packets dropped.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping counters [COUNTER_TYPE]
switch# show ipv6 dhcp snooping counters
| Dhcpv6 Request Pkts | Dhcpv6 Reply Pkts |
Vlan | Rcvd Fwdd Drop | Rcvd Fwdd Drop | Last Cleared
-----|------ ------ -------|------ ----- ------|-------------
2789 | 1 1 0 | 1 1 0 | 0:03:09 agoswitch# show ipv6 dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 1 1
Forwarded 1 1
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Remote-ID Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 0:04:29 agoThe show ipv6 dhcp snooping hardware command displays internal hardware DHCP snooping status on the switch.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping hardware
Example
switch# show ipv6 dhcp snooping hardware
DHCPv6 Snooping is enabled
DHCPv6 Snooping is enabled on following VLANs:
2789
Vlans enabled per Slice
Slice: Linecard0-0
2789
Slice: Linecard0-1
2789
Slice: Linecard0-2
2789
Slice: Linecard0-3
2789The show ipv6 hardware fib aggregate-address command displays the IPv6 prefixes that are restricted from entry into the hardware routing table. The ipv6 hardware fib aggregate-address command configures IPv6 prefix restictions.
Command Mode
EXEC
Command Syntax
show ipv6 address fib aggregate-address [ADDRESS][RESTRICTION]
Example
switch> show ipv6 hardware fib aggregate-address
Codes: S - Software Forwarded
S fd77:4890:5313:aaed::/64
S fd77:4890:5313:ffed::/64
switch>The ipv6 interface command displays the status of specified routed interfaces that are configured for IPv6.
Command Mode
EXEC
Command Syntax
show ipv6 interface [INTERFACE_NAME][INFO_LEVEL]
Example
switch> show ipv6 interface vlan 903
Vlan903 is up, line protocol is up (connected)
IPv6 is enabled, link-local is fe80::21c:73ff:fe01:21e/64
Global unicast address(es):
fd7a:629f:52a4:fe10::3, subnet is fd7a:629f:52a4:fe10::/64
Joined group address(es):
ff02::1
ff02::1:ff01:21e
ff02::1:ff00:3
ff01::2
switch>Displays information about the IPv6 Duplicate Address Detection (DAD) feature configured on an interface.
Command Mode
Interface-Ethernet Configuration
Command Syntax
show ipv6 nd dad proxy
Example
switch# show ipv6 nd dad interface ethernet1/1
Ethernet1/1
ipv6 nd proxy prefix connected
ipv6 nd dad proxy
ipv6 address 2001:db8:3::/64The ipv6 nd ra internal state command displays the state of the IPv6 Router Advertisement (RA) daemon for the specified routable interface.
Command Mode
EXEC
Command Syntax
show ipv6 nd ra internal state [INTERFACE_NAME]
Parameters
Example
switch> show ipv6 nd ra internal state vlan 1243
INTERFACE: Vlan3908
ifindex : 0x00000021
mtu : 9212
numIpv6Addr : 2
numPrefixToAdvertise : 0
numPrefixToSuppress : 0
RaSuppress : 0
RsRspSuppress : 0
raIntervalMaxMsec : 200000
raIntervalMinMsec : 0
managedConfigFlag : 0
otherConfigFlag : 0
raMtuSuppress : 0
raLifetime : 1800
reacheableTime : 0
routerPreference : 0
lastRaTime : 2012-05-01 09:22:57.020634
lastRsRspSentTime :
nextTimeout : 171.474535 (sec)
raNotSentIntfNotReady : 0
numRaSent : 219
numRsRcvd : 0
numRsSuppressed : 0
numRsRspSent : 0
numRsDroppedInvalidHopLimit : 0
numPktDroppedUnexpectedType : 0
initialized : 1The show ipv6 neighbors command displays the IPv6 neighbor discovery cache. The command provides filters to restrict the list to a specified IPv6 address or routable interface.
Command Mode
EXEC
Command Syntax
show ipv6 neighbors [PORT][SOURCE][INFO_LEVEL]
Example
switch> show ipv6 neighbors fe80::21c:73ff:fe01:5fe1
IPv6 Address Age Hardware Addr State Interface
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Et12
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Po999
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl102
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl103
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl205
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl207
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3901
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3902
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3903
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3904
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3905
fe80::21c:73ff:fe01:5fe1 0 001c.d147.8214 REACH Vl3996The show ipv6 route command displays IPv6 routing table entries that are in the Forwarding Information Base (FIB), including static routes, routes to directly connected networks, and dynamically learned routes. Multiple equal cost paths to the same prefix are displayed contiguously as a block, with the destination prefix displayed only on the first line.
The show running-config command displays all configured routes.
Command Mode
EXEC
Command Syntax
show ipv6 route [ADDRESS][ROUTE_TYPE][INFO_LEVEL]
Parameters
Examples
switch> show ipv6 route fd7a:3418:52a4:fe18::/64
IPv6 Routing Table - 77 entries
Codes: C - connected, S - static, K - kernel, O - OSPF, B - BGP, R - RIP, A -
Aggregate
O fd7a:3418:52a4:fe18::/64 [10/20]
via fe80::21c:73ff:fe00:1319, Vlan3601
via fe80::21c:73ff:fe00:1319, Vlan3602
via fe80::21c:73ff:fe00:1319, Vlan3608
via fe80::21c:73ff:fe0f:6a80, Vlan3610
via fe80::21c:73ff:fe00:1319, Vlan3611This example displays an IPv6 route with Forwarding Equivalency Class (FEC) with an IPv6 next hop and an IPv4 next hop route.
# show ipv6 route 2001:1::/64
VRF: default
Routing entry for 2001:1::/64
Source Codes:
C - connected, S - static, K - kernel, O3 - OSPFv3,
B - Other BGP Routes, A B - BGP Aggregate, R - RIP,
I L1 - IS-IS level 1, I L2 - IS-IS level 2, DH - DHCP,
NG - Nexthop Group Static Route, M - Martian,
DP - Dynamic Policy Route, L - VRF Leaked,
G - gRIBI, RC - Route Cache Route,
CL - CBF Leaked Route
B I 2001:1::/64 [200/0]
via 2001:2:0:40::2, Ethernet1
via 10.0.0.2, Ethernet3, backupThe show ipv6 route age command displays the IPv6 route age to the specified IPv6 address or prefix.
Command Mode
EXEC
Command Syntax
show ipv6 route ADDRESS age
Parameters
Example
switch> show ipv6 route 2001::3:0/11 age
IPv6 Routing Table - 74 entries
Codes: C - connected, S - static, K - kernel, O - OSPF, B - BGP, R - RIP, A -
Aggregate
C 2001::3:0/11 age 00:02:34Command Mode
EXEC
Command Syntax
show ipv6 route host
Example
switch> show ipv6 route host
R - receive F - FIB, A - attached
F ::1 to cpu
A fee7:48a2:0c11:1900:400::1 on Vlan102
R fee7:48a2:0c11:1900:400::2 to cpu
F fee7:48a2:0c11:1a00::b via fe80::21c:73ff:fe0b:a80e on Vlan3902
R fee7:48a2:0c11:1a00::17 to cpu
F fee7:48a2:0c11:1a00::20 via fe80::21c:73ff:fe0b:33e on Vlan3913
F fee7:48a2:0c11:1a00::22 via fe80::21c:73ff:fe01:5fe1 on Vlan3908
via fe80::21c:73ff:fe01:5fe1 on Vlan3902The show ipv6 route interface command displays routing table entries on a specified routed port.
Command Mode
EXEC
Command Syntax
show ipv6 route [ADDRESS] interface PORT_NAME [INFO_LEVEL]
Parameters
Example
switch> show ipv6 route interface ethernet 8
IPv6 Routing Table - 77 entries
Codes: C - connected, S - static, K - kernel, O - OSPF, B - BGP, R - RIP, A -
Aggregate
O fd7a:629f:63af:1232::/64 [150/11]
via fe80::823c:73ff:fe00:3640, Ethernet8
O fd7a:629f:63af:4118::/64 [150/11]
via fe80::823c:73ff:fe00:3640, Ethernet8
O fd7a:629f:63af:4119::/64 [150/11]
via fe80::823c:73ff:fe00:3640, Ethernet8
O fd7a:629f:63af:411a::/64 [150/11]
via fe80::823c:73ff:fe00:3640, Ethernet8
O fd7a:629f:63af:fe78::/64 [150/11]
via fe80::823c:73ff:fe00:3640, Ethernet8
C fd7a:629f:63af:fe88::/64 [0/1]
via ::, Ethernet12
O fd7a:629f:63af:fe8c::/64 [10/20]
via fe80::21c:73ff:fe00:3640, Ethernet8
C fe80:0:40::/64 [0/1]
via ::, Ethernet8The show ipv6 route match tag command displays the route tag assigned to the specified IPv6 address or prefix. Route tags are added to static routes for use by route maps.
Command Mode
EXEC
Command Syntax
show ipv6 route ADDRESS match tag
Parameters
Example
switch> show ipv6 route 2001:0DB8::/64 match tag
IPv6 Routing Table - 74 entries
Codes: C - connected, S - static, K - kernel, O3 - OSPFv3, B - BGP, R - RIP, A B
- BGP Aggregate, I L1 - IS-IS level 1, I L2 - IS-IS level 2, DH - DHCP, NG -
Nexthop Group Static Route, M - Martian, DP - Dynamic Policy Route, L - VRF Leaked
C 2001:0DB8::/64 tag 0The show ipv6 route summary command displays the information about the IPv6 routing table.
Command Mode
EXEC
Command Syntax
show ipv6 route summary
Example
switch> show ipv6 route summary
Route Source Number Of Routes
------------------ ----------------
connected 2
static 0
ospf 5
bgp 7
isis 0
internal 1
attached 0
aggregate 2
Total Routes 17The show platform fap mroute ipv6 command enables PIM Sparse Mode (PIM-SM) and IGMP (router mode) on the configuration mode interface.
Command Mode
EXEC
Command Syntax
show platform fap mroute ipv6
Example
switch# show platform fap mroute ipv6
Jericho0 Multicast Routes:
--------------------------
Location GroupId Group Source IIF McId OIF
FLP/TT FLP/TT TT FLP FLP FLP FLP
----------------------------------------------------------------------------------------------------
4096/2048 1/1 ff33::1:0:0:23/128 101:1::2/128 Vlan1357 21504 Vlan1044(Et7/1) Vlan1123(Et9/1)
Vlan1200(Et8/1) Vlan1223(Et2/1)
Vlan1226(Et5/1) Vlan1232(Et3/1)
Vlan1307(Et6/1) Vlan1337(Et4/1)The show rib route ipv6 command displays a list of IPv6 Routing Information Base (RIB) routes.
Command Mode
EXEC
Command Syntax
show rib route ipv6 [vrf vrf_name] [PREFIX][ROUTE TYPE]
switch# show rib route ipv6 bgp
VRF name: default, VRF ID: 0xfe, Protocol: bgp
Codes: C - Connected, S - Static, P - Route Input
B - BGP, O - Ospf, O3 - Ospf3, I - Isis
> - Best Route, * - Unresolved Nexthop
L - Part of a recursive route resolution loop
B 2001:10:1::/64 [200/42]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100::/64 [200/200]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100:1::/64 [200/0]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connected
>B 2001:10:100:2::/64 [200/42]
via 2001:10:1::100 [0/1]
via Ethernet1, directly connectedswitch# show rib route ipv6 connected
VRF name: default, VRF ID: 0xfe, Protocol: connected
Codes: C - Connected, S - Static, P - Route Input
B - BGP, O - Ospf, O3 - Ospf3, I - Isis
> - Best Route, * - Unresolved Nexthop
L - Part of a recursive route resolution loop
>C 2001:10:1::/64 [0/1]
via 2001:10:1::102, Ethernet1
>C 2001:10:2::/64 [0/1]
via 2001:10:2::102, Ethernet2
>C 2001:10:3::/64 [0/1]
via 2001:10:3::102, Ethernet3Dynamic Host Configuration Protocol (DHCP) for IPv4 and IPv6 dynamically assign network configurations to end hosts without statically configure an IP address for each device on the network. However, the underlying architecture and feature sets require different configurations on the switch.
| Feature | DHCPv4 | DHCPv6 |
|---|---|---|
| Transport Protocol | UDP Ports 67 (Server) and 68 (Client) | UDP Ports 547 (Server) and 546 (Client) |
| Initial Discovery | Layer 2 Broadcast (255.255.255.255) |
Layer 3 Multicast (ff02::1:2) |
| Default Gateway | Provided by the DHCP Server | Provided by ICMPv6 Router Advertisements |
| Lease Tracking | Always Stateful | Can be Stateful and Stateless |
| Hardware ID | Relies on the physical MAC Address | Relies on a generated DUID (DHCP Unique Identifier) |
The router with DHCP Server enabled acts as a server that allocates and delivers network addresses with desired configuration parameters to its hosts.
The DHCP server is based on ISC Kea.
The router with an DHCP Server enabled acts as a server that allocates and delivers network addresses with desired configuration parameters to its hosts.
DHCP Server support includes:
Additional features for DHCPv4 include a configurable static IP address for exclusive use by a given client, based on the client’s MAC address.
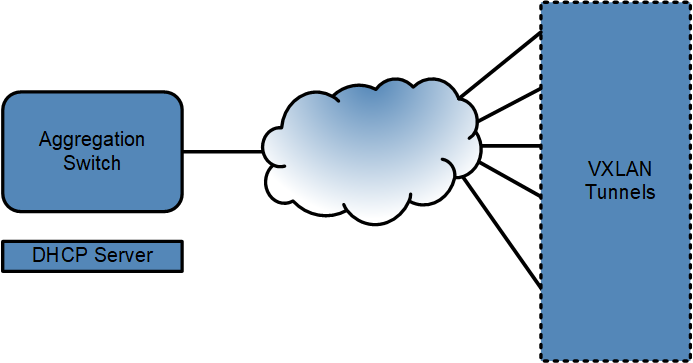
Example deployment:
DHCP Server on an aggregation switch, via VXLAN tunnels.
Global DHCP server options are configured per address family and apply to all subnets. Access the commands in the DHCP Server Configuration Mode.
switch# configure
switch(config)# dhcp server
switch(config-dhcp-server)#switch(config-dhcp-server)# disabledswitch(config-dhcp-server)# dns server ipv4 192.0.2.4 192.0.2.5
switch(config-dhcp-server)# dns server ipv6 2001:db8:0:10::53 2001:db8:0:10::5353switch(config-dhcp-server)# dns domain name ipv4 podV4.example.com
switch(config-dhcp-server)# dns domain name ipv6 podV6.example.comswitch(config-dhcp-server)# lease time ipv4 1 days 0 hours 0 minutes
switch(config-dhcp-server)# lease time ipv6 1 days 0 hours 0 minutes192.0.2.6 and an TFTP
server with the IPv6 address,
2601:600:cb02:d070:14b7:6ad0:bedb:ef3:switch(config-dhcp-server)# tftp server option 66 ipv4 192.0.2.6switch(config-dhcp-server)# tftp server option 150 ipv4 192.0.2.6 192.0.2.7switch(config-dhcp-server)# tftp server file ipv4 bootfile.conf
switch(config-dhcp-server)# tftp server file ipv6 bootfile.confswitch(config-dhcp-server)# vendor-option ipv4 vendorClassIDAswitch(config-dhcp-server)# vendor-option ipv4 defaultSub option number is 1
Length of the Data is 4
Data is c0:0:2:8
dhcp server
vendor-option ipv4 vendorClassIDA
sub-option 1 type ipv4-address data 192.0.2.8switch(config-dhcp-server)# vendor-option ipv4 vendorClassIDA sub-option 254 type array ipv4-address data 192.0.2.8 192.0.2.9 switch(config-dhcp-server)# vendor-option ipv4 default sub-option 30 type string data "vendor"switch(config-dhcp-server)# vendor-option ipv4 default sub-option 1 type ipv4-address data 192.0.2.8 sub-option 2 type string data “vendor"DHCP Server settings can also be configured per subnet and overrides the DHCP Server global mode configurations. There can be multiple subnets configured, but they must not overlap. EOS disables overlapping subnets.
switch# config
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 192.0.2.0/32switch(config-dhcp-subnet-ipv4)# name subnetv4switch(config-dhcp-subnet-ipv4)# range 192.0.2.100 192.0.2.199switch(config-dhcp-subnet-ipv4-range)# dns server 192.0.2.1 192.0.2.10switch(config-dhcp-subnet-ipv4)# lease time ipv4 3 days 0 hours 0 minutesswitch(config-dhcp-server)# subnet 192.0.2.0/32
switch(config-dhcp-subnet-ipv4)# default-gateway 192.0.2.3switch(config-dhcp-subnet-ipv4)# tftp server option 66 subnet-tftp.example.comswitch(config-dhcp-subnet-ipv4)# tftp server option 150 192.0.2.6 192.0.2.7switch(config-dhcp-subnet-ipv4)# tftp server file subnet-bootfile.confswitch# config
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 192.0.2.0/32
switch(config-dhcp-subnet-ipv4)# name subnetv4
switch(config-dhcp-subnet-ipv4)# range 192.0.2.100 192.0.2.199
switch(config-dhcp-subnet-ipv4-range)# dns server 192.0.2.1 192.0.2.10
switch(config-dhcp-subnet-ipv4)# lease time ipv4 3 days 0 hours 0 minutes
switch(config-dhcp-server)# subnet 192.0.2.0/32
switch(config-dhcp-subnet-ipv4)# default-gateway 192.0.2.3
switch(config-dhcp-subnet-ipv4)# tftp server option 66 subnet-tftp.example.com
switch(config-dhcp-subnet-ipv4)# tftp server option 150 192.0.2.6 192.0.2.7
switch(config-dhcp-subnet-ipv4)# tftp server file subnet-bootfile.confswitch(config-dhcp-subnet-ipv4)# reservations
switch(config-dhcp-sub-v4-reserve)# mac-address 1a1b.1c1d.1e1f
switch(config-dhcp-sub-v4-rsrv-mac-address)# ipv4-address 192.0.2.0High Availability (HA) provides a mechanism to add redundancy to DHCP servers using a heartbeat to monitor the communication state with the peer server, and synchronize lease information with other DHCP servers. EOS supports hot stand-by HA mode.
In the hot stand-by HA mode, the primary server acts as the sole responder to DHCP requests while the secondary server receives updates from the primary DHCP server and maintains a synchronized lease database. When the secondary DHCP server detects the primary DHCP status as down, the secondary DHCP server responds to DHCP requests until the primary DHCP server becomes available.
Each DHCP server in the HA setup must have an HA role, for example, hot stand-by mode requires a primary and secondary DHCP server configuration. To allow communication between the HA servers, each device must connect with another device through an HA peer link. Each interface contains an IP address used by the peer server to identify the local server through port 8000.
DHCPv4 and DHCPv6 apply the same configuration to HA.
To configure DHCP Server HA, enter the DHCP HA Configuration Mode:
switch(config)# dhcp-server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-server-ha)#Use the following command to add an IPv4 or IPv6 address used to accept incoming HA communication from peers:
switch(config-dhcp-server-ha)# address 10.0.1.1
switch(config-dhcp-server-ha)#Optionally, configure the period for sending heartbeats in seconds. This has a default value of 10 seconds. Use the following command to add a heartbeat of 60 seconds:
switch(config-dhcp-server-ha)# heartbeat interval 60 seconds
switch(config-dhcp-server-ha)#Configure the timeout value for the heartbeat as 600 seconds. The heartbeat timeout determines how long the primary server waits for a heartbeat response before determining the status of the peer server as down.
switch(config-dhcp-server-ha)# heartbeat timeout 600 seconds
switch(config-dhcp-server-ha)#For hot stand-by HA, both primary and secondary DHCP servers must be configured as active. Use the following command to configure the local DHCP server as the primary DHCP server:
switch(config-dhcp-server-ha)# role primary
switch(config-dhcp-server-ha)#To configure a peer server, add the IPv4 or IPv6 address. In this configuration, use the IPv4 address, 10.0.2.2:
switch(config-dhcp-server-ha)# peer 10.0.2.2
switch(config-dhcp-server-ha-10.0.2.2)#To set the peer DHCP server role as secondary, use the following command:
switch(config-dhcp-server-ha-10.0.2.2)# role secondary
switch(config-dhcp-server-ha-10.0.2.2)#switch# show dhcp server ipv4
IPv4 DHCP Server is active
Debug log is enabled
DNS server(s): 192.0.2.4 192.0.2.5
DNS domain name: podV4.example.com
Lease duration: 1 days 0 hours 0 minutes
TFTP server: 192.0.2.6 (Option 66)
192.0.2.6 192.0.2.7 (Option 150)
TFTP file: https://This email address is being protected from spambots. You need JavaScript enabled to view it.:123/example/one
Active Leases: 1
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Inactive (Could not determine VRF)
Ethernet2 Inactive (Not in default VRF)
Ethernet3 Inactive (Kernel interface not created yet)
Ethernet4 Inactive (Not up)
Ethernet5 Inactive (No IP address)
Ethernet6 Inactive (No Link Local address)
Ethernet7 Inactive (DHCP relay is configured for this interface)
Ethernet8 Inactive (DHCP relay is always on)
Ethernet9 Active
Vendor information:
Vendor ID: default
Sub-options Data
---------------- ----------------
1 192.0.2.0
2 “vendor”
Vendor ID: vendorClassIDA
Sub-options Data
---------------- --------------------
254 192.0.2.8, 192.0.2.9
Subnet: 192.0.2.0/24
Subnet name: subnetFooV4
Range: 192.0.2.100 to 192.0.2.199
DNS server(s): 192.0.2.1 192.0.2.10
Lease duration: 3 days 0 hours 0 minutes
Default gateway address: 192.0.2.3
TFTP server:
subnet-tftp.example.com (Option 66)
192.0.2.6 192.0.2.7 (Option 150)
TFTP boot file: subnet-bootfile.conf
Active leases: 1
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 192.0.2.201
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 192.0.2.150switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/24 (Subnet is disabled)
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0
Disabled reason(s):
Overlapping subnets: 10.0.0.0/8
Subnet: 10.0.0.0/8 (Subnet is disabled)
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.5.5.5
Default gateway address: 10.0.0.3
Active leases: 0
Disabled reason(s):
Overlapping subnets: 10.0.0.0/24
For Overlapping ranges:
switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/8 (Subnet is disabled)
Range: 10.0.0.1 to 10.0.0.10
Range: 10.0.0.9 to 10.0.0.12
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0
Disabled reason(s):
Overlapping range: 10.0.0.9 to 10.0.0.12
E.g. Duplicate static IP address reservation:
Subnet: 10.0.0.0/8 (Subnet is disabled)
Subnet name:
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.5.5.5
Default gateway address: 10.0.0.3
Active leases: 0
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 10.0.0.11
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 10.0.0.11
Disabled reason(s):
Duplicate IPv4 address reservation: 10.0.0.11switch# show dhcp server ipv6
IPv6 DHCP server is active
Debug log is enabled
DNS server(s): fe80::6
DNS domain name: aristanetworks.example.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Ethernet3 Active
Subnet: fe80::/10
Subnet name: foo
Range: fe80::1 to fe80::3
DNS server(s): fe80::4 fe80::5
Direct: Inactive (Multiple interfaces match this subnet: Ethernet1 Ethernet3)
Relay: Active
Active leases: 0interface Ethernet1
no switchport
ipv6 address 2001:db8:0:10::1/64
dhcp server ipv6
interface Ethernet3
no switchport
ipv6 address 2001:db8:0:11::1/64
dhcp server ipv6
dhcp server
subnet 2001:db8::/56interface Ethernet1
no switchport
ipv6 address fc00::1/7
ipv6 address fe80::1/64 link-local
dhcp server ipv6
dhcp server
subnet fc00::/7
subnet fe80::/64
#show dhcp server ipv6
IPv6 DHCP server is active
DNS server(s): fc00::2
DNS domain name: aristanetworks.example.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Subnet: fc00::/7
Subnet name: foo
Range: fc00::1 to fc00::5
DNS server(s): fc00::6 fc00::8
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0
Subnet: fe80::/64
Subnet name: subnetBarV6
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0switch# show dhcp server leases
10.0.0.10
End: 2019/06/20 17:44:34 UTC
Last transaction: 2019/06/19 17:44:34 UTC
MAC address: 5692.4c67.460a
2000:0:0:40::b
End: 2019/06/20 18:06:33 UTC
Last transaction: 2019/06/20 14:36:33 UTC
MAC address: 165a.a86d.ffacswitch# show dhcp server ipv4
IPv4 DHCP Server is active
Debug log is enabled
DNS server(s): 10.2.2.2
DNS domain name: domainFoo
Lease duration: 1 days 0 hours 0 minutes
TFTP server:
serverFoo (Option 66)
10.0.0.3 (Option 150)
TFTP file: fileFoo
Active Leases: 1
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Inactive (Could not determine VRF)
Ethernet2 Inactive (Not in default VRF)
Ethernet3 Inactive (Kernel interface not created yet)
Ethernet4 Inactive (Not up)
Ethernet5 Inactive (No IP address)
Ethernet6 Active
Vendor information:
Vendor ID: default
Sub-options Data
---------------- ----------------
1 192.0.2.0, 192.0.2.1
Vendor ID: vendorFoo
Sub-options Data
---------------- -----------
2 192.0.2.2
3 “Foo”
Subnet: 10.0.0.0/8
Subnet name: subnetFoo
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.1.1.1 10.2.2.2
Lease duration: 3 days 3 hours 3 minutes
Default gateway address: 10.0.0.3
TFTP server:
subnetServerFoo (Option 66)
10.0.0.4 (Option 150)
TFTP boot file: subnetFileFoo
Active leases: 1
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 10.0.0.1
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 10.0.0.2The Direct field displays Active when the subnet matches the interface with DHCPv6 configured. This indicates the server is accepting broadcast messages.
The Direct field displays Inactive when there is another existing subnet already matching the interface, or when the subnet matches more than one DHCP configured interface.
Examples of outputs for the DHCPv6 show dhcp server command:
switch# show dhcp server ipv6
IPv6 DHCP server is active
Debug log is enabled
DNS server(s): fe80::6
DNS domain name: testaristanetworks.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Ethernet3 Active
Subnet: fe80::/10
Subnet name: foo
Range: fe80::1 to fe80::3
DNS server(s): fe80::4 fe80::5
Direct: Inactive (Multiple interfaces match this subnet: Ethernet1 Ethernet3)
Relay: Active
Active leases: 0switch# show dhcp server ipv6
IPv6 DHCP server is active
DNS server(s): fc00::2
DNS domain name: testaristanetworks.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Subnet: fc00::/7
Subnet name: foo
Range: fc00::1 to fc00::5
DNS server(s): fc00::6 fc00::8
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0
Subnet: fe80::/10
Subnet name: bar
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/24 (Subnet is disabled - overlapping subnet 10.0.0.0/8)
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0
Subnet: 10.0.0.0/8 (Subnet is disabled - overlapping subnet 10.0.0.0/24)
DNS server(s):
Default gateway address: 10.0.0.3
Active leases: 0switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/8 (Subnet is disabled - range 10.0.0.9-10.0.0.12 overlaps with an existing pool)
Range: 10.0.0.1 to 10.0.0.10
Range: 10.0.0.9 to 10.0.0.12
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0Subnet: 10.0.0.0/8 (Subnet is disabled - ipv4-address 10.0.0.11 is reserved more than once)
Subnet name:
DNS server(s):
Default gateway address: 10.0.0.3
Active leases: 0
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 10.0.0.11
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 10.0.0.11switch# show dhcp server leases
10.0.0.10
End: 2019/06/20 17:44:34 UTC
Last transaction: 2019/06/19 17:44:34 UTC
MAC address: 5692.4c67.460a
2000:0:0:40::b
End: 2019/06/20 18:06:33 UTC
Last transaction: 2019/06/20 14:36:33 UTC
MAC address: 165a.a86d.ffacConfigure DHCP Relay using the dhcp relay command in the global configuration mode. The command places the switch in DHCP Relay mode and allows the configuration of DHCP Relay on several interfaces with a single command. The configuration entered in the DHCP Relay global configuration mode can be overridden by equivalent interface specific commands.
Examples
switch(config)# dhcp relay
switch(config-dhcp-relay)#Specify the IP address of the default DHCP or DHCPv6 Server. Multiple IP addresses can be specified and DHCP requests forward to all specified helper addresses. Configure an ip helper-address IP_Address under each desired routing interface.
switch(config)# interface ethernet1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# ip address 192.168.1.1/16
switch(config)# interface vlan2
switch(config-if-Et1)# ip address 172.16.1.1/16
switch(config)# dhcp relay
switch(config-dhcp-relay)# server 10.0.0.1
switch(config-dhcp-relay)# server 10.0.0.2
switch(config-dhcp-relay)# server DefaultDHCPHostnameswitch(config)# interface ethernet1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# ipv6 address fc00::1/10
switch(config)# dhcp relay
switch(config-dhcp-relay)# server fc00::3switch(config)# dhcp relay
switch(config-dhcp-relay)# no server 10.0.0.1
switch(config-dhcp-relay)# no server 10.0.0.2
switch(config-dhcp-relay)# no server DefaultDHCPHostname
switch(config-dhcp-relay)# no server fc00::3To override the default DHCP Server on an interface, the parameter,ip helper-addressIP_Address, must be used.
switch(config)# interface ethernet 1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# ip address 192.168.1.1/16
switch(config)# interface vlan2
switch(config-if-Et1)# ip address 172.16.1.1/16
switch(config-if-Et1)# ip helper-address 10.0.0.3
switch(config)# dhcp relay
switch(config-dhcp-relay)# server 10.0.0.1
switch(config-dhcp-relay)# server 10.0.0.2
switch(config-dhcp-relay)# server DefaultDHCPHostnameTo override the default DHCPv6 Server on an interface, the parameter, ipv6 helper-address IPv6_Address> must be used.
switch(config)# interface ethernet 1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# ipv6 address fc00::1/10
switch(config)# interface vlan2
switch(config-if-Et1)# ipv6 address fc00::2/10
switch(config-if-Et1)# ipv6 helper-address fc00::4
switch(config)# dhcp relay
switch(config-dhcp-relay)# server fc00::3Configure DHCP Relay for IPv4 unnumbered interfaces by adding a DHCP IPv4 helper address and configuring the vendor option.
switch(config)# dhcp relay
switch(config-dhcp-relay)# information option
switch(config-information-option)# vendor-optionConfigure Option-37 in DHCPv6 Relay to include the host name of the switch along with MAC
address and interface name in the remote id of the option. It requires the
remote-id format to be specified in the configuration mode.
switch(config)# ipv6 dhcp relay option remote-id format %m:%h:%p You can disable DHCP or DHCPv6 Relay functionality from a specific interface. This disables both DHCP Relay global and interface mode configurations.
switch(config)# interface vlan3
switch(config-if-Et1)# dhcp relay ipv4 disabledswitch(config)# interface vlan3
switch(config-if-Et1)# dhcp relay ipv6 disabledVirtual Router Redundancy Protocol (VRRP) provides high availability for the default gateway within a broadcast domain. In VRRP-based deployments with DHCP Relay, each participating router forwarded DHCP requests using its interface IP address, which resulted in duplicate relay requests, duplicate DHCP server ACKs, and increased control-plane noise. This feature solves these issues by making DHCP relay processing VRRP state-aware.
After disabling backup requests, only the VRRP Master router performs DHCP relay processing, ensuring a single authoritative relay agent per subnet. Routers in the Backup state suppress all DHCP relay processing and drop the requests, reducing control-plane overhead. When VRRP failovers, the newly elected Master automatically assumes relay responsibilities.
The fhrp parameter in DHCP Relay configures the relay agent to
use the First Hop Redundancy Protocol (FHRP) virtual IP address as the Gateway IP
address in relayed DHCP request packets instead of the interface physical IP
address.
switch(config)# dhcp relay
switch(config-dhcp-relay)# fhrp backup requests disabled
switch(config-dhcp-relay)#You must configure VRRP as active on the respective interfaces before enabling FHRP and checking the VRRP state before relaying DHCP packets. On a master router, the configuration relays DHCP packets, and on a backup router, the configuration drops DHCP packets. Be sure to apply the configuration consistently across both master and backup routers.
The show ip dhcp relay command displays all the interfaces enabled with DHCP Relay and the server configured on these interfaces.
switch# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCPv6 Relay Link-layer Address Option (79) is disabled
DHCPv6 Relay Remote ID (Option 37) encoding format: MAC address:interface ID
DHCP Smart Relay is disabled
Default L3 interface DHCP servers:
DHCPv4 servers: 10.0.0.1
10.0.0.2
DefaultDHCPHostname
DHCPv6 servers: fc00::3
Interface: Ethernet1
DHCP Smart Relay is disabled
DHCPv6 all subnet relaying is disabled
Using default DHCPv4 servers
Using default DHCPv6 servers
Interface: Ethernet2
DHCP Smart Relay is disabled
DHCPv6 all subnet relaying is disabled
Using default DHCPv4 servers
DHCPv6 servers: fc00::4
Interface: Vlan2
DHCP Smart Relay is disabled
DHCPv6 all subnet relaying is disabled
DHCPv4 servers: 11.0.0.3
DHCPv6 servers: fc00::4
Interface: Vlan3
DHCP Smart Relay is disabled
DHCPv6 all subnet relaying is disabled
DHCPv4 Relay is disabled
DHCPv6 Relay is disabled switch# show ip dhcp relay
DHCP Relay Option (82) is enabled
DHCP Relay vendor-specific suboption (9) under information option (82)The EOS DHCP relay agent supports forwarding of DHCP requests to DHCP servers located in a different VRF to the DHCP client interface VRF. In order to enable VRF support for the DHCP relay agent, Option 82 (DHCP Relay Agent Information Option) must first be enabled. The DHCP relay agent uses Option 82 to pass client specific information to the DHCP server.
| SubOpt | Len | ASCII VRF Identifier | ||||||
|---|---|---|---|---|---|---|---|---|
| 151 | 7 | V | R | F | N | A | M | E |
| SubOpt | Len | Subnet IP Address | |||
|---|---|---|---|---|---|
| 5 | 4 | A1 | A2 | A3 | A4 |
| SubOpt | Len | Overriding Server Identifier Address | |||
|---|---|---|---|---|---|
| 11 | 4 | B1 | B2 | B3 | B4 |
Direct communication between DHCP client and server may not be possible if they reside in separate VRFs. The Server identifier override and Link Selection sub-options set the relay agent to act as the DHCP server, and enable all DHCP communication to flow through the relay agent.
The relay agent adds all the appropriate sub-options, and forwards all request packets, including renew and release,to the DHCP server. When the relay receives the DHCP server response messages, EOS removes Option 82 information and forwards the response to the DHCP client in the client VRF.
EOS inserts the DHCP relay agent information option into DHCP messages relayed to the DHCP server. The ip helper-address command enables DHCP relay on an interface and relays DHCP messages to the specified IPv4 address.
Example
switch(config)# interface ethernet 1/2
switch(config-if-Et1/2)# ip helper-address 1.1.1.1
switch(config-if-Et1/2)#The commands provided in the following examples enable the attachment of VRF-related tags in the relay agent information option. If both the DHCP client interface and server interface exist on the same VRF, default or non-default, then EOS does not insert the VRF-related DHCP relay agent information option.
switch(config)# ip dhcp relay information optionswitch(config)# vrf instance mtxxg-vrf
switch(config-vrf-mtxxg-vrf)# router bgp 50
switch(config-router-bgp)# vrf mtxxg-vrf
switch(config-router-bgp-vrf-mtxxg-vrf)# rd 5546:5546
switch(config)# vrf instance qchyh-vrf
switch(config-vrf-qchyh-vrf)# router bgp 50
switch(config-router-bgp)# vrf qchyh-vrf
switch(config-router-bgp-vrf-qchyh-vrf)# rd 218:218switch(config)# interface ethernet 9
switch(config-if-Et9)# no switchportswitch(config-if-Et9)# vrf mtxxg-vrf
switch(config-if-Et9)# ip address 10.10.0.1/16switch(config-if-Et11)# vrf qchyh-vrf
switch(config-if-Et11)# ip address 10.40.0.1/16switch(config-if-Et11)# ip helper-address 10.40.2.3 vrf qchyh-vrfswitch(config)# dhcp relay
switch(config-dhcp-relay)# information option
switch(config-information-option)#switch(config-information-option)# circuit-id encoding (%x | %p)The default format uses string denoted by %p. Setting the encoding to %x enables hex encoding for the circuit ID. The configured value must be a valid hex number. If not configured, DHCP Relay uses the default format.
switch(config-information-option)# remote-id encoding (%x | %p)The default format uses string denoted by %p. Setting the encoding to %x enables hex encoding for the remote ID. The configured value must be a valid hex number. If not configured, DHCP Relay uses the default format.
Example
switch# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is enabled
DHCP Smart Relay is disabled
Interface: Ethernet9
Option 82 Circuit ID: Ethernet9
DHCP Smart Relay is disabled
DHCP servers: 10.40.2.3
10.40.2.3:vrf=qchyh-vrfThe ip dhcp relay information option (Global) command enables the configuration of the DHCP server to uniquely identify the origin of the request using a source-interface and the helper address. Configure the source interface with a routable address used by the DHCP server to uniquely identify the DHCP relay agent that forwarded the client request.
switch(config)# ip dhcp relay information optionswitch(config)# interface Loopback1
switch(config-if-Lo1)# ip address 1.1.1.1/24switch(config)# interface vlan100
switch(config-if-Vl100)# ip helper-address 10.1.1.4 source-interface Loopback1switch(config)# interface Loopback3
switch(config-if-Lo3)# vrf red
switch(config-if-Lo3)# ip address 1.1.1.1/24
switch(config)# interface vlan100
switch(config-if-Vl100)# ip helper-address 10.1.1.4 vrf red source-interface Loopback3switch(config)# interface vlan100
switch(config-if-Vl100)# no ip helper-address 10.1.1.4 source-interface Loopback1switch(config)# interface Loopback2
switch(config-if-Vl100)# ipv6 address 2001::10:20:30:1/128switch(config)# interface vlan200
switch(config-if-Vl200)# ipv6 dhcp relay destination 2002::10:20:30:2 local-interface Loopback2switch(config)# interface Loopback4
switch(config-if-Lo4)# vrf red
switch(config-if-Lo4)# ipv6 address 2001::10:20:30:1/128
switch(config)# interface vlan200
switch(config-if-Vl200)# ipv6 dhcp relay destination 2002::10:20:30:2 vrf red local-interface Loopback4switch(config-if-Vl200)# no ipv6 dhcp relay destination 2002::10:20:30:2 local-interface Loopback4switch# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is enabled
DHCP Smart Relay is disabled
Interface: Vlan100
Option 82 Circuit ID: Vlan100
DHCP Smart Relay is disabled
DHCP servers: 10.1.1.4
Interface: Vlan200
Option 82 Circuit ID: Vlan100
DHCP Smart Relay is disabled
DHCP servers: 2002::10:20:30:2The ipv6 dhcp relay always-on command enables the switch DHCP IPv6 Relay Agent globally regardless of the DHCP IPv6 Relay Agent status on any interface. EOS enables DHCP IPv6 Relay Agent by default if at least one routable interface has an ipv6 dhcp relay destination statement.
Example
switch(config)# ipv6 dhcp relay always-on
switch(config)#The ipv6 dhcp relay destination command enables the DHCP IPv6 Relay Agent function and specifies the client message destination address on an interface.
Example
switch(config)# interface ethernet 4
switch(config-if-Et4)# ipv6 dhcp relay destination 2001:0db8:0:1::1
switch(config-if-Et4)#The ipv6 dhcp relay option link-layer address command enables the DHCPv6 relay agent to configure the Client Link Layer Address option to solicit and request messages. In other words, the command enables the Client Link Layer Address option (79) in the Global Configuration Mode. The no ipv6 dhcp relay option link-layer address command disables the link layer address option (79) in the Global Configuration Mode.
Example
switch(config)# ipv6 dhcp relay option link-layer addressThe DHCPv6 Relay Option 37 allows a DHCPv6 relay agent to insert a Remote-ID option (Option 37) into DHCPv6 messages. This option provides the DHCPv6 server with information about the client's location, such as the MAC address of the relay agent, the ingress interface, and the VLAN ID. This is useful for network administrators to track the origin of DHCP requests and to enforce policies based on the client's location.
switch(config)# ipv6 dhcp relay option remote-id format %m:%h:%p switch# show ip dhcp relay
DHCP relay is active
DHCPv6 relay remote ID option (37) encoding format: MAC address:hostname:interface nameswitch(config-if-Et4)# exit
switch(config)# clear ipv6 dhcp relay counters
switch(config)#switch(config)# interface ethernet 4
switch(config-if-Et4)# clear ipv6 dhcp relay counters
switch(config)#The show ip dhcp relay command displays the status of DHCP relay agent parameters on the switch and each interface where at least one feature parameter is listed. The command displays the status for both global and interface configurations.
Example
switch(config)# interface ethernet 1/2
switch(config-if-Et1/2)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCPv6 Relay Link-layer Address Option (79) is disabled
DHCP Smart Relay is disabled
Interface: Ethernet1/2
DHCP Smart Relay is disabled
DHCP servers: 1::1
2001:db8:0:1::1
switch(config-if-Et1/2)#The show ipv6 dhcp relay counters command displays the number of DHCP packets received, forwarded, or dropped on the switch and on all interfaces enabled as DHCP relay agents.
Example
switch> show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Ethernet4 | 207 148 0 | 4 days, 19:54:24 ago
switch>switch# ip dhcp snoopingswitch# ip dhcp snooping information optionswitch# ip dhcp snooping vlanswitch# ip dhcp snooping information option circuit-id type 2 format
%h:%p Hostname and interface name
%p:%v Interface name and VLAN IDswitch# ip dhcp snooping bridgingThe ipv6 dhcp snooping command enables DHCP snooping globally on the switch. DHCP snooping provides a Layer 2 feature that can be configured on LAN switches. Arista switches support Option-37 insertion that allows relay agents to provide remote-ID information in DHCP request packets.
switch(config)# ipv6 dhcp snooping
switch(config)# ipv6 dhcp snooping remote-id option
switch(config)# ipv6 dhcp snooping vlan <vlan|vlan-range>switch(config)# ipv6 dhcp snooping
switch(config)# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
2789-2790
DHCPv6 Snooping is operational on following VLANs:
2789
Insertion of Option-37 is enabledswitch# show ip dhcp snooping
DHCP Snooping is enabled
DHCP Snooping is operational
DHCP Snooping is configured on following VLANs:
650
DHCP Snooping bridging is operational on following VLANs:
650
Insertion of Option-82 is enabled
Circuit-id sub-option Type: 0
Circuit-id format: Interface name:Vlan ID
Remote-id: 00:1c:73:8d:eb:67 (Switch MAC)
switch# show ip dhcp snooping counters debug
Counter Requests Responses
----------------------------- ----------------- -----------------
Received 3 2
Forwarded 3 2
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Info Option 0 0
Dropped - Snooping disabled 0 0switch# show platform trident tcam detail | grep -i dhcp
DHCP Snooping uses 3 entries.
…
655402 45 hits - DHCP client to relay trap-to-cpuThe clear ip dhcp relay counters command resets the DHCP relay counters. The configuration mode determines which counters are reset:.
The Interface configuration command clears the counter for the configuration mode interface.
Command Mode
Privileged EXEC
Command Syntax
clear ip dhcp relay counters [interface_name]
Parameters
switch# show ip dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Vlan1001 | 207 148 0 | 4 days, 19:54:24 ago
Vlan1045 | 376 277 0 | 4 days, 19:54:24 ago
switch# clear ip dhcp relay counters interface vlan 1045
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 380 380 0 | 4 days, 21:19:17 ago
All Resp | 281 281 0 |
| |
Vlan1000 | 207 148 0 | 4 days, 21:18:30 ago
Vlan1045 | 0 0 0 | 0:00:07 agoswitch(config-if-Vl1045)# exit
switch(config)# clear ip dhcp relay counters
switch(config)# show ip dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|-------------
All Req | 0 0 0 | 0:00:03 ago
All Resp | 0 0 0 |
| |
Vlan1000 | 0 0 0 | 0:00:03 ago
Vlan1045 | 0 0 0 | 0:00:03 agoThe clear ip dhcp snooping counters command resets the DHCP snooping packet counters.
Command Mode
Privileged EXEC
Command Syntax
clear ip dhcp snooping counters [counter_type]
Parameters
switch# clear ip dhcp snooping counters
switch# show ip dhcp snooping counters
| Dhcp Request Pkts | Dhcp Reply Pkts |
Vlan | Rcvd Fwdd Drop | Rcvd Fwdd Drop | Last Cleared
-----|------ ----- ------|----- ---- ------|-------------
100 | 0 0 0 | 0 0 0 | 0:00:10 ago
switch#switch# clear ip dhcp snooping counters debug
switch# show ip dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 0 0
Forwarded 0 0
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Info Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 0:00:08 ago
switch#The clear ipv6 neighbors command removes the specified dynamic IPv6 neighbor discovery cache entries. Commands that do not specify an IPv6 address remove all dynamic entries for the listed interface. Commands that do not specify an interface remove all dynamic entries.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 neighbors [port][dynamic_ipv6]
Example
switch# clear ipv6 neighbors vlan 200
switch#The clear ipv6 dhcp relay counters command resets the DHCP relay counters. If you do not specify a port, the command clears the counters for the switch and for all interfaces. Otherwise, the command clears the counter for the specified interface.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 dhcp relay counters [port]
Parameters
Example
switch(config)# show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Ethernet4 | 207 148 0 | 4 days, 19:54:24 ago
switch(config)# interface ethernet 4
switch(config-if-Et4)# clear ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 380 380 0 | 4 days, 21:19:17 ago
All Resp | 281 281 0 |
| |
Ethernet4 | 0 0 0 |4 days, 21:18:30 ago
These commands clear all DHCP relay counters on the switch.
switch(config-if-Et4)# exit
switch(config)# clear ipv6 dhcp relay counters
switch(config)# show ipv6 dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|-------------
All Req | 0 0 0 | 0:00:03 ago
All Resp | 0 0 0 |
| |
Ethernet4 | 0 0 0 | 0:00:03 ago
switch(config)#The clear ipv6 dhcp snooping counters command resets the DHCP snooping packet counters.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 dhcp snooping counters [counter_type]
switch# clear ipv6 dhcp snooping counters
switch# show ipv6 dhcp snooping counters
| Dhcpv6 Request Pkts | Dhcpv6 Reply Pkts |
Vlan | Rcvd Fwdd Drop | Rcvd Fwdd Drop | Last Cleared
-----|------ ------ -------|------ ----- ------|-------------
2789 | 1 1 0 | 1 1 0 | 0:03:09 agoswitch# clear ipv6 dhcp snooping counters debug
switch# show ipv6 dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 1 1
Forwarded 1 1
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Remote-ID Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 0:04:29 agoThe default-gateway command in DHCP Server Subnet Configuration Mode populates DHCP Option 3 (Router Option) in the DHCP payload sent from the switch to the client and allows communication to another VLAN or network.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv4 Subnet Configuration
Command Syntax
default-gateway
no default-gateway
default default-gateway
Parameters
default-gateway ipv4_address - Add a default gateway to the subnet.
Example
10.10.10.1, to
subnet
172.16.23.11/32:switch(config)# dhcp server
switch(config-dhcp-server)# subnet 172.16.23.11/32
switchconfig-dhcp-subnet-ipv4)# default-gateway 10.10.10.1
switchconfig-dhcp-subnet-ipv4)#The default-gateway command in DHCP Server Subnet Configuration Mode populates DHCP Option 3 (Router Option) in the DHCP payload sent from the switch to the client and allows communication to another VLAN or network.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv6 Subnet Configuration
Command Syntax
default-gateway
no default-gateway
default default-gateway
Example
2001:db8:cafe:a100::99, to subnet
2001:db8:acad:1::fe21/32:switch(config)# dhcp server
switch(config-dhcp-server)# subnet 2001:db8:acad:1::fe21/32
switchconfig-dhcp-subnet-ipv6)# default-gateway 2001:db8:cafe:a100::99
switchconfig-dhcp-subnet-ipv6)#The dhcp relay command places the switch in the DHCP relay mode. Execute this command in the Global Configuration Mode.
The no dhcp relay command removes DHCP relay configuration from the running-config.
Command Mode
Global Configuration Mode
Command Syntax
dhcp relay
no dhcp relay
Example
switch(config)# dhcp relay
switch(config-dhcp-relay)#The dhcp relay ipv6 command in the DHCP Relay Configuration Mode configures DHCP Relay IPv6 routes and disable DHCP route persistence or synchronize neighbors.
Command Mode
DHCP Relay Configuration
Command Syntax
dhcp relay ipv6 routes [persistence disable] | [sync neighbor [ ipv4 | ipv6]
no dhcp relay ipv6
default dhcp relay ipv6
switch(config)# dhcp relay
switch(config-dhcp-relay)# ipv6 routes persistence disabled
switch(config-dhcp-relay)#Use the following commands to synchronize with neighbor,
172.16.23.15:
switch(config)# dhcp relay
switch(config-dhcp-relay)# sync neighbor 172.16.23.15
switch(config-dhcp-relay)#The client requests command in the DHCP Relay Configuration Mode configures DHCP Relay to evaluate incoming.
Command Mode
DHCP Relay Configuration
Command Syntax
client requests [[cross-vrf server-id preserve] | [flooding suppress]]
no client requests
default client requests
switch(config)# dhcp relay
switch(config-dhcp-relay)# client requests cross-vrf server-id preserve
switch(config-dhcp-relay)#switch(config)# dhcp relay
switch(config-dhcp-relay)# client requests flooding suppress
switch(config-dhcp-relay)#The dhcp server command places the switch in the DHCP relay mode. Execute this command in the DHCP Server Configuration Mode.
The no dhcp server command removes DHCP relay configuration from the running-config.
Command Mode
Global Configuration Mode
Command Syntax
dhcp server
no dhcp server
Example
switch(config)# dhcp server
switch(config-dhcp-server)#The dhcp server client command in the IPv4 or IPv6 Subnet Configuration Mode configures client options for the DHCP server. Execute this command under the dhcp server configuration mode.
Command Mode
DHCP Server Configuration
DHCP Server Subnet Configuration
DHCP Server IPv4 or IPv6 Subnet Range Configuration
Command Syntax
dhcp server client class [ipv4|ipv6] definition client_class assignments [default-gateway|dns|lease|option|private-option|tftp]
Example
switch(config-dhcp-server)# client class ipv4 definition test1 default-gateway 10.0.0.1The dhcp server debug log command configures DHCP server debugging configuration. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server debug log file
Parameters
log file - Specify the file location to store debugging logs.
Example
switch(config-dhcp-server)# debug logThe dhcp server dns command configures DHCP server DNS options. Execute this command in the DHCP Server Configuration Mode and DHCP Server IPv4 Subnet Configuration Mode.
Command Mode
DHCP Server Configuration
DHCP Server IPv4 or IPv6 Subnet Configuration
Command Syntax
dhcp server dns [domain name domain_name ] [server [ipv4|ipv6] ip_address
Example
switch(config-dhcp-server)# dns server ipv4 192.168.10.5The dhcp server lease command configures DHCP server lease options. Execute this command in the DHCP Server Configuration Mode and DHCP Server IPv4 Subnet Configuration Mode.
Command Mode
DHCP Server Configuration
DHCP Server IPv4 or IPv6 Subnet Configuration
Command Syntax
dhcp server lease time [ipv4|ipv6] days days hourshours minutesminutes
Example
switch(config-dhcp-server)# dns lease time ipv4 10 daysThe dhcp server next-server command in the DHCP Server Configuration Mode
populates a specific legacy field in the DHCP packet header called the siaddr, Server
IP address. During initialization, a switch requires information about the location of a DHCP server. After
receiving an IP address for the bootstrap process, the switch contacts the TFTP or HTTP server and downloads
the configuration file specified in the bootfile command.
Command Mode
DHCP Server Configuration
Command Syntax
next-server ipv4_address
no next-server
Parameters
next-server ipv4_address - Specify the IPv4 address for the DHCP server.
Example
172.16.23.3, as the
DHCP
server:switch(config)# dhcp server
switch(config-dhcp-server)# next-server 172.16.23.3
switch(config-dhcp-server)#The dhcp server option command configures DHCP server options. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration
DHCP Server IPv4 or IPv6 Subnet Configuration
Command Syntax
dhcp server option ipv4 code [always-send data type [hex |string] data]] quoted_string hex [client-id disable] hours hours minutes minutes
dhcp server option ipv6 code [always-send data type [hex |string] data]] quoted_string hex [client-id disable] hours hours minutes minutes
Example
switch(config-dhcp-server)# option ipv4 option 67The dhcp server private-option command configures DHCP server private options. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server private-option [ipv4|ipv6] code [always-send data type [hex |string] data]] quoted_string hex
Example
switch(config-dhcp-server)# option ipv4 private-option 225 always-send private-option ipv4 225 always-send type string data "Code Sent"The dhcp server subnet command configures DHCP server subnet options. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server subnet ipv4_address ipv6_address
Example
switch(config-dhcp-server)# subnet 198.168.0.0/24The dhcp server subnet [ipv4 | ipv6] client command configures client options for the DHCP server. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server subnet [ipv4|ipv6] client class definition client_class [default-gateway|dns|lease|name|range|reservations|tftp]
Example
switch(config-dhcp-server)#subnet ipv4 client class ipv4 definition test1 default-gateway 10.0.0.1The dhcp server tftp command configures DHCP server TFTP options. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server tftp server [file [ipv4|ipv6] file_name] [option [150|66]] ipv4
Example
switch(config-dhcp-server)# tftp option 150 ipv4 198.168.0.11The dhcp server vendor-option command configures the DHCP server vendor identifier options. Execute this command under the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server vendor-option ipv4 vendor_id default vendor_id sub-option sub-option_code
Example
switch(config-dhcp-server)# vendor-option 1:4:c0:0:2:8The dhcp server vendor-option command configures the DHCP server vendor identifier options. Execute this command in the DHCP Server Configuration Mode.
Command Mode
DHCP Server Configuration Mode
Command Syntax
dhcp server vendor-option ipv4 vendor_id default vendor_id sub-option sub-option_code type [array | ipv4-address | string] array [ipv4-address data ip_address [string data quoted_string
Example
switch(config-dhcp-server)# vendor-option 1:4:c0:0:2:8The high-availability command in the DHCP Server Configuration Mode enters the High Availability (HA) Configuration Mode and allows the configuration of HA for a primary and secondary DHCP server. The parameter, mode, places the DHCP server in hot stand-by mode for HA.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server High Availability Configuration Mode
Command Syntax
high-availability [ address [ ipv4 | ipv6]] [mode hot-standby] [role [primary |secondary]]
no high-availability
default high-availability
Parameters
Examples
Use the following commands to specify the IPv4 address, 10.0.1.1, for the DHCP server:
switch(config)# dhcp-server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-server-ha)# 10.0.1.1
switch(config-dhcp-server-ha)#Use the following commands to place the DHCP server into hot stand-by mode for HA:
switch(config)# dhcp-server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-server-ha)# mode hot-standby
switch(config-dhcp-server-ha)#Use the following commands to specify the local DHCP server HA role as primary:
switch(config)# dhcp-server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-server-ha)# role primary
switch(config-dhcp-server-ha)#The high-availability heartbeat command places the switch in the DHCP Server High Availability Configuration Mode configures the heartbeat and timeout interval for a DHCP server in HA mode.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server High Availability Configuration Mode
Command Syntax
high-availability heartbeat [interval seconds seconds] [timeout seconds seconds]
no high-availability heartbeat
default high-availability heartbeat
Parameters
Examples
Use the following commands to configure a heartbeat interval of 30 seconds:
switch(config)# dhcp server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-ha)# interval 30 seconds
switch(config-dhcp-ha)#Use the following commands to configure a heartbeat timeout of 30 seconds:
switch(config)# dhcp server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-ha)# timeout 30 seconds
switch(config-dhcp-ha)#The high-availability peer role command in the DHCP Server High Availability Configuration Mode configures DHCP peer servers for HA.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server High Availability Configuration
Command Syntax
high-availability [peer [ ipv4 | ipv6 ]] [role [primary | secondary]]
no high-availability peer
default high-availability peer
Parameters
Example
Use the following commands to configure the IPv4 address, 10.0.2.2, as the secondary HA DHCP server:
switch(config)# dhcp server
switch(config-dhcp-server)# high-availability
switch(config-dhcp-ha)# peer 10.0.2.2
switch(config-dhcp-ha-10.0.2.2)# role secondary
switch(config-dhcp-ha-10.0.2.2)#The ip dhcp relay all-subnets command configures the DHCP smart relay status in the Interface Configuration Mode. DHCP smart relay supports forwarding DHCP requests with a client secondary IP addresses in the gateway address field. Enabling DHCP smart relay on an interface requires that you enable DHCP relay on that interface.
By default, an interface assumes the global DHCP smart relay setting as configured by the ip dhcp relay all-subnets default command. The ip dhcp relay all-subnets command, when configured, takes precedence over the global smart relay setting.
The no ip dhcp relay all-subnets command disables DHCP smart relay on the configuration mode interface. The default ip dhcp relay all-subnets command restores the interface to the default DHCP smart relay setting, as configured by the ip dhcp relay all-subnets default command, by removing the corresponding ip dhcp relay all-subnets or no ip dhcp relay all-subnets statement from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip dhcp relay all-subnets
no ip dhcp relay all-subnets
default ip dhcp relay all-subnets
switch(config)# interface vlan 100
switch(config-if-Vl100)# ip helper-address 10.4.4.4
switch(config-if-Vl100)# ip dhcp relay all-subnets
switch(config-if-Vl100)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCP Smart Relay is enabled
Interface: Vlan100
DHCP Smart Relay is enabled
DHCP servers: 10.4.4.4
switch(config-if-Vl100)#switch(config-if-Vl100)# no ip dhcp relay all-subnets
switch(config-if-Vl100)# show active
interface Vlan100
no ip dhcp relay all-subnets
ip helper-address 10.4.4.4
switch(config-if-Vl100)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCP Smart Relay is enabled
Interface: Vlan100
DHCP Smart Relay is disabled
DHCP servers: 10.4.4.4
switch(config-if-Vl100)#switch(config)# ip dhcp relay all-subnets default
switch(config)# interface vlan 100
switch(config-if-Vl100)# ip helper-address 10.4.4.4
switch(config-if-Vl100)# default ip dhcp relay
switch(config-if-Vl100)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCP Smart Relay is enabled
Interface: Vlan100
Option 82 Circuit ID: 333
DHCP Smart Relay is enabled
DHCP servers: 10.4.4.4
switch(config-if-Vl100)#The ip dhcp relay all-subnets default command configures the global DHCP smart relay setting. DHCP smart relay supports forwarding DHCP requests with a client secondary IP addresses in the gateway address field. The default global DHCP smart relay setting is disabled.
The global DHCP smart relay setting applies to all interfaces for which an ip dhcp relay all-subnets statement does not exist. Enabling DHCP smart relay on an interface requires that you also enable DHCP relay on that interface.
The no ip dhcp relay all-subnets default and default ip dhcp relay all-subnets default commands restore the global DHCP smart relay default setting of disabled by removing the ip dhcp relay all-subnets default command from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp relay all-subnets default
no ip dhcp relay all-subnets default
default ip dhcp relay all-subnets default
Example
switch(config)# ip dhcp relay all-subnets default
switch(config)#The ip dhcp relay always-on command enables the DHCP relay agent on the switch regardless of the DHCP relay agent status on any interface. By default, EOS enables the DHCP relay agent only if you have one routable interface configured with an ip helper-address statement.
The no ip dhcp relay always-on and default ip dhcp relay always-on commands remove the ip dhcp relay always-on command from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp relay always-on
no ip dhcp relay always-on
default ip dhcp relay always-on
Example
switch(config)# ip dhcp relay always-on
switch(config)#The ip dhcp relay information option command configures the switch to attach tags to DHCP requests before forwarding them to the DHCP servers designated by the ip helper-address commands. The command specifies the tag contents for packets forwarded by the configured interface. The default value for each interface configured with an ip helper-address is the name and number of the interface.
The no ip dhcp relay information option and default ip dhcp relay information option commands restore the switch default setting of not attaching tags to DHCP requests by removing the ip dhcp relay information option command from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp relay information option
no ip dhcp relay information option
default ip dhcp relay information option
Example
switch(config)# ip dhcp relay information option
switch(config)#The ip dhcp relay information option circuit-id command specifies the content of tags that the switch attaches to DHCP requests before forwarding them from the configuration mode interface to DHCP server addresses specified by ip helper-address commands. Tags attach to outbound DHCP requests only if you enable the information option on the switch (ip dhcp relay information option circuit-id).
The no ip dhcp relay information option circuit-id and default ip dhcp relay information option circuit-id commands restore the default content setting for the configuration mode interface by removing the corresponding command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip dhcp relay information option circuit-id id_label
no ip dhcp relay information option circuit-id
default ip dhcp relay information option circuit-id
Parameters
id_label- Specifies the tag content. Use a format in alphanumeric characters (maximum 15 characters).
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ip dhcp relay information option circuit-id x-1234
switch(config-if-Vl200)#The ip dhcp snooping command enables DHCP snooping globally on the switch. Configure DHCP snooping as a set of Layer 2 processes and use it with DHCP servers to control network access to clients with specific IP/MAC addresses. The switch supports Option-82 insertion,a DHCP snooping process that allows relay agents to provide remote-ID and circuit-ID information to DHCP reply and request packets. DHCP servers use this information to determine the originating port of DHCP requests and associate a corresponding IP address to that port. DHCP servers use port information to track host location and IP address usage by authorized physical ports.
DHCP snooping uses the information option (Option-82) to include the switch MAC address as the router-ID along with the physical interface name and VLAN number as the circuit-ID in DHCP packets. After adding the information to the packet, the DHCP relay agent forwards the packet to the DHCP server as specified by the DHCP protocol.
The no ip dhcp snooping and default ip dhcp snooping commands disables global DHCP snooping by removing the ip dhcp snooping command from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp snooping
no ip dhcp snooping
default ip dhcp snooping
Example
switch(config)# show ip dhcp snooping
DHCP Snooping is disabled
switch(config)# ip dhcp snooping
switch(config)# show ip dhcp snooping
DHCP Snooping is enabled
DHCP Snooping is not operational
DHCP Snooping is configured on following VLANs:
None
DHCP Snooping is operational on following VLANs:
None
Insertion of Option-82 is disabled
switch(config)#The ip dhcp snooping bridging command enables the DHCP snooping bridging configuration.
The no ip dhcp snooping bridging command removes the DHCP snooping bridging configuration from the running-config.
Command Mode
Global Configuration Mode
Command Syntax
ip dhcp snooping bridging
no ip dhcp snooping bridging
Example
switch# configure
switch(config)# ip dhcp snooping bridgingThe ip dhcp snooping information option command enables the insertion of option-82 DHCP snooping information in DHCP packets on VLANs where you have DHCP snooping enabled. DHCP snooping provides a Layer 2 switch process that allows relay agents to provide remote-ID and circuit-ID information to DHCP reply and request packets. DHCP servers use this information to determine the originating port of DHCP requests and associate a corresponding IP address to that port.
DHCP snooping uses information option (Option-82) to include the switch MAC address (router-ID) along with the physical interface name and VLAN number (circuit-ID) in DHCP packets. After adding the information to the packet, the DHCP relay agent forwards the packet to the DHCP server through DHCP protocol processes.
Ifnot enabling DHCP snooping globally, the ip dhcp snooping information option command persists in running-config without any operational effect.
The no ip dhcp snooping information option and default ip dhcp snooping information option commands disable the insertion of option-82 DHCP snooping information in DHCP packets by removing the ip dhcp snooping information option statement from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp snooping information option
no ip dhcp snooping information option
default ip dhcp snooping information option
Example
switch(config)# ip dhcp snooping information option
switch(config)# show ip dhcp snooping
DHCP Snooping is enabled
DHCP Snooping is operational
DHCP Snooping is configured on following VLANs:
100
DHCP Snooping is operational on following VLANs:
100
Insertion of Option-82 is enabled
Circuit-id format: Interface name:Vlan ID
Remote-id: 00:1c:73:1f:b4:38 (Switch MAC)
switch(config)#The ip dhcp snooping vlan command enables DHCP snooping on specified VLANs. DHCP snooping provides a Layer 2 process that allows relay agents to provide remote-ID and circuit-ID information in DHCP packets. DHCP servers use this data to determine the originating port of DHCP requests and associate a corresponding IP address to that port. Configure DHCP snooping on a global and VLAN basis.
If not enabling global DHCP snooping, the ip dhcp snooping vlan command persists in running-config without any operational affect.
The no ip dhcp snooping information option and default ip dhcp snooping information option commands disable DHCP snooping operability by removing the ip dhcp snooping information option statement from running-config.
Command Mode
Global Configuration
Command Syntax
ip dhcp snooping vlan v_range
no ip dhcp snooping vlan v_range
default ip dhcp snooping vlan v_range
Parameters
v_range - Specifies the range of VLANs to enable DHCP snooping. Formats include a number, a number range, or a comma-delimited list of numbers and ranges. Numbers range from 1 to 4094.
Example
switch(config)# ip dhcp snooping
switch(config)# ip dhcp snooping information option
switch(config)# ip dhcp snooping vlan 100
switch(config)# interface vlan 100
switch(config-if-Vl100)# ip helper-address 10.4.4.4
switch(config-if-Vl100)# show ip dhcp snooping
DHCP Snooping is enabled
DHCP Snooping is operational
DHCP Snooping is configured on following VLANs:
100
DHCP Snooping is operational on following VLANs:
100
Insertion of Option-82 is enabled
Circuit-id format: Interface name:Vlan ID
Remote-id: 00:1c:73:1f:b4:38 (Switch MAC)
switch(config)#The iv6p dhcp relay always-on command enables the switch DHCP relay agent on the switch regardless of the DHCP relay agent status on any interface. By default, the DHCP relay agent is enabled only if at least one routable interface is configured with an ipv6 dhcp relay destination statement.
The no ipv6 dhcp relay always-on and default ipv6 dhcp relay always-on commands remove the ipv6 dhcp relay always-on command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay always-on
no ipv6 dhcp relay always-on
default ipv6 dhcp relay always-on
Exampleswitch(config)# ipv6 dhcp relay always-on
switch(config)#The ipv6 dhcp relay destination command enables the DHCPv6 relay agent and sets the destination address on the configuration mode interface.
The no ipv6 dhcp relay destination and default ipv6 dhcp relay destination commands remove the corresponding ipv6 dhcp relay destination command from running-config. When the commands do not list an IPv6 address, all ipv6 dhcp relay destination commands are removed from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 dhcp relay destination [ipv6_addr][source-address ipv6_addr]
no ipv6 dhcp relay destination [ipv6_addr]
default ipv6 dhcp relay destination [ipv6_addr]
Guidelines
If the source-address parameter is specified, then the DHCP client receives an IPv6 address from the subnet of source IP address. The source-address must be one of the configured addresses on the interface.
Example
switch(config)# interface ethernet 4
switch(config-if-Et4)# ipv6 dhcp relay destination 2001:0db8:0:1::1
switch(config-if-Et4)# show ip dhcp relay
DHCP Relay is active
DHCP Relay Option 82 is disabled
DHCPv6 Relay Link-layer Address Option (79) is disabled
DHCP Smart Relay is disabled
Interface: Ethernet4
DHCP Smart Relay is disabled
DHCP servers: 1::1
2001:db8:0:1::1
switch(config-if-Et4)#The ipv6 dhcp relay option link-layer address command enables the DHCPv6 relay agent to configure the client link layer address option to solicit and request messages. In other words, the command enables the link layer address option (79) in the global configuration mode.
The no ipv6 dhcp relay option link-layer address command disables the link layer address option (79) in the global configuration mode.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay option link-layer address
no ipv6 dhcp relay option link-layer address
default ipv6 dhcp relay option link-layer address
Example
switch(config)# ipv6 dhcp relay option link-layer addressThe ipv6 dhcp relay option command configures DHCPv6 Relay Option 37, Remote-ID, to add the MAC address, interface ID or name, and hostname as the remote-id format. The no version of the command removes the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp relay option remote-id format {%m:%h:%p | %m:%i | %m:%p}
no ipv6 dhcp relay option remote-id format {%m:%h:%p | %m:%i | %m:%p}
Example
switch(config)# ipv6 dhcp relay option remote-id format %m:%h:%p The ipv6 dhcp snooping command enables DHCP snooping globally on the switch.
The no ipv6 dhcp snooping and default ipv6 dhcp snooping commands disable global DHCP snooping by removing the ipv6 dhcp snooping command from running-config.
Command Mode
Global Configuration
Command Syntax
ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
no ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
default ipv6 dhcp snooping [remote-id option | vlan [$ | vlan-range]]
Examples
switch(config)# ipv6 dhcp snooping
switch(config)# ipv6 dhcp snooping remote-id option
switch(config)# ipv6 dhcp snooping vlan <vlan|vlan-range>switch(config)# ipv6 dhcp snooping
switch(config)# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
2789-2790
DHCPv6 Snooping is operational on following VLANs:
2789
Insertion of Option-37 is enabledThe name command in DHCP Server Subnet Configuration Mode creates a name for the subnet and improves readability of the subnet list.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv4 or IPv6 Subnet Configuration
Command Syntax
name
no name
default name
Parameters
Example
Use the following commands to configure a name, remote_switch, to subnet
172.16.23.11/32:
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 172.16.23.11/32
switchconfig-dhcp-subnet-ipv4)# name remote_switch
switchconfig-dhcp-subnet-ipv4)#The prefix-delegation command in DHCP Server IPv6 Subnet Configuration Mode configures a block of IPv6 addresses for a downstream router on the network. The router then splits the block into subnets and assigns the IPv6 addresses to devices on its network.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv6 Subnet Configuration
Command Syntax
prefix-delegation
no prefix-delegation
default prefix-delegation
Parameters
Example
Use the following commands to delegate a block of IPv6 addresses, 2001:db8:100:aa00::/56, to subnet
2001:db8:100::/48:
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 2001:db8:100::/48
switchconfig-dhcp-subnet-ipv6)# prefix-delegation 2001:db8:100:aa00::/56
switchconfig-dhcp-subnet-ipv6)#The range command in DHCP Server Subnet Configuration Mode explicitly defines the contiguous block of IP addresses that the DHCP server is allowed to dynamically lease to clients.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv6 Subnet Configuration
Command Syntax
subnet [ipv4 | ipv6] range start_ipaddress end_ipaddress
no range
default range
Parameters
Example
Use the following commands to configure a name, remote_switch, to subnet
172.16.23.11/32:
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 172.16.23.11/32
switchconfig-dhcp-subnet-ipv4)# range 172.16.23.100 172.16.23.200
switchconfig-dhcp-subnet-ipv4)#The reservations mac-address command in DHCP Server IPv4 Subnet Reservations Configuration Mode builds static DHCP bindings from the client MAC address on the reservations list. Once in the DHCP Server IPv4 Subnet Reservations MAC Address Configuration Mode, add reservations for a hostname and an IPv4 address to map to the MAC address.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
DHCP Server IPv4 Subnet Reservations Configuration
Command Syntax
reservations mac-address
Parameters
Example
Use the following commands to configure a reservation for MAC address,
80:A9:97:27:1A:AC, and IPv4 address, 172.26.23.25
to the subnet reservation. 172.16.23.11/32:
switch(config)# dhcp server
switch(config-dhcp-server)# subnet 172.16.23.11/32
switchconfig-dhcp-subnet-ipv4)# reservations
switchconfig-dhcp-subnet-ipv4-reserve)# mac-address 80:A9:97:27:1A:AC
switchconfig-dhcp-subnet-ipv4-rsrv-mac-address)# ipv4-address 172.26.23.25
switchconfig-dhcp-subnet-ipv4-rsrv-mac-address)#Use the show dhcp server command to display DHCP server information.
Command Mode
EXEC
Command Syntax
show dhcp server [ipv4 | ipv6 | leases | vrf]
switch# show dhcp server ipv4
IPv4 DHCP Server is active
Debug log is enabled
DNS server(s): 10.2.2.2
DNS domain name: mydomain
Lease duration: 1 days 0 hours 0 minutes
TFTP server:
myserver (Option 66)
10.0.0.3 (Option 150)
TFTP file: fileFoo
Active Leases: 1
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Inactive (Could not determine VRF)
Ethernet2 Inactive (Not in default VRF)
Ethernet3 Inactive (Kernel interface not created yet)
Ethernet4 Inactive (Not up)
Ethernet5 Inactive (No IP address)
Ethernet6 Active
Vendor information:
Vendor ID: default
Sub-options Data
---------------- ----------------
1 192.0.2.0, 192.0.2.1
Vendor ID: vendorFoo
Sub-options Data
---------------- -----------
2 192.0.2.2
3 “data”
Subnet: 10.0.0.0/8
Subnet name: subnetFoo
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.1.1.1 10.2.2.2
Lease duration: 3 days 3 hours 3 minutes
Default gateway address: 10.0.0.3
TFTP server:
subnetServerFoo (Option 66)
10.0.0.4 (Option 150)
TFTP boot file: subnetFiletftp
Active leases: 1
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 10.0.0.1
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 10.0.0.2switch# show dhcp server ipv6
IPv6 DHCP server is active
Debug log is enabled
DNS server(s): fe80::6
DNS domain name: testaristanetworks.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Ethernet3 Active
Subnet: fe80::/10
Subnet name: foo
Range: fe80::1 to fe80::3
DNS server(s): fe80::4 fe80::5
Direct: Inactive (Multiple interfaces match this subnet: Ethernet1 Ethernet3)
Relay: Active
Active leases: 0switch# show dhcp server ipv6
IPv6 DHCP server is active
DNS server(s): fc00::2
DNS domain name: testaristanetworks.com
Lease duration: 1 days 3 hours 30 minutes
Active leases: 0
IPv6 DHCP interface status:
Interface Status
--------------- ------
Ethernet1 Active
Subnet: fc00::/7
Subnet name: data
Range: fc00::1 to fc00::5
DNS server(s): fc00::6 fc00::8
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0
Subnet: fe80::/10
Subnet name: bar
Direct: Inactive (This and other subnets match interface Ethernet1)
Relay: Active
Active leases: 0switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/24 (Subnet is disabled - overlapping subnet 10.0.0.0/8)
Range: 10.0.0.1 to 10.0.0.10
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0
Subnet: 10.0.0.0/8 (Subnet is disabled - overlapping subnet 10.0.0.0/24)
DNS server(s):
Default gateway address: 10.0.0.3
Active leases: 0switch# show dhcp server
IPv4 DHCP Server is active
DNS server(s): 10.2.2.2
Lease duration: 1 days 0 hours 0 minutes
Active Leases: 0
IPv4 DHCP interface status:
Interface Status
-------------------------------------------------
Ethernet1 Active
Subnet: 10.0.0.0/8 (Subnet is disabled - range 10.0.0.9-10.0.0.12 overlaps with an existing pool)
Range: 10.0.0.1 to 10.0.0.10
Range: 10.0.0.9 to 10.0.0.12
DNS server(s): 10.3.3.3 10.4.4.4
Default gateway address: 10.0.0.4
Active leases: 0Subnet: 10.0.0.0/8 (Subnet is disabled - ipv4-address 10.0.0.11 is reserved more than once)
Subnet name:
DNS server(s):
Default gateway address: 10.0.0.3
Active leases: 0
Reservations:
MAC address: 1a1b.1c1d.1e1f
IPv4 address: 10.0.0.11
MAC address: 2a2b.2c2d.2e2f
IPv4 address: 10.0.0.11switch# show dhcp server leases
10.0.0.10
End: 2019/06/20 17:44:34 UTC
Last transaction: 2019/06/19 17:44:34 UTC
MAC address: 5692.4c67.460a
2000:0:0:40::b
End: 2019/06/20 18:06:33 UTC
Last transaction: 2019/06/20 14:36:33 UTC
MAC address: 165a.a86d.ffacUse the show dhcp server leases command to display DHCP server lease information.
Command Mode
EXEC
Command Syntax
show dhcp server leases [ipv4 | ipv6]
Example
switch# show dhcp server leases
10.0.0.10
End: 2019/06/20 17:44:34 UTC
Last transaction: 2019/06/19 17:44:34 UTC
MAC address: 5692.4c67.460a
2000:0:0:40::b
End: 2019/06/20 18:06:33 UTC
Last transaction: 2019/06/20 14:36:33 UTC
MAC address: 165a.a86d.ffacThe show ip dhcp relay command displays the DHCP relay agent configuration status on the switch.
Command Mode
EXEC
Command Syntax
show ip dhcp relay
Example
switch> show ip dhcp relay
DHCP Relay is active
DHCP Relay Option (82)is enabled
DHCP Relay vendor-specific suboption (9) under information option (82)
DHCP Smart Relay is enabled
Interface: Vlan100
DHCP Smart Relay is disabled
DHCP servers: 10.4.4.4
switch>The show ip dhcp relay counters command displays the number of DHCP packets received, forwarded, or dropped on the switch and on all interfaces enabled as DHCP relay agents.
Command Mode
EXEC
Command Syntax
show ip dhcp relay counters
Example
switch> show ip dhcp relay counters
| Dhcp Packets |
Interface | Rcvd Fwdd Drop | Last Cleared
----------|----- ---- -----|---------------------
All Req | 376 376 0 | 4 days, 19:55:12 ago
All Resp | 277 277 0 |
| |
Vlan1000 | 0 0 0 | 4 days, 19:54:24 ago
Vlan1036 | 376 277 0 | 4 days, 19:54:24 ago
switch>The show ip dhcp snooping command displays the DHCP snooping configuration.
Command Mode
EXEC
Command Syntax
show ip dhcp snooping
Example
switch> show ip dhcp snooping
DHCP Snooping is enabled
DHCP Snooping is operational
DHCP Snooping is configured on following VLANs:
100
DHCP Snooping is operational on following VLANs:
100
Insertion of Option-82 is enabled
Circuit-id format: Interface name:Vlan ID
Remote-id: 00:1c:73:1f:b4:38 (Switch MAC)
switch>The show ip dhcp snooping counters command displays counters that track the quantity of DHCP request and reply packets received by the switch. The output displays data for each VLAN or aggregated for all VLANs with counters for packets dropped.
Command Mode
EXEC
Command Syntax
show ip dhcp snooping counters [counter_typedebug]
Parameters
switch> show ip dhcp snooping counters
| Dhcp Request Pkts | Dhcp Reply Pkts |
Vlan | Rcvd Fwdd Drop | Rcvd Fwdd Drop | Last Cleared
-----|------ ----- ------|----- ---- ------|-------------
100 | 0 0 0 | 0 0 0 | 0:35:39 ago
switch>switch> show ip dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 0 0
Forwarded 0 0
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Info Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 3:37:18 ago
switch>The show ip dhcp snooping hardware command displays internal hardware DHCP snooping status on the switch.
Command Mode
EXEC
Command Syntax
show ip dhcp snooping hardware
Example
switch> show ip dhcp snooping hardware
DHCP Snooping is enabled
DHCP Snooping is enabled on following VLANs:
None
Vlans enabled per Slice
Slice: FixedSystem
None
switch>The show ipv6 dhcp relay counters command displays the number of DHCP packets received, forwarded, or dropped on the switch and on all interfaces enabled as DHCP relay agents.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp relay counters
Example
switch> show ipv6 dhcp relay counters

          |  Dhcp Packets  |
Interface | Rcvd Fwdd Drop |         Last Cleared
----------|----- ---- -----|---------------------
  All Req |  376  376    0 | 4 days, 19:55:12 ago
 All Resp |  277  277    0 |
          |                |
Ethernet4 |  207  148    0 | 4 days, 19:54:24 ago

switch> The show ipv6 dhcp snooping command displays information about the DHCP snooping configuration.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping
Example
switch# show ipv6 dhcp snooping
DHCPv6 Snooping is enabled
DHCPv6 Snooping is operational
DHCPv6 Snooping is configured on following VLANs:
  2789-2790
DHCPv6 Snooping is operational on following VLANs:
  2789
Insertion of Option-37 is enabledThe show ipv6 dhcp snooping counters command displays counters that track the quantity of DHCP request and reply packets that the switch receives. Data is either presented for each VLAN or aggregated for all VLANs with counters for packets dropped.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping counters [COUNTER_TYPE]
switch# show ipv6 dhcp snooping counters

     | Dhcpv6 Request Pkts | Dhcpv6 Reply Pkts |
Vlan |  Rcvd   Fwdd   Drop |  Rcvd  Fwdd  Drop | Last Cleared
-----|------ ------ -------|------ ----- ------|-------------
2789 | 1 1 0 | 1 1 0 | 0:03:09 agoswitch# show ipv6 dhcp snooping counters debug
Counter Snooping to Relay Relay to Snooping
----------------------------- ----------------- -----------------
Received 1 1
Forwarded 1 1
Dropped - Invalid VlanId 0 0
Dropped - Parse error 0 0
Dropped - Invalid Dhcp Optype 0 0
Dropped - Invalid Remote-ID Option 0 0
Dropped - Snooping disabled 0 0
Last Cleared: 0:04:29 agoThe show ipv6 dhcp snooping hardware command displays internal hardware DHCP snooping status on the switch.
Command Mode
EXEC
Command Syntax
show ipv6 dhcp snooping hardware
Example
switch# show ipv6 dhcp snooping hardware
DHCPv6 Snooping is enabled
DHCPv6 Snooping is enabled on following VLANs:
    2789
    Vlans enabled per Slice
        Slice:  Linecard0-0
        2789
        Slice:  Linecard0-1
        2789
        Slice:  Linecard0-2
        2789
        Slice:  Linecard0-3
2789A virtual IP (VIP) address is an IP address that does not directly connect to a specific interface. Inbound packets sent to a Virtual IP address are redirected to a physical network interface. VIPs support connection redundancy by assigning the address to multiple switches. If one device becomes unavailable, packets sent to the address are still serviced by the functioning device.
A virtual router, also known as a virtual router group, is defined by a Virtual Router Identifier (VRID) and a virtual IP address. A virtual routers mapping of VRID and IP address must be consistent among all switches implementing the virtual router group. A virtual routers scope is restricted to a single LAN.
A LAN may contain multiple virtual routers for distributing traffic. Each virtual router on a LAN is assigned a unique VRID. A switch may be configured with virtual routers among multiple LANs.
VRRP uses priority ratings to assign Master or Backup roles for each VRRP router configured for a virtual router group. The Master router sends periodic VRRP Advertisement messages along the LAN and forwards packets received by the virtual router to their destination. Backup routers are inactive but are available to assume Master router duties when the current Master fails.
A VRRP can be configured to allow VRRP routers with higher priority to take over Master router duties. Alternatively, the group can be configured to prevent a router from preemptively assuming the Master role. A VRRP router is always assigned the Master of any virtual router configured with the address owned by the VRRP router, regardless of the preemption prevention setting.
On 7280R3, 7500R3 and 7800R3 series, maximally 14 unique VRRP groups can be configured along with VARP and MLAG Peer gateway virtual MAC capabilities.
RFC 5798 defines version 3 of the Virtual Router Redundancy Protocol (VRRP) for both IPv4 and IPv6. It is based on version 2 of VRRP, as defined in RFC 3768.
Virtual VRRP (VARP) allows multiple switches to simultaneously route packets from a common IP address in an active-active router configuration. Each switch is configured with the same set of virtual IP addresses on corresponding VLAN interfaces and a common virtual MAC address. In MLAG configurations, VARP is preferred over VRRP because VARP does not require traffic to traverse the peer-link to the master router as VRRP would.
A maximum of 500 virtual IP addresses can be assigned to a VLAN interface. All virtual addresses on all VLAN interfaces resolve to the same virtual MAC address.
VARP functions by having each switch respond to ARP and GARP requests for the configured router IP address with the virtual MAC address. The virtual MAC address is only for inbound packets and never used in the source field of outbound packets.
To implement a virtual router, it must be configured and enabled. A virtual router is typically configured before it is enabled; this ensures that the VRRP router operates as required before its priority settings immediately make it the master virtual router. Because assigning a primary address to a virtual router enables it, address assignment is normally performed after all other configuration tasks.
The no vrrp command removes all VRRP commands for the specified virtual router from running-config.
The vrrp ipv4 version command sets the version of VRRP for the corresponding IPv4 virtual router. IPv6 version is not configurable as it only supports version 3. The version selected in a VRRP group can either be same for all group members or independent of each other. By default, Arista switches use VRRP version 2, which supports only IPv4 environments. VRRP version 3 supports both IPv4 and IPv6 environments.
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 1 ipv4 version 3
switch(config-if-vl20)#The VRRP routers within a virtual router group determine the Master router through priority settings. Priority values range from 254 (highest priority) to 1 (lowest priority). Priority is either set by a CLI command or is assigned the default value of 100. A switch specifies priority settings for each of its virtual routers. Once set, VRRP priority level can also be changed by a tracked object. The vrrp tracked-object command configures the VRRP client process to track an object created by the track command and react if its status changes to down.
Preemption mode determines when a VRRP router with a higher priority rating becomes the Master router. If preemption is enabled, the VRRP router with the highest priority immediately becomes the Master router. If preemption is disabled, a VRRP router with a higher priority value does not become the Master router unless the current Master becomes unavailable; this is applicable when a new VRRP router becomes available on the LAN or VRRP routers priority value changes for the virtual router.
The vrrp priority-level command configures the switchs priority setting for the specified virtual router.
Example
switch(config-if-vl20)# vrrp 15 priority-level 250
switch(config-if-vl20)#The vrrp preempt command controls the preempt mode setting of the specified virtual router. By default, preempt mode is enabled.
Examples
switch(config-if-vl20)# no vrrp 15 preempt
switch(config-if-vl20)#switch(config-if-vl20)#vrrp 30 preempt
switch(config-if-vl20)#The vrrp preempt delay command configures a period between an event that elevates a switch to master VRRP router status and the switch's assumption of master VRRP router role. Command options configure delays during normal operation and after a switch reboot.
The Master router sends periodic VRRP Advertisement messages to other VRRP routers. The vrrp advertisement interval command specifies the interval between successive advertisement message transmissions.
The advertisement interval also defines the timeout that determines when the switch assumes the Master router role. This timeout interval is three times the advertisement interval.
Example
switch(config-if-vl100)# vrrp 35 advertisement interval 10
switch(config-if-vl100)#The vrrp session description command associates a text string to the specified virtual router. The maximum string length is 80 characters. The string has no functional impact on the virtual router.
Example
switch(config-if-vl20)# vrrp 15 session description Laboratory Router
switch(config-if-vl20)#VRRP peer authentication validates VRRP advertisement packets that the switch receives from other VRRP routers in a specified virtual router group. When a virtual router uses authentication, all VRRP routers in the group must use the same authentication parameters.
The vrrp peer authentication command configures virtual router authentication parameters for the specified virtual router.
Example
switch(config-if-vl100)#vrrp 40 peer authentication text 12345
switch(config-if-vl100)#The vrrp ipv4 secondary command assigns a secondary IP address to a virtual router. Secondary addresses are optional; a virtual routers configuration may include more than one secondary address command. The primary and secondary address list must be identical for all switches in a virtual router group.
A primary IP address is assigned to a virtual router with the vrrp ipv4 command (Virtual Router Enabling and the Primary IP address).
Example
switch(config-if-vl20)# vrrp 15 ipv4 10.2.4.5 secondary
switch(config-if-vl20)#The vrrp ipv4 command configures the primary IP address of the specified virtual router and enables the virtual router if the primary address is contained within the configuration mode interfaces IP address subnet. A virtual routers configuration may contain only one primary IP address assignment command; subsequent vrrp ipv4 commands reassign the virtual routers primary IP address.
Example
switch(config-if-vl20)# vrrp 15 ipv4 10.1.1.5
switch(config-if-vl20)#The vrrp disabled command places the switch in stopped state for the specified virtual router. While in stopped state, the switch cannot act as a Master or backup router for the virtual router group. The no vrrp disabled command changes the switchs virtual router state to backup or master if the virtual router is properly configured.
switch(config-if-vl20)# vrrp 24 disabled
switch(config-if-vl20)#switch(config-if-vl20)# no vrrp 24 disabled
switch(config-if-vl20)#switch(config-if-vl20)# vrrp 24 tracked-object interfaceE6/48 shutdown
switch(config-if-vl20)#The no vrrp and no vrrp ipv4 commands delete the specified virtual IP address from the interface. Additionally, the no vrrp command removes all residual VRRP commands for the virtual router.
switch(config-if-vl15)# no vrrp 10
switch(config-if-vl15)#switch(config-if-vl20)# no vrrp 25 ipv4 10.1.1.5
switch(config-if-vl20)#To implement a virtual router, it must be configured and enabled. A virtual router is typically configured before it is enabled; this ensures that the VRRP router operates as required before its priority settings immediately make it the master virtual router. Because assigning a primary address to a virtual router enables it, address assignment is normally performed after all other configuration tasks.
The no vrrp command removes all VRRP commands for the specified virtual router from running-config.
The vrrp ipv4 version command sets the version of VRRP used on an interface. The version selected in a VRRP group must be the same for all group members. By default, Arista switches use VRRP version 2, which is not compatible with IPv6.
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 1 ipv4 version 3
switch(config-if-vl20)#The vrrp ipv6 command assigns an IPv6 address to the interface being configured and creates a VRRP group.
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 3 ipv6 2001:db8:0:1::1
switch(config-if-vl20)#The vrrp tracked-object command configures the VRRP client process to track an object created by the track command and react if its status changes to down.
Example
switch(config-if-vl20)# vrrp 1 tracked-object ETH8 shutdown
switch(config-if-vl20)#The vrrp priority-level command configures the switchs priority setting for the specified virtual router.
Example
switch(config-if-vl20)# vrrp 15 priority-level 250
switch(config-if-vl20)#Preemption mode determines when a VRRP router with a higher priority rating becomes the Master router. If preemption is enabled, the VRRP router with the highest priority immediately becomes the Master router. If preemption is disabled, a VRRP router with a higher priority value does not become the Master router unless the current Master becomes unavailable; this is applicable when a new VRRP router becomes available on the LAN or VRRP routers priority value changes for the virtual router.
The vrrp preempt command controls the preempt mode setting of the specified virtual router. By default, preempt mode is enabled.
Example
switch(config-if-vl20)# vrrp 30 preemptThe ip virtual-router mac-address advertisement-interval command specifies the interval between advertisement packets sent by the master router to the VRRP group members.
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# ip virtual-router mac-address advertisement-interval 60
switch(config-if-vl20)#Use the following commands to display the VRRP configurations and status.
The show vrrp command displays information about the Virtual Router Redundancy Protocol (VRRP) groups configured on a specified interface.
Example
switch# show vrrp interface vlan 3060 brief
Interface Id Ver Pri Time State VrIps
Vlan3060 1 3 100 3609 Master 2001::2
2001::3
Vlan3060 2 3 100 3609 Master 2002::2
2002::3
switch#Implementing VARP consists of assigning virtual IP addresses to VLAN interfaces and configuring a virtual MAC address.
The ip virtual-router address command assigns a virtual IP address to the VLAN interface being configured. Unlike VRRP, the virtual IP address does not have to be in the same subnet as the physical interface.
A virtual IPv4 address may optionally be configured with a subnet, but doing so modifies the behavior of ARP requests sent from the router. When the router sends an ARP request for an IPv4 address in a virtual subnet, the ARP request uses the virtual IPv4 address as the source IP address and the virtual MAC address as the source MAC address inside the ARP header. For virtual IP addresses configured without the subnet option, no modifications are made to outgoing ARP requests.
switch(config)# interface vlan 10
switch(config-if-Vl10)# ip address 10.0.0.2/24
switch(config-if-Vl10)# ip virtual-router address 10.0.0.6
switch(config-if-Vl10)# ipv6 address 2001::1/64
switch(config-if-Vl10)# ipv6 virtual-router address 2001::2
switch(config-if-Vl10)# exit
switch(config)#switch(config)# ip route 192.0.0.0/24 vlan 10
switch(config)# interface vlan 10
switch(config-if-Vl10)# ip address 10.0.0.2/24
switch(config-if-Vl10)# ip virtual-router address 192.0.0.6/24
switch(config-if-Vl10)# exit
switch(config)#The ip virtual-router mac-address command assigns a virtual MAC address to the switch. The switch maps all virtual router IP addresses to this MAC address. The address is receive-only; the switch never sends packets with this address as the source.
When the destination MAC of a packet destined to a remote network matches the virtual MAC address, the MLAG peer forwards the traffic to the next hop destination. Each MLAG peer must have the same routes available, either through static configuration or learned through a dynamic routing protocol.
Example
switch(config)# ip virtual-router mac-address 001c.7300.0099
switch(config)#To display the virtual router MAC and IP addresses, enter the show ip virtual-router command.
Example
switch# show ip virtual-router
IP virtual router is configured with MAC address: 24cd.5a29.cc31
Interface IP Address Virtual IP Address Status Protocol
Vlan15 10.1.1.3/24 10.1.1.15 up up
Vlan15 10.1.1.3/24 10.1.1.16 up up
Vlan15 10.1.1.3/24 10.1.1.17 up up
Vlan20 10.12.1.6/24 10.1.1.51 up up
Vlan20 10.12.1.6/24 10.1.1.53 up up
Vlan20 10.12.1.6/24 10.1.1.55 up up
switch#The show ipv6 virtual-router command displays the virtual MAC address assigned to the switch and all virtual IPv6 addresses assigned to each VLAN interface.
Example
switch# show ipv6 virtual-router
IP virtual router is configured with MAC address: 001c.7300.0099
MAC address advertisement interval: 30 seconds
Interface Vlan4094
State is up
Protocol is up
IPv6 address
2001:b8:2001::1011/64
Virtual IPv6 address
2001:db8:ac10:fe01::
switch#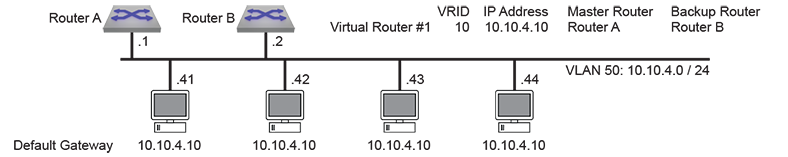
The following code configures the first switch (Router A) as the master router and the second switch (Router B) as a backup router for virtual router 10 on vlan 50. Router A becomes the Master virtual router by setting its priority at 200; Router B maintains the default priority of 100. The advertisement interval is three seconds on both switches. Priority preemption is enabled by default.
switch-A(config)# interface vlan 50
switch-A(config-if-vl50)# ip address 10.10.4.1/24
switch-A(config-if-vl50)# no vrrp 10
switch-A(config-if-vl50)# vrrp 10 priority 200
switch-A(config-if-vl50)# vrrp 10 advertisement interval 3
switch-A(config-if-vl50)# vrrp 10 ip 10.10.4.10
switch-A(config-if-vl50)# exitswitch-B(config)# interface vlan 50
switch-B(config-if-vl50)# ip address 10.10.4.2/24
switch-B(config-if-vl50)# no vrrp 10
switch-B(config-if-vl50)# vrrp 10 advertisement interval 3
switch-B(config-if-vl50)# vrrp 10 ip 10.10.4.10
switch-B(config-if-vl50)# exit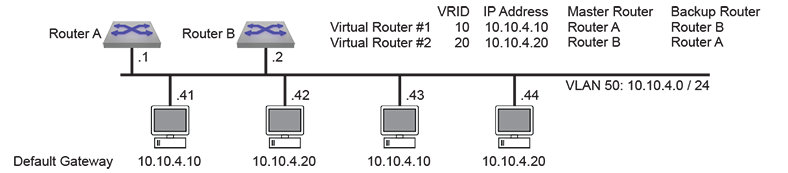
switch-A(config)# interface vlan 50
switch-A(config-if-vl50)# ip address 10.10.4.1/24
switch-A(config-if-vl50)# no vrrp 10
switch-A(config-if-vl50)# vrrp 10 priority 200
switch-A(config-if-vl50)# vrrp 10 advertisement interval 3
switch-A(config-if-vl50)# vrrp 10 ip 10.10.4.10
switch-A(config-if-vl50)# no vrrp 20
switch-A(config-if-vl50)# vrrp 20 advertisement interval 5
switch-A(config-if-vl50)# vrrp 20 ip 10.10.4.20
switch-A(config-if-vl50)# exitswitch-B(config)# interface vlan 50
switch-B(config-if-vl50)# ip address 10.10.4.2/24
switch-B(config-if-vl50)# no vrrp 10
switch-B(config-if-vl50)# vrrp 10 advertisement interval 3
switch-B(config-if-vl50)# vrrp 10 ip 10.10.4.10
switch-B(config-if-vl50)# no vrrp 20
switch-B(config-if-vl50)# vrrp 20 priority 200
switch-B(config-if-vl50)# vrrp 20 advertisement interval 5
switch-B(config-if-vl50)# vrrp 20 ip 10.10.4.20
switch-B(config-if-vl50)# exit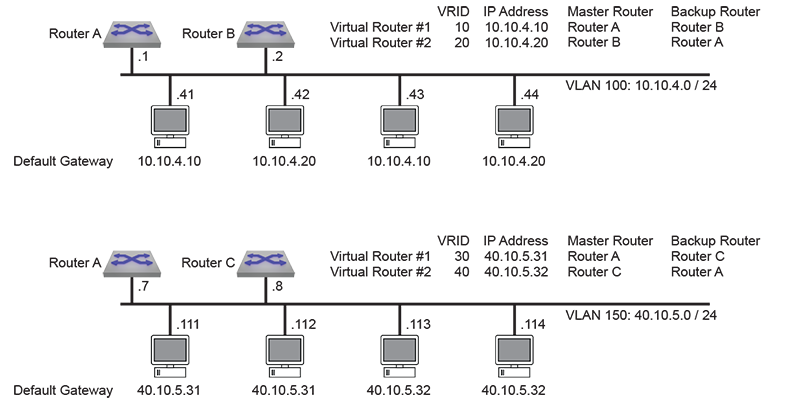
switch-A(config)# interface vlan 100
switch-A(config-if-vl100)# ip address 10.10.4.1/24
switch-A(config-if-vl100)# no vrrp 10
switch-A(config-if-vl100)# vrrp 10 priority 200
switch-A(config-if-vl100)# no vrrp 10 preempt
switch-A(config-if-vl100)# vrrp 10 ip 10.10.4.10
switch-A(config-if-vl100)# vrrp 10 advertisement interval 1
switch-A(config-if-vl100)# no vrrp 20
switch-A(config-if-vl100)# no vrrp 20 preempt
switch-A(config-if-vl100)# vrrp 20 ip 10.10.4.20
switch-A(config-if-vl100)# interface vlan 150
switch-A(config-if-vl150)# ip address 40.10.5.7/24
switch-A(config-if-vl150)# no vrrp 30
switch-A(config-if-vl150)# vrrp 30 priority 200
switch-A(config-if-vl150)# no vrrp 30 preempt
switch-A(config-if-vl150)# vrrp 30 ip 40.10.5.31
switch-A(config-if-vl100)# vrrp 30 advertisement interval 1
switch-A(config-if-vl150)# no vrrp 40
switch-A(config-if-vl150)# no vrrp 40 preempt
switch-A(config-if-vl150)# vrrp 40 ip 40.10.5.32
switch-A(config-if-vl150)# exitswitch-B(config)# interface vlan 100
switch-B(config-if-vl100)# ip address 10.10.4.2/24
switch-B(config-if-vl100)# no vrrp 10
switch-B(config-if-vl100)# no vrrp 10 preempt
switch-B(config-if-vl100)# vrrp 10 ip 10.10.4.10
switch-B(config-if-vl100)# no vrrp 20
switch-B(config-if-vl100)# vrrp 20 priority 200
switch-B(config-if-vl100)# no vrrp 20 preempt
switch-B(config-if-vl100)# vrrp 20 ip 10.10.4.20
switch-A(config-if-vl100)# vrrp 20 advertisement interval 1
switch-B(config-if-vl100)# exitswitch-C(config)# interface vlan 150
switch-C(config-if-vl150)# ip address 40.10.5.8/24
switch-C(config-if-vl150)# no vrrp 30
switch-C(config-if-vl150)# no vrrp 30 preempt
switch-C(config-if-vl150)# vrrp 30 ip 40.10.5.31
switch-C(config-if-vl150)# no vrrp 40
switch-C(config-if-vl150)# vrrp 40 priority 200
switch-C(config-if-vl150)# no vrrp 40 preempt
switch-C(config-if-vl150)# vrrp 40 ip 40.10.5.32
switch-A(config-if-vl100)# vrrp 40 advertisement interval 1
switch-C(config-if-vl150)# exitThis section provides code that implements a VARP configuration. The network diagram displays the Example 1 network. Two switches in an MLAG domain are configured as VARP routers.
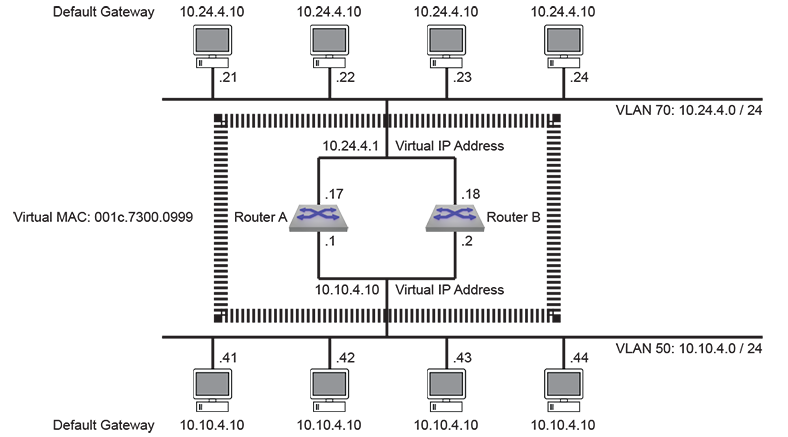
switch-A(config)# ip virtual-router mac-address 001c.7300.0999
switch-A(config)# interface vlan 50
switch-A(config-if-vl50)# ip address 10.10.4.1/24
switch-A(config-if-vl50)# ip virtual-router address 10.10.4.10
switch-A(config-if-vl50)# interface vlan 70
switch-A(config-if-vl70)# ip address 10.24.4.17/24
switch-A(config-if-vl70)# ip virtual-router address 10.24.4.1
switch-A(config-if-vl70)# exitswitch-B(config)# ip virtual-router mac-address 001c.7300.0999
switch-B(config)# interface vlan 50
switch-B(config-if-vl50)# ip address 10.10.4.2/24
switch-B(config-if-vl50)# ip virtual-router address 10.10.4.10
switch-B(config-if-vl50)# interface vlan 70
switch-B(config-if-vl70)# ip address 10.24.4.18/24
switch-B(config-if-vl70)# ip virtual-router address 10.24.4.1
switch-B(config-if-vl70)# exitThis section contains descriptions of CLI commands that support VRRP and VARP.
The ip fhrp accept-mode command configures the switch to permit SSH access to the VRRP Master and VARP Master router. All routers within a VRRP or VARP group should be configured consistently. By default, SSH access to the VRRP and VARP Master routers is not permitted.
The no ip fhrp accept-mode and default ip fhrp accept-mode commands restores the default SSH access availability by removing the ip fhrp accept-mode command from running-config.
Command Mode
Global Configuration
Command Syntax
ip fhrp accept-mode
no ip fhrp accept-mode
default ip fhrp accept-mode
Example
switch(config)# ip fhrp accept-mode
switch(config)# show running-config
!
ip fhrp accept-mode
!
switch(config)#The ip virtual-router address command assigns a virtual IPv4 address to the VLAN interface being configured. (To assign a virtual IPv6 address to a VLAN interface, use the ipv6 virtual-router address command.) Unlike VRRP, the virtual IP address does not have to be in the same subnet as the physical interface.
A virtual IP address may optionally be configured with a subnet, but doing so will modify the behavior of ARP requests sent from the router. When the router sends an ARP request for an IP address in a virtual subnet, the ARP request will use the virtual IP address as the source IP address and the virtual MAC address as the source MAC address inside the ARP header. For virtual IP addresses configured without the subnet option, no modifications are made to outgoing ARP requests.
A maximum of 500 virtual IP addresses can be assigned to a VLAN interface. All virtual addresses on all VLAN interfaces resolve to the same virtual MAC address configured through the ip virtual-router mac-address command.
This command is typically used in MLAG configurations to create identical virtual routers on switches connected to the MLAG domain through an MLAG.
The no ip virtual-router address and default ip virtual-router address commands remove the specified virtual IP address from the configuration mode interface by deleting the corresponding ip virtual-router address command from running-config. If the command does not specify an address, all virtual IPv4 addresses are removed from the interface.
Command Mode
Interface-VLAN Configuration
Command Syntax
ip virtual-router address ipv4_addr
no ip virtual-router address [ipv4_addr]
default ip virtual-router address [ipv4_addr]
Parameter
ipv4_addr IP address of router. Dotted decimal notation.
switch(config)# interface vlan 10
switch(config-if-Vl10)# ip address 10.0.0.2/24
switch(config-if-Vl10)# ip virtual-router address 10.0.0.6
switch(config-if-Vl10)# exitswitch(config)# ip route 192.0.0.0/24 vlan 10
switch(config)# interface vlan 10
switch(config-if-Vl10)# ip address 10.0.0.2/24
switch(config-if-Vl10)# ip virtual-router address 192.0.0.6/24
switch(config-if-Vl10)# exitThe ip virtual-router mac-address command assigns a virtual MAC address to the switch. The switch maps all virtual router IP addresses to this MAC address. The address is receive-only; the switch never sends packets with this address as the source. The virtual router is not configured on the switch until this virtual mac-address is assigned.
This command is typically used in MLAG configurations to create identical virtual routers on switches connected to the MLAG domain through an MLAG. When the destination MAC of a packet destined to a remote network matches the virtual MAC address, the MLAG peer forwards the traffic to the next hop destination. Each MLAG peer must have the same routes available, either through static configuration or learned through a dynamic routing protocol.
The no ip virtual-router mac-address command removes a virtual MAC address from the interface by deleting the corresponding ip virtual-router mac-address command from running-config.
Command Mode
Global Configuration
Command Syntax
ip virtual-router mac-address [mac_addr]
no ip virtual-router mac address [mac_addr]
Parameter
mac_addr MAC IP address (dotted hex notation). Select an address does not appear on the switch.
Example
switch(config)# ip virtual-router mac-address 001c.7300.0099
switch(config)#The ip virtual-router mac-address advertisement interval command specifies the period between the transmission of consecutive gratuitous ARP requests that contain the virtual router mac address for each virtual-router IP address configured on the switch. The default period is 30 seconds.
The no ip virtual-router mac-address advertisement-interval command restores the default period of 30 seconds by removing the ip virtual-router mac-address advertisement-interval command from running-config.
Command Mode
Global Configuration
Command Syntax
ip virtual-router mac-address advertisement-interval period
no ip virtual-router mac-address advertisement-interval
default ip virtual-router mac-address advertisement-interval
Parameter
period advertisement interval (seconds). Values range from 0 to 86400. Default is 30.
Example
switch(config)# ip virtual-router mac-address advertisement-interval 60
switch(config)#The ipv6 virtual-router address command assigns a virtual IPv6 address to the VLAN interface being configured. (To assign a virtual IPv4 address to a VLAN interface, use the ip virtual-router address command.) Unlike VRRP, the virtual IP address does not have to be in the same subnet as the physical interface.
A maximum of 500 virtual IP addresses can be assigned to a VLAN interface. All virtual addresses on all VLAN interfaces resolve to the same virtual MAC address configured through the ip virtual-router mac-address command.
This command is typically used in MLAG configurations to create identical virtual routers on switches connected to the MLAG domain through an MLAG.
The no ipv6 virtual-router address and default ipv6 virtual-router address commands remove the specified virtual IPv6 address from the configuration mode interface by deleting the corresponding ipv6 virtual-router address command from running-config. If the command does not specify an address, all virtual IPv6 addresses are removed from the interface.
Command Mode
Interface-VLAN Configuration
Command Syntax
ipv6 virtual-router address net_addr
no ipv6 virtual-router address [net_addr]
default ipv6 virtual-router address [net_addr]
Parameter
net_addr network IPv6 address.
Example
switch(config)# interface vlan 10
switch(config-if-Vl10)# ipv6 address 2001:0DB8:0:1::1/64
switch(config-if-Vl10)# ipv6 virtual-router address 2001:0DB8:0:1::2
switch(config-if-Vl10)# exitThe no vrrp command removes all VRRP configuration commands for the specified virtual router on the configuration mode interface. The default vrrp command also reverts VRRP configuration parameters to default settings by removing the corresponding vrrp commands.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
no vrrp group
default vrrp group
Parameter
group Virtual Router Identifier (VRID). Values range from 1 to 255.
Example
switch(config)# interface vlan 15
switch(config-if-vl15)# no vrrp 10
switch(config-if-vl15)#The show ip virtual-router command displays the virtual MAC address assigned to the switch and all virtual IP addresses assigned to each VLAN interface.
Command Mode
EXEC
Command Syntax
show ip virtual-router
switch# show ip virtual-router
IP virtual router is configured with MAC address: 24cd.5a29.cc31
Interface IP Address Virtual IP Address Status Protocol
Vlan15 10.1.1.3/24 10.1.1.15 up up
Vlan15 10.1.1.3/24 10.1.1.16 up up
Vlan15 10.1.1.3/24 10.1.1.17 up up
Vlan20 10.12.1.6/24 10.1.1.51 up up
Vlan20 10.12.1.6/24 10.1.1.53 up up
Vlan20 10.12.1.6/24 10.1.1.55 up up
switch#switch# show ip virtual-router
IP virtual router is not configured
switch#The show ipv6 virtual-router command displays the virtual MAC address assigned to the switch and all virtual IPv6 addresses assigned to each VLAN interface.
Command Mode
EXEC
Command Syntax
show ipv6 virtual-router
Example
switch# show ipv6 virtual-router
IP virtual router is configured with MAC address: 001c.7300.0099
MAC address advertisement interval: 30 seconds
Interface Vlan4094
State is up
Protocol is up
IPv6 address
2001:b8:2001::1011/64
Virtual IPv6 address
2001:db8:ac10:fe01::
switch#The show vrrp command displays information about the Virtual Router Redundancy Protocol (VRRP) groups configured on a specified interface. Parameter options control the amount and formatting of the displayed information.
Command Mode
Privileged EXEC
Command Syntax
show vrrp [INFO_LEVEL] [STATES]
show vrrp INTF GROUP_NUM [INFO_LEVEL] [STATES]
show vrrp GROUP_NUM INTF_GROUP [INFO_LEVEL] [STATES]
switch# show vrrp brief
Interface Id Ver Pri Time State VrIps
Vlan1006 3 2 100 3609 Master 127.38.10.2
Vlan1006 4 3 100 3609 Master 127.38.10.10
Vlan1010 1 2 100 3609 Master 128.44.5.3
Vlan1014 2 2 100 3609 Master 127.16.14.2switch# show vrrp interface vlan 1006 all
Vlan1010 - Group 1
VRRP Version 2
State is Stopped
Virtual IPv4 address is 128.44.5.3
Virtual MAC address is 0000.5e00.0101
Mac Address Advertisement interval is 30s
VRRP Advertisement interval is 1s
Preemption is enabled
Preemption delay is 0s
Preemption reload delay is 0s
Priority is 100
Master Router is 0.0.0.0
Master Advertisement interval is 1s
Skew time is 0.609s
Master Down interval is 3.609sswitch# show vrrp interface vlan 1014 group 2
Vlan1006 - Group 2
VRRP Version 2
State is Master
Virtual IPv4 address is 127.38.10.2
Virtual MAC address is 0000.5e00.0103
Mac Address Advertisement interval is 30s
VRRP Advertisement interval is 1s
Preemption is enabled
Preemption delay is 0s
Preemption reload delay is 0s
Priority is 100
Master Router is 127.38.10.1 (local), priority is 100
Master Advertisement interval is 1s
Skew time is 0.609s
Master Down interval is 3.609sThe vrrp advertisement interval command configures the interval between successive advertisement messages that the switch sends to VRRP routers in the specified virtual router group. The switch must be the groups Master virtual router to send advertisement messages. The advertisement interval must be configured identically on all physical routers in the virtual router group.
The advertisement interval also influences the timeout interval that defines when the virtual router becomes the master virtual router. When preemption is enabled, the virtual router becomes the master when three times the advertisement interval elapses after the switch detects master router priority conditions.
The no vrrp advertisement interval and default vrrp advertisement interval commands restore the default advertisement interval of one second for the specified virtual router by removing the corresponding vrrp advertisement interval command from running-config. The no vrrp command also removes the vrrp advertisement interval command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group advertisement interval adv_time
no vrrp group advertisement interval
default vrrp group advertisement interval
Example
switch(config)# interface vlan 100
switch(config-if-vl100)# vrrp 35 advertisement interval 5
switch(config-if-vl100)#The vrrp disabled command places the switch in stopped state for the specified virtual router. While in stopped state, the switch cannot act as a master or backup router for the virtual router group.
The no vrrp disabled and default vrrp disabled commands remove the corresponding vrrp disabled command from running-config. This changes the switch's virtual router state to backup or master if the virtual router is properly configured.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group disabled
no vrrp group disabled
default vrrp group disabled
Parameter
group Virtual Router IDentifier (VRID). Values range from 1 to 255.
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 24 disabled
switch(config-if-vl20)#switch(config-if-vl20)# no vrrp 24 disabled
switch(config-if-vl20)#The vrrp ipv4 command configures the primary IP address for the specified VRRP virtual router. The command also activates the virtual router if the primary address is contained in the interfaces subnet. A VRRP virtual routers configuration may contain only one primary IP address assignment command; subsequent vrrp ipv4 commands replace the existing primary address assignment.
The vrrp ipv4 secondary command assigns a secondary IP address to the VRRP virtual router.
The no vrrp ipv4and default vrrp ipv4 commands disable the VRRP virtual router and deletes the primary IP address by removing the corresponding vrrp ipv4 statement from running-config. The no vrrp command also removes the vrrp ipv4 command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group ipv4 ipv4_address
no vrrp group ipv4 ipv4_address
default vrrp group ipv4 ipv4_address
Related Command
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 15 ipv4 10.1.1.5
switch(config-if-vl20)#This command excludes the pseudo-header in IPv4 VRRPv3 checksum calculation on the VRRP group on the configuration mode interface of the switch and supports IPv4 VRRPv3 interoperability.
The no form of the command deletes the vrrp ipv4 checksum pseudo-header exclude configuration from the Ethernet interface on the switch.
The exit command returns the switch to global configuration mode.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group ipv4 checksum pseudo-header exclude
no vrrp group ipv4 checksum pseudo-header exclude
Parameter
group Virtual Router IDentifier (VRID). Values range from 1 to 255.
Example
switch(config-if-Et1)# vrrp 1 ipv4 checksum pseudo-header excludeThe vrrp ipv4 secondary command assigns a secondary IP address to the specified virtual router. Secondary IP addresses are an optional virtual router parameter. A virtual router may contain multiple secondary address commands. The IP address list must be identical for all VRRP routers in a virtual router group.
The virtual router is assigned a primary IP address with the vrrp ipv4 command.
The no vrrp ipv4 secondary and default vrrp ipv4 secondary commands remove the secondary IP address for the specified VRRP virtual router by deleting the corresponding vrrp ipv4 secondary statement from running-config. The no vrrp command also removes all vrrp ipv4 secondary commands for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group ipv4 ipv4_addr secondary
no vrrp group ipv4 ipv4_addr secondary
default vrrp group ipv4 ipv4_addr secondary
Related Command
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 15 ipv4 10.2.4.5 secondary
switch(config-if-vl20)#The vrrp ipv4 version command enables VRRP on the configuration mode interface and configures the VRRP version for the specified VRRP virtual router.
The no vrrp ipv4 version and default vrrp ipv4 version commands restore the default VRRP version to VRRPv2 by removing the corresponding vrrp ipv4 version statement from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group ipv4 version VERSION_NUMBER
no vrrp group ipv4 version
default vrrp group ipv4 version
switch(config)# interface ethernet 3
switch#(config-if-Et3)# vrrp 1 ipv4 version 3switch(config)# interface ethernet 3
switch(config-if-Et3)# no vrrp 1 ipv4 versionThe vrrp ipv6 command configures the IPv6 address for the specified VRRP virtual router. The command also activates the virtual router if the primary address is contained in the interfaces subnet.
The no vrrp ipv6 and default vrrp ipv6 commands disable the VRRP virtual router and deletes the IPv6 address by removing the corresponding vrrp ipv6 statement from running-config. The no vrrp command also removes the vrrp ipv6 command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group ip ipv6_address
no vrrp group ip ipv6_address
default vrrp group ip ipv6_address
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 3 ipv6 2001:db8:0:1::1
switch(config-if-vl20)#switch(config)# interface vlan 20
switch(config-if-vl20)# no vrrp 3 ipv6 2001:db8:0:1::1
switch(config-if-vl20)#The vrrp mac-address advertisement-interval command specifies the interval between advertisement packets sent by the master router to the VRRP group members.
The vrrp mac-address advertisement-interval 0, no vrrp mac-address advertisement-interval and default vrrp mac-address advertisement-interval commands disable the feature by removing the vrrp mac-address advertisement-interval command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group mac-address advertisement-interval period
no vrrp group mac-address
default vrrp group mac-address
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 3 mac-address advertisement-interval 60
switch(config-if-vl20)#switch(config)# interface vlan 20
switch(config-if-vl20)# no vrrp 3 mac-address advertisement-interval
switch(config-if-vl20)#The vrrp peer authentication command configures parameters the switch uses to authenticate virtual router packets it receives from other VRRP routers in the group.
The no vrrp peer authentication and default vrrp peer authentication commands disable VRRP peer authentication of packets from the specified virtual router by removing the corresponding vrrp peer authentication command from running-config . The no vrrp command also removes the vrrp peer authentication command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group peer authentication AUTH_PARAMETER
no vrrp group peer authentication
default vrrp group peer authentication
Guidelines
This command is applicable to VRRPv2 which supports IPv4 addresses only.
switch(config)# interface vlan 100
switch(config-if-vl100)# vrrp 40 peer authentication text 12345
switch(config-if-vl100)#switch(config-if-vl100)# vrrp 40 peer authentication ietf-md5 key-string 0 12345
switch(config-if-vl100)#switch(config-if-vl100)# vrrp 40 peer authentication ietf-md5 key-string 7
EA3TUPxdddFCLYT8mb+kxw==
switch(config-if-vl100)#The vrrp preempt command controls a virtual routers preempt mode setting. When preempt mode is enabled, if the switch has a higher priority it will preempt the current master virtual router. When preempt mode is disabled, the switch can become the master virtual router only when a master virtual router is not present on the subnet, regardless of VRRP priority level settings. By default, preempt mode is enabled.
The no vrrp preemptcand default vrrp preemptccommands disable preempt mode for the specified virtual router; the default vrrp preempt command stores a corresponding no vrrp preempt statement in running-config. The vrrp preempt command enables preempt mode by removing the corresponding no vrrp preempt statement from running-config.
The no vrrp command also enables preempt mode by removing the no vrrp preempt command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group preempt
no vrrp group preempt
default vrrp group preempt
Parameter
group Virtual Router IDentifier (VRID). Values range from 1 to 255.
Related Command
switch(config)# interface vlan 40
switch(config-if-vl40)# no vrrp 20 preempt
switch(config-if-vl40)#switch(config-if-vl40)# vrrp 20 preempt
switch(config-if-vl40)#The vrrp preempt delay command specifies the interval between a VRRP preemption event and the point when the switch becomes the master VRRP router. A preemption event is any event that results in the switch having the highest virtual router priority setting while preemption is enabled. The vrrp preempt command enables preemption for a specified virtual router.
Running-config maintains separate delay statements for minimum and reload parameters. Commands may list both parameters. Commands that list one parameter do not affect the omitted parameter. Values range from 0 to 3600 seconds (one hour). The default delay is zero seconds for both parameters.
The no vrrp preempt delay and default vrrp preempt delay commands reset the specified delay to the default of zero seconds. Commands that do no list either parameter resets both periods to zero. The no vrrp command also removes all vrrp preempt delay commands for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group preempt delay [MINIMUM_INTERVAL] [RELOAD_INTERVAL]
no vrrp group preempt delay [DELAY_TYPE]
default vrrp group preempt delay [DELAY_TYPE]
(DELAY_TYPE parameter is only used in no vrrp preempt delay and default vrrp preempt delay commands).
Related Command
switch(config)# interface vlan 40
switch(config-if-vl40)# vrrp 20 preempt delay minimum 90
switch(config-if-vl40)#switch(config-if-vl40)# no vrrp 20 preempt delay
switch(config-if-vl40)#The vrrp priority-level command configures the switchs priority setting for a VRRP virtual router. Priority values range from 1 to 254. The default value is 100.
The router with the highest VRRP priority level setting for a group becomes the master virtual router for that group. The master virtual router controls the IP address and is responsible for forwarding traffic sent. The vrrp preempt command controls the time when a switch can become the master virtual router.
The no vrrp priority-level and default vrrp priority-level commands restore the default priority of 100 to the virtual router on the configuration mode interface by removing the corresponding vrrp priority-level command from running-config. The no vrrp command also removes the vrrp priority-level command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group priority-level level
no vrrp group priority-level level
default vrrp group priority-level level
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 45 priority-level 250
switch(config-if-vl20)#The vrrp session description command associates a text string to a VRRP virtual router on the configuration mode interface. The string has no functional impact on the virtual router. The maximum length of the string is 80 characters.
The no vrrp session description and default vrrp session description commands remove the text string association from the VRRP virtual router by deleting the corresponding vrrp session description command from running-config. The no vrrp command also removes the vrrp session description command for the specified virtual router.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group session description label_text
no vrrp group session description
default vrrp group session description
Example
switch(config)# interface vlan 20
switch(config-if-vl20)# vrrp 15 session description Laboratory Router
switch(config-if-vl20)#The vrrp timers delay reload command delays the time for VRRP initialization after a system reboot.
The no vrrp timers delay reload and default vrrp timers delay reload commands restore the default value of 0 by deleting the vrrp timers delay reload statement from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group timers delay reload [INTERVAL]
no vrrp group timers delay reload
default vrrp group timers delay reload
Parameters
switch(config)# interface vlan 100
switch(config-if-Vl100)# vrrp 2 timers delay reload 900
switch(config-if-Vl100)#switch(config)# interface vlan 100
switch(config-if-Vl100)# no vrrp 2 timers delay reload
switch(config-if-Vl100)#The vrrp tracked-object command configures the VRRP client process on the configuration mode interface to track the specified tracked object and react when its status changes to down. The tracked object is created by the track command.
The no vrrp tracked-object and default vrrp tracked-object commands cause the VRRP client process to stop tracking the specified tracked object by removing the corresponding vrrp tracked-object command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
vrrp group tracked-object object_name ACTION amount
no vrrp group tracked-object object_name ACTION
default vrrp group tracked-object object_name ACTION
Example
switch(config-if-Et5)# vrrp 1 tracked-object eth8 shutdown
switch(config-if-Et5)#This feature supports per-interface ingress and egress packet and byte counters for IPv4 and IPv6.
This section describes Ingress and Egress per-port for IPv4 and IPv6 counters, including configuration instructions and command descriptions.
IPv4 and IPv6 ingress counters (count bridged and routed traffic, supported only on front-panel ports) can be enabled and disabled using the hardware counter feature ip in command:
[no] hardware counter feature ip inFor IPv4 and IPv6 ingress and egress counters that include only routed traffic (supported on Layer3 interfaces such as routed ports and L3 subinterfaces only), use the following commands:
[no] hardware counter feature ip in layer3[no] hardware counter feature ip out layer3Use the hardware counter feature ip command to enable ingress and egress counters at Layer 3. The no and default forms of the command disables the feature. The feature is enabled by default.
Command Mode
Configuration mode
Command Syntax
hardware counter feature ip in|out layer3
no hardware counter feature ip in|out layer3
default hardware counter feature in|out layer3
Example
switch(config)# hardware counter feature in layer3switch(config)# hardware counter feature out layer3Use the show interfaces counters ip command to display IPv4, IPv6 packets, and octets.
Example
switch# show interfaces counters ip
Interface IPv4InOctets IPv4InPkts IPv6InOctets IPv6InPkts
Et1/1 0 0 0 0
Et1/2 0 0 0 0
Et1/3 0 0 0 0
Et1/4 0 0 0 0
...
Interface IPv4OutOctets IPv4OutPkts IPv6OutOctets IPv6OutPkts
Et1/1 0 0 0 0
Et1/2 0 0 0 0
Et1/3 0 0 0 0
Et1/4 0 0 0 0
...You can also query the output from the show interfaces counters ip command through SNMP via the ARISTA-IP-MIB.
To clear the IPv4 or IPv6 counters, use the clear counters command.
switch# clear countersIPv4/IPv6 egress Layer 3 (hardware counter feature ip out layer3) counting on DCS-7280SR, DCS-7280CR, and DCS-7500-R platforms work based on ARP entry of the next hop. By default, IPv4's next-hop and IPv6's next-hop resolve to the same MAC address and interface that shared the ARP entry.
To differentiate the counters between IPv4 and IPv6, disable arp entry sharing with the following command:
ip hardware fib next-hop arp dedicatedThe switch uses rule-based lists to control packet access to ports and to select routes for redistribution to routing domains defined by dynamic routing protocols.
The following provides an introduction to Access Control Lists (ACL), Service ACLs, Route Maps, Prefix Lists, and Router Access Control List (RACL) Divergence:
The switch processes ACLs, Service ACLs, route maps, and prefix lists in order, beginning with the first rule and continuing until a match is found.
An ACL contains a list of rules that control the inbound and outbound flow of packets into Ethernet interfaces, subinterfaces, port-channel interfaces, or the switch control plane. The switch supports implementing various filtering criteria, including IP and MAC addresses and TCP/UDP ports, with include/exclude options without compromising its performance or feature set. Filtering syntax is the industry standard.
A Service ACL applies a control-plane process to control connections to, or packets processed by, the agent process.
A route map contains a list of rules that control the redistribution of IP routes into a protocol domain based on criteria such as route metrics, access control lists, next-hop addresses, and route tags. Additionally, route maps can modify route parameters during redistribution.
A prefix list contains a list of rules that defines route redistribution access for a specified IP address space. Route maps often use prefix lists to filter routes.
ACLs can also be made dynamic using payload, turning them into a User-Defined Field (UDF) alias for use in other ACLs.
An ACL is an ordered list of rules that defines access restrictions for the entities (the control plane or an interface) to which it is applied. Route maps also use ACLs to select routes for redistribution into specified routing domains.
ACL rules specify the data to which packet contents are compared when filtering data.
Upon its arrival at an interface, the switch compares a packet’s fields to the first rule of the ACL applied to the interface. Packets that match the rule are forwarded (permit rule) or dropped (deny rule). The process continues whereby the switch compares packets that do not match the rule to the next rule in the list and continues until the packet either matches a rule or the rule list is exhausted. The interface drops packets that do not match a rule.
The sequence number designates the rule's placement in the ACL.
The switch compares an ACL rule's command list to inbound and outbound packet fields. When all of a rule’s criteria match a packet’s contents, the interface performs the action specified by the rule.
The set of available commands depends on the ACL type and the specified protocol within the rule. The following is a list of commands available for supported ACL types:
Standard ACLs filter only on the source address.
Lists created in one mode cannot be modified in any other mode.
A sequence number determines a rule's position within a list. New rules are inserted into a list based on their sequence numbers. You can reference a rule's sequence number to delete it from a list.
ACL Configuration describes procedures for configuring ACLs.
Implement an Access Control List (ACL) by assigning the list to an Ethernet interface, subinterface, port channel interface, or control plane. The switch assigns a default ACL to the control plane unless the configuration contains a valid control-plane ACL assignment statement. Ethernet and port-channel interfaces are not assigned an ACL by default. Apply standard ACLs to interfaces in the same manner as other ACLs.
IPv4 and MAC ACLs are separately applied for inbound and outbound packets. An interface or subinterface can be assigned multiple ACLs, with a limit of one ACL per packet direction per ACL type. A subset of all available switches supports Egress ACLs. The control plane does not support egress ACLs.
Applying ACLs describes procedures for applying ACLs to interfaces or the control plane.
ACL rules provide a log option that produces a log message when a packet matches the rule. ACL logging creates a syslog entry when a packet matches an ACL rule where logging is enabled. Packets that match a logging-enabled ACL rule are copied to the CPU by the hardware. These packets trigger the creation of a syslog entry. The information provided in the entry depends on the ACL type or the protocol specified by the ACL. The system applies hardware rate limiting to packets written to the CPU, which prevents potential Denial-of-Service attacks. The logging rate is also limited in software to avoid creating syslog lists that are too large for human operators to use in practical ways.
ACL Rule Tracking Configuration describes procedures for configuring and enabling ACL logging.
The system assigns an ACL counter to each ACL rule. The activity of the ACL counters for rules within a list depends on the list’s counter state. When the list is in a counting state, the ACL counter of a rule increments when the rule matches a packet. When the list is in a non-counting state, the counter does not increment. A list’s counter state applies to all rules in the ACL. The default state for new ACLs is non-counting.
The system maintains the values of the counters for all rules in the list when an ACL changes from a counting state to a non-counting state or is no longer applied to any interfaces that increment counters. The counters do not reset. When the ACL returns to counting mode or is applied to an interface that increments counters, the counter operation continues from its last value.
Counters never decrement and are reset only through CLI commands.
ACL Rule Tracking Configuration describes procedures for configuring and enabling ACL counters.
Egress ACL counters count the number of packets matching rules associated with egress ACLs applied to various interfaces in a switch. 7050 and 7060 series switches maintain these counters for every TCAM rule. On these platforms, commands such as show platform trident tcam, show platform trident counters, and show ip access-list always display packet counters greater than zero.
Other switches do not enable counters by default. You must configure counters for each ACL. The show hardware counter and show ip access-list commands display the counters.
7050 and 7060 series switches enable egress ACL counters and do not require configuration.
For other platforms, to enable egress ACL counters for a specific ACL, use the counters per-entry command in the ACL's configuration mode.
Example
switch(config)# ip access-list acl1
switch(config-acl-acl1)# counters per-entry7050 and 7060 series switches enable egress counters.
For other switches, enable IPv4 and IPv6 egress ACL counters in the global configuration mode using the hardware counter feature acl out command.
Example
switch(config)# hardware counter feature acl out ipv4
switch(config)#switch(config)# hardware counter feature acl out ipv6
switch(config)#For 7050 and 7060 series switches, egress counters cannot be disabled.
For other switches, disable IPv4 and IPv6 egress ACL counters in the global configuration mode by using the hardware counter feature acl out command.
switch(config)# no hardware counter feature acl out ipv4
switch(config)#switch(config)# no hardware counter feature acl out ipv6
switch(config)#The counters roll over when the counter value for an ACL rule exceeds 2^64 (2 to the power of 64).
Example
In the following example, the hardware counter feature acl ipv6 out command is configured using units and packets.
switch(config)# hardware counter feature acl ipv6 out units packets
switch(config)#The clear ip access-lists counters command clears the counters for all of the IPv4 ACLs or a specific IPv4 ACL, either globally or per CLI session.
Example
switch(config)# clear ip access-list counters red session
switch(config)#The IPv6 egress ACL counters do not work in unshared mode.
Example
switch(config)# hardware access-list resource sharing vlan ipv6 out
switch(config)#The clear ipv6 access-list counters command clears the counters for all of the IPv6 ACLs or a specific IPv6 ACL, either globally or per CLI session.
Example
switch(config)# clear ipv6 access-list counters green session
switch(config)#Use the following show commands to display information on Egress ACL Counters.
switch(config)# show ip access-list acl1
IP Access List acl1
counter per-entry
10 deny ip 11.1.1.0/24 any dscp af11
20 deny ip any any [match 39080716, 0:00:00 ago]
Total rules configured: 2
Configured on Ingress: Et2/1
Active on Ingress: Et2/1
switch(config)# show ipv6 access-list acl1
IPV6 Access List acl1
counter per-entry
10 permit ipv6 any any [match 3450000, 0:00:10 ago]
20 deny ipv6 any any
Total rules configured: 2
Configured on Ingress: Et2/1
Active on Ingress: Et2/1
switch(config)# show hardware counter drop
Summary:
Total Adverse (A) Drops: 0
Total Congestion (C) Drops: 0
Total Packet Processor (P) Drops: 250
Type Chip CounterName : Count : First Occurrence : Last Occurrence
-------------------------------------------------------------------------------
P Fap0 EgressAclDropCounter : 250 : 2015-11-11 22:39:02 : 2015-11-11 22:51:44The switch enters the appropriate ACL Configuration Mode for the list. When adding the name of an existing ACL to the command, subsequent commands edit that list (see Modifying an ACL for additional information).
switch(config)# ip access-list test1
switch(config-acl-test1)#switch(config)# ip access-list standard stest1
switch(config-std-acl-stest1)#switch(config)# mac access-list mtest1
switch(config-mac-acl-mtest1)#ACL Configuration Modes are group-change modes. Changes made in a group-change mode are saved when exiting the mode. To discard changes, use the abort command instead of exit.
switch(config-acl-test1)# permit ip 10.10.10.0/24 any
switch(config-acl-test1)# permit ip any host 10.20.10.1
switch(config-acl-test1)# deny ip host 10.10.10.1 host 10.20.10.1switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.30.10.0/24 host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any anyBecause EOS has not saved the changes, the ACL remains empty, as displayed by show ip access-lists.
switch(config-acl-test1)# show ip access-lists test1
switch(config-acl-test1)#switch(config-acl-test1)# exit
switch(config)# show ip access-lists test1
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.30.10.0/24 host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
Total rules configured: 4
Configured on Ingress: Et1/1
Active on Ingress: Et1/1switch(config)# int et1/1
switch(config-if-Et1/1)# ip access-group test1 inswitch(config-if-Et1/1)# exit
switch(config)#
switch(config)# show ip access-lists test1
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.30.10.0/24 host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
Total rules configured: 4
Configured on Ingress: Et1/1
Active on Ingress: Et1/1The abort command exits ACL Configuration mode without saving pending changes.
switch(config-acl-test1)# permit ip 10.10.10.0/24 any
switch(config-acl-test1)# permit ip any host 10.20.10.1
switch(config-acl-test1)# deny ip host 10.10.10.1 host 10.20.10.1switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.30.10.0/24 host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any anyswitch(config-acl-test1)# abort
switch(config)#An existing ACL, including those applied to interfaces, can be modified by entering the appropriate configuration mode for the ACL as described in Creating and Opening a List. By default, while modifying an ACL, all traffic is blocked on any interface using the ACL.
To avoid packet loss and interference with features like routing and dynamic NAT, you can configure the following switches to permit all traffic on Ethernet and VLAN interfaces during ACL modifications:
Use the hardware access-list update default-result permit command to configure the preceding switches.
deny rules to the appropriate ACL:
permit rules to the appropriate ACL:
To append a rule to the end of a list, enter the rule without a sequence number while in ACL configuration mode for the list. The switch computes the new rule’s sequence number by adding 10 to the last rule’s sequence number.
switch(config)# hardware access-list update default-result permit switch(config-acl-test1)# permit ip 10.10.10.0/24 any
switch(config-acl-test1)# permit ip any host 10.20.10.1
switch(config-acl-test1)# deny ip host 10.10.10.1 host 10.20.10.1To view the edited list, use the show command.
switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1switch(config-acl-test1)# permit ip any any
switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any anyTo insert a rule into an ACL, enter the rule with a sequence number between the existing rules’ numbers.
Switch(config-acl-test1)# 15 permit ip 10.30.10.0/24 host 10.20.10.1
Switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
15 permit ip 10.30.10.0/24 host 10.20.10.1
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any anyswitch(config-acl-test1)# no 20
switch(config-acl-test1)# no permit ip any host 10.20.10.1
switch(config-acl-test1)# default permit ip any host 10.20.10.1This ACL results from entering one of the preceding commands.
switch(config-acl-test1)# show
ip access list test1
10 permit ip 10.10.10.0/24 any
15 permit ip 10.30.10.0/24 host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any anySequence numbers determine the order of the rules in an ACL. After editing a list and deleting existing rules while inserting new rules between existing rules, the sequence number distribution may not be uniform. Resequencing rule numbers changes the sequence number of rules to provide a constant difference between adjacent rules. The resequence (ACLs) command adjusts the sequence numbers of ACL rules.
switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
25 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
50 permit ip any any
90 remark end of list
switch(config-acl-test1)# resequence 100 20
switch(config-acl-test1)# show
IP Access List test1
100 permit ip 10.10.10.0/24 any
120 permit ip any host 10.20.10.1
140 deny ip host 10.10.10.1 host 10.20.10.1
160 permit ip any any
180 remark end of listACL Rules provide a log option that produces a syslog message about the packets matching a desired packet. ACL Logging creates a syslog entry when a packet matches an ACL rule with logging enabled.
switch(config-acl-test1)# 15 permit ip 10.30.10.0/24 host 10.20.10.1 log
switch(config-acl-test1)#IPACCESS: list acl intf filter protocol src-ip(src_port) -> dst-ip(dst_port)
IPACCESS: list acl intf filter icmp src-ip(src-port) -> dst-ip(dst-port) type= n code= m
IPACCESS: list acl intf filter protocol src-ip -> dst-ip
MACACCESS: list acl intf filter vlan ether src_mac -> dst_mac
MACACCESS: list acl intf filter vlan ether ip-prt src-mac src-ip : src-prt -> dst-mac dst-ip : dst-prt
MACACCESS: list acl intf filtervlan ether src_mac src_ip -> dst_mac dst_ip
ACLs provide a command that configures as counter state as counting or non-counting. The counter state applies to all rules in the ACL. The initial state for new ACLs defaults to non-counting.
The counters per-entry (ACL configuration modes) command places the ACL in counting mode.
switch(config-acl-test1)# counters per-entry
switch(config-acl-test1)# exit
switch(config-acl-test1)# show ip access-list test1
IP Access List test1
counters per-entry
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of list
Total rules configured: 5
Configured on Ingress: Et1
Active on Ingress: Et1The clear ip access-lists counters and clear ipv6 access-lists counters commands set the IP access list counters to zero for the specified IP access list.
switch(config)# clear ip access-lists counters test1
switch(config)#Display ACLs using the show running-config command. The show ip access-lists command also displays ACL rosters and contents as specified by command parameters.
When editing an ACL, the show (ACL configuration modes) command displays the current or pending list as specified by command parameters.
To display the roster of ACLs on the switch, use the show [ip | ipv6 | mac] access-lists command with the summary option.
switch(config)# show ip access-lists summary
IPV4 ACL default-control-plane-acl
Total rules configured: 12
Configured on: control-plane
Active on : control-plane
IPV4 ACL list2
Total rules configured: 3
IPV4 ACL test1
Total rules configured: 6
IPV4 ACL test_1
Total rules configured: 1
IPV4 ACL test_3
Total rules configured: 0
switch(config)#Each command can display the contents of one ACL or of all ACLs of the type specified by the command:
ACLs in counting mode display the number of inbound packets matching each rule in the list and the elapsed time since the last match.
switch# show ip access-lists default-control-plane-acl
IP Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmp any any
20 permit ip any any tracked [match 1725, 0:00:00 ago]
30 permit ospf any any
40 permit tcp any any eq ssh telnet www snmp bgp https
50 permit udp any any eq bootps bootpc snmp [match 993, 0:00:29 ago]
60 permit tcp any any eq mlag ttl eq 255
70 permit udp any any eq mlag ttl eq 255
80 permit vrrp any any
90 permit ahp any any
100 permit pim any any
110 permit igmp any any [match 1316, 0:00:23 ago]
120 permit tcp any any range 5900 5910
Total rules configured: 12
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)switch# show ip access-lists
IP Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmp any any
20 permit ip any any tracked [match 1371, 0:00:00 ago]
30 permit ospf any any
40 permit tcp any any eq ssh telnet www snmp bgp https
50 permit udp any any eq bootps bootpc snmp
60 permit tcp any any eq mlag ttl eq 255
70 permit udp any any eq mlag ttl eq 255
80 permit vrrp any any
90 permit ahp any any
100 permit pim any any
110 permit igmp any any [match 1316, 0:00:23 ago]
120 permit tcp any any range 5900 5910
Total rules configured: 12
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IP Access List list2
10 permit ip 10.10.10.0/24 any
20 permit ip 10.30.10.0/24 host 10.20.10.1
30 permit ip any host 10.20.10.1
40 deny ip host 10.10.10.1 host 10.20.10.1
50 permit ip any any
Total rules configured: 5
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
IP Access List test1
switch(config)#
The examples in this section display previously configured ACL commands.
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.21.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of list20 permit ip any host 10.21.10.120 permit ip 10.10.0.0/16 any
25 permit tcp 10.10.20.0/24 any
45 deny pim 239.24.124.0/24 10.5.8.4/30switch(config-acl-test_1)# show pending
IP Access List test_1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.10.0.0/16 any
25 permit tcp 10.10.20.0/24 any
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
45 deny pim 239.24.124.0/24 10.5.8.4/30
50 remark end of listswitch(config-acl-test_1)# show active
IP Access List test_1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.21.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of listThe following command displays the difference between the saved and modified ACLs.
switch(config-acl-test_1)# show diff
---
+++
@@ -1,7 +1,9 @@
IP Access List test_1
10 permit ip 10.10.10.0/24 any
- 20 permit ip any host 10.21.10.1
+ 20 permit ip 10.10.0.0/16 any
+ 25 permit tcp 10.10.20.0/24 any
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
+ 45 deny pim 239.24.124.0/24 10.5.8.4/30The following show commands display Egress ACL Counters information.
switch(config)# show ip access-list acl1
IP Access List acl1
counter per-entry
10 deny ip 11.1.1.0/24 any dscp af11
20 deny ip any any [match 39080716, 0:00:00 ago]
Total rules configured: 2
Configured on Ingress: Et2/1
Active on Ingress: Et2/1switch(config)# show ipv6 access-list acl1
IPV6 Access List acl1
counter per-entry
10 permit ipv6 any any [match 3450000, 0:00:10 ago]
20 deny ipv6 any any
Total rules configured: 2
Configured on Ingress: Et1/1
Active on Ingress: Et1/1switch(config)# show hardware counter drop
Summary:
Total Adverse (A) Drops: 0
Total Congestion (C) Drops: 0
Total Packet Processor (P) Drops: 250
Type Chip CounterName : Count : First Occurrence : Last Occurrence
-------------------------------------------------------------------------------
P Fap0 EgressAclDropCounter : 250 : 2015-11-11 22:39:02 : 2015-11-11 22:51:44switch# config
switch(config)# hardware tcam profile qosswitch(config)# ip access-list acl1
switch(config-acl-acl1)# permit vlan 100 0xfff ip any any
switch(config-acl-acl1)# exitswitch(config)# class-map match-any class1
switch(config-cmap-qos-class1)# match vlan 20-40, 1000-1250, 2000
switch(config-cmap-qos-class1)# exitThe following show commands display the status, traffic hit counts, TCAM profile information, and policy maps configured on an interface.
switch# show policy-map policy1
Service-policy policy1
Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes
Class-map: class-default (match-any)switch# show policy-map interface ethernet 1
Service-policy input: p1
Hardware programming status: Successful
Class-map: c2001 (match-any)
Match: vlan 2001 0xfff
set dscp 4
Class-map: c2002 (match-any)
Match: vlan 2002 0xfff
set dscp 8
Class-map: c2003 (match-any)
Match: vlan 2003 0xfff
set dscp 12Access Control Lists (ACLs) are configured to permit or deny traffic between source and destination ports on Strata-based platforms. Mirror ACLs are used in mirroring traffic by matching VLAN ID of the configured ACLs. Mirror ACLs are applied for IPv4, IPv6, and MAC ACLs.
switch(config)# ip access-list acl1
switch(config-acl-acl1)# permit vlan 1234 0x0 ip any anyswitch(config)# monitor session sess1 source ethernet 1 rx ip access-group acl1
switch(config)# monitor session sess1 destination ethernet 2Access Control Lists (ACLs) become active when assigned to an interface, subinterface, or control plane. This section describes the process of adding and removing ACL interface assignments.
IPv4, IPv6, and MAC ACLs are separately applied for inbound and outbound packets. You can assign an interface or subinterface with multiple ACLs, with a limit of one ACL per packet direction per ACL type. A subset of all available switches support Egress ACLs. IPv6 egress ACLs have limited availability, and IPv6 egress ACLs applied to routed interfaces or subinterfaces across the same chip on the DCS-7500E and the DCS-7280E series can be shared. In addition to that, the DSCP value can match on IPv6 egress ACLs. This ability results in more efficient utilization of system resources and is particularly useful for environments with few, potentially large, IPv6 egress ACLs applied across multiple routed interfaces.
switch(config)# interface ethernet 3
switch(config-if-Et3)# ip access-group test1 in
switch(config-if-Et3)# show running-config interfaces ethernet 3
interface Ethernet3
ip access-group test1 in
switch(config-if-Et3)#switch(config)# control-plane
switch(config-cp)# ip access-group test_cp inswitch(config)# hardware access-list resource sharing vlan ipv6 out
switch(config)#switch(config)# no hardware access-list resource sharing vlan ipv6 out
switch(config)#switch(config)# interface ethernet 5.1
switch(config-if-Et5.1)# ipv4 access-group test_ACL in
switch(config-if-Et5.1)#The no ip access-group command removes an IP ACL assignment statement from running-config for the configuration mode interface. After removing an ACL, the interface is no longer associated with an IP ACL.
The no mac ip access-group command removes a MAC ACL assignment statement from running-config for the configuration mode interface. After removing a MAC ACL is removed, the interface is no longer associated with an MAC ACL.
To remove an ACL from the control plane, enter the no ip access-group command in control plane configuration mode. Removing the control plane ACL command from running-config reinstates default-control-plane-acl as the control plane ACL.
switch(config)# interface ethernet 3
switch(config-if-Et3)# no ip access-group test in
switch(config-if-Et3)#switch(config)# control-plane
switch(config-cp)# no ip access-group test_cp in
switch(config-cp)#Service ACL enforcement is a feature added to a control plane service (the SSH server, the SNMP server, routing protocols, etc.) that allows the switch administrator to restrict the processing of packets and connections by the control plane processes that implement that service. The control plane program run by the control plane process checks already received packets and connections against a user-configurable Access Control List (ACL), a Service ACL.
The Service ACL contains permit and deny rules matching any source address, destination address, and TCP or UDP ports of received packets or connections. After receiving a packet or connection, the control plane process evaluates the packet or connection against the rules of the Service ACL configured for the control plane process. If the received packet or connection matches a deny rule, the control plane process drops or closes it without further processing.
Control Plane Process Enforced Access Control enables the system administrator to restrict which systems on the network can access the services provided by the switch. Each service has its own access control list, giving the system administrator fine-grained control over access to the switch's control plane services. The CLI for this uses the familiar pattern of access control lists assigned for a specific purpose, in this case, for each control plane service.
config-mgt-ssh configuration mode:
switch(config)# management ssh
switch(config-mgmt-ssh)# ip access-group <acl_name> [vrf <vrf_name>] in
switch(config-mgmt-ssh)# ipv6 access-group <acl_name> [vrf <vrf_name>] inIn Release EOS-4.19.0, all VRFs are required to use the same SSH Server Service ACL. The Service ACL assigned without the vrf keyword is applied to all VRFs where the SSH Server is enabled.
switch# show management ssh ip access-list
switch# show management ssh ipv6 access-listUse the snmp-server community command to apply the SNMP Server Service ACLs to restrict which hosts can access SNMP services on the switch:
switch(config)# snmp-server community community-name [view viewname] [ro | rw] acl_nameswitch(config)# snmp-server community community-name [view viewname] [ro | rw] ipv6 ipv6_acl_nameswitch(config)# management api http-commands
switch(config-mgmt-api-http-cmds)# vrf <vrf_name>
switch(config-mgmt-api-http-cmds-vrf-<vrf>)# ip access-group <acl_name>
switch(config-mgmt-api-http-cmds-vrf-<vrf>)# ipv6 access-group <ipv6_acl_name>switch# show management api http-commands ip access-list
switch# show management api http-commands ipv6 access-listswitch(config)# router bgp <asn>
switch(config-router-bgp)# ip access-group <acl_name>
switch(config-router-bgp)# ipv6 access-group <ipv6_acl_name>
switch(config-router-bgp)# vrf <vrf_name>
switch(config-router-bgp-vrf-<vrf>)# ip access-group <acl_name>
switch(config-router-bgp-vrf-<vrf>)# ipv6 access-group <ipv6_acl_name>switch# show bgp ipv4 access-list
switch# show bgp ipv6 access-listUnequal Cost MultiPath (UCMP) for BGP forwards traffic based on weight assignments for next hops of Equal Cost MultiPath (ECMP) routes. The system programs the weights in the Forwarding Information Base (FIB).
Devices that receive BGP routes disseminate BGP link-bandwidth extended community attribute information. These devices then program the next hops in the FIB using the received link-bandwidth values. The system appends the percentage of interface speed to the received link bandwidth extended community value of the route. It adjusts the weight ratio of the traffic sent over egress ports to forward more traffic toward the peer with a higher interface speed.
switch(config-router-bgp)# neighbor group1 link-bandwidth adjust auto percent 62.3PERCENT is a float value between 0.0 and 100.0 and is optional.
Use the ip access-group (Service ACLs) and ipv6 access-group (Service ACLs) commands to apply Service ACLs to control packets processed by the OSPF routing protocol agent:
switch(config)# router ospf <id>
switch(config-router-ospf)# ip access-group <acl_name>
switch(config-router-ospf)# ipv6 access-group <ipv6_acl_name>When using VRFs, each per VRF OSPF instance must be explicitly assigned its Service ACL.
switch# show ospf ipv4 access-list
switch# show ospf ipv6 access-listswitch(config)# router pim
switch(config-router-pim)# ipv4
switch(config-router-pim-ipv4)# access-group <acl_name>
switch(config-router-pim-ipv4)# vrf <vrf_name>
switch(config-router-pim-vrf-<vrf>)# ipv4
switch(config-router-pim-vrf-<vrf>-ipv4)# access-group <acl_name>switch# show ip pim access-listswitch(config)# router igmp
switch(config-router-igmp)# ip igmp access-group <acl_name>
switch(config-router-igmp)# vrf <vrf_name>
switch(config-router-igmp-vrf-<vrf>)# ip igmp access-group <acl_name>switch# show ip igmp access-listswitch(config)# ip dhcp relay access-group <acl_name> [vrf <vrf_name>]
switch(config)# ipv6 dhcp relay access-group <acl_name> [vrf <vrf_name>]switch# show ip dhcp relay access-list
switch# show ipv6 dhcp relay access-listswitch(config)# mpls ldp
switch(config-mpls-ldp)# ip access-group <acl_name>switch# show mpls ldp access-listswitch(config)# queue-monitor streaming
switch(config-qm-streaming)# ip access-group <acl_name>
switch(config-qm-streaming)# ipv6 access-group <ipv6_acl_name>switch# show queue-monitor streaming access-listsswitch(config)# mpls ping
switch(config-mpls-ping)# ip access-group <acl_name> [vrf <vrf_name>]
switch(config-mpls-ping)# ipv6 access-group <ipv6_acl_name> [vrf <vrf_name>]switch(config)# management telnet
switch(config-mgmt-telnet)# ip access-group <acl_name> [vrf <vrf_name>] in
switch(config-mgmt-telnet)# ipv6 access-group <ipv6_acl_name> [vrf <vrf_name>] inIn EOS 4.19.0, all VRFs are required to use the same Telnet server Service ACL. The Service ACL assigned without the vrf keyword is applied to all VRFs where the Telnet server is enabled.
switch# show management telnet ip access-list
switch# show management telnet ipv6 access-listip|ipv6 access-group acl-name in | outno ip|ipv6 access-group in | outConfigure a mirror session using subinterface sources and apply explicit ACLs to each source in the session. EOS only supports ingress mirroring from the Rx direction.
switch(config)# monitor session ACLMirror1 source Ethernet 5/1.1 rx
switch(config)# monitor session ACLMirror1 source Ethernet 5/1.2 rx ip access-group acl1
switch(config)# monitor session ACLMirror1 source Ethernet 6/1 rx
switch(config)# monitor session ACLMirror1 destination Ethernet 14/1switch(config)# show monitor session
Session ACLMirror1
------------------------
Programmed in HW: Yes
Source Ports:
Rx Only: Et5/1.2(IP ACL: acl1), Et5/1.1
Et6/1
Destination Ports:
Et14/1 : activeThe show ip access-lists and show ipv6 access-lists commands display the summary of a configured ACL including the subinterface on which the ACL is configured and active.
show ip|ipv6 access-lists acl-name summary
switch(config)# show ip access-lists acl1 summary
IPV4 ACL acl1
Total rules configured: 1
Configured on Ingress: Et5.1
Active on Ingress: Et5.1switch(config)# show ipv6 access-lists acl1 summary
IPV6 ACL acl1
Total rules configured: 1
Configured on Egress: Et5.1
Active on Egress: Et5.1IPv4 ingress sharing optimizes the utilization of hardware resources by sharing them between different VLAN interfaces when they have the same ACL attached.
Larger deployments benefit from this function, where IPv4 ingress sharing is applied on multiple SVIs with member interfaces on the same forwarding ASIC. For example, a trunk port carrying multiple VLANs and an ingress sharing is applied on all VLANs; it occupies lesser hardware resources irrespective of the number of VLANs. By default, IPv4 ingress sharing is disabled on the switches.
IPv4 Egress Sharing optimizes the utilization of hardware resources by sharing TCAM entries for a group of SVIs on which IPv4 ACLs are shared. The TCAM entries are shared for all the SVIs per chip, saving a lot of hardware resources and enabling ACLs to scale to larger configurations.
Larger deployments benefit from IPv4 Egress Sharing, which is applied on multiple SVIs with member interfaces on the same forwarding ASIC. For example, a trunk port carrying multiple VLANs, and when applying Egress Sharing on all VLANs, it occupies lesser hardware resources irrespective of the number of VLANs.
By default, the system enables IPv4 Egress Sharing on the switches. However, enabling both IPv4 Egress Sharing and uRPF cannot at the same time is not possible. Disabling IPv4 RACL sharing will allow uRPF configuration and ensure the simultaneous configuration of the RACL in non-shared mode.
To enable unicast Reverse Path Forwarding (uRPF) on the switch, the IPv4 Egress Sharing must be disabled using the no hardware access-list resource sharing vlan ipv4 out command.
The no form of the command disables the switch's IPv4 Egress Sharing, allowing you to configure the uRPF.
switch# show ip access-lists summary
IPV4 ACL default-control-plane-acl [readonly]
Total rules configured: 17
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IPV4 ACL ipAclLimitTest
Total rules configured: 0
Configured on Egress: Vl2148,2700
Active on Egress: Vl2148,2700switch# show vlan
VLAN Name Status Ports
----- -------------- --------- -----------------
1 default active
2148 VLAN2148 active Cpu, Et1, Et26
2700 VLAN2700 active Cpu, Et18switch# show platform arad acl tcam detail
ip access-list ipAclLimitTest (Shared RACL, 0 rules, 1 entries, direction out,
state success, Acl Label 2)
Fap: Arad0, Shared: true, Interfaces: Vl2148, Vl2700
Bank Offset Entries
0 0 1
Fap: Arad1, Shared: true, Interfaces: Vl2148
Bank Offset Entries
0 0 1
switch# show platform arad acl tcam summary
The total number of TCAM lines per bank is 1024.
========================================================
Arad0:
========================================================
Bank Used Used % Used By
0 1 0 IP Egress PACLs/RACLs
Total Number of TCAM lines used is: 1
========================================================
Arad1:
========================================================
Bank Used Used % Used By
0 1 0 IP Egress PACLs/RACLs
Total Number of TCAM lines used is: 1switch# show ip route
VRF name: default
Codes: C - connected, S - static, K - kernel,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type2, B I - iBGP, B E - eBGP,
R - RIP, I - ISIS, A B - BGP Aggregate, A O - OSPF Summary,
NG - Nexthop Group Static Route
Gateway of last resort is not set
C 10.1.0.0/16 is directly connected, Vlan2659
C 10.2.0.0/16 is directly connected, Vlan2148
C 10.3.0.0/16 is directly connected, Vlan2700
S 172.17.0.0/16 [1/0] via 172.24.0.1, Management1
S 172.18.0.0/16 [1/0] via 172.24.0.1, Management1
S 172.19.0.0/16 [1/0] via 172.24.0.1, Management1
S 172.20.0.0/16 [1/0] via 172.24.0.1, Management1
S 172.22.0.0/16 [1/0] via 172.24.0.1, Management1
C 172.24.0.0/18 is directly connected, Management1switch# show platform arad ip route
Tunnel Type: M(mpls), G(gre)
-------------------------------------------------------------------------------
| Routing Table | |
|------------------------------------------------------------------------------
|VRF| Destination | | | | Acl | |
ECMP| FEC | Tunnel
| ID| Subnet | Cmd | Destination | VID | Label | MAC / CPU Code
|Index|Index|T Value
--------------------------------------------------------------------------------
|0 |0.0.0.0/8 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1031 | -
|0 |10.1.0.0/16 |TRAP | CoppSystemL3DstMiss|2659 | - | ArpTrap | - |1030 | -
|0 |10.2.0.0/16 |TRAP | CoppSystemL3DstMiss|2148 | - | ArpTrap | - |1026 | -
|0 |10.3.0.0/16 |TRAP | CoppSystemL3DstMiss|2700 | - | ArpTrap | - |1034 | -
|0 |127.0.0.0/8 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1031 | -
|0 |172.17.0.0/16 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1025 | -
|0 |172.18.0.0/16 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1025 | -
|0 |172.19.0.0/16 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1025 | -
|0 |172.20.0.0/16 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1025 | -
|0 |172.22.0.0/16 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1025 | -
|0 |172.24.0.0/18 |TRAP | CoppSystemL3DstMiss|0 | - | ArpTrap | - |1032 | -
|0 |0.0.0.0/0 |TRAP | CoppSystemL3LpmOver|0 | - | SlowReceive | -
|1024 | -
|0 |10.1.0.0/32* |TRAP | CoppSystemIpBcast |0 | - | BcastReceive | -
|1027 | -
|0 |10.1.0.1/32* |TRAP | CoppSystemIpUcast |0 | - | Receive | - |32766| -
|0 |10.1.255.1/32* |ROUTE| Po1 |2659 |4094 | 00:1f:5d:6b:ce:45
| - |1035 | -
|0 |10.1.255.255/32* |TRAP | CoppSystemIpBcast |0 | - | BcastReceive | -
|1027 | -
|0 |10.2.0.0/32* |TRAP | CoppSystemIpBcast |0 | - | BcastReceive | -
|1027 | -
|0 |10.2.0.1/32* |TRAP | CoppSystemIpUcast |0 | - | Receive | - |32766| -
|0 |10.2.255.1/32* |ROUTE| Et1 |2148 |2 | 00:1f:5d:6d:54:dc |
- |1036 | -
|0 |10.2.255.255/32* |TRAP | CoppSystemIpBcast |0 | - | BcastReceive | -
|1027 | -
|0 |10.3.0.0/32* |TRAP | CoppSystemIpBcast |0 | - | BcastReceive | -
|1027 | -
|0 |10.3.0.1/32* |TRAP | CoppSystemIpUcast |0 | - | Receive | - |32766| -
|0 |10.3.255.1/32* |ROUTE| Et18 |2700 |2 | 00:1f:5d:6b:00:01 |
- |1038 | -A route map is an ordered set of rules that controls the redistribution of IP routes into a protocol domain based on criteria such as route metrics, access control lists, next-hop addresses, and route tags. Route maps can also alter route parameters as they are redistributed.
Route maps are composed of route map statements, each consisting of a list of match and set commands.
The Set commands modify parameters for redistributed routes and are valid in permit statements.
switch# route-map MAP_1 permit 10
match as 10
set local-preference 100 A route map consists of statements with the same name and different sequence numbers. Statements filter routes by ascending order based on their sequence numbers. When a statement passes a route, the redistribution action is performed as the filter type specifies, ignoring all subsequent statements. When the statement fails the route, the statement with the smallest sequence number larger than the current one filters the route.
All route maps contain an implied final statement containing a single deny statement without a match command. This statement denies the redistribution of any routes that no other statement passes.
switch# route-map MAP_1 permit 10
match as 10
set local-preference 100
!
switch# route-map MAP_1 permit 20
match metric-type type-1
match as 100Route Map Configuration describes route map configuration procedures.
Route map statements that contain a continue (route map) command support additional route map evaluation of routes whose parameters meet the statement’s match commands. Routes that match a statement containing a continue command are evaluated against the statement specified by the continue command.
When a route matches multiple route-map statements, the filter action (deny or permit) is determined by the last statement that the route matches. The set commands in all statements matching the route are applied to the route after the route map evaluation is complete. Multiple set commands are applied in the same order by which the route was evaluated against the statements containing them.
switch# route-map MAP_2 permit 10
match as 10
continue 20
set local-preference 100
!
switch# route-map MAP_2 deny 20
match metric-type type-1
match as 100The route is redistributed if it passes statement 10 and is rejected by statement 20. The route is denied redistribution in all other instances. The continue command guarantees the evaluation of all routes against both statements.
To create a route map, use the route-map command, including the map name and filter type (deny or permit). If the command does not specify a number, the system assigns a default sequence number to the statement.
switch(config)# route-map map1 permit 50
switch(config-route-map-map1)#To edit an existing route map statement, use the route-map, including the map’s name and the statement’s number. The switch enters the route map configuration mode for the statement. Subsequent match (route-map) and set (route-map) commands add the corresponding commands to the statement.
The show command displays the contents of the existing route map.
switch(config)# route-map MAP2
switch(config-route-map-MAP2)#show
Match clauses:
match as 10
match tag 333
Set clauses:
set local-preference 100
switch(config-route-map-MAP2)#Route map configuration mode is a group-change mode. You can save changes by exiting the mode, either with an explicit exit command or by switching directly to another configuration mode. This includes switching to the configuration mode for a different route map.
switch(config)# route-map map1 permit
switch(config-route-map-map1)# match as 100
switch(config-route-map-map1)# show
switch(config-route-map-map1)#switch(config-route-map-map1)# exit
switch(config)# show route-map map1
route-map map1 permit 10
Match clauses:
match as 100
Set clauses:
switch(config)#The abort command discards all pending changes and exits route-map configuration mode.
switch(config)# route-map map1 permit
switch(config-route-map-map1)# match as 100
switch(config-route-map-map1)# abort
switch(config)# show route-map map1
switch(config)#To insert a new statement into an existing route map, create a new statement with a sequence number that differs from any existing statement in the map.
switch(config)# route-map Map1 permit 50
switch(config-route-map-Map1)# match as 150
switch(config-route-map-Map1)# exit
switch(config)# show route-map Map1
route-map Map1 deny 10
Match clauses:
match as 10
match tag 333
Set clauses:
set local-preference 100
route-map Map1 permit 50
Match clauses:
match as 150
Set clauses:
switch(config)#Protocol redistribution commands include a route map parameter determining the routes to be redistributed into the specified protocol domain.
switch(config)# router bgp 1
switch(config-router-bgp)# redistribute ospf route-map Map1
switch(config-router-bgp)# exit
switch(config)#A prefix list is an ordered set of rules that defines route redistribution access for a specified IP address space. It consists of a filter action (deny or permit), an address space identifier (IPv4 subnet
address or IPv6 prefix), and a sequence number.
A prefix list is an ordered set of rules that defines route redistribution access for a specified IP address space. A prefix list rule consists of a filter action (deny or permit), a network address (IPv4 subnet or IPv6 prefix), and a sequence number. A rule may also include an alternate mask size.
The switch supports IPv4 and IPv6 prefix lists. The switch is placed in a Prefix-list configuration mode to create and edit IPv4 or IPv6 prefix lists.
IPv4 prefix lists are created or modified by adding an IPv4 prefix list rule in the Prefix-list configuration mode. Each rule includes the name of a prefix list and the sequence number, network address, and filter action. A list consists of all rules that have the same prefix-list name.
The ip prefix-list command creates a prefix list or adds a rule to an existing list. Route map match commands use prefix lists to filter routes for redistribution into OSPF, RIP, or BGP domains.
To create an IPv4 prefix list, enter the ip prefix-list command, followed by the list's name. The switch enters the IPv4 prefix-list configuration mode for the list. If the name of an existing ACL follows the command, subsequent commands edit that list.
switch(config)# ip prefix-list route-one
switch(config-ip-pfx)#switch(config)# ip prefix-list route-one
switch(config-ip-pfx)# seq 10 deny 10.1.1.0/24
switch(config-ip-pfx)# seq 20 deny 10.1.0.0/16
switch(config-ip-pfx)# seq 30 permit 12.15.4.9/32
switch(config-ip-pfx)# seq 40 deny 1.1.1.0/24switch(config-ip-pfx)# exit
switch(config)# ip prefix-list route-one
switch(config-ip-pfx)# show active
ip prefix-list route-one
seq 10 deny 10.1.1.0/24
seq 20 deny 10.1.0.0/16
seq 30 permit 12.15.4.9/32
seq 40 deny 1.1.1.0/24
switch(config-ip-pfx)# ip prefix-list route-oneIPv4 prefix lists are referenced in the match (route-map) command.
The switch provides an IPv6 prefix-list configuration mode for creating and modifying IPv6 prefix lists. A list can be edited only in the mode where it was created.
To create an IP ACL, enter the ipv6 prefix-list command and the list's name. The switch enters the list's IPv6 prefix-list configuration mode. If the name of an existing ACL follows the command, subsequent commands edit that list.
switch(config)# ipv6 prefix-list map1
switch(config-ipv6-pfx)#To append a rule to the end of a list, enter the rule without a sequence number while in Prefix-List configuration mode for the list. The system derives the new rule’s sequence number by adding 10 to the last rule’s sequence number.
switch(config-ipv6-pfx)# permit 3:4e96:8ca1:33cf::/64
switch(config-ipv6-pfx)# permit 3:11b1:8fe4:1aac::/64switch(config-ipv6-pfx)# exit
switch(config)# ipv6 prefix-list map1
switch(config-ipv6-pfx)# show active
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 20 permit 3:11b1:8fe4:1aac::/64
switch(config-ipv6-pfx)#switch(config-ipv6-pfx)# permit 3:1bca:1141:ab34::/64
switch(config-ipv6-pfx)# exit
switch(config)# ipv6 prefix-list map1
switch(config-ipv6-pfx)# show active
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 20 permit 3:11b1:8fe4:1aac::/64
seq 30 permit 3:1bca:1141:ab34::/64
switch(config-ipv6-pfx)#To insert a rule into a prefix list, use the seq (IPv6 Prefix Lists) command to enter a rule with a sequence number between the numbers of two existing rules.
switch(config-ipv6-pfx)# seq 15 deny 3:4400::/64
switch(config-ipv6-pfx)# exit
switch(config)# show ipv6 prefix-list map1
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 15 deny 3:4400::/64
seq 20 permit 3:11b1:8fe4:1aac::/64
seq 30 permit 3:1bca:3ff2:634a::/64
switch(config)#To remove a rule from the configuration mode prefix list, enter no seq (see seq (IPv6 Prefix Lists)), followed by the rule's sequence number.
switch(config-ipv6-pfx)# no seq 20
switch(config-ipv6-pfx)# exit
switch(config)# show ipv6 prefix-list map1
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 15 deny 3:4400::/64
seq 30 permit 3:1bca:3ff2:634a::/64
switch(config)#Route map match commands include an option that matches a specified prefix list.
Example
switch(config)# route-map MAP_1 permit
switch(config-route-map-MAP_1)# match ip address prefix-list PL_1
switch(config-route-map-MAP_1)# set community 500
switch(config-route-map-MAP_1)# exitUse match ip next-hop to match against next-hops in a route-map. This can be used to redistribute matching static routes into an IGP (IS-IS, OSPF, etc.).
switch(config)# ip route 10.20.30.0/24 1.2.3.4switch (config)# ip prefix-list prefixListName
switch(config-ip-pfx)# permit 1.2.3.4/321.2.3.4 is a configured next-hop for static route 10.20.30.0/24.
switch(config)# route-map routeMapName
switch(config-route-map-routeMapName)# match ip next-hop prefix-list prefixListNameswitch(config-router-isis)# redistribute static route-map routeMapNameView redistributed routes using the following show commands.
switch# show ip route
VRF: default
Codes: C - connected, S - static, K - kernel,
O - OSPF, IA - OSPF inter area, E1 - OSPF external type 1,
E2 - OSPF external type 2, N1 - OSPF NSSA external type 1,
N2 - OSPF NSSA external type2, B - BGP, B I - iBGP, B E - eBGP,
R - RIP, I L1 - IS-IS level 1, I L2 - IS-IS level 2,
O3 - OSPFv3, A B - BGP Aggregate, A O - OSPF Summary,
NG - Nexthop Group Static Route, V - VXLAN Control Service,
DH - DHCP client installed default route, M - Martian,
DP - Dynamic Policy Route, L - VRF Leaked
Gateway of last resort is not set
...
I L2 10.20.30.0/24 [115/10] via 1.2.3.4, Ethernet1switch# show isis database detail
IS-IS Instance: B VRF: default
IS-IS Level 1 Link State Database
LSPID Seq Num Cksum Life IS Flags
...
IS-IS Level 2 Link State Database
LSPID Seq Num Cksum Life IS Flags
0000.0000.0001.00-00 6 10364 840 L2 <>
...
Reachability : 10.20.30.0/24 Metric: 0 Type: 1 Up
...While the preceding example applies to IS-IS, a similar approach may be taken for other IGPs, such as OSPF.
Describes the support for specifying User-Defined Fields (UDF) in Port ACLs, including IPv4, IPv6, and MAC ACLs. The purpose of the User-Defined Fields feature is to permit or deny packets based on custom offset pattern matching.
User-Defined Fields, or UDFs, are part of an access-list filter and comprise an offset, length, pattern match and mask. This describes a single portion of any incoming packet that matches the provided value.
UDFs may also be defined via aliases. Aliases can save a UDF configuration for reuse in multiple access lists or access list rules. An alias may substitute for a fully defined UDF, including the offset, pattern, and mask. The pattern or mask may be overridden when the alias is used in an access list rule.
The behavior, CLI syntax, and configuration of UDFs are identical to Traffic Steering UDF and Mirroring ACL UDF.
User-Defined Fields (UDFs) are specified as part of an access list. However, the type of access list dictates the base position of the UDF and the options available. In addition, you must configure a TCAM profile to include UDFs as part of the Port ACL feature’s key.
User-Defined Fields are defined as additional fields in the Port ACL feature’s key. By default, UDFs are not included in the keys for the Port ACL features. Adding a UDF to the key requires removing different key fields to fit within the TCAM width restrictions.
The following are example configurations of the TCAM profile.
switch(config)# hardware tcam
switch(config-hw-tcam)# profile ipv4Udf copy default
switch(config-hw-tcam-profile-ipv4Udf)# feature acl port ip
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# no key field l4-ops
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# no key field l4-src-port
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# no key field l4-dst-port
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# key field udf-16b-1
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# key field udf-32b-1
switch(config-hw-tcam-profile-ipv4Udf-feature-acl-port-ip)# exit
switch(config-hw-tcam-profile-ipv4Udf)# exit
switch(config-hw-tcam)# system profile ipv4UdfExample
The following configurations match IPv4 packets based on the Identification (ID) field.
0x03E80000) are forwarded, while packets with an ID different from 1000 are dropped.
(config)# ip access-list udfAcl
(config-acl-udfAcl)# permit ip any any payload header start offset 1 pattern 0x03E80000 mask 0x0000FFFF
(config-acl-udfAcl)# deny ip any any
(config-acl-udfAcl)# exit
(config)# interface ethernet 7
(config-if-Et7)#switch(config)# hardware tcam
switch(config-hw-tcam)# profile ipv6Udf copy default
switch(config-hw-tcam-profile-ipv6Udf)# feature acl port ipv6
switch(config-hw-tcam-profile-ipv6Udf-feature-acl-port-ipv6)# no key field dst-ipv6
switch(config-hw-tcam-profile-ipv6Udf-feature-acl-port-ipv6)# key field udf-32b-1
switch(config-hw-tcam-profile-ipv6Udf-feature-acl-port-ipv6)# key field udf-32b-2
switch(config-hw-tcam-profile-ipv6Udf-feature-acl-port-ipv6)# exit
switch(config-hw-tcam-profile-ipv6Udf)# exit
switch(config-hw-tcam)# system profile ipv6UdfExample
The following configurations match IPv6 UDP packets based on the first 32 bits of the packet payload.
(config)# ipv6 access-list udfAcl
(config-ipv6-acl-udfAcl)# permit udp any any payload offset 2 pattern 0x12345670 mask 0x0000000f
(config-ipv6-acl-udfAcl)# deny ipv6 any any
(config-ipv6-acl-udfAcl)# exit
(config)# interface ethernet 7
(config-if-Et7)# ipv6 access-group udfAcl inThis section describes CLI commands that this chapter references.
The clear ip access-lists counters command sets ACL counters to zero for the specified IPv4 Access Control List (ACL). The session parameter limits ACL counter clearing to the current CLI session.
Command Mode
Privileged EXEC
Command Syntax
clear ip access-lists counters acl_name scope
Example
switch(config)# clear ip access-lists counters
switch(config)#The clear ipv6 access-lists counters command sets ACL counters to zero for the specified IPv6 Access Control List (ACL). The session parameter limits ACL counter clearing to the current CLI session.
Command Mode
Privileged EXEC
Command Syntax
clear ipv6 access-lists counters [acl_name][scope]
Example
switch(config)# clear ipv6 access-lists counters
switch(config)#The continue command creates a route map statement entry that enables additional route map evaluation of routes with parameters meeting the statement matching criteria.
A statement typically contains a match (route-map) and a set (route-map) command. The evaluation of routes with settings the same as match command parameters normally ends and the statement's set commands apply to the route. Routes that match a statement containing a continue command evaluate against the statement specified by the continue command.
When a route matches multiple route map commands, the last statement that the route matches determines the filter action (deny or permit) . The set commands in all statements matching the route apply to the route after completing the route map evaluation. Multiple set commands apply in the same order by the route evaluation against the statement containing them.
The no continue and default continue commands remove the corresponding continue command from the configuration mode route map statement by deleting the corresponding command from running-config.
Command Mode
Route-Map Configuration
Command Syntax
continue next_seq
no continue next_seq
default continue next_seq
Parameters
Restrictions
A continue command cannot specify a sequence number smaller than the sequence number of the route map statement.
Related Command
route-map command enters the Route-Map Configuration Mode.
Example
switch(config)# route-map map1 deny 40
switch(config-route-map-map1)# match as 15
switch(config-route-map-map1)# continue 100
switch(config-route-map-map1)# set local-preference 50
switch(config-route-map-map1)#The counters per-entry command places the ACL in counting mode. In counting mode, the feature generally displays the number of instances in which each rule in the list matches an inbound packet and the elapsed time since the last match. However, for certain select platforms, in addition to the packet counter, ACL counters can also be enabled for byte counts when applied to data plane ACLs. Review the complete list of platforms that support byte count for data plan ACLslisted below:
On the FM6000 platform, this command has no effect when used in an ACL for a PBR class map.
The no counters per-entry and default counters per-entry commands place the ACL in non-counting mode.
Command Mode
ACL Configuration
IPv6-ACL Configuration
Std-ACL Configuration
Std-IPv6-ACL Configuration
MAC-ACL Configuration
Command Syntax
counters per-entry
no counters per-entry
default counters per-entry
switch(config)# ip access-list test1
switch(config-acl-test1)# counters per-entry
switch(config-acl-test1)#switch# show ip access-lists
IP Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmp any any
20 permit ip any any tracked [match 12041 packets, 0:00:00 ago]
30 permit ospf any any
40 permit tcp any any eq ssh telnet www snmp bgp https [match 11 packets, 1:41:07 ago]
50 permit udp any any eq bootps bootpc snmp rip [match 78 packets, 0:00:27 ago]
60 permit tcp any any eq mlag ttl eq 255
70 permit udp any any eq mlag ttl eq 255
80 permit vrrp any any
90 permit ahp any any
100 permit pim any any
110 permit igmp any any [match 14 packets, 0:23:27 ago]
120 permit tcp any any range 5900 5910
130 permit tcp any any range 50000 50100
140 permit udp any any range 51000 51100
Total rules configured: 14
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)switch# show ip access-lists
IP Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmp any any [match 30 packets, 0:02:08 ago]
20 permit ip any any tracked [match 97777 packets, 0:00:00 ago]
30 permit udp any any eq bfd ttl eq 255
40 permit udp any any eq bfd-echo ttl eq 254
50 permit udp any any eq multihop-bfd micro-bfd sbfd
60 permit udp any eq sbfd any eq sbfd-initiator
70 permit ospf any any
80 permit tcp any any eq ssh telnet www snmp bgp https msdp ldp netconf-ssh gnmi [match 72 packets, 0:00:00 ago]
90 permit udp any any eq bootps bootpc snmp rip ntp ldp ptp-event ptp-general
100 permit tcp any any eq mlag ttl eq 255
110 permit udp any any eq mlag ttl eq 255
120 permit vrrp any any
130 permit ahp any any
140 permit pim any any
Total rules configured: 14
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IP Access List ipCountersTest:The ipCountersTest ACL is applied to the data plane. Hence, it displays the byte count information as shown below:
counters per-entry
10 permit tcp host 10.1.1.1 range 2000 4000 host 10.2.1.1 [match 486 bytes in 3 packets, 0:00:26 ago]
20 permit tcp host 10.1.1.1 range 14000 16000 host 10.2.1.1 [match 486 bytes in 3 packets, 0:00:18 ago]
30 permit udp host 10.1.1.1 range 62000 64000 host 10.2.1.1 [match 450 bytes in 3 packets, 0:00:00 ago]
40 permit tcp host 10.1.1.1 range 50000 52000 host 10.2.1.1 [match 486 bytes in 3 packets, 0:00:02 ago]
50 permit tcp host 10.1.1.1 range 38000 40000 host 10.2.1.1 [match 486 bytes in 3 packets, 0:00:10 ago]
60 permit tcp host 10.1.1.1 range 26000 28000 host 10.2.1.1 [match 486 bytes in 3 packets, 0:00:18 ago]
Total rules configured: 6
ipCountersTest ACL applies to the data plane and displays the byte count information.
The deny command adds a deny rule to the configuration mode IPv4 Access Control List (ACL). Interfaces with the ACL drop packets filtered by a deny rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL's last rule.
The no deny and default deny commands remove the specified rule from the configuration mode ACL. The no sequence number (ACLs) command also removes the specified rule from the ACL.
Command Mode
ACL Configuration
Command Syntax
[seq_num] deny protocol source_addr source_port dest_addrR dest_port flags message fragments tracked dscp_filter ttl_filter log
no deny protocol source_addr source_port dest_addrR dest_port flags message fragments tracked dscp_filter ttl_filter log]
default deny protocol source_addr source_port dest_addrR dest_port flags message fragments tracked dscp_filter ttl_filter log]
Subnet addresses support discontiguous masks.
switch(config)# ip access-list text1
switch(config-acl-text1)# deny ospf 10.1.1.0/24 any
switch(config-acl-text1)#switch(config-acl-text1)# 65 deny pim any any
switch(config-acl-text1)#The deny command adds a deny rule to the an IPv6 Access Control List (ACL). Interfaces with the ACL drop packets filtered by a deny rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL's last rule.
The no deny and default deny commands remove the specified rule from the configuration mode ACL. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
IPv6-ACL Configuration
Command Syntax
seq_num deny protocol src_addr source_pt dest_addr dest_pt flag msg hop tracked dscp_filter log
no deny protocol src_addr source_pt dest_addr dest_pt flag msg hop tracked dscp_filter log
default deny protocol src_addr source_pt dest_addr dest_pt flag msg hop tracked dscp_filter log
Example
switch(config)# ipv6 access-list text1
switch(config-acl-text1)# deny ipv6 3710:249a:c643:ef11::/64 any
switch(config-acl-text1)#The deny command adds a deny rule in the IPv6 Prefix List Configuration Mode . Route map match commands use prefix lists to filter routes for redistribution into OSPF, RIP, or BGP domains. Routes are denied access when they match the prefix in a deny statement.
The no deny and default deny commands remove the specified rule from theIPv6 prefix list. The no deny command also removes the specified rule from the prefix list.
Command Mode
IPv6-pfx Configuration
Command Syntax
sequence deny ipv6_prefix mask
Example
switch(config)# ipv6 prefix-list route-five
switch(config-ipv6-pfx)# deny 3100::/64
switch(config-ipv6-pfx)#The deny command adds a deny rule to the MAC Access Control List (ACL) Configuration Mode.
Interfaces with an applied ACL drop packets filtered by a deny rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL last rule.
The no deny and default deny commands remove the specified rule from the MAC Access Control List (ACL) Configuration Mode. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
MAC-ACL Configuration Mode
Command Syntax
seq_num deny source_addr dest_addr [protocol][log]
no deny source_addr dest_addr [protocol][log]
default deny source_addr dest_addr [protocol][log]
switch(config)# mac access-list text1
switch(config-mac-acl-text1)# deny 10.1000.0000 0.0.FFFF any aarpswitch(config-mac-acl-text1)# 25 deny any anyThe deny command adds a deny rule to the Standard IPv4 Access Control List (ACL) Configuration Mode. Standard ACL rules filter on the source field.
Interfaces with an applied ACL drop packets filtered by a deny rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL last rule.
The no deny and default deny commands remove the specified rule from the Standard IPv4 Access Control List (ACL) Configuration Mode. The no sequence number (ACLs) command also removes the specified rule from the ACL.
Command Mode
Std-ACL Configuration
Command Syntax
[seq_num] deny source_addr log
no deny source_addr log
default deny source_addr log
Subnet addresses support noncontinuous masks.
Example
switch(config)# ip access-list standard text1
switch(config-std-acl-text1)# deny 10.1.1.1/24
switch(config-std-acl-text1)#The deny command adds a deny rule to the Standard IPv6 Access Control List (ACL) Configuration Mode. Standard ACL rules filter on the source field.
Interfaces with an applied ACL drop packets filtered by a deny rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL's last rule.
The no deny and default deny commands remove the specified rule from the Standard IPv6 Access Control List (ACL) Configuration Mode. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
Std-IPv6-ACL Configuration
Command Syntax
seq_num deny source_addr
no deny source_addr
default deny source_addr
Example
switch(config)# ipv6 access-list standard text1
switch(config-std-acl-ipv6-text1)# deny 2103::/64
switch(config-std-acl-ipv6-text1)#The description command adds a text string to the configuration mode route map. The string has no functional impact on the route map.
The no description and default description commands remove the text string from the configuration mode route map by deleting the corresponding description command from running-config.
Command Mode
Route-Map Configuration
Command Syntax
description label_text
no description
default description
Parameter
label_text Character string assigned to the route map configuration.
Related Command
Example
switch(config)# route-map XYZ-1
switch(config-route-map-XYZ-1)# description This is the first map.
switch(config-route-map-XYZ-1)# exit
switch(config)# show route-map XYZ-1
route-map XYZ-1 permit 10
Description:
description This is the first map.
Match clauses:
Set clauses:
switch(config)#The hardware access-list resource sharing vlan in command enables the IPv4 Ingress Sharing of hardware resources on the switch when the same ACL applies to different VLANs.
The no hardware access-list resource sharing vlan in command disables the IPv4 Ingress Sharing of hardware resources on the switch.
Command Mode
Global Configuration
Command Syntax
hardware access-list resource sharing vlan [ipv4 | ipv6] in
no hardware access-list resource sharing vlan in
Use the show platform trident command to verify the Ingress IPv4 Sharing information.
The hardware access-list resource sharing vlan ipv4 out command enables IPv4 Egress RACL TCAM sharing on the switch.
The no hardware access-list resource sharing vlan ipv4 out command disables the IPv4 Egress RACL TCAM sharing on the switch. By default, the switch enables IPv4 Egress RACL sharing.
Command Mode
Global Configuration
Command Syntax
hardware access-list resource sharing vlan ipv4 out
no hardware access-list resource sharing vlan ipv4 out
Example
switch# show running-config all | include sharing
hardware access-list resource sharing vlan ipv4 out
---->It returns the following output if IPv4 RACL sharing is enabled.The hardware access-list update default-result permit command configures the switch to permit all traffic on Ethernet and VLAN interfaces with ACLs applied to them while modifying the ACLs. Permits traffic when modifying the ACL using one of the ip access-list commands, and ends when exiting the ACL Configuration Mode and rules populated in hardware. EOS disables this by default.
The no hardware access-list update default-result permit and default hardware access-list update default-result permit commands restore the switch to the default state and blocks traffic during ACL modifications by removing the corresponding hardware access-list update default-result permit command from the running-config.
Command Mode
Global Configuration
Command Syntax
hardware access-list update default-result permit
no hardware access-list update default-result permit
default hardware access-list update default-result permit
Restrictions
This command is available on the Arista 7050X, 7060X, 7150, 7250X, 7280, 7280R, 7300X, 7320X, and 7500 series switches.
When enabled, static NAT, and ACL-based mirroring are affected during ACL updates.
Example
switch(config)# hardware access-list update default-result permit
switch(config)#The hardware counter feature acl out command enables egress ACL hardware counters for IPv4 or IPv6 and count the number of packets matching rules associated with egress ACLs applied to various interfaces on a switch.
The no hardware counter feature acl out and default hardware counter feature acl out commands disable or return the egress ACL hardware counters to the default state.
Command Mode
Global Configuration
Command Syntax
hardware counter feature acl out [options [ipv4 | ipv6]
no hardware counter feature acl out [options [ipv4 | ipv6]
default hardware counter feature acl out [options [ipv4 | ipv6]
switch(config)# hardware counter feature acl out ipv4
switch(config)#switch(config)# no hardware counter feature acl out ipv4
switch(config)#The ip access-group (Service ACLs) command configures a Service ACL to apply to a control-plane service. Specify the service by the command mode used to apply the Service ACL.
The no ip access-group and default ip access-group commands remove the corresponding ip access-group (Service ACLs) command from running-config.
Command Mode
Mgmt-SSH Configuration
Mgmt-API Configuration
Router-BGP Configuration
Router-OSPF Configuration
Router-IGMP Configuration
MPLS-LDP Configuration
Queue-Monitor-Streaming Configuration
MPLS-Ping Configuration
Mgmt-Telnet Configuration
Command Syntax
ip access-group acl_name [vrfvrf_name][in]
no ip access-group acl_name [vrfvrf_name][in]
default ip access-group acl_name [vrfvrf_name][in]
Parameters
Example
(config)# router bgp 5
(config-router-bgp)# vrf purple
(config-router-bgp-vrf-purple)# ip access-group bgpaclFor additional configuration examples, see Configuring Service ACLs and Displaying Status and Counters.
The ip access-group command applies an IPv4 or standard IPv4 Access Control List (ACL) to an interface or subinterface in the Interface Configuration Mode.
The no ip access-group and default ip access-group commands remove the corresponding ip access-group command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
ip access-group list_name[direction [in | out]]
no ip access-group list_name[direction [in | out]]
default ip access-group list_name [direction [in | out]]
Considerations
Filtering of outbound packets by ACLs not supported on Petra platform switches.
Filtering of outbound packets by ACLs on FM6000 switches supported on physical interfaces only (Ethernet and port channels).
ACLs on sub-interfaces are supported on DCS-7280E, DCS-7500E, DCS-7280R, and DCS-7500R.
Example
switch(config)# interface ethernet 3
switch(config-if-Et3)# ip access-group test2 in
switch(config-if-Et3)#The ip access-list command places the switch in ACL Configuration Mode, a group change mode that modifies an IPv4 access control list. The command specifies the name of the IPv4 ACL that subsequent commands modify and creates an ACL if it references a nonexistent list. All changes in a group change mode edit session are pending until the end of the session.
The exit command saves pending ACL changes to running-config, then returns the switch to Global Configuration Mode. ACL changes are also saved by entering a different configuration mode.
The abort command discards pending ACL changes, returning the switch to Global Configuration Mode.
The no ip access-list and default ip access-list commands delete the specified IPv4 ACL.
Command Mode
Global Configuration
Command Syntax
ip access-list list_name
no ip access-list list_name
default ip access-list list_name
Parameter
list_name - Specify the name of the ACL. Must begin with an alphabetic character. Cannot contain spaces or quotation marks.
switch(config)# ip access-list filter1
switch(config-acl-filter1)#switch(config-acl-filter1)# exit
switch(config)#switch(config-acl-filter1)# abort
switch(config)#The ip access-list standard command places the switch in STD-ACL Configuration Mode, a group change mode that modifies a standard IPv4 access control list. The command specifies the name of the standard IPv4 ACL that subsequent commands modify, and creates an ACL if it references a nonexistent list. All group change mode edit session changes are pending until the session ends.
The exit command saves pending ACL changes to running-config, then returns the switch to Global Configuration Mode. Pending changes are also saved by entering a different configuration mode.
The abort command discards pending ACL changes, returning the switch to global configuration mode.
The no ip access-list standard and default ip access-list standard commands delete the specified ACL.
Command Mode
Global Configuration
Command Syntax
ip access-list standard list_name
no ip access-list standard list_name
default ip access-list standard list_name
Parameter
list_name - Specify the name of standard ACL. Must begin with an alphabetic character. Cannot contain spaces or quotation marks.
switch(config)# ip access-list standard filter2
switch(config-std-acl-filter2)#switch(config-std-acl-filter2)# exit
switch(config)#switch(config-std-acl-filter2)# abort
switch(config)#The ip prefix-list command creates a prefix list or adds an entry to an existing list. Route map match commands use prefix lists to filter routes for redistribution into OSPF, RIP, or BGP domains.
A prefix list comprises all prefix list entries with the same label. The sequence numbers of the rules in a prefix list specify the order for applying rules to a route evaluated by the match command.
The no ip prefix-list and default ip prefix-list commands delete the specified prefix list entry by removing the corresponding ip prefix-list statement from running-config. If the no or default ip prefix-list command does not list a sequence number, the command deletes all entries of the prefix list.
Command Mode
Global Configuration
Command Syntax
ip prefix-list list_name [deny | permit] [seq index] network_addr [mask] resequence seq_number remark comment
no ip prefix-list list_name seq [index]
default ip prefix-list list_name seq [index]
switch(config)# ip prefix-list route-one
switch(config-ip-pfx)#switch(config)# ip prefix-list route-one
switch(config-ip-pfx)# seq 10 deny 10.1.1.0/24
switch(config-ip-pfx)# seq 20 deny 10.1.0.0/16
switch(config-ip-pfx)# seq 30 permit 12.15.4.9/32
switch(config-ip-pfx)# seq 40 deny 1.1.1.0/24The ipv6 access-groupcommand applies an IPv6 or standard IPv6 Access Control List (ACL) to the configuration mode interface.
The no ipv6 access-group and default ipv6 access-group commands remove the corresponding ipv6 access-group command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
ipv6 access-group list_name [in | out]
no ipv6 access-group list_name [in | out]
default ipv6 access-group list_name [in | out]
Examples
switch(config)# interface ethernet 3
switch(config-if-Et3)# ipv6 access-group test2 in
switch(config-if-Et3)#The ipv6 access-group (Service ACLs) command configures an IPv6 or standard IPv6 Service ACL to be applied by a control-plane service. Specify the service with the command mode to apply the Service ACL.
The no ipv6 access-group (Service ACLs) and default ipv6 access-group (Service ACLs) commands remove the corresponding ipv6 access-group (Service ACLs) command from running-config.
Command Mode
Mgmt-SSH Configuration
Mgmt-API Configuration
Router-BGP Configuration
Router-OSPF Configuration
MPLS-LDP Configuration
Queue-Monitor-Streaming Configuration
MPLS-Ping Configuration
Mgmt-Telnet Configuration
Command Syntax
ipv6 access-group ipv6_acl_name [vrf vrf_name][in]
no ipv6 access-group [ipv6_acl_name][vrfvrf_name][in]
default ipv6 access-group ipv6_acl_name [vrf vrf_name][in]
Parameters
Example
(config)# router bgp 5
(config-router-bgp)# vrf purple
(config-router-bgp-vrf-purple)# ipv6 access-group bgpaclFor additional configuration examples, see Configuring Service ACLs and Displaying Status and Counters.
The ipv6 access-list command places the switch in IPv6-ACL Configuration Mode, a group change mode that modifies an IPv6 access control list. The command specifies the name of the IPv6 ACL that subsequent commands modify and creates an ACL if it references a nonexistent list. All changes in a group change mode edit session pend until the end of the session.
The exit command saves pending ACL changes to running-config, then returns the switch to global configuration mode. ACL changes are also saved by entering a different configuration mode.
The abort command discards pending ACL changes, returning the switch to Global Configuration Mode.
The no ipv6 access-list and default ipv6 access-list commands delete the specified IPv6 ACL.
Command Mode
Global Configuration
Command Syntax
ipv6 access-list list_name
no ipv6 access-list list_name
default ipv6 access-list list_name
Parameters
list_name - Specify a name for the ACL. Must begin with an alphabetic character and cannot contain spaces or quotation marks.
switch(config)# ipv6 access-list filter1
switch(config-ipv6-acl-filter1)#switch(config-ipv6-acl-filter1)# exit
switch(config)#switch(config-ipv6-acl-filter1)# abort
switch(config)#The ipv6 access-list standard command places the switch in std-IPv6-ACL-configuration mode, a group change mode that modifies a standard IPv6 access control list. The command specifies the name of the standard IPv6 ACL that subsequent commands modify and creates an ACL if it references a nonexistent list. All group change mode edit session changes are pending until the session ends.
The exit command saves pending ACL changes to running-config, then returns the switch to Global Configuration Mode. Pending changes are also saved by entering a different configuration mode.
The abort command discards pending ACL changes, returning the switch to global configuration mode.
The no ipv6 access-list standard and default ipv6 access-list standard commands delete the specified ACL.
Command Mode
Global Configuration
Command Syntax
ipv6 access-list standard list_name
no ipv6 access-list standard list_name
default ipv6 access-list standard list_name
Parameters
list_name - Specify a name for the ACL. Must begin with an alphabetic character and cannot contain spaces or quotation marks.
switch(config)# ipv6 access-list standard filter2
switch(config-std-ipv6-acl-filter2)#switch(config-std-ipv6-acl-filter2)# exit
switch(config)#switch(config-std-ipv6-acl-filter2)# abort
switch(config)#The ip prefix-list command places the switch in IPv6 prefix-list configuration mode, which is a group change mode that modifies an IPv6 prefix list. The command specifies the name of the IPv6 prefix list that subsequent commands modify and creates a prefix list if it references a nonexistent list. All changes in a group change mode edit session are pending until the end of the session.
The exit command saves pending prefix list changes to running-config, then returns the switch to global configuration mode. ACL changes are also saved by entering a different configuration mode.
The abort command discards pending changes, returning the switch to global configuration mode.
The no ipv6 prefix-list and default ipv6 prefix-list commands delete the specified IPv6 prefix list.
Command Mode
Global Configuration
Command Syntax
ipv6 prefix-list list_name
no ipv6 prefix-list list_name
default ipv6 prefix-list list_name
Parameter
list_name Name of prefix list. Must begin with an alphabetic character. Cannot contain spaces or quotation marks.
switch(config)# ipv6 prefix-list route-five
switch(config-ipv6-pfx)#switch(config-ipv6-pfx)# exit
switch(config)#switch(config-ipv6-pfx)# interface ethernet 3
switch(config-if-Et3)#switch(config-ipv6-pfx)# abort
switch(config)#The mac access-group command applies a MAC Access Control List (MAC ACL) when in the Interface Configuration Mode.
The no mac access-group and default mac access-group commands remove the specified mac access-group command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
mac access-group list_name [direction [in | out]]
no mac access-group list_name[direction [in | out]]
default mac access-group list_name [direction [in | out]]
Restrictions
Only Helix, Trident, and Trident II platform switches support filtering of outbound packets by MAC ACLs.
Example
switch(config)# interface ethernet 3
switch(config-if-Et3)# mac access-group mtest2 in
switch(config-if-Et3)#The mac access-list command places the switch in MAC-ACL Configuration Mode, a group change mode that modifies a MAC access control list. The command specifies the name of the MAC ACL that subsequent commands modify and creates an ACL if it references a nonexistent list. All changes in a group change mode edit session are pending until the end of the session.
The exit command saves pending ACL changes to running-config, then returns the switch to Global Configuration Mode. ACL changes are also saved by entering a different configuration mode.
The abort command discards pending ACL changes, returning the switch to Global Configuration Mode.
The no mac access-list and default mac access-list commands delete the specified list.
Command Mode
Global Configuration
Command Syntax
mac access-list list_name
no mac access-list list_name
default mac access-list list_name
Parameter
list_name - Specify the name of the MAC ACL. Names must begin with an alphabetic character and cannot contain a space or quotation mark.
switch(config)# mac access-list mfilter1
switch(config-mac-acl-mfilter1)#switch(config-mac-acl-mfilter1)# exit
switch(config)#switch(config-mac-acl-mfilter1)# interface ethernet 3
switch(config-if-Et3)#switch(config-mac-acl-mfilter1)# abort
switch(config)#The match command creates a route map statement entry that specifies one route filtering command. When a statement contains multiple match commands, the permit or deny filter applies to a route only if the properties equal the corresponding parameters in each match command. When a route properties do not equal the command parameters, the route is evaluated against the next statement in the route map, as determined by sequence number. If all statements fail to permit or deny the route, the route is denied.
The no match and default match commands remove the match command from the configuration mode route map statement by deleting the corresponding command from running-config.
Command Mode
Route-Map Configuration
Command Syntax
match condition
no match condition
default match condition
Related Command
Examples
switch(config)# route-map map1
switch(config-route-map-map1)# match as 15
switch(config-route-map-map1)#switch(config-route-map-map1)# match as-path length <= 300
switch(config-route-map-map1)#The no sequence number command removes the rule with the specified sequence number from the ACL. The default sequence number command also removes the specified rule.
Command Mode
ACL Configuration
IPv6-ACL Configuration
Std-ACL Configuration
Std-IPv6-ACL Configuration
MAC-ACL Configuration
Command Syntax
no line_num
default line_num
Parameter
line_num - Specify the sequence number of rule to delete. Values range from 1 - 4294967295.
Example
switch(config-acl-test1)# show IP Access Lists test1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of list
Total rules configured: 5
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
switch(config-acl-test1)# no 30
switch(config-acl-test1)# show IP Access Lists
20 permit ip any host 10.20.10.1
40 permit ip any any
50 remark end of list
Total rules configured: 4
Configured on Ingress: Et1/1
Active on Ingress: Et1/1The permit command adds a permit rule to the configuration mode IPv4 Access Control List (ACL). Interfaces with the applied ACL accept packets filtered by a permit rule the ACL is applied. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL last rule.
The no permit and default permit commands remove the specified rule from the configuration mode ACL. The no <sequence number> (ACLs) command also removes a specified rule from the ACL.
Command Mode
ACL Configuration
Command Syntax
seq_num permit protocol src_addr source_pt dest_addr dest_pt flags msg fragments tracked dscp_filter ttl_filter log
no permit protocol src_addr source_pt dest_addr dest_pt flags msg fragments tracked dscp_filter ttl_filter log
default permit protocol src_addr source_pt dest_addr dest_pt flags msg fragments tracked dscp_filter ttl_filter log
Commands use a subset of the listed fields and available parameters depend on specified protocol.
Source and destination subnet addresses support discontiguous masks.
switch(config)# ip access-list text1
switch(config-acl-text1)# permit ospf 10.1.1.0/24 any
switch(config-acl-text1)#switch(config-acl-text1)# 25 permit pim any any
switch(config-acl-text1)#switch(config)# ip access-list acl1
switch(config-acl-acl1)# permit vlan 1234 0x0 ip any anyThe permit command adds a permit rule to the configuration mode IPv6 Access Control List (ACL). Interfaces with the applied ACL accept packets filtered by a permit rule the ACL is applied. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL last rule.
The no permit and default permit commands remove the specified rule from the configuration mode ACL. The no <sequence number> (ACLs) command also removes a specified rule from the ACL.
Command Mode
IPv6-ACL Configuration
Command Syntax
seq_num permit protocol src_addr source_pt dest_addr dest_pt flags msg hop tracked dscp_filter log
no permit protocol src_addr source_pt dest_addr dest_pt flag msg hop tracked dscp_filter log
default deny protocol src_addr source_pt dest_addr dest_pt flag msg hop tracked dscp_filter log
switch(config)# ipv6 access-list acl1
switch(config-acl-acl1)# permit ipv6 3710:249a:c643:ef11::/64 any
switch(config-acl-acl1)# exit
switch(config)#switch(config)# ip access-list acl2
switch(config-acl-acl2)# permit ipv6 vlan 1234 0x0 ip any any
switch(config-acl-acl2)# exit
switch(config)#switch(config)# ipv6 access-list acl3
switch(config-acl-acl3)# permit ipv6 any any flow-label eq 23
switch(config-acl-acl3)# exit
switch(config)#switch(config)# ipv6 access-list acl4
switch(config-acl-acl4)# permit ipv6 any any flow-label 23 0x5678
switch(config-acl-acl4)# exit
switch(config)#The permit command adds a rule to the configuration mode IPv6 prefix list. Route map match commands use prefix lists to filter routes for redistribution into OSPF, RIP, or BGP domains. Routes are redistributed into the specified domain when they match the prefix that a permit statement specifies.
The no permit and default permit commands remove the specified rule from the prefix list. The no seq (IPv6 Prefix Lists) command also removes the specified rule from the prefix list.
Command Mode
IPv6-pfx Configuration
Command Syntax
seq_num permit ipv6_prefix mask
Example
switch(config)# ipv6 prefix-list route-five
switch(config-ipv6-pfx)# permit 3100::/64
switch(config-ipv6-pfx)#The permit command adds a permit rule to the configuration mode MAC access control list packets through the interface to which the list is applied. Rule filters include protocol, source, and destination.
The no permit and default permit commands remove the specified rule from the configuration mode ACL. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
MAC-ACL Configuration
Command Syntax
seq_num permit source_addr dest_addr protocol log
no permit source_addr dest_addr protocol log
default permit source_addr dest_addr protocol log
mac_address - Specifies a MAC address in 3x4 dotted hexadecimal notation (hhhh.hhhh.hhhh).
switch(config)# mac access-list text1
switch(config-mac-acl-text1)# permit 10.1000.0000 0.0.FFFF any aarp
switch(config-mac-acl-text1)#switch(config-mac-acl-text1)# 25 permit any any
switch(config-mac-acl-text1)#The permit command adds a permit rule to a standard IPv4 Access Control List (ACL). Standard ACL rules filter on the source field.
Interfaces with the applied ACL accept packets filtered by a permit rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL's last rule..
The no permit and default permit commands remove the specified rule from the ACL. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
Std-ACL Configuration
Command Syntax
[seq_num] permit [ source_addr network_addr [any | host] [log]
no permit [ source_addr network_addr [any | host] [log]
default permit [ source_addr network_addr [any | host][log]
Subnet addresses support discontiguous masks.
Example
switch(config)# ip access-list standard text1
switch(config-std-acl-text1)# permit 10.1.1.1/24
switch(config-std-acl-text1)#The permit command adds a permit rule to the standard IPv6 access control list. Standard ACL rules filter on the source field.
Interfaces with the applied ACL accept packets filtered by a permit rule. Sequence numbers determine rule placement in the ACL. Sequence numbers for commands without numbers derive from adding 10 to the number of the ACL's last rule.
The no permit and default permit commands remove the specified rule from the configuration mode ACL. The no <sequence number> (ACLs) command also removes the specified rule from the ACL.
Command Mode
Std-IPv6-ACL Configuration
Command Syntax
[seq_num] permit source_addr
no permit source_addr
default permit source_addr
Example
switch(config)# ipv6 access-list standard text1
switch(config-std-acl-ipv6-text1)# permit 2103::/64
switch(config-std-acl-ipv6-text1)#The remark command adds a non-executable comment statement into the pending ACL. Remarks entered without a sequence number are appended to the end of the list. Remarks with a sequence number insert into the list as specified by the sequence number.
The default remark command removes the comment statement from the ACL.
The no remark command removes the comment statement from the ACL. The command can specify the remark by content or by sequence number.
Command Mode
ACL Configuration
IPv6-ACL Configuration
Std-ACL Configuration
Std-IPv6-ACL Configuration
MAC-ACL Configuration
Command Syntax
remark text
line_num remark [text]
no remark text
default remark text
Example
switch(config-acl-test1)# remark end of list
switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of listThe resequence command assigns sequence numbers to rules in the configuration mode ACL. Command parameters specify the number of the first rule and the numeric interval between consecutive rules.
Maximum rule sequence number is 4294967295.
Command Mode
ACL Configuration
IPv6-ACL Configuration
Std-ACL Configuration
Std-IPv6-ACL Configuration
MAC-ACL Configuration
Command Syntax
resequence [start_num [inc_num]]
Example
switch(config-acl-test1)# show
IP Access List test1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of list
switch(config-acl-test1)# resequence 100 20
switch(config-acl-test1)# show
IP Access List test1
100 permit ip 10.10.10.0/24 any
120 permit ip any host 10.20.10.1
140 deny ip host 10.10.10.1 host 10.20.10.1
160 permit ip any any
180 remark end of listThe route-map command places the switch in Route-Map Configuration Mode, a group change mode that modifies a route map statement. The command specifies the name and number of the route map statement that subsequent commands modify and creates a route map statement if it references a nonexistent statement. All changes in a group change mode edit session pend until the end of the session.
Route maps define commands for redistributing routes between routing protocols. Use names, filter type (permit or deny), and sequence number to identify a route map statement. Statements with the same name are components of a single route map, and the sequence number determines the order in which the statements compare to a route.
The exit command saves pending route map statement changes to running-config, then returns the switch to global configuration mode. Also, save ACL changes by entering a different configuration mode.
The abort command discards pending changes, returning the switch to global configuration mode.
The no route-map and default route-map commands delete the specified route map statement from running-config.
Command Mode
Global Configuration
Command Syntax
route-map map_name [filter_type] [sequence_number]
no route-map map_name [filter_type] [sequence_number]
default route-map map_name [filter_type][sequence_number]
switch(config)# route-map map1 permit 20
switch(config-route-map-map1)#switch(config-route-map-map1)# exit
switch(config)#switch(config-route-map-map1)# interface ethernet 3
switch(config-if-Et3)#switch(config-route-map-map1)# abort
switch(config)#The no seq command removes the rule with the specified sequence number from the ACL. The default seq command also removes the specified rule.
The seq keyword provides a command option used at the beginning of deny (IPv6 Prefix List) and permit (IPv6 Prefix List) commands that places a new rule between two existing rules.
Command Mode
IPv6-pfx Configuration
Command Syntax
no seq line_num
default seq line_num
Parameter
line_num - Specify the sequence number of rule to delete. Valid rule numbers range from 0 to 65535.
Example
switch(config)# ipv6 prefix-list map1
switch(config-ipv6-pfx)# no seq 20
switch(config-ipv6-pfx)# exit
switch(config)# show ipv6 prefix-list map1
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 15 deny 3:4400::/64
seq 30 permit 3:1bca:3ff2:634a::/64
seq 40 permit 3:1bca:1141:ab34::/64
switch(config)#The set command specifies modifications to routes selected for redistribution by the Route-Map Configuration Mode.
The no set and default set commands remove the specified set command from the Route-Map Configuration Mode statement by deleting the corresponding set command from running-config.
Command Mode
Route-Map Configuration
Command Syntax
set condition [as-path prepend [num | auto]]
no set condition [as-path prepend [num | auto]]
default set condition[as-path prepend [num | auto]]
Example
switch(config)# route-map map1
switch(config-route-map-map1)# set local-preference 100
switch(config-route-map-map1)#The set as-path match command configures the as_path attribute for prefixes either received from a BGP neighbor or advertised to a BGP neighbor in the Route-Map Configuration Mode.
The no set as-path match command removes the AS path specified for the BGP prefix.
Command Mode
Route-Map Configuration
Command Syntax
set as-path match [all replacement [none| auto]] as_path
set as-path match[all replacement [none| auto]] as_path
switch# show ip bgp neighbors 80.80.1.2 advertised-routes
BGP routing table information for VRF default
Router identifier 202.202.1.1, local AS number 200
Route status codes: s - suppressed, * - valid, > - active, # - not installed, E
- ECMP head, e - ECMP
S - Stale, c - Contributing to ECMP, b - backup, L - labeled-unicast, q - Queued
for advertisement
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop -
Link Local Nexthop
Network Next Hop Metric LocPref Weight Path
* > 101.101.1.0/24 80.80.1.1 - - - 200 i
* > 102.102.1.0/24 80.80.1.1 - - - 200 i
* > 103.103.1.0/24 80.80.1.1 - - - 200 302 i
* > 202.202.1.0/24 80.80.1.1 - - - 200 i
switch# configure terminal
switch(config)# route-map foo permit 10
switch(config-route-map-foo)# set as-path match all replacement none
switch(config-route-map-foo)# exit
switch(config)# router bgp 200
switch(config-router-bgp)# neighbor 80.80.1.2 route-map foo out
switch(config-router-bgp)# end
switch# show ip bgp neighbors 80.80.1.2 advertised-routes
BGP routing table information for VRF default
Router identifier 202.202.1.1, local AS number 200
Route status codes: s - suppressed, * - valid, > - active, # - not installed, E
- ECMP head, e - ECMP
S - Stale, c - Contributing to ECMP, b - backup, L - labeled-unicast, q - Queued
for advertisement
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop -
Link Local Nexthop
Network Next Hop Metric LocPref Weight Path
* > 101.101.1.0/24 80.80.1.1 - - - 200 i
* > 102.102.1.0/24 80.80.1.1 - - - 200 i
* > 103.103.1.0/24 80.80.1.1 - - - 200 i
* > 202.202.1.0/24 80.80.1.1 - - - 200 iswitch(config)# route-map foo permit 10
switch(config-route-map-foo)# set as-path match all replacement auto
switch(config-route-map-foo)# end
switch# show ip bgp neighbors 80.80.1.2 advertised-routes
BGP routing table information for VRF default
Router identifier 202.202.1.1, local AS number 200
Route status codes: s - suppressed, * - valid, > - active, # - not installed, E
- ECMP head, e - ECMP
S - Stale, c - Contributing to ECMP, b - backup, L - labeled-unicast, q - Queued
for advertisement
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop -
Link Local Nexthop
Network Next Hop Metric LocPref Weight Path
* > 101.101.1.0/24 80.80.1.1 - - - 200 200 i
* > 102.102.1.0/24 80.80.1.1 - - - 200 200 i
* > 103.103.1.0/24 80.80.1.1 - - - 200 200 i
* > 202.202.1.0/24 80.80.1.1 - - - 200 200 iReplaces the AS-Path of matching prefixes with the locally configured AS 200.
switch(config)# route-map foo permit 10
switch(config-route-map-foo)# set as-path match all replacement 500 600
switch(config-route-map-foo)# end
switch# show ip bgp neighbors 80.80.1.2 advertised-routes
BGP routing table information for VRF default
Router identifier 202.202.1.1, local AS number 200
Route status codes: s - suppressed, * - valid, > - active, # - not installed, E
- ECMP head, e - ECMP
S - Stale, c - Contributing to ECMP, b - backup, L - labeled-unicast, q - Queued
for advertisement
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop -
Link Local Nexthop
Network Next Hop Metric LocPref Weight Path
* > 101.101.1.0/24 80.80.1.1 - - - 200 500 600 i
* > 102.102.1.0/24 80.80.1.1 - - - 200 500 600 i
* > 103.103.1.0/24 80.80.1.1 - - - 200 500 600 i
* > 202.202.1.0/24 80.80.1.1 - - - 200 500 600 iReplaces the AS-Path of matching prefixes with 500 600 as configured.
switch(config)# route-map foo permit 10
switch(config-route-map-foo)# set as-path match all replacement auto 500 600
switch(config-route-map-foo)# end
switch# show ip bgp neighbors 80.80.1.2 advertised-routes
BGP routing table information for VRF default
Router identifier 202.202.1.1, local AS number 200
Route status codes: s - suppressed, * - valid, > - active, # - not installed, E
- ECMP head, e - ECMP
S - Stale, c - Contributing to ECMP, b - backup, L - labeled-unicast, q - Queued
for advertisement
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop -
Link Local Nexthop
Network Next Hop Metric LocPref Weight Path
* > 101.101.1.0/24 80.80.1.1 - - - 200 200 500 600 i
* > 102.102.1.0/24 80.80.1.1 - - - 200 200 500 600 i
* > 103.103.1.0/24 80.80.1.1 - - - 200 200 500 600 i
* > 202.202.1.0/24 80.80.1.1 - - - 200 200 500 600 iReplaces the AS-Path of matching prefixes with the locally configured AS 200 and 500 600.
The set as-path prepend command adds a set statement to a route map to prepend one or more Autonomous System (AS) numbers to the as_path attribute of a BGP route.
The no set as-path prepend and default set as-path prepend commands remove the specified set statements from the route map and update all corresponding routes.
Command Mode
Route-Map Configuration
Command Syntax
set as-path prepend auto | as_number [auto | as_number | last-as count]
no set as-path prepend auto | as_number [auto | as_number | last-as count]
default set as-path prepend auto | as_number [auto | as_number | last-as count]
switch(config)# route-map map1
switch(config-route-map-map1)# set as-path prepend 64496 auto auto
switch(config-route-map-map1)# exit
switch(config)# show route-map map1
route-map map1 permit 10
Description:
Match clauses:
SubRouteMap:
Set clauses:
set as-path prepend 64496 auto auto
switch(config)#switch(config)# route-map map2
switch(config-route-map-map2)# set as-path prepend 64496 64498 1.16
switch(config-route-map-map2)# exit
switch(config)# show route-map map2
route-map map2 permit 10
Description:
Match clauses:
SubRouteMap:
Set clauses:
set as-path prepend 64496 64498 65552
switch(config)#switch(config)# route-map map3
switch(config-route-map-map3)# set as-path prepend last-as 12
switch(config-route-map-map3)# exit
switch(config)# show route-map map3
route-map map3 permit 10
Description:
Match clauses:
SubRouteMap:
Set clauses:
set as-path prepend last-as 12
switch(config)#The set community command specifies community attribute modifications to routes selected for redistribution. The set community none command removes community attributes from the route.
The no set community and default set community commands remove the specified community from the Route-Map Configuration Modestatement by deleting the corresponding statement from the running config.
Command Mode
Route-Map Configuration
Command Syntax
set community [gshut | aa:nn | community-list | internet | local-as | no-advertise | no-export | none | number]
no set community [gshut | aa:nn | additive | community-list | delete | internet | local-as | no-advertise | no-export | none | number]
default set community [gshut | aa:nn | additive | community-list | delete | internet | local-as | no-advertise | no-export | none | number]
Guideline
EOS does not support disabling the process of graceful shutdown community.
Example
switch(config-route-map-map1)# show active
route-map map1 permit 10
match community instances <= 50
set community 0:456 0:2345
switch(config-route-map-map1)# set community local-as
switch(config-route-map-map1)# ip community-list 345 permit 23
switch(config)# route-map map1
switch(config-route-map-map1)# show active
route-map map1 permit 10
match community instances <= 50
set community 0:456 0:2345 local-as
switch(config-route-map-map1)#The set extcommunity command specifies extended community attribute modifications to routes selected for redistribution. The set extcommunity none command removes extended community attributes from the route.
The no set extcommunity and default set extcommunity commands remove the specified set extcommunity command from the Route-Map Configuration Mode statement by deleting the corresponding statement from running-config.
Command Mode
Route-Map Configuration Mode
Command Syntax
set extcommunity cond_x [cond_2][cond_n][mod_type]
set extcommunity none
no set extcommunitycond_x [cond_2][cond_n][mod_type]
default set extcommunity cond_x [cond_2][cond_n][mod_type]
default set extcommunity none
Example
switch(config)# route-map map1
switch(config-route-map-map1)# set extcommunity rt 10.13.2.4:100
switch(config-route-map-map1)#Exiting the ACL configuration mode stores all pending ACL changes to running-config.
Command Mode
ACL Configuration
IPv6-ACL Configuration
Std-ACL Configuration
Std-IPv6-ACL Configuration
MAC-ACL Configuration
Command Syntax
show
show active
show comment
show diff
show pending
Examples
The examples in this section assume these ACL commands are entered as specified.
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.21.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of list20 permit ip any host 10.21.10.120 permit ip 10.10.0.0/16 any
25 permit tcp 10.10.20.0/24 any
45 deny pim 239.24.124.0/24 10.5.8.4/30switch(config-acl-test_1)# show active
IP Access List test_1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.21.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
50 remark end of listswitch(config-acl-test_1)# show pending
IP Access List test_1
10 permit ip 10.10.10.0/24 any
20 permit ip 10.10.0.0/16 any
25 permit tcp 10.10.20.0/24 any
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
45 deny pim 239.24.124.0/24 10.5.8.4/30
50 remark end of listswitch(config-acl-test_1)# show diff
---
+++
@@ -1,7 +1,9 @@
IP Access List test_1
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.21.10.1
20 permit ip 10.10.0.0/16 any
25 permit tcp 10.10.20.0/24 any
30 deny ip host 10.10.10.1 host 10.20.10.1
40 permit ip any any
45 deny pim 239.24.124.0/24 10.5.8.4/30The show hardware tcam profile command displays the hardware specific information for the current operational TCAM profile in the running configuration.
This command is applicable to DCS-7280(E/R) and DCS-7500(E/R) series switches only.
Command Mode
EXEC
Command Syntax
show hardware tcam profile [[profileName [[feature featureName] detail]]|[detail]
Guidelines
If the profile cannot be programmed, the Status column will print ‘ERROR‘. Any features that use TCAM functionality will not work properly. Do not expect any features to work if the profile is in the ‘ERROR’ state. If there are warnings or errors, a summary message will display warnings or errors found in programming the profile in addition to the system log messages.
switch(config)# show hardware tcam profile
Configuration Status
FixedSystem testprofile testprofile(config)# show hardware tcam profile
Configuration Status
Linecard3 newprofile1 ERROR
Linecard4 newprofile1 ERROR Linecard5 newprofile1 ERROR
Linecard6 newprofile1 ERROR
Linecard7 newprofile1 WARNING
Detailed Programming Status
Linecard3, Linecard4, Linecard5
[Error] feature flow is not supported on this hardware platform
Linecard7
[Warning] the key size of feature flow exceeds the configured key size limitswitch(config-hw-tcam)# show hardware tcam profile myprofile detail
Profile myprofile [ FixedSystem ]
Feature: acl port ip egress
Key size: 320
Key Fields: dscp, dst-ip, ip-frag, ip-protocol, l4-dst-port,
l4-src-port, src-ip
Feature: acl port ip ingress
Key size: 320
Key Fields: dscp, dst-ip, ip-frag, ip-protocol, l4-dst-port, l4-ops,
l4-src-port, src-ip, tcp-control, ttl
Feature: acl port ipv6 egress
Key size: 320
Key Fields: dst-ipv6, ip-protocol, ipv6-next-header,
ipv6-traffic-class, l4-dst-port, l4-src-port, src-ipv6,
tcp-control, ttl
Feature: acl port ipv6 ingress
Key size: 320
Key Fields: dst-ipv6, ip-protocol, ipv6-next-header,
ipv6-traffic-class, l4-dst-port, l4-ops, l4-src-port,
src-ipv6, tcp-control, ttl
Feature: acl port ipv6 source-only egress
Key size: 320
Key Fields: ip-protocol, src-ipv6
Feature: acl port mac egress
Key size: 320
Key Fields: dst-mac, ether-type, src-mac
...(config-hw-tcam-profile-newfeature)# show hardware tcam profile default
Features enabled in TCAM profile default: [ Linecard3, Linecard4, Linecard6, Linecard
7, Linecard8, Linecard9, Linecard10 ]
mpls
acl vlan ipv6
acl subintf ipv6
acl vlan ipv6 egress
acl port ipv6
pbr ipv6
acl vlan ip
acl subintf ip
acl port ip
tunnel vxlan
acl port mac
pbr ip
pbr mpls
qos ipv6
qos ip
mirror ip
counter lfib
mpls pop ingressThe show access-lists command displays the contents of all IPv4, IPv6, and MAC Access Control Lists (ACLs) on the switch in addition to the configuration and status. Use the summary option to display only the configuration and status, which contains details such as the name of the ACL, total rules configured, configured and active status containing interface information, and supplicant information as in the case of dynamic ACLs from dot1x sessions.
Command Mode
Privileged EXEC
Command Syntax
show access-lists[interface interface_acl] | [acl_name acl_name] acl_name | [scope summary]
Parameters
switch# show access-lists
Phone ACL bypass: disabled
IP Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmp any any
20 permit ip any any tracked [match 149061 bytes in 1721 packets, 0:00:00 ago]
30 permit udp any any eq bfd ttl eq 255
40 permit udp any any eq bfd-echo ttl eq 254
50 permit udp any any eq multihop-bfd micro-bfd sbfd
60 permit udp any eq sbfd any eq sbfd-initiator
70 permit ospf any any
80 permit tcp any any eq ssh telnet www snmp bgp https msdp ldp netconf-ssh gnmi [match 180 bytes in 3 packets, 0:03:08 ago]
90 permit udp any any eq bootps bootpc snmp rip ntp ldp ptp-event ptp-general [match 984 bytes in 3 packets, 1 day, 9:02:21 ago]
100 permit tcp any any eq mlag ttl eq 255
110 permit udp any any eq mlag ttl eq 255
120 permit vrrp any any
130 permit ahp any any
140 permit pim any any
150 permit igmp any any
160 permit tcp any any range 5900 5910
170 permit tcp any any range 50000 50100
180 permit udp any any range 51000 51100
190 permit tcp any any eq 3333
200 permit tcp any any eq nat ttl eq 255
210 permit tcp any eq bgp any
220 permit rsvp any any
230 permit tcp any any eq 9340
240 permit tcp any any eq 9559
250 permit udp any any eq 8503
260 permit udp any any eq lsp-ping
270 permit udp any eq lsp-ping any
Total rules configured: 27
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IP Access List v4Acl
10 permit ip any any
Total rules configured: 1
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
Standard IP Access List stAcl
10 permit any
Total rules configured: 1
IP Access List noRulesAcl
Total rules configured: 0
Configured on Ingress: Et2/1
Active on Ingress: Et2/1
IPV6 Access List default-control-plane-acl [readonly]
counters per-entry
10 permit icmpv6 any any [match 335448 bytes in 4424 packets, 0:01:13 ago]
20 permit ipv6 any any tracked
30 permit udp any any eq bfd hop-limit eq 255
40 permit udp any any eq bfd-echo hop-limit eq 254
50 permit udp any any eq multihop-bfd micro-bfd sbfd
60 permit udp any eq sbfd any eq sbfd-initiator
70 permit ospf any any
80 permit 51 any any
90 permit 50 any any
100 permit tcp any any eq ssh telnet www snmp bgp https netconf-ssh gnmi
110 permit udp any any eq bootps bootpc snmp ntp ptp-event ptp-general
120 permit tcp any any eq mlag hop-limit eq 255
130 permit udp any any eq mlag hop-limit eq 255
140 permit tcp any any range 5900 5910
150 permit tcp any any range 50000 50100
160 permit udp any any range 51000 51100
170 permit udp any any eq dhcpv6-client dhcpv6-server
180 permit tcp any eq bgp any
190 permit tcp any any eq nat hop-limit eq 255
200 permit udp any any eq nat hop-limit eq 255
210 permit rsvp any any
220 permit pim any any
230 permit tcp any any eq 9340
240 permit tcp any any eq 9559
250 permit udp any any eq 8503
260 permit udp any any eq lsp-ping
270 permit udp any eq lsp-ping any
Total rules configured: 27
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IPV6 Access List v6Acl
10 permit ipv6 3891:3c58:6300::/64 any
20 permit ipv6 any host 2fe1:b468:24a::
30 deny ipv6 host 3411:91c1:: host 4210:cc23:d2de::
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
MAC Access List mlist
10 deny any any
Total rules configured: 1
Configured on Ingress: Et11/1
Configured on Egress: Et11/1
Active on Ingress: Et11/1
Active on Egress: Et11/1switch# show access-lists summary
Phone ACL bypass: disabled
IPV4 ACL default-control-plane-acl [readonly]
Total rules configured: 27
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IPV4 ACL v4Acl
Total rules configured: 1
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
Standard IPV4 ACL stAcl
Total rules configured: 1
IPV4 ACL noRulesAcl
Total rules configured: 0
Configured on Ingress: Et2/1
Active on Ingress: Et2/1
IPV6 ACL default-control-plane-acl [readonly]
Total rules configured: 27
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IPV6 ACL v6Acl
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
MAC ACL mlist
Total rules configured: 1
Configured on Ingress: Et11/1
Configured on Egress: Et11/1
Active on Ingress: Et11/1
Active on Egress: Et11/1This command displays all rules in list2 ACL and the configuration and status.
switch# show access-list list2
IP Access List list2
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
IPV6 Access List list2
10 permit ipv6 3891:3c58:6300::/64 any
20 permit ipv6 any host 2fe1:b468:24a::
30 deny ipv6 host 3411:91c1:: host 4210:cc23:d2de::
Total rules configured: 3
Configured on Ingress: Et2/1
Active on Ingress: Et2/1
switch#The above output displayed two ACLs as the switch had an IPv4 ACL and an IPv6 ACL with the same name.
switch# show access-list list2 interface Ethernet 1/1
IP Access List list2
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
switch#The show ip access-lists command displays the contents of IPv4 and standard IPv4 Access Control List (ACLs) on the switch with the configuration and status. Use the summary option to display only the configuration and status with details such the name of the ACL, total rules configured, configured and active status containing interface information, and supplicant information as in the case of dynamic ACLs from dot1x sessions.
Command Mode
Privileged EXEC
Command Syntax
show ip access-lists [interface interface_ipv4]|[acl_name acl_name] | [scope summary]
Parameters
switch# show ip access-lists list2
IP Access List list2
10 permit ip 10.10.10.0/24 any
20 permit ip any host 10.20.10.1
30 deny ip host 10.10.10.1 host 10.20.10.1
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
switch#The above output can also be displayed with the help of the show ip access-lists interface Ethernet 1/1 command since the ACL list2 applies to the Ethernet 1/1 interface.
switch# show ip access-lists summary
IPV4 ACL default-control-plane-acl
Total rules configured: 12
Configured on: control-plane
Active on : control-plane
IPV4 ACL list2
Total rules configured: 3
IPV4 ACL test1
Total rules configured: 6
Standard IPV4 ACL test_1
Total rules configured: 1
IPV4 ACL test_3
Total rules configured: 0
switch#switch # show ip access-lists summary
IPV4 ACL default-control-plane-acl [readonly]
Total rules configured: 17
Configured on Ingress: control-plane(default VRF)
Active on Ingress: control-plane(default VRF)
IPV4 ACL ipAclLimitTest
Total rules configured: 0
Configured on Egress: Vl2148,2700
Active on Egress: Vl2148,2700The show ip prefix-list command displays all rules for the specified IPv4 prefix list. The command displays all IPv4 prefix list rules if a prefix list name is not specified.
Command Mode
EXEC
Command Syntax
show ip prefix-list [display_items list_name]
Parameters
Example
switch(config-ip-pfx)# show ip prefix-list
ip prefix-list route-one
seq 10 deny 10.1.1.0/24
seq 20 deny 10.1.0.0/16
seq 30 permit 12.15.4.9/32
seq 40 deny 1.1.1.0/24
switch(config-ip-pfx)#The show ipv6 access-lists command displays the contents of all IPv6 Access Control Lists (ACLs) on the switch with the configuration and status. Use the summary option to display only the configuration and status with contains details such as the name of the ACL, total rules configured, configured and active on status with interface information, and supplicant information in case of dynamic ACLs from dot1x sessions.
Command Mode
Privileged EXEC
Command Syntax
show ipv6 access-lists [ interface interface_ipv6] [supplicant supplicant][acl_name acl_name][scope summary]
Parameters
switch# show ipv6 access-lists list2
IP Access List list2
10 permit ipv6 3891:3c58:6300::/64 any
20 permit ipv6 any host 2fe1:b468:024a::
30 deny ipv6 host 3411:91c1:: host 4210:cc23:d2de:::
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
switch#The above output can also be displayed using the show ipv6 access-lists interface Ethernet 1/1 command since the ACL list2 applies to the Ethernet 1/1 interface.
switch# show ipv6 access-lists summary
IPV6 ACL list2
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
IPV6 ACL test1
Total rules configured: 6
IPV6 ACL test_1
Total rules configured: 1
Standard IPV6 ACL test_3
Total rules configured: 0
switch#The show ipv6 prefix-list command displays all rules for the specified IPv6 prefix list. The command displays all IPv6 prefix lists if a prefix list name is not specified.
Command Mode
EXEC
Command Syntax
show ipv6 prefix-list [display_items list_name]
Parameters
switch> show ipv6 prefix-list map1
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 15 deny 3:4400::/64
seq 20 permit 3:11b1:8fe4:1aac::/64
seq 30 permit 3:1bca:3ff2:634a::/64
seq 40 permit 3:1bca:1141:ab34::/64switch> show ipv6 prefix-list
ipv6 prefix-list map1
seq 10 permit 3:4e96:8ca1:33cf::/64
seq 15 deny 3:4400::/64
seq 20 permit 3:11b1:8fe4:1aac::/64
seq 30 permit 3:1bca:3ff2:634a::/64
seq 40 permit 3:1bca:1141:ab34::/64
ipv6 prefix-list FREDD
ipv6 prefix-list route-five
ipv6 prefix-list map2
seq 10 deny 10:1:1:1::/64 ge 72 le 80
seq 20 deny 10:1::/32The show mac access-lists command displays the contents of all MAC Access Control Lists (ACLs) on the switch, along with their configuration and status. Use the summary option to display only the configuration and status, which contain details such as the name of the ACL, the total rules configured, and where the ACL is configured/active with a status containing specific interface information.
Command Mode
Privileged EXEC
Command Syntax
show mac access-lists [interface interface_acl] [acl_name acl_name] [scope summary]
switch# show mac access-list mlist2
MAC Access List mlist2
10 permit 1024.4510.F125 0.0.0 any aarp
20 permit any 4100.4500.0000 0.FF.FFFF novell
30 deny any any
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1The above output can also be displayed with the help of show mac access-lists interface Ethernet 1/1 command since the ACL mlist2 applies to the Ethernet 1/1 interface.
switch# show mac access-list summary
MAC ACL mlist1
Total rules configured: 6
MAC ACL mlist2
Total rules configured: 3
Configured on Ingress: Et1/1
Active on Ingress: Et1/1
MAC ACL mlist3
Total rules configured: 1
MAC ACL mlist4
Total rules configured: 0The show platform arad tcam summary command displays the percentage of TCAM utilization per forwarding ASIC.
Command Mode
EXEC
Command Syntax
show platform arad acl tcam summary
Parameter
summary - Displays the ACL TCAM summary.
Example
switch# show platform arad acl tcam summary
The total number of TCAM lines per bank is 1024.
========================================================
Arad3/0:
========================================================
Bank Used Used % Used By
1 4 0 IP RACLs
Total Number of TCAM lines used is: 4
========================================================
Arad3/4:
========================================================
Bank Used Used % Used By
1 2 0 IP RACLs
Total Number of TCAM lines used is: 2The show platform arad acl tcam command displays the number of TCAM entries (hardware resources) occupied by the ACL on each forwarding ASIC.
This command applies only to DCS-7500E, DCS-7280E series switches.
Command Mode
EXEC
Command Syntax
show platform arad acl tcam [scope [detail | diff | hw | shadow | summary]
Parameters
switch# show platform arad acl tcam detail
ip access-list ipAclLimitTest (Shared RACL, 0 rules, 1 entries, direction out,
state success, Acl Label 2)
Fap: Arad0, Shared: true, Interfaces: Vl2148, Vl2700
Bank Offset Entries
0 0 1
Fap: Arad1, Shared: true, Interfaces: Vl2148
Bank Offset Entries
0 0 1switch# show platform arad acl tcam summary
The total number of TCAM lines per bank is 1024.
========================================================
Arad0:
========================================================
Bank Used Used % Used By
0 1 0 IP Egress PACLs/RACLs
Total Number of TCAM lines used is: 1
========================================================
Arad1:
========================================================
Bank Used Used % Used By
0 1 0 IP Egress PACLs/RACLs
Total Number of TCAM lines used is: 1The show platform arad mapping command displays the mapping between the interfaces and the forwarding ASICs.
Command Mode
EXEC
Command Syntax
show platform arad chip_name mapping
Parameter
chip_name Specifies the Arad chip name.
Example
switch# show platform arad arad3/0 mapping
Arad3/0 Port SysPhyPort Voq ( Fap,FapPort) Xlge Serdes
-------------------------------------------------------------------------------
Ethernet3/1/1 34 288 (0 , 2) n/a (20)
...............................................................................The show platform fap acl command displays the ACL information of Sand platform devices.
Command Mode
Privileged EXEC
Command Syntax
show platform fap acl [ipkgv | l4ops | mirroring | opkgv | pmf | tcam | udf | vsicfg]
Guidelines
Supported on DCS-7280SE and DCS-7500E series platforms only.
Example
switch(config)# show platform fap acl mirroring
==============
Aggregate ACLs
==============
(list2:0->2) type=2; version=0
- list2 [ prio 0 ] => session 2
(list1:10->1,list3:20->3) type=0; version=13
- list3 [ prio 20 ] => session 3
- list1 [ prio 10 ] => session 1
======================
Interface-ACL Mapping
======================
Ethernet1 => (list1:10->1,list3:20->3) [ ipv4 ]
Ethernet33 => (list2:0->2) [ mac ]The show platform fap tcam command displays the number of TCAM entries (hardware resources) occupied by the ACL on each forwarding ASIC of Sand platform devices.
Command Mode
Privileged EXEC
Command Syntax
show platform fap acl tcam [detail | diff | hw | shadow | summary]
Example
switch# show platform fap acl tcam detail
ip access-list ipAcl0000 (RACL, 1 rules, 2 entries, direction in, state success)
Shared: false
Interface: Vlan0002
-------------------
Fap: Arad3/0
Bank Offset Entries
1 0 2
Interface: Vlan0003
-------------------
Fap: Arad3/0
Bank Offset Entries
1 2 2
Fap: Arad3/4
Bank Offset Entries
1 0 2The show platform fap acl tcam hw command displays the TCAM entries configured for each TCAM bank including policy-maps and corresponding traffic match.
This command applies only to DCS-7280(E/R), DCS-7500(E/R) series switches.
Command Mode
EXEC
Command Syntax
show platform fap fap_name acl tcam hw
Example
switch# show platform fap Arad1 acl tcam hw
================================================================================
Arad1 Bank 0 Type: dbPdpIp, dbPdpIp6, dbPdpMpls, dbPdpNonIp, dbPdpTunnel
================================================================================
----------------------------------------------------
|Offs|X|PR|TT|R|QI|V6MC|DPRT|SPRT|F|DEST |V|ACT |H|
----------------------------------------------------
|29 |4|59| | |01| | | | | |3|0008f|0|
| |4|59| | |01| | | | | |0|00000|0|
|30 |4|33| | |01| | | | | |3|0008f|0|
| |4|33| | |01| | | | | |0|00000|0|
|31 |4|32| | |01| | | | | |3|0008f|0|
| |4|32| | |01| | | | | |0|00000|0|
|32 |4| | | |01|ff02| | | | |3|00097|0|
| |4| | | |01|ff02| | | | |0|00000|0|
|33 |4|06| | |01| | |00b3| |26ffd|3|0009b|0|
| |4|06| | |01| | |00b3| |26ffd|0|00000|0|
|34 |4|06| | |01| |00b3| | |26ffd|3|0009b|0|
----------------------------------------------
|Offs|X|R|QI|DAHI|PT|DALO |DEST |V|ACT |H|
----------------------------------------------
-----------------------------------------------------------------------------
|Offs|X|TT0|QI|FOI|TT1|DEST |TT1P |PT|VX_DP|PN|F|MC|O|V|HDR OFFSETS |ACT |H|
================================================================================
Arad1 Bank 1 Type: dbIpQos
================================================================================
----------------------------------------------------------------------
|Offs|X|TC|CL|DPRT|SPRT|VQ|L4OPS |PP|PR|F|V4_DIP |V4_SIP |V|ACT |H|
----------------------------------------------------------------------
|0 |0| | | | | | |01| | | | |3|00000|0|
| |0| | | | | | |01| | | | |0|00000|0|
----------------------------------------------------------------------
<-------OUTPUT OMITTED FROM EXAMPLE-------->The show platform fap acl tcam summary command displays for each forwarding ASIC, the number of TCAM entries consumed per ACL type, and in which TCAM bank the entries are installed. A mirroring ACL does not consume TCAM resources unless attached to a mirroring source interface, and a mirroring destination is configured. If the mirroring destination is a GRE tunnel, at least one nexthop entry for the tunnel destination must be resolved before a TCAM entry is installed.
Command Mode
EXEC
Command Syntax
show platform fap acl tcam summary
Example
switch# show platform fap acl tcam summary
========================================================
Arad0:
========================================================
Bank Used Used % Used By
0, 1 2 0 IP Mirroring
Total Number of TCAM lines used is: 4
========================================================
Arad1:
========================================================
Bank Used Used % Used By
2 1 0 Mac MirroringThe show platform trident tcam command displays the TCAM entries configured for each TCAM group including policy maps and corresponding hits.
Command Mode
EXEC
Command Syntax
show platform trident tcam [acl | cpu-bound | detail | directed-broadcast | entry | mirror | pbr | pipe | qos | shared | summary]
Guidelines
Applies only to DCS-7010, DCS-7050/DCS-7050X, DCS7250X, DCS-7300X series switches.
switch(config)# show platform trident tcam mirror
=== Mirroring ACLs on switch Linecard0/0 ===
Session: mir-sess2
INGRESS ACL mirAcl2* uses 2 entries
Assigned to ports: Ethernet32/1switch# show platform trident tcam directed-broadcast
DirectedBroadcast Feature Tuples.
Src Ip Dst Ip Action Hits
--------------- --------------- ------- ------------
10.1.1.1 192.164.2.15 Permit 0
20.1.1.1 192.164.2.15 Permit 0
30.1.1.1 192.164.2.15 Permit 0
10.1.1.1 192.166.2.15 Permit 0
20.1.1.1 192.166.2.15 Permit 0
30.1.1.1 192.166.2.15 Permit 0
10.1.1.1 192.168.2.255 Permit 0
20.1.1.1 192.168.2.255 Permit 0
30.1.1.1 192.168.2.255 Permit 0
* 192.164.2.15 Deny 0
* 192.166.2.15 Deny 0
* 192.168.2.255 Deny 0switch# show platform trident tcam detail
=== TCAM detail for switch Linecard0/0 ===
TCAM group 9 uses 42 entries and can use up to 1238 more.
Mlag control traffic uses 4 entries.
589826 0 hits - MLAG - SrcPort UDP Entry
589827 0 hits - MLAG - DstPort UDP Entry
589828 0 hits - MLAG - SrcPort TCP Entry
589829 0 hits - MLAG - DstPort TCP Entry
CVX traffic reserves 6 entries (0 used).
L3 Control Priority uses 23 entries.
589836 0 hits - URM - SelfIp UDP Entry
589837 0 hits - URM - SelfIp TCP Entry
589848 0 hits - OSPF - unicast
589849 71196 hits - OSPFv2 - Multicast
589850 0 hits - OSPFv3 - Multicast
589851 0 hits - OSPF Auth ESP - Multicast
589852 0 hits - OSPF Auth ESP - Unicast
589853 0 hits - IP packets with GRE type and ISIS protocol
589854 0 hits - RouterL3 Vlan Priority 6,7 Elevator
589855 0 hits - RouterL3 DSCP 48-63 Elevator
589856 0 hits - RouterL3 Priority Elevator
589857 0 hits - NextHopToCpu, Glean
589858 0 hits - L3MC Cpu OIF
IGMP Snooping Flooding reserves 8 entries (6 used).
589864 0 hits - IGMP Snooping Restricted Flooding L3 from local
mlag peer
589865 0 hits - IGMP Snooping Restricted Flooding L3
L4 MicroBfd traffic reserves 1 entries (0 used).
TCAM group 13 uses 99 entries and can use up to 1181 more.
Dot1x MAB traffic uses 1 entries.
851968 0 hits - Dot1xMab Rule
<-------OUTPUT OMITTED FROM EXAMPLE-------->
ck338.22:14:38(config-pmap-qos-policy1)#The show route-map command displays the contents of configured route maps.
Command Mode
EXEC
Command Syntax
show route-map [map_name]
switch(config)# show route-map map1
route-map map1 permit 10
Description:
Match clauses:
SubRouteMap:
Set clauses:
set as-path prepend last-as 12
set as-path prepend auto autoswitch> show route-map map
route-map map permit 5
Match clauses:
match as 456
Set clauses:
route-map map permit 10
Match clauses:
match ip next-hop 2.3.4.5
match as-path path_2
Set clauses:
set local-preference 100The system profile command creates a new Ternary Content-Addressable Memory (TCAM) profile in the running configuration.
The default system profile and no system profile commands delete non-default TCAM profiles from the running configuration.
Command Mode
Hardware TCAM
Command Syntax
system profile [profile_name | default | mirroring-acl | pbr-match-nexthop-group | qos | tap-aggregation-default | tap-aggregation-extended | tc-counters]
default system profile
no system profile
Guideline
Compatible with the DCS-7280SE and DCS-7500E series switches only.
switch(config)# hardware tcam
switch(config-hw-tcam)# system profile mirroring-acl
switch(config-hw-tcam)# show hardware tcam profile
Configuration Status
FixedSystem mirroring-acl mirroring-acl
switch(config-hw-tcam)#switch(config)# hardware tcam
switch(config-hw-tcam)#show hardware tcam profile
Configuration Status
Linecard9 mirroring-acl mirroring-acl
Linecard8 mirroring-acl mirroring-acl
Linecard3 mirroring-acl mirroring-acl
Linecard4 mirroring-acl mirroring-acl
Linecard6 mirroring-acl mirroring-acl
switch(config-hw-tcam)# default system profile
switch(config-hw-tcam)# show hardware tcam profile
Configuration Status
Linecard9 default default
Linecard8 default default
Linecard3 default default
Linecard4 default default
Linecard6 default default
switch(config-hw-tcam)#switch(config-hw-tcam)# show hardware tcam profile
Configuration Status
Linecard9 tc-counters tc-counters
Linecard8 tc-counters tc-counters
Linecard3 tc-counters tc-counters
Linecard4 tc-counters tc-counters
Linecard6 tc-counters tc-counters
switch(config-hw-tcam)# no system profile
switch(config-hw-tcam)# show hardware tcam profile
Configuration Status
Linecard9 default default
Linecard8 default default
Linecard3 default default
Linecard4 default default
Linecard6 default default
switch(config-hw-tcam)#DirectFlow allows you to define flows consisting of conditions to match, and actions to perform, that are a superset of the OpenFlow 1.0 specification. DirectFlow runs alongside the existing L2/L3 forwarding plane, enabling a network architecture that incorporates new capabilities such as TAP aggregation and custom traffic engineering, alongside traditional forwarding models. DirectFlow does not require a controller or any third party integration, as flows can be installed via the CLI.
DirectFlow exposes the underlying forwarding ASIC's capabilities through a programmable interface like EAPI or the standard CLI.
DirectFlow works in conjunction with all other aspects of standard Layer 2 or Layer 3 bridging or forwarding, and DirectFlow traffic is subject to the standard packet processing pipeline within the ASIC. You can think of DirectFlow as a stage in packet processing that processes traffic after ingress checks and before any egress actions.
DirectFlow enables you to configure flows that consist of matching criteria and actions, and to modify how traffic is processed, by overriding the L2 lookup decision or rewriting a MAC address or VLAN for example.
Features like MAC learning, STP state checks, ingress or egress VLAN membership checks on ports, ACLs, QoS, and others are all respected by DirectFlow. Traffic that does not match any programmed flow is processed normally, while traffic that matches programmed flows is now subject to the actions specified in the flows.
You can define a relative priority between flows and define idle or hard timeouts for the flow. DirectFlow also enables you to insert a flow entry that matches on specified criteria, and define actions to be taken on traffic that matches the specified matching conditions. You can define flows to match on TCP flags, IPv6 source and destination addresses, input ports, and more.
DirectFlow enables you to configure flows that are not visible in the startup or running configurations and do not persist over a reboot. This feature is designed to be used for flows that are configured by a custom agent using the EOS SDK or eAPI and age out (expire) after a specified time period.
For example, if you are using a custom agent that reacts to traffic sent to the CPU (the redirect to CPU action), and you want to use a flow that will drop all matching traffic for 5 minutes, the agent can program a non-persistent flow that expires after a hard timeout of 300 seconds.
Using a non-persistent flow for this purpose ensures that other administrator actions (for example, saving the configuration) do not result in the flow being resurrected on startup or reverting to the saved configuration. It also removes the need for the agent to delete the expired flow.
DirectFlow supports all matches on VLAN, ether type, source or destination MAC address, COS, source or destination IP address, IP protocol, IP TOS, L4 source, destination ports, ICMP type, and code.
DirectFlow also permits re-using the same flow on multiple input ports, saving valuable TCAM space.
The redirect to CPU action is useful in cases in which a custom agent is running on EOS and you want to trap specific traffic (matching traffic) and send the trapped traffic to the agent.
A number of different commands are provided for the DirectFlow feature. The different commands enable you to enter the DirectFlow configuration mode, enable DirectFlow, configure flows, and display configured flows.
switch(config)# directflow
switch(config-directflow)#switch(config-directflow)# no shutdown switch(config-directflow)# flow Test-1
switch(config-directflow-Test-1)#switch(config-directflow-Test-1)# match ethertype ip
switch(config-directflow-Test-1)# match source ip 10.10.10.10switch(config-directflow-Test-1)# action egress mirror ethernet 7
switch(config-directflow-Test-1)# action set destination mac 0000.aaaa.bbbbswitch(config-directflow-Test-1)# exit
switch(config-directflow)#switch(config)# directflow
switch(config-directflow)# flow redirect-http-cpu
switch(config-directflow-redirect-http=cpu)# match ip protocol tcp
switch(config-directflow-redirect-http-cpu)# match destination port 80
switch(config-directflow-redirect-http-cpu)# action output interface cpuswitch config)# directflow
switch(config-directflow)# flow example-non-persistent
switch(config-directflow-example-non-persistent)# match input interface ethernet 25
switch(config-directflow-example-non-persistent)# action drop
switch(config-directflow-example-non-persistent)# no persistent
switch(config-directflow-example-non-persistent)# timeout hard 300The detail option of the show directflow flows command enables you to display the details of configured flows. You can use this command to verify that a non-persistent flow is deleted after the timeout period configured for the flow has elapsed.
The following example shows the use of this command to view the configuration of a non-persistent flow before the timeout period has elapsed, and a second time, after the timeout period has expired.
switch(config-directflow)# show directflow flows example-non-persistent detail
Flow example-non-persistent: (Flow programmed)
persistent: False
priority: 0
hard timeout: 300
idle timeout: 0
match:
ingress interface:
Et25
actions:
drop
matched: 0 packets, 0 bytesswitch(config-directflow)# show directflow flows example-non-persistent detail
Flow example-non-persistent: (Flow not programmed)
persistent: False
priority: 0
hard timeout: 300
idle timeout: 0
match:
ingress interface:
Et25
actions:
drop
matched: 0 packets, 0 bytesThe only exception is the ingress or egress mirroring action, where the DirectFlow entry causes the packet to be mirrored.
When the ingress or egress packets are mirrored, the original traffic is sent out normally.
DirectFlow runs alongside MSTP, RSTP, and PVST. DirectFlow entries do not match on packets that ingress an STP discarding port. DirectFlow entries that cause a packet to be forwarded out an STP discarding port will result in the packets being dropped on egress.
When STP is enabled, BPDUs will always be trapped to the CPU. When STP is disabled, BPDUs will be subject to DirectFlow entries and not be copied to the CPU by default.
sFlow is unaffected by DirectFlow.
IGMP control packets are trapped to the CPU when IGMP Snooping is enabled. DirectFlow entries can match IGMP Snooping control traffic and override the trap to CPU.
Link-local-multicast packets are flooded in hardware in the VLAN via a TCAM entry. DirectFlow entries can match link-local-multicast packets and change the flooding behavior. As DirectFlow entries have to specify output interfaces or drop, the action will conflict and so matching DirectFlow entries will get precedence.
When IGMP snooping is enabled, unknown IPV4 multicast packets are flooded to the multicast-router ports in the VLAN. If DirectFlow entries match unknown IPV4 multicast packets, they will override the flooding behavior.
Data packets in groups under IGMP snooping control are sent to the group members through a MAC table entry. Matching DirectFlow entries override the MAC table entries.
DirectFlow entries are lower priority than any configured Port ACLs (ingress). Packets coming in on a port that match DirectFlow entries obey any configured ACL on that port, and will only apply to packets that have a permit action.
DirectFlow entries are higher priority than any configured RACLs. Packets coming in on an L3 interface that match DirectFlow entries ignore any RACLs configured on that interface.
DirectFlow entries are lower priority than any configured Egress ACLs.
DirectFlow runs alongside IP routing. If a packet is routed out a layer three interface using a DirectFlow entry, the actions associated with the entry will have to specify the new source MAC and destination MAC for the packet, as well as the physical port or LAG. If there are no output ports specified in an entry, packets that match that entry will be dropped.
When unicast routing is enabled, DirectFlow entries that match take precedence for all packets that would have been otherwise been routed. The three exceptions are the ingress mirror, egress mirror and copy-to-CPU actions where the packets will be routed normally in addition to the action being performed. Routed packets that do not match DirectFlow entries are forwarding based on the L3 lookup.
When multicast routing is enabled, DirectFlow entries that match take precedence for all packets that would have otherwise been multicast routed. The packets are not replicated based on the hardware multicast tables, but are forwarded strictly according to the actions specified by the DirectFlow entry. The entry can specify a set of output interfaces, which will result in the packet being replicated based on the DirectFlow entry.
switch(config-directflow)# show directflow flows
Flow Test1:
priority: 0
match:
ingress interface: Ethernet1
ethertype ip
source ip address: 10.10.10.10
actions:
output mirror: Ethernet2
matched: 0 packets, 0 bytes
switch(config-directflow)# switch(config-directflow)# show directflow flows example-non-persistent
Flow example-non-persistent:
persistent: False
priority: 0
hard timeout: 300
idle timeout: 0
match:
ingress interface:
Et25
actions:
drop
matched: 0 packets, 0 bytesThe action drop command configures packets that match an entry to be dropped.
The no action drop and default action drop commands remove the statement from the DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
action drop
no action drop
default action drop
Example
switch(config-directflow-Test-1)# action drop
switch#The action mirror command can be used to ingress or egress mirror traffic to a mirror destination. This requires a mirror destination to be setup on the switch. If a packet comes in or goes out an interface that is part of another mirror session, then the destination for that destination as well as the DirectFlow destination will receive a copy of the packet.
The no action mirror and default action mirror commands remove the statement from DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
action DIRECTION mirror INT_NAME
no action DIRECTION mirrorINT_NAME
default action DIRECTION mirror INT_NAME
Example
switch(config-directflow)# flow Test1
switch(config-directflow-Test1)# match ethertype ip
switch(config-directflow-Test1)# match source ip 10.10.10.10
switch(config-directflow-Test1)# action egress mirror ethernet 2
switch(config-directflow-Test1)# The action output command configures an Ethernet or port channel interface as the output of a specified port mirroring session.
The no action output and default action outputcommands remove the statement from DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
action output DESTINATION
no action output DESTINATION
default action output DESTINATION
Parameters
switch(config-directflow-Test1)# action output interface ethernet 7
switch(config-directflow-Test1)#switch(config-directflow)# flow flow-sip-10_10_1_2-redirect-to-10_30_1_2
switch(config-directflow-Test1)# match ethertype ip
switch(config-directflow-Test1)# match source ip 10.10.1.2
switch(config-directflow-Test1)# action output nexthop 10.30.1.2
switch(config-directflow-Test1)#The action output interface cpu command configures the action (other commands are used to define the traffic matching conditions).
The no action output interface cpu and default action output commands remove the statement from DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
action output DESTINATION
no action output DESTINATION
default action output DESTINATION
Parameters
switch(config-directflow-Test1)# action output interface ethernet 7
switch(config-directflow-Test1)#switch (config)# directflow
switch(config-directflow)# flow redirect-http-cpu
switch(config-directflow-redirect-http=cpu)# match ip protocol tcp
switch{config-directflow-redirect-http-cpu)# match destination p cpuort 80
switch(config-directflow-redirect-http-cpu)# action output interfaceThe action set command allows you to configure a packet to be routed out a layer three interface using a DirectFlow entry. The actions associated with the entry will have to specify the new source MAC and destination MAC for the packet, as well as the physical port or LAG. If there are no output ports specified in an entry, packets that match that entry will be dropped.
The no action set and default action set commands remove action set statement from DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
action set CONDITION
no action set CONDITION
default action set CONDITION
Parameters
The no action set and default action set commands require only the CONDITION type without a specific condition value.
Example
switch(config-directflow)# flow Test1
switch(config-directflow-Test1)# action egress mirror ethernet 7
switch(config-directflow-Test1)# action set destination mac 0000.aaaa.bbbbThe directflow command places the switch in DirectFlow configuration mode.
The no directflow and default directflow commands delete the DirectFlow configuration mode statements from running-config.
DirectFlow configuration mode is not a group change mode; running-config is changed immediately upon entering commands. The exit command returns the switch to global configuration mode.
Command Mode
Global Configuration
Command Syntax
directflow
no directflow
default directflow
switch(config)# directflow
switch(config-directflow)#switch(config-directflow)# exit
switch(config)#The flow command places the switch in flow configuration mode.
The no flow and default flow commands delete the specified role by removing the role and its statements from running-config.
Command Mode
DirectFlow Configuration
Command Syntax
flow flow_name
no flow flow_name
default flow flow_name
Parameter
flow_name Name of flow.
The match command allows you to configure a rule or a flow which could match on L2, L3, L4 fields of a packet and specify a certain action to modify, drop or redirect the packet.
All traffic ingressing on the switch will be matched against the flows installed. In cases where none of the packets match, normal switching or routing behavior will take over. When multiple entries match a packet, precedence is given to the entry that was installed first.
The no match and default match commands remove the match statement from the configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
match CONDITION
no match CONDITION
default match CONDITION
Parameters
The no match and default match commands require only the CONDITION type without a specific condition value.
Example
switch(config-directflow)# flow Test1
switch(config-directflow-Test1)# persistent
switch(config-directflow-Test1)# match ethertype ip
switch(config-directflow-Test1)# match source ip 10.10.10.10DirectFlow flows are persistent by default. Once finalized, they appear in the running configuration, and if saved to startup config they will persist over a reboot. The no form of the persistent command prevents the flow from showing up in running config, ensuring that it will not persist over a reboot.
Command Mode
Directflow-flow Configuration
Command Syntax
persistent
no persistent
Example
switch(config)# directflow
switch(config-directflow)# flow example-non-persistent
switch(config-directflow-example-non-persistent)# match input interface ethernet 25
switch(config-directflow-example-non-persistent)# action drop
switch(config-directflow-example-non-persistent)# no persistent
switch(config-directflow-example-non-persistent)# timeout hard 300
switch(config-directflow-example-non-persistent)# exit
switch(config-directflow)#The priority command sets the priority for the flow match rules. Each flow-table entry has an optional priority field, with a higher number indicating a higher priority. Flows with the same priority may be loaded in any order, and the order may be changed at any time. If multiple entries match a packet, precedence is given to the entry that was installed first.
Priority numbers range from 0 to 65535. The default is 0. The higher priority rules match first.
The no priority and default priority commands remove priority statement from the DirectFlow configuration mode.
Command Mode
Directflow-flow Configuration
Command Syntax
priority priority_value
no priority
default priority
Parameter
priority_value priority xxx. Value ranges from 0 to 65535. Default is 0.
Example
switch(config-directflow-Test-1)# priority 150
switch(config-directflow-Test-1)#The show directflow command displays summary information for DirectFlow. With the counters or details options, it displays counters or details for all flows configured on the switch.
Command Mode
EXEC
Command Syntax
show directflow [counters | details]
switch# show directflow
DirectFlow configuration: Enabled
Total matched: 0 packets
Total programmed flows: 3 flows
switch#switch# show directflow counters
Flow Name Source Matched packets Matched bytes
--------- ------ --------------- -------------
test3 config 0 0
test2 config 0 0
test1 config 0 0
Total matched packets: 0
switch>switch# show directflow detail
Flow test3: (Flow programmed)
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
Ethernet type: 0x86dd
source IPv6 address: fcaa::/ffff:ffff:ffff:ffff:ffff:ffff:ffff:ffff
actions:
output interfaces:
Et32
source: config
matched: 0 packets, 0 bytes
Flow test2: (Flow programmed)
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
Ethernet type: IPv4
source IPv4 address: 10.1.2.12/255.255.255.255
IPv4 protocol: TCP
destination TCP/UDP port or ICMP type: 8080
actions:
output interfaces:
Et3/1
source: config
matched: 0 packets, 0 bytes
Flow test1: (Flow programmed)
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et1/1
actions:
output interfaces:
Et2/1
source: config
matched: 0 packets, 0 bytes
Flows: 3 programmed, 0 rejectedThe show directflow flows command displays the contents of the flow table, showing each entry with its match rules, actions, and packet counters. Including the name of a specific flow limits the output to information about the specified flow.
Command Mode
EXEC
Command Syntax
show directflow flows [flow_name [counters | detail]]
switch# show directflow flows
Flow test3:
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
Ethernet type: 0x86dd
source IPv6 address: fcaa::/ffff:ffff:ffff:ffff:ffff:ffff:ffff:ffff
actions:
output interfaces:
Et32
source: config
matched: 0 packets, 0 bytes
Flow test2:
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
Ethernet type: IPv4
source IPv4 address: 10.1.2.12/255.255.255.255
IPv4 protocol: TCP
destination TCP/UDP port or ICMP type: 8080
actions:
output interfaces:
Et3/1
source: config
matched: 0 packets, 0 bytes
Flow test1:
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et1/1
actions:
output interfaces:
Et2/1
source: config
matched: 0 packets, 0 bytesswitch# show directflow flows test-1
Flow test1:
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et1/1
actions:
output interfaces:
Et2/1
source: config
matched: 0 packets, 0 bytesswitch# show directflow flows test-1 detail
switch>show directflow flows test1 detail
Flow test1: (Flow programmed)
persistent: True
priority: 0
priorityGroupType: default
tableType: ifp
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et1/1
source Ethernet address: 00:aa:aa:aa:aa:aa/ff:ff:ff:ff:ff:ff
VLAN ID: 10
actions:
output interfaces:
copy ingress to mirror dest interfaces: Ethernet1
forward normally
source: config
matched: 0 packets, 0 bytesswitch# show directflow detail
Flow test-3: (Flow programmed)
persistent: False
priority: 0
priorityGroupType: default
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et11
actions:
copy ingress to mirror dest interfaces: Ethernet1
forward normally
source: config
matched: 0 packets, 0 bytes
Flow test-1: (Flow programmed)
persistent: True
priority: 0
priorityGroupType: default
hard timeout: 0
idle timeout: 0
match:
ingress interface:
Et10
source Ethernet address: 00:aa:aa:aa:aa:aa/ff:ff:ff:ff:ff:ff
VLAN ID: 10
actions:
copy ingress to mirror dest interfaces: Ethernet1
forward normally
source: config
matched: 0 packets, 0 bytes
Flow test-2: (Flow rejected due to invalid match criteria)
persistent: True
priority: 0
priorityGroupType: default
hard timeout: 0
idle timeout: 0
match:
Ethernet type: IPv4
IPv4 protocol: ICMP
source TCP/UDP port or ICMP type: 3
destination TCP/UDP port or ICMP type: 6
actions:
copy ingress to mirror dest interfaces: Ethernet1
forward normally
source: config
matched: 0 packets, 0 bytes
Flows: 2 programmed, 1 rejectedswitch# show directflow flows test-1 counters
Flow Name Source Matched packets Matched bytes
--------- ------ --------------- -------------
test1 config 0 0switch# show directflow counters
Flow Name Source Matched packets Matched bytes
--------- ------ --------------- -------------
test1 config 0 146
Total matched packets: 1The shutdown command, in DirectFlow mode, disables DirectFlow on the switch. DirectFlow is disabled by default.
The no shutdown command re-enables DirectFlow.
Command Mode
Directflow Configuration
Command Syntax
shutdown
no shutdown
default shutdown
switch(config)# directflow
switch(config-directflow)# no shutdown
switch(config-directflow)#switch(config-directflow-Test1)# shutdownThe timeout command, in DirectFlow mode, command configures the connection timeout period for connection sessions. The connection timeout period defines the interval between a users most recently entered command and an automatic connection shutdown. Automatic connection timeout is disabled by setting the idle-timeout to zero, which is the default setting.
Command Mode
Directflow-flow Configuration
Command Syntax
timeout [hard | idle]
no timeout
switch(config)# directflow
switch(config-directflow-Test1)# timeout hard 5
switch(config-directflow-Test1)#switch(config)# directflow
switch(config-directflow-Test1)# no timeout hard
switch(config-directflow-Test1)#EOS provides IP Address Locking capabilities when configured on an Ethernet Layer 2 port.
IP Address Locking prevents a host on a different interface from claiming ownership of an IP address through ARP spoofing. IPv6 Locking extends this behavior to IPv6 packets, including ICMPv6 Neighbor Discovery Router Advertisement and Redirect and DHCP server-to-client packets.
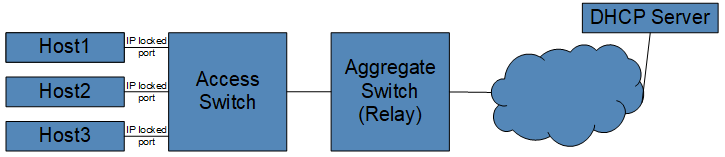
IP Address Locking determines port authorization for IP addresses by untilizing DHCP LeaseQuery and MAC address. Ensure that DHCP servers used in the network allow LeaseQuery messages.
Alternatively, IP locking can be configured to monitor incoming DHCPACK packets on designated ports to verify IP address authorization. This specific configuration method operates independently and eliminates the need for DHCP LeaseQuery.
This section describes IP Locking configuration tasks. Topics in this section include:
Before enabling IPv4 Address Locking, you must configure a DHCP Server and a Local Layer 3 interface.
Add the DHCP servers used by hosts to acquire leases. IPv4 Address Locking communicates with the DHCP servers to learn the authorized IP addresses on the switch.
Example
switch(config-address-locking)# dhcp server ipv4 10.1.1.1
switch(config-address-locking)# dhcp server ipv4 10.30.1.3Add a local L3 interface to communicate with the DHCP server. This could be the management interface, a routed interface, or a Switch Virtual Interface (SVI). This interface requires an assigned valid IP address, routable to the configured DHCP server, and can reside in a non-default VRF. The switch packets sent to the DHCP Server use the interface IP address as the source IP address.
Examples
switch# configure
switch(config)# interface Vlan2160
switch(config-if-Vl2160)# ip address 10.10.1.2/16switch# configure
switch(config)# address locking
switch(config-address-locking)# local-interface Vlan2160Configure IP Address Locking for either IPv4 or IPv6 addresses, and both types of IP addresses can be enabled for IP Address Locking. IPv6 Address Locking requires a different approach outlined in this section.
Configure IPv4 Address Locking commands in the configuration mode.
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv4To enable IPv6 locking, disable the enforcement of IPv6 Address Locking.
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv6 enforcement disabled
switch(config-address-locking)# locked-address ipv6Disable IP Address Locking using the disabled command in address-locking mode. This turns off the feature and allows a host to use any IP address, authorized or unauthorized, on any port.
switch# configure
switch(config)# address locking
switch(config-address-locking)# disabledTo enable IPv4 Address Locking on ports connected to clients, IP Address Locking must be enabled in the Interface Configuration Mode. Running this command only enables IPv4 Locking and overrides the previous configuration for the interface.
Example
switch(config)# interface Ethernet27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-address-locking)# address-family ipv4Use the following commands to enable IPv6 Address Locking on ports connected to clients, use the address-family ipv6 parameter.
Example
switch(config)# interface Ethernet53/4
switch(config-if-Et53/4)# address locking
switch(config-if-Et53/4-address-locking)# address-family ipv6To activate IP Address Locking on all VLAN port members, use the VLAN address locking configuration submode.
Examples
switch(config)# vlan 20
switch(config-vlan-20)# address locking
switch(config-vlan-20-addr-lock)# address-family ipv4To exclude a VLAN port member, disable IP Address Locking on that port using the interface configuration submode.
switch(config)# interface Ethernet2/25
switch(config-if-Et2/25)# address locking
switch(config-if-Et2/25)# address-family ipv4 disabledTo configure IPv6 Address Locking on all ports, use the same commands, but designate the address-family as ipv6.
switch(config)# interface Ethernet 27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-address-locking)# address-family ipv6switch(config)# vlan 20
switch(config-vlan-20)# address locking
switch(config-vlan-20-addr-lock)# address-family ipv6switch(config)# interface Ethernet 27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-address-locking)# address-family ipv4
switch(config-if-Et27/1-address-locking)# address-family ipv6Use the deny ip_address on IPv4 Address Locking ports to block all IPv4 and ARP packets with a specific source IPv4 address. The port denies the packet and affects only IPv4 enforcement modes. This action deauthorizes the addresses on the port and can be configured with multiple IPv4 addresses. You must configure this on an interface already configured with IPv4 Address Locking.
switch(config)# interface Ethernet27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-addr-lock)# deny 172.21.16.25The lease mac command within address locking configuration mode installs a lease into hardware for the configured IP address on the interface with the configured associated MAC address. If the MAC address does not appear in the MAC table or the MAC address on an interface without a configured IP Locking feature, the lease does not install until the interface adds the MAC address to an interface configured with IP Locking.
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# lease 172.21.13.11 mac a0:ce:c8:b1:78:d3The command, lease query retry interval interval timeout minutes configures sending lease queries at specific retry intervals. The no lease query retry command removes the retry interval and timeout configuration.
Example
switch(config)# address locking
switch(config-address-locking)# lease query retry interval 5 timeout 100When IP Address Locking sends out a LeaseQuery request, and does not receive a LeaseActive reply, IP Address Locking sends six (6) additional retries over 64 seconds using an exponential backoff algorithm. A 0-25% delay sending requests which may take up to 80 seconds to send out all seven (7) requests.
Every LeaseQuery request includes a transaction ID. After sending the last request, and for an additional 10 seconds, IP Address Locking accepts any LeaseActive reply matching the transaction ID and then queries for the MAC address of a sent LeaseQuery request.
If a LeaseActive reply contains multiple IP addresses, IP Address Locking begins a query process for the additional IP addresses using the same retry mechanisms. However, if you configure the LeaseQuery retry interval and timeout but do not receive LeaseActive replies, IP Address Locking sends continuous lease query requests at the configured retry interval until reaching the specified timeout period.
The IP addresses remain authorized and installed after the corresponding MAC addresses age out. IP Address Locking, by default, removes authorized leases after the corresponding MAC addresses age out. The locked-address expiration mac disabled command configures IP Address Locking to keep leases installed, after the corresponding MAC addresses age out.
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address expiration mac disabledAddress-locking mode can be enabled using the command dhcp server interface interface. In this mode, the IP Locking agent monitors the server interface for DHCP ACK packets and tracks release packets on protected interfaces.
When both a local interface and a DHCP server interface are specified, the system prioritizes the local-interface interface setting. In this scenario, IP Locking disregards the DHCP server interface and utilizes the local interface for outgoing DHCP LeaseQuery messages.
Furthermore, specifying DHCP server IP addresses within the dhcp server interface interface configuration is optional. If specific IP addresses are provided, IP Locking strictly learns leases from those identified servers. However, if no addresses are defined, the agent learns leases from all DHCP server traffic detected on the configured interfaces.
Example
switch# config
switch(config)# address locking
switch(config-address-locking)# dhcp server interface Ethernet28/1The locked-address ipv4 enforcement disabled command disables address filtering for all ports with IPv4 Address Locking enabled. This permits IPv4 packets while still keeping all other drop rules. When configured, IP Address Locking does not drop IP or ARP packets, and does not send out lease queries to configured DHCP servers.
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv4 enforcement disabledswitch(config)# interface Ethernet27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-address-locking)# locked-address ipv4 enforcement disabled switch(config)# vlan 20
switch(config-vlan-20)# address locking
switch(config-vlan-20-addr-lock)# locked-address ipv4 enforcement disabledswitch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv6 enforcement disabledswitch(config)# interface Ethernet27/1
switch(config-if-Et27/1)# address locking
switch(config-if-Et27/1-address-locking)# locked-address ipv6 enforcement disabledswitch(config)# vlan 20
switch(config-vlan-20)# address locking
switch(config-vlan-20-addr-lock)# locked-address ipv6 enforcement disabledThe output displays separate counters for the different types of messages communicated between the switch and the DHCP server.
switch# show address locking counters
Lease Active Lease Unknown Lease Unassigned
DHCP Server Query Rcvd Drop Rcvd Drop Rcvd Drop Unknown
----------- ----- ----- ------ ------ ------ -------- ------- -------
80.80.80.80 32860 8002 34 8001 32 13423 134 3234
Interface Query Lease Active Lease Unknown Lease Unassigned
--------- ----- ------------ ------------- ----------------
Ethernet2 1747 1234 189 324The clear address locking counters command resets all the counters associated with IP Locking to zero.
Use the show address locking command to display the status of IPv4 and IPv6 locking.
switch# show address locking
IP Locking is active
Interface IPv4 IPv6
--------------- ------------------- ---------------------------
Ethernet27/1 yes no (not configured)
Ethernet31/1 no (not configured) no (not a layer 2 interface)The show address locking table ipv4 command displays all the DHCP leases that IP Address Locking knows about, current status of installed leases, and the authorized interfaces for these IP addresses.
switch# show address locking table ipv4
IP Address MAC Address Interface Installed Expiration Time
-------------- ---------------- ---------- ------------ ---------------
10.30.4.4 ba76.a467.7ff8 Et27/1 installed in 0:01:57 Use the address locking command to block IPv4 and ARP packets with specific IPv4 addresses on the switch. You must perform this command from an interface configured for IP Address Locking on the switch.
Command Mode
Interface Configuration
Address Locking Configuration
Command Syntax
address locking deny ip_address
Parameter
ip_address - Specify the IPv4 address to block packets.
Example
switch(config)# interface Ethernet53/4
switch(config-if-Et53/4)# address locking
switch(config-address-locking)# deny 172.16.21.131Use the address locking command to enter address locking mode and then dhcp to configure the DHCP server.
Command Mode
Address Locking Configuration
Command Syntax
address locking dhcp server ipv4 ip_address
Example
switch(config)# address locking
switch(config-address-locking)# dhcp server ipv4 172.13.21.3The address-locking disable command disables IP Address Locking on a switch.
Command Mode
Address Locking Configuration
Command Syntax
address-locking disable
Example
switch(config)# address-locking
switch(config-address-locking)# disableUse the address locking command to enter the IPv4 and IPv6 locking mode and then on the switch, use the lease to configure DHCP leases.
The lease mac command within the address locking configuration mode installs a lease onto hardware for the configured IP address on the interface with the associated configured MAC address. If the MAC address does not exist in the MAC table or the MAC address appears on an interface with an IP Locking configuration feature, the lease does not install until you add the MAC address to an interface configured with IP Locking.
Command Mode
Address Locking Configuration
Command Syntax
lease ip_address mac ip_address
Example
switch(config)# address locking
switch(config-address-locking)# lease 1.1.1.1 mac a.b.cUse the address locking command to enter the IPv4 and IPv6 locking mode and then use the lease query retry interval to configure DHCP leases.
The no lease query retry command removes the retry interval and timeout configuration.
Command Mode
Address Locking Configuration
Command Syntax
lease query retry interval interval-time
Parameters
interval interval-time - Configure the query retry interval and timeout. The interval can be from 1 - 4294967295 seconds.
Example
switch(config)# address locking
switch(config-address-locking)# lease query retry interval 5 timeout 100Use the address locking local-interface command to configure a local interface for IPv4 and IPv6 locking IP addresses on the switch.
Command Mode
Address Locking Configuration
Command Syntax
address locking local-interface [Ethernet | Loopback | Management | Port Channel | Tunnel | Vlan]
Example
switch(config)# address locking
switch(config-address-locking)# local-interface Ethernet53/4Use the clear address locking lease command to remove lease bindings at different granularities.
Command Mode
Address Locking mode
Command Syntax
clear address locking lease [ all | interface [ ethernet slot ] | ipv4 V4ADDR | ipv6 V6ADDR ]
Example
switch(config-address-locking)# clear address locking lease allCommand Mode
Address Locking Configuration
Command Syntax
dhcp server interface <INTF>
Parameter
<INTF> - Specify the DHCP server interface.
Example
switch# conf
switch(config)# address locking
switch(config-address-locking)# dhcp server interface Ethernet28/1IP Address Locking, by default, removes authorization from leases after the corresponding MAC addresses age out. Use the locked-address expiration mac disabled command to configure IP Address Locking to keep the leases installed, even after the corresponding MAC addresses age out.
Command Mode
Address Locking Configuration
Command Syntax
locked-address expiration mac disabled
no locked-address expiration mac disabled
default locked-address expiration mac disabled
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address expiration mac disabledThe locked-address ipv4 enforcement disabled command disables address filtering for all ports with IPv4 Locking enabled. This permits IPv4 packets while still keeping all other drop rules.
Command Mode
Address Locking Configuration
Command Syntax
locked-address ipv4 enforcement disabled
no locked-address ipv4 enforcement disabled
default locked-address ipv4 enforcement disabled
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv4 enforcement disabledThe locked-address ipv6 enforcement disabled command disables address filtering for all ports with IPv6 Locking enabled. This permits IPv6 packets while retaining all other drop rules.
Command Mode
Address Locking Configuration
Command Syntax
locked-address IPv6 enforcement disabled
no locked-address IPv6 enforcement disabled
default locked-address IPv6 enforcement disabled
Example
switch# configure
switch(config)# address locking
switch(config-address-locking)# locked-address ipv6 enforcement disabledUse the show address locking command to display the status of IP and IPv6 locking.
Command Mode
EXEC
Command Syntax
show address locking
Example
switch# show address locking
IP Locking is active
Interface IPv4 IPv6
--------------- ------------------- ---------------------------
Ethernet27/1 yes no (not configured)
Ethernet31/1 no (not configured) no (not a layer 2 interface)Command Mode
EXEC
Command Syntax
show address locking counters
Related Commands
The clear address locking counters command resets all the counters associated with IP Locking to zero.
switch# show address locking counters
Lease Active Lease Unknown Lease Unassigned
DHCP Server Query Rcvd Drop Rcvd Drop Rcvd Drop Unknown
----------- ----- ----- ------ ------ ------ -------- ------- -------
80.80.80.80 32860 8002 34 8001 32 13423 134 3234
Interface Query Lease Active Lease Unknown Lease Unassigned
--------- ----- ------------ ------------- ----------------
Ethernet2 1747 1234 189 324switch# show address locking counters detail
Action Count
-------------------------------- --------
DHCP from client to server PERMIT 0
DHCP from server DROP 0
ARP (0.0.0.0) PERMIT 3
DHCP6 to client DROP 2
DHCP6 to server PERMIT 2
NDP Router Solicitation PERMIT 1
NDP Router Advertisement DROP 1
NDP Router Redirect DROP 0
DHCP from server on VLAN DROP 2
DHCP from client to server on VLAN PERMIT 2
ARP (0.0.0.0) on VLAN PERMIT 1
DHCP6 to client on VLAN DROP 2
DHCP6 to server on VLAN PERMIT 2
NDP Router Solicitation on VLAN PERMIT 2
NDP Router Advertisement on VLAN DROP 1
NDP Router Redirect on VLAN DROP 2
Interface Action IP MAC Count
----------- ----------------------- ------- ---------------- -----
Ethernet46 unknown ARP on VLAN DROP any any 5
Ethernet46 unknown IP on VLAN DROP any any 5
Ethernet46 unknown ARP DROP any any 0
Ethernet46 unknown IP DROP any any 0
Ethernet49/1 ARP DROP 10.0.0.1 any 0
Ethernet49/1 IP DROP 10.0.0.1 any 5
Ethernet49/1 ARP PERMIT 10.0.0.2 c4:01:32:58:00:00 0
Ethernet49/1 IP PERMIT 10.0.0.2 c4:01:32:58:00:00 0switch# show address locking counters detail ipv4
Action Count
-------------------------------- --------
DHCP from client to server PERMIT 0
DHCP from server DROP 0
ARP (0.0.0.0) PERMIT 3
DHCP from server on VLAN DROP 2
DHCP from client to server on VLAN PERMIT 2
ARP (0.0.0.0) on VLAN PERMIT 1
Interface Action IP MAC Count
------------ ------------------------ -------- ----------------- -----
Ethernet46 unknown ARP on VLAN DROP any any 5
Ethernet46 unknown IP on VLAN DROP any any 5
Ethernet46 unknown ARP DROP any any 0
Ethernet46 unknown IP DROP any any 0
Ethernet49/1 ARP DROP 10.0.0.1 any 0
Ethernet49/1 IP DROP 10.0.0.1 any 5
Ethernet49/1 ARP PERMIT 10.0.0.2 c4:01:32:58:00:00 0
Ethernet49/1 IP PERMIT 10.0.0.2 c4:01:32:58:00:00 0switch# show address locking counters detail ipv6
Action Count
-------------------------------- --------
DHCP6 to client DROP 2
DHCP6 to server PERMIT 2
NDP Router Solicitation PERMIT 1
NDP Router Advertisement DROP 1
NDP Router Redirect DROP 0
DHCP6 to client on VLAN DROP 2
DHCP6 to server on VLAN PERMIT 2
NDP Router Solicitation on VLAN PERMIT 2
NDP Router Advertisement on VLAN DROP 1
NDP Router Redirect on VLAN DROP 2switch# show address locking counters detail ipv4 interface Et49/1
Interface Action IP MAC Count
------------ ------------------------ -------- ----------------- -----
Ethernet49/1 ARP DROP 10.0.0.1 any 0
Ethernet49/1 IP DROP 10.0.0.1 any 5
Ethernet49/1 ARP PERMIT 10.0.0.2 c4:01:32:58:00:00 0
Ethernet49/1 IP PERMIT 10.0.0.2 c4:01:32:58:00:00 0 Use the show address locking table ipv4 command to display all DHCP leases with IP Locking, and the interfaces with authorized the IP addresses.
Command Mode
EXEC
Command Syntax
show address locking table ipv4 [ dynamic [ installed | [ interface Ethernet slot ] | installed | interface [ Ethernet [ slot ] | static [ installed | interface [ Ethernet slot ]]]
switch# show address locking table ipv4
IP Address MAC Address Interface Installed Expiration Time
-------------- ---------------- ---------- ------------ ---------------
AC 10.30.4.4 ba76.a467.7ff8 Et27/1 installed in 0:01:57
IP Address Action
--------------- --------
10.30.4.4 permit