Integrated Routing and Bridging
In traditional data center design, inter-subnet forwarding is provided by a centralized router, where traffic traverses across the network to a centralized routing node and back again to its final destination. In a large multi-tenant data center environment this operational model can lead to inefficient use of bandwidth and sub-optimal forwarding.
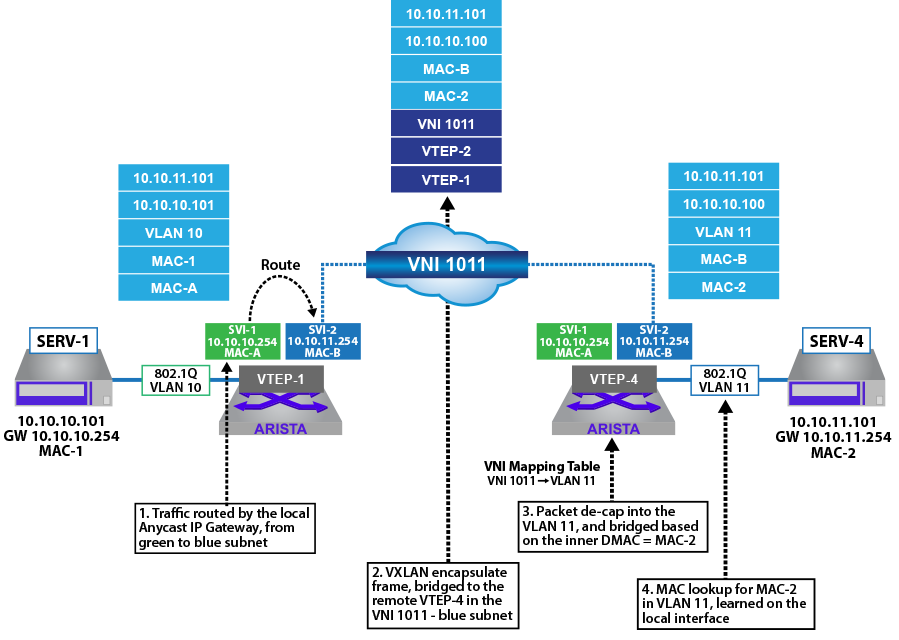
To provide a more optimal forwarding model and avoid traffic tromboning, the IETF draft Integrated Routing and Bridging in evpn proposes integrating routing and bridging functionality directly onto the VTEP, thereby allowing the routing operation to occur as close to the end host as possible. The draft proposes two forwarding models for the Integrated Routing and Bridging (IRB) functionality, which are termed asymmetric IRB and symmetric IRB.These two models are described in the following sections.
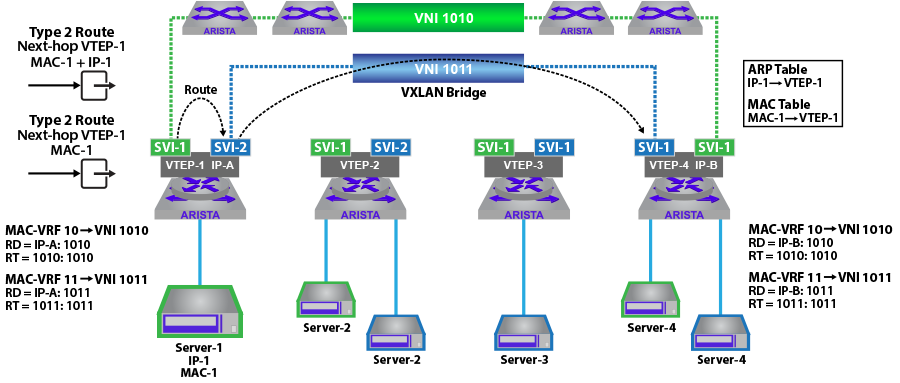
To provide inter-subnet routing on all VTEPs for all subnets, an anycast IP address is utilized for each subnet and configured on each VTEP. The anycast IP acts as the default gateway for the hosts; therefore, regardless of where the host resides, the directly attached VTEPs can act as the host’s default gateway. The host MAC and MAC to IP bindings are learned by each VTEP based on a combination of local learning/ARP snooping and type-2 route advertisement from remote VTEPs.
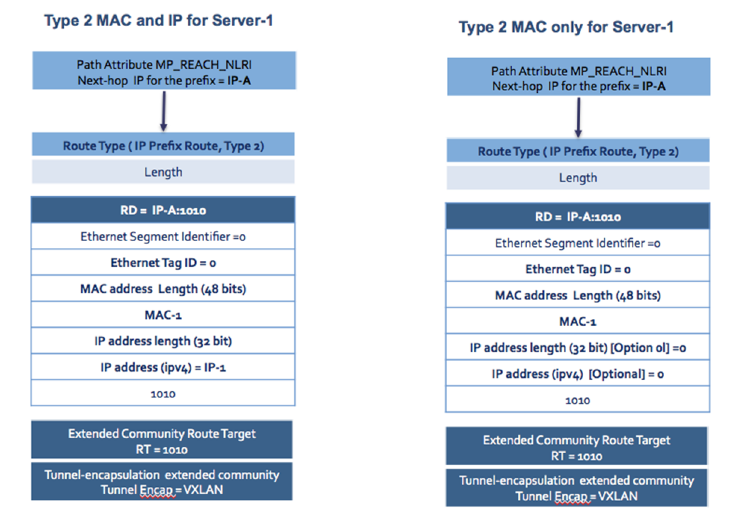
In a typical implementation, the optional MAC and IP, type-2 route is advertised separately from the MAC only type-2 route. This is done so that if the MAC and IP route is cleared, for example the ARP flushed, or the ARP timeout is set to less than the MAC timeout, then the MAC only route will still exist.
- VNI Scaling: The number of VNIs supported on a hardware VTEP will be finite, so not all VNIs can reside on all VTEPs. This is especially true in data-center deployments, where the TOR’s have traditionally been more resource constrained than chassis-based edge systems.
- Forwarding memory scaling: The VTEPs needs to store all host MACs and ARP entries for all subnets in the network, on leaf switch this is hardware resource which again will be a finite resource defined by the specific hardware platform deployed at the leaf.
Symmetric IRB
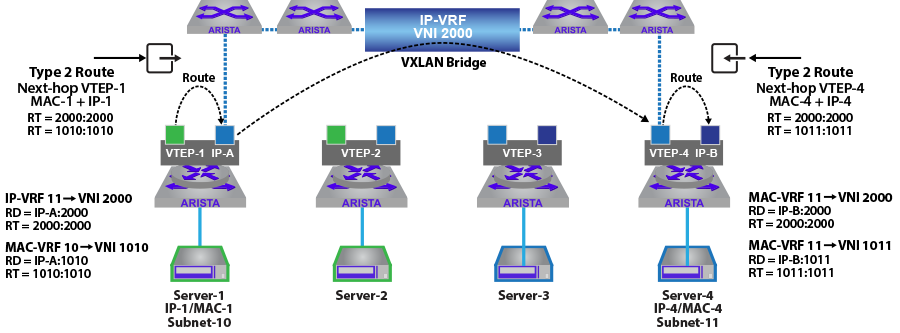
To provide the inter-subnet routing, when the subnet is stretched across multiple VTEPs, an anycast IP address is utilized for each subnet, but only configured on the VTEP’s where the subnet exists. The host MAC and MAC to IP bindings are learned by each VTEP based on a combination of local learning/ARP snooping and type-2 route advertisements.
For the symmetric IRB model the type-2 (MAC and IP) route is advertised with two labels and two route-targets corresponding to the MAC-VRF the MAC address is learned on and the IP-VRF. Remote VTEP’s receiving the route, import the IP host route into the corresponding IP-VRF based on the IP-VRF route-target and if the corresponding MAC-VRF exists on the VTEP the MAC address is imported into the local MAC-VRF based on the MAC-VRF’s Route-Target. The import behavior for the type-2 route is illustrated in the diagrams below for the host Server-1.
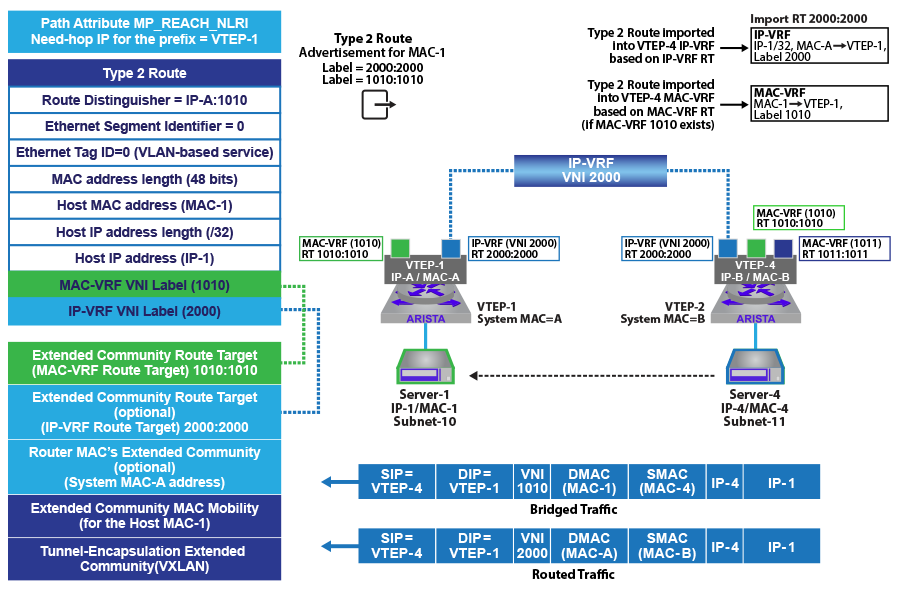
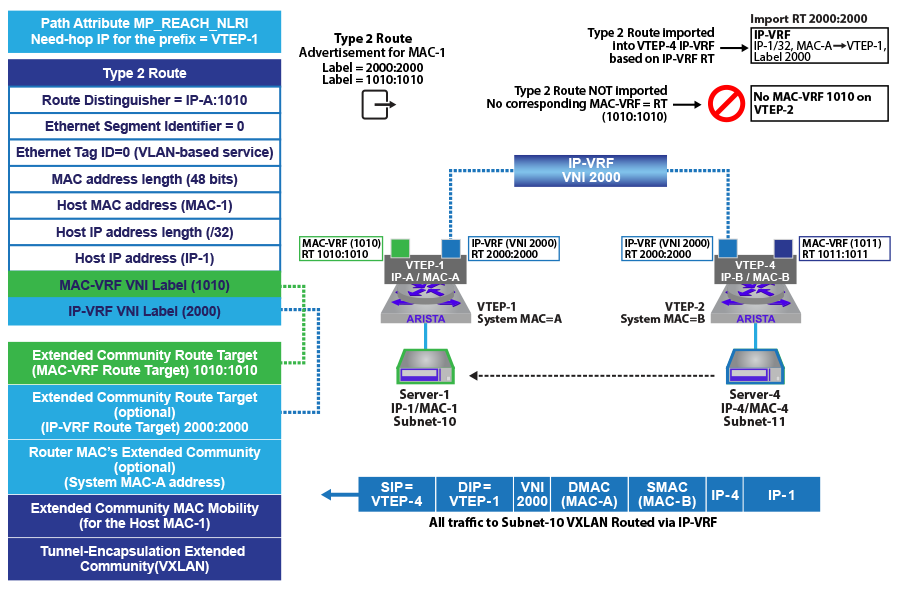
- Multi-protocol Reachable NLRI (MP_REACH_NLRI) attribute carries the next-hop hop for the advertised route. In the context of a VXLAN forwarding plane, this becomes the source address of the advertising VTEP.
- Route Distinguisher of the advertising node’s MAC-VRF. For Server-1 in the example above, this would be IPA:1010.
- MAC address field contains the 48-bit MAC address of the host being advertised. For Server-1 in the example above, this would be MAC-1.
- IP address and length fields contain the IP address and 32-bit mask for the host being advertised. For Server-1 in the example above, this would be IP-1.
- MAC-VRF label, this contains the VNI number (label) corresponding to the local Layer 2 domain/MAC-VRF the host MAC was learned on. For Server-1 in the example above, this would be VNI 1010.
- IP-VRF label, this contains the VNI number (label) corresponding to the MAC-VRF’s associated lP-VRF. For MAC-VRF 10 in the example above, this would be IP-VRF 2000.
- Extended community Route Target for the IP-VRF. This contains the route-target of the IP-VRF associated with the learned MAC address.
- Extended community Router MAC. This field advertises the system MAC of the advertising VTEP and is used as the DMAC for any packet sent to the VTEP via the IP-VRF.
- Extended community Route Target for the MAC-VRF. This contains the route-target of the MAC-VRF associated with the learned MAC address.
IP VPN
- Maintaining privacy.
- Allowing for IP address overlap amongst customers.
- Constraining route distribution - so that only the service provider routers that need the routes have them.
This is achieved through the usage of VRFs, Route Distinguishers and Route-Targets
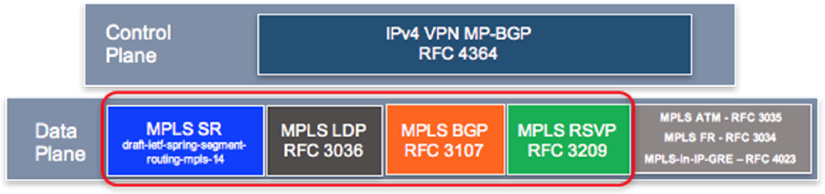
- Specifics an BGP IPv4 VPN control plane with a MPLS data plane.
- BGP control plane, new address family to advertise IP VPN prefixes.
- This RFC obsoleted the original RFC 2547.
- MPLS data-plane defined in multiple RFCs and drafts.
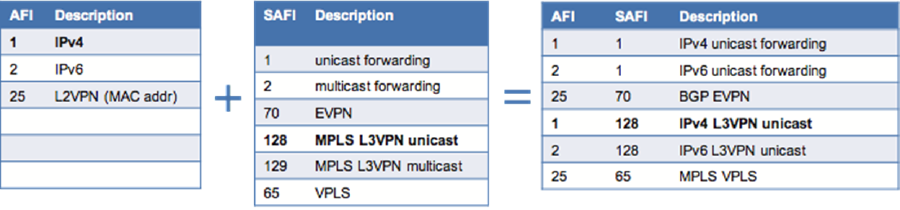
- Update
- Withdrawal
Each route type has its own NLRI prefix format and ach route type advertises its own set of prefixes to update/withdraw.
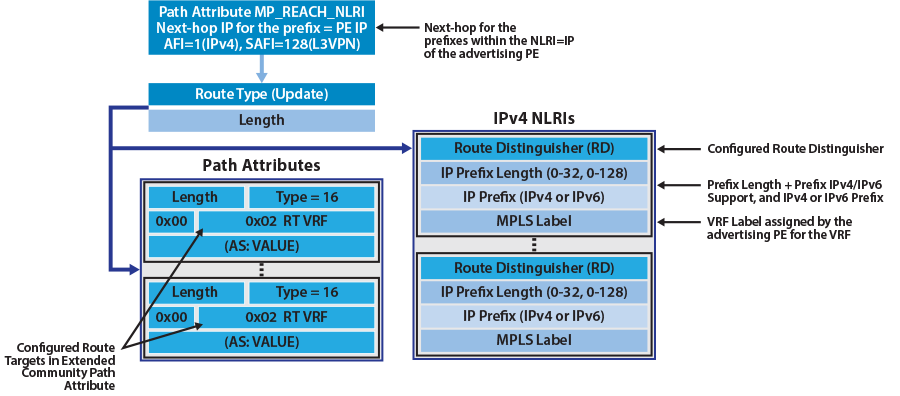
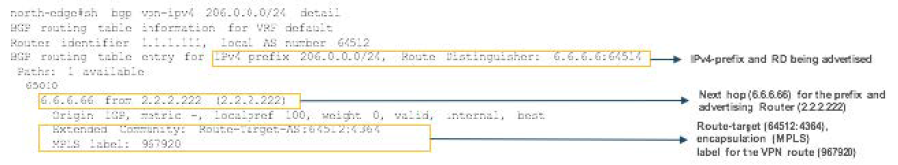
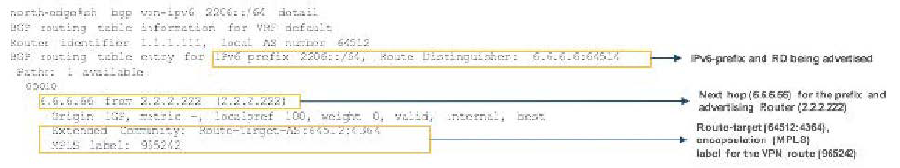
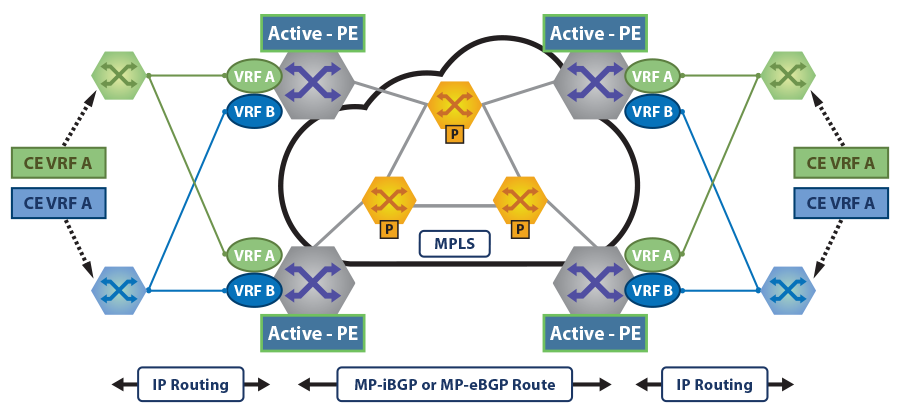
An IP VRF is used on a PE router for each customer (Layer 3 overlay). VRF IP routes are exported into the MP-BGP table and advertised to remote PEs as VPN routes. The exported VPN routes carry the Route-Target (RT) extended communities that are configured as export route-targets on the IP VRF from which they were exported.
The RTs carried by the VPN routes received by a PE are matched against the VRF import route-target configuration. When a received route carries an RT that is configured as an import route-target on an IP VRF, the route is imported into the IPv4 or IPv6 table for that VRF.
PE routers allocate per-VRF and address family Labels that are advertised as part of the VPN route NLRI. Forwarding of overlay packets between PEs across the underlay requires underlay MPLS connectivity provided by a backbone.