Security
The Security section contains the following topics:
The switch authenticates user identity and verifies user authorization to control access to EOS commands. Three data services conduct authentication, authorization, and accounting (AAA) activities: a local security database, TACACS+ servers, and RADIUS servers.
The Configuring the Security Services section provides details about these services.
EOS uses aaa authorization, aaa authentication, and aaa accounting commands to manage the primary and backup services. The Activating Security Services section provides details on implementing a security environment.
The switch uses clear-text passwords and server access keys to authenticate users and communicate with security systems. To safeguard against accidental disclosure of passwords and keys, running-config stores encrypted versions of these passwords and keys. The encryption method depends on the type of password or key.
Commands used to configure passwords or keys can accept either the clear-text password or an encrypted string generated by the designated encryption algorithm, using the clear-text password as the basis (seed) for encryption.
The switch can access three security data services to authenticate users and authorize switch tasks: a local file, TACACS+ servers, and RADIUS Servers.
The local file stores username-password combinations for user authentication. Passwords also control access to configuration commands and the switch's root login.
Valid passwords can include characters A-Z, a-z, 0-9, and any of the following punctuation characters:
! @ # $ % ^ & * ( ) - _ = + { } [ ] ; : < > , . ? / ~ \
Usernames govern access to the EOS and all switch commands. You typically access the switch through an SSH login using a previously defined username and password. Use the username command to create a new username or change an existing one.
Valid usernames begin with A-Z, a-z, or 0-9 and may also contain any of these characters:
@ # $ % ^ & * - _ = + ; < > , . ~ |
The default username is admin, which the section on Admin Username explains.
switch(config)# username john secret x245
switch(config)# username john secret 0 x245switch(config)# username john secret 5 $1$sU.7hptc$TsJ1qslCL7ZYVbyXNG1wg1switch(config)# username jane nopasswordswitch(config)# no username williamThe default switch configuration allows usernames that are not password-protected to log in only from the console. The aaa authentication policy local allow-nopassword-remote-login command configures the switch to allow unprotected usernames to log in from any port. To reverse this setting to the default state, use the no form of aaa authentication policy local allow-nopassword-remote-login.
switch(config)# aaa authentication policy local allow-nopassword-remote-loginswitch(config)# no aaa authentication policy local allow-nopassword-remote-loginmain-host> enable
Password:
main-host#If an incorrect password is entered three times in a row, the CLI displays the EXEC mode prompt.
If no enable password is set, the CLI does not prompt for a password when a user attempts to enter Privileged EXEC mode.
To set the enable password, use the enable password command.
switch(config)# enable password xyrt1
switch(config)# enable password 0 xyrt1switch(config)# enable password 5 $1$8bPBrJnd$Z8wbKLHpJEd7d4tc5Z/6h/switch(config)# no enable passwordThe root account accesses the root directory in the underlying Linux shell. When it is not password protected, you can log into the root account only through the console port. After you assign a password to the root account, you can log in through any port.
To set the password for the root account, use the aaa root command.
switch(config)# aaa root secret f4980
switch(config)# aaa root secret 0 f4980switch(config)# aaa root secret 5 $1$HW05LEY8$QEVw6JqjD9VqDfh.O8r.bswitch(config)# aaa root nopasswordswitch(config)# no aaa rootRemote Authentication Dial-In User Service (RADIUS) consists of a networking protocol that provides centralized AAA services for computers connecting to a network and then using network resources. RADIUS manages access to the Internet, internal networks, wireless networks, and integrated email services.
These sections describe the steps to configure access to RADIUS servers. Before configuring switch parameters,confirm yourRADIUS server functionality.
RADIUS servers and client companies extend basic RADIUS functionality through vendor-specific attributes. A dictionary file includes a list of RADIUS attribute-value pairs that Arista switches use to perform AAA operations through the RADIUS server.
Example
#
# dictionary.arista
#
VENDOR           Arista    30065
#   Standard Attribute
BEGIN-VENDOR     Arista
ATTRIBUTE        Arista-AVPair    1    string
END-VENDOR AristaRADIUS policies specify the settings the switch uses to communicate with RADIUS servers. Configure a set of values for each RADIUS server that the switch accesses. Global parameters define settings for communicating with servers without configured individual parameters.
The switch defines the following RADIUS parameters.
switch(config)# radius-server host RAD-1 key rp31E2v switch(config)# radius-server key 0 cv90jr1switch(config)# radius-server key 7 020512025B0C1D70switch(config)# radius-server host RAD-1 timeout 20switch(config)# radius-server timeout 50switch(config)# radius-server host RAD-1 retransmit 2switch(config)# radius-server retransmit 5switch(config)# radius-server host RAD-1 deadtime 90switch(config)# radius-server deadtime 120Example
switch(config)# radius-server host RAD-1 auth-port 1850
switch(config)# radius-server host RAD-1 acct-port 1851
To remove the configuration for this server, use the no radius-server host command and specify the hostname or IP address with both the authorization and accounting port numbers.
Adjust the MTU of RADIUS requests for 802.1x supplicants using EAP TLS authentication. Adjusting the size may be useful where the hops between the switches and the RADIUS server do not support IP MTU discovery and the switch sends Access Requests based on the interface MTU size. Configuring this feature allows you to select an MTU size compatible with the topology and forces the Dot1x agent to send Access Requests with the configured MTU.
switch(config)# dot1x
switch(config-dot1x)# radius mtu 1500
switch(config-dot1x)Arista-Config-Vlan, with attribute ID 22, that contains the configured VLAN and sent only in the Access-Request.Tunnel-Private-Group-ID, sent in both Access-Requests and Accounting-Requests with the Tunnel-Type and Tunnel-Medium-Type attributes.Values Sent in Tunnel-Private-Group-Id
The Tunnel-Private-Group-Id attribute in the Accounting-Request always contains the VLAN of the supplicant. The behavior of the Tunnel-Private-Group-Id attribute in the Access-Request depends on the current state of the port and the supplicant type.
Unauthorized Port
Tunnel-Private-Group-Id attribute:
Supplicants on ports in fallback VLANs, such as AAA Unresponsive VLAN, Guest VLAN, or Auth Fail VLAN, receive treatment similar to those on unauthorized ports.
Authorized Ports
Configuring VLANs in AAA Requests
switch(config)# dot1x
switch(config-dot1x)# radius av-pair config-vlan
switch(config-dot1x)#switch(config)# dot1x
switch(config-dot1x)# radius av-pair tunnel-private-group-id
switch(config-dot1x)#Enable a RADIUS proxy to send requests from a RADIUS client and forward them to a remote RADIUS server. In return, the RADIUS proxy receives the reply from the remote RADIUS server and forwards it to the client. Dynamic authorization requests initiated by remote servers also proxy to the correct clients based on the user name and calling station ID.
switch(config)# radius proxy
switch(config-radius-proxy)#A client group consists of a set of IPv4 or IPv6 prefixes, addresses, or hostnames. RADIUS proxies the requests from these clients to the configured RADIUS server. A client may belong to a VRF and can be configured with the VRF key.
Example
switch(config)# radius proxy
switch(config-radius-proxy)# client group MyClientGroup
switch(config-radius-proxy-MyClientGroup)# client 192.168.1.25 vrf default key 0 password1234A client group can be associated with one or more server groups. The server groups proxy the client requests in the order of configuration. The following example, the client group, MyClientGroup sends all client requests and proxies the request in the order of the configured server groups.
switch(config-radius-proxy)# client group MyClientGroup
switch(config-radius-proxy-MyClientGroup)# server group RADIUS1 RADIUS2 RADIUS3The client key command configures a global key, up to 128 characters, for all clients in all client groups:
Example
switch(config-radius-proxy)# client key MySuperSecretKeyThe client session idle-timeout following command to configure the client session idle timeout, in seconds, for dynamic authorization. EOS uses 600 seconds by default. The configuration applies globally to the configuration.
Example
switch(config-radius-proxy)# client session idle-timeout 300 secondsThe dynamic-authorization command enables dynamic authorization for RADIUS proxy server groups configured for client groups. Dynamic authorization uses port 3799 for UDP authorization requests and port 2083 for TLS authorization requests.
Example
switch(config-radius-proxy)# dynamic-authorizationConfigure RADIUS to send authentication requests across all reachable or live servers within a RADIUS server group and select a server group using round robin for new authentication requests. The configured dead timer or server probe determines the reachability or liveliness of the RADIUS servers.
switch(config)# dot1x
                switch(config-dot1x)# aaa authentication load-balance round-robin
switch(config-dot1x)#The show radius proxy client group command displays information about the RADIUS proxy configuration on the switch.
Example
switch# show radius proxy client group
Radius Client Group                : MyClientGroup
Last time counters were cleared    : never

     Client                          : 192.168.1.25, authentication port 1812, accounting port 1813, vrf default
     Resolved IP address             : 192.168.1.25/32
            Messages received:          0
                Messages sent:          0
         Accept response sent:          0
         Reject response sent:          0
    Accounting start received:          0
     Interim updates received:          0
     Accounting stop received:          0
                 Bad requests:          0
            CoA requests sent:          0
             DM requests sent:          0
            CoA ACKs received:          0
             DM ACKs received:          0
            CoA NAKs received:          0
             DM NAKs received:          0
                Bad responses:          0
Connection errors: 0switch# show radius proxy server group
Radius Server Group: MyServerGroup
Radius Server 1: RADIUS
Resolved IP address: 192.168.25.33
Status: activeTo clear the counters, use the clear radius proxy counters client group command.
Arista EOS implements Per-MAC Access Lists (Per-Host ACLs) to provide granular security at the individual device level. Unlike standard port-based ACLs, this feature allows the switch to apply unique IPv4 or IPv6 filtering rules to each 802.1X supplicant, even when they share the same physical interface.
When a device authenticates via 802.1X, the switch identifies the device by the MAC address. The system then applies a specific ACL to that MAC address traffic flow. This ensures that a compromised or unauthorized device cannot access restricted resources, even iflocated behind a port used by other authorized devices.
switch(config)# mac traffic-policies
switch(config-mac-traffic-policies)# field-set mac MAC8021x
switch(config-macTp-field-set-mac-MAC8021x)# 2601:600:c903:5708:3e:3fb0:a22f:fd6a
switch(config-macTp-field-set-mac-MAC8021x)# 2601:600:c903:5708:3e:3fb0:a22f:fe7bswitch(config-macTp-field-set-mac-MAC8021x)# exit
switch(config-mac-traffic-policies)# traffic-policy
switch(config-mac-traffic-policy)#switch(config-mac-traffic-policy)# match M1
switch(config-mac-traffic-policy-match-M1)# source mac field-set MAC8021x
switch(config-mac-traffic-policy-match-M1)#switch(config-mac-traffic-policy-match-M1)# actions
switch(config-mac-traffic-policy-actions-M1)# access-list ACL1switch(config-mac-traffic-policies)# host move disabled
switch(config-mac-traffic-policies)#switch(config-mac-traffic-policies)# no disabledBe default, the MAC Traffic Policy applies globally to the configuration, and also applies to all traffic with a specified MAC regardless of the port. If you configure the host move disabled parameter and an authenticated MAC appears on any other interface other than the authenticated interface, the Per MAC ACL does not apply to it.
switch(config)# radius-server qos dscp 62switch(config)# tacacs-server qos dscp 36switch(config)# snmp-server qos dscp 36switch(config)# sFlow qos dscp 36switch(config)# snmp-server qos dscp 36EOS uses Status-Server packets to probe RADIUS servers and configures the format of the packet. EOS considers the Status-Server packets as successful in the following situations:
Since a probe can drop or get lost on the network, declaring a server unresponsive after sending a single probe may not be desirable on your network. Use the fail
count parameter to configure the number of probes sent before declaring a server as unresponsive. The parameter has a default value of 1.
switch(config)# monitor server radius
switch(config-monitor-radius)# service dot1x
switch(config-monitor-radius)#Configuring the Probe Properties
access-request or server-status with a default value of server-status. The parameter access-request requires a username and password configured on the switch and the RADIUS server.600
seconds, method as server-status, and a threshold of 50:
switch(config)# monitor server radius
switch(config-monitor-server-radius)# probe interval 600 seconds
switch(config-monitor-server-radius)# probe method server-status
switch(config-monitor-server-radius)# probe threshold failure 50show monitor server radius command to display information about the RADIUS servers:
switch(config)# show monitor server radius
Probe method: Status-Server packet
RADIUS Server Messages Sent Messages Accepted Messages Dropped Status
------------- ------------- ----------------- ---------------- ---------
10.0.0.101 48 35 1 alive
10.0.0.102 48 29 1 not aliveshow monitor server radius detail command to display details about the RADIUS servers:
switch(config)# show monitor server radius detail
Probe method: Status-Server packet
RADIUS server: 10.0.0.101, Authentication port: 33922, Accounting port: 34685
Status: alive, Last changed: 0:02:32 ago
Last probed: 0:00:02 ago
Last successful probe: 0:00:02 ago, Failed probes since then: 0
Messages sent: 47
Messages accepted: 34
Messages dropped: 1
Last time counters were cleared: never
RADIUS server: 10.0.0.102 Authentication port: 34406, Accounting port: 47258
Status: not alive, Last changed: 0:00:12 ago
Last probed: 0:00:02 ago
Last successful probe: 0:00:27 ago, Failed probes since then: 4
Messages sent: 47
Messages accepted: 29
Messages dropped: 1
Last time counters were cleared: neverThe show radius command displays configured RADIUS servers and their interactions with the switch.
switch(config)# show radius
server1: 10.1.1.45
Messages sent: 24
Messages received: 20
Requests accepted: 14
Requests rejected: 8
Requests timeout: 2
Requests retransmitted: 1
Bad responses: 1
Last time counters were cleared: 0:07:02 agoTo reset the RADIUS status counters, use the clear aaa counters radius command.
switch(config)# clear aaa counters radiusTerminal Access Controller Access-Control System Plus (TACACS+), derived from the TACACS protocol defined in RFC 1492, is a network protocol that provides centralized user validation services. A remote database maintains TACACS+ information. EOS requires access to a TACACS+ server to support TACACS+ services.
TACACS+ manages multiple network access points from a single server. The switch defines a TACACS+ server connection by its address and port, allowing it to conduct multiple data streams to a single server by addressing different ports on the server.
These sections describe the steps to configure access to TACACS+ servers. Configuring TACACS+ access is most efficient when TACACS+ is functioning before you configure switch parameters.
TACACS+ parameters define the settings the switch uses to communicate with TACACS+ servers. You can configure a set of values for individual TACACS+ servers that the switch accesses. Global parameters define settings for communicating with servers where you haven't configured individual parameters.
The switch supports the following TACACS+ parameters.
switch(config)# tacacs-server host TAC-1 key rp31E2vswitch(config)# tacacs-server key 0 cv90jr1switch(config)# tacacs-server key 7 020512025B0C1D70Example
switch(config)# tacacs-server host 10.12.7.9 single-connectionswitch(config)# tacacs-server host TAC_1 timeout 20switch(config)# tacacs-server timeout 40Example
switch(config)# tacacs-server host 10.12.7.9 port 54To display the TACACS+ servers and their interactions with the switch, use the show tacacs command.
Example
switch(config)# show tacacs
server1: 10.1.1.45
Connection opens: 15
Connection closes: 6
Connection disconnects: 6
Connection failures: 0
Connection timeouts: 2
Messages sent: 45
Messages received: 14
Receive errors: 2
Receive timeouts: 2
Send timeouts: 3
Last time counters were cleared: 0:07:02 agoTo reset the TACACS+ status counters, use the clear aaa counters tacacs+ command.
Example
switch(config)# clear aaa counters tacacsThe switches support AAA with the LDAP protocol for authentication and authorization. They use Transport Layer Security (TLS) communication with a remote LDAP server and interoperate with Microsoft's Active Directory when configured with LDAP plugins. LDAP authentication configuration is necessary for LDAP to function. The switch sends AAA requests to servers in the order of their configuration. Once marked unreachable, the switch will only retry a server after all other servers are also found unreachable.
For all platforms, the ldap command is configured from the management ldap mode and requires configuration files to provide remote authentication.
aaa authentication login default group ldap local
aaa authorization exec default group ldap local
!
management ldap
server host ldap-server.samplecompany.com
!
server defaults
base-dn dc=samplecompany,dc=com
rdn attribute user cn
ssl-profile testProfile
authorization group policy basic-role-example
search username cn=ldap-admin-acct,OU=ServiceAccounts,OU=Sample,dc=samplecompany,dc=com password 0 secretString
!
group policy basic-role-example
search filter objectclass group attribute member
group "Network Admin" role network-admin
group "Network Newbie" role network-operator
!
management security
ssl profile testProfile
fips restrictions
trust certificate caCert
!management ldap
server host ldap-server.samplecompany.com
ssl-profile testProfile2
authorization group policy company1
!
Server host ldap-server.company2.com
!
server defaults
base-dn dc=samplecompany,dc=com
rdn attribute user cn
ssl-profile testProfile1
authorization group policy basic-role-example
search username cn=ldap-admin-acct,OU=ServiceAccounts,OU=Sample,dc=samplecompany,dc=com password 0 secretString
!
group policy basic-role-example
search filter objectclass group attribute member
group "Network Admin" role network-admin
group "Network Newbie" role network-operator
!
group policy company1
search filter objectclass group attribute member
group "Network Admin2" role network-admin
group "Network Newbie2" role network-operator
!aaa authentication login default group ldap
!
management ldap
server host <ldap server hostname/ip>
!
server defaults
base-dn <base distinguished name>
rdn attribute user <relative distinguished attribute name>
search username <full distinguished name> password <password>The configuration sets up AAA authentication with LDAP. The LDAP server supports IPv4, IPv6, hostnames, and VRFs for specifying the address. The RDN, relative distinguished name, is typically an attribute/value pair to specify a user. When a user attempts to connect to the switch, the admin username searches recursively for the RDNs that match the passed-in username from the base-dn folder to generate a shortened list of potential DNs, which are then searched for a match with the provided password.
Active Directory Server with LDAP Plugin Configured
aaa authorization exec default group ldap
!
management ldap
server defaults
authorization group policy basic-role-example
!
group policy basic-role-example
search filter objectclass group attribute member
group "Network Admin" role network-admin
group "Network Newbie" role network-operatorThe group/role maps an LDAP group to an EOS role for RBAC. The matching process ensures that the first matched group results in the role being assigned to the user. Use the before and after commands to insert rules in the appropriate priority.
The LDAP admin account uses the search filter command to search for LDAP groups that contain the user, where objectclass defines the object that contains the LDAP group, and attribute is the entry attribute name that contains the DN of the group member.Active Directory Server with LDAP Plugin Configured
management ldap
!
server defaults
ssl-profile testProfile
management security
ssl profile testProfile
trust certificate <root of trust>A server group is a collection of servers associated with a single group name. Subsequent authorization and authentication commands can access all servers in a group by invoking the group name. The switch supports TACACS+ and RADIUS server groups.
The aaa group server commands create server groups and place the switch in a server-group configuration mode to assign servers to the group. Commands referencing an existing group place the switch in a server-group configuration mode to modify the group.
The server (server-group-RADIUS configuration mode) commands add servers to the configuration mode server group. Before they are added to a group, servers must have been previously configured with a radius-server host or tacacs-server host command.
switch(config)# aaa group server tacacs+ TAC-GR
switch(config-sg-tacacs+-TAC-GR)#The CLI remains in server-group configuration mode after adding the TAC-1 server (port 49) and the server located at 10.1.4.14 (port 151) to the group.
switch(config-sg-tacacs+-TAC-GR)# server TAC-1
switch(config-sg-tacacs+-TAC-GR)# server 10.1.4.14 port 151
switch(config-sg-tacacs+-TAC-GR)#switch(config-sg-tacacs+-TAC-GR)# exit
switch(config)#switch(config)# aaa group server radius RAD-SV1
switch(config-sg-radius-RAD-SV1)#The CLI remains in server-group configuration mode after adding the RAC-1 server (authorization port 1812, accounting port 1813) and the server located at 10.1.5.14 (authorization port 1812, accounting port 1850) to the group.
switch(config-sg-radius-RAD-SV1)# server RAC-1
switch(config-sg-radius-RAD-SV1)# server 10.1.5.14 acct-port 1850
switch(config-sg-radius-RAD-SV1)#Role-based authorization is a method of restricting access to CLI commands through the assignment of profiles, called roles, to user accounts. Each role consists of rules that permit or deny access to a set of commands within specified command modes.
All roles are accessible to the local security file through a username parameter and to remote users through RADIUS or TACACS+ servers. You can apply each role to multiple user accounts, but only one role to each user.
Built-in roles supplied by the switch are network-operator and network-admin.
Upon its entry in the CLI, a command is compared to the first rule of the role. Commands that match the rule are executed (permit rule) or disregarded (deny rule). Commands that do not match the rule are compared to the next rule. This process continues until the command either matches a rule or the rule list is exhausted. The switch disregards commands that do not match any rule.
Role rules have four components: sequence number, filter type, mode expression, and command expression.
The sequence number designates a rule’s placement in the role. Sequence numbers range in value from 1 to 256. Rule commands that do not include a sequence number append the rule at the end of the list, deriving its sequence number by adding 10 to the sequence number of the last rule in the list.
Example
10 deny mode exec command reload
20 deny mode config command (no |default )?routerThe filter type specifies the disposition of matching commands. The filter types are permit and deny. Commands matching permit rules are executed, and commands matching deny rules are disregarded.
Example
10 deny mode exec command reload
20 permit mode config command interfaceswitch(config)# prompt switch%p
switch(config)# interface ethernet 1
switch(config-if)# exit
switch(config)# prompt switch%P
switch(config)# interface ethernet 1
switch(config-if-Et1)#The command supports the use of regular expressions to reference multiple command modes.
The command expression is a regular expression that corresponds to one or more CLI commands.
Examples
The network-admin role is typically assigned to the admin user to allow it to run any command.
Built-in roles are not editable.
Example
switch(config)# show users roles network-operator
The default role is network-operator
role: network-operator
10 deny mode exec command bash|\|
20 permit mode exec command .*
switch(config)# show users roles network-admin
The default role is network-operator
role: network-admin
10 permit command .*
switch(config)#Roles are created and modified in Role configuration mode. To create a role, enter the role command with the role’s name. The switch enters Role configuration mode. If the name of an existing role follows the command, subsequent commands edit that role.
Example
switch(config)# role sysuser
switch(config-role-sysuser)#Role configuration mode is a group-change mode; changes are saved by exiting the mode.
switch(config)# role sysuser
switch(config-role-sysuser)# deny mode exec command reload
switch(config-role-sysuser)# show users roles sysuser
The default role is network-operator
switch(config-role-sysuser)#switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
switch(config)#The abort command exits the Role configuration mode without saving pending changes.
Example
switch(config)# role sysuser
switch(config-role-sysuser)# deny mode exec command reload
switch(config-role-sysuser)# abort
switch(config)# show users roles sysuser
The default role is network-operator
switch(config)#The deny (Role) command adds a deny rule to the configuration mode role. The permit (Role) command adds a permit rule to the configuration mode role.
To append a rule to the end of a role, enter the rule without a sequence number while in Role Configuration Mode. The new rule's sequence number is derived by adding 10 to the last rule's sequence number.
Example
switch(config)# role sysuser
switch(config-role-sysuser)# deny mode exec command reload
switch(config-role-sysuser)# deny mode config command (no |default )?router
switch(config-role-sysuser)# permit command .*
switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
20 deny mode config command (no |default )?router
30 permit command .*
switch(config)#To insert a rule into a role, enter the rule with a sequence number between the existing rules numbers.
Example
switch(config)# role sysuser
switch(config-role-sysuser)# 15 deny mode config-all command lacp
switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
15 deny mode config-all command lacp
20 deny mode config command (no |default )router
30 permit command .*
switch(config)#switch(config-role-sysuser)# no 30
switch(config-role-sysuser)# default 30
switch(config-role-sysuser)# no permit command .*
switch(config-role-sysuser)# default permit command .*switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
15 deny mode config-all command lacp|spanning-tree
20 deny mode config command (no |default )router
switch(config)#Sequence numbers determine the order of the rules in a role. After a list editing session where existing rules are deleted, and new rules are inserted between existing rules, the sequence number distribution may not be uniform. Redistributing rule numbers changes adjusts the sequence number of rules to provide a constant difference between adjacent rules. The resequence (Role) command adjusts the sequence numbers of role rules.
Example
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
20 deny mode config-all command lacp|spanning-tree
25 deny mode config command (no |default )?router
30 permit command .*
switch(config)# role sysuser
switch(config-role-sysuser)# resequence 100 20
switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
100 deny mode exec command reload
120 deny mode config-all command lacp|spanning-tree
140 deny mode config command (no |default )?router
160 permit command .*
switch(config)#Roles are assigned to local users through the username command and to remote users through RADIUS or TACACS+ servers. Each user is assigned one role, which can be assigned to multiple local and remote users.
Users that are not explicitly assigned a role are assigned the default role. The aaa authorization policy local default-role command designates the default role. The network-operator built-in role is the default role when the default role is not configured.
switch(config)# aaa authorization policy local default-role sysuser
switch(config)# show users roles
The default role is sysuser
switch(config)#switch(config)# no aaa authorization policy local default-role
switch(config)# show users roles
The default role is network-operator
switch(config)#Roles are assigned to users with the username command's role parameter. A username whose running-config username statement does not include a role parameter is assigned the default role.
The role parameter function in a command creating a username is different from its function in a command to edit an existing name.
A username command creating a username explicitly assigns a role to the username by including the role parameter; commands without a role parameter assign the default role to the username.
Example
switch(config)# username FRED secret 0 axced role sysuser1
switch(config)# username JANE nopassword
switch(config)# show running-config
<-------OUTPUT OMITTED FROM EXAMPLE-------->
!
username FRED role sysuser1 secret 5 $1$dhJ6vrPV$PFOvJCX/vcqyIHV.vd.l20
username JANE nopassword
!
<-------OUTPUT OMITTED FROM EXAMPLE-------->
switch(config)#A username command may edit the role of a previously configured username without altering its password. However, username commands that do not include a role parameter do not change the role assignment of a username.
switch(config)# username JANE role sysuser2
switch(config)# show running-config
<-------OUTPUT OMITTED FROM EXAMPLE-------->
!
username FRED role sysuser1 secret 5 $1$dhJ6vrPV$PFOvJCX/vcqyIHV.vd.l20
username JANE role sysuser2 nopassword
!
<-------OUTPUT OMITTED FROM EXAMPLE-------->
switch(config)#switch(config)# no username FRED role
switch(config)# show running-config
<-------OUTPUT OMITTED FROM EXAMPLE-------->
!
username FRED secret 5 $1$dhJ6vrPV$PFOvJCX/vcqyIHV.vd.l20
username JANE role sysuser2 nopassword
!
<-------OUTPUT OMITTED FROM EXAMPLE-------->
switch(config)#The show users accounts command displays role assignment of the configured users. The show users detail command displays roles of users that are currently logged into the switch.
switch(config)# show users accounts
user: FRED
role: <unknown>
privilege level: 1
user: JANE
role: sysuser2
privilege level: 1
user: admin
role: network-admin
privilege level: 1
switch(config)#switch(config)# show aaa session
Session Username Roles TTY State Duration Auth Remote Host
------- --------- ------------ ------ ----- -------- ------------- ------------
2 admin network-operator ttyS0 E 0:01:21 local
4 Fred sysadmin telnet E 0:02:01 local sf.example.com
6 Jane sysuser2 ssh E 0:00:52 group radius ny.example.com
9 admin network-admin ssh E 0:00:07 local bj.example.com
10 max network-admin telnet E 0:00:07 local sf.example.comA role can be assigned to a remote user authenticated through a RADIUS server.Roles are assigned through the vendor-specific Attribute-Value (AV) pair named Arista-AVPair. When RADIUS authentication is enabled, the switch extracts the remote user’s role upon successful authentication.
Example
# Sample RADIUS server users file
"Jane" Cleartext-Password := "Abc1235"
Arista-AVPair = "shell:roles=sysuser2",
Service-Type = NAS-Prompt-User
"Mary" Cleartext-Password := "xYz$2469"
Arista-AVPair = "shell:roles=sysadmin",
Service-Type = NAS-Prompt-User
"Fred" Cleartext-Password := "rjx4#222"
Arista-AVPair = "shell:roles=network-operator",
Service-Type = NAS-Prompt-UserThe aaa authentication login command selects the user authentication service (see Configuring Service Lists ).
Example
switch(config)# aaa authentication login default group radiusswitch(config)# aaa authorization commands all default localConfigure AAA to support X.509 Certificates for Secure Shell (SSH) connections to securely send commands over an unsecured network. X.509 certificates use a type of public key authentication, and must be enabled on the switch.
| Name Extracted from the Certificate | ||
|---|---|---|
| Login User Name | Username | This email address is being protected from spambots. You need JavaScript enabled to view it. |
| Username | Valid Match | Match Failure |
| This email address is being protected from spambots. You need JavaScript enabled to view it. | Match Failure | Valid Match |
Successful login attempts must match one of the names on the certificate.
switch(config)# management ssh
switch(config-mgmt-ssh)# authentication protocol public-key keyboard-interactiveYou must add at least one trusted certificate (CA) to allow X.509 authentication, and specify a Certificate Revocation List (CRL) with revoked certificates.
switch(config)# management security
switch(config-mgmt-security)# ssl profile x509-profileswitch(config-mgmt-sec-profile-x509-profile)# trust trusted-cert switch(config-mgmt-sec-profile-x509-profile)# revocation crl name my-crlswitch(config)# management ssh
switch(config-mgmt-ssh)# authentication x509
switch(config-mgmt-ssh-auth-x509)# server ssl profile x509-profileswitch(config)# management ssh
switch(config-mgmt-ssh)# authentication x509
switch(config-mgmg-ssh-auth-x509)# username domain omit| Name Extracted from the Certificate | ||
|---|---|---|
| Login User Name | Username | This email address is being protected from spambots. You need JavaScript enabled to view it. |
| Username | Valid Match | Valid Match |
| This email address is being protected from spambots. You need JavaScript enabled to view it. | Match Failure | Match Failure |
Instead of using a CRL to perform certificate validation, use an OCSPquery to an authorized server for the revocation status of a certificate. Performing an OCSP lookup requires access to a remote OCSP server, or a local OSCP server. Configure an OCSP profile with the appropriate settings for your network.
switch(config)# managment security
switch(config-mgmt-security)# ocsp profile myOSCPLink an OCSP profile to an SSL profile by adding the parameter, revocation ocsp profile.
switch(config-mgmt-sec-ocsp-profile-myOCSP)# timeout 120switch(config-mgmt-sec-ocsp-profile-myOCSP)# url http://www.myocspserver.comswitch(config-mgmt-sec-ocsp-profile-myOCSP)# extension nonce request disabledswitch(config-mgmt-sec-ocsp-profile-myOCSP)# chain certificate requirement responder allswitch(config)# management security
switch(config-mgmt-security)# ocsp profile myOCSP
switch(config-mgmt-security-myOCSP)# vrf VRF2switch(config)# management security
switch(config-mgmt-security)# ssl profile MySSLProfile
switch(config-mgmt-security-MySSLProfile)# revocation ocsp profile myOCSPswitch(config)# show run section management ssh
management ssh
authentication X.509
server ssl profile x509-profile
username domain omitswitch(config)# show management ssh
User certificate authentication methods: x509-certificates
SSL profile: X509-profile invalid. See "show management security ssl profile” output for details.switch(config)# show management security ssl profile
Profile State Additional Information
---------------------- ------- ----------------------
ARISTA_DEFAULT_PROFILE valid
x509-profile invalid Profile has no dataswitch(config)# show run section management security
management security
ocsp profile myOCSP
chain certificate requirement responder leaf
extension nonce request response
timeout 20
url http://127.0.0.1:8080
vrf VRF2
!
ssl profile X509-profile
…
revocation ocsp profile revoke-ocsp
…In the output, only the leaf certificate validates, and an extension request requires a nonce. The timeout occurs after 20 seconds, and the URL for certificate validation set to the local address.
X.509 automatic certificate management provides support for retrieving signed X.509v3 certificates from a server using the Enrollment over Secure Transport (EST) protocol. EOS only supports EST as the client protocol.
Use protocol options to specify the details, such as server identity, validation, or retry behavior, for the EST protocol used to retrieve the certificate.
Use profile options to specify the parameters for the certificate such as a distinguished name and subject alternative name. Each certificate profile manages a single certificate and multiple certificate profiles can apply to a single protocol profile. However, a single certificate profile cannot apply to multiple protocol profiles.
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)#The parameter, connection, configures the request send and retry behavior, and includes the maximum number of retries with the configured interval between retries. A device continues to send certificate signing requests to the switch until retrieving the certificate or exceeding the number of configured retries. The maximum number of retries resets to the maximum value for each new retry initiation or the retry count changes. By default, the switch allows an infinite number of retries and the interval between each request doubles exponentially to a maximum of 24 hours.
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# connection retry count 10 interval 5 backoff exponentialswitch(config-mgmt-sec-auto-cert-proto-est-EST_1)# connection retry interval 10switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# credentials enroll username user_1 secret myS3cr3t switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# credentials re-enroll username user_1 secret myS3cr3t The server parameters identify the EST server and manage the authentication process by setting the server URL and then validating the server. The server URL must begin with https:// and only contains the relevant identifying information. When retrieving a new certificate, the server checks the URL against the subject names in the EST server certificate and against the configured hostname or IP address. Otherwise, the server rejects the connection.
The URL can contain an IPv4 or IPv6 address or a DNS and may also contain a port.
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# server url https://my-est-server.com switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# server ssl profile SSL_LabThe disabled parameter temporarily pauses retrieving credentials from the server configured for the selected EST protocol profile. Use this option when EST server errors detected on the network and prevent sending unnecessary requests while resolving issues with the server without changing the EST protocol profile parameters.
switch(config)# management security
switch(mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-est-EST1)# disabledswitch(config)# management security
switch(mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-est-EST1)# no disabledUse EST certificate profiles to manage certificates for EST and configure each profile with a unique name. A certificate profile can only manage one certificate. For example, use the following commands to create a certificate profile, CertAlpha:
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#Use the following commands add a 512 bit SHA digest algorithm to the certificate profile, CertAlpha:
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# digest sha512
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#The key parameter configures the private and public key pair used for creating the certificate. By default, no value exists. Create or copy a key file and store it in the sslkey directory. For instance, use the following command to copy the key file, key.pem from the /tmp directory on the switch to the sslkey directory:
switch# copy file:/tmp/ssl/key.pem sslkey:To generate a 2048-bit RSA key with the name, key.pem, and save it to the sslkey directory, use the following command:
switch# security pki generate rsa 2048 key.pemAdd the key to the certificate profile using the following commands:
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# key key.pem
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#The certificate profile configuration requires adding a key. If left empty or contains an invalid key, the configuration marks the profile as mis-configured and does not send certificate signing requests.
Changing the key for the certificate while associated with a certificate profile triggers a rekey operation which sends a re-enrollment request to the EST server and uses the new key for creating a new certificate. The old key and certificate pair authenticates the client as well as using the re-enrollment credentials to authenticate.
distinguished name and the subject
alternative name for the certificate. The distinguished name parameter configures the following:
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters distinguished-name common-name "Switch 1"
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters distinguished-name organization Arista
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#To clear the values from the configuration, use the no | default versions of the command.
Use the following commands to add the IPv4 address, 192.168.1.1, the IPv6 address, 3FF.FFFF::1, the email address, This email address is being protected from spambots. You need JavaScript enabled to view it., and the URI, http://example.com/path/etc to the certificate profile, CertAlpha:
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name ip 192.0.2.1 192.0.2.2 3FFF:FFFF::1"
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name email This email address is being protected from spambots. You need JavaScript enabled to view it.
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name uri https://example.com/path/one
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#To clear the values from the configuration, use the no | default versions of the command.
Configure at least one option for parameters, either the distinguished name or the subject alternative name. If left empty, the configuration marks the profile as misconfigured and does not send certificate signing requests.
Changing the key for the certificate while associated with a certificate profile triggers a rekey operation which sends a re-enrollment request to the EST server and uses the new key for creating a new certificate. The old key and certificate pair authenticates the client as well as using the re-enrollment credentials to authenticate.
system.
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters distinguished-name serial-number systemThe protocol parameter assigns a certificate profile to an EST profile. Use the following commands to add the CertAlpha certificate protocol to the EST_1 protocol profile:
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# protocol instance EST_1
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#You must configure this parameter to assign a valid EST protocol profile to a certificate profile. Multiple certificate profiles can be assigned to a single EST protocol profile.
The renewal parameter sets the time to renew the certificate. Configure this parameter as the number of seconds before a certificate expires. By default, the certificate expires after two hours. Use the following commands to configure the renewal time as 3600 seconds, one hour before the certificate expires:
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# renewal 3600 seconds
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#Using the no version of the command resets the renewal time to 7200 seconds (2 hours).
switch# show management security auto-certificate profile CertAlpha
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Valid
Next request in 89 days, 21:59:47 at: 2025-02-05 01:45:51
switch# show management security auto-certificate profile CertAlpha detail
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Valid
Next request in 89 days, 21:59:37 at: 2025-02-05 01:45:51
Initial enrollment statistics:
Number of successes: 1
Number of failures: 0
Renewal statistics:
Number of successes: 0switch# show management security auto-certificate profile CertAlpha
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Invalid configuration
Last error:
Message: Protocol instance not set
Time: 2024-11-07 04:59:19
Next request at: Never
switch# show management security auto-certificate profile CertAlpha detail
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Invalid configuration
Last error:
Message: Protocol instance not set
Time:2024-11-07 04:59:19
Next request at: Never
Initial enrollment statistics:
Number of successes: 0
Number of failures: 0
Renewal statistics:
Number of successes: 0
Number of failures: 0The profile does not have a valid protocol instance in the configuration and the configuration fails.
switch# show management security auto-certificate profile certProfileCharlie
Auto certificate profile certProfileCharlie:
Key: clientkey.pem
State: Enrolling
Last error:
Message: HTTP connection refused
Time:2024-11-07 05:37:49
Next request in 0:00:07 at: 2024-11-07 05:37:57
switch# show management security auto-certificate profile certProfileCharlie detail
Auto certificate profile certProfileCharlie:
Key: clientkey.pem
State: Enrolling
Last error:
Message: HTTP connection refused
Time:2024-12-10 05:17:52
Next request in 0:00:04 at: 2024-11-07 05:37:57
Initial enrollment statistics:
Number of successes: 0
Number of failures: 4
Renewal statistics:
Number of successes: 0
Number of failures: 0
The certificate request has encountered errors when attempting to reach the EST server.
switch# show management security auto-certificate profile detail
Auto certificate profile certProfileCharlie:
Key: clientkey.pem
State: Enrolling
Last error:
Message: HTTP connection refused
Time: 2024-11-07 05:46:19
Next request in 0:04:41 at: 2024-11-07 05:54:51
Initial enrollment statistics:
Number of successes: 0
Number of failures: 4
Renewal statistics:
Number of successes: 0
Number of failures: 0
Auto certificate profile certProfileAlpha:
Key: clientkey.pem
State: Valid
Next request in 89 days, 19:55:41 at: 2025-02-05 01:45:51
Initial enrollment statistics:
Number of successes: 1
Number of failures: 0
Renewal statistics:
Number of successes: 0
Number of failures: 0
Auto certificate profile certProfileDelta:
Key:
State: Invalid configuration
Last error:
Message: No parameters set
Time: 2024-11-07 05:43:07
Next request at: Never
Initial enrollment statistics:
Number of successes: 0
Number of failures: 0
Renewal statistics:
Number of successes: 0
Number of failures: 0
Auto certificate profile certProfileBravo:
Key: clientkey.pem
State: Enrolling
Last error:
Message: HTTP connection refused
Time: 2024-11-07 05:45:05
Next request in 0:11:59 at: 2024-11-07 06:02:09
Initial enrollment statistics:
Number of successes: 0
Number of failures: 6
Renewal statistics:
Number of successes: 0
Number of failures: 0switch# show management security auto-certificate protocol est EST_1
Automatic Certificate Management policy EST_1:
State: Valid
switch# show management security auto-certificate protocol est EST_1 detail
Automatic Certificate Management policy EST_1:
State: Valid
Managed certificate profile:
certProfileAlpha:
Certificate state: Valid
certProfileDelta:
Certificate state: Invalid configurationswitch# show management security auto-certificate protocol est EST_2
Automatic Certificate Management policy EST_2:
State: Invalid
Last error:
Message: Invalid SSL profile
Time: 2024-11-07 06:28:20
switch# show management security auto-certificate protocol est EST_2 detail
Automatic Certificate Management policy EST_2:
State: Invalid
Last error:
Message: Invalid SSL profile
Time: 2024-11-07 06:28:20
Managed certificate profile:
certProfileBravo:
Certificate state: Needs enrollingAfter configuring the access databases, aaa authentication, aaa authorization, and aaa accounting commands designate active and backup services for handling access requests.
These sections describe the methods of selecting the switch's database to authenticate users and authorize access to network resources.
Service lists specify the services the switch uses to authenticate usernames and the enable password.
Service list elements are service options, ordered by their priority.
Example
The switch initially attempts to authenticate a username using the Location_1 server group. If a server within that group is available, authentication proceeds through it. If not, the switch continues checking subsequent server groups until it finds an available one, or it resorts to option 5 (None), permitting access without authentication.
switch(config)# aaa authentication login default group TAC-1 localswitch(config)# aaa authentication login default group tacacs+ group radius noneswitch(config)# aaa authentication enable default group TACACS+ localAAA time-based lockout enables managing remote user unsuccessful login attempts for a specified period.
switch(config)# aaa authentication policy lockout failure 4 duration 360switch# show aaa authentication lockoutswitch# clear aaa authentication lockoutAuthorization commands control EOS shell access, CLI command access, and configuration access through the console port. The switch also supports role-based authorization, which allows access to specified CLI commands by assigning command profiles (or roles) to usernames. See Role-Based Authorization for details.
During the exec authorization process, TACACS+ server responses may include attribute-value (AV) pairs. The switch recognizes the mandatory AV pair named priv-lvl=x (where x is between 0 and 15).
A TACACS+ server that sends any other mandatory AV pair is denied access to the switch by default. The switch's receipt of optional AV pairs does not affect decisions to permit or deny access to the TACACS+ server. The tacacs-server policy command programs the switch to allow access to TACACS+ servers that send unrecognized mandatory AV pairs.
switch(config)# aaa authorization exec default group tacacs+switch(config)# aaa authorization commands all default localswitch(config)# aaa authorization commands all default none switch(config)# tacacs-server policy unknown-mandatory-attribute ignoreBy default, EOS does not verify the authorization of commands entered on the console port.
switch(config)# no aaa authorization config-commandsThis command enables the authorization of configuration commands.
switch(config)# aaa authorization config-commandsThis command configures the switch to authorize commands entered on the console using the method specified through a previously executed aaa authorization command.
switch(config)# aaa authorization serial-consoleThe accounting service collects information for billing, auditing, and reporting. The switch supports TACACS+ and RADIUS accounting by reporting user activity to either the TACACS+ server or the RADIUS server as accounting records.
The aaa accounting command enables accounting.
switch(config)# aaa accounting commands all default start-stop group tacacs+switch(config)# aaa accounting exec console stop group tacacs+These sections describe two sample TACACS+ host configurations.
The switch authenticates the username and enable command against all TACACS+ servers which, in this case, is one host. If the TACACS+ server is unavailable, the switch authenticates with the local file.
Traditional TACACS+ (Terminal Access Controller Access-Control System Plus) relies on raw TCP (Port 49) for transport. While it encrypts the body of the packets, the packet headers, including sensitive fields such as usernames, authorization states, and accounting command logs, remain visible in plaintext. Additionally, the cryptographic model depends on a legacy pre-shared MD5 key, leaving it vulnerable to session hijacking, packet manipulation, and offline brute-force attacks in modern untrusted networks.
10.21.22.23, and the profile name, tacacs_server1:
switch(config) tacacs-server host 10.21.22 tls ssl-profile tacacs_server1
switch(config)#switch(config) no tacacs-server host tls
switch(config)#Creating the Client SSL Profile
TACACS-TLS-CLIENT, and add the certificates:
switch(config)# management security
switch(config-mgmt-security)# ssl TACACS-TLS-CLIENT
switch(config-mgmt-sec-ssl-profile-TACACS-TLS-CLIENT)# certificate switch-identity.crt key switch-identity.key
switch(config-mgmt-sec-ssl-profile-TACACS-TLS-CLIENT)# trust certficate enterprise-root-ca.crt
switch(config-mgmt-sec-ssl-profile-TACACS-TLS-CLIENT)# tls versions 1.3
switch(config-mgmt-sec-ssl-profile-TACACS-TLS-CLIENT)#Provisioning the Secure TACACS+ Host Entry
TACACS-TLS-CLIENT profile:
switch(config)# tacacs-server host 192.168.10.20 tls ssl-profile TACACS-TLS-CLIENT
switch(config)#Mapping the Secure Host to the AAA Engine
switch(config)# aaa group server tacacs+ SECURE-AAA-GROUP
switch(config-aaa-vessel-SECURE-AAA-GROUP)# server 192.168.10.50
switch(config-aaa-vessel-SECURE-AAA-GROUP)# exit
!
switch(config)# aaa authentication login default group SECURE-AAA-GROUP local
switch(config)# aaa authorization exec default group SECURE-AAA-GROUP local
switch(config)# aaa accounting commands 15 default start-stop group SECURE-AAA-GROUP
switch(config)#switch# show management security ssl profile TACACS-TLS-CLIENT
Profile: TACACS-TLS-CLIENT
Type: Client
State: Operational
TLS Versions: 1.3
Certificate: switch-identity.crt
Trust Anchor: enterprise-root-ca.crt
Active Connections: 1OpenConfig allows network engineers to collaboratively develop programming interfaces and tools to manage networks dynamically and in a vendor-neutral manner.
EOS supports AAA Accounting for gRPC Network Management Interface (gNMI), gRPC Network Operations (gNOI) Interface, and gRPC Network Security Interface (gNSI) RPCs by logging the accounting records to a TACACS+ server, RADIUS server, or to a syslog server.
The aaa accounting dot1x command enables the accounting of requested 802.1X services for network access.
The no aaa accounting dot1x and default aaa accounting dot1x commands disable the specified method list by removing the corresponding aaa accounting dot1x command from running-config.
Command Mode
Global Configuration
Command Syntax
aaa accounting dot1x default [METHOD_1][METHOD_2][METHOD_N]
no aaa accounting dot1x default
default aaa accounting dot1x default
No parameter specified if MODE is set to none. If MODE not set to none, the command must provide at least one method. Each method consists of one of the following:
logging server group that includes all defined TACACS+ hosts.
switch(config)# aaa accounting dot1x default start-stop group radius
switch(config)#switch(config)# no aaa accounting dot1x default
switch(config)#The aaa accounting system command performs accounting for all system-level events.
The no aaa accounting system and default aaa accounting system commands clear the specified method list by removing the corresponding aaa accounting system command from running-config.
Command Mode
Global Configuration
Command Syntax
aaa accounting system default [METHOD_1][METHOD_2] ... [METHOD_N]
no aaa accounting system default
default aaa accounting system default
switch(config)# aaa accounting system default none
switch(config)#switch(config)# aaa accounting system default stop-only group radius
switch(config)#The aaa accounting command configures accounting method lists for a specified authorization type. Each list consists of a prioritized list of methods. The accounting module uses the first available listed method for the authorization type.
The no aaa accounting and default aaa accounting commands clear the specified method list by removing the corresponding aaa accounting command from running-config.
Command Mode
Global Configuration
Command Syntax
aaa accounting TYPE CONNECTION MODE [METHOD_1][METHOD_2] ... [METHOD_N]
no aaa accounting TYPE CONNECTION
default aaa accounting TYPE CONNECTION
switch(config)# aaa accounting commands all default start-stop group tacacs+
switch(config)#switch(config)# aaa accounting exec console stop group tacacs+
switch(config)#switch(config)# aaa accounting commands all default start-stop group tacacs+
switch(config)#switch(config)# aaa accounting exec console stop group tacacs+
switch(config)#The aaa authentication dot1x command configures the default authentication list of requested 802.1X services for network access.
The no aaa authentication dot1x and default aaa authentication dot1x commands remove the default authentication list for IEEE 802.1X.
Command Mode
Global Configuration
Command Syntax
aaa authentication dot1x default group {group_name | radius}
no aaa authentication dot1x default
default aaa authentication dot1x
Example
switch(config)# aaa authentication dot1x default group auth1
switch(config)#The aaa authentication enable command configures the service list that the switch references to authorize access to Privileged EXEC command mode.
The switch authorizes access by using the first listed service option available. When the local file is a service list element, attempts to locally authenticate a usernamenot in the local file results in the switch continuing to the next service list element.
The no aaa authentication enable and default aaa authentication enable commands revert the list configuration to the default by removing the corresponding aaa authentication enable command from running-config.
Command Mode
Global Configuration
Command Syntax
aaa authentication enable [console | default] METHOD_1 [METHOD_2] ... [METHOD_N]
no aaa authentication enable [console | default]
default aaa authentication enable [console | default]
Parameters
console - Uses the console authentication list.
default - Uses the default authentication list.
Example
switch(config)# aaa authentication default enable group TACACS+ local
switch(config)#When the local file contains a service list element, attempts to locally authenticate a username not in the local file results in the switch continuing to the next service list element.
The no aaa authentication login and default aaa authentication login commands revert the specified list configuration to its default by removing the corresponding aaa authentication login command from running-config.
Command Mode
Global Configuration
Command Syntax
aaa authentication login CONNECTION SERVICE_1 [SERVICE_2] ... [SERVICE_N]
no aaa authentication login CONNECTION
default aaa authentication login CONNECTION
switch(config)# aaa authentication login default group TAC-1 local
switch(config)#switch(config)# aaa authentication login default group tacacs+ group radius none
switch(config)#The aaa authentication policy local allow-nopassword-remote-login command permits usernames without passwords to log in from any port. The default switch setting only allows unprotected usernames to log in from the console.
The no aaa authentication policy local allow-nopassword-remote-login and default aaa authentication policy local allow-nopassword-remote-login commands return the switch to the default setting of allowing unprotected usernames to log in only from the console.
Command Mode
Global Configuration
Command Syntax
aaa authentication policy local allow-nopassword-remote-login
no aaa authentication policy local allow-nopassword-remote-login
default aaa authentication policy local allow-nopassword-remote-login
switch(config)# aaa authentication policy local allow-nopassword-remote-login
switch(config)#switch(config)# no aaa authentication policy local allow-nopassword-remote-login
switch(config)#The aaa authentication policy lockout failure command configures the switch to block the remote user from access after a specified number of unsuccessful login attempts within a lockout period.
The no aaa authentication policy lockout failure and the default aaa authentication policy lockout failure commands disable the lockout period configuration.
Command Mode
Global Configuration
Command Syntax
aaa authentication policy lockout failure failure_count duration duration_time {window window_time}
no aaa authentication policy lockout failure
default aaa authentication policy lockout failure
switch(config)# aaa authentication policy lockout failure 4 duration 360switch(config)# aaa authentication policy lockout failure 5 window 10 duration 60The aaa authentication policy log command configures the switch to generate syslog messages for login authentication success or failure events.
The no aaa authentication policy log and the default aaa authentication policy log commands restore the default behavior of not generating syslog messages for these events.
Command Mode
Global Configuration
Command Syntax
aaa authentication policy {on-failure | on-success} log
no aaa authentication policy {on-failure | on-success} log
default aaa authentication policy {on-failure | on-success} log
Example
switch(config)# aaa authentication policy on-success log
switch(config)# aaa authentication policy on-failure logCommand usage is authorized for each privilege level specified in the command.
The list is set to none for all unconfigured privilege levels, allowing all CLI access attempts to succeed.
The no aaa authorization commands and default aaa authorization commands commands revert the list contents to none for the specified privilege levels.
Command Mode
Global Configuration
Command Syntax
aaa authorization commands PRIV default SERVICE_1[SERVICE_2] ... [SERVICE_N]
no aaa authorization commands PRIV default
default aaa authorization commands PRIV default
switch(config)# aaa authorization commands all default local
switch(config)#switch(config)# aaa authorization commands all default none
switch(config)#The aaa authorization config-commands command enables authorization of commands in any configuration mode, such as Global Configuration and all interface configuration modes. The policy specified by the aaa authorization commands setting authorizes the commands. EOS enables authorization by default, so issuing this command has no effect unless running-config contains the no aaa authorization config-commands command.
The no aaa authorization config-commands command disables configuration command authorization. When disabled, running-config contains the no aaa authorization config-commands command. The default aaa authorization config-commands command restores the default setting by removing the no aaa authorization config-commands from running-config.
Command Mode
Global Configuration
Command Syntax
aaa authorization config-commands
no aaa authorization config-commands
default aaa authorization config-commands
switch(config)# aaa authorization config-commands
switch(config)#switch(config)# no aaa authorization config-commands
switch(config)#The aaa authorization exec command configures the service list that the switch references to authorize access to open an EOS CLI shell.
The list consists of a prioritized list of service options. The switch authorizes access by using the first listed service option to which the switch can connect. When the switch cannot communicate with an entity that provides a specified service option, it attempts to use the next option in the list.
The no aaa authorization exec and default aaa authorization exec commands set the list contents to none.
Command Mode
Global Configuration
Command Syntax
aaa authorization exec default METHOD_1 [METHOD_2] ... [METHOD_N]
no aaa authorization exec default
default aaa authorization exec default
The command must provide at least one method. Each method is composed of one of the following:
Guidelines
During the EXEC authorization process, the TACACS+ server response may include attribute-value (AV) pairs. The switch recognizes priv-lvl=x (where x is an integer between 0 and 15), which is a mandatory AV pair. A TACACS+ server that sends any other mandatory AV pair cannot access the switch. The receipt of optional AV pairs by the switch has no effect on decisions to permit or deny access to the TACACS+ server.
Example
switch(config)# aaa authorization exec default group tacacs+
switch(config)#The aaa authorization policy local command specifies the name of the default role. A role provides a data structure that supports local command authorization through assignment to user accounts. Roles consist of permit and deny rules that define authorization levels for specified commands. Applying a role to a username authorizes the user to execute commands specified by the role.
If you do not specify the default-role for a user, EOS assigns network-operator to qualified users as the default role. The network-operator role authorizes assigned users access to all CLI commands in EXEC and Privileged EXEC modes.
The no aaa authentication policy local default-role and default aaa authentication policy local default-role commands remove the authentication policy local default-role statement from running-config. Removing this statement restores network-operator as the default role.
Command Mode
Global Configuration
Command Syntax
aaa authorization policy local default-role role_name
no aaa authorization policy local default-role
default aaa authorization policy local default-role
Parameter
role_name - Specify the name of the default role.
Related Command
The role command places the switch in role configuration mode for creating and editing roles.
switch(config)# aaa authorization policy local default-role sysuser
switch(config)#switch(config)# no aaa authorization policy local default-role
switch(config)#switch# show users roles network-operator
The default role is network-operator
role: network-operator
10 deny mode exec command bash|\|
20 permit mode exec command .*
switch#The aaa authorization serial-console command configures the switch to authorize commands entered through the console. By default, commands entered through the console do not require authorization.
The no aaa authorization serial-console and default aaa authorization serial-console commands restore the default setting.
Command Mode
Global Configuration
Command Syntax
aaa authorization serial-console
no aaa authorization serial-console
default aaa authorization serial-console
Example
switch(config)# aaa authorization serial-console
switch(config)#The aaa group server radius command enters the Server-group-RADIUS Configuration Mode for the specified group name. The command creates the specified group if not previously created.
A server group consists ofa collection of servers associated with a single label. Subsequent authorization and authentication commands access all servers in a group by invoking the group name. Server group members must be previously configured with a radius-server host command.
The no aaa group server radius and default aaa group server radius commands delete the specified server group from running-config.
Command Mode
Global Configuration
Command Syntax
aaa group server radius group_name
no aaa group server radius group_name
default aaa group server radius group_name
Parameters
group_name - Specify a name, as a text string, to assign to the group. Cannot be identical to a name already assigned to a TACACS+ server group.
Commands Available in Server-group-RADIUS Configuration Mode
server (server-group-RADIUS configuration mode).
Related Command
Example
switch(config)# aaa group server radius RAD-SV1
switch(config-sg-radius-RAD-SV1)#The aaa group server tacacs+ command enters Server-group-TACACS+ Configuration Mode for the specified group name. The command creates the specified group if not previously created.
A server group consists of a collection of servers associated with a single label. Subsequent authorization and authentication commands access all servers in a group by invoking the group name. Server group members must be previously configured with a tacacs-server host command.
The no aaa group server tacacs+ and default aaa group server tacacs+ commands delete the specified server group from running-config.
Command Mode
Global Configuration
Command Syntax
aaa group server tacacs+ group_name
no aaa group server tacacs+ group_name
default aaa group server tacacs+ group_name
Parameters
group_name - Specify a name, as a text string, to assign to the group. Cannot be identical to a name already assigned to a RADIUS server group.
Commands Available in Server-group-TACACS+ Configuration Mode
server (server-group-TACACS+ configuration mode)Related Command
aaa group server radiusExample
switch(config)# aaa group server tacacs+ TAC-GR
switch(config-sg-tacacs+-TAC-GR)#The aaa root command specifies the password security level for the root account and can assign a password to the account.
The no aaa root and default aaa root commands disable the root account by removing the aaa root command from running-config. The root account is disabled by default.
Command Mode
Global Configuration
Command Syntax
aaa root SECURITY_LEVEL [ENCRYPT_TYPE] [password]
no aaa root
default aaa root
Encrypted strings entered through this parameter are generated elsewhere.
switch(config)# aaa root secret f4980
switch(config)# aaa root secret 0 f4980switch(config)# aaa root secret 5 $1$HW05LEY8$QEVw6JqjD9VqDfh.O8r.b
switch(config)#switch(config)# aaa root nopassword
switch(config)#switch(config)# no aaa root
switch(config)#The auto-certificate protocol connection command configures parameters for Enrollment over Secure Transport (EST) profiles used for Automatic Certificate Management.
Command Mode
Management Security Configuration
EST Protocol Profile Configuration
Command Syntax
auto-certificate protocol est profile_name connection retry [count retries | interval seconds
Parameters
Example
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# connection retry count 100
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# connection retry interval 2 secondsThe auto-certificate protocol credentials command configures the enrollment and re-enrollment usernames and pairs or JSON Web Tokens (JWTs). The EST profile only uses the credentials for HTTP authentication requests to the server.
The no | default versions of the command disables the credentials configuration on the switch.
Command Mode
Management Security Configuration
EST Protocol Profile Configuration
Command Syntax
auto-certificate protocol est profile_name credentials [enroll | re-enroll] [secret | token | username][0 | 7 | 8a] line]
Example
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# credentials enroll secret 0 password1234
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)#The auto-certificate protocol disabled command temporarily pauses retrieving certificates from the server by disabling the profile and prevents sending unnecessary requests to the server. This may be helpful when troubleshooting server connections and does not require reconfiguration of the EST protocol profile. The no version of the command re-enables the profile.
Command Mode
Management Security
EST Protocol Profile Configuration
Command Syntax
auto-certificate protocol est profile_name disabled
Parameters
disabled - Temporarily disable sending EST requests to the server.
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# disabledswitch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# no disabledThe auto-certificate protocol server command configures EST server behavior and options such as SSL profiles, server URLs, and VRFs.
The no | default versions of the command removes the configuration from the EST Protocol Profile.
Command Mode
Management Security
EST Protocol Profile Configuration
Command Syntax
auto-certificate protocol est profile_name server [ssl ssl_profile][url server_url][vrf vrf]
Example
switch(config)# management security
switch(config-mgmt-security)# auto-certificate protocol est EST_1
switch(config-mgmt-sec-auto-cert-proto-est-EST_1)# server url https://myestserver.mycompany.comThe auto-certificate profile command allows configuration of Automatic Certificate Management and profiles for X.509 certificates. X.509 automatic certificate management provides support for retrieving signed X.509v3 certificates from a server using the Enrollment over Secure Transport (EST) protocol. EOS only supports EST as the client protocol.
The no | default versions of the command remove the configuration from the running-config.
Command Mode
Management Security Configuration
Certificate Profile Configuration
Command Syntax
auto-certificate profile profile_name [digest [sha256 | sha384 | sha512]] [key key_name] [protocol instance protocol_instance_name] [renewal expire_seconds seconds]
Example
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertACM
switch(config-mgmt-sec-auto-cert-prof-CertACM) digest sha512The auto-certificate profile parameters command configures the certificate attributes including distinguished name and subject alternative name. By default, all fields do not have values until configured. Use quotation marks (" ") for attributes with multiple words, such as "Switch 1". Repeating the commands with different values replaces the existing values. For the configuration to be valid, you must configure at least one parameter.
The no | default versions of the command clears the field values from the running-config.
Command Mode
Management Security Configuration
Certificate Profile Configuration
Command Syntax
auto-certificate profile profile_name parameters [distinguished-name [common-name common_name] [country country_code] [email email_address ] [locality locality_name ] [organization name ] [organization-unit unit_name ] [state state_name]]
auto-certificate profile profile_name parameters [subject-alternative-name [dns dns_name] [email email_address] [ ip ip_address] [uri uri]]
Example
switch(config)# management security
switch(config-mgmt-security)# auto-certificate profile CertAlpha
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name ip 192.0.2.1 192.0.2.2 3FFF:FFFF::1"
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name email This email address is being protected from spambots. You need JavaScript enabled to view it.
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)# parameters subject-alternative-name uri https://example.com/path/one
switch(config-mgmt-sec-auto-cert-prof-CertAlpha)#
The clear aaa authentication lockout command clears the locked status of a user and allows access within a lockout period. If no user specified, the command clears the locked status of all users.
Command Mode
Privileged EXEC
Command Syntax
clear aaa authentication lockout [user user_name]
Parameter
user user_name - Specify the name of the user.
switch# clear aaa authentication lockout user AliceThe clear aaa counters radius command resets the counters tracking the statistics for the RADIUS servers that the switch accesses. The show radius command displays the counters reset by the clear aaa counters radius command.
Command Mode
Privileged EXEC
Command Syntax
clear aaa counters radius
Example
switch# show radius
RADIUS server : radius/10
Connection opens: 204
Connection closes: 0
Connection disconnects: 199
Connection failures: 10
Connection timeouts: 2
Messages sent: 1490
Messages received: 1490
Receive errors: 0
Receive timeouts: 0
Send timeouts: 0
Last time counters were cleared: never
switch# clear aaa counters radius
switch# show radius
RADIUS server : radius/10
Connection opens: 0
Connection closes: 0
Connection disconnects: 0
Connection failures: 0
Connection timeouts: 0
Messages sent: 0
Messages received: 0
Receive errors: 0
Receive timeouts: 0
Send timeouts: 0
Last time counters were cleared: 0:00:03 agoThe clear aaa counters tacacs+ command resets the counters tracking the statistics for the TACACS+ servers that the switch accesses. The show tacacs command displays the counters reset by the clear aaa counters tacacs+ command.
Command Mode
Privileged EXEC
Command Syntax
clear aaa counters tacacs+
Example
switch# show tacacs
TACACS+ server : tacacs/49
Connection opens: 15942
Connection closes: 7
Connection disconnects: 1362
Connection failures: 0
Connection timeouts: 0
Messages sent: 34395
Messages received: 34392
Receive errors: 0
Receive timeouts: 2
Send timeouts: 0
Last time counters were cleared: never
TACACS+ source-interface: Enabled
TACACS+ outgoing packets will be sourced with an IP address associated with the
Loopback0 interface
switch# clear aaa counters tacacs+
switch# show tacacs
TACACS+ server : tacacs/49
Connection opens: 0
Connection closes: 0
Connection disconnects: 0
Connection failures: 0
Connection timeouts: 0
Messages sent: 0
Messages received: 0
Receive errors: 0
Receive timeouts: 0
Send timeouts: 0
Last time counters were cleared: 0:00:03 ago
switch#
TACACS+ source-interface: Enabled
TACACS+ outgoing packets will be sourced with an IP address associated with the
Loopback0 interfaceThe clear aaa counters command resets the counters tracking the number of service transactions performed by the switch since the last reset of the counters. The show aaa counters command displays the counters reset by the clear aaa counters command.
Command Mode
Privileged EXEC
Command Syntax
clear aaa counters [SERVICE_TYPE]
Example
switch# clear aaa counters
switch# show aaa counters
Authentication
Successful: 0
Failed: 0
Service unavailable: 0
Authorization
Allowed: 1
Denied: 0
Service unavailable: 0
Accounting
Successful: 0
Error: 0
Pending: 0
Last time counters were cleared: 0:00:44 agoThe clear radius proxy client group command clears RADIUS proxy client packet counters.
Command Mode
Privileged EXEC
Command Syntax
clear radius proxy client group group_name
Parameters
group_name - Clear all RADIUS proxy client group packet counters or specify a group name to clear counters for a specific group.
Example
switch# clear radius proxy client groupThe deny command adds a deny rule to the configuration mode role. Deny rules prohibit access of specified commands from usernames with the applied role. Sequence numbers determine rule placement in the role. Commands are compared sequentially to rules within a role until it matches a rule. A commands authorization is determined by the first rule it matches. Sequence numbers for commands without numbers are derived by adding 10 to the number of the roles last rule.
Deny rules use regular expressions to denote commands. A mode parameter specifies command modes with restricted commands. Modes use either by predefined keywords, a command modes short key, or a regular expression that specifies the long key of one or more command modes.
The no deny and default deny commands remove the specified rule from the configuration mode role. The no sequence number (Role) command also removes the specified rule from the role.
Command Mode
Role Configuration
Command Syntax
[SEQ_NUM] deny [MODE_NAME] command command_name
no deny [MODE_NAME] command command_name
default deny [MODE_NAME] command command_name
Guidelines
Deny statements save to the running-config only when exiting the Role configuration mode.
Related Command
The role command places the switch in Role configuration mode.
Example
switch(config)# role sysuser
switch(config-mode-sysuser)# deny mode exec command reload
switch(config-mode-sysuser)#The enable password command creates a new enable password or changes an existing password.
The no enable password and default enable password commands delete the enable password by removing the enable password command from running-config.
Command Mode
Global Configuration
Command Syntax
enable password [ENCRYPT_TYPE] password
no enable password
default enable password
Encrypted strings entered through this parameter are generated elsewhere.
switch(config)# enable password xyrt1
switch(config)# enable password 0 xyrt1switch(config)# enable password 5 $1$8bPBrJnd$Z8wbKLHpJEd7d4tc5Z/6h/
switch(config)#switch(config)# no enable password
switch(config)#The ip radius source-interface command specifies the interface from which the IPv4 or IPv6 address is derived for use as the source for outbound RADIUS packets. If the interface has an IP address but the address becomes unavailable, AAA falls back to the next configured authentication method.
The no ip radius source-interface and default ip radius source-interface commands remove the ip radius source-interface command from running-config.
Command Mode
Global Configuration
Command Syntax
ip radius [vrf_inst] source-interface slot_number
no ip radius [vrf_inst] source-interface
default ip radius [vrf_inst] source-interface
Example
switch(config)# ip radius source-interface loopback 0
switch(config)#The ip tacacs source-interface command specifies the interface from which the IPv4 or IPv6 address is derived for use as the source for outbound TACACS+ packets. If the interface has an IP address but the address becomes unavailable, AAA falls back to the next configured authentication method.
The no ip tacacs source-interface and default ip tacacs source-interface commands remove the ip tacacs source-interface command from running-config.
Command Mode
Global Configuration
Command Syntax
ip tacacs [VRF_INST] source-interface INT_NAME
no ip tacacs [VRF_INST] source-interface
default ip tacacs [VRF_INST] source-interface
Example
switch(config)# ip tacacs source-interface loopback 0
switch(config)#The no sequence number command removes the rule with the specified sequence number from the configuration-mode role. The default sequence number command also removes the specified rule.
Command Mode
Role Configuration
Command Syntax
no sequence_num
default sequence_num
Parameters
sequence_num sequence number of rule to be deleted. Values range from 1 to 256.
Guidelines
Role statement changes are saved to running-config only upon exiting Role configuration mode.
Related Command
The role command places the switch in Role configuration mode.
Example
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
20 deny mode config command (no |default )?router
30 deny mode config command (no |default )?(ip|mac) access-list
40 deny mode if command (no |default )?(ip|mac) access-group
50 deny mode config-all command lacp|spanning-tree
60 permit command .*
switch(config)# role sysuser
switch(config-role-sysuser)# no 30
switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
20 deny mode config command (no |default )?router
40 deny mode if command (no |default )?(ip|mac) access-group
50 deny mode config-all command lacp|spanning-tree
60 permit command .*
switch(config)#The monitor server radius command enters the Monitor Server RADIUS Configuration Mode and allows the configuration of RADIUS server monitoring on the switch.
The no version of the command removes the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
monitor server radius
no monitor server radius
Parameters
monitor server radius - Enter the RADIUS Server Monitor Configuration mode.
Example
switch(config)# monitor server radius
switch(config-monitor-server-radius)#The probe interval command in the Monitor Server RADIUS Configuration Mode configures EOS to send probes to the RADIUS server at specific time intervals to ensure the availability of the server.
The no probe interval command disables the configuration and removes it from the running-config.
Command Mode
Monitor Server RADIUS Configuration
Command Syntax
probe interval period seconds
no probe interval
Parameters
interval period seconds. - Specify the probe interval for RADIUS servers with a value between 1 and 1000 seconds with a default value of 300 seconds.
Example
switch(config)# monitor server radius
switch(config-monitor-server-radius)# probe interval 600 seconds
switch(config-monitor-server-radius)#The probe method command in the Monitor Server RADIUS Configuration Mode determines the type of probe sent to the RADIUS server. Some RADIUS servers do not respond to RADIUS Status-Server packets, but respond to the RADIUS Access-Request packets. This applies to RADIUS servers configured for IEEE 802.1X authentication.
The no version of the command disables the configuration and removes it from the running-config.
Command Mode
Monitor Server RADIUS Configuration
Command Syntax
probe method [[access-request username username password password ]|[status-server]]
no probe method
Example
switch(config)# monitor server radius
switch(config-monitor-server-radius)# probe method access-request username ServerAdmin password Sup3rS3cr3t
switch(config-monitor-server-radius)#The probe threshold command in the Monitor Server RADIUS Configuration Mode configures sets the number of consecutive failed probes before determining a RADIUS server has become nonresponsive. By default, the threshold as a value of 1.
The no version of the command disables the configuration and removes it from the running-config.
Command Mode
Monitor Server RADIUS Configuration
Command Syntax
probe threshold failure number
no probe threshold failure
Example
switch(config)# monitor server radius
switch(config-monitor-server-radius)# probe threshold failure 60
switch(config-monitor-server-radius)#The radius proxy command enters the RADIUS Proxy Configuration Mode on a switch.
Command Mode
RADIUS Proxy Configuration Mode
Command Syntax
radius proxy
Parameters
None
Example
switch(config)# radius proxy
switch(config-radius-proxy)#The radius proxy client group client command configures RADIUS Proxy client groups on the switch.
Command Mode
RADIUS Proxy Configuration Mode
Command Syntax
radius proxy client group group_name client [host host_name]|[ipv4 ipv4_addr]|[ipv6 ipv6_addr]
Example
switch(config)# radius proxy
switch(config-radius-proxy)# client group MyGroup
switch(config-rp-cg-MyGroup)# client ipv4 192.168.1.25The radius proxy client group server command configures RADIUS Proxy server groups on the switch.
Command Mode
RADIUS Proxy configuration mode
Command Syntax
radius proxy client group group_name server group_name
Example
switch(config)# radius proxy
switch(config-radius-proxy)# client group MyGroup
switch(config-rp-cg-MyGroup)# server group RADIUS_SG1The radius proxy client key command enters the RADIUS Proxy Configuration Mode on a switch and allows the configuration of a global client key.
Command Mode
RADIUS Proxy configuration mode
Command Syntax
radius proxy client key [0 | 7 | 8a] line
Example
switch(config)# radius proxy
switch(config-radius-proxy)# client key 0 SuperSecretKeyThe radius proxy client session command enters the RADIUS proxy configuration mode on a switch and allows the configuration of a client session idle-timeout parameter.
Command Mode
RADIUS proxy configuration mode
Command Syntax
radius proxy client session idle-timeout seconds
Parameters
idle-timeout seconds - Configure the minimum time to wait before clearing the client session.
Example
switch(config)# radius proxy
switch(config-radius-proxy)# client session idle-timeout 300 secondsThe radius proxy client key command enters the RADIUS proxy configuration mode on a switch and enables dynamic authorization for RADIUS proxy server groups.
Command Mode
RADIUS proxy configuration mode
Command Syntax
radius proxy dynamic-authorization
Example
switch(config)# radius proxy
switch(config-radius-proxy)# dynamic-authorizationThe radius-server deadtime command defines global deadtime period, when the switch ignores a non-responsive RADIUS server. A non-responsive server is one that fails to answer any attempt to retransmit after a timeout expiry. Deadtime is disabled if a value is not configured.
The no radius-server deadtime and default radius-server deadtime commands restore the default global deadtime period of three minutes by removing the radius-server deadtime command from running-config.
Command Mode
Global Configuration
Command Syntax
radius-server deadtime dead_interval
no radius-server deadtime
default radius-server deadtime
Parameter
dead_interval period that the switch ignores non-responsive servers (minutes). Values range from 1 to 1000. Default is 3.
Example
switch(config)# radius-server deadtime 120
switch(config)#The radius-server host command sets parameters for communicating with a specific RADIUS server. These values override global settings when the switch communicates with the specified server.
A RADIUS server is defined by its server address, authorization port, and accounting port. Servers with different address-authorization port-accounting port combinations have separate configurations.
The no radius-server host and default radius-server commands remove settings for the RADIUS server configuration at the specified address-authorization port-accounting port location by deleting the corresponding radius-server host command from running-config.
Command Mode
Global Configuration
Command Syntax
radius-server host ADDR [VRF_INST][AUTH][ACCT][TIMEOUT][DEAD][RETRAN][ENCRYPT]
no radius-server host [ADDR][VRF_INST][AUTH][ACCT]
default radius-server host [ADDR][VRF_INST][AUTH][ACCT]
switch(config)# radius-server host 10.1.1.5
switch(config)#switch(config)# radius-server host RAD-1 auth-port 1850
switch(config)#The radius-server key command defines the global encryption key the switch uses when communicating with any RADIUS server for which a key is not defined.
The no radius-server key and default radius-server key commands remove the global key from running-config.
Command Mode
Global Configuration
Command Syntax
radius-server key [ENCRYPT_TYPE] encrypt_key
no radius-server key
default radius-server key
Encrypted strings entered through this parameter are generated elsewhere.
Related Command
switch(config)# radius-server key 0 cv90jr1
switch(config)#switch(config)# radius-server key 7 020512025B0C1D70
switch(config)#The radius-server retransmit command defines the global retransmit count, which specifies the number of times the switch attempts to access the RADIUS server after the first timeout expiry.
The no radius-server retransmit and default radius-server retransmit commands restore the global retransmit count to its default value of three by deleting the radius-server retransmit command from running-config.
Command Mode
Global Configuration
Command Syntax
radius-server retransmit count
no radius-server retransmit
default radius-server retransmit
Parameters
count retransmit attempts after first timeout expiry. Values range from 1 to 100. Default is 3.
Related Command
Example
switch(config)# radius-server retransmit 5
switch(config)#The radius-server timeout command defines the global timeout the switch uses when communicating with any RADIUS server for which a timeout is not defined.
The no radius-server timeout and default radius-server timeout commands restore the global timeout default period of five seconds by removing the radius-server timeout command from running-config.
Command Mode
Global Configuration
Command Syntax
radius-server timeout time_period
no radius-server timeout
default radius-server timeout
Parameters
time_period timeout period (seconds). Values range from 1 to 1000. Default is 5.
Related Commands
Example
switch(config)# radius-server timeout 50
switch(config)#The resequence command assigns sequence numbers to rules in the configuration mode role. Command parameters specify the number of the first rule and the numeric interval between consecutive rules.
The maximum sequence number is 256.
Command Mode
Role Configuration
Command Syntax
resequence start_num inc_num
Guidelines
Role statement changes are saved to running-config only upon exiting Role configuration mode.
Related Command
The role command places the switch in Role configuration mode.
Example
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
10 deny mode exec command reload
20 deny mode config command (no |default )?router
40 deny mode if command (no |default )?(ip|mac) access-group
50 deny mode config-all command lacp|spanning-tree
60 permit command .*
switch(config)# role sysuser
switch(config-role-sysuser)# resequence 15 5
switch(config-role-sysuser)# exit
switch(config)# show users roles sysuser
The default role is network-operator
role: sysuser
15 deny mode exec command reload
20 deny mode config command (no |default )?router
25 deny mode if command (no |default )?(ip|mac) access-group
30 deny mode config-all command lacp|spanning-tree
35 permit command .*
switch(config)#The permit command adds a permit rule to the configuration mode role. Permit rules authorize access to specified commands for usernames to which the role is applied. Sequence numbers determine rule placement in the role. Commands compare sequentially to rules within a role until it matches a rule. The first matching rule determines a command's authorization. EOS derives sequence numbers for commands without numbers by adding 10 to the number of the role's last rule.
Permit rules use regular expression to denote commands. A mode parameter specifies the command modes for authorized commands. EOS denotes modes either by predefined keywords, a command modes short key, or a regular expression that specifies the long key of one or more command modes.
The no deny and default deny commands remove the specified rule from the configuration mode role. The no sequence number (Role) command also removes the specified rule from the role.
Command Mode
Role Configuration
Command Syntax
[SEQ_NUM] permit [MODE_NAME] command command_name
no permit [MODE_NAME] command ] command_name
default permit [MODE_NAME] command command_name
Guidelines
Permit statements save to the running-config only when exiting Role configuration mode.
Related Commands
The role command places the switch in the Role Configuration Mode.
Example
switch(config)# role sysuser
switch(config-mode-sysuser)# permit mode if-Vl(1|2) command .*
switch(config-mode-sysuser)#The role command places the switch in Role Configuration Mode, which is a group-change mode that modifies a role. A role is a data structure that supports local command authorization through its assignment to user accounts. Roles consist of permit and deny rules that define authorization levels for specified commands. Applying a role to a username authorizes the user to execute commands specified by the role.
The no role and default role commands delete the specified role by removing the role and its statements from running-config.
Command Mode
Global Configuration
Command Syntax
role role_name
no role role_name
default role role_name
Parameter
role_name Name of role.
Commands Available in Role Configuration Mode:
Related Commands
switch(config)# role speaker
switch(config-role-speaker)#This command saves changes to speaker role, then returns the switch to Global configuration mode.
switch(config-role-speaker)# exit
switch(config)#This command discards changes to speaker, then returns the switch to Global configuration mode.
switch(config-role-speaker)# abort
switch(config)#The server (server-group-RADIUS configuration mode) command adds the specified RADIUS server to the configuration-mode group. Servers must be configured with the radius-server host command before adding them to the server group.
A RADIUS server is defined by its server address, authorization port, and accounting port. A group can contain multiple servers with the same IP address that have different authorization or accounting ports.
The no server and default server commands remove the specified server from the group.
Command Mode
Server-Group-RADIUS Configuration
Command Syntax
server LOCATION [VRF_INST][AUTH][ACCT]
no server LOCATION [VRF_INST][AUTH][ACCT]
default server LOCATION [VRF_INST][AUTH][ACCT]
Related Commands
The aaa group server radius command places the switch in Server-group-RADIUS configuration mode.
Example
switch(config)# aaa group server radius RAD-SV1
switch(config-sg-radius-RAD-SV1)# server RAC-1
switch(config-sg-radius-RAD-SV1)# server 10.1.5.14 acct-port 1851
switch(config-sg-radius-RAD-SV1)#The server (server-group-TACACS+ configuration mode) command adds the specified TACACS+ server to the configuration-mode group. Servers must be configured with the tacacs-server host command before adding them to the server group.
A TACACS+ server is defined by its server address and port number. Servers with different address-port combinations have separate statements in running-config.
The no server and default server commands remove the specified server from the group.
Command Mode
Server-group-TACACS+ Configuration
Command Syntax
server LOCATION [VRF_INST][PORT]
no server LOCATION [VRF_INST][PORT]
default server LOCATION [VRF_INST][PORT]
Related Command
The aaa group server tacacs+ command places the switch in Server-group-TACACS+ configuration mode.
Example
switch(config)# aaa group server tacacs+ TAC-GR
switch(config-sg-tacacs+-TAC-GR)# server TAC-1
switch(config-sg-tacacs+-TAC-GR)# server 10.1.4.14
switch(config-sg-tacacs+-TAC-GR)#The service dot1x command in the Monitor Server RADIUS Configuration Mode applies monitoring globally to the RADIUS servers used for 802.1X authentication.
The no service dot1x command disables monitoring and removes the configuration from the running-config.
Command Mode
Monitor Server RADIUS Configuration
Command Syntax
service dot1x
no service dot1x
Parameters
service dot1x - Specify to apply monitoring globally to all RADIUS servers used for 802.1X authentication.
Example
switch(config)# monitor server radius
switch(config-monitor-server-radius)# service dot1x
switch(config-monitor-server-radius)#The show aaa command displays the user database. The command displays the encrypted enable password first, followed by a table of usernames and their corresponding encrypted password.
The command does not display unencrypted passwords.
Command Mode
Privileged EXEC
Command Syntax
show aaa
Example
switch# show aaa
Enable password (encrypted): $1$UL4gDWy6$3KqCPYPGRvxDxUq3qA/Hs/
Username Encrypted passwd
-------- ----------------------------------
admin
janis $1$VVnDH/Ea$iwsfnrGNO8nbDsf0tazp9/
thomas $1$/MmXTUil$.fJxLfcumzppNSEDVDWq9.
switch#
The show aaa authentication lockout command displays the status of locked-out users who could not log within the specified time and number of login attempts.
Command Mode
Privileged EXEC
Command Syntax
show aaa authentication lockout
Example
switch# show aaa authentication lockout
User Start Time End Time Expires In
--------- ------------------------- ------------------------- ----------
alice Fri Jul 12 17:50:06 2020 Fri Jul 12 17:51:06 2020 0:00:58The show aaa counters command displays the number of service transactions performed by the switch since the last time the counters were reset.
Command Mode
Privileged EXEC
Command Syntax
show aaa counters
Example
switch# show aaa counters
Authentication
Successful: 30
Failed: 0
Service unavailable: 0
Authorization
Allowed: 188
Denied: 0
Service unavailable: 0
Accounting
Successful: 0
Error: 0
Pending: 0
Last time counters were cleared: neverThe show aaa methods command displays all the named method lists defined in the specified Authentication, Authorization, and Accounting (AAA) service.
Command Mode
Privileged EXEC
Command Syntax
show aaa methods [SERVICE_TYPE [accounting | authentication | authorization | all]]
Parameters
Example
switch# show aaa methods all
Authentication method lists for LOGIN:
name=default methods=group tacacs+, local
Authentication method list for ENABLE:
name=default methods=local
Authorization method lists for COMMANDS:
name=privilege0-15 methods=group tacacs+, local
Authentication method list for EXEC:
name=exec methods=group tacacs+, local
Accounting method lists for COMMANDS:
name=privilege0-15 default-action=none
Accounting method list for EXEC:
name=exec default-action=none
switch#The show management ldap command displays information about the LDAP configuration.
Command Mode
EXEC
Command Syntax
show management ldap
switch# show management ldap
LDAP server: prod-dc-hq1.aristanetworks.com/389
Binds requested: 6
Binds successful: 6
Binds failed: 0
Binds timed out: 0
FIPS is ON
Last time counters were cleared: 1:16:41 agoswitch# show management security ssl profile
Profile State
----------------- -----------
testProfile valid
To verify a user accounts authorization being performed by ldap, use “show users detail”:
switch# show users detail
Session Username Roles TTY State Duration Auth Remote Host
-------- --------- ------------- ---- ----- --------- ---------- ---------------------------------------
1006 erahn network-admin vty3 E 0:00:05 group ldap fd7a:629f:52a4:dc25:b08d:feff:feed:2ce7switch# show users
Line User Host(s) Idle Location
1 con 0 admin idle 01:19:00 -
2 vty 10 srv-sw-ldaptest idle 01:19:00 172.16.124.151
* 3 vty 3 erahn idle 00:00:04 fd7a:629f:52a4:dc25:b08d:feff:feed:2ce7The show management security auto-certificate profile displays information about auto-certificate profiles configured on the switch. Add the detail parameter to displayed detailed information about the profiles.
Command Mode
EXEC
Command Syntax
show management security auto-certificate profile profile_name detail
Examples
switch# show management security auto-certificate profile CertAlpha
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Valid
Next request in 89 days, 21:59:47 at: 2025-02-05 01:45:51switch# show management security auto-certificate profile CertAlpha detail
Auto certificate profile CertAlpha:
Key: clientkey.pem
State: Valid
Next request in 89 days, 21:59:37 at: 2025-02-05 01:45:51
Initial enrollment statistics:
Number of successes: 1
Number of failures: 0
Renewal statistics:
Number of successes: 0The show management security auto-certificate protocol est command displays information about all Enrollment over Secure Transport (EST) protocol profiles configured on the switch.
Command Mode
EXEC
Command Syntax
show management security auto-certificate protocol est [profile_name] [detail]
Examples
switch# show management security auto-certificate protocol est EST_2
Automatic Certificate Management policy EST_2:
State: Invalid
Last error:
Message: Invalid SSL profile
Time: 2025-05-07 06:28:20switch# show management security auto-certificate protocol est EST_2 detail
Automatic Certificate Management policy EST_2:
State: Invalid
Last error:
Message: Invalid SSL profile
Time: 2025-05-07 06:28:20
Managed certificate profile:
certProfileBravo:
Certificate state: Needs enrollingThe show monitor server radius command in EXEC mode displays information about RADIUS server monitoring on the switch. Use the output to determine the status of the RADIUS servers.
Command Mode
EXEC
Command Syntax
show monitor server radius [detail]
Parameters
Examples
switch(config)# show monitor server radius
Probe method: Status-Server packet
RADIUS Server Messages Sent Messages Accepted Messages Dropped Status
------------- ------------- ----------------- ---------------- ---------
10.0.0.101 48 35 1 alive
10.0.0.102 48 29 1 not aliveswitch(config)# show monitor server radius detail
Probe method: Status-Server packet
RADIUS server: 10.0.0.101, Authentication port: 33922, Accounting port: 34685
Status: alive, Last changed: 0:02:32 ago
Last probed: 0:00:02 ago
Last successful probe: 0:00:02 ago, Failed probes since then: 0
Messages sent: 47
Messages accepted: 34
Messages dropped: 1
Last time counters were cleared: never
RADIUS server: 10.0.0.102 Authentication port: 34406, Accounting port: 47258
Status: not alive, Last changed: 0:00:12 ago
Last probed: 0:00:02 ago
Last successful probe: 0:00:27 ago, Failed probes since then: 4
Messages sent: 47
Messages accepted: 29
Messages dropped: 1
Last time counters were cleared: neverThe show privilege command displays the current privilege level for the CLI session.
Command Mode
EXEC
Command Syntax
show privilege
Example
switch> show privilege
Current privilege level is 15
switch>The show radius command displays statistics for the RADIUS servers that the switch accesses.
Command Mode
EXEC
Command Syntax
show radius
Example
switch# show radius
RADIUS server : radius/10
Connection opens: 204
Connection closes: 0
Connection disconnects: 199
Connection failures: 10
Connection timeouts: 2
Messages sent: 1490
Messages received: 1490
Receive errors: 0
Receive timeouts: 0
Send timeouts: 0
Last time counters were cleared: never
switch#The show radius proxy client group command displays information about RADIUS proxy configurations.
Command Mode
Privileged EXEC
Command Syntax
show radius proxy client group group_name
Parameters
group_name - Display all RADIUS proxy client groups or specify a group name to see details about a specific group.
Example
switch# show radius proxy client group
Radius Client Group : MyClientGroup
Last time counters were cleared : never
Client : 192.168.1.25, authentication port 1812, accounting port 1813, vrf default
Resolved IP address : 192.168.1.25/32
Messages received: 0
Messages sent: 0
Accept response sent: 0
Reject response sent: 0
Counting start received: 0
Interim updates received: 0
Accounting stop received: 0
Bad requests: 0
CoA requests sent: 0
DM requests sent: 0
CoA ACKs received: 0
DM ACKs received: 0
CoA NAKs received: 0
DM NAKs received: 0
Bad responses: 0
Connection errors: 0The show radius proxy server group command displays information about RADIUS proxy server group configurations.
Command Mode
Privileged EXEC
Command Syntax
show radius proxy server group group_name
Parameters
group_name - Display all RADIUS proxy server groups or specify a group name to see details about a specific group.
Example
switch# show radius proxy server group
            Radius Server Group: MyServerGroup
                Radius Server 1: RADIUS
            Resolved IP address: 192.168.25.33
Status: activeThe show tacacs command displays statistics for the TACACS+ servers that the switch accesses.
Command Mode
EXEC
Command Syntax
show tacacs
Example
switch# show tacacs
TACACS+ server            : tacacs/49
          Connection opens:      15942
         Connection closes:          7
    Connection disconnects:       1362
       Connection failures:          0
       Connection timeouts:          0
             Messages sent:      34395
         Messages received:      34392
            Receive errors:          0
          Receive timeouts:          2
             Send timeouts:          0

Last time counters were cleared: never

TACACS+ source-interface: Enabled
  TACACS+ outgoing packets will be sourced with an IP address associated with the
Loopback0 interfaceThe show users accounts command displays the names, roles, and privilege levels of users that are listed in running-config. The SSH public key is also listed for names for which an SSH key is configured.
Command Mode
Privileged EXEC
Command Syntax
show users accounts
Example
switch# show users accounts
user: FRED
       role: <unknown>
       privilege level: 1
       ssh public key: ssh-rsa AAAAB3NzaC1yc2EAAAADAQABAAABAQDjUg2VDiBX7In0q
HtN5PyHOWtYvIoeZsxF5YmesQ/rh++mbpT504dL7So+Bpr9T/0qIj+zilat8fX/JlO42+3pjfkHY/+l
sT2EPNjGTK7uJv1wSGmhc3+90dNmJtr5YVlJFjjQ5m+5Pa+PGe3z4JIV1lY2NhLrV2fXtbciLdjnj6F
AlhXjiLt51DJhG13uUxGBJe0+NlGvpEsTJVJvMdJuS6weMi+xSXc9yQimVD2weJBHsYFnghST2j0pAy
F2S7/EOU13pY42RztDSs42nMNNrutPT0q5Z17aAKvhpd0dDlc+qIwrCrXbeIChHem7+0N8/zA3alBK4
eKSFSZBd3Pb admin@switch
switch#
user: JANE
       role: sysuser2
       privilege level: 1
user: admin
       role: network-admin
privilege level: 1The show users detail command displays information about active AAA login sessions. Information includes username, roles, TTY, state of the session (pending or established), duration, authentication method, and if available, remote host and remote username.
Command Mode
Privileged EXEC
Command Syntax
show users detail
Example
switch# show users detail
Session  Username Roles           TTY    State Duration  Auth          Remote Host
-------   ---------- ------------ ------ ----- --------  ------------- ------------
2      admin     network-admin    ttyS0  E     0:01:21  local
4      joe       sysadmin         telnet E     0:02:01  local        sf.example.com
6      alice     sysadmin         ssh    E     0:00:52  group radius ny.example.com
7      bob       sysadmin         ssh    E     0:00:48  group radius la.example.com
8      kim       network-admin1   ssh    E     0:00:55  group radius de.example.com
9      admin     network-admin    ssh    E     0:00:07  local        bj.example.com
10 max network-admin telnet E 0:00:07 local sf.example.comThe show users roles command displays the name of the default role and the contents of the specified roles. Commands that do not specify a role display the rules in all built-in and configured roles.
Command Mode
Privileged EXEC
Command Syntax
show users roles [ROLE_LIST]
Parameters
Related Command
The role command places the switch in Role configuration mode, which is used to create new roles or modify existing roles.
Example
switch# show users roles
The default role is network-operator

role: network-admin
        10 permit command .*
role: network-operator
        10 deny mode exec command bash|\|
        20 permit mode exec command .*
role: sysuser
        15 deny mode exec command reload
        20 deny mode config command (no |default )?router
        25 deny mode if command (no |default )?(ip|mac) access-group
        30 deny mode config-all command lacp|spanning-tree
        35 permit command .*
        40 deny mode exec command .*
50 permit mode exec command show|clear (counters|platform)|configureThe show users command displays the usernames that are currently logged into the switch.
Command Mode
Privileged EXEC
Command Syntax
show users
Example
switch# show users
    Line       User       Host(s)              Idle       Location
   1 vty 2     john       idle                       1d  10.22.6.113
   2 vty 4     jane       idle                 21:33:00  10.22.26.26
* 3 vty 6 ted idle 00:00:01 10.17.18.71The tacacs-server host command sets communication parameters for communicating with a specific TACACS+ server. These values override global settings when the switch communicates with the specified server.
A TACACS+ server is defined by its server address and port number. Servers with different combinations of address-port-VRF-multiplex settings have separate statements in running-config.
The no tacacs-server host and default tacacs-server host commands remove settings for the TACACS+ server configuration at the specified address-port-VRF combination by deleting the corresponding tacacs-server host command from running-config.
Command Mode
Global Configuration
Command Syntax
tacacs-server host SERVER_ADDR [MULTIPLEX][VRF_INST][PORT][TIMEOUT][ENCRYPT]
no tacacs-server host [SERVER_ADDR][MULTIPLEX][VRF_INST][PORT]
default tacacs-server host [SERVER_ADDR][MULTIPLEX][VRF_INST][PORT]
switch(config)# tacacs-server host 10.1.1.5
switch(config)#switch(config)# tacacs-server host TAC_1 timeout 20 key rp31E2v
switch(config)#switch(config)# tacacs-server host 10.12.7.9 single-connection port 54
switch(config)#The tacacs-server key command defines the global encryption key the switch uses when communicating with any TACACS+ server for which a key is not defined.
The no tacacs-server key and default tacacs-server key commands remove the global key from running-config.
Command Mode
Global Configuration
Command Syntax
tacacs-server key [ENCRYPT_TYPE] encrypt_key
no tacacs-server key
default tacacs-server key
Encrypted strings entered through this parameter are generated elsewhere.
Related Command
switch(config)# tacacs-server key 0 cv90jr1
switch(config)#switch(config)# tacacs-server key 7 020512025B0C1D70
switch(config)#The tacacs-server policy command programs the switch to permit access to TACACS+ servers that send mandatory attribute-value (AV) pairs that the switch does not recognize. By default, the switch denies access to TACACS+ servers when it receives unrecognized AV pairs from the server.
The switch recognizes the following mandatory AV pairs:
priv-lvl=x where x is an integer between 0 and 15.
The no tacacs-server policy and default tacacs-server policy commands restore the switch default of denying access to servers from which it receives unrecognized mandatory AV pair by deleting the tacacs-server policy statement from running-config.
Command Mode
Global Configuration
Command Syntax
tacacs-server policy unknown-mandatory-attribute ignore
no tacacs-server policy unknown-mandatory-attribute ignore
default tacacs-server policy unknown-mandatory-attribute ignore
Parameters
Example
switch(config)# tacacs-server policy unknown-mandatory-attribute ignore
switch(config)#The tacacs-server timeout command defines the global timeout the switch uses when communicating with any TACACS+ server for which a timeout is not defined.
The no tacacs-server timeout and default tacacs-server timeout commands restore the global timeout default period of five seconds by removing the tacacs-server timeout command from running-config.
Command Mode
Global Configuration
Command Syntax
tacacs-server timeout time_period
no tacacs-server timeout
default tacacs-server timeout
Parameters
time_period timeout period (seconds). Values range from 1 to 1000. Default is 5.
Related Command
Example
switch(config)# tacacs-server timeout 20
switch(config)#The username ssh-key command configures an SSH key for the specified username. Command options allow the key to be entered directly into the CLI or referenced from a file.
The specified username must be previously configured through a username command.
The no username ssh-key and default username ssh-key commands delete the SSH key for the specified username by removing the corresponding username ssh-key command from running-config.
Command Mode
Global Configuration
Command Syntax
username name sshkey KEY
no username name sshkey [role]
default username name sshkey [role]
Valid usernames begin with A-Z, a-z, or 0-9 and may also contain any of these characters:
@ # $ % ^ & * - _ = + ; < > , . ~ |
Example
switch(config)# username john secret x245
switch(config)# username john sshkey file john-ssh
switch(config)#The username command adds a username to the local file and optionally assigns a password to the username. If the command specifies an existing username, the command replaces the password in the local file. The command can also define a username without a password or remove the password from a username.
The no username command deletes the specified username by removing the corresponding username statement from running-config. The default username command removes user-specified usernames, but restores the admin username to its default parameters.
The no username role command assigns the default role assignment to the specified username statement by editing the corresponding username statement in running-config. The default username role command reverts the specified username to its default role by editing the corresponding username statement in running-config. For the admin username, this restores network-admin as its role, even if the admin username has been deleted and then created again.
Command Mode
Global Configuration
Command Syntax
username name [privilege_level] security [role_user]
no username name [role]
default username name [role]
All parameters except name can be placed in any order.
Valid usernames begin with A-Z, a-z, or 0-9 and may also contain any of these characters:
@ # $ % ^ & * - _ = + ; < > , . ~ |
Guidelines
Encrypted strings entered through this parameter are generated elsewhere. The secret 5 option (security) is typically used to enter a list of username-passwords from a script.
The security parameter is mandatory for unconfigured usernames. For previously configured users, the command can specify a privilege_level or ROLE without a security setting.
username admin privilege 1 role network-admin nopasswordswitch(config)# username john secret x245
switch(config)# username john secret 0 x245switch(config)# username john secret 5 $1$sU.7hptc$TsJ1qslCL7ZYVbyXNG1wg1
switch(config)#A user authenticates the username john by entering x245 when the CLI prompts for a password.
switch(config)# username jane nopassword
switch(config)#switch(config)# no username william
switch(config)#Transport Layer Security (TLS), the successor to Secure Sockets Layer (SSL), is a security protocol used to communicate between client and server. It establishes an encrypted communication channel to secure data.
An SSL certificate is required to establish a secure connection between the client and server. The certificate includes all of the details necessary for authentication. Cryptographic keys are used to provide a secure channel of communication. TLS uses two cryptographic keys: a private key known only to the server and a public key embedded in the certificate. The keys are used to validate the certificate.
We can manage and configure SSL certificates, keys, and profiles with the SSL certificate, key, and profile management framework. SSL is an application-layer protocol that transfers the data securely between the client and server using a combination of authentication, encryption, and data integrity. SSL uses certificates and private-public key pairs to provide this security. A user can configure an SSL profile, which includes a certificate, key, and trusted CA certificates used in SSL communication. A user can manage certificates, keys, and also multiple SSL profiles. An SSL profile can be configured and attached to any other EOS configuration which supports SSL communication. The individual EOS configuration using this framework includes details of using the SSL profile in their configuration.
The only private keys supported are those using the RSA algorithm. Encode both the certificate and keys in the Privacy Enhanced Mail (PEM) format.
$cat server.crt
-----BEGIN CERTIFICATE-----
MIIC3zCCAkgCAQkwDQYJKoZIhvcNAQEEBQAwcTELMAkGA1UEBhMCVVMxCzAJBgNV
BAgMAkNBMQswCQYDVQQHDAJTQzEPMA0GA1UECgwGQXJpc3RhMQwwCgYDVQQLDANT
RE4xCzAJBgNVBAMMAmNhMRwwGgYJKoZIhvcNAQkBFg1jYUBhcmlzdGEuY29tMCAX
DTE0MDgxMTIxNDQxN1oYDzIwNjkwNTE0MjE0NDE3WjB5MQswCQYDVQQGEwJVUzEL
MAkGA1UECAwCQ0ExCzAJBgNVBAcMAlNDMQ8wDQYDVQQKDAZBcmlzdGExDDAKBgNV
BAsMA1NETjEPMA0GA1UEAwwGc2VydmVyMSAwHgYJKoZIhvcNAQkBFhFzZXJ2ZXJA
YXJpc3RhLmNvbTCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAOBOP/jh
xk28sUH+lhM/mY6QoyLGcbnygwe/hzIjn2mASnf7uPFGhB62JTt7tQv2xmu/MJfs
aVsNeYXP3ZOcmRO0uk9suGVbII7QJUomnsq1dJh59UyMfws6V6ergmhwEZCDIirV
7nbUDz+uSdNutQL4w/VB+juuWXQ8ztbmygT2ymySaHRK3XnDrAiva0UUVbSmEHH0
wLPsNVNYUxJ4PpOB9luw4upe6ACF9SFtMDz3BDcrL6Gq5idWw3YkQfzBwEl+5hkF
hu0owON29I5T8FpAx+Hzpl48YWW65d/4F40S3XRN312xALM8RrQOU/Chx9Sfg0iJ
dsXWNagx1eyW2EECAwEAATANBgkqhkiG9w0BAQQFAAOBgQBedfuKHvNDpEkdO2AE
Kihs/YeRGgp+5g7hXU0U2TMAMS545ZQ99pFbnScmIC0m68aw1VXILuj+vlkxAM27
oc8iB+gG7oaFtJpWTvmIHqzeHWb0zrwjPhtXTafWEoam8sJZt38Pc4UVb7lQCd6v
ZCLZZJmC2IL0SG7bLN7yaALCSQ==
-----END CERTIFICATE-----$cat server.key
-----BEGIN RSA PRIVATE KEY-----
MIIEowIBAAKCAQEA4E4/+OHGTbyxQf6WEz+ZjpCjIsZxufKDB7+HMiOfaYBKd/u4
8UaEHrYlO3u1C/bGa78wl+xpWw15hc/dk5yZE7S6T2y4ZVsgjtAlSiaeyrV0mHn1
TIx/CzpXp6uCaHARkIMiKtXudtQPP65J0261AvjD9UH6O65ZdDzO1ubKBPbKbJJo
dErdecOsCK9rRRRVtKYQcfTAs+w1U1hTEng+k4H2W7Di6l7oAIX1IW0wPPcENysv
oarmJ1bDdiRB/MHASX7mGQWG7SjA43b0jlPwWkDH4fOmXjxhZbrl3/gXjRLddE3f
XbEAszxGtA5T8KHH1J+DSIl2xdY1qDHV7JbYQQIDAQABAoIBACv/TU8NQi+HXqGa
RWe7Juyu9EDi+fXGWutPJz6vfBpenrzQNGOnOE0p3z2+szGIkz0ZQHfcWIISr46O
ymCk6+XQombn5XeEG2vH6jiUQLt0Qk2SRopgWJ8kL4NlAexoZxmYj0AlvGO0jtUn
47VEVt8hWpal/WZteYByWQQQOvoj7EhlANIKUGUG9yOcBcEApdHsgOcXewrbilZQ
d4kbpegxQhjKU9jLUXRsIPV2YFrDcT83/94PFTRk/vFBOnWS/Ygt5vRedcoF2HcR
TJMyE+JwnwGJzTPKwbPJgLnjrEGVrqEerCuTU9v0PpFxu0AOEeV1kPyNbRZzzC+p
al70ZI0CgYEA/Ge1Hj5OBjS2DLUYG0zhmc4xoiIqcgPJCn6QQmfqa6DbscQzXsnp
GqNlwvB76L0mwNOSABX53YaXhFCrYXMRsXWl95hK7NYCGnD6f/fYcr3u+NdBm5+N
qEiqcq779arAXqGaN/TGKsm507ngyLBrMbUlaPQEXfaBjrQL3f0k7qMCgYEA44AW
1ptUWy0Wx5oa1wdYVgGw+Wbxb8JY88pj29JhE3Qwhy9FBq7x0wZOoQDSkyvbu9aZ
bEiUtctXDDNE/Fy7XgEBMiqrn4R383pbZ5LnmsFKZEcADU1Pe4HjDgSq1rjNSJSA
xEz8xRQvIvy4kpp/tpKsN/Xg2ZBnQmqgj6LWv8sCgYBKeSsWnlmVOS5R94kCXR/f
qtg4N46Aj59dClT0Uwb29MJ95B8oI7k00+ttpllZJZ5unL5iahmMhG7maor2uOYK
j2UF9hh9YvPB633uDin+SQ5eu9yu11gLxE0Og5TyOoyCH3qKch2aeGTtFNY/QNaQ
FxvPqNg1BUva2EL8H/oqswKBgQDjbW1nZSjTbSPUrq4eQG2CrXYqHUtHmlYqgS2K
16nMNN8+hXbP05xUhX2dXqEkFzg3c7U0lupzQq/mtmpEjr+Qnhh/+kBP27G+aZdu
12FJR+oCjSf0JFFM+u/tV6UhuuUdpbeEhiI7Mo5cv6AUjvcVoVMhLmB1nvJbZxTU
AsoEOQKBgHHVuuq4kWDfORCYwTvZPX0byQu++QhlOFfClYBIVuCP4/cU0o3Kw1Z6
tf+zP2rBMOl5eD7IBHjAtOlNjXcFgiyymNxJDKJSmTpw1VePncmuT5UMq8rbljSW
Yg0QGwyvB1Cat2mpgqVWS7YT0nmTooWmQdO3Qp48f+bVvmO/dJXS
-----END RSA PRIVATE KEY-----The copy file: certificate: command copies the certificate to the certificate: file system from any supported source URLs of the copy command. The source file may contain multiple PEM-encoded certificates but must not contain other entities such as keys.
Example
switch(config)# copy file:/tmp/ssl/server.crt certificate:
Copy completed successfully.
switch(config)#switch(config)# copy file:tmp/ssl/mixed.crt certificate:
% Error copying file:tmp/ssl/mixed.crt to certificate: (Multiple types of entities in
certificate file not supported)
switch(config)#switch(config)# copy file:tmp/ssl/bad.crt certificate:
% Error copying file:tmp/ssl/bad.crt to certificate: (Invalid certificate)
switch(config)#switch(config)# copy file:tmp/ssl/dsa.crt certificate:
% Error copying file:tmp/ssl/dsa.crt to certificate: (Certificate does not have RSA key)
switch(config)#The delete certificate command deletes a certificate configuration from the certificate: file system on the switch.
Example
switch(config)#delete certificate:server.crt
switch(config)#The following commands help the user to generate a self-signed certificate or Certificate Signing Request (CSR).
switch# security pki certificate generate self-signed test.crt key test.key
Common Name for use in subject: test
[...]
certificate:test.crt generated
switch#switch# security pki certificate generate signing-request key test.key digest sha256 validity 365
Common Name for use in subject: test
[...]
certificate:test.crt generated
switch#switch# security pki certificate generate signing-request key test.key parameters common-name Test [country US ...]
certificate:test.crt generated
switch#The copy command copies an RSA key to the sslkey: file system. The key can be copied from any supported source URLs of the copy command. The source file must contain only one key. Password-protected keys are not supported.
Example
switch# copy file:/tmp/ssl/server.key sslkey:
Copy completed successfully.
switch#switch# copy file:tmp/ssl/multi.key sslkey:
% Error copying file:tmp/ssl/multi.key to sslkey: (Multiple PEM entities in
single file not supported)switch# copy file:tmp/ssl/bad.key sslkey:
% Error copying file:tmp/ssl/bad.key to sslkey: (Invalid RSA key)switch# copy file:/tmp/ssl/pass.key sslkey:
% Error copying file:tmp/ssl/pass.key to sslkey: (Password protected keys are not
supported)The delete command deletes the key configuration from the switch.
Example
switch# delete sslkey:server.key The following commands generate the RSA keys.
switch# security pki key generate rsa 2048 test.key switch# security pki certificate generate self-signed test.crt key test.key generate rsa 4096
switch# security pki certificate generate signing-request key test.key generate rsa 2048Configure an SSL profile with a certificate and its corresponding RSA key. The public key information in the certificate must match the RSA key. Use the certificate and RSA key pair to authenticate to the peer during SSL negotiation. The individual EOS features that use SSL profile configuration decide if the certificate and key configuration is optional or mandatory.
switch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# certificate server.crt key server.keyswitch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# certificate server.crt key client.key
switch(config-mgmt-sec-ssl-profile-server)# show management security ssl profile
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'server.crt' does not match
with keyDuring SSL negotiation with mutual authentication, the peer (or client) certificate is verified by checking if it is signed by one of these trusted certificates. The full bundle of certificates leading to the trusted certificates must be included for peer certificates that do not have a chain to a trusted certificate. The individual EOS features that use SSL profile configuration will decide whether the trusted certificate configuration is optional or mandatory.
switch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# trust certificate ca1.crt
switch(config-mgmt-sec-ssl-profile-server)# trust certificate ca2.crtCertificate chains establish a chain of trust for the SSL Profile server certificate, ensuring its authenticity to a remote party. Several chain certificate commands can be issued to build a certificate chain with many intermediate CAs, regardless of the order. Use the chain certificate command to configure the certificate chain for an SSL profile. The no form of the command deletes the certificate configuration.
Examples
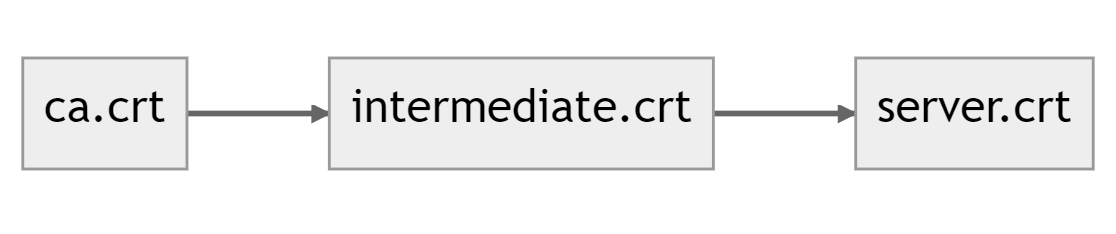
switch#(config)# management security
switch#(config-mgmt-security)# ssl profile server
switch#(config-mgmt-sec-ssl-profile-server)# certificate server.crt key server.key
switch#(config-mgmt-sec-ssl-profile-server)# chain certificate intermediate.crt
switch#(config-mgmt-sec-ssl-profile-server)# exit
switch(config)#switch# config
switch#(config)# management security
switch(config-mgmt-security)# ssl profile client
switch(config-mgmt-sec-ssl-profile-client)# certificate client.crt key client.key
switch(config-mgmt-sec-ssl-profile-client)# trust certificate ca.crtswitch# config
switch#(config)# management security
switch(config-mgmt-security)# ssl profile client
switch(config-mgmt-sec-ssl-profile-client)# crl intermediate.crl
switch(config-mgmt-sec-ssl-profile-client)# crl ca.crl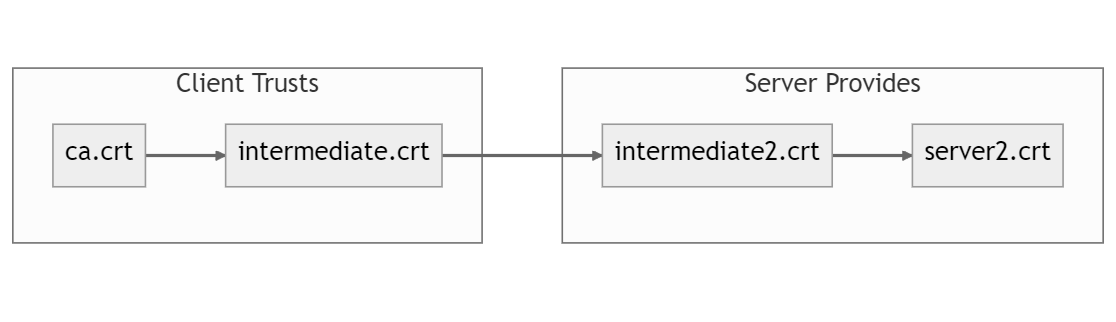
switch(config)# management security
switch(config-mgmt-security)# ssl profile server2
switch(config-mgmt-sec-ssl-profile-server2)# certificate server2.crt key server2.key
switch(config-mgmt-sec-ssl-profile-server2)# chain certificate intermediate2.crt
switch(config-mgmt-sec-ssl-profile-server2)# chain certificate intermediate.crt
switch(config-mgmt-sec-ssl-profile-server2)# exit
switch(config-mgmt-security)# exit
switch(config)#You can divide a certificate chain into two segments, each configured on a separate peer. As long as this division occurs somewhere between the client and the server, they can collaborate to assemble a complete chain. The provided example illustrates precisely this scenario, demonstrating how to configure server and client SSL profiles with a split certificate chain.
switch(config)# management security
switch(config-mgmt-security)# ssl profile server2
switch(config-mgmt-sec-ssl-profile-server2)# certificate server2.crt key server2.key
switch(config-mgmt-sec-ssl-profile-server2)# chain certificate intermediate2.crt
switch(config-mgmt-sec-ssl-profile-server2)# exit
switch(config-mgmt-security)# exit
switch(config)#switch(config)# management security
switch(config-mgmt-security)# ssl profile client
switch(config-mgmt-sec-ssl-profile-client)# certificate client.crt key client.key
switch(config-mgmt-sec-ssl-profile-client)# trust certificate ca.crt
switch(config-mgmt-sec-ssl-profile-client)# trust certificate intermediate.crt
switch(config-mgmt-sec-ssl-profile-client)# exit
switch(config-mgmt-security)# exit
switch(config)#Incorrect Configuration Example
The following configuration will not work, as it results in invalid SSL profiles.
switch(config)# management security
switch(config-mgmt-security)# ssl profile server2
switch(config-mgmt-sec-ssl-profile-server2)# certificate server2.crt key server2.key
switch(config-mgmt-sec-ssl-profile-server2)# chain certificate intermediate.crt
switch(config-mgmt-sec-ssl-profile-server2)# show management security ssl profile
Profile State Additional Info
---------------------------- ------------- ----------------------------------------
server3 invalid Profile has invalid certificate chain
switch(config-mgmt-sec-ssl-profile-server3)# exit
switch(config-mgmt-security)# exit
switch(config)#switch(config)# management security
switch(config-mgmt-security)# ssl profile client3
switch(config-mgmt-sec-ssl-profile-client3)# certificate client3.crt key client3.key
switch(config-mgmt-sec-ssl-profile-client3)# trust certificate intermediate.crt
switch(config-mgmt-sec-ssl-profile-client3)# show management security ssl profile
Profile State Additional Info
---------------------------- ------------- ----------------------------------------
client3 invalid Profile has invalid trusted certificate
chain
switch(config-mgmt-sec-ssl-profile-client3)# exit
switch(config-mgmt-security)# exit
switch(config)#EOS conducts various checks on the certificates in an SSL profile before allowing its use. You can modify, add to, or relax these checks locally. Here are some checks EOS performs before communicating with the peer:
switch(config-mgmt-sec-ssl-profile-client)# certificate requirement extended-key-usageswitch(config-mgmt-sec-ssl-profile-client)# trust certificate requirement basic-constraints ca true
switch(config-mgmt-sec-ssl-profile-client)# chain certificate requirement basic-constraints ca trueswitch(config-mgmt-sec-ssl-profile-client)# certificate policy expiry-date ignoreThe show management security ssl profile command displays the SSL profile status information. To view a specific SSL profile status, use the name of the SSL profile. Otherwise, all SSL profile statuses are displayed.
Example
switch# show management security ssl profile server
Profile State
------------- -----------
server valid
If the SSL profile contains errors, an invalid state is displayed, and the errors are listed in the third column. After fixing the error, the SSL profile becomes valid.
switch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'server.crt' does not match
with keyswitch# show management security ssl profile server
Profile State Error
------------- ------------- -------------------------------------
server invalid Certificate 'ca2.crt' does not existswitch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'foo.crt' is trusted and not
a root certificateswitch# show management security ssl profile server
Profile State Error
------------- ------------- -------------------------------------
server invalid Certificate 'server.crt' has expiredswitch# show management security ssl profile server
Profile State Error
-------------- ------------- ---------------------------------------------
server invalid Profile has invalid certificate chain
Certificate 'intermediate.crt' does not existswitch01# show running-config section ssl
management security
ssl profile profile01
certificate cert.pem key key.pemswitch01# security pki certificate generate signing-request rotation ssl profile profile01 key generate rsa 2048 parameters common-name switch01
Rotation ID: 2ad7771e8cbc11ebbba37483ef8d9c4b
Certificate Signing Request:
-----BEGIN CERTIFICATE REQUEST-----
MIICZzCCAU8CAQAwEzERMA8GA1UEAwwIc3dpdGNoMDEwggEiMA0GCSqGSIb3DQEB
AQUAA4IBDwAwggEKAoIBAQCy5EsczfEZlAVNZQ8/nfRgEF3bg/tz0XrQJwP/zHhI
UFx1A1VI4O7XhUrYReH1h4OQWhXXX0AHTLTsaClJWHH9m7SXb4iZVo/Y1zXGdyju
1FmnWnNDi72M8f60WXG9gAMtnZK9K53A3lwvrKS+CwJkLCOjlH4xyp1Wsg1+yfay
AdfXAj+s1Vmg3Rux/XR8iP3N620YVbQ+AfWUQkSNFSsykcTeLvx2WybqX4p4Kids
nqU28ml/NZPS5wEc2OXhagrBn3jHbxdmI33/4SJHN8iNZ6h+gQz+JI18bQrlTHng
RzAx1ENvnz7ZzzeN/n/wh/ArZ6Q9aojrBtAk55aGuY4hAgMBAAGgDzANBgkqhkiG
9w0BCQ4xADANBgkqhkiG9w0BAQsFAAOCAQEAqwQbAsdw6UhpvjDk8OdmXLgCNOSC
jGFLFZe4I67gDmyGQR2lG1brRTQPKp7OphpPxaqr3YvxErEFdQ35gvIUyo9j8qp1
F22yAZGjLqU3prnGLEAZ/I3PcdivNVzL9UJw/JMfHI1CMH6yGtbEI2BXsCTetfxm
JE+N9ujfBlQ/MjUR6IszNxEB2YkFh/DvnVUHoqV0ka+JRmMhGkmTrXwad8bhxYZs
g7cwXktsMLuy2otK21fkFcRvd9OHXssJ2Mf7914ALiDe2sfixHX+35SytR8bahTk
z09HPCkxJmfl+cdhS9SWXrXpHHwXicjwYCj1pqZulBFXtgnVs2Kmd3NnRA==
-----END CERTIFICATE REQUEST-----switch# security pki certificate generate signing-request rotation ssl profile <profile-name>
key generate rsa <2048|3072|4096>
[ import-timeout <minutes> ] (default: 60 mins)
[ digest <sha256|sha384|sha512> ] (default: sha256) parameters common-name <common-name>
[ country <country-code> ]
[ state <state-name> ]
[ locality <locality-name> ]
[ organization <org-name> ]
[ organization-unit <org-unit-name> ]
[ email <email> ]
[ subject-alternative-name [ ip <ip1 ip2 …> ]
[ dns <nm1 nm2 …> ] [ dns <nm1 nm2 …> ]Use the show security pki certificate rotation command to view the status of rotation IDs.
switch# show security pki certificate rotation
Rotation ID Profile Name State Expiry
--------------------------------- ------------ --------------- -------------------
2ad7771e8cbc11ebbba37483ef8d9c4b profile01 Import Pending 2021-03-24 10:15:37switch# security pki certificate rotation import 2ad7771e8cbc11ebbba37483ef8d9c4b
Enter TEXT certificate. Type 'EOF' on its own line to end.
-----BEGIN CERTIFICATE-----
MIICnTCCAYWgAwIBAgIJANzHst3ljdWfMA0GCSqGSIb3DQEBCwUAMA4xDDAKBgNV
BAMMA2ZvbzAeFw0yMTAzMjQxNjAyMDdaFw0yMjAzMjQxNjAyMDdaMA4xDDAKBgNV
BAMMA2ZvbzCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAK2LhqPnQ3Oz
1Pg1PB5toNyCNB60IdCDUVXZcwmyCgS6ifwBYgmw/mCq3iOFncEilaCNIkaFKiWf
b7s43jQd9tmAbnnQw3xUO8jDweus+yCumMNjLLQApbTOZDE4zDonmbWh6kswh8qI
batiz9wR7l5K1bPbbmQx6nO28LrcLCuFSZWrw4R2nprQxdoo5eAotMsGDQdh2vn7
k4yD0CQGVCquVzKI+iVgW7yIfiZ9cwWdFTAlTmkrqQsq+edZmvnuNcOaZm22R5Sb
aPy9osv82oZk8iMX+oDYddY2wMQzLd7ByWlAh4bzCJxNMPIz8hrxU84up0I4srXi
xDVXdL1d2JsCAwEAATANBgkqhkiG9w0BAQsFAAOCAQEADkjfobxF7BAVFdIjyWHL
ID+9D1t96JvCe+PDUyggow6iZE8ROq2fIFHuXhXMrd/neN3WtxqtjvGBnS49t4fa
qIcjerkIPwLaBSwWdpm/1FrIFejYqU0symRE3bKJULLBEdQhyox37D2uqPm71ado
5rXCX9pSu2oNOThd/877QKxtrKa5pekx1acxEa4E0QJ0/YPwkA5nCzM9jy7DZlH2
+cdtCxREeqlhOJUJxQ2354LyykU2fOXe6AGGdVE9hdIOJDnG26VVb+gFt2qaKD5+
3D3/Gd1pm4P3+9aENlhAcr0PUoL3xUApeIdkEf7n8KHiNP+gmlPyVDTCAudwHnwq
Vg==
-----END CERTIFICATE-----
EOF
Successswitch# security pki certificate rotation commit 2ad7771e8cbc11ebbba37483ef8d9c4b
Successswitch# security pki certificate rotation commit ssl profile profile01
Enter TEXT private key. Type 'EOF' on its own line to end.
-----BEGIN PRIVATE KEY-----
MIIEvAIBADANBgkqhkiG9w0BAQEFAASCBKYwggSiAgEAAoIBAQCti4aj50Nzs9T4
NTwebaDcgjQetCHQg1FV2XMJsgoEuon8AWIJsP5gqt4jhZ3BIpWgjSJGhSoln2+7
ON40HfbZgG550MN8VDvIw8HrrPsgrpjDYyy0AKW0zmQxOMw6J5m1oepLMIfKiG2r
Ys/cEe5eStWz225kMepztvC63CwrhUmVq8OEdp6a0MXaKOXgKLTLBg0HYdr5+5OM
g9AkBlQqrlcyiPolYFu8iH4mfXMFnRUwJU5pK6kLKvnnWZr57jXDmmZttkeUm2j8
vaLL/NqGZPIjF/qA2HXWNsDEMy3ewclpQIeG8wicTTDyM/Ia8VPOLqdCOLK14sQ1
V3S9XdibAgMBAAECggEAEdDMLSD4HTVzDFoBW8mlpQ10G/TNBd1Sk7gY0FV9JCLM
OIPMfzHdeKoB15lcv691DIArP8cQM8A21ab5tKr2JOTuMnDaffXIagyikzb0/tQT
1qhaFeHaHCTFP4yBQKBgQDczahFFYJRP0joT4HuiywlkhbyOHV7b9xuPPhqwQxFY
qHvEE0qBnmjBzXujbpdb+V18QFGyl0uH4mHr+ltizcyAbEx5YL/y5Vu08bITZr0m
UxS0ZkDXg6n6GKJVIPUH05xSZb/eqtSFIq/DsBQYSwu6WzOj4dNpEQAeD8jMmGAl
wKBgQDJNWTNyC2JgDYmF039gwNEOY+UuJQ3v/JoEi2IHG4ISxVlZc9lZgLuWHDyS
6zNOIeSAYIzDVSsRAGH9sWaK4E4Yno4KHptRC5FMEbtnrojTO2ANC9JcWo2EgP31
r1OJolFpKUiPhOEAzdEYd/sdp9tWEusszTrn8fbPHvSHUFknQKBgDe8VhByOH4Hy
oCRqUusp80oDlDAPa+V8f+FtnNEHbPaDORKqh/EmKm1ZUC9V+DEIRjfaCIVbOX6o
f21Quga7yjZUoA03hdxrVvXa2Mea9H4bFKvg79c27g4qb7erZQ6/tML72i370z90
HQf5h2kGcIRvBx8EHxhzaSMtetNiV0rAoGAP3QzQiJrGf3xFborwlNa6F0uxrwfI
iXKkL+K1G4C1WK4cK3W5idxrTD/DaqH6IB3YLhRE0CU/27C/Nn6H1CxA9MqsCMz2
NmzreY3uCBim1dbXx8V+pdl439y+Ooj8U195RSzb0UcanmJKGulbrFKPfWmh+RMQ
DK3mJBOjEjlopECgYAr6F+60TZ7ZAvA0vZ9PlrntzvY7GhopJgJfAvfi5nBXPS+f
kdKtWzOmhW1jon1ka0fEeRQnQjB7DSYB4zldufPKiD+EXgJtQbhSqfdtgL7QlhVr
pO/s5tUrPE/KRu/yLGtEWruQlDCawpMPA63eP4XER/MHVXBkqbWy85vx46SisOBA
nuEum0yMngru5fARoBKO1aV7G94FI7Eu5rDqeVYsE5jrdnWJTZTgpHf9RYUOlz8R
wwbD/xUs+cKbM1qhaFeHaHCTFP4yBQKBgQDczahFFYJRP0joT4HuiywlkhbyOHV7
b9xuPPhqwQxFYqHvEE0qBnmjBzXujbpdb+V18QFGyl0uH4mHr+ltizcyAbEx5YL/
y5Vu08bITZr0mUxS0ZkDXg6n6GKJVIPUH05xSZb/eqtSFIq/DsBQYSwu6WzOj4dN
pEQAeD8jMmGAlwKBgQDJNWTNyC2JgDYmF039gwNEOY+UuJQ3v/JoEi2IHG4ISxVl
Zc9lZgLuWHDyS6zNOIeSAYIzDVSsRAGH9sWaK4E4Yno4KHptRC5FMEbtnrojTO2A
NC9JcWo2EgP31r1OJolFpKUiPhOEAzdEYd/sdp9tWEusszTrn8fbPHvSHUFknQKB
gDe8VhByOH4HyoCRqUusp80oDlDAPa+V8f+FtnNEHbPaDORKqh/EmKm1ZUC9V+DE
IRjfaCIVbOX6of21Quga7yjZUoA03hdxrVvXa2Mea9H4bFKvg79c27g4qb7erZQ6
/tML72i370z90HQf5h2kGcIRvBx8EHxhzaSMtetNiV0rAoGAP3QzQiJrGf3xFbor
wlNa6F0uxrwfIiXKkL+K1G4C1WK4cK3W5idxrTD/DaqH6IB3YLhRE0CU/27C/Nn6
H1CxA9MqsCMz2NmzreY3uCBim1dbXx8V+pdl439y+Ooj8U195RSzb0UcanmJKGul
brFKPfWmh+RMQDK3mJBOjEjlopECgYAr6F+60TZ7ZAvA0vZ9PlrntzvY7GhopJgJ
fGr1GYQPJi38DJ5NR/w64js21t5X2yJ4xcCB3H7R0QWJ9EE+fc+7nBYFJlaDzSRB
bES24yGh4n4Vc6luYW9A+YJR3EaElE6RMWyzIY8J8kV2xuTaK9xepdM9x1J1kIm2
rA1mcO4Xqw==
-----END PRIVATE KEY-----
EOF
Enter TEXT certificate. Type 'EOF' on its own line to end.
-----BEGIN CERTIFICATE-----
MIICnTCCAYWgAwIBAgIJANzHst3ljdWfMA0GCSqGSIb3DQEBCwUAMA4xDDAKBgNV
BAMMA2ZvbzAeFw0yMTAzMjQxNjAyMDdaFw0yMjAzMjQxNjAyMDdaMA4xDDAKBgNV
BAMMA2ZvbzCCASIwDQYJKoZIhvcNAQEBBQADggEPADCCAQoCggEBAK2LhqPnQ3Oz
1Pg1PB5toNyCNB60IdCDUVXZcwmyCgS6ifwBYgmw/mCq3iOFncEilaCNIkaFKiWf
b7s43jQd9tmAbnnQw3xUO8jDweus+yCumMNjLLQApbTOZDE4zDonmbWh6kswh8qI
batiz9wR7l5K1bPbbmQx6nO28LrcLCuFSZWrw4R2nprQxdoo5eAotMsGDQdh2vn7
k4yD0CQGVCquVzKI+iVgW7yIfiZ9cwWdFTAlTmkrqQsq+edZmvnuNcOaZm22R5Sb
aPy9osv82oZk8iMX+oDYddY2wMQzLd7ByWlAh4bzCJxNMPIz8hrxU84up0I4srXi
xDVXdL1d2JsCAwEAATANBgkqhkiG9w0BAQsFAAOCAQEADkjfobxF7BAVFdIjyWHL
ID+9D1t96JvCe+PDUyggow6iZE8ROq2fIFHuXhXMrd/neN3WtxqtjvGBnS49t4fa
qIcjerkIPwLaBSwWdpm/1FrIFejYqU0symRE3bKJULLBEdQhyox37D2uqPm71ado
5rXCX9pSu2oNOThd/877QKxtrKa5pekx1acxEa4E0QJ0/YPwkA5nCzM9jy7DZlH2
+cdtCxREeqlhOJUJxQ2354LyykU2fOXe6AGGdVE9hdIOJDnG26VVb+gFt2qaKD5+
3D3/Gd1pm4P3+9aENlhAcr0PUoL3xUApeIdkEf7n8KHiNP+gmlPyVDTCAudwHnwq
Vg==
-----END CERTIFICATE-----
EOF
SuccessAfter rotating the certificate and key pair, use the show management security ssl certificate cert.pem and the show management security ssl key key.pem commands to display the new contents.
The Diffie-Hellman parameters file facilitates the exchange of symmetric keys during SSL negotiations. When the system boots, it auto-generates a Diffie-Hellman parameters file if one does not exist. Use the reset command to reset the auto-generated Diffie-Hellman parameters file. The individual features that use SSL profile configuration decides if they also use the Diffie-Hellman parameters file. The switch uses 2048-bit Diffie-Hellman parameters with no options to select the size.
Example
switch# reset ssl diffie-hellman parametersThe show management security ssl diffie-hellman command displays the Diffie-Hellman parameters.
Example
switch# show management security ssl diffie-hellman
Last successful reset on Apr 10 16:18:08 2015
Diffie-Hellman Parameters 1024 bits
Generator: 2
Prime: dc47b5edc0d2b41451432f79f45efab452bba7b1ab118c194d671d6752ed1c550
664ed8f052ad0fdad623c1d54ae5aee5e728d2bd7a6221636b787a4c08d1fef8c
6dcd10759d38f8b70b47d1c7972d69b0b295a2ee6ab44cfc7352cb133e85197c8
9f1fc27aac7e8e02afb4fb01ca1cb05558a7bef505b73a8d06cdfe403576bDuring a TLS handshake, both peers send each other a list of the TLS versions they support to agree on and use the highest common version. The following allowable versions can be configured in an SSL profile using the tls versions command. By default, TLSv1, TLSv1.1, and TLSv1.2 are enabled.
switch# config
switch#(config)# management security
switch(config-mgmt-security)# ssl profile client
switch(config-mgmt-sec-ssl-profile-client)#
switch(config-mgmt-sec-ssl-profile-client)# tls versions 1.2switch(config-mgmt-sec-ssl-profile-client)# tls versions add 1.1
switch(config-mgmt-sec-ssl-profile-client)# tls versions 1.1 1.2The TLS handshake establishes a secure communication channel by negotiating the cipher suite and the TLS version. The client initiates this process by providing the server a list of supported cipher suites. Based on the client's list and capabilities, the server selects a mutually supported cipher suite. This selection ensures both parties utilize the same cryptographic algorithms for secure data exchange.
The default cipher-list setting employs an OpenSSL cipher string (HIGH:!eNULL:!aNULL:!MD5). This configuration permits only key lengths longer than 128 bits and excludes cipher suites using MD5.
To view the complete list of cipher suites included in this setting, execute the following shell command: openssl ciphers HIGH:!eNULL:!aNULL:!MD5.
Example
switch(config-mgmt-sec-ssl-profile-client)# cipher-list AESGCM
switch(config-mgmt-sec-ssl-profile-client)# cipher-list SHA256:SHA384
switch(config-mgmt-sec-ssl-profile-client)# cipher-list ECDHE-ECDSA-AES256-GCM-SHA384Use TLSv1.3 Key Establishment Groups to ensure cryptographic security and Perfect Forward Secrecy (PFS) during the TLS handshake. Key Establishment Groups provide specific mathematical structures to perform the Diffie-Hellman key exchange which creates a shared secret key between the client and the server.
ClientHello message, the client lists
the supported name groupsand sends the public key share for the preferred
group in the key_share extension.switch(config)# management security
switch(config-mgmt-security)# ssl profile mytls_key
switch(config-mgmt-sec-ssl-profile-mytls_key)# tls versions 1.3
switch(config-mgmt-sec-ssl-profile-mytls_key)#switch(config-mgmt-sec-ssl-profile-mytls_key)# key-establishment-group X25519MLKEM768:ecdh_x25519:secp256r1X25519MLKEM768, a PQC-classical hybrid
mechanism, as the most preferred key, and then two classical ECC groups as the next
preferred keys. Separate the keys using colons. By default, the SSL profile uses the
following list of Key Establishment
Groups:ecdh_x25519:secp256r1:ecdh_x448:secp521r1:secp384r1:ffdhe2048:ffdhe3072:ffdhe4096:ffdhe6144:ffdhe8192switch# show management security ssl profile mytls_key key-establishment-group
Profile: server
- X25519MLKEM768
- ecdh_x25519
- secp256r1Federal Information Processing Standards (FIPS) is a cryptographic standard that restricts the cryptographic functions and protocol versions used by OpenSSL.
Example
switch(config-mgmt-sec-ssl-profile-client)# fips restrictionsCollecting syslog information on a remote syslog server requires defining an SSL profile. This profile ensures the secure transmission of syslog data to the server over a TLS connection.
switch(config)# logging host test.example.com 1234 protocol tls ssl-profile test-profileswitch(config-mgmt-security)# ssl profile test-profile
switch(config-mgmt-sec-ssl-profile-test-profile)# certificate clientCert key clientKey
switch(config-mgmt-sec-ssl-profile-test-profile)# trust certificate serverCAThe dir command displays the directory output of certificate file systems.
Example
switch# dir certificate:
Directory of certificate:/
-rw- 3319 Apr 10 11:50 server.crt
No space information availableThe show management security ssl certificate command displays the certificate information. To display a specific certificate, specify the certificate name. Omitting a name displays all available certificates.
Example
switch# show management security ssl certificate server.crt
Certificate server.crt:
Version: 1
Serial Number: 9
Issuer:
Common name: ca
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: Foo Org
Organization: Foo
Locality: SC
State: CA
Country: US
Validity:
Not before: Aug 11 21:44:17 2014 GMT
Not After: May 14 21:44:17 2069 GMT
Subject:
Common name: server
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: Foo Org
Organization: Foo
Locality: SC
State: CA
Country: US
Subject public key info:
Encryption Algorithm: RSA
Size: 2048 bits
Public exponent: 65537
Modulus: e04e3ff8e1c64dbcb141fe96133f998e90a322c671b9f28307bf873
2239f69804a77fbb8f146841eb6253b7bb50bf6c66bbf3097ec695b
0d7985cfdd939c9913b4ba4f6cb8655b208ed0254a269ecab574987
ea5ee80085f5216d303cf704372b2fa1aae62756c3762441fcc1c04
635a831d5ec96d841The show management security ssl crl command displays the installed Certificate Revocation List (CRL) information. To view a specific CRL, use its name. Omitting a name displays all the CRLs.
Example
switch# show management security ssl crl intermediate.crl
CRL intermediate.crl:
CRL Number: 11
Issuer:
Common name: intermediate
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: Foo Org
Organization: Foo
State: CA
Country: US
Validity:
Last Update: Jul 19 19:27:34 2016 GMT
Next Update: Dec 05 19:27:34 2043 GMTThe dir command displays the directory output of SSL key file systems.
Example
switch# dir sslkey:
Directory of sslkey:/
-rw- 1675 Apr 10 12:55 server.key
No space information availableThe show management security ssl key command displays the RSA key information. To view a specific RSA key, use the name of the key; otherwise, all the keys are displayed. For security reasons, only the public part of the key is displayed.
Example
switch# show management security ssl key server.key
Key server.key:
Encryption Algorithm: RSA
Size: 2048 bits
Public exponent: 65537
Modulus: e04e3ff8e1c64dbcb141fe96133f998e90a322c671b9f28307bf873
2239f69804a77fbb8f146841eb6253b7bb50bf6c66bbf3097ec695b
0d7985cfdd939c9913b4ba4f6cb8655b208ed0254a269ecab574987
b502f8c3f541fa3bae59743cced6e6ca04f6ca6c9268744add79c3a
f8178d12dd744ddf5db100b33c46b40e53f0a1c7d49f83488976c5dThe copy file: certificate: command copies the certificate to the certificate: file system. The certificate can be copied from any supported source URL of the copy command.
Command Mode
Global Configuration
Command Syntax
copy file: file_name certificate:
Parameter
file_name location or the path of the file or the directory to save the certificate.
Guidelines
switch(config)# copy file:tmp/ssl/mixed.crt certificate:
% Error copying file:tmp/ssl/mixed.crt to certificate: (Multiple types of entities in certificate file not supported)
switch(config)#switch(config)# copy file:tmp/ssl/bad.crt certificate:
% Error copying file:tmp/ssl/bad.crt to certificate: (Invalid certificate)
switch(config)#switch(config)# copy file:tmp/ssl/dsa.crt certificate:
% Error copying file:tmp/ssl/dsa.crt to certificate: (Certificate does not have RSA key)
switch(config)#switch(config)# copy file:/tmp/ssl/server.crt certificate:
Copy completed successfully.The copy file: sslkey: command copies the SSL key to the sslkey: file system. The key can be copied from any supported source URL of the copy command.
Command Mode
Global Configuration
Command Syntax
copy file: file_name sslkey:
Parameter
file_name location or the path of the file or the directory to save the key.Guidelines
switch# copy file:tmp/ssl/multi.key sslkey:
% Error copying file:tmp/ssl/multi.key to sslkey: (Multiple PEM entities in single file not supported)switch# copy file:tmp/ssl/bad.key sslkey:
% Error copying file:tmp/ssl/bad.key to sslkey: (Invalid RSA key)switch# copy file:/tmp/ssl/pass.key sslkey:
% Error copying file:tmp/ssl/pass.key to sslkey: (Password protected keys are not supported)Example
switch(config)# copy file:/tmp/ssl/server.key sslkey:
Copy completed successfully.
switch(config)#The delete certificate: command deletes a specified certificate from the certificate: file system on the switch.
Command Mode
Global Configuration
Command Syntax
delete certificate: certificate_name
Parameter
certificate_name name of the certificate to delete.
Example
switch(config)# delete certificate:server.crtThe delete sslkey: command deletes a SSL key from the sslkey: file system on a switch.
Command Mode
Global Configuration
Command Syntax
delete sslkey: key_name
Parameter
key_name name of the key.
Example
switch(config)# delete sslkey:server.keyThe dir certificate: command displays the directory output of the certificate: file system on the switch.
Command Mode
Global Configuration
Command Syntax
dir certificate:
Example
switch(config)# dir certificate:
Directory of certificate:/
-rw- 3319 Apr 10 11:50 server.crt
No space information availableThe dir sslkey: command displays the directory output of sslkey: file system on the switch.
Command Mode
Global Configuration
Command Syntax
dir sslkey:
Example
switch(config)# dir sslkey:
Directory of sslkey:/
-rw- 1675 Apr 10 12:55 server.key
No space information availableThe reset ssl diffie-hellman parameters command resets the Diffie-Hellman parameters file after a system reboot.
Command Mode
Global Configuration
Command Syntax
reset ssl diffie-hellman parameters
Example
switch(config)# reset ssl diffie-hellman parameters
switch(config)#The security pki certificate generate command generates a self-signed certificate or a Certificate Signing Request (CSR) certificate. The CLI displays the generated CSR, and a self-signed certificate saves to the certificate: file system.
Many other parameters can be entered and applied to the certificate as shown in the following examples.
Command Mode
Global Configuration
Command Syntax
security pki certificate generate {self-signed |signing-request} certificate_name Key key_name
switch(config)# security pki certificate generate self-signed test.crt key test.keyswitch(config)# security pki certificate generate signing-request key test.key digest sha256 validity 365 switch(config)# security pki certificate generate signing-request key test.key parameters common-name Test [country US ...] The security pki key generate command generates a RSA key used to validate a specific certificate.
The key generated can be modified and saved by entering the value of the length in the generate rsa length parameter.
Command Mode
Global Configuration
Command Syntax
security pki key generate [rsa [2048 | 3072 | 4096] key_name
switch(config)# security pki key generate rsa 2048 test.keyswitch(config)# security pki certificate generate self-signed test.crt key
test.key generate rsa 4096
switch(config)# security pki certificate generate signing-request key test.key
generate rsa 2048The show management security ssl certificate command displays information about the certificate. Provide the name of the certificate to view more information about the certificate. If you do not provide a name, this command displays information about all of the certificates.
Command Mode
EXEC
Command Syntax
show management security ssl certificate [certificate_name]
Parameter
certificate_name - The name of the certificate (optional).
Example
switch# show management security ssl certificate server.crt
Certificate server.crt:
Version: 1
Serial Number: 9
Issuer:
Common name: ca
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: Myorg Org
Organization: Myorg
Locality: SC
State: CA
Country: US
Validity:
Not before: Aug 11 21:44:17 2014 GMT
Not After: May 14 21:44:17 2069 GMT
Subject:
Common name: server
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: Org Org
Organization: ORg
Locality: SC
State: CA
Country: US
Subject public key info:
Encryption Algorithm: RSA
Size: 2048 bits
Public exponent: 65537
Modulus: e04e3ff8e1c64dbcb141fe96133f998e90a322c671b9f28307bf873
2239f69804a77fbb8f146841eb6253b7bb50bf6c66bbf3097ec695b
0d7985cfdd939c9913b4ba4f6cb8655b208ed0254a269ecab574987
9f54c8c7f0b3a57a7ab826870119083222ad5ee76d40f3fae49d36e
b502f8c3f541fa3bae59743cced6e6ca04f6ca6c9268744add79c3a
c08af6b451455b4a61071f4c0b3ec3553585312783e9381f65bb0e2
ea5ee80085f5216d303cf704372b2fa1aae62756c3762441fcc1c04
97ee6190586ed28c0e376f48e53f05a40c7e1f3a65e3c6165bae5df
f8178d12dd744ddf5db100b33c46b40e53f0a1c7d49f83488976c5d
635a831d5ec96d841The show management security ssl crl command displays the basic information about the installed Certificate Revocation List (CRLs). To view information of a specific CRL provide the name of the CRL. If you do not provide a name, this command displaysinformation about all of the CRLs.
Command Mode
EXEC
Command Syntax
show management security ssl crl
Example
switch# show management security ssl crl intermediate.crl
CRL intermediate.crl:
CRL Number: 11
Issuer:
Common name: intermediate
Email address: This email address is being protected from spambots. You need JavaScript enabled to view it.
Organizational unit: mycompany Org
Organization: mycompany
State: CA
Country: US
Validity:
Last Update: Jul 19 19:27:34 2016 GMT
Next Update: Dec 05 19:27:34 2043 GMTThe show management security ssl diffie-hellman command displays the Diffie-Hellman parameter information.
Command Mode
EXEC
Command Syntax
show management security ssl diffie-hellman
Example
switch# show management security ssl diffie-hellman
Last successful reset on Apr 10 16:18:08 2015
Diffie-Hellman Parameters 1024 bits
Generator: 2
Prime: dc47b5edc0d2b41451432f79f45efab452bba7b1ab118c194d671d6752ed1c550
664ed8f052ad0fdad623c1d54ae5aee5e728d2bd7a6221636b787a4c08d1fef8c
6dcd10759d38f8b70b47d1c7972d69b0b295a2ee6ab44cfc7352cb133e85197c8
9f1fc27aac7e8e02afb4fb01ca1cb05558a7bef505b73a8d06cdfe403576bThe show management security ssl key command displays the RSA key information. To view information of a specific key, provide the name of the key in the command. If you do not provide a name, this command displays information about all of the keys.
Command Mode
EXEC
Command Syntax
show management security ssl key [key_name]
Parameter
key_name name of the key (optional).
Example
switch# show management security ssl key server.key
Key server.key:
Encryption Algorithm: RSA
Size: 2048 bits
Public exponent: 65537
Modulus: e04e3ff8e1c64dbcb141fe96133f998e90a322c671b9f28307bf873
2239f69804a77fbb8f146841eb6253b7bb50bf6c66bbf3097ec695b
0d7985cfdd939c9913b4ba4f6cb8655b208ed0254a269ecab574987
9f54c8c7f0b3a57a7ab826870119083222ad5ee76d40f3fae49d36e
b502f8c3f541fa3bae59743cced6e6ca04f6ca6c9268744add79c3a
c08af6b451455b4a61071f4c0b3ec3553585312783e9381f65bb0e2
ea5ee80085f5216d303cf704372b2fa1aae62756c3762441fcc1c04
97ee6190586ed28c0e376f48e53f05a40c7e1f3a65e3c6165bae5df
f8178d12dd744ddf5db100b33c46b40e53f0a1c7d49f83488976c5d
635a831d5ec96d841The show management security ssl profile command displays the SSL profile status information. To display information about a specific SSL profile, provide the name of the profile. If you do not provide a name, this command displays profile status of all the SSL profiles.
If the SSL profile contains errors, the state displays as invalid and lists the errors are listed in the third column.
Command Mode
EXEC
Command Syntax
show management security ssl profile [profile_name]
Parameter
profile_name - Name of the SSL profile (optional).
switch# show management security ssl profile server
Profile State
------------- -----------
server validswitch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'server.crt' does not match
with keyswitch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'ca2.crt' does not existswitch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'mycert.crt' is trusted and not
a root certificateswitch# show management security ssl profile server
Profile State Error
------------- ------------- ----------------------------------------
server invalid Certificate 'server.crt' has expiredswitch# show management security ssl profile server
Profile State Error
-------------- ------------- ---------------------------------------------
server invalid Profile has invalid certificate chain
Certificate 'intermediate.crt' does not existThe ssl profile command places the switch in the SSL profile configuration mode. Various SSL profile management configurations are allowed in this mode. For example, this mode allows to configure a SSL profile with a certificate and its corresponding RSA key.
Similarly, other configurations such as trust certificate, chain certificate, crl, tls, cipher-list can be configured to a SSL profile in this mode.
The no form of the command deletes the SSL profile management configuration from running-config.
Command Mode
Management Security Mode
SSL Profile Mode
Command Syntax
ssl profile profile_name
Parameter
profile_name name of the profile.
switch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)#switch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# certificate server.crt key server.key
switch(config-mgmt-sec-ssl-profile-server)# no certificate server.crt key server.keyswitch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# trust certificate ca1.crt
switch(config-mgmt-sec-ssl-profile-server)# no trust certificate ca1.crtswitch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# certificate server.crt key server.key
switch(config-mgmt-sec-ssl-profile-server)# chain certificate intermediate.crt
switch(config-mgmt-sec-ssl-profile-server)# no chain certificate intermediate.crtswitch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# crl intermediate.crl
switch(config-mgmt-sec-ssl-profile-server)# crl ca.crl
switch(config-mgmt-sec-ssl-profile-server)# no crl ca.crlswitch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# tls versions 1.2switch# config
switch(config)# management security
switch(config-mgmt-security)# ssl profile server
switch(config-mgmt-sec-ssl-profile-server)# cipher-list AESGCM
switch(config-mgmt-sec-ssl-profile-server)# cipher-list SHA256:SHA38
switch(config-mgmt-sec-ssl-profile-server)# cipher-list ECDHE-ECDSA-AES256-GCM-SHA384switch(config-mgmt-sec-ssl-profile-client)# certificate requirement extended-key-usageswitch(config-mgmt-sec-ssl-profile-client)# trust certificate requirement basic-constraints ca true
switch(config-mgmt-sec-ssl-profile-client)# chain certificate requirement basic-constraints ca trueswitch(config-mgmt-sec-ssl-profile-client)# fips restrictions802.1X is an IEEE standard protocol that prevents unauthorized devices from accessing the network.
Before authentication can succeed, the switch port is in unauthorized mode and blocks all traffic, but after authentication has succeeded, normal data can flow through the switch port.
Port security controls who can send or receive traffic from an individual switch port. An end node cannot send or receive traffic through a port until a RADIUS server authenticates the node.
This security prevents unauthorized individuals from connecting to a switch port to access the network. Only designated valid users on a RADIUS server can use the switch to access the network.
The Single Host and the Multi-Host modes allow only one 802.1X supplicant to authenticate for one port. After successfully authenticating, no other 802.1X supplicant can authenticate unless the current one logs off. However, the Multi-Host Authenticated Mode allows multiple 802.1X supplicants to authenticate and provide access to the network.
In addition to 802.1X authentication, EOS supports MAC-Based Authentication (MBA) and allows devices without 802.1X to access the network. The authenticator uses the MAC address of such devices as username/password in its RADIUS request packets. Depending on the MAC-Based Authentication configuration on the RADIUS server, the server permits or denies authentication to the supplicant. Unlike 802.1X supplicants, a single port allows multiple MBA supplicants. The MBA configuration does not require the 802.1X host modes. MBA supplicants permit or reject unauthenticated traffic based on the host mode.
EOS also supports Dynamic VLAN assignment, which permits the RADIUS server to assign the desired VLAN for the supplicant, using the tunnel attributes with the Access-Accept message. The RADIUS server assigns VLANs to the 802.1X and MBA supplicants. EOS supports only one VLAN per port. When the first host authenticates, the authenticator port assigns the respective VLAN through dynamic VLAN assignment, and subsequently, all other hosts must belong to that VLAN as well.
802.1X features support 802.1Q trunk ports that permit the user to use Port-Based Network Access Control (PNAC) on a port. With this feature, traffic arriving at an 802.1X-enabled port with a VLAN tag authenticates the 802.1X and MBA supplicants.
By default, traffic from any unauthenticated device on an 802.1X-enabled port drops. However, by configuring the Authentication Failure VLAN on the authenticator switch, the 802.1X or MBA supplicant traffic can be put into a specific VLAN, if the supplicant fails to authenticate via the RADIUS server.
The 802.1X standard specifies the roles of Supplicant (client), Authenticator, and Authentication Server in a network. Switch Roles for 802.1X Configurations illustrates these roles.
Authentication Server- The switch that validates the client and specifies if the client may access services on the switch. The switch supports Authentication Servers running RADIUS.
Authenticator - The switch that controls access to the network. In an 802.1X configuration, the switch serves as the Authenticator. As the Authenticator, it moves messages between the client and the Authentication Server. The Authenticator either grants or does not grant network access to the client based on the identity data provided by the client, and the authentication data provided by the Authentication Server.
Supplicant/Client - The client provides a username or password data to the Authenticator. The Authenticator sends this data to the Authentication Server. Based on the supplicants information, the Authentication Server determines whether the supplicant can use services given by the Authenticator. The Authentication Server sends this data to the Authenticator, which then provides services to the client, based on the authentication result.
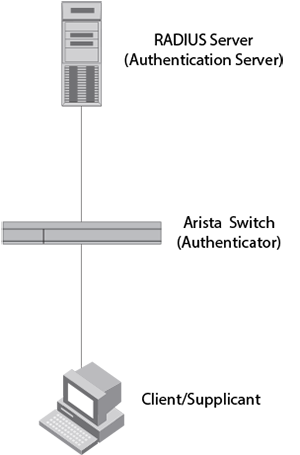
802.1X port security uses the Extensible Authentication Protocol (EAP), defined in RFC 2284 and the RADIUS authentication protocol For communication between the switches.
The 802.1X standard defines a method for encapsulating and sendingEAP messages over a LAN. This type of encapsulated EAP is known as EAP over LAN (EAPOL). The standard also specifies a method for transferring the EAPOL information between the client or Supplicant, Authenticator, and Authentication Server.
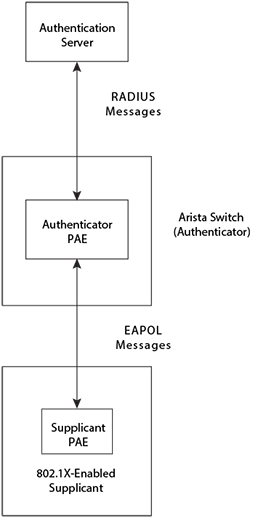
Authenticator PAE - The Authenticator PAE communicates with the Supplicant PAE to receive the Supplicants identifying information. Behaving as a RADIUS client, the Authenticator PAE passes the Supplicants information to the Authentication Server, which decides whether to grant the Supplicant access. If the Supplicant passes authentication, the Authenticator PAE allows it access to the port.
Supplicant PAE - The Supplicant PAE provides information about the client to the Authenticator PAE and replies to requests from the Authenticator PAE. The Supplicant PAE may initiate the authentication procedure with the Authenticator PAE, as well as send logoff messages.
switch(config)# eapol mac destination rx physical
switch(config)#The Dot1x Dropped Counters count the packets dropped by dot1x interfaces. The dropped counter will not represent all the dropped packets in case of high volume dropping, and the CPU queue drop counter will reflect the rest of the dropped packet counter. This is due to the fact that EOS limits the bandwidth for the packets that get sent to the CPU.
switch(config)# dot1x system-auth-controlswitch(config-if-Et1)# switchport mode access
switch(config-if-Et1)# dot1x pae authenticator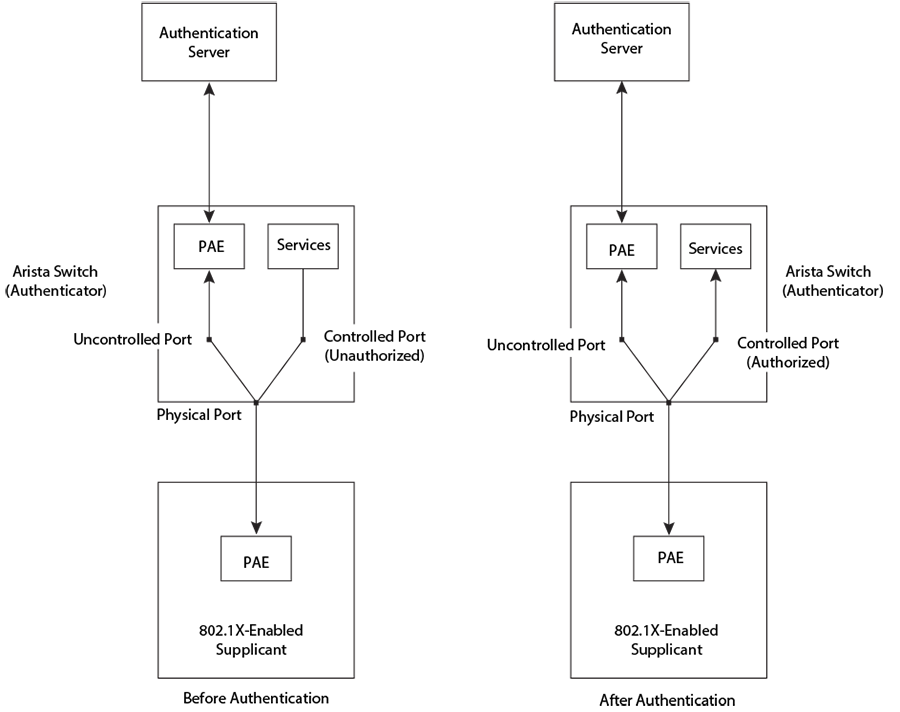
The Authenticator only opens one uncontrolled port before authenticating a client. The client and the Authentication Server swap EAPOL frames through the uncontrolled port. No other traffic passes through the controlled port in the unauthorized state.
During authentication, the Supplicant PAE and the Authenticator PAE exchange EAPOL messages, and the Authenticator PAE and the Authentication Server exchange RADIUS messages. If the client successfully authenticates, the controlled port authorizes, and traffic from the client flows through the port normally.
By default, all controlled ports on the switch authorize and allow all traffic. When initially authenticating, the controlled port on the interface initially sets to the unauthorized state. If a client connected to the port authenticates successfully, the controlled port sets to the authorized state.
The following figure illustrates an exchange of messages between an 802.1X-enabled client, an Authenticator switch, and a RADIUS server operating as an Authentication Server.
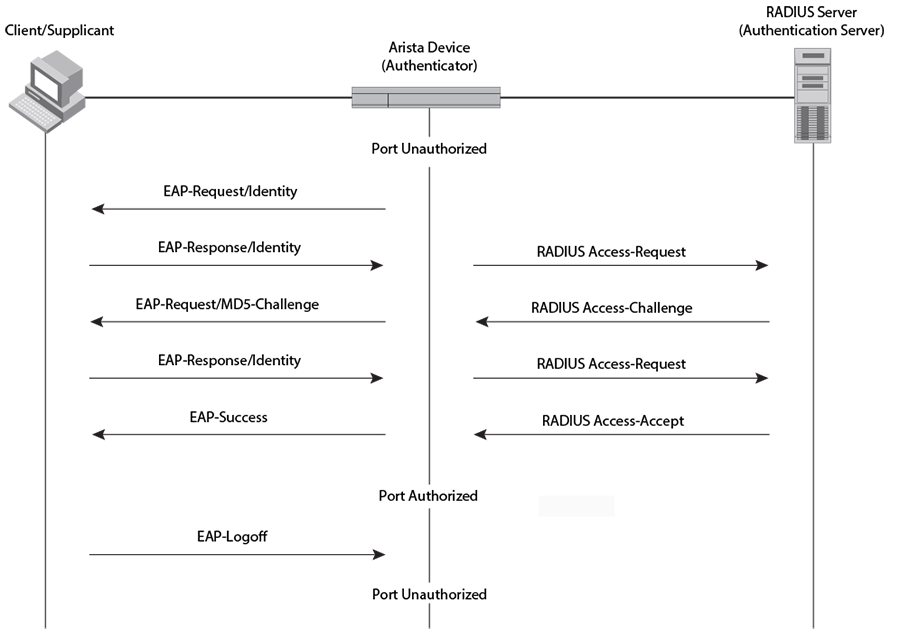
Arista switches support 802.1X authentication for ports with more than one client connected to them. Figure 7 - Multiple clients connected to a 802.1X-enabled port illustrates a sample configuration where multiple clients connect to a single 802.1X port. 802.1X authentication may use multi-host mode, or, on selected switches, single-host mode. In both modes, the port authenticates the packets received from any one client, and drops the packets received from other clients, until authentication of the connected client by the RADIUS server.
In single-host mode, the 802.1X client has authenticated on the RADIUS server and does not require further authentication. However, the port accepts packets only from the MAC address of the authenticated client.
In multi-host mode, once the 802.1X client authenticates with the RADIUS server, the port accepts all packets from any connected client, and these packets do not require any authentication.
Adding Round Robin Authentication enables sending authentication requests across all live servers within a RADIUS server group and selects a group based on Round Robin Authentication. The dead timer or server probe determines the liveliness or reachability of the RADIUS server group. Fallback to the next RADIUS server group only happens if none of the servers can be reached in the current RADIUS server group.
switch(config)# dot1x
switch(config-dot1x)# aaa authentication load-balance round-robin802.1X MAC-based authentication allows programming a set of MAC addresses into the RADIUS server. These MAC addresses (MAC-based authentication supplicants) do not connect to 802.1X profiles but are still allowed access to the network. The authenticator identifies devices that do not support 802.1X and uses the MAC address of these devices as username and password in its RADIUS request packets.
In MAC-based authentication, every supplicant attempting to access the authenticator port individually authenticates, as opposed to authenticating just one supplicant on a given VLAN or port with 802.1X. Different behavior occurs for MAC-based authentication supplicants when an 802.1X supplicant authenticates in single-host and multi-host 802.1X modes.
switch(config)#dot1x mac based authentication delay 60 secondsswitch(config-if-Et1/1)# show active
speed forced 1000full
dot1x pae authenticator
dot1x port-control auto
dot1x mac based authentication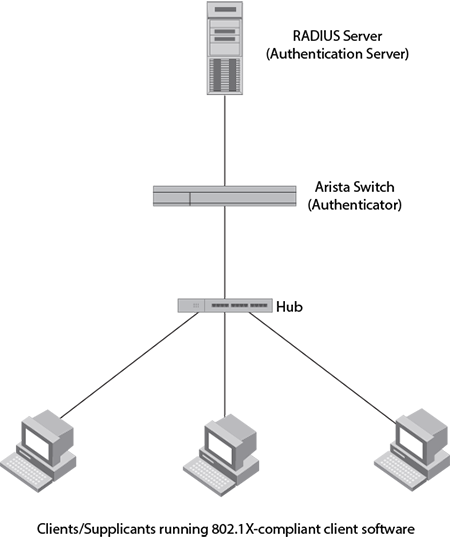
Use the mac based authentication delay command to configure a MAC-based Authentication delay. By default, the delay triggers after 5 seconds.
Command Syntax
mac based authentication delay 0-300 seconds
When an AAA server rejects a MAC-based Authentication, a default hold period of 60 seconds occurs before the MAC-based Authentication retries again even if the host continues to send traffic. However, the hold-period can be configured manually using the mac based authentication hold period command.
Command Syntax
mac based authentication hold period 0-300 seconds
When using dot1x captive portal authentication, supplicants receive the WEB-AUTH-START page to begin redirecting the HTTPS requests to a captive portal as a second step in the authentication process. The Dot1x Web Authentication Fully Qualified Domain Name (FQDN) Allowlist provides a list of FQDN masks that bypass the redirection and allows the supplicant to access URLs on these hosts before completing the second step of the authentication process.
The Dot1x Web Authentication captures the IP address that the supplicant attempts to access and performs a reverse DNS resolution to check if the FQDN matches an entry on the configured Allowlist.
Devices connected to 802.1X controlled ports must perform authentication before their generic traffic is allowed into the network. During this process, the switch contacts a configured AAA server that determines if the device’s access to the network is accepted or denied. When the AAA server is unresponsive, the default behavior is to deny all authentication attempts. The AAA Unresponsive VLAN feature allows the user to specify different behavior for this case, accepting authentication attempts and assigning devices to the native VLAN or a specified VLAN. As in other failure scenarios, the switch tries to authenticate the supplicant after the quiet period has passed.
Configure the aaa unresponsive action traffic allow vlan command to enable the dot1x AAA unresponsive VLAN feature on the switch. When configured, the switch changes the action taken with authentication attempts when the AAA server becomes unresponsive. Unresponsiveness occurs when the AAA communication times out.
Example
switch(config)# dot1x
switch(config-dot1x)# aaa unresponsive action traffic allow vlanThe 802.1X Web authentication feature provides authentication for a supplicant through a Web page, referred to as a captive portal. Redirection to a captive portal provides support for guest devices or supplicants where 802.1X is insufficient and requires an additional Web based authentication.
Use the following global command under the 802.1X node to enable the 802.1X Web authentication:
captive portal url URL][ssl profile profile]
Enabling the 802.1X Web authentication starts the redirection agent (Dot1xWeb) and the internal HTTP redirector. Then, 802.1X acts on the RADIUS web-auth-start VSAs. If specifying a URL, the URL redirects the authentication when AAA does not provide a specific URL. If providing a valid SSL profile, the 802.1X Web internal HTTPS redirector uses the configured certificate and key.
switch(config-dot1x)# captive portal access-list ipv4 test-ACL| AttributeName | Attribute ID | Type | Value |
|---|---|---|---|
| Arista-WebAuth | 6 | integer | start =
1 complete = 2 |
| Arista-Captive-Portal | 10 | string | any valid URL |
Show Commands
The show commands that display the state of a host includes the new values for WebAuth stage as well.
switch(config)# show dot1x hosts
Interface: Ethernet36
Supplicant MAC Auth Method State VLAN Id
-------------- ----------- ----- -------
00:1c:73:73:f9:38 MAC-BASED-AUTH WEB-AUTH-START
00:1c:73:73:f9:39 MAC-BASED-AUTH WEB-AUTH-FAILEDBasic steps to implementing 802.1X Port-based Network Access Control and RADIUS accounting on the switch:
Configure external client authentication methods for IEEE 802.1X port security. Arista currently supports RADIUS authentication. Use the aaa authentication dot1x command to configure the switch to use a RADIUS server for client authentication.
Example
switch(config)# aaa authentication dot1x default group radius
switch(config)#Use the statistics packets dropped command to configure the dot1x dropped counters on the switch in the dot1x configuration mode. By default, EOS turns off the dot1x dropped counters. The no form of the command disables them from the running configuration.
Example
switch(config-dot1x)# statistics packets droppedTo enable IEEE 802.1X port authentication globally on the switch, use the dot1x system-auth-control command.
Example
switch(config)# dot1x system-auth-control
switch(config)#To set the port access entity (PAE) type of an Ethernet or management interface to the authenticator, use the dot1x pae authenticator command.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x pae authenticator
switch(config-if-Et1)#Example
For ports to act as authenticator ports to connected supplicants, those ports must be designated using the dot1x port_control command.
The auto option of the dot1x port_control command designates an authenticator port for immediate use, blocking all traffic that is not authenticated by the AAA server.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x port-control auto
switch(config-if-Et1)#The force-authorized option of the dot1x port_control command sets the state of the port to authorized without authentication, allowing traffic to continue uninterrupted.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x port-controlforce-authorized
switch(config-if-Et1)#To designate a port as an authenticator but prevent it from authorizing any traffic, use the force-unauthorized option of the dot1x port_control command.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x port-control force-unauthorized
switch(config-if-Et1)#By default, Arista switches authenticate in multi-host mode, allowing packets from any source MAC address once 802.1X authentication has taken place. To configure the switch for single-host mode (allowing traffic only from the authenticated clients MAC address), use the dot1x host-mode command.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x host-mode single-host
switch(config-if-Et1)#The dot1x reauthentication command enables the authenticator ports to re-authenticate with the default values..
The dot1x timeout reauth-period command allows the customization of the re-authentication period of authenticator ports.
switch(config)# interface Ethernet 1
switch(config-if-Eth)# dot1x reauthenticationswitch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x reauthentication
switch(config-if-Et1)# dot1x timeout reauth-period 21600
switch(config-if-Et1)#switch(config)# interface Ethernet 1
switch(config-if-Et1)# no dot1x reauthentication
switch(config-if-Et1)#The dot1x reauthorization request limit command configures the number of times the switch retransmits an 802.1X Extensible Authentication Protocol (EAP) request packet before ending the conversation and restarting authentication.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x reauthorization request limit 4
switch(config-if-Et1)#The default value is 2.
To disable authentication on an authenticator port, use the no form of the dot1x port-control command.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# no dot1x port-control
switch(config-if-Et1)#If the switch fails to immediately authenticate the client, the dot1x timeout quiet-period command specifies the time the switch waits before trying again. This timer also indicates how long a client that failed authentication is blocked.
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x timeout quiet-period 30The default value is 60 seconds.
The dot1x timeout reauth-period command specifies the time period in seconds that the configuration mode interface waits before requiring re-authentication from clients.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x reauthentication
switch(config-if-Et1)# dot1x timeout reauth-period 21600The default value is 3600 seconds.
The authenticator sends an Extensible Authentication Protocol (EAP) request to the supplicant, and the supplicant sends a response that the authenticator forwards to an authentication server. If the authenticator doesn't receive a reply to the EAP request, it waits a specified time before retransmitting the request. To configure the wait time, use the dot1x timeout tx-period command.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x timeout tx-period 30
switch(config-if-Et1)#The default value is 5 seconds.
switch(config-if-Et1/1)# dot1x authentication failure action traffic allow vlan 10When configuring a VLAN with no authentication failure VLAN on a dot1x-enabled port, the default action drops any unauthorized traffic on the port. This behavior can also be specified using the following command:
switch(config-if-Et1/1)# dot1x authentication failure action traffic drop802.1X provides a guest VLAN that allows access to hosts unable to communicate over EAPoL and then perform actions to become EAPoL capable. Then, the host can move out of the guest VLAN. A typical use case includes situations where hosts perform PXE booting and become capable of responding to EAPoL requests.
Example
switch(config)# interface Ethernet6/1
switch(config-if-Et6/1)# dot1x
switch(config-dot1x)# eapol unresponsive action traffic allow vlan 25switch(config-dot1x)# eapol unresponsive action traffic disable The clear dot1x statistics command resets the 802.1X counters.
switch# clear dot1x statistics all
switch#switch# clear dot1x statistics interface ethernet 1
switch#switch(config)# dot1x
switch(config-dot1x)# captive-portal bypass fqdn_wildcardRepeat the configuration statement to add more FQDNs to the list. The wildcard * can be used once at the start of the FQDN and must be followed by a dot, for example *.myfqdn.com.
Example
switch(config)#dot1x
switch(config-dot1x)#captive-portal bypass *.mycompany.comswitch# clear dot1x captive portal resolutionsswitch# show captive-portal bypass
Captive portal bypass:
*.eng.mycompany.com matched by 10.0.1.3, 1.0.2.4
web5.it.mycompany.com matched by 10.0.5.7switch# show dot1x captive-portal resolutions
Address Hostnames Expiration
--------------- ------------------------- -------------------
1.0.2.4 www1.eng.mycompany.com 2033-05-17 20:33:20
10.0.5.7 web4.it.mycompany.com 2033-05-17 20:33:23
web5.it.mycompany.com
10.10.1.3 - 2033-05-17 20:33:26
10.20.1.3 (pending)
80.0.6.3 www1.eng.mycompany.com 2033-05-17 20:33:21You can display information about 802.1X on the switch and on individual ports.
Use the show dot1x statistics command to display 802.1X statistics for the specified port or ports.
switch# show dot1x interface ethernet 5 statistics
Dot1X Authenticator Port Statistics for Ethernet5
-------------------------------------------------
RxStart = 0 RxLogoff = 0 RxRespId = 0
RxResp = 0 RxInvalid = 0 RxTotal = 0
TxReqId = 0 TxReq = 0 TxTotal = 0
RxVersion = 0 LastRxSrcMAC = 0000.0000.0000
switch#switch# show dot1x all statistics
Dot1X Authenticator Port Statistics for Ethernet51/1
-------------------------------------------------
RX start = 1 RX logoff = 0 RX response ID = 1
RX response = 10 RX invalid = 0 RX total = 12
TX request ID = 2 TX request = 11 TX total = 13
RX version = 2 Last RX src MAC = ded6.404b.ec94
Data packet drop counters:
EAPOL unauthorized port = 2
EAPOL unauthorized host = 1
MBA unauthorized host = 0
Dot1X Authenticator Port Statistics for Ethernet49
-------------------------------------------------
RX start = 1 RX logoff = 0 RX response ID = 1
RX response = 10 RX invalid = 0 RX total = 12
TX request ID = 2 TX request = 11 TX total = 13
RX version = 2 Last RX src MAC = ded6.404b.ec94
Data packet drop counters:
EAPOL unauthorized port = 2
EAPOL unauthorized host = 1
MBA unauthorized host = 0Use the show dot1x hosts command to display information for all the supplicants.
Example
switch# show dot1x hosts
Interface: Ethernet1/1
Supplicant MAC Auth Method State VLAN Id
-------------- ----------- ----- -------
e2:29:cb:11:2f:4a EAPOL SUCCESS 300
e2:29:cb:11:2f:4b MAC-BASED-AUTH SUCCESS 300Use the show mac address-table command to display the MAC address of the supplicants allowed to pass the traffic through the port.
switch# show mac address-table
Mac Address Table
------------------------------------------------------------------
Vlan Mac Address Type Ports Moves Last Move
---- ----------- ---- ----- ----- ---------
300 e229.cb11.2f4a STATIC Et1/1
300 e229.cb11.2f4b STATIC Et1/1
Total Mac Addresses for this criterion: 2The show dot1x command shows information about the 802.1X configuration on the specified port or ports.
Example
switch# show dot1x interface ethernet 5
Dot1X Information for Ethernet5
--------------------------------------------
PortControl : auto
QuietPeriod : 60 seconds
TxPeriod : 5 seconds
ReauthPeriod : 3600 seconds
MaxReauthReq : 2
switch#Use the show dot1x interface interface-id command to display the status of the 802.1X attributes for each port.
switch(config-if-Et1/1)# show dot1x interface ethernet1/1
Dot1X Information for Ethernet1
--------------------------------------------
PortControl : force-authorized
HostMode : multi-host
QuietPeriod : 60 seconds
TxPeriod : 5 seconds
ReauthPeriod : 0 seconds
MaxReauthReq : 2
ReauthTimeoutIgnore : No
AuthFailVlan : 10Use the show dot1x all brief command to display IEEE 802.1X status for all ports.
Example
switch# show dot1x all brief
Interface Client Status
---------- -------- -------------
Ethernet5 None Unauthorized
switch#Use the show vlan command to display dynamically assigned VLANs on the port.
switch# show vlan
VLAN Name Status Ports
----- ------------- --------- ----------------------------------
1 default active
2 VLAN0002 active Et7, Et17, Et18, Et41
300* VLAN0300 active Et1/1, Et6, Et19, Et20, Et29
Et30, Et31, Et32, Et42, Et43, Et44
* indicates a Dynamic VLANUse the show dot1x interface interface ID details command to display information about the EAPOL fallback to MBA authentication and MBA timeout details.
switch(config-if-Et1)# show dot1x interface Ethernet1 details
Dot1X Information for Ethernet1
--------------------------------------------
Port control: auto
Host mode: multi-host authenticated
Quiet period: 60 seconds
TX period: 5 seconds
Maximum reauth requests: 2
Ignore reauth timeout: No
Auth failure VLAN: 101
Unauthorized access VLAN egress: Yes
Unauthorized native VLAN egress: Yes
EAPOL: enabled
MAC-based authentication: disabled
EAPOL authentication failure fallback: MBA, timeout 200 seconds
Dot1X Authenticator Client
Port status: Authorized
Supplicant MAC Reauth Period (in seconds)
-------------- --------------------------
0022.0100.0001 120The aaa unresponsive action traffic allow vlan enables the the dot1x AAA unresponsive VLAN feature on the switch.
The no aaa unresponsive action traffic allow vlan command disbales the dot1x AAA unresponsive VLAN feature from the running-config.
Command Mode
Dot1x Configuration Mode
Command Syntax
aaa unresponsive action traffic allow vlan VLAN-ID
no unresponsive action traffic allow vlan
Parameters
Example
switch(config)# dot1x
switch(config-dot1x)# aaa unresponsive action traffic allow vlan 50The aaa authentication load-balance round-robin command in the Dot1X Configuration Mode enables round robin authentication for RADIUS Server Groups.
The no version of the command disables the feature and removes it from the running-config.
Command Mode
Dot1X Configuration
Command Syntax
aaa authentication load-balance round-robin
no aaa authentication load-balance round-robin
Example
Use the following commands to configure round robin authentication for 802.1X:
switch(config)# dot1x
switch(config-dot1x)# aaa authentication load-balance round-robin
switch(config-dot1x)#The captive portal command enables the 802.1X Web Authentication on the switch.
The no captive portal command removes the 802.1X Web Authentication configuration from the running-config.
Command Mode
Dot1x Configuration Mode
Command Syntax
captive portal url URL ssl profile profile access-list ipv4 ACL name bypass fqdn_wildcard request timeout seconds
no captive portal url URL ssl profile profile access-list ipv4 ACL name bypass fqdn_wildcardrequest timeout seconds
switch(config)# dot1x
switch(config-dot1x)# captive portal ssl profile test-ssl_profileswitch(config)# dot1x
switch(config-dot1x)# captive portal access-list ipv4 test-ACLswitch(config)# dot1x
switch(config-dot1x)# captive portal bypass www.mycompany.comThe clear dot1x statistics command resets the 802.1X counters on the specified interface or all interfaces.
Privileged EXEC
clear dot1x statistics INTERFACE_NAME
Example
switch# clear dot1x statistics all
switch#The dot1x eapol command places the switch into 802.1X Configuration Mode and configures the EAPoL actions for Guest VLAN access. The [no | default] options reverts the configuration to match the global configuration.
Command Mode
Dot1x Configuration Mode
Command Syntax
dot1x eapol unresponsive action traffic allow [vlan vlan_id]
Example
switch(config)#interface Ethernet6/1
switch(config-if-Et6/1)#dot1x
switch(config-dot1x)#eapol unresponsive action traffic allow vlan 25The dot1x mac based authentication command enables MAC-based authentication on the existing 802.1X authenticator port.
The no dot1x mac based authentication and the default dot1x mac based authentication commands restore the switch default by disabling the corresponding dot1x mac based authentication command for the specific 802.1X authenticator port.
Interface-Ethernet Configuration
dot1x mac based authentication
no dot1x mac based authentication
default dot1x mac based authentication
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x mac based authentication
switch(config-if-Et1)#The dot1x mac based authentication delay command enables MAC-based authentication delay. By default, the delay is triggered after 5 seconds.
The no dot1x mac based authentication delay and the default dot1x mac based authentication delay commands restore the switch default by disabling the corresponding dot1x mac based authentication delay command.
Dot1x Configuration
dot1x mac based authentication delay delay-time seconds
no dot1x mac based authentication delay
default dot1x mac based authentication delay
Example
switch(config)# dot1x
switch(config-dot1x)# mac based authentication delay 30 secondsThe dot1x mac based authentication hold period command enables MAC-based authentication hold period. By default, the hold period is 60 seconds.
The no dot1x mac based authentication hold period and the default dot1x mac based authentication hold period commands restore the switch default by disabling the corresponding dot1x mac based authentication hold period command.
Dot1x Configuration
dot1x mac based authentication hold period hold period-time seconds
no dot1x mac based authentication hold period
default dot1x mac based authentication hold period
Example
switch(config)# dot1x
switch(config-dot1x)# mac based authentication hold period 100 secondsThe dot1x mac based authentication request-identity command in the Global Configuration Mode sends identity requests at 60 second intervals until successfully authenticating the EAPOL supplicant. The [no | default] versions of the command remove the configuration from the running-config.
Command Mode
Global Configuration Mode
Command Syntax
dot1x mac based authentication request-identity common
no dot1x mac based authentication request-identity common
default dot1x mac based authentication request-identity common
Example
switch(config)# doct1x
switch(config-dot1x)# mac based authentication request-identity common
switch(config-dot1x)#The dot1x pae authenticator command sets the port access entity (PAE) type of the configuration mode interface to authenticator, which enables IEEE 802.1X on the port. EOS disables IEEE 802.1X on all ports by default.
The no dot1x pae authenticator and default dot1x pae authenticator commands restore the switch default by deleting the corresponding dot1x pae authenticator command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x pae authenticator
no dot1x pae authenticator
default dot1x pae authenticator
switch(config-if-Et1)# interface ethernet 2
switch(config-if-Et1)# dot1x pae authenticator
switch(config-if-Et1)#switch(config-if-Et1)# interface ethernet 2
switch(config-if-Et1)# no dot1x pae authenticator
switch(config-if-Et1)#The dot1x protocol bpdu command enables bypassing BPDU guard on unauthenticated hosts and does not require configuration of the Wake on LAN feature.
The no dot1x system-auth-control command disables bypassing BPDU guard by removing the dot1x system-auth-control command from running-config.
Command Mode
Global Configuration
Command Syntax
dot1x protocol bpdu bypass
no dot1x dot1x protocol bpdu bypass
Examples
switch(config)# dot1x system-auth-control
switch(config)#The dot1x reauthentication command configures the configuration mode interface to require re-authentication from clients at regular intervals. Use the dot1x timeout reauth-period command to set the interval.
The no dot1x reauthentication and default dot1x reauthentication commands restore the default setting by deleting the corresponding dot1x reauthentication command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x reauthentication
no dot1x reauthentication
default dot1x reauthentication
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x reauthentication
switch(config-if-Et1)#The dot1x reauthorization request limit command configures how often the switch retransmits an 802.1X Extensible Authentication Protocol (EAP) request packet before ending the conversation and restarting authentication.
The no dot1x reauthorization request limit and default dot1x reauthorization request limit commands restore the default value of 2 by deleting the corresponding dot1x reauthorization request limit command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x reauthorization request limit attempts
no dot1x reauthorization request limit
default dot1x reauthorization request limit
attempts Maximum number of attempts. Values range from 1 to 10; default value is 2.
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x reauthorization request limit 6
switch(config-if-Et1)#switch(config)# interface ethernet 1
switch(config-if-Et1)# no dot1x reauthorization request limit
switch(config-if-Et1)#The dot1x system-auth-control command enables 802.1X authentication on the switch.
The no dot1x system-auth-control and default dot1x system-auth-control commands disables 802.1X authentication by removing the dot1x system-auth-control command from running-config.
Global Configuration
dot1x system-auth-control
no dot1x system-auth-control
default dot1x system-auth-control
switch(config)# dot1x system-auth-control
switch(config)#switch(config)# no dot1x system-auth-control
switch(config)#If the switch fails to immediately authenticate the client, the switch waits a specified time configured with thedot1x timeout quiet-period command. This timer also indicates the blocked time for a client with failed authentication.
The no dot1x timeout quiet-period and default dot1x timeout quiet-period commands restore the default quiet period of 60 seconds by removing the corresponding dot1x timeout quiet-period command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x timeout quiet-period quiet_time
no dot1x timeout quiet-period
default dot1x timeout quiet-period
quiet_time Interval in seconds. Values range from 1 to 65535. Default value is 60.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x timeout quiet-period 30
switch(config-if-Et1)#The dot1x timeout reauth-period command specifies the time period that the configuration mode interface waits before requiring re-authentication from clients.
The no dot1x timeout reauth-period and default dot1x timeout reauth-period commands restore the default period of 60 minutes by removing the corresponding dot1x timeout reauth-period command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x timeout reauth-period reauth_time
no dot1x timeout reauth-period
default dot1x timeout reauth-period
reauth_time The number of seconds the interface passes traffic before requiring re-authentication. Values range from 1 to 65535. Default value is 3600.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x reauthentication
switch(config-if-Et1)# dot1x timeout reauth-period 21600
switch(config-if-Et1)#The authenticator establishes authentication and re-authentication by sending Extensible Authentication Protocol (EAP) requests to the supplicant, and the supplicant sends a reply which the authenticator forwards to an authentication server. If the authenticator does not receive a reply to the EAP request, it waits a specified time before retransmitting the request. The dot1x timeout tx-period command configures the wait time.
The no dot1x timeout tx-period and default dot1x timeout tx-period commands restore the default wait time by removing the corresponding dot1x timeout tx-period command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x timeout tx-period tx_time
no dot1x timeout tx-period
default dot1x timeout tx-period
tx_time Values range from 1 to 65535. Default value is 5.
Example
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x timeout tx-period 30
switch(config-if-Et1)#When multiple clients are connected to an Ethernet interface providing 802.1X authentication, the port can accept packets from all MAC addresses once the supplicant has been authenticated (multi-host mode), or it can accept only those packets originating from the MAC address of the authenticated client (single-host mode) or ultiple authenticated clients (multi-host authenticated mode) . The dot1x host-mode command specifies the host mode for authentication of multiple clients on the configuration mode interface.
The no dot1x host-mode and default dot1x host-mode commands restore the switch default (multi-host mode) by removing the corresponding dot1x host-mode command for the configuration mode interface.
Command Mode
Interface-Ethernet Configuration
dot1x host-mode [multi-host | single-host | multi-host authenticated]
no dot1x host-mode
default dot1x host-mode
Example
switch(config)# interface ethernet 1
switch(config-if-Et1)# dot1x host-mode single-host
switch(config-if-Et1)#The dot1x port-control command configures the configuration mode interface as an authenticator port and specifies whether it will authenticate traffic.
The no dot1x port-control and default dot1x port-control commands configure the port to pass traffic without authorization by removing the corresponding dot1x port-control command from running-config.
Interface-Ethernet Configuration
Interface-Management Configuration
dot1x port-control STATE
no dot1x port-control
default dot1x port-control
switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x port-control force-authorized
switch(config-if-Et1)#switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x port-control force-unauthorized
switch(config-if-Et1)#switch(config)# interface Ethernet 1
switch(config-if-Et1)# dot1x port-control auto
switch(config-if-Et1)#The neighbor classification command in the Global Configuration Mode centralizes how the switch responds when it identifies a device, such as a VoIP phone, and moves between different classes such as moving from a generic host to a phone.
When a device authenticates using dot1x or MBA,the switch monitors the device classification. If the classification changes, for instance, a RADIUS VSA suddenly identifies a generic MAC address as a phone, the switch automatically flaps the port to force the device to restart the DHCP process in the correct Voice VLAN.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
neighbor classification post-auth action port-flap
no neighbor classification post-auth action port-flap
default neighbor classification post-auth action port-flap
Example
switch(config)# neighbor classification post-auth action port-flap
switch(config)#The neighbor resolution command in the Global Configuration Mode enters the Neighbor Resolution Configuration Mode. Then configure the switch to actively discover the IP addresses of authenticated devices, using ARP or Neighbor Discovery, so that it can correctly apply classification rules, such as identifying a device as a phone, based on IP-specific attributes.
The no version of the command disable the feature and remove the configuration from the running-config.
Command Mode
Global Configuration
Neighbor Resolution Configuration
Neighbor Resolution Interface Configuration
Command Syntax
neighbor resolution interface interface [ neighbor ipv4 | ipv6] ] [mac-address mac_address]
no neighbor resolution
Example
switch(config)# neighbor resolution
switch(config-nbr-res)# interface Ethernet1/1
switch(config-nbr-res-if-Et1/1)# neighbor 172.16.21.101 mac-address fcbd.670f.49fa
switch(config-nbr-res-if-Et1/1)#The radius mtu command in the Dot1X Configuration Mode configures the size of the RADIUS Access-Request Maximum Transmission Unit (MTU) for an 802.1X payload to prevent fragmentation of the packet on the RADIUS server.
The no of the command removes the configuration from the switch running-config.
Command Mode
Dot1X Configuration
Command Syntax
radius mtu bytes
no radius mtu
Example
switch(config)# dot1x
switch(config-dot1x)# radius mtu 1500
switch(config-dot1x)#The show dot1x all brief command displays the IEEE 802.1X status for all ports.
EXEC
show dot1x all brief
Example
switch# show dot1x all brief
Interface Client Status
-------------------------------------------------
Ethernet5 None Unauthorized
switch#The show dot1x hosts command displays 802.1X information for all the supplicants.
EXEC
show dot1x hosts [ethernet]
ethernet e_num Ethernet interface specified by e_num.
switch# show dot1x hosts
Legend:
* - Statically configured VLAN
Port Supplicant MAC Username Auth State Fallback VLAN VLAN Name
--------- -------------- —----------------- ----- ------------- -------------- ------ —--------
Et1/4 36d4.b67b.67c6 user101 EAPOL SUCCESS NONE 123 DATA
Et2/4 36d4.b67b.67c7 user102 EAPOL SUCCESS NONE 124 VLAN0124
Et1/4 36d4.b67b.68e3 36:d4:b6:7b:68:e3 MBA SUCCESS NONE 1* defaultUse the following command to display 802.1X details for an interface:
switch# show dot1x hosts interface Ethernet2/4 detail
Supplicant: user1 (36d4.b67b.67c8)
Operational:
Supplicant MAC: 36d4.b67b.67c8
Supplicant IP: 192.168.1.4 sourceLldp
User name: user1
Interface: Ethernet2/4
Authentication method: EAPOL
Supplicant state: SUCCESS
Fallback Applied: AUTH-FAIL-VLAN
Reauthentication behaviour: DO-NOT-RE-AUTH
Reauthentication interval: 0 seconds
VLAN ID: 200 (static)
VLAN Name: VLAN0200
Device type: Phone
Accounting-Session-Id: 1x00000005
Captive portal:
AAA Server Returned:
Arista-WebAuth:
Filter-Id: WEB-AUTH-ACL
NAS-Filter-Rule: permit in ip from 11.0.0.0/8 to 12.0.0.0/8
deny in ip from 10.1.0.0/16 to 20.1.0.0/16
Session-Timeout: 28800 seconds
Idle-Timeout: 200 secondsThe show dot1x statistics command displays 802.1X statistics for the specified port or ports.
Command ModeEXEC
Command Syntaxshow dot1x INTERFACE_NAME statistics
Parametersvlan v_num VLAN interface specified by v_num.
Example
switch# show dot1x interface ethernet 5 statistics
Dot1X Authenticator Port Statistics for Ethernet5
-------------------------------------------------
RxStart = 0 RxLogoff = 0 RxRespId = 0
RxStart= 0 RxInvalid = 0 RxTotal = 0
TxReqId = 0 TxReq = 0 TxTotal = 0
RxVersion = 0 LastRxSrcMAC = 0000.0000.0000
switch#The show dot1x command displays 802.1X information for the specified interface.
EXEC
show dot1x INTERFACE_NAME INFO
switch# show dot1x interface ethernet 5
Dot1X Information for Ethernet5
--------------------------------------------
PortControl : auto
QuietPeriod : 60 seconds
TxPeriod : 5 seconds
ReauthPeriod : 3600 seconds
MaxReauthReq : 2
switch#switch# show dot1x interface ethernet 5 detail
Dot1X Information for Ethernet5
--------------------------------------------
PortControl : auto
QuietPeriod : 60 seconds
TxPeriod : 5 seconds
ReauthPeriod : 3600 seconds
MaxReauthReq : 2
Dot1X Authenticator Client
Port Status : Unauthorized
switch#The show dot1x captive-portal bypass command displays information about dot1x captive portal bypass configurations.
Command Mode
EXEC
Command Syntax
show dot1x captive-portal bypass address [ipv4 | ipv6]
Parameters
[ipv4 | ipv6] - Display dot1x captive portal bypass information for a specific IP address.
Example
switch# show captive-portal bypass
Captive portal bypass:
*.eng.mycompany.com matched by 10.0.1.3, 1.0.2.4
web5.it.mycompany.com matched by 10.0.5.7The show dot1x captive-portal resolutions command displays information for all reverse DNS resolution entries in use by the captive portal.
Command Mode
EXEC
Command Syntax
show dot1x captive-portal resolutions address [ipv4 | ipv6]
Parameters
[ipv4 | ipv6] - Display dot1x captive portal resolutions information for a specific IP address.
Example
switch# show dot1x captive-portal resolutions
Address Hostnames Expiration
--------------- ------------------------- -------------------
1.0.2.4 www1.eng.arista.com 2033-05-17 20:33:20
10.0.5.7 web4.it.arista.com 2033-05-17 20:33:23
web5.it.mycompany.com
10.10.1.3 - 2033-05-17 20:33:26
10.20.1.3 (pending)
80.0.6.3 www1.eng.mycompany.com 2033-05-17 20:33:21The statistics packets droppedcommand to configure the dot1x dropped counters on the switch in the dot1x configuration mode. By default, EOS disable the dot1x dropped counters. The no form of the command disables the dot1x dropped counters from the running configuration.
The no statistics packets dropped command disables the dot1x dropped counters from the running configuration.
Command Mode
Dot1x Configuration
Command Syntax
statistics packets dropped
no statistics packets dropped
Example
switch(config-dot1x)# statistics packets droppedNetwork Address Translation (NAT) is a router process that modifies the address information of IP packets in transit. NAT is typically used to correlate address spaces between a local network and a remote, often public, network. Static NAT defines a one-to-one map between local and remote IP addresses. Static maps are configured manually through CLI commands. An interface can support multiple NAT commands, but each command must specify a unique local IP address-port location.
NAT is configured on routers with interfaces connecting to the local networks and interfaces connecting to a remote network.
NAT configurations categorize IP addresses into one of two categories: inside or outside. Inside refers to IP addresses used within the organizational network, while outside refers to addresses on an external network outside the organizational network.
Static NAT configurations create a one-to-one mapping and translate a particular address to another address. This type of configuration creates a permanent entry in the NAT table as long as the configuration is present, enabling both inside and outside hosts to initiate a connection.
Enable the NAT of a source address (source NAT) using the ip nat source static command for the configuration mode interface. Applying source NAT to interfaces that connect to local hosts shields the hosts' IP address when sending IP packets to remote destinations.
This command installs hardware translation entries for forward and reverse unicast traffic. When the rule specifies a multicast group, the command does not install the reverse path in hardware. The command may include an access control list to filter packets for translation.
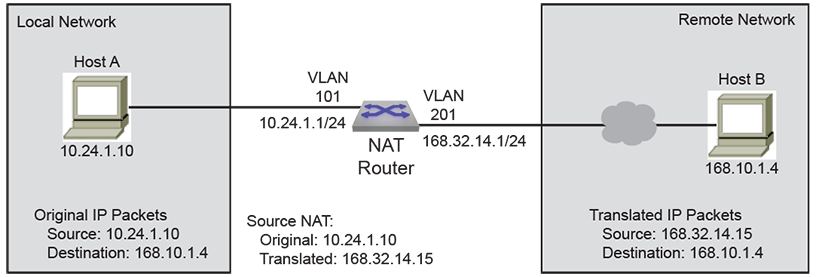
Example
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip nat source static 10.24.1.10 168.32.14.15
switch(config-if-Vl201)#The ip nat source static command may include an ACL to limit packet translation. Only packets whose source IP address matches the ACL are cleared. ACLs configured for source NAT must specify a source IP address of any. Source port or protocol matching is not permitted. The destination may be an IP subnet. Commands referencing nonexistent ACLs are accepted by the CLI but only installed in hardware once the ACL is created. Modifying a referenced ACL causes the corresponding hardware entries to be replaced by entries that match the new command.
Example
switch(config)# ip access-list ACL1
switch(config-acl-ACL1)# permit ip any 168.10.1.0/24
switch(config-acl-ACL1)# exit
switch(config)# interface vlan 101
switch(config-if-Vl101)# ip nat source static 10.24.1.10 access-list ACL1 168.32.14.15
switch(config-if-Vl101)#Enable the NAT of a destination address (destination NAT) using the ip nat destination static command for the configuration mode interface. Applying destination NAT to interfaces that connect to remote hosts shields the IP address of the recipient host when receiving IP packets from remote destinations.
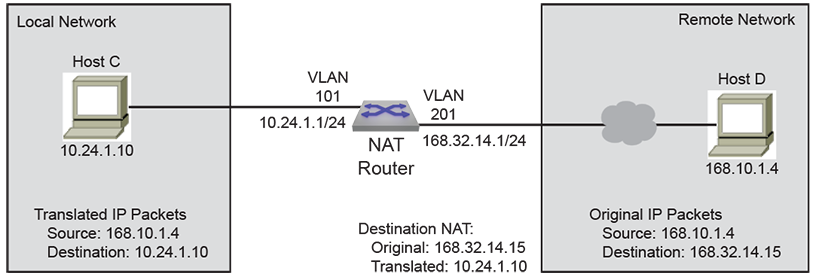
Example
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip nat destination static 168.32.14.15 10.24.1.10
switch(config-if-Vl201)#The ip nat destination static command may include an ACL to limit packet translation. Only packets whose source IP address matches the ACL are cleared. ACLs configured for destination NAT must specify a destination IP address of any. Destination port or protocol matching is not permitted. The source may be an IP subnet. Commands referencing nonexistent ACLs are accepted by the CLI but not installed in hardware until the ACL is created. Modifying a referenced ACL causes the corresponding hardware entries to be replaced by entries that match the new command.
Example
switch(config)# ip access-list ACL2
switch(config-acl-ACL2)# permit ip 168.10.1.4/32 any
switch(config-acl-ACL2)# exit
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip nat destination static 168.32.14.15 access-list ACL2 10.24.1.10
switch(config-if-Vl201)#Network address translation of both source and destination addresses on the same interface (twice NAT) is enabled by creating one source NAT rule and one destination NAT rule on the same interface and associating them through a NAT group using the ip nat source static and ip nat destination static commands.
The ip nat source static command translates the actual local source address to a source address, which can be used outside the local network to reference the source. The ip nat destination static command translates an internally used destination address to the actual IP address that is the packet's destination.
The source and destination NAT rules must reference the same NAT group, and both should either specify only IP addresses or specify both IP addresses and L4 port information. An error message will be displayed if L4 port information is configured in one rule but not in the other.
Each NAT rule installs hardware translation entries for forward and reverse unicast traffic. When the rule specifies a multicast group, the command does not install the reverse path in hardware. Twice NAT does not support using access control lists to filter packets for translation.
Example
switch(config)# interface ethernet 2
switch(config-if-Et2)# ip nat source static 10.24.1.10 168.32.14.15 group 3
switch(config-if-Et2)# ip nat destination static 10.68.104.3 168.25.10.7 group 3When a static source NAT is configured on an interface, the source IP translation happens only for those packets going 'out' of this interface. If a packet is egressing on an interface that does not have NAT configured, then the source IP is not translated.
When static SNAT is configured on two interfaces, the translation specified for one interface can be applied to a packet going out on the other interface.
switch(config)# interface ethernet 1
switch(config-if-Et1)# ip nat source static 10.1.1.1 171.1.1.1
switch(config)# interface ethernet 2
switch(config-if-Et2)# ip nat source static 20.1.1.1 172.1.1.1switch(config)# ip access-list acl1
switch(config-acl-acl1)# permit ip any 171.1.1.0/24
switch(config)# ip access-list acl2
switch(config-acl-acl2)# permit ip any 172.1.1.0/24
switch(config)# interface ethernet 1
switch(config-if-Et1)# ip nat source static 10.1.1.1 access-list acl1 171.1.1.1
switch(config)# interface ethernet 2
switch(config-if-Et2)# ip nat source static 20.1.1.1 access-list acl2 172.1.1.1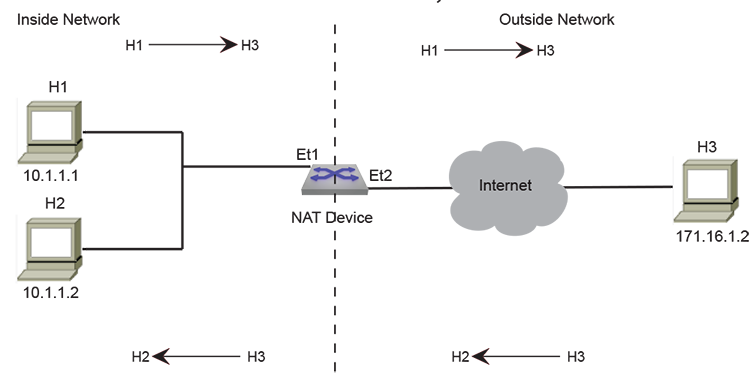
Many-to-Many NAT maps local addresses to a global address selected from a pool of global addresses. After configuring the pool, EOS dynamically picks the first available address from the pool after receiving the first packet.
PAT is a form of dynamic NAT where multiple local addresses are mapped to a single global address (many-to-one) using different source ports. This method is also called NAT Overloading, Network Address Port Translation (NAPT), and Masquerade. The global address can be the IP address configured on the outside interface.
EOS creates hardware entries that translate packets when processing the CLI command, and creates entries for forward and reverse traffic for unicast traffic. For multicast traffic, EOS does not create the hardware entry for reverse traffic.Commands may include ACLs to filter packets that are cleared. Source NAT uses ACLs to filter packets based on the destination IP address, while destination NAT uses ACLs to filter packets based on the source IP address. When using NAT, inside usually refers to a private network, while outside usually refers to a public network.
A switch with NAT configured translates forwarded traffic between inside and outside interfaces and the flow that matches the criteria specified for translation.Commands may include ACLs to filter cleared packets. Source NAT uses ACLs to filter packets based on destination IP address. Destination NAT uses ACLs to filter packets based on the source IP address. When using NAT, inside refers to a private network, while outside refers to a public network.
A switch with NAT configured translates forwarded traffic between inside and outside interfaces and the flow that matches the criteria specified for translation.
The addresses used for translation are configured by issuing the ip nat pool command in global configuration mode.
Example
switch(config)# ip nat pool p1 10.15.15.15 10.15.15.25
switch(config)#The ip address command configures VLAN 201 with an IP address.
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip address 10.0.0.1/24
switch(config-if-Vl201)#switch(config-if-Vl201)# ip nat source dynamic access-list ACL2 pool p2
switch(config-if-Vl201)#For each Dynamic NAT configuration, you can specify the priority from lowest to highest in an interface mode. The ip nat source dynamic command allows you to configure dynamic NAT priority from the source IP address. Multiple dynamic NAT configurations have the same priority irrespective of the order. If a priority is not specified in NAT rule, by default, the priority is 0 (lowest priority).
Service FTP dynamic NAT rules with a single IP in the pool are considered to be of the highest priority.
Example
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip address 10.0.0.1/24
switch(config-if-Vl201)# ip nat source dynamic access-list a0 pool p0
switch(config-if-Vl201)# ip nat source dynamic access-list a1 pool p1 priority 1
switch(config-if-Vl201)# ip nat source dynamic access-list a2 pool p2 priority 2
switch(config-if-Vl201)# ip nat source dynamic access-list a3 pool p3 priority 3
switch(config-if-Vl201)# ip nat source dynamic access-list a4 pool p4 priority 4
switch(config-if-Vl201)# ip nat source dynamic access-list a5 pool p5 priority 5
switch(config-if-Vl201)#The following configures a dynamic NAT profile with overload.
Example
ip nat profile patName
ip nat source dynamic access-list accessList1 overload
!
ip access-list accessList1
20 permit ip host 1.1.1.2 any logThe ip nat source dynamic command specifies a dynamic translation from the source IP address to the pool and to overload the pool address (or addresses).
Example
switch(config)# interface ethernet 3/1
switch(config-if-Et3/1)# ip nat source dynamic access-list ACL2 pool p2
switch(config-if-Et3/1)#The ip nat translation tcp-timeout or ip nat translation udp-timeout commands alter the translation timeout period for NAT translation table entries.
switch(config)# ip nat translation tcp-timeout 600
switch(config)#switch(config)# ip nat translation udp-timeout 800
switch(config)#The show ip nat pool command displays the configuration of the address pool.
Example
switch# show ip nat pool
Pool StartIp EndIp Prefix
p1 10.15.15.15 10.15.15.25 24
p2 10.10.15.15 10.10.15.25 22
p3 10.12.15.15 10.12.15.25 12
switch#Use the clear ip nat flow translation command to remove all or the specified NAT table entries.
Example
switch# clear ip nat flow translation
switch#Example:
switch(config)# ip nat pool p1 10.1.1.1 10.1.1.4 prefix-length 24
switch(config)# interface ethernet 1
switch(config-if-Et1)# ip nat source dynamic access-list a1 pool p1
switch(config-if-Et1)# ip address 10.1.1.1/24 secondary
switch(config-if-Et1)# ip address 10.1.1.2/24 secondary
switch(config-if-Et1)# ip address 10.1.1.3/24 secondary
switch(config-if-Et1)# ip address 10.1.1.4/24 secondaryIf the next hop of the NAT device uses a different subnet, configure a static Null route for the IP addresses in the NAT pool. Redistribute the static route using BGP/OSPF.
switch(config)# interface port-channel 319
switch(config-if-Po319)# ip nat source dynamic access-list dynamic-nat-m2m pool natpl-dynamic-nat-m2m
switch(config)# ip access-list dynamic-nat-m2m
switch(config-acl-dynamic-nat-m2m)# 10 permit ip 192.168.93.0/24 any
switch(config)# ip nat pool natpl-dynamic-nat-m2m prefix-length 24
switch(config-natpool-p1)# range 11.3.3.2 11.3.3.10switch(config)# ip route 11.0.0.0/8 Null0
switch(config)# router ospf 1
switch(config-router-ospf)# redistribute staticThe NAT peer state synchronization provides redundancy and resiliency for dynamic NAT across a pair of devices to avoid a single NAT device failure. Both devices in redundant pair are active and they track new sessions and create or delete NAT entries dynamically. Essentially, an active NAT entry is maintained on both devices, irrespective of who created the NAT entry.
ip nat pool POOL61 prefix-length 24
range 170.24.0.2 170.24.0.200
ip access-list NatACL61
10 permit ip 61.0.0.0/16 any
interface Port-Channel5
mtu 9214
no switchport
ip address 10.0.0.1/31
ip nat source dynamic access-list NatACL61 pool POOL61
ip nat synchronization
peer-address 11.11.11.1
local-interface Vlan1111
port-range 1024 2048switch(config)# ip nat synchronization
switch(config-nat-synchronization)# description <description>switch(config)# ip nat synchronization
switch(config-nat-synchronization)# expiry-interval 6switch(config)# ip nat synchronization
switch(config-nat-synchronization)# peer address 202.1.1.2switch(config)# show ip nat synchronization advertised-translations
Source IP Destination IP Translated IP TGT Type Interface/Profile
--------------------------------------------------------------------------------------------
10.1.3.10:21800 191.1.1.10:80 139.1.1.1:21800 SRC DYN Port-Channel100
10.1.2.10:13750 191.1.1.10:80 139.1.1.1:13750 SRC DYN Port-Channel100
10.1.2.10:33757 191.1.1.10:80 139.1.1.1:5951 SRC DYN Port-Channel100
10.1.5.10:37111 191.1.1.10:80 139.1.1.1:7561 SRC DYN Port-Channel100switch(config)# show ip nat synchronization discovered-translations
Source IP Destination IP Translated IP TGT Type Interface/Profile
--------------------------------------------------------------------------------------------
10.1.3.10:28606 191.1.1.10:80 139.1.1.1:28606 SRC DYN Port-Channel100
10.1.6.10:39697 191.1.1.10:80 139.1.1.1:39697 SRC DYN Port-Channel100
10.1.6.10:20583 191.1.1.10:80 139.1.1.1:31683 SRC DYN Port-Channel100
10.1.6.10:28419 191.1.1.10:80 139.1.1.1:28419 SRC DYN Port-Channel100The following commands apply the configured NAT profile on a tunnel interface.
Example
interface Tunnel0
ip address 10.1.1.1/24
tunnel source 2.1.1.1
tunnel destination 2.1.1.2
ip nat service-profile natNameProfile
The clear ip nat flow translation command clears all or the specified NAT table entries.
Command Mode
Privileged EXEC
Command Syntax
clear ip nat flow translation [HOST_ADDR [DEST_ADDR]][INTF][PROT_TYPE]
Parameters
HOST_ADDR Host address to be modified. Options include:
DEST_ADDR Destination address of translated packet. Destination address can be entered only when the HOST_ADDR is specified. Options include:
INTF Route source. Options include:
PROT_TYPE Filters packets based on protocol type. Options include:
udp UDP packets with specified destination address are cleared.
switch# clear ip nat flow translation
switch#switch# clear ip nat flow translation address 172.22.30.52
switch#switch# clear ip nat flow translation address 172.22.30.52 10.10.10.3
switch#The ip address command configures the IPv4 address and connected subnet on the configuration mode interface. Each interface can have one primary address and multiple secondary addresses.
The no ip address and default ip address commands remove the IPv4 address assignment from the configuration mode interface. Entering the command without specifying an address removes the primary and all secondary addresses from the interface. The primary address cannot be deleted until all secondary addresses are removed from the interface.
Removing all IPv4 address assignments from an interface disables IPv4 processing on that port.
Command Mode
Interface-Ethernet Configuration
Interface-Loopback Configuration
Interface-Management Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip address [ipv4_subnet][PRIORITY]
no ip address [ipv4_subnet][PRIORITY]
default ip address [ipv4_subnet][PRIORITY]
secondary The address is the secondary IPv4 address for the interface.
Guidelines
The ip address command is supported on routable interfaces.
Example
switch(config)# interface vlan 200
switch(config-if-Vl200)# ip address 10.0.0.1/24
switch(config-if-Vl200)#The ip nat destination static command enables NAT of a specified destination address for the configuration mode interface. This command installs hardware translation entries for forward and reverse unicast traffic. When the rule specifies a multicast group, the command does not install the reverse path in hardware. The command may include an access control list to filter packets for translation.
When configuring twice NAT, an arbitrary NAT group number is used to associate the source NAT and destination NAT rules. This number must be the same in both rules.
The no ip nat destination static and default ip nat destination static commands disables NAT translation of the specified destination address by removing the corresponding ip nat destination static command from running_config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip nat destination static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE][group group_number]
no ip nat destination static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE] [group group_number]
default ip nat destination static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE][group group_number]
switch(config)# interface vlan 201
switch(config-if-Vl201)# ip nat destination static 10.24.1.10 168.32.14.15
switch(config-if-Vl201)#switch(config)# ip access-list ACL2
switch(config-acl-ACL2)# permit ip 168.10.1.1/32 any
switch(config-acl-ACL2)# exit
switch(config)# interface vlan 201
switch(config-if-Vl201)#
switch(config-if-Vl201)#switch(config)# interface ethernet 2
switch(config-if-Et2)# ip nat source static 10.24.1.10 168.32.14.15 group 3
switch(config-if-Et2)# ip nat destination static 10.68.104.3 168.25.10.7 group 3The ip nat pool command identifies a pool of addresses using start address, end address, and either netmask or prefix length. If its starting IP address and ending IP address are the same, there is only one address in the address pool.
The no ip nat pool removes the ip nat poolcommand from running_config.
Command Mode
Global Configuration
Command Syntax
ip nat pool pool_name [ADDRESS_SPAN] SUBNET_SIZE
no ip nat pool pool_name
default ip nat pool pool_name
switch(config)# ip nat pool poo1 10.15.15.15 10.15.15.25 prefix-length 24
switch(config)switch(config)# no ip nat pool poo1 10.15.15.15 10.15.15.25 prefix-length 24
switch(config)The ip nat source dynamic command enables NAT of a specified source address for packets sent and received on the configuration mode interface. This command installs hardware translation entries for forward and reverse traffic. When the rule specifies a multicast group, the command does not install the reverse path in hardware. The command may include an access control list to filter packets for translation.
The no ip nat source dynamic and default ip nat source dynamic commands disables NAT translation of the specified destination address by removing the corresponding ip nat source dynamic command from running_config .
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip nat source dynamic access-list acl_name POOL_TYPE
no ip nat source dynamic access-list acl_name
default ip nat source dynamic access-list acl_name
ParametersPOOL_TYPE Options include:
The pool option is required even if the pool has just one address. NAT uses that one address for all of the translations.
pool_fullcone Enables full cone NAT where all requests from the same internal IP address and port are mapped to the same external IP address and port.
switch(config)# interface ethernet 3/1
switch(config-if-Et3/1)# ip nat source dynamic access-list ACL2 pool p2
switch(config-if-Et3/1)#switch(config)# interface ethernet 3/1
switch(config-if-Et3/1)# no ip nat source dynamic access-list ACL2
switch(config-if-Et3/1)# The ip nat source static command enables NAT of a specified source address for the configuration mode interface. This command installs hardware translation entries for forward and reverse unicast traffic. When the rule specifies a multicast group, the command does not install the reverse path in hardware. The command may include an access control list to filter packets for translation.
When configuring twice NAT, an arbitrary NAT group number is used to associate the source NAT and destination NAT rules. This number must be the same in both rules.
The no ip nat source static and default ip nat source static commands disables NAT translation of the specified source address by removing the corresponding ip nat source command from running_config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-channel Configuration
Interface-VLAN Configuration
Command Syntax
ip nat source static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE] [group group_number]
no ip nat source static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE] [group group_number]
default ip nat source static ORIGINAL [FILTER] TRANSLATED [PROT_TYPE] [group group_number]
switch(config)# interface vlan 101
switch(config-if-Vl101)# ip nat source static 10.24.1.10 168.32.14.15
switch(config-if-Vl101)#switch(config)# ip access-list ACL1
switch(config-acl-ACL1)# permit ip any 168.10.1.1/24
switch(config-acl-ACL1)# exit
switch(config)# interface vlan 101
switch(config-if-Vl101)# ip nat source static 10.24.1.10 access-list ACL1
168.32.14.15
switch(config-if-Vl101)#switch(config)# interface ethernet 2
switch(config-if-Et2)# ip nat source static 10.24.1.10 168.32.14.15 group 3
switch(config-if-Et2)# ip nat destination static 10.68.104.3 168.25.10.7 group 3The ip nat synchronization command places the switch into the NAT Synchronization Configuration Mode and configures NAT Synchronization to provide redundancy and resiliency for dynamic NAT across a pair of switches. This mitigates the risk of a single NAT failure.
To disable the feature, use the parameter shutdown in NAT Synchronization Mode.
Command Mode
IP NAT Synchronization Configuration
Command Syntax
ip nat synchronization [description description] [expiry-interval seconds] [local-interface interface_type port_number] [peer-address ip_address] [port-range [port_range] [split [port_range | disabled]] [shutdown]
Parameters
Example
Use the following commands to configure IP NAT Synchronization:
switch(config)#ip nat synchronization
switch(config-nat-synchronization)# expiry-interval 3600
switch(config-nat-synchronization)# peer-address 202.1.1.2
switch(config-nat-synchronization)# local-interface Vlan2022
switch(config-nat-synchronization)# port-range 1024 24000The ip nat translation counters command enables the feature to count packets that are translated by static and twice NAT rules in hardware. Once this feature is enabled, all current rules in hardware and new rules that are configured after running this command receive policers for counting packets.
The no ip nat translation counters and default ip nat translation counters commands disable the packet counter feature for static and twice NAT connections.
Command Mode
Global Configuration
Command Syntax
ip nat translation counters
no ip nat translation counters
default ip nat translation counters
Guidelines
The ip nat translation counters command is supported on the DCS-7150 series switches only. This command is solely intended to debug static and twice NAT translation failures in hardware. Disable this feature after completing troubleshooting. If this feature remains enabled even when the count of static connections exceed 275, it can cause unpredictable behavior including restart of FocalPointV2 agent. The restart of FocalPointV2 agent results in traffic disruption.
Example
switch(config)# ip nat translation counters
switch(config)# show ip nat translation hardware detail
Source IP Destination IP Translated IP TGT Type Intf Proto Packets Packets Reply
----------------------------------------------------------------------------------------------
192.168.10.2:0 - 20.1.10.2:0 SRC STAT Vl2640 - 2 1
192.168.110.2:0 - 20.1.110.2:0 SRC STAT Vl2640 - 2 1
switch(config)# show ip nat translation twice hardware detail
Source IP Destination IP Translated Translated Intf Group Packets Packets
Src IP Dst IP Proto Reply
---------------------------------------------------------------------------------------------
192.16.50.2:0 10.1.50.2:0 20.1.50.2:0 10.1.60.2:0 Vl2922 2 - 2 1
19.16.150.2:0 10.1.150.2:0 20.1.150.2:0 10.1.160.2:0 Vl2922 12 - 2The ip nat translation low-mark command configures the minimum threshold that triggers the resumption of programming new NAT translation connections.
The ip nat translation max-entries command specifies the maximum number of NAT translation connections that can be stored. When this limit is reached, new connections are dropped instead of being programmed in hardware or software. At this point no new connections will be programmed until the number of stored entries drop below the configured low-mark, expressed as a percentage of the max-entries value. The default low mark value is 90%.
The no ip nat translation low-mark and default ip nat translation low-mark commands restores the default low-mark value by removing the ip nat translation low-mark command from running_config.
Command Mode
Global Configuration
Command Syntax
ip nat translation low-mark threshold
no ip nat translation low-mark
default ip nat translation low-mark
Parameter
threshold Percentage of maximum connection entries. Value ranges from 1 to 99. Default is 90.
Example
switch(config)# ip nat translation low-mark 93
switch(config)#The ip nat translation max-entries command specifies maximum number of NAT translation connections. After this threshold is reached, new connections are dropped until the number of programmed connections is reduced below the level specified by the ip nat translation low-mark command.
The no ip nat translation max-entries and default ip nat translation max-entries commands removes the maximum connection limit and resets the parameter value to zero by removing the ip nat translation max-entries command from running_config.
Command Mode
Global Configuration
Command Syntax
ip nat translation max-entries connections
no ip nat translation max-entries
default ip nat translation max-entries
Parameters
connections The maximum number of NAT translation connections. Value ranges from 0 to 4294967295. Default value is 0, which removes the connection limit.
Example
switch(config)# ip nat translation max-entries 3000
switch(config)#The ip nat translation tcp-timeout command specifies the translation timeout period for translation table entries. The timeout period specifies the interval during which the switch will attempt to reuse an existing TCP translation for devices specified by table entries.
The no ip nat translation tcp-timeout and default ip nat translation tcp-timeout commands reset the timeout to its default by removing the corresponding ip nat translation tcp-timeout command from running_config.
Command Mode
Global Configuration
Command Syntax
ip nat translation tcp-timeout period
no ip nat translation tcp-timeout
default ip nat translation tcp-timeout
Parameter
period Time-out period in seconds for port translations. Value ranges from 0 to 4294967295. Default value is 86400 (24 hours).
switch(config)# ip nat translation tcp-timeout 600
switch(config)#switch(config)# no ip nat translation tcp-timeout
switch(config)#The ip nat translation udp-timeout command specifies the translation timeout period for translation table entries. The timeout period specifies the interval the switch attempts to establish a UDP connection with devices specified by table entries.
The no ip nat translation udp-timeout and default ip nat translation udp-timeout commands disables NAT translation of the specified destination address by removing the corresponding ip nat translation udp-timeout command from running_config.
Command Mode
Global Configuration
Command Syntax
ip nat translation udp-timeout period
no ip nat translation udp-timeout
default ip nat translation udp-timeout
Parameter
period Value ranges from 0 to 4294967295. Default value is 300 (5 minutes).
switch(config)# ip nat translation udp-timeout 800switch(config)# no ip nat translation udp-timeoutCommand Mode
EXEC
Command Syntax
show ip nat access-list interface [INTF][LISTS]
Example
switch> show ip nat acl ACL1
acl ACL1
(0.0.0.0/0, 168.10.1.1/32)
Interfaces using this ACL for Nat:
Vlan100
switch> show ip nat acl ACL2
acl ACL2
(168.10.1.1/32, 0.0.0.0/0)
Interfaces using this ACL for Nat:
Vlan201
switch>The show ip nat pool command displays the configuration of the address pool.
Command Mode
EXEC
Command Syntax
show ip nat pool POOL_SET
switch# show ip nat pool
Pool StartIp EndIp Prefix
p1 10.15.15.15 10.15.15.25 24
p2 10.10.15.15 10.10.15.25 22
p3 10.12.15.15 10.12.15.25 12
switch#switch# show ip nat pool p1
Pool StartIp EndIp Prefix
p1 4.1.1.1 4.1.1.2 24
1.1.1.1 1.1.1.2 24
3.1.1.1 3.1.1.2 24
switch# show ip nat pool p2
Pool StartIp EndIp Prefix
p2 10.1.1.1 10.1.1.2 16
switch#The show ip nat synchronization advertised-translations command displays the detailed status of devices that are advertised to a peer device.
Command Mode
EXEC
Command Syntax
show ip nat synchronization advertised-translations
Example
switch# show ip nat synchronization advertised-translations
Source IP Destination IP Translated IP TGT Type Intf
------------------------------------------------------------------------
61.0.0.15:6661 100.0.0.2:80 192.170.230.171:6661 SRC DYN Et5
61.0.0.41:2245 100.0.0.2:80 192.170.230.170:2245 SRC DYN Et5
61.0.0.48:22626 100.0.0.2:80 192.170.230.169:22626 SRC DYN Et5
61.0.0.41:22601 100.0.0.2:80 192.170.230.170:22601 SRC DYN Et5
61.0.0.41:16798 100.0.0.2:80 192.170.230.170:16798 SRC DYN Et5
61.0.0.18:22605 100.0.0.2:80 192.170.230.177:22605 SRC DYN Et5
61.0.0.16:2256 100.0.0.2:80 192.170.230.166:2256 SRC DYN Et5The show ip nat synchronization discovered-translations command displays details of what has been advertised from a peer device.
Command Mode
EXEC
Command Syntax
show ip nat synchronization discovered-translations
Example
switch# show ip nat synchronization discovered-translations
Source IP Destination IP Translated IP TGT Type Intf
-------------------------------------------------------------------------
61.0.2.229:63 100.0.0.2:63 170.24.86.180:63 SRC DYN Et5
61.0.15.51:63 100.0.0.2:63 170.24.73.90:63 SRC DYN Et5
61.0.6.68:63 100.0.0.2:63 170.24.110.128:63 SRC DYN Et5
61.0.7.163:63 100.0.0.2:63 170.24.104.35:63 SRC DYN Et5The show ip nat synchronization peer command displays the detailed status of a peer device.
Command Mode
EXEC
Command Syntax
show ip nat synchronization peer
Example
switch# show ip nat synchronization peer
Description : Value
Peer : 11.11.11.0
Connection Port : 4532
Connection Source : 0.0.0.0
Kernel Interface : vlan1111
Local Interface : Vlan1111
Established Time : 1969-12-31 16:00:00
Connection Attempts : 0
Oldest Supported Version : 1
Newest Supported Version : 1
Version Compatible : True
Connection State : connected
Shutdown State : False
Status Mount State : mountMounted
Version Mount State : mountMounted
Recover Mount State : mountMounted
Reboot Mount State : mountMountedThe show ip nat translation command displays configured NAT statements in the switch hardware.
Command Mode
EXEC
Command Syntax
show ip nat translation [address | address-only | destination | detail | dynamic | hardware | interface | kernel | max-entries | source | static | summary | twice]
The command position of all parameters are interchangeable.
twice Displays twice NAT connections.
switch> show ip nat translation
Source IP Destination IP Translated IP TGT Type Intf
---------------------------------------------------------------------------
192.168.1.10:62822 172.22.22.40:53 172.17.254.161:62822 SRC DYN Vl3925
192.152.1.10:20342 172.22.22.40:80 172.17.254.161:22222 SRC STAT Vl3945
switch#switch> show ip nat translation dynamic interface Ethernet 26
Source IP Destination IP Translated IP TGT Type Intf
-------------------------------------------------------------------------
192.168.1.2:8080 10.1.1.5:600 20.1.1.5:8080 SRC DYN Et26switch> show ip nat translation max-entries
Global connection limit 100
Global connection limit low mark 90(90%)
Hosts connection limit 20
Hosts connection limit low mark 18(90%)
Total number of connections 1
Host Max-Entries Low-Mark Connections
-----------------------------------------------------------------------
10.1.1.1 10 9(90%) 0Media Access Control Security (MACsec) is an industry-standard encryption mechanism that protects all traffic flowing on Ethernet links. MACsec is based on IEEE 802.1X and IEEE 802.1AE standards.
MACsec Key Agreement Protocol (MKA) - provides the key agreement protocol for discovering MACsec peers and negotiating keys between MACsec peers (IEEE 802.1X-REV).
Connectivity Association (CA) - allows a security relationship between MACsec-capable devices (endpoints). Endpoints in the same CA share a Connectivity Association Key (CAK). The Arista implementation supports 2 endpoints.
Connectivity Association Key (CAK) - contains a master key used to generate all other keys that are used for MACsec. Endpoints in the same secure Connectivity Association (CA) share a CAK. This key can either be a static pre-shared key or dynamically derived using 802.1X authentication.
Primary Key - contains the CAK for the MKA session in progress. The Primary key consists of a combination of the key name and the actual key. For example, when a configuration uses 0abcd1 0 1234abcd as a primary key, 0abcd1 is the hex key name, while 1234abcd is the actual key.
Fallback Key - When the configured primary key does not establish a connection, the fallback key establishes the session to ensure no traffic loss.
Secure Association Key (SAK) - Derived from the CAK and used by the network device ports to encrypt traffic for a given session.
Key Server - One of the MACsec peers in the CA becomes the Key Server. The Key Server creates and distributes SAKs and uses them for data encryption.
Static Secure Association Key (SAK) - A SAK configured directly on a switch and used with unidirectional links when the MKA protocol is not feasible. Static SAKs require using eXtended Packet Numbering (XPN) cipher suites.
Secure Channel Identifier (SCI) - Uniquely identifies a Secure Channel (SC) consisting of a unidirectional connection for transmitting protected MACsec frames from one MACsec entity (SecY) to one or more others.
The SCI allows a receiving device to determine which secure channel and subsequently, which Secure Association Key (SAK), should be used to decrypt and authenticate the incoming frame.
MACsec encryption is an EOS-licensed feature that requires a valid MACsec license on a switch. MACsec licenses are based on a switch's serial number and the licensee. Every switch running MACsec requires a separate license.
Contact your system engineer to acquire the required license codes before attempting to configure MACsec.
Federal Information Processing Standards (FIPS) are a set of standards defined by the United States federal government related to data processing in computer systems by non-military government agencies and government contractors. These standards define specific requirements for various purposes, such as ensuring computer security and interoperability within and across the computer networking industry.
Arista devices are compliant with FIPS 140. The FIPS 140 enforces the use of a "FIPS Crypto Module." This implementation ensures that the algorithms are correct and restricts the set of allowed algorithms to those approved by the FIPS standard. These are the FIPS-supported algorithms AES-128/256, SHA-256/512, RSA with 2048 bit keys, a subset of Elliptic Curve Digital Signature Algorithm (ECDSA). MACsec has both the AES-128-GCM and AES-256-GCM algorithms certified for the data plane. The FIPS mode is enabled using the fips restrictions command, which, when enabled, filters out any unapproved algorithms and warns you if you try to set them.
MAC security uses the MACsec Key Agreement (MKA) protocol to negotiate between peers using keys (CAKs and CKNs) which are either pre-shared or derived from an 802.1X session and derives a Secure Association Key (SAK) based on the MKA negotiation. This SAK is then programmed in hardware and used for encrypting and decrypting data traffic. In cases where MKA negotiation is not feasible but encryption and decryption of traffic is required (such as unidirectional links), MACsec can instead be configured to use static Secure Association Keys (SAK) configured separately on transmitting and receiving peers. Each peer can have up to four receiving secure keys and one transmitting key.
Use the mac security command to enable MACsec and enter the MAC Security Configuration Mode, followed by the profile command to create a profile and enter the MAC Security Profile Configuration Mode.
Example
switch(config)# mac security
switch(config-mac-security)# profile MACsec_test
switch(config-mac-security-profile-MACsec_test)#The key server is responsible for generating and distributing encryption keys. Run the mka key-server priority command on a peer to change its priority. The peer with the lowest priority is elected as the key server. If multiple peers have the same priority, the system chooses the peer with the lowest MAC address. Priority values range from 0 to 255; the default priority is 16.
Configure the refresh period for the Secure Association Key (SAK) using the mka session rekey-period command. MACsec uses an SAK to encrypt data traffic and derives this SAK from the CAK. The rekey-period values range from 30 to 100000 seconds. The system does not enforce a session rekey period by default and does not refresh the SAK periodically.
To improve the randomness of the numbers used to generate MACsec's cryptographic keys, add a source of entropy with the entropy source command in the Management Security Configuration Mode.
Examples
switch(config-mac-security-profile-test)# cipher aes256-gcm-xpn
switch(config-mac-security-profile-test)# key 0abc12340def56780abc12340def5678 7 06070E234E4D0A48544540585F507E
switch(config-mac-security-profile-test)# key 0def56780abc12340def56780abc1234 7 09484A0C1C0311475E5A527D7C7C70 fallbackswitch(config-mac-security-profile-test)# mka key-server priority 10
switch(config-mac-security-profile-test)# mka session rekey-period 600switch(config-mac-security-profile-test)# management security
switch(config-mgmt-security)# entropy source hardwareswitch(config-mgmt-security)# interface ethernet 5/3/1
switch(config-if-Et5/3/1)# mac security profile test
switch(config-if-Et5/3/1)#To configure the FIPS mode on the MACsec protocol, use the FIPS command.
Example
switch(config)# mac security
switch(config-mac-security) fips restrictionsTo configure the Layer 2 (L2) Protocol Processing mode on the MACsec protocol, use the l2-protocol command.
Example
switch(config)# mac security
switch(config-mac-security) l2-protocol ethernet-flow-control bypassUse the following commands to configure a MACsec profile on a subinterface.
switch(config)# interface ethernet1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# interface ethernet1.10
switch(config-if-Et1.10)# encapsulation dot1q vlan 20
switch(config-if-Et1.10)# mac security profile test-profile
Static SAK is configured separately for receive (Rx) and transmit (Tx) directions. In the Rx direction, multiple SAKs can be configured. For the Tx direction, only one SAK is allowed at a time. An SAK configured for Rx on the local peer should match the SAK configured for Tx on the connected peer and vice versa. Configure the Rx direction first on all the MACsec peers, then configure the Tx direction.Use the cipher command to select a cipher suite. You must choose an eXtended Packet Number (XPN) cipher suite, such as AES128-GCM-XPN or AES256-GCM-XPN. Static SAK will not work with a non-XPN cipher.
switch(config)# mac security
switch(config-mac-security)# profile rx_test
switch(config-mac-security-profile-rx_test)# cipher aes128gcm-xpn
switch(config-mac-security-profile-rx_test)#switch(config-mac-security-profile-rx_test)# key source sak static
switch(config-mac-security-profile-rx_test-sak-static)#switch(config-mac-security-profile-rx_test-sak-static)# secure channel rx
switch(config-mac-security-profile-rx_test-sak-static-rx)# identifier 01:02:03:04:05:06::1234
switch(config-mac-security-profile-rx_test-sak-static-rx)#switch(config-mac-security-profile-rx_test-sak-static-rx)# an 0 key 0 11112222333344445555666677778888
switch(config-mac-security-profile-rx_test-sak-static-rx)#switch(config-mac-security-profile-rx_test-sak-static-rx)# an 1 key 0 9999aaaabbbbccccddddeeeeffff0000
switch(config-mac-security-profile-rx_test-sak-static-rx)#switch(config-mac-security-profile-tx_test-sak-static)# secure channel tx
switch(config-mac-security-profile-tx_test-sak-static-tx)# identifier 01:02:03:04:05:07::1235
switch(config-mac-security-profile-tx_test-sak-static-tx)# an 0 key 0 22223333444455556666777788889999
switch(config-mac-security-profile-tx_test-sak-static-tx)#The mandatory steps to configure a MACsec proxy sub-interface on an Arista switch are:
A new option is added to the 802.1X authenticator configuration to make the authenticator stronger for unreliable authentication servers. By default, when an authentication server is unreachable, the authenticator blocks all traffic on the port and keeps the port as Unauthorized until it gets replies from the authentication server. The following option changes the behavior and maintains the port in its current state if the authentication server is not reachable:
switch(config-if-Et1)# dot1x timeout reauth-timeout-ignore alwaysConfigure 802.1X supplicant using MACsec profiles. The MACsec profile contains all the credentials necessary for 802.1X authentication to succeed. EAP-PWD provides an EAP method that uses a shared password for authentication and allows EOS devices to interoperate with systems that rely on EAP-PWD for deriving MACsec CAK/CKN from the EAP Master Session Key (MSK) and EAP Session ID.
Perform the following steps to configure an 802.1X supplicant profile:
switch # show dot1x supplicant
Interface: Ethernet6/1
Identity: arastra
EAP method: fast
Status: success
Supplicant MAC: 44:4c:a8:34:bf:20
Authenticator MAC: 00:1c:73:e0:d3:76EOS supports this feature on all MACsec capable cards except the 7500E-6CFPX-LC.
The MACsec Fallback to Unprotected Traffic feature is configured under MACsec profile mode using the traffic unprotected allow command. The no form of the command removes the configuration from the switch. This configuration must be present in both the peers for the unprotected traffic to flow between them successfully.
switch(config-mac-security-profile-sampleProfile)# no traffic unprotected allowConfigure the Secure Channel Identifier (SCI) as part of a MACsec profile using the sci command. The no form of the command removes the configuration from the switch.
The sci command adds a Secure Channel Identifier (SCI) in data packets for MACsec on the switch. Each MACsec device has a Secure Channel (SC) used to send traffic to other device. Each channel has an 8-byte Secure Channel Identifier (SCI). The first 6 bytes match the MAC address of the device transmitting through that channel. The remaining 2 bytes are a Port Identifier used to distinguish between multiple channels from the same device.
switch(config)# mac security
switch(config-mac-security)# profile Macsec_office
switch(config-mac-security-profile-Macsec_office)# sci
switch(config-mac-security-profile-Macsec_office)#The following sections provide information about MACsec on a switch.
The show mac security interface command shows information about the MACsec on the interface.
switch# show mac security interface
Interface SCI Controlled Port Key in Use
Ethernet4/1/1 28:99:3a:82:6f:82::605 True 9d5bc0d3076ea4a08b99b9d9:1
Ethernet4/3/1 28:99:3a:82:6f:85::613 True 9d5bc0d3076ea4a08b99b9d9:1Use the show mac security interface detail command to display detailed information about MACsec.
Example
switch# show mac security interface detail
Interface: Ethernet4/1/1
SCI: 28:99:3a:82:6f:82::605
SSCI: 00000002
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Protected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)
Interface: Ethernet4/3/1
SCI: 28:99:3a:82:6f:85::613
SSCI: 00000001
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Protected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)Use the show mac security participants command to display information about the MACsec participants.
switch# show mac security participants
Interface: Ethernet4/1/1
CKN: abcd
Message ID: 9d5bc0d3076ea4a08b99b9d9
Elected self: True
Success: True
Principal: True
Default: False
CKN: dead
Message ID: 4ef4cf009161bd551b5e7434
Elected self: True
Success: True
Principal: False
Default: True
Interface: Ethernet4/3/1
CKN: abcd
Message ID: c79ad8882c2dd3a8e838a691
Elected self: False
Success: True
Principal: True
Default: False
CKN: dead
Message ID: 3dfd4486b5f68a81014a37ec
Elected self: False
Success: True
Principal: False
Default: TrueUse the show mac security participants detail command to display detailed information about the MACsec participants.
Example
switch# show mac security participants detail
Interface: Ethernet4/1/1
CKN: abcd
Message ID: 9d5bc0d3076ea4a08b99b9d9
Elected self: True
Success: True
Principal: True
Default: False
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: True
LLPN exhaustion: 0
Distributed key identifier: 9d5bc0d3076ea4a08b99b9d9:1
Live peer list: ['c79ad8882c2dd3a8e838a691']
Potential peer list: []
CKN: dead
Message ID: 4ef4cf009161bd551b5e7434
Elected self: True
Success: True
Principal: False
Default: True
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: False
LLPN exhaustion: 0
Distributed key identifier: None
Live peer list: ['3dfd4486b5f68a81014a37ec']
Potential peer list: []
Interface: Ethernet4/3/1
CKN: abcd
Message ID: c79ad8882c2dd3a8e838a691
Elected self: False
Success: True
Principal: True
Default: False
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: True
LLPN exhaustion: 0
Distributed key identifier: 9d5bc0d3076ea4a08b99b9d9:1
Live peer list: ['9d5bc0d3076ea4a08b99b9d9']
Potential peer list: []
CKN: dead
Message ID: 3dfd4486b5f68a81014a37ec
Elected self: False
Success: True
Principal: False
Default: True
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: False
LLPN exhaustion: 0
Distributed key identifier: None
Live peer list: ['4ef4cf009161bd551b5e7434']
Potential peer list:About the Output
Use the show mac security mka counters command to display information about the MACsec MKA counters.
switch# show mac security mka counters
Interface Rx Success Rx Failure Tx Success Tx Failure
Ethernet4/1/1 287 0 288 0
Ethernet4/3/1 288 0 287 0Use the show mac security mka counters detail command to display detailed information about the MACsec MKA counters.
switch# show mac security mka counters detail
Interface: Ethernet4/1/1
Tx packet success: 290
Tx packet failure: 0
Tx invalid: 0
Rx packet success: 289
Rx packet failure: 0
Rx invalid: 0
Rx eapol error: 0
Rx basic parameter set error: 0
Rx unrecognized CKN error: 0
Rx ICV validation error: 0
Rx live peer list error: 0
Rx potential peer list error: 0
Rx SAK use set error: 0
Rx distributed SAK set error: 0
Rx distributed CAK set error: 0
Rx ICV Indicator error: 0
Rx unrecognized parameter set error: 0
Interface: Ethernet4/3/1
Tx packet success: 289
Tx packet failure: 0
Tx invalid: 0
Rx packet success: 290
Rx packet failure: 0
Rx invalid: 0
Rx eapol error: 0
Rx basic parameter set error: 0
Rx unrecognized CKN error: 0
Rx ICV validation error: 0
Rx live peer list error: 0
Rx potential peer list error: 0
Rx SAK use set error: 0
Rx distributed SAK set error: 0
Rx distributed CAK set error: 0
Rx ICV Indicator error: 0
Rx unrecognized parameter set error: 0Use the show mac security counters command to display information about the MACsec security counters.
switch# show mac security counters
Port InPktsDecrypted InOctetsDecrypted OutPktsEncrypted OutOctetsEncrypted
Et4/1/1 2 214 109 11663
Et4/3/1 109 11663 2 214Use the show mac security counters detail command to display detailed information about the MACsec security counters.
switch# show mac security counters detail
Ethernet4/1/1 Counter Name Count
-------------------------------------------------------
outPktsEncrypted 112
outOctetsEncrypted 11984
outPktsUntagged 0
outPktsTooLong 0
outPktCtrl 224
inPktsDecrypted 2
inOctetsDecrypted 214
inPktsUnchecked 0
inPktsOK 2
inPktsNotValid 0
inPktsNotUsingSA 0
inPktsCtrl 223
inPktsNoTag 8
inPktsTagged 0
inPktsBadTag 0
inPktsNoSCI 0
inPktsLate 0
Ethernet4/3/1 Counter Name Count
-------------------------------------------------------
outPktsEncrypted 2
outOctetsEncrypted 214
outPktsUntagged 0
outPktsTooLong 0
outPktCtrl 223
inPktsDecrypted 111
inOctetsDecrypted 11877
inPktsUnchecked 0
inPktsOK 111
inPktsNotValid 0
inPktsNotUsingSA 0
inPktsCtrl 224
inPktsNoTag 9
inPktsTagged 0
inPktsBadTag 0
inPktsNoSCI 0
inPktsLate 0Use the show mac sec status command to display information about the MACsec FIPS status.
switch(config)# mac security
switch(config-mac-security)# show mac sec status
Active Profiles: 1
FIPS Mode: Yes
Secured Interfaces: 2In MAC Security configuration mode, the show active command displays the MAC security key source. If one or more static SAKs are configured, this key source will be shown as "key source sak static."
With a static SAK configured, the show mac security interface command shows the association numbers for SAKs which are programmed for Rx and Tx. Show commands never display actual SAK values.
If a unidirectional link is configured with a static SAK, the Rx side will show the SCI as "00:00:00:00:00:00::0," and only the Rx AN will be shown. On the Tx side, the configured SCI and Tx AN will be shown.
If one or more SAKs are configured in the switch, the show mac security sak command will show SAK-related details.
The MACsec configures two keys for MKA negotiation: Primary and Fallback (as a backup). For a given MAC security profile configured on an interface, an actor is created per key and is responsible for MKA negotiation with the other peer. After configuring a new primary key, the old primary key actor is retained in the system until the MKA session succeeds with the configured new primary key. The same holds for the fallback key. Using the key retirement immediate command immediately removes the actor corresponding to the old key, be it primary or fallback, from the system.
MACsec EAP-FAST Support
When using Dynamic MAC Security keys with key retirement immediate, then with every new primary key derived from 802.1X, the system deletes the old primary key actor. This action usually happens based on the reauth time interval configuration for 802.1X.
MACsec Fallback to Unprotected Traffic Support
The key retirement immediate is configured with the Fallback to Unprotected Traffic feature, and the transition between unprotected and protected traffic may become more frequent. This is because with the Key Retirement Immediate feature, whenever a new key is configured, existing successful MKA sessions corresponding to the old key are not maintained, which might bring down the number of successful MKA sessions to zero, eventually moving the interface to an unprotected traffic state as per the Fallback to Unprotected Traffic feature functionality.
The show dot1x supplicant command is configured in the mac security profile mode. The configuration must be present on both key server and non-key server peers. Since the key server decides the principal actor for SAK distribution, it is recommended that this configuration be present in the key server to trigger the re-election of the principal actor immediately.
If key retirement immediate is configured only on the key server, the non-key server will still try to negotiate MKA over the old primary key, unnecessarily utilizing some system resources and some time even when not required.
switch(config-mac-security-profile-sampleProfile)# [no] key retirement immediateConfiguring both Primary Key and Fallback Key without configuring key retirement immediate: When configuring a new primary, the actor corresponding to the old actor stays active until the MKA session succeeds on the new primary. With key retirement immediate, the system immediately deletes the actor corresponding to the old primary. Since Fallback is also configured, the key server will choose it as the new principal actor if it is eligible. After choosing a new principal actor, a new SAK is distributed, which will eventually be programmed and used for encryption and decryption.
When only the Primary Key is configured, the behavior is the same as described earlier, except no other actor will become principal until the new primary becomes successful. Until then, hardware will continue to use SAK generated with the old primary.
When the Fallback is a Principal actor and configured without immediate key retirement, when configuring a new fallback key, the old Fallback will stay in the system until the new Fallback becomes active or the primary becomes active. With immediate key retirement, the system deletes the fallback actor immediately. Until a new principal actor is elected, hardware will continue to use SAK generated with the old Fallback.
The show mac security participants command shows all the participants present in the system. When key retirement immediate is configured, the actor corresponding to old keys will no longer appear in the command output.
The Media Access Control Security (MACsec) with static keys feature supports dynamic Mac Security keys. Configure both peers for 802.1X authentication to derive Mac Security keys dynamically. Configure one peer as the Authenticator and the other peer as the Supplicant.
Upon a successful 802.1X authentication sequence between the peers, both the Authenticator and the Supplicant generate keying material. This keying material is then used to derive Mac Security keys to establish a MACsec Key Agreement (MKA) protocol session. This feature supports Arista devices acting as the Supplicant to derive Mac Security keys bidirectionally.
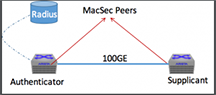
EOS supports this feature on all MACsec capable cards except the 7500E-6CFPX-LC.
The MACsec Fallback to Unprotected Traffic feature is configured under MACsec profile mode using the traffic unprotected allow command. The no form of the command removes the configuration from the switch. This configuration must be present in both the peers for the unprotected traffic to flow between them successfully.
switch(config-mac-security-profile-sampleProfile)# no traffic unprotected allowswitch# show mac security interface Ethernet 6/1/1 detail
Interface: Ethernet4/1/1
SCI: 28:99:3a:82:6f:82::605
SSCI: 00000002
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Unprotected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)
Interface: Ethernet4/3/1
SCI: 28:99:3a:82:6f:85::613
SSCI: 00000001
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Protected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)
Command Mode
MAC Security Profile SAK Static Secure Channel Configuration
Command Syntax
an an_number key key_type key_string
no an an_number
default an an_number
switch(config)# mac security
switch(config-mac-security)# profile test
switch(config-mac-security-profile-test)# key source sak static
switch(config-mac-security-profile-test-sak-static)# secure channel rx
switch(config-mac-security-profile-test-sak-static-rx)# an 1 key 0 11112222333344445555666677778888
switch(config-mac-security-profile-test-sak-static-rx)#The cipher command configures the cipher authentication for MAC security on the switch.
Command Mode
MACsec Profile
Command Syntax
cipher encryption_standard
Parameters
Example
switch(config-mac-security-profile-test)# cipher aes128-gcm-xpn
switch(config-mac-security-profile-test)#The dot1x pae supplicant command applies the supplicant profile by enabling it on the Mac Security interface.
Command Mode
Interface Configuration
Command Syntax
dot1x pae supplicant
Example
switch(config-if-Et6/1)# dot1x pae supplicant testThe dot1x timeout reauth-timeout-ignore always command retains the current port state without blocking it, irrespective of when the authentication server is unreachable or in case of supplicant timeouts.
Command Mode
Interface Configuration
Command Syntax
dot1x timeout reauth-timeout-ignore always
Example
switch(config-if-Et6/1)# dot1x timeout reauth-timeout-ignore alwaysThe dot1x command places the switch in the dot1x mode. In this mode, the user is allowed to configure various MACsec configurations.
Command Mode
Global Configuration
Command Syntax
dot1x
Example
switch(config)# dot1x
switch(config-dot1x)#In Arista EOS, Media Access Control Security (MACsec, IEEE 802.1AE) uses the MACsec Key Agreement (MKA) protocol to discover peers, negotiate security keys, and manage live sessions. EOS encapsulates MKA protocol data units (MKPDUs)inside EAPoL (Extensible Authentication Protocol over LAN) frames.
By default, EOS sends the EAPoL frames using the standard IEEE 802.1X link-local multicast MAC address (0180.c200.0003). However, in WAN MACsec scenarios, such as deploying MACsec over provider-managed Metro Ethernet, E-Line, or dark fiber networks, intermediate carrier devices often intercept, process, or entirely drop well-known link-local multicast addresses.
The eapol destination-mac command in the MAC Security Configuration Mode allows you to alter the destination MAC address of these protocol frames. By shifting to a non-reserved multicast address, a custom provider-assigned address, or a broadcast address, the EAPoL frames can pass transparently across the service provider infrastructure to reach the remote MACsec peer.
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
MAC Security Configuration
Command Syntax
eapol mac destination mac_address
no eapol mac destination
default eapol mac destination
Example
switch(config)# mac security
switch(config-mac-sec)# eapol mac destination 0100.0ccc.ccfd
switch(config-mac-sec)#The entropy source hardware command generates the cryptographic keys to strengthen the random number generator used by MACsec.
Command Mode
Management Configuration
Command Syntax
entropy source hardware
Example
switch(config)# management security
switch(config-mgmt-security)# entropy source hardwareIn Arista EOS, Federal Information Processing Standards (FIPS) mode dictates the cryptographic boundaries used to secure the system. When dealing with MACsec (Media Access Control Security), enabling FIPS mode forces the MACsec Key Agreement (MKA) protocol and data plane encryption to adhere strictly to FIPS-approved cryptographic algorithms and key strengths.
The no version of the command disables the feature and removes the configuration from the running-config.
Command Mode
MAC Security Configuration
Command Syntax
fips restrictions
no fips restrictions
Example
switch(config)# mac security
switch(config-mac-security)# fips restrictions
switch(config-mac-security)#
Command Mode
MAC Security Profile SAK Static Secure Channel Configuration
Command Syntax
identifier MAC_address
no identifier
default identifier
Parameter
MAC_address The MAC address identifying the secure channel.
switch(config)# mac security
switch(config-mac-security)# profile test
switch(config-mac-security-profile-test)# key source sak static
switch(config-mac-security-profile-test-sak-static)# secure channel rx
switch(config-mac-security-profile-test-sak-static-rx)# identifier 01:02:03:04:05:06::1234
switch(config-mac-security-profile-test-sak-static-rx)#The key command configuresthe primary key to activate the MACsec profile
Command Mode
MACsec Profile Configuration
Command Syntax
key <options>
switch(config)# mac security
switch(config-mac-security)# profile sample_Profile
switch(config-mac-security-profile-sample_Profile)# key 0abcd1 0 1234abcdswitch(config)# mac security
switch(config-mac-security)# profile sample_Profile
switch(config-mac-security-profile-sample_Profile)# key 0abcd1 0 1234abcd fallbackThe key retirement immediate command configures the key retirement feature on the key server and assists the key server to decide the principal actor for SAK distribution by triggering the re-election of principal actor immediately. It is recommended that the key retirement is configured on both key server and non key server peers.
The no key retirement immediate command disable the key retirement function by removing the key retirement immediate command from the running-config.
Command Mode
MACsec Profile
Command Syntax
key retirement immediate
Example
switch(config)# mac security
switch(config-mac-security)# profile sample
switch(config-mac-security-profile-sample)# key retirement immediateThe license command configures EOS licenses on the switch under the global configuration mode. These licenses include the MACsec license.
Command Mode
Global Configuration
Command Syntax
license [[import URL] | update]
Example
switch# license import flash:EOSLic-1.json
switch#The license command configures the MACsec license on the switch under the MAC Security configuration mode using a hex key.
The no license and default license commands delete the current license from running-config.
Command Mode
MAC Security
Command Syntax
license licensee_name license_value
Example
switch(config)# mac security
switch(config-mac-security)# license Test-LICNC AABBCCDD
switch(config-mac-security)#The command l2-protocol configures the Layer 2 protocol processing for MACsec. The no l2-protocol and the default l2-protocol remove the command from the configuration.
Command Mode
MAC Security Configuration
Command Syntax
l2-protocol ethernet-flow-control [bypass | encrypt]
no l2-protocol ethernet-flow-control [bypass | encrypt]
default l2-protocol ethernet-flow-control [bypass | encrypt]
Example
switch(config)# mac-security
switch(config-mac-security)# l2 protocol ethernet-flow-control bypassThe mac security command enables MAC security provision on the switch.
The no mac security and default mac security commands restore the switch to its default state by removing the corresponding mac security command from running-config.
Command Mode
Global Configuration
Command Syntax
mac security
no mac security
default mac security
Example
switch(config)# mac security
switch(config-mac-security)#The mac security profile command applies a MACsec profile to an interface or subinterface.
The no mac security profile and default mac security profile commands remove the MACsec profile, disabling MACsec on the configuration-mode interface.
Command Mode
Interface Ethernet Configuration Mode
Command Syntax
mac security profile profile-name
no mac security profile profile-name
default mac security profile profile-name
Parameter
profile-name the MACsec profile name.
Example
switch(config)# interface ethernet1
switch(config-if-Et1)# no switchport
switch(config-if-Et1)# interface ethernet1.10
switch(config-if-Et1.10)# encapsulation dot1q vlan 20
switch(config-if-Et1.10)# mac security profile test-profileThe mka key-server command configures key server among the MACsec peers.
Command Mode
MACsec Profile Configuration
Command Syntax
mka key-server [priority value]
Example
switch(config)# mac security
switch(config-mac-security)# profile sample_Profile
switch(config-mac-security-sample_Profile)# mka key-server priority 10The mka session command configures period at which the SAK is refreshed .
Command Mode
MACsec Profile Configuration
Command Syntax
mka session [rekey-period value]
Example
switch(config)# mac security
switch(config-mac-security)# profile sample_Profile
switch(config-mac-security-sample_Profile)# mka session rekey-period 10The profile command places the switch in MAC Security Profile configuration mode and creates a MACsec profile if a profile of the specified name does not already exist. MACsec profiles contain the configuration information needed to establish a MACsec connection, and are applied to interfaces using the mac security profile command.
Command Mode
MAC Security Configuration
Command Syntax
profile profile-name
Parameter
profile-name Name of the MACsec profile.
Example
switch(config)# mac security
switch(config-mac-security)# profile test
switch(config-mac-security-profile-test)#The ptp bypass command in the MAC Security Configuration Mode establishing a PTP MACsec Bypass and skips the encryption and integrity checks for PTP data plane frames. PTP traffic transmits in the clear, allowing the PHY to perform precise hardware timestamping and maintain sub-microsecond synchronization across a link otherwise fully encrypted.
The no version of the command disables the feature and removes the configuration from the running-config.
Command Mode
MAC Security Configuration
Command Syntax
ptp bypass
no ptp bypass
Example
switch(config)# mac security
switch(config-mac-security)# ptp bypass
switch(config-mac-security)#The replay command configures the action to be taken when packets received are not in order, based on their packet numbers. The window size in replay protection specifies the window size within which out-of-order packets are allowed. This command is configured under the MACsec Profile configuration mode.
The no and default form of the command removes all the configurations related to replay command from the running configuration on the switch.
Command Mode
MACsec Profile
Command Syntax
replay protection {disabled | window window_size}
no replay protection {disabled | window window_size}
default replay protection {disabled | window window_size}
Example
switch(config)# mac security
switch(config-mac-security)# profile TEST
switch(config-mac-security-profile-TEST)# replay protection window 100The sci command add a Secure Channel Identifier (SCI) in data packets for MACsec on the switch. Each MACsec device has a Secure Channel (SC) used to send traffic to other device. Each channel has an 8-byte Secure Channel Identifier (SCI). The first 6 bytes match the MAC address of the device transmitting through that channel. The remaining 2 bytes are a Port Identifier used to distinguish between multiple channels from the same device. The command is configured under the MACsec profile configuration mode.
Command Mode
MACsec Profile
Command Syntax
sci
Example
switch(config)# mac security
switch(config-mac-security)# profile TEST
switch(config-mac-security-profile-TEST)# sci
Command Mode
MAC Security Profile Static SAK Configuration Mode
Command Syntax
secure channel {Rx|Tx}
Example
switch(config)# mac security
switch(config-mac-security)# profile test
switch(config-mac-security-profile-test)# key source sak static
switch(config-mac-security-profile-test-sak-static)# secure channel tx
switch(config-mac-security-profile-test-sak-static-sc-tx)#The show dot1x supplicant command displays the 802.1X supplicant status.
Command Mode
EXEC
Command Syntax
show dot1x supplicant
Example
switch# show dot1x supplicant
Interface: Ethernet6/1
Identity: arastra
EAP method: fast
Status: success
Supplicant MAC: 44:4c:a8:34:bf:20
Authenticator MAC: 00:1c:73:e0:d3:76The show mac security counters command to displays information about the MACsec security counters.
Command Mode
EXEC
Command Syntax
show mac security counters
Example
switch# show mac security counters Port InPktsDecryptedInOctetsDecryptedOutPktsEncrypted OutOctetsEncrypted Et4/1/12214 10911663 Et4/3/110911663 2214
The show mac security counters detail command to displays the detail information about the MACsec security counters.
Command Mode
EXEC
Command Syntax
show mac security counters detail
Example
switch# show mac security counters detail Ethernet4/1/1 Counter NameCount ------------------------------------------------------- outPktsEncrypted112 outOctetsEncrypted11984 outPktsUntagged 0 outPktsTooLong0 outPktCtrl224 inPktsDecrypted 2 inOctetsDecrypted 214 inPktsUnchecked 0 inPktsOK2 inPktsNotValid0 inPktsNotUsingSA0 inPktsCtrl223 inPktsNoTag 8 inPktsTagged0 inPktsBadTag0 inPktsNoSCI 0 inPktsLate0 Ethernet4/3/1 Counter NameCount ------------------------------------------------------- outPktsEncrypted2 outOctetsEncrypted214 outPktsUntagged 0 outPktsTooLong0 outPktCtrl223 inPktsDecrypted 111 inOctetsDecrypted 11877 inPktsUnchecked 0 inPktsOK111 inPktsNotValid0 inPktsNotUsingSA0 inPktsCtrl224 inPktsNoTag 9 inPktsTagged0 inPktsBadTag0 inPktsNoSCI 0 inPktsLate0
The show mac security interface command shows information aboutMACsec on the interface.
Command Mode
EXEC
Command Syntax
show mac security interface
switch# show mac security interface
Interface SCI Controlled Port Key in Use
Ethernet4/1/1 28:99:3a:82:6f:82::605 True 9d5bc0d3076ea4a08b99b9d9:1
Ethernet4/3/1 28:99:3a:82:6f:85::613 True 9d5bc0d3076ea4a08b99b9d9:1
switch#switch# show mac security interface
Interface SCI Controlled Port Key in Use
Ethernet9/1 01:02:03:04:05:06::1235 True static SAK: Rx AN: 0,1 Tx AN: 0
switch#switch# show mac security interface
Interface SCI Controlled Port Key in Use
Ethernet9/1 00:00:00:00:00:00::0000 True static SAK: Rx AN: 0
switch#switch(config)# show mac security interface
Interface SCI Controlled Port Key in Use
Ethernet9/1 01:02:03:04:05:06::1235 True static SAK: Tx AN: 0The show mac security interface detail command displays the detail information about the MACsec on the interface.
Command Mode
EXEC
Command Syntax
show mac security interface detail
Example
switch# show mac security interface detail
Interface: Ethernet4/1/1
SCI: 28:99:3a:82:6f:82::605
SSCI: 00000002
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Protected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)
Interface: Ethernet4/3/1
SCI: 28:99:3a:82:6f:85::613
SSCI: 00000001
Controlled port: True
Key server priority: 16
Session rekey period: 0
Traffic: Protected
Key in use: 9d5bc0d3076ea4a08b99b9d9:1
Latest key: None
Old key: 9d5bc0d3076ea4a08b99b9d9:1(RT)
Old Key: The last SAK negotiated by Mac Security Key Agreement Protocol (MKA).
The show mac security mka counters command to display information about the MACsec MKA counters.
Command Mode
EXEC
Command Syntax
show mac security mka counters
Example
switch# show mac security mka counters
Interface Rx Success Rx Failure Tx Success Tx Failure
Ethernet4/1/1 287 0 288 0
Ethernet4/3/1 288 0 287 00The show mac security participants interface command displays information about the MACsec participants.
Command Mode
EXEC
Command Syntax
show mac security interface
Example
switch# show mac security participants
Interface: Ethernet4/1/1
CKN: abcd
Message ID: 9d5bc0d3076ea4a08b99b9d9
Elected self: True
Success: True
Principal: True
Default: False
CKN: dead
Message ID: 4ef4cf009161bd551b5e7434
Elected self: True
Success: True
Principal: False
Default: True
Interface: Ethernet4/3/1
CKN: abcd
Message ID: c79ad8882c2dd3a8e838a691
Elected self: False
Success: True
Principal: True
Default: False
CKN: dead
Message ID: 3dfd4486b5f68a81014a37ec
Elected self: False
Success: True
Principal: False
Default: TrueThe show mac security participants detail command displays detail information about the MACsec participants.
Command Mode
EXEC
Command Syntax
show mac security participants detail
Example
switch# show mac security participants detail
Interface: Ethernet4/1/1
CKN: abcd
Message ID: 9d5bc0d3076ea4a08b99b9d9
Elected self: True
Success: True
Principal: True
Default: False
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: True
LLPN exhaustion: 0
Distributed key identifier: 9d5bc0d3076ea4a08b99b9d9:1
Live peer list: ['c79ad8882c2dd3a8e838a691']
Potential peer list: []
CKN: dead
Message ID: 4ef4cf009161bd551b5e7434
Elected self: True
Success: True
Principal: False
Default: True
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: False
LLPN exhaustion: 0
Distributed key identifier: None
Live peer list: ['3dfd4486b5f68a81014a37ec']
Potential peer list: []
Interface: Ethernet4/3/1
CKN: abcd
Message ID: c79ad8882c2dd3a8e838a691
Elected self: False
Success: True
Principal: True
Default: False
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: True
LLPN exhaustion: 0
Distributed key identifier: 9d5bc0d3076ea4a08b99b9d9:1
Live peer list: ['9d5bc0d3076ea4a08b99b9d9']
Potential peer list: []
CKN: dead
Message ID: 3dfd4486b5f68a81014a37ec
Elected self: False
Success: True
Principal: False
Default: True
KeyServer SCI: 28:99:3a:82:6f:82::605
SAK transmit: False
LLPN exhaustion: 0
Distributed key identifier: None
Live peer list: ['4ef4cf009161bd551b5e7434']
Potential peer list:
Command Mode
EXEC
Command Syntax
show mac security profile [profile_name]
Parameters
profile_name The MACsec profile to show information about.
Example
switch# show mac security profile
Profile: test
Cipher: aes256-gcm-xpn
Primary CKN:
Primary CAK SHA-256 hash:
Fallback CKN:
Fallback CAK SHA-256 hash:
Source: cli
Priority: 100
SCI Inclusion: disabled
Key retirement policy: delayed
Unprotected traffic policy: allow active-sak
MKA lifetime: 6 seconds
MKA key server priority: 16
Session rekey period: 0
Bypassed protocols:
Max AN value of SAK: 3
Configured on:
switch#Command Mode
EXEC
Command Syntax
show mac security sak [interface ethernet Ethernet_interface]
Parameters
interface ethernet Show SAK status information about the specified Ethernet interface. If this option is omitted, information for all Ethernet interfaces is shown.
Ethernet_interface The Ethernet interface to show SAK status for.
Example
switch(config-mac-security-profile-test)# show mac security sak
Interface: Ethernet9/1
Installed SAK ID: static SAK: Rx AN: 0,1 Tx AN: 0
Installed SAK from: static-SA
Total SAK generated: 0
SAK generated due to new live peer: 0
SAK generated due to rekey timer: 0
SAK generated due to packet number exhaustion: 0
SAK installation time( in seconds ):
Direction 0-1 1-2 2-3 3+
---------- ----- ----- ----- -----
Rx 1 0 0 0
Tx 1 0 0 0
Maximum Rx installation time: 0.0884998080001 seconds
Maximum Tx installation time: 0.0884941590002 seconds
Forced new Tx SAK installation count: 0The show mac security status command displays the MACsec status information on a switch.
Command Mode
EXEC
Command Syntax
show mac security status
Example
switch# show mac security status
Active Profiles: 1
Data Delay Protection: No
FIPS Mode: No
Secured Interfaces: 2
License: EnabledThe supplicant profile command configures the supplicant profile containing all the credentials necessary for 802.1X authentication to succeed.
Command Mode
dot1x Configuration
Command Syntax
supplicant profile profile_name options
switch(config)# dot1x
switch(config-dot1x)# supplicant profile test
switch(config-dot1x-supp-profile-test)#switch(config)# dot1x
switch(config-dot1x)# supplicant profile test
switch(config-dot1x-supp-profile-test)#eap-method fastswitch(config)# dot1x
switch(config-dot1x)# supplicant profile test
switch(config-dot1x-supp-profile-test)# identity New_Userswitch(config)# dot1x
switch(config-dot1x)# supplicant profile test
switch(config-dot1x-supp-profile-test)# passphrase 7 070E334D5D1D0B04The traffic unprotected allow command configures the switch to allow the unprotected traffic whenever there is no successful MKA session established with the peer.
The no traffic unprotected allow command disable the MACsec Fallback to Unprotected Traffic function by removing the traffic unprotected allow command from running-config.
Command Mode
MACsec Profile
Command Syntax
traffic unprotected allow
no traffic unprotected allow
Example
switch(config)# mac security
switch(config-mac-security)# profile sample
switch(config-mac-security-profile-sample)# no traffic unprotected allowInternet Protocol Security (IPsec) is a protocol suite for securing Internet Protocol (IP) communications by authenticating and encrypting each IP packet of a communication session. IPsec includes protocols for establishing mutual authentication between agents periodically during the session and negotiation of cryptographic keys to be used during the session. IPsec supports network-level peer authentication, data origin authentication, data integrity, data confidentiality (encryption), and replay protection.
IPsec protects data traffic between sites, such as between an enterprise's Branch, HQ, and Data center sites.
Security Associations (SA) provide the bundle of algorithms and data that provide the parameters necessary for AH and ESP operations. The Internet Security Association and Key Management Protocol (ISAKMP) provides a framework for authentication and key exchange, with actual authenticated keying material provided by manual configuration with pre-shared keys, Internet Key Exchange (IKE and IKEv2), and other mechanisms.
IPsec uses the Security Parameter Index (SPI) and the destination address in the packet header to determine the necessary protection for an outgoing packet. The SPI is an index to the security association database (SADB). The SPI uniquely identifies a security association for the packet in combination with the destination address.
The system performs a similar procedure for an incoming packet, where IPsec gathers decryption and verification keys from the security association database.
IPsec on Arista switches operates in tunnel mode. In tunnel mode, the entire IP packet is encrypted and authenticated, then encapsulated into a new IP packet with a new IP header.
IPsec uses tunnel mode to create virtual private networks (VPN) for network-to-network communications, such as secure connections between routers across different sites. Tunnel mode serves as the foundation for the majority of network-to-network IPsec implementations.
Key management on Arista switches uses the Internet Key Exchange (IKE) method. Internet Key Exchange (IKE) supports automated generation and renegotiation of SAs (includes keys) between the devices at a configured interval, making it much more scalable and secure.
IPsec needs SAs to define the algorithms and keys to protect traffic. IKE establishes the SA so IPsec can protect traffic.
There are two IKE versions, IKEv1 and IKEv2. IKEv2 builds on IKEv1, but both are still widely used today.
IKE initially performs a Diffie-Hellman (DH) exchange at the start of the IKE session. A Diffie-Hellman (DH) exchange allows participants to produce a shared secret value. The strength of the technique is that it allows participants to create the secret value over an unsecured medium without passing the secret value through the wire. From that exchange, peers get shared keying material, which is then used for IKE encryption and integrity functions. The strength of that keying material is that it can be used for faster performance by choosing lower key sizes for Diffie-Hellman exchanges. Diffie-Hellman exchanges' key length (strength) can be changed using different DH groups.
When an IKE session's lifetime expires, a new Diffie-Hellman exchange is performed between peers, and the IKE SA is re-established.
The key material for IPsec SA (also called Child SA) is derived from keying material from IKEv1 phase 1.
EOS provides a restriction on the combinations of IKE and IPSec algorithms used for a security combination.
| Algorithm | Description |
|---|---|
| 3des | Three key triple DES |
| aes128 | 128-bit Advanced Encryption Standard |
| aes192 | 192-bit Advanced Encryption Standard |
| aes256 | 256-bit Advanced Encryption Standard |
| Algorithm | Description |
|---|---|
| 3des | Three key triple DES |
| aes128 | 128-bit Advanced Encryption Standard |
| aes128gcm128 | 128-bit Advanced Encryption Standard-Galois/Counter Mode (AES-GCM) with 128-bit Integrity Check Value (ICV) |
| aes128gcm64 | 128-bit Advanced Encryption Standard-Galois/Counter Mode (AES-GCM) with 64-bit Integrity Check Value (ICV) |
| aes256 | 256-bit Advanced Encryption Standard |
| aes256gcm128 | 256-bit Advanced Encryption Standard-Galois/Counter Mode (AES-GCM) with 128-bit Integrity Check Value (ICV) |
| null | Null encryption |
| Algorithm | Key Size |
|---|---|
| 3des | 168 bits |
| aes128/aes128gcm64/aes128/gcm128 | 128 bits |
| aes192 | 192 bits |
| aes256 / aes256gcm128 | 256 bits |
| null | 0 bits |
| IKE Algorithm | IPSec Algorithm |
|---|---|
| 3des | 3des, null |
| aes128 | 3des, aes128, aes128gcm64, aes128gcm128, null |
| aes192 | 3des, aes128, aes128gcm64, aes128gcm128, null |
| aes256 | 3des, aes128, aes128gcm64, aes128gcm128, aes256, aes256gcm128, null |
switch(config)# ip security
switch(config-ipsec)# encryption key-length aligned
switch(config-ipsec)#By default, EOS disables key length checking for IKE and IPSec. All new and existing sessions work as expect. When enabled, all new sessions undergo key length checking and existing sessions reset and undergo re-evaluation for the key length. Only sessions that adhere to the key length restrictions return to an active status.
switch# show ip security connection
Legend: (P) policy based VPN tunnel
Tunnel Source Dest Status Uptime Input Output Rekey Time
Tunnel152 10.1.0.1 10.1.0.2 NotKeyLenAligned N/A 0 bytes 0 bytes 41 minutes
0 pkts 0 pktsswitch# show ip security encryption key-length status
Key length alignment: disabledA route-based VPN employs routed tunnel interfaces as the virtual network's endpoints. All traffic passing through a tunnel interface traverses the VPN. Rather than relying on an explicit policy to dictate which traffic enters the VPN, static and dynamic IP routes are formed to direct the desired traffic through the VPN tunnel interface.
Since route-based VPNs support dynamic routing information through VPN tunnels, EOS supports only route-based VPNs for dynamic routing support and easier configuration and management.
In route-based VPN, features like NAT, ACL, and QoS are applied to packets before they are encrypted by applying these features to the tunnel interface and can be applied to encrypted packets by applying these features on the physical interface carrying the tunnel traffic.
A new tunnel interface type, vti, represents the VPN tunnel. This tunnel interface will participate in the routing, and any packets forwarded to it will be encrypted and forwarded to the other end of the tunnel. Note that this does not add a new header to the packet.
This configuration uses the default IKE version 2 procedure.
switch# show ip security policy
Policy Name Authentication Encryption Integrity Lifetime Rekey DH Group
ike-policy Pre-shared 256-bit AES 256bit Hash 8 hours False 3072 bitswitch# show ip security profile
Profile name IKE Policy Name SA
ipsec-profile ike-policy sa-policy Configure PKI as a certificate-based authentication for the IPsec protocol.
Configure the authentication mode as PKI for the IKE policy. The IPsec refers to this policy when using PKI authentication.
switch(config)# ip security
switch(config-ipsec)# ike policy MyPolicy
switch(config-ipsec)# authentication pki
switch(config-ipsec)# exit
switch(config-ipsec)# show active
ip security
ike policy MyPolicy
authentication pki
switch(config)# ip security
switch(config-ipsec)# profile MyProfile
switch(config-ipsec)# pki-profile pki-abc
switch(config-ipsec)# ike-profile MyPKI
switch(config-ipsec)# exit
switch(config-ipsec)# show active
profile MyProfile
...
ike-policy MyPKI
pki-profile pki-abc
...
!switch# show ip security policy
Policy Name Authentication Crypto Suite Encryption Integrity Lifetime Rekey DH Group
----------- -------------- ------------ ---------- --------- -------- ----- --------
a Pre-shared - 128-bit AES 256bit Hash 8 hours False 3072 bit
MyPKI PKI - 128-bit AES 256bit Hash 8 hours False 3072 bitswitch# show ip security profile
Profile name IKE Policy Name SA PKI Profile
------------- ----------------- --------- ------------
MyPKI ike-xyz sa-xyz pki-xyzThe ike policy command configures the Internet Security Association and Key Management Protocol on the switch and related policies. Configure the IKE policy in IP security configuration mode.
The no ike policy command deletes the IKE policy configuration from the switch.
The exit command returns the switch to the global configuration mode.
Command Mode
IP Security Configuration
Command Syntax
ike policy policy-name
no ike policy policy-name
Example
switch(config)# ip security
switch(config-ipsec)# ike policy MyIKEPolicy
switch(config-ipsec)#The interface tunnel command places the switch in the Interface Tunnel Configuration Mode.
Interface tunnel configuration mode does not provide a group change mode. The running-config changes immediately after executing the commands.
The no interface tunnel command deletes the interface tunnel configuration.
The exit command returns the switch to the global configuration mode.
Command Mode
Global Configuration
Command Syntax
interface tunnel value
no interface tunnel value
Parameter
value - Specify the tunnel interface number. The value ranges from 0 to 255.
Example
switch(config)# interface tunnel 10
switch(config-if-Tu10)#The ip security command places the switch in the IP Security Configuration Mode.
IP security configuration mode is not a group change mode. The running-config changes immediately after executing the commands.
The no ip security command deletes the IP security configuration.
The exit command returns the switch to the global configuration mode.
Command Mode
Global Configuration
Command Syntax
ip security
no ip security
Example
switch(config)# ip security
switch(config-ipsec)# ike policy IKE1
switch(config-ipsec-IKE1)# exit
switch(config-ipsec)# sa policy SA1
switch(config-SA1)#The ip security encryption key-length command in the IP Security Configuration Mode enables key-length checking for IKE and IPSec algorithms.
The [no | default] versions of the command disables the feature and removes it from the running-config.
Command Mode
IP Security Configuration
Command Syntax
ip security encryption key-length aligned
no ip security encryption key-length
default ip security encryption key-length
Parameters
encryption key-length aligned - Align IKE and IPSec encryption keys.
Example
switch(config)# ip security
switch(config-ip-sec)# encryption key-length aligned
switch(config-ip-sec)#The profile command configures the IP security profile on the switch. Configure the profile in IP security configuration mode.
The no profile command deletes the IP security profile configuration from the switch.
The exit command returns the switch to the global configuration mode.
Command Mode
IP Security Configuration
Command Syntax
profile profile-name
no profile profile-name
Parameters
profile-name Specifies the IP security profile name.
Example
switch(config)# ip security
switch(config-ipsec)# profile test
switch(config-ipsec-profile)#The sa policy command specifies a Security Association (SA) policy used for IPsec configuration, and enters IP security SA policy configuration mode to configure the named policy.
The no sa policy command deletes the specified SA policy configuration from the switch.
The exit command returns the switch to the global configuration mode.
Command Mode
IP Security Configuration
Command Syntax
sa policy policy_name
no sa policy policy_name
Parameters
policy_name - Specifies the SA policy name.
Example
switch(config)# sa policy test
switch(config-ipsec-sa)# sa lifetime 30 minutesThe show ip security applied-profile command displays the IP security profile names and the corresponding interfaces with the profile.
Command Mode
EXEC
Command Syntax
show ip security applied-profile
Example
switch# show ip sec applied-profile
Profile Name Interface
ipsec-profile-1 Tunnel1,
Tunnel2,
Tunnel3,
Tunnel4,
Tunnel5,
Tunnel6,
Tunnel7,
Tunnel8,
Tunnel9,
Tunnel10,
Tunnel11,
Tunnel12,
Tunnel13,
Tunnel14,
Tunnel15,
Tunnel16,
Tunnel17,
Tunnel18,
Tunnel19,
Tunnel20,
Tunnel21,
Tunnel22,
Tunnel23,
Tunnel24,
Tunnel25,
Tunnel26,The show ip security connection command displays the IP security connection status information.
Command Mode
EXEC
Command Syntax
show ip security connection
Example
switch# show ip sec conn tunnel 1
Tunnel Source Dest Status Uptime Input Output Rekey Time
Tunnel1 11.1.1.1 11.2.1.1 Established 19 hours 0 bytes 0 bytes 4 hours
0 pkts 62937679 pkts
switch# show ip sec conn tunnel 1 detail
Tunnel1:
source address 11.1.1.1, dest address 11.2.1.1
state: Established
uptime: 19 hours, 7 minutes, 23 seconds
Inbound SPI 0xca5560f4:
request id 193, mode tunnel replay-window 16384, seq 0x0
stats errors:
replay-window 0, replay 0, integrity_failed 0
lifetime config:
softlimit 4534352933249 bytes, hardlimit 6442450944000 bytes
softlimit 2077499095 pkts, hardlimit 4000000000 pkts
expire add soft 85619 secs, hard 86400 secs
lifetime current:
0 bytes, 0 pkts
add time Mon May 13 17:33:54 2019, use time Mon May 13 17:33:54 2019
Outbound SPI 0xc60da749:
request id 193, mode tunnel replay-window 16384, seq 0x0
stats errors:
replay-window 0, replay 0, integrity_failed 0
lifetime config:
softlimit 3286021368749 bytes, hardlimit 6442450944000 bytes
softlimit 2480571031 pkts, hardlimit 4000000000 pkts
expire add soft 85418 secs, hard 86400 secs
lifetime current:
0 bytes, 62937679 pkts
add time Mon May 13 17:33:54 2019, use time Mon May 13 18:06:42 2019The show ip security encryption command displays the IP security encryption status information.
Command Mode
EXEC
Command Syntax
show ip security encryption key-length status
Example
switch# show ip security encryption key-length status
Key length alignment: disabledThe show ip security policy command displays the IP security policy information.
Command Mode
EXEC
Command Syntax
show ip security policy
Example
switch# show ip security policy
Policy Name Authentication Encryption Integrity Lifetime Rekey DH Group
ike-policy Pre-shared 256-bit AES 256bit Hash 8 hours False 3072 bitThe show ip security profile command displays the IP security profile information.
Command Mode
EXEC
Command Syntax
show ip security profile
Example
switch# show ip security profile
Profile name IKE Policy Name SA
ipsec-profile ike-policy sa-policyThe show ip security security-association command displays the IP security SA information.
Command Mode
EXEC
Command Syntax
show ip security security-association
Example
switch# show ip sec security-association
SA Name ESP Encryption ESP Integrity Lifetime PFS Group
sa-policy-1 256-bit AES 256bit Hash 24 hours 2k bitArista Macro-Segmentation Service (MSS) is a CloudVision-based service that supports the integration of vendor firewalls with the Arista network fabric.
The advent of contemporary networking features such as mobile applications and the Internet of Things (IoT) brings additional security challenges unprotected by legacy infrastructure. These security breaches cannot be handled by installing a firewall at the Internet edge. Arista Macro-Segmentation Service (MSS) addresses the security breach issue by securing access, protecting critical data, and ensuring end-user privacy.
Arista MSS provides a CloudVision-based service that provides the point of integration between individual vendor firewalls or a firewall manager and the Arista network fabric. MSS supports flexibility on where to place the service devices and workloads, Physical-to-Physical (P-to-P) and Physical-to-Virtual (P-to-V).
This scenario provides information about the role of MSS in securing network traffic between physical-to-physical (P-to-P) and physical to virtual (P-to-V) servers. Prior to MSS, network infrastructure devices followed the firewall sandwich setup where firewalls were placed in line between the security zones. This setup would impact scalability and performance of the servers.

This usage scenario demonstrates how MSS successfully monitors and secures management interfaces in the data center.


The following sections provide detailed information about MSS configuration, system requirements, recommendations, and limitations.

End users in the untrust zone access the web server through the TCP/443 port. Traffic flows through the active firewall to the web server interface in the web-untrust security zone. The web server interface in the web-trust security zone accesses the application server interface in the app-untrust security zone through port TCP/80 after traversing the firewall. From there, the application server interface in the app-trust security zone accesses the database through TCP/1433 in the db-untrust zone.
The following physical topology indicates the MSS setup.

The firewall policy name must not have any whitespace character in the name. As an example, PCI policy is an unacceptable policy name. An acceptable name would be PCI_policy.
Deploy CloudVision and configure the Arista TOR switches to connect to it. A CVX cluster of three instances with host names of cvx01, cvx02, and cvx03 are configured as an example.
Enable the VXLAN Control Service (VCS) on every CVX instance after deploying the three Arista CVX instances to manage the TOR switches.
VCS allows hardware VXLAN Tunnel End Points (VTEPs) to share state with each other in order to establish VXLAN tunnels without the need for a multicast control plane.
Example
cvx01(config-cvx)# service VXLAN
cvx01(config-cvx-VXLAN)# no shutdownSimilarly, VCS is enabled on the cvx02 and cvx03 devices.
Configure the switch ports that are connected to the hosts, whose traffic should be steered to the firewalls and the service switch ports which are connected to the firewalls.
The switch ports connected to the hosts, whose traffic needs to be intercepted, need to be configured as 802.1q trunks with the VLAN that is mapped to the VNI requiring interception. Unique VLAN IDs are configured for each tier of the application.
intercept-1# configure
intercept-1(config)# interface et10
intercept-1(config-if-Et10)# description web server
intercept-1(config-if-Et10)# switchport mode trunk
intercept-1(config-if-Et10)# switchport trunk allowed vlan 100
intercept-1(config)# interface et16
intercept-1(config-if-Et16)# description app server
intercept-1(config-if-Et16)# switchport mode trunk
intercept-1(config-if-Et16)# switchport trunk allowed vlan 200intercept-2# configure
intercept-2(config)# interface et10
intercept-2(config-if-Et1)# description db server
intercept-2(config-if-Et1)# switchport mode trunk
intercept-2(config-if-Et1)# switchport trunk allowed vlan 300service-1# configure
service-1(config)# interface port-channel 10
service-1(config-if-Po10)# description Far Interface
service-1(config-if-Po10)# switchport mode trunk
service-1(config-if-Po10)# switchport trunk allowed vlan none
service-1(config-if-Po10)# spanning-tree bpdufilter enable
service-1(config)# interface port-channel 20
service-1(config-if-Po20)# description Near Interface
service-1(config-if-Po20)# switchport mode trunk
service-1(config-if-Po20)# switchport trunk allowed vlan none
service-1(config-if-Po20)# spanning-tree bpdufilter enableArista MSS uses DirectFlow to intercept traffic while the VXLAN is used to carry tunnel traffic from the intercepted host to the firewall and back. DirectFlow should be enabled on every intercept switch as well as the service switches.
service-1# configure
service-1(config)# directflow
service-1(config-directflow)# no shutdownintercept-1# configure
intercept-1(config)# directflow
intercept-1(config-directflow)# no shutdownintercept-2# configure
intercept-2(config)# directflow
intercept-2(config-directflow)# no shutdownCVX uses Address Resolution Protocol (ARP) to determine where intercept hosts are physically located in the network. VXLAN routing should be configured on every TOR switch that will be intercepting traffic to ensure that CVX is aware of every host ARP entry.
The following configuration shows the routing configuration for each tier of the application, but not the entire VXLAN configuration. For more information on how to configure VXLAN and VXLAN routing, refer to the VXLAN section of the Arista EOS Configuration Guide.
intercept-1# configure
intercept-1(config)# ip routing
intercept-1(cofig)# interface vlan100
intercept-1(config-if-Vl100)# ip address virtual 10.0.10.254/24
intercept-1(config)# interface vlan200
intercept-1(config-if-Vl200)# ip address virtual 10.0.20.254/24
intercept-1(config)# interface vlan300
intercept-1(config-if-Vl300)# ip address virtual 10.0.30.254/24intercept-2# configure
intercept-2(config)# ip routing
intercept-2(cofig)# interface vlan100
intercept-2(config-if-Vl100)# ip address virtual 10.0.10.254/24
intercept-2(config)# interface vlan200
intercept-2(config-if-Vl200)# ip address virtual 10.0.20.254/24
intercept-2(config)# interface vlan300
intercept-2(config-if-Vl300)# ip address virtual 10.0.30.254/24service-1# configure
service-1(config)# ip routing
service-1(cofig)# interface vlan100
service-1(config-if-Vl100)# ip address virtual 10.0.10.254/24
service-1(config)# interface vlan200
service-1(config-if-Vl200)# ip address virtual 10.0.20.254/24
service-1(config)# interface vlan300
service-1(config-if-Vl300)# ip address virtual 10.0.30.254/24This step enables configuring Arista MSS on CVX. The topology diagram depicts three CVX instances in a cluster and the configuration is the same for every instance. The active and standby vendor firewalls are configured. If Panorama is used, only Panorama should be configured.
Example
In the example, the primary vendor firewall has a DNS name of fw-ha-node-1. The standby firewall has a DNS name of fw-ha-node-2. The username and password are set as admin.
cvx01# configure
cvx01(config)# cvx
cvx01(config-cvx)# no shutdown
cvx01(config-cvx)# service mss
cvx01(config-cvx-mss)# no shutdown
cvx01(config-cvx-mss)# vni range 20000-30000
cvx01(config-cvx-mss)# dynamic device-set panfw1
cvx01(config-cvx-mss-panfw1)# tag Arista_MSS
cvx01(config-cvx-mss-panfw1)# type palo-alto firewall
cvx01(config-cvx-mss-panfw1)# state active
cvx01(config-cvx-mss-panfw1)# device fw-ha-node-1
cvx01(config-cvx-mss-panfw1-fw-ha-node-1)# username admin password 0 admincvx02# configure
cvx02(config)# cvx
cvx02(config-cvx)# no shutdown
cvx02(config-cvx)# service mss
cvx02(config-cvx-mss)# no shutdown
cvx02(config-cvx-mss)# vni range 20000-30000
cvx02(config-cvx-mss)# dynamic device-set panfw1
cvx02(config-cvx-mss-panfw1)# tag Arista_MSS
cvx02(config-cvx-mss-panfw1)# type palo-alto firewall
cvx02(config-cvx-mss-panfw1)# state active
cvx02(config-cvx-mss-panfw1)# device fw-ha-node-1
cvx02(config-cvx-mss-panfw1-fw-ha-node-1)# username admin password 0 admincvx03# configure
cvx03(config)# cvx
cvx03(config-cvx)# no shutdown
cvx03(config-cvx)# service mss
cvx03(config-cvx-mss)# no shutdown
cvx03(config-cvx-mss)# vni range 20000-30000
cvx03(config-cvx-mss)# dynamic device-set panfw1
cvx03(config-cvx-mss-panfw1)# tag Arista_MSS
cvx03(config-cvx-mss-panfw1)# type palo-alto firewall
cvx03(config-cvx-mss-panfw1)# state active
cvx03(config-cvx-mss-panfw1)# device fw-ha-node-1
cvx03(config-cvx-mss-panfw1-fw-ha-node-1)# username admin password 0 admin Three policies are created in addition to the default implicit deny policy for inter-zone traffic. The implicit deny ensures that the inter-zone traffic is not allowed unless a policy explicitly allows for it.
The first policy untrust_to_web1 is from the untrust zone to the web1 zone, that allows HTTPS traffic from anywhere to the web server web.
The third policy web2_to_app1 is from the web2 zone to the app1 zone that allows HTTP traffic between the web server web and the application server app.
The fifth policy app2_to_db1 is from the app2 zone to the db1 zone that allows database traffic on port TCP/1433 between the application server app and the database server db.
The second, fourth, and sixth policies prevent the firewall to drop a session for which does not see the initial connection to the protected resource. This could happen if the protected resource has not sent any traffic previous to this point.


Create a rule that Arista MSS will use to intercept and redirect traffic and add a firewall policy with the default Arista_MSS tag as shown in the example above. MSS intercepts all traffic from endpoints identified in policies that match the tag values configured in CVX. The firewall will apply all rules (tagged or untagged) to all traffic.
dynamic device-set fw1
device dc-firewall-1
map device-interface ethernet1/1 switch 00:1c:73:7e:21:bb interface Ethernet1
map device-interface ethernet1/2 switch 00:1c:73:7e:21:bb interface Ethernet9The first policy untrust_to_web1 is from the untrust zone to the web1 zone, that allows HTTPS traffic from anywhere to the web server web.
The third policy web2_to_app1 is from the web2 zone to the app1 zone that allows HTTP traffic between the web server web and the application server app.
The fifth policy app2_to_db1 is from the app2 zone to the db1 zone that allows database traffic on port TCP/1433 between the application server app and the database server db.
The second, fourth, and sixth policies prevent the firewall to drop a session for which does not see the initial connection to the protected resource. This could happen if the protected resource has not sent any traffic previous to this point.
Create a rule that Arista MSS will use to intercept and redirect traffic and add a firewall policy with the default Arista_MSS tag as shown in the example above. MSS intercepts all traffic from endpoints identified in policies that match the tag values configured in CVX. The firewall will apply all rules (tagged or untagged) to all traffic.
dynamic device-set fw1
device dc-firewall-1
map device-interface ethernet1/1 switch 00:1c:73:7e:21:bb interface Ethernet1
map device-interface ethernet1/2 switch 00:1c:73:7e:21:bb interface Ethernet9Macro Segmentation Service (MSS) is configurable for Check Point Software Technologies (Check Point) Firewalls. The configuration and deployment requires the use of Check Point Management Server (Gaia), a security management platform which allows central management of Check Point gateway security devices.
Check Point Firewalls (Gateways)
Interface Configuration
Configure IPv4 addresses on the routed L3 interfaces on the firewall interfaces connected to the Arista TORs.
IPv4 Static Routes Configuration
set static-route 192.0.2.0/24 nexthop gateway address 192.0.2.155 ongateway1> show route static
Codes: C - Connect ed, S - Static, R - RIP, B - BGP (D - Default),
O - OSPF IntraArea (IA - InterArea, E - External, N - NSSA),
A - Aggregate, K - Kernel Remnant, H - Hidden, P - Suppressed,
U - Unreachable, i - Inactive
S 0.0.0.0/0 via 172.2.18.12, Mgmt, cost 0, age 3134690
S 10.6.10.0/24 via 10.6.100.2, eth1, cost 0, age 3134690
S 10.6.20.0/24 via 10.6.200.2, eth2, cost 0, age 3134690Check Point Management Server Configuration
The following figure shows the 1-to-1 HA cluster. The HA interface pairs connected to the Arista switches should have Virtual IP addresses where the intercepted traffic will be forwarded. The active firewall sends out a GARP with its own MAC to indicate where traffic sent to the VIP should be forwarded.
Arista Leaf Switches Configuration
switchport trunk native vlan <interface vlan>
switchport mode trunk
spanning-tree portfast
spanning-tree bpdufilter enable
interface Vlan<interface vlan>
ip address virtual <interface IPv4 address>/<mask>CVX Configuration
!! Standalone firewall
cvx
no shutdown
service mss
no shutdown
!
dynamic device-set chkpt
device <management-server-ip-or-dnsName>
username admin password 7 PKigsm//o3IcnW5rqoZXWQ==
protocol https 4434 (or the configured https port like 443)
group <management-server-network-layer>
!
device member <checkpoint-device-name>
map device-interface eth1 switch 00:1c:73:7e:28:11 interface Ethernet39
map device-interface eth2 switch 00:1c:73:7e:28:11 interface Ethernet40
type check-point management-server
policy tag offload Arista_MSS_offload
policy tag redirect Arista_MSS
state active!! HA Active/Passive firewall pair
cvx
no shutdown
service mss
no shutdown
!
dynamic device-set chkpt
device <management-server-ip-or-dnsName>
username admin password 7 PKigsm//o3IcnW5rqoZXWQ==
protocol https 4434 (or the configured https port like 443)
group <management-server-network-layer>
!
device member <checkpoint-device1-name>
map device-interface eth1 switch 00:1c:73:7e:28:11 interface Ethernet39
map device-interface eth2 switch 00:1c:73:7e:28:11 interface Ethernet40
device member <checkpoint-device2-name>
map device-interface eth1 switch 00:1c:73:7e:28:11 interface Ethernet41
map device-interface eth2 switch 00:1c:73:7e:28:11 interface Ethernet42
type check-point management-server
policy tag offload Arista_MSS_offload
policy tag redirect Arista_MSS
state activeThe verbatim qualifier enhances the Macro Segmentation Service (MSS) with two policy actions: redirect and offload. For firewall policies tagged with the redirect tag, MSS extracts IP addresses from the policy and forwards all traffic destined to or generated from that set of IP addresses to the firewall. The additional verbatim tag, redirecting bidirectional traffic is restricted to the subset that matches the additional qualifiers of a firewall policy to a firewall (such as the source, destination IP addresses or subnets, protocol, L4 ports).
The verbatim tag can also be paired with the offload tag for a policy which installs necessary DirectFlow rules at the TORs to drop or allow the traffic matching the exact qualifiers in the policy definition. If the verbatim tag is not used with the offload tag, the behavior is to offload enforcement for all traffic matching the specific policy rule, while redirecting the remainder of the (non-matching) traffic to the firewall to ensure the security policy for the protected host remains in compliance. The addition of the verbatim tag removes this implicit redirection
The verbatim is a modifier of the original policy enforcement scheme and works with multiple firewalls such as those from Palo Alto Networks and Fortinet.
Policies with broadcast or multicast destination:
Only offload and offloadverbatim tags are supported for policies with IPv4 broadcast or IPv4 multicast destination.
cvx
service mss
dynamic device-set <device-set-name>
device <device-name>
[no | default] policy tag redirect <tag-list>
[no | default] policy tag offload <tag-list>
[no | default] policy tag modifier verbatim <tag-list>hardware tcam
profile direct-flow-mssl3-VXLAN
feature acl port ip
sequence 50
key size limit 160
key field dscp dst-ip ip-frag ip-protocol l4-dst-port l4-ops l4-src-port src-ip tcp-control ttl
action count drop
packet ipv4 forwarding bridged
packet ipv4 forwarding routed
packet ipv4 forwarding routed multicast
packet ipv4 mpls ipv4 forwarding mpls decap
packet ipv4 mpls ipv6 forwarding mpls decap
packet ipv4 non-VXLAN forwarding routed decap
packet ipv4 VXLAN eth ipv4 forwarding routed decap
packet ipv4 VXLAN eth ipv6 forwarding routed decap
packet ipv4 VXLAN forwarding bridged decap
feature acl port ip egress mpls-tunnelled-match
sequence 100
feature acl port ipv6
sequence 30
key field dst-ipv6 ipv6-next-header ipv6-traffic-class l4-dst-port l4-ops-3b l4-src-port
src-ipv6-high src-ipv6-low tcp-control
action count drop
packet ipv6 forwarding bridged
packet ipv6 forwarding routed
packet ipv6 forwarding routed multicast
packet ipv6 ipv6 forwarding routed decap
feature acl port mac
sequence 60
key size limit 160
key field dst-mac ether-type src-mac
action count drop
packet ipv4 forwarding bridged
packet ipv4 forwarding routed
packet ipv4 forwarding routed multicast
packet ipv4 mpls ipv4 forwarding mpls decap
packet ipv4 mpls ipv6 forwarding mpls decap
packet ipv4 non-VXLAN forwarding routed decap
packet ipv4 VXLAN eth ipv4 forwarding routed decap
packet ipv4 VXLAN forwarding bridged decap
packet ipv6 forwarding bridged
packet ipv6 forwarding routed
packet ipv6 forwarding routed decap
packet ipv6 forwarding routed multicast
packet ipv6 ipv6 forwarding routed decap
packet mpls forwarding bridged decap
packet mpls ipv4 forwarding mpls
packet mpls ipv6 forwarding mpls
packet mpls non-ip forwarding mpls
packet non-ip forwarding bridged
feature acl subintf ip
sequence 45
key size limit 160
key field dscp dst-ip ip-frag ip-protocol l4-dst-port l4-ops-18b l4-src-port src-ip tcp-control ttl
action count drop
packet ipv4 forwarding routed
feature acl subintf ipv6
sequence 20
key field dst-ipv6 ipv6-next-header l4-dst-port l4-src-port src-ipv6-high src-ipv6-low tcp-control
action count drop
packet ipv6 forwarding routed
feature acl vlan ip
sequence 40
key size limit 160
key field dscp dst-ip ip-frag ip-protocol l4-dst-port l4-ops-18b l4-src-port src-ip tcp-control ttl
action count drop
packet ipv4 forwarding routed
packet ipv4 mpls ipv4 forwarding mpls decap
packet ipv4 mpls ipv6 forwarding mpls decap
packet ipv4 non-VXLAN forwarding routed decap
packet ipv4 VXLAN eth ipv4 forwarding routed decap
packet ipv4 VXLAN eth ipv6 forwarding routed decap
feature acl vlan ipv6
sequence 15
key field dst-ipv6 ipv6-next-header l4-dst-port l4-src-port src-ipv6-high src-ipv6-low tcp-control
action count drop
packet ipv6 forwarding routed
packet ipv6 ipv6 forwarding routed decap
feature acl vlan ipv6 egress
sequence 25
key field dst-ipv6 ipv6-next-header ipv6-traffic-class l4-dst-port l4-src-port src-ipv6-high src-ipv6-low
tcp-control
action count drop
packet ipv6 forwarding routed
feature flow
key size limit 160
key field dst-ip ether-type in-port ip-protocol l4-dst-port l4-src-port src-ip
action drop redirect set-fwd-header
packet ipv4 forwarding bridged
packet ipv4 forwarding routed
feature forwarding-destination mpls
sequence 105
feature mpls
sequence 5
key size limit 160
action drop redirect set-ecn
packet ipv4 mpls ipv4 forwarding mpls decap
packet ipv4 mpls ipv6 forwarding mpls decap
packet mpls ipv4 forwarding mpls
packet mpls ipv6 forwarding mpls
packet mpls non-ip forwarding mpls
feature mpls pop ingress
sequence 95
feature pbr mpls
sequence 70
key size limit 160
key field mpls-inner-ip-tos
action count drop redirect
packet mpls ipv4 forwarding mpls
packet mpls ipv6 forwarding mpls
packet mpls non-ip forwarding mpls
feature tunnel VXLAN
sequence 55
key size limit 160
key field in-port VXLAN-inner-etype VXLAN-inner-ip-options VXLAN-inner-ip-ttl
packet ipv4 VXLAN eth ipv4 forwarding routed decap
packet ipv4 VXLAN eth ipv6 forwarding routed decap
packet ipv4 VXLAN forwarding bridged decap
feature tunnel VXLAN routing
sequence 10
packet ipv4 forwarding routed
packet ipv4 non-VXLAN forwarding routed decap
packet ipv4 VXLAN eth ipv4 forwarding routed decap
packet ipv4 VXLAN eth ipv6 forwarding routed decap
switch# show hardware tcam profile
Configuration Status
FixedSystem direct-flow-mssl3-VXLAN direct-flow-mssl3-VXLAN| Both compute and service TORs: DCS-7050X, DCS-7050X2, DCS-7050X3, DCS-7060X, DCS-7060X2 | group, verbatim |
|
| Both compute and service TORs: DCS-7020R, DCS-7280R, DCS-7280R2, DCS-7500R, DCS-7500R2 | verbatim |
|
| Both compute and service TORs: DCS-7050X, DCS-7050X2, DCS-7050X3, DCS-7060X, DCS-7060X2, DCS-7020R, DCS-7280R, DCS-7280R2, DCS-7500R, DCS-7500R2 | verbatim |
|
| DCS-7050X, DCS-7050X2, DCS-7050X3, DCS-7060X, DCS-7060X2 as compute TOR and other series as service TOR (with no intercepted hosts connected). | group, verbatim |
|
cvx
service mss
policy enforcement rules group verbatimThe command [no|default] policy enforcement rules
{group verbatim | verbatim} disables / enables policy enforcement.
switch# show service mss policy
<--snip-->
Macro-Segmentation L3 Policy Table
-------------------------------------------------------------------------------
Source Device Policy Offload Redirect Unconverged
status status IPs
---------------- --------- ---------- ---------- ----------- ----------
PaloAltoFirewall fwpan1 policy1 N/A Active N/A
PaloAltoFirewall fwpan1 policy2 Active N/A N/A
PaloAltoFirewall fwpan1 policy3 Active Active 0 of 2
PaloAltoFirewall fwpan1 policy4 N/A Active 0 of 2switch# show service mss policy detail
-------------------------------------------------------------------
Source: PaloAltoFirewall
-------------------------------------------------------------------
Device: fwpan1
Policy (L3): policy1
Offload Status: N/A
Redirect Status: Active
Tags: MSS_redirect, MSS_verbatim
Policy Modifier: Verbatim
VRF: default
Policy (L3): policy2
Offload Status: Active
Redirect Status: N/A
Tags: MSS_offload, MSS_verbatim
Policy Modifier: Verbatim
VRF: default
Policy (L3): policy3
Offload Status: Active
Redirect Status: Active
Tags: MSS_offload
VRF: default
IP Addresses:
Active: 10.10.10.1
Active: 10.10.20.1
Policy (L3): policy4
Offload Status: N/A
Redirect Status: Active
Tags: MSS_redirect
VRF: default
IP Addresses:
Active: 10.10.10.1
Active: 10.10.10.2switch# show directflow detail
Flow default:spm:fwpan1:30000::10.10.20.2/32::10.10.20.3/32::::nh-1.100.0.2:(Flow programmed)
persistent: False
priority: 30000
priorityGroupType: default
hard timeout: 0
idle timeout: 0
match:
Ethernet type: IPv4
source IPv4 address: 10.10.20.2/255.255.255.255
destination IPv4 address: 10.10.20.3/255.255.255.255
IPv4 protocol: TCP
destination TCP/UDP port: 22
actions:
output nexthop: 1.10.100.2
source: mssl3
matched: 0 packets, 0 bytes
Flow default:spm:fwpan1:30000::10.10.20.3/32::10.10.20.2/32::::nh-1.100.0.2:(Flow programmed)
persistent: False
priority: 30000
priorityGroupType: default
hard timeout: 0
idle timeout: 0
match:
Ethernet type: IPv4
source IPv4 address: 10.10.20.3/255.255.255.255
destination IPv4 address: 10.10.20.2/255.255.255.255
IPv4 protocol: TCP
source TCP/UDP port: 22
actions:
output nexthop: 1.10.100.2
source: mssl3
matched: 0 packets, 0 bytes
<--snip-->
The dynamic device-set command configures a device such as a firewall to communicate with the MSS in the MSS configuration mode.
The no dynamic device-set command removes a previously configured device from the MSS configuration and returns to the CVX mode.
Command Mode
MSS Configuration
Command Syntax
dynamic device-set device-set_name
no dynamic device-set device-set_name
Parameter
device-set_name a unique name for the device set.
Example
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
cvx(config-cvx-mss)# vni range 30000-40000
cvx(config-cvx-mss)# dynamic device-set panfw1
cvx(config-cvx-mss-panfw1)#The exception device command bypasses or continues redirecting traffic to service device such as a firewall if the service device control-plane API is unreachable after initial policies have been processed.
The no exception device command.
Command Mode
MSS Configuration
Command Syntax
exception device unreachable [bypass | redirect]
no exception device unreachable [bypass | redirect]
default exception device unreachable bypass
Example
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
cvx(config-cvx-mss)# vni range 30000-40000
cvx(config-cvx-mss)# dynamic device-set fw
cvx(config-cvx-mss-fw)# device firewall-dc7
cvx(config-cvx-mss-fw)# username admin password 7 PKigsmo3IcnW5rqoZXWQ
cvx(config-cvx-mss-fw)# state active
cvx(config-cvx-mss-fw)# type palo-alto firewall
cvx(config-cvx-mss-fw)# exception device unreachable redirectThe group command configures the Panorama device group name to be used with MSS.
The no group command removes the group from the MSS configuration when the Panorama firewall manager is used.
See the type Palo-Alto command for more information about the firewall manager.
Command Mode
Device-set mode
Command Syntax
group group_name
no group group_name
Parameters
group_name the name of the group.
Example
cvx(config)# cvx
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# dynamic device-set pano2
cvx(config-cvx-mss-pano2)# type palo-alto panorama
cvx(config-cvx-mss-pano2)# device myPanorama
cvx(config-cvx-mss-pano2-myPanorama)# group mssDevicesThe name-resolution interval command specifies the period between consecutive requests that the OpenStack controller sends to the Keystone service for VM and tenant name updates. Keystone is OpenStack's authentication and authorization service.
The default period is 21600 seconds (6 hours).
The name-resolution force (CVX-OpenStack) command performs an immediate update, as opposed to waiting for the periodic update.
Command Mode
CVX-OpenStack Configuration
Command Syntax
name-resolution interval period
Parameters
period: Keystone identity service polling interval (seconds).
Comment
service openstack places the switch in CVX-OpenStack configuration mode.Example
switch(config)# cvx
switch(config-cvx)# service openstack
switch(config-cvx-openstack)# name-resolution interval 18000
switch(config-cvx-openstack)#
The service mss command enters the MSS configuration sub-mode.
The no service mss command exits the MSS configuration mode and returns to the CVX mode.
Command Mode
CVX Configuration
Command Syntax
service mss
no service mss
default service mss
Example
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
The show service mss dynamic device-set command displays detailed information about a specific service device set. Information such as device group members, high availability, network, resource details are displayed.
Command Mode
EXEC
CVX Configuration
Command Syntax
show service mss dynamic device-set device_set_name [device device_name [group-members | high-availability | neighbors | network | policies | resources]]
switch# show service mss zone
Source: static
------------------------------------------------
Device: device1switch# show service mss zone
Source: static
----------------------------------------------
Device: device1
Zone: zone1
Switch: 00:00:00:00:00:01
Hostname: switch1.arista.com
Interfaces:
Ethernet1/1
Allowed VLAN: 1000-1010
Port-Channel2/1:
Allowed VLAN: 1000-2000
Switch: 00:00:00:00:00:02
Hostname: switch2.arista.com
Interfaces:
Ethernet10/1
Allowed VLAN: 1000-1010
Zone: zone2
Switch: 00:00:00:00:00:01
Hostname: switch1.arista.com
Interfaces:
Ethernet10/1
Allowed VLAN: 1000-1010
Ethernet 20/1
Allowed VLAN: 1000-2000
The show service mss policy command displays generic information about the configuration and operational state of the macro-segmentation service (MSS) policies on a device.
Command Mode
EXEC
CVX Configuration
Command Syntax
show service mss policy [[device device_name][name policy-name][source (static | plugin_name)]]
Example
cvx# show service mss policy name policy1
Source Device Policy Config Status
------ -------- ------ ------- ------------- -------------
vendor Firewall pan100 policy1 Enabled InitializedThe Config column indicates the configuration state of a policy. The different states are: Enabled, dry run, and disabled states.
The Status column indicates the operational state of a policy. The different status types are initialized, pending, initializing, active, reinitializing, dry-run Complete, and deactivating.
The show service mss status command displays the status of a macro-segmentation service (MSS) on the device.
Command Mode
EXEC
CVX Configuration
Command Syntax
show service mss status
switch# show service mss status
State: Enabled
Service VNIs: 1500-1600,1800,1900-2000switch# show service mss status
State: Disabled
Service VNIs: 1-16777214
The show service mss zone command displays information about the interfaces that are placed in a single zone by the service device. Along with the show service mss policy command, we can use this command to identify issues with the policy configuration.
Interfaces from multiple switches can be placed in the same zone by the device.
Command Mode
EXEC
CVX Configuration
Command Syntax
show service mss zone [[device device_name]|[name zone_name]|[source (static | dynamic_source)]]
Example
switch# show service mss zone
Source: static
---------------------------------------
Device: device1
Zone: zone1
Switch: 00:00:00:00:00:01
Hostname: switch1.arista.com
Interfaces:
Ethernet1/1
Allowed VLAN: 1000-1010
Port-Channel2/1:
Allowed VLAN: 1000-2000
Switch: 00:00:00:00:00:02
Hostname: switch2.arista.com
Interfaces:
Ethernet10/1
Allowed VLAN: 1000-1010
Zone: zone2
Switch: 00:00:00:00:00:01
Hostname: switch1.arista.com
Interfaces:
Ethernet10/1
Allowed VLAN: 1000-1010
Ethernet 20/1
Allowed VLAN: 1000-2000
The state command configures device set as active or disabled or suspended state.
The no state command disables the previously configured state of the device set.
Command Mode
MSS Configuration
Command Syntax
state [active | shutdown | suspend]
no state
Example
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
cvx(config-cvx-mss)# vni range 30000-40000
cvx(config-cvx-mss)# dynamic device-set panfw1
cvx(config-cvx-mss-panfw1)# tag Arista_MSS
cvx(config-cvx-mss-panfw1)# type palo-alto firewall
cvx(config-cvx-mss-panfw1)# state activeThe tag command specifies the tag or tags that MSS searches when it is reading the security policy from the firewall or firewall manager in the dynamic device-set configuration mode. You can specify more than one tag as well.
The no tag command removes the tag from the MSS configuration.
Command Mode
MSS Configuration
Command Syntax
tag tag_name
no tag
default tag
Parameter
tag_name: a unique name for the tag.
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
cvx(config-cvx-mss)# vni range 30000-40000
cvx(config-cvx-mss)# dynamic device-set panfw1
cvx(config-cvx-mss-panfw1)# tag Arista_MSScvx# configure
cvx(config)# cvx
cvx(config-cvx)# no shutdown
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# no shutdown
cvx(config-cvx-mss)# vni range 30000-40000
cvx(config-cvx-mss)# dynamic device-set panfw1
cvx(config-cvx-mss-panfw1)# tag mss1 mss2 mss3The type palo-alto command configures the firewall type to be used in the MSS configuration.
The no type palo-alto command disables the firewall type from the MSS configuration.
Command Mode
MSS Configuration
Command Syntax
type palo-alto [firewall | panorama]
no type palo-alto
Example
cvx# configure
cvx(config)# cvx
cvx(config-cvx)# service mss
cvx(config-cvx-mss)# dynamic device-set panfw1
cvx(config-cvx-mss-panfw1)# type palo-alto firewall
QoS processes apply to traffic that flows through Ethernet ports and control planes. These processes can modify data fields (CoS or DSCP) or assign data streams to traffic classes for prioritized handling. Transmission queues are configurable for individual Ethernet ports to shape traffic based on its traffic class. Many switches also support traffic policies that apply to data that is filtered by access control lists.
QoS configuration varies significantly by switch platform. A list of Arista switch model numbers and their corresponding switch platforms (chipsets) can be found in the Chipset Mapping for QoS.
On some switches, the platform can also be determined by entering platform ? in the CLI.
Example
switch(config)# platform ?
trident Trident chip
switch(config)#Quality of Service (QoS) defines a method of differentiating data streams to provide varying levels of service to the different streams.
Criteria determining a packet’s priority level include packet field contents and the port where data packets are received. QoS settings are translated into traffic classes, which are then used by switches to manage all traffic flows. Traffic flow management varies with each switch platform.
The default mode setting is CoS trust for switched ports and DSCP trust for routed ports.
Ports are associated with default CoS, DSCP, and traffic class settings; defaults vary by platform.
Switches can rewrite the CoS field for outbound tagged packets. The new CoS value is configurable, and is derived from a data stream’s traffic class as specified by the traffic class-to-CoS rewrite map. CoS rewrite is disabled on all the traffic received on CoS trusted ports.
On Petra platform switches, CoS rewrite is always enabled on DSCP trusted ports and untrusted ports.
Switches can rewrite the DSCP field for outbound IP packets. On FM6000, Trident and Tomahawk, Trident II, and Helix platform switches, DSCP rewrite is disabled by default on all ports and always disabled for traffic received on DSCP trusted ports. On Petra, Arad, and Jericho platform switches, DSCP rewrite is always disabled.
FM6000, Trident and Tomahawk, Trident II, and Helix platform switches provide a command that enables or disables DSCP rewrite for packets received on CoS trusted ports and untrusted ports. The new DSCP value is configurable, based on the data stream’s traffic class, as specified by the traffic class-to-DSCP rewrite map.
Map entries are configurable through CLI commands. Default maps determine the traffic class value when CLI map entry commands are not configured. Default maps vary by switch platform.
Transmit queues are logical partitions of an Ethernet port’s egress bandwidth. Data streams are assigned to queues based on their traffic class, then sent as scheduled by port and transmit settings. Support varies by switch platform. A queue’s label determines its priority: queues with the suffix 0 have the lowest priority.
Explicit Congestion Notification (ECN) is an IP and TCP extension that facilitates end-to-end network congestion notification without dropping packets. ECN recognizes early congestion and sets flags that signal affected hosts. Trident and Tomahawk, Trident II, and Helix platform switches extend ECN support to non-TCP packets. LAG interfaces on Strata platforms support ECN counters.
ECN usage requires that it is supported and enabled by both endpoints. Although only unicast flows are modified by ECN markers, the multicast, broadcast, and unmarked unicast flows can affect network congestion and influence the indication of unicast packet congestion.
Networks typically signal congestion by dropping packets. After an ECN-capable host negotiates ECN, it signals impending congestion by marking the IP header of packets encountering the congestion instead of dropping the packets. The recipient echoes the congestion indication back to the sender, which reduces its transmission rate as if it had detected a dropped packet.
Treatment of packets marked as not ECN capable varies by platform.
ACL policing monitors the ingress data rates for a particular class of traffic and performs the action configured when the traffic exceeds the user configured value. Therefore, it allows the user to control ingress bandwidth based on packet classification. The incoming traffic is metered and marked by the policing, and based on the metering results the actions are performed.
ACL policing uses a token bucket shaping algorithm for packet transmission. Packets are eligible for transmission when token count is positive, and when token count is negative the next packet will have to wait until the token count turns positive again. The tokens are renewed at 96ns time interval (Tc). The tokens are collected in the policer bucket up to a max burst size of 16KB, and any traffic beyond this shape rate and burst size is buffered in the shared memory. The packets are dropped if there is a memory overflow.
For example, assume that shaping is disabled, and the link is at 10 Gbps at 1.25 bytes/nsec. In such case a each refill cycle adds tokens worth 120 bytes. For a shape rate of 500 Mbps, each refill cycle adds 6 bytes. And for 64 byte worth of tokens EOS needs 11 refill cycles = 1us. A 64 byte packet coming immediately after a jumbo frame waits longer compared to a jumbo frame coming after 64 byte packet.
At lower shaping rates (less than 10 Mbps), granularity and rounding errors may alter the actual shaping rate by 20% from the specified rate, and the rounding errors are much less at higher speeds. For example, At 100 Mbps you see 98.9 Mbps configured in hardware. You can use the show qos interfaces command to verify the interface speed.
It meters the packet stream and marks packets based on committed burst size (bc) and excess burst size (be).
It meters the packet stream and marks its packets based on two rates, peak information rate (pir) and committed information rate (cir), and associated burst sizes (bc and be).The packet is marked red if rate exceeds ‘pir’, and yellow if it exceeds ‘cir’ but not 'pir' and marked green if rate is lower than 'cir'. The two rate mode is configured by setting four parameters pir, cir, bc, and be.
| Platform Supported | ACL Policing | ACL Policing on LAG Interface |
|---|---|---|
| Trident | Yes | Yes |
| Trident II | Yes | Yes |
| Trident+ | Yes | Yes |
| FM6000 | Yes | Yes |
| Yes | Only Per-Port | |
| Jericho | Yes | Yes |
| Helix | Yes | Yes |
| XP | Yes | Yes |
| Trident 3 | Yes | Yes |
| Tomahawk | Yes | Yes |
| Tomahawk 2 | Yes | Yes |
| Tofino | No | No |
Steps to Configure ACL Policing
switch# configure terminal
switch(config)# policy-map [type qos] policy-name
switch(config-pmap)# class { class-name }
switch(config-pmap-c)# [no] police cir cir [{bps|kbps|mbps}] bc
committed-burst-size [{bytes|kbytes|mbytes}]switch(config)# class-map type qos match-any class1
switch(config-cmap-class1)# match ip access-group acl1
switch(config-cmap-class1)# exit
switch(config)# policy-map type quality-of-service policy1
switch(config-pmap)# class class1
switch(config-pmap-c)# police cir 512000 bc 96000
switch(config-pmap-c)# exit
switch(config-pmap)#Displaying ACL Policing Information
switch(config)# show policy-map
Service-policy p
Class-map: c (match-any)
Match: ip access-group name a
police rate 1000 mbps burst-size 100 bytes
Class-map: class-default (match-any)
Service-policy p
Class-map: c (match-any)
Match: ip access-group name a
police rate 1000 mbps burst-size 100 bytes
Class-map: class-default (match-any)switch(config)# show policy-map interface Ethernet 1 input counters
Service-policy input: policy1
Hardware programming status: Successful
Class-map: class1 (match-any) Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes Conformed 4351 packets, 1857386 bytes
Conformed 2536 packets, 3384260 bytes
Class-map: class-default (match-any) matched packets: 0switch(config)# show policy-map type qos p1 input counters
Service-policy input: p1 Class-map: c1 (match-any)
Match: ip access-group name a1
Police cir 512000 bps bc 96000 bytes Interface: Ethernet1
Conformed 4351 packets, 1857386 bytes
Exceeded 2536 packets, 3384260 bytes
Interface: Ethernet2
Conformed 2351 packets, 957386 bytes
Exceeded 1536 packets, 1384260 bytes
Class-map: class-default (match-any)
Matched packets : 3229switch(config)# show policy-map interface Ethernet 1 input type qos
Interface: Ethernet 1 Service-policy input: policy1
Hardware programming status: Successful Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 9000 bytes
Class-map: class2 (match-any)
Match: ip access-group name acl2 set dscp 2
Class-map: class3 (match-any) Match: ip access-group name acl3
Police cir 1280000 bps bc 9000 bytes
Class-map: class-default (match-any)QoS profiles are sets of QoS configuration instructions defined and applied at the interface level. A QoS profile serves the traffic better by reducing disorder in the running configuration. QoS profiles can modify all interface-level QoS configurations, and are supported on fabric, Ethernet, and port-channel interfaces. Control-plane policies cannot be applied using QoS profiles. Because configuration can be applied through QoS profiles or directly at the interface level, multiple configurations can be applied to the same interface. In such cases, QoS configurations with non-default values, whether configured through the CLI at the interface level or through a QoS profile, are given priority. In the case of multiple non-default values being configured, the interface-level CLI configuration is given priority.
Policy maps incorporating traffic resolution commands can also be applied by a QoS profile. If two policy maps are applied to the same interface (one through a QoS profile and another directly to the CLI).
Policy maps cannot be used on fabric interfaces. If a QoS profile which includes a policy map is applied to a fabric interface, a warning message will be displayed and the policy map will not be applied to the interface, but any additional supported configurations in the QoS profile will be applied. On SVIs and subinterfaces, QoS profiles are not supported, so policy maps must be applied directly through the CLI for these interfaces.
Certain packets may include a flow label in their IPv6 headers when the source requests special handling by routers, such as for a media stream or other “real-time” service, among others. A flow consists of packets which share a single flow label, which is preserved throughout their passage from source to destination.
QoS policy map rules can match IPv6 traffic based on their flow labels. This requires a special TCAM profile (qos-match-ipv6-flow-label). These rules require either an exact match, using the “eq” operator, or both a label and a mask.
QoS profiles are created by using the qos profile command. This also places the switch in QoS profile configuration mode, where the QoS parameters applied to interfaces are configured. To delete a QoS profile from the running configuration, use the no form of the command.
Example
switch(config)# qos profile Test-Profile
switch(config-qos-profile-Test-Profile)#The parameters that a QoS profile applies to interfaces are configured in QoS profile configuration mode by issuing the same QoS configuration commands that are available in interface configuration mode. QoS profile configuration mode is a group change mode, and changes made in the mode are not saved until the mode is exited. To abandon all changes made while in the mode, use the abort command.
Example
switch(config)# qos profile Test-Profile
switch(config-qos-profile-Test-Profile)# qos cos 3
switch(config-qos-profile-Test-Profile)# priority-flow-control on
switch(config-qos-profile-Test-Profile)# exit
switch(config)#switch(config)# qos profile Latency
switch(config-qos-profile-Latency)# tx-queue 3
switch(config-qos-profile-Latency)# latency maximum <1-50000> microseconds
switch(config-qos-profile-Latency)# latency maximum <1-50> milliseconds
switch(config-qos-profile-Latency)# exit
switch(config)#The qos profile command places the switch in QoS Profile Configuration mode. The profile applies the QoS configurations to Ethernet and Port-Channel, and even to the Fabric interfaces, if it exists. A profile specifies the policy-map and other QoS supported configurations. The policy-map then attaches to the QoS profile using service-policy command.
Create profiles in the QoS Profile Configuration mode, then apply it to an interface in interface configuration mode.
switch(config)# qos profile TP
switch(config-qos-profile-TP)#switch(config-qos-profile-TP)# service-policy type qos input PM-1 The service-profile command applies a QoS profile to the configuration mode interface.
switch(config)# interface ethernet 13
switch(config-if-Et13)# service-profile TPThe show qos profile command displays information about the QoS profiles configured and their parameters. To display the attribute of a specific profile, add the name of the profile. To display a list of configured QoS profiles and the interfaces on which they are configured, add the summary keyword.
switch# show qos profile
qos profile p
qos cos 1
no priority-flow-control pause watchdog
priority-flow-control priority 1 no-drop
priority-flow-control priority 2 no-drop
qos profile p2
qos cos 3
priority-flow-control priority 0 no-dropswitch# show qos profile p2
qos profile p2
qos cos 3
priority-flow-control priority 0 no-dropswitch# show qos profile summary
Qos Profile: p
Configured on: Et13,7
Fabric
Po12
Qos Profile: p2
Configured on: Et56Port Settings – Trust Mode and Traffic Class describes port trust and default port CoS and DSCP values.
The show qos interfaces trust command displays the trust mode of specified interfaces.
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# qos trust dscp
switch(config-if-Et3/5/1)# interface ethernet 3/5/2
switch(config-if-Et3/5/2)# no qos trust
switch(config-if-Et3/5/2)# interface ethernet 3/5/3
switch(config-if-Et3/5/3)# qos trust cos
switch(config-if-Et3/5/3)# interface ethernet 3/5/4
switch(config-if-Et3/5/4)# switchport
switch(config-if-Et3/5/4)# default qos trust
switch(config-if-Et3/5/4)# interface ethernet 3/6/1
switch(config-if-Et3/6/1)# no switchport
switch(config-if-Et3/6/1)# default qos trust
switch(config-if-Et3/6/1) #show qos interface ethernet 3/5/1 - 3/6/1 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet3/5/1 DSCP DSCP
Ethernet3/5/2 UNTRUSTED UNTRUSTED
Ethernet3/5/3 COS COS
Ethernet3/5/4 COS DEFAULT
Ethernet3/6/1 DSCP DEFAULT
switch(config-if-Et3/6/1)#Example
switch(config)# interface ethernet 3/6/2
switch(config-if-Et3/6/2)# qos cos 4
switch(config-if-Et3/6/2)# qos dscp 44
switch(config-if-Et3/6/2)# show active
interface Ethernet3/6/2
qos cos 4
qos dscp 44
switch(config-if-Et3/6/2)# show qos interfaces ethernet 3/6/2
Ethernet3/6/2:
Trust Mode: COS
Default COS: 4
Default DSCP: 44
switch(config-if-Et3/6/2)#Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default CoS (port) | Default CoS (port) | Default DSCP (port) |
| Untagged IP | Default CoS (port) | Default CoS (port) | DSCP (packet) |
| Tagged Non-IP | Default CoS (port) | CoS (packet) | Default DSCP (port) |
| Tagged IP | Default CoS (port) | CoS (packet) | DSCP (packet) |
CoS and DSCP Port Settings – Arad Platform Switches describes the default CoS and DSCP settings for each port.
The qos map cos command assigns a traffic class to a list of CoS values. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the chip upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 5 2 5 4 5 6 5
switch(config)#| Inbound CoS | Untagged | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class | Derived: use default CoS as inbound | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 24 41 44 45 46 47 to traffic-class 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 2 2 2 2 0 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 0 5 5 0 0 0 0 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS rewrite functions.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class–CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 2 2 2 4 2 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
DSCP rewrite is always disabled on Arad platform switches.
Transmit Queues and Port Shaping describes transmit queues and port shaping.
Arad platform switches provide 16 physical queues for each egress port: eight unicast and eight multicast queues. Data is scheduled to the physical queues based on transmit queue assignments.
Multicast queue capacity that remains after multicast traffic is serviced is available for unicast traffic of a corresponding priority. Similarly, unicast queue capacity that remains after unicast traffic is serviced is available for overflow multicast traffic. Under conditions of unicast and multicast congestion, egress traffic is evenly split between unicast and multicast traffic.
A data stream’s traffic class determines the transmit queue it uses. The switch defines a single traffic class–transmit queue map for unicast and multicast traffic on all Ethernet and port channel interfaces. The show qos maps command displays the traffic class–transmit queue map.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
Transmit queue parameters are configured in tx-queue configuration command mode, which is entered from interface-ethernet configuration mode.
The qos map traffic-class to tx-queue command assigns traffic classes to a transmit queue. Multiple commands complete the traffic class-transmit queue map. Traffic class 7 and transmit queue 7 are always mapped to each other. This association is not editable.
Example
switch(config)# qos map traffic-class 1 3 5 to tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to tx-queue 2
switch(config)# qos map traffic-class 0 to tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 1 2 1 2 7
switch(config)#The tx-queue (Arad/Jericho) command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. Tx-queue 7 is not configurable. The show qos interfaces displays the transmit queue configuration for a specified port.
Example
switch(config)# interface ethernet 3/3/3
switch(config-if-Et3/3/3)# tx-queue 4
switch(config-if-Et3/3/3-txq-4)#switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# shape rate 5000000
switch(config-if-Et3/5/1)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: 5000012 / 5000000 kbps
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/5/1)#switch(config)# interface ethernet 3/4/1
switch(config-if-Et3/4/1)# tx-queue 4
switch(config-if-Et3/4/1-txq-4)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-4)# tx-queue 3
switch(config-if-Et3/4/1-txq-3)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-3)# show qos interface ethernet 3/4/1
Ethernet3/4/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - 999 / 1000 ( Mbps ) SP / SP D
3 - / - 999 / 1000 ( Mbps ) SP / SP D
2 - / - - / - ( - ) SP / SP D
1 - / - - / - ( - ) SP / SP D
0 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/4/1-txq-3)#A queue’s configuration as round robin also applies to all lower priority queues regardless of other configuration statements.
The bandwidth percent (Arad/Jericho) command configures a round robin queue’s bandwidth share. The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# no priority
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 10
switch(config-if-Et3/5/1-txq-3)# tx-queue 2
switch(config-if-Et3/5/1-txq-2)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-2)# tx-queue 1
switch(config-if-Et3/5/1-txq-1)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-1)# tx-queue 0
switch(config-if-Et3/5/1-txq-0)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-0)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 10 / 10 - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) RR / SP D
switch(config-if-Et3/5/1-txq-0)#switch(config-if-Et3/5/1-txq-0)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-3)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 24 / 30 - / - ( - ) RR / RR D
2 24 / 30 - / - ( - ) RR / SP D
1 24 / 30 - / - ( - ) RR / SP D
0 24 / 30 - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/5/1-txq-3)#Explicit Congestion Notification (ECN) describes Explicit Congestion Notification (ECN).
ECN is independently configurable on all egress queues of each Ethernet interface. ECN settings for Port-Channels are applied on each of the channel’s member Ethernet interfaces. Average queue length is tracked for transmit queues. When it reaches maximum threshold, all subsequent packets are marked.
Although the switch does not limit the number of queues that can be configured for ECN, hardware table limitations restrict the number of queues that can simultaneously implement ECN.
The random-detect ecn (Arad/Jericho) command enables ECN marking for the configuration mode unicast transmit queue and specifies threshold queue sizes.
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 4
switch(config-if-Et3/5/1-txq-4)# random-detect ecn minimum-threshold 128 kbytes maximum-threshold 1280 kbyte
switch(config-if-Et3/5/1-txq-4)# show active
interface Ethernet3/5/1
tx-queue 4
random-detect ecn minimum-threshold 128 kbytes maximum-threshold 1280 kbytes
switch(config-if-Et3/5/1-txq-4)#ACL Policing describes ACL policing.
The default unit for the metering rate CIR is bits per second; the default unit for the burst size is bytes.
The policer is applied to the class inside the policy map. Policy maps can contain one or more policy map classes, each with different match criteria and policer.
Example
switch(config)# class-map type qos match-any class1
switch(config-cmap-class1)# match ip access-group acl1
switch(config-cmap-class1)# exit
switch(config)# policy-map type quality-of-service policy1
switch(config-policy1)# class class1
switch(config-policy1-class1)# police cir 512000 bc 96000
switch(config-policy1-class1)# exit
switch(config-policy1)# exit
switch(config)#switch(config)# show policy-map
Service-policy policy1
Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes
Class-map: class-default (match-any)
switch(config)#switch(config)# show policy-map interface Ethernet 1 input counters
Service-policy input: policy1
Hardware programming status: Successful
Class-map: class1 (match-any) Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes Conformed 4351 packets, 1857386 bytes
Conformed 2536 packets, 3384260 bytes
Class-map: class-default (match-any) matched packets: 0
switch(config)#switch(config)# show policy-map type qos p1 input counters
Service-policy input: p1 Class-map: c1 (match-any)
Match: ip access-group name a1
Police cir 512000 bps bc 96000 bytes Interface: Ethernet1
Conformed 4351 packets, 1857386 bytes
Exceeded 2536 packets, 3384260 bytes
Interface: Ethernet2
Conformed 2351 packets, 957386 bytes
Exceeded 1536 packets, 1384260 bytes
Class-map: class-default (match-any)
Matched packets : 3229
switch(config)#switch(config)# show policy-map interface Ethernet 1 input type qos
Interface: Ethernet 1 Service-policy input: policy1
Hardware programming status: Successful Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 9000 bytes
Class-map: class2 (match-any)
Match: ip access-group name acl2 set dscp 2
Class-map: class3 (match-any) Match: ip access-group name acl3
Police cir 1280000 bps bc 9000 bytes
Class-map: class-default (match-any)
switch(config)#Port Settings – Trust Mode and Traffic Class describes port trust and default port CoS and DSCP values.
The show qos interfaces trust command displays the trust mode of specified interfaces.
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# qos trust dscp
switch(config-if-Et3/5/1)# interface ethernet 3/5/2
switch(config-if-Et3/5/2)# no qos trust
switch(config-if-Et3/5/2)# interface ethernet 3/5/3
switch(config-if-Et3/5/3)# qos trust cos
switch(config-if-Et3/5/3)# interface ethernet 3/5/4
switch(config-if-Et3/5/4)# switchport
switch(config-if-Et3/5/4)# default qos trust
switch(config-if-Et3/5/4)# interface ethernet 3/6/1
switch(config-if-Et3/6/1)# no switchport
switch(config-if-Et3/6/1)# default qos trust
switch(config-if-Et3/6/1)# show qos interface ethernet 3/5/1 - 3/6/1 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet3/5/1 DSCP DSCP
Ethernet3/5/2 UNTRUSTED UNTRUSTED
Ethernet3/5/3 COS COS
Ethernet3/5/4 COS DEFAULT
Ethernet3/6/1 DSCP DEFAULT
switch(config-if-Et3/6/1)#Example
switch(config)# interface ethernet 3/6/2
switch(config-if-Et3/6/2)# qos cos 4
switch(config-if-Et3/6/2)# qos dscp 44
switch(config-if-Et3/6/2)# show active
interface Ethernet3/6/2
qos cos 4
qos dscp 44
switch(config-if-Et3/6/2)# show qos interfaces ethernet 3/6/2
Ethernet3/6/2:
Trust Mode: COS
Default COS: 4
Default DSCP: 44
switch(config-if-Et3/6/2)#Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default CoS (port) | Default CoS (port) | Default DSCP (port) |
| Untagged IP | Default CoS (port) | Default CoS (port) | DSCP (packet) |
| Tagged Non-IP | Default CoS (port) | CoS (packet) | Default DSCP (port) |
| Tagged IP | Default CoS (port) | CoS (packet) | DSCP (packet) |
CoS and DSCP Port Settings – Arad Platform Switches describes the default CoS and DSCP settings for each port.
The qos map cos command assigns a traffic class to a list of CoS values. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the chip upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 5 2 5 4 5 6 5
switch(config)#| Inbound CoS | Untagged | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class | Derived: use default CoS as inbound | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 24 41 44 45 46 47 to traffic-class 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 2 2 2 2 0 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 0 5 5 0 0 0 0 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS rewrite functions.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class–CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 2 2 2 4 2 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
DSCP rewrite is always disabled on Jericho platform switches.
Transmit Queues and Port Shaping describes transmit queues and port shaping.
Jericho platform switches provide 16 physical queues for each egress port: eight unicast and eight multicast queues. Data is scheduled to the physical queues based on transmit queue assignments.
Multicast queue capacity that remains after multicast traffic is serviced is available for unicast traffic of a corresponding priority. Similarly, unicast queue capacity that remains after unicast traffic is serviced is available for overflow multicast traffic. Under conditions of unicast and multicast congestion, egress traffic is evenly split between unicast and multicast traffic.
A data stream’s traffic class determines the transmit queue it uses. The switch defines a single traffic class–transmit queue map for unicast and multicast traffic on all Ethernet and port channel interfaces. The show qos maps command displays the traffic class–transmit queue map.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
Transmit queue parameters are configured in tx-queue configuration command mode, which is entered from interface-ethernet configuration mode.
The qos map traffic-class to tx-queue command assigns traffic classes to a transmit queue. Multiple commands complete the traffic class-transmit queue map. Traffic class 7 and transmit queue 7 are always mapped to each other. This association is not editable.
Example
switch(config)# qos map traffic-class 1 3 5 to tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to tx-queue 2
switch(config)# qos map traffic-class 0 to tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 1 2 1 2 7
switch(config)#The tx-queue (Arad/Jericho) command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. Tx-queue 7 is not configurable. The show qos interfaces displays the transmit queue configuration for a specified port.
Example
switch(config)# interface ethernet 3/3/3
switch(config-if-Et3/3/3)# tx-queue 4
switch(config-if-Et3/3/3-txq-4)# switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# shape rate 5000000
switch(config-if-Et3/5/1)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: 5000012 / 5000000 kbps
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/5/1)#switch(config)# interface ethernet 3/4/1
switch(config-if-Et3/4/1)# tx-queue 4
switch(config-if-Et3/4/1-txq-4)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-4)# tx-queue 3
switch(config-if-Et3/4/1-txq-3)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-3)# show qos interface ethernet 3/4/1
Ethernet3/4/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - 999 / 1000 ( Mbps ) SP / SP D
3 - / - 999 / 1000 ( Mbps ) SP / SP D
2 - / - - / - ( - ) SP / SP D
1 - / - - / - ( - ) SP / SP D
0 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/4/1-txq-3)#A queue’s configuration as round robin also applies to all lower priority queues regardless of other configuration statements.
The bandwidth percent (Arad/Jericho) command configures a round robin queue’s bandwidth share. The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# no priority
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 10
switch(config-if-Et3/5/1-txq-3)# tx-queue 2
switch(config-if-Et3/5/1-txq-2)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-2)# tx-queue 1
switch(config-if-Et3/5/1-txq-1)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-1)# tx-queue 0
switch(config-if-Et3/5/1-txq-0)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-0)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 10 / 10 - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) RR / SP D
switch(config-if-Et3/5/1-txq-0)#switch(config-if-Et3/5/1-txq-0)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-3)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 24 / 30 - / - ( - ) RR / RR D
2 24 / 30 - / - ( - ) RR / SP D
1 24 / 30 - / - ( - ) RR / SP D
0 24 / 30 - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/5/1-txq-3)#ACL Policing describes ACL policing.
The default unit for the metering rate CIR is bits per second; the default unit for the burst size is bytes.
The policer is applied to the class inside the policy map. Policy maps can contain one or more policy map classes, each with different match criteria and policer.
Example
switch(config)# class-map type qos match-any class1
switch(config-cmap-class1)# match ip access-group acl1
switch(config-cmap-class1)# exit
switch(config)# policy-map type quality-of-service policy1
switch(config-policy1)# class class1
switch(config-policy1-class1)# police cir 512000 bc 96000
switch(config-policy1-class1)# exit
switch(config-policy1)# exit
switch(config)#switch(config)# show policy-map
Service-policy policy1
Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes
Class-map: class-default (match-any)
switch(config)#switch(config)# show policy-map interface Ethernet 1 input counters
Service-policy input: policy1
Hardware programming status: Successful
Class-map: class1 (match-any) Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes Conformed 4351 packets, 1857386 bytes
Conformed 2536 packets, 3384260 bytes
Class-map: class-default (match-any) matched packets: 0
switch(config)#switch(config)# show policy-map type qos p1 input counters
Service-policy input: p1 Class-map: c1 (match-any)
Match: ip access-group name a1
Police cir 512000 bps bc 96000 bytes Interface: Ethernet1
Conformed 4351 packets, 1857386 bytes
Exceeded 2536 packets, 3384260 bytes
Interface: Ethernet2
Conformed 2351 packets, 957386 bytes
Exceeded 1536 packets, 1384260 bytes
Class-map: class-default (match-any)
Matched packets : 3229
switch(config)#switch(config)# show policy-map interface Ethernet 1 input type qos
Interface: Ethernet 1 Service-policy input: policy1
Hardware programming status: Successful Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 9000 bytes
Class-map: class2 (match-any)
Match: ip access-group name acl2 set dscp 2
Class-map: class3 (match-any) Match: ip access-group name acl3
Police cir 1280000 bps bc 9000 bytes
Class-map: class-default (match-any)
switch(config)#Port Settings – Trust Mode and Traffic Class describes port trust and default port CoS and DSCP values.
The show qos interfaces trust command displays the trust mode of specified interfaces.
Example
switch(config)# interface ethernet 15
switch(config-if-Et15)# qos trust dscp
switch(config-if-Et15)# interface ethernet 16
switch(config-if-Et16)# no qos trust
switch(config-if-Et16)# interface ethernet 17
switch(config-if-Et17)# qos trust cos
switch(config-if-Et17)# interface ethernet 18
switch(config-if-Et18)# switchport
switch(config-if-Et18)# default qos trust
switch(config-if-Et19)# interface ethernet 19
switch(config-if-Et19)# no switchport
switch(config-if-Et19)# default qos trust
switch(config-if-Et19)# show qos interface ethernet 15 - 19 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet15 DSCP DSCP
Ethernet16 UNTRUSTED UNTRUSTED
Ethernet17 COS COS
Ethernet18 COS DEFAULT
Ethernet19 DSCP DEFAULT
switch(config-if-Et19)#Example
switch(config)# interface ethernet 19
switch(config-if-Et19)# qos cos 4
switch(config-if-Et19)# qos dscp 44
switch(config-if-Et19)# show active
interface Ethernet19
qos cos 4
qos dscp 44
switch(config-if-Et19)# show qos interfaces ethernet 19
Ethernet19:
Trust Mode: COS
Default COS: 4
Default DSCP: 44
switch(config-if-Et19)#Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default CoS (port) | Default CoS (port) | Default DSCP (port) |
| Untagged IP | Default CoS (port) | Default CoS (port) | DSCP (packet) |
| Tagged Non-IP | Default CoS (port) | CoS (packet) | Default DSCP (port) |
| Tagged IP | Default CoS (port) | CoS (packet) | DSCP (packet) |
CoS and DSCP Port Settings – FM6000 Platform Switches describes the default CoS and DSCP settings for each port.
The qos map cos command assigns a traffic class to a list of CoS settings. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the port upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 5 2 5 4 5 6 5
switch(config)#| Inbound CoS | Untagged | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
|---|---|---|---|---|---|---|---|---|---|
| Traffic Class | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 13 25 37 to traffic-class 3
switch(config)# show qos map
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 3 3 0 0 2 2 2 2
2 : 2 2 2 2 3 3 3 3 3 3
3 : 3 3 4 4 4 4 4 3 4 4
4 : 5 5 5 5 5 5 5 5 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS and DSCP rewrite functions.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class–CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 3 4 5 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The DSCP rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-DSCP rewrite map. The qos map traffic-class to dscp command assigns a DSCP rewrite value to a list of traffic classes. Multiple commands create the complete traffic class-DSCP rewrite map.
Example
switch(config)# qos map traffic-class 2 4 6 to dscp 37
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-dscp map:
tc: 0 1 2 3 4 5 6 7
-----------------------------
dscp: 8 0 37 24 37 40 37 56
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| DSCP Rewrite Value | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
Transmit Queues and Port Shaping describes transmit queues and port shaping.
A data stream’s traffic class determines the transmit queue it uses. The switch defines a single traffic class-transmit queue map for all Ethernet and port channel interfaces and is used for unicast and multicast traffic. The show qos maps command displays the traffic class to transmit queue map.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map traffic-class to tx-queue command assigns traffic classes to a transmit queue. Multiple commands create the complete map.
Example
switch(config)# qos map traffic-class 1 3 5 to tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to tx-queue 2
switch(config)# qos map traffic-class 0 to tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 1 2 1 2 7
switch(config)#Transmit queues are configurable on Ethernet ports and port channels. Queue parameters are configured in tx-queue configuration command mode, which is entered from interface ethernet configuration mode. The tx-queue (FM6000) command places the switch in tx-queue configuration mode. The show qos interfaces displays the transmit queue configuration for a specified port.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# tx-queue 3
switch(config-if-Et5-txq-3)#A port’s shape rate specifies its maximum outbound traffic bandwidth. A transmit queue’s shape rate specifies the queue’s maximum outbound bandwidth. Shape rate commands specify data rates in kbps.
Example
transmit queues 3, 4, and 5: 400 Mbps.
switch(config)# interface ethernet 3
switch(config-if-Et3)# shape rate 5000000
switch(config-if-Et3)# tx-queue 0
switch(config-if-Et3-txq-0)# shape rate 500000
switch(config-if-Et3-txq-0)# tx-queue 1
switch(config-if-Et3-txq-1)# shape rate 500000
switch(config-if-Et3-txq-1)# tx-queue 3
switch(config-if-Et3-txq-3)# shape rate 400000
switch(config-if-Et3-txq-3)# tx-queue 4
switch(config-if-Et3-txq-4)# shape rate 400000
switch(config-if-Et3-txq-4)# tx-queue 5
switch(config-if-Et3-txq-5)# shape rate 400000
switch(config-if-Et3-txq-5)# exit
switch(config-if-Et3)# show qos interface ethernet 3
Ethernet3:
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A 400000 strict
4 N/A 400000 strict
3 N/A 400000 strict
2 N/A disabled strict
1 N/A 500000 strict
0 N/A 500000 strict
switch(config-if-Et3)#A queue’s configuration as round robin also applies to all lower priority queues regardless of other configuration statements.
The bandwidth percent (FM6000) command configures a round robin queue’s bandwidth share. The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
switch(config)# interface ethernet 19
switch(config-if-Et19)# tx-queue 3
switch(config-if-Et19-txq-3)# no priority
switch(config-if-Et19-txq-3)# bandwidth percent 40
switch(config-if-Et19-txq-3)# tx-queue 2
switch(config-if-Et19-txq-2)# bandwidth percent 30
switch(config-if-Et19-txq-2)# tx-queue 1
switch(config-if-Et19-txq-1)# bandwidth percent 20
switch(config-if-Et19-txq-1)# tx-queue 0
switch(config-if-Et19-txq-0)# bandwidth percent 10
switch(config-if-Et19-txq-0)# show qos interface ethernet 19
Ethernet19:
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 40 disabled round-robin
2 30 disabled round-robin
1 20 disabled round-robin
0 10 disabled round-robin
switch(config-if-Et19-txq-0)#switch(config-if-Et19-txq-0) #tx-queue 3
switch(config-if-Et19-txq-3)# bandwidth percent 60
switch(config-if-Et19-txq-3)# show qos interface ethernet 19
Ethernet19:
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 49 disabled round-robin
2 24 disabled round-robin
1 16 disabled round-robin
0 8 disabled round-robin
switch(config-if-Et19-txq-3)#Port Settings – Trust Mode and Traffic Class describes port trust and default port CoS and DSCP values.
The show qos interfaces trust command displays the trust mode of specified interfaces.
Example
switch(config)# interface ethernet 3/25
switch(config-if-Et3/25)# qos trust dscp
switch(config-if-Et3/25)# interface ethernet 3/26
switch(config-if-Et3/26)# no qos trust
switch(config-if-Et3/26)# interface ethernet 3/27
switch(config-if-Et3/27)# qos trust cos
switch(config-if-Et3/27)# interface ethernet 3/28
switch(config-if-Et3/28)# switchport
switch(config-if-Et3/28)# default qos trust
switch(config-if-Et3/28)# interface ethernet 3/29
switch(config-if-Et3/29)# no switchport
switch(config-if-Et3/29)# default qos trust
switch(config-if-Et3/29)# show qos interface ethernet 3/25 - 3/29 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet3/25 DSCP DSCP
Ethernet3/26 UNTRUSTED UNTRUSTED
Ethernet3/27 COS COS
Ethernet3/28 COS DEFAULT
Ethernet3/29 DSCP DEFAULT
switch(config-if-Et3/29)#Port channel and Ethernet interfaces are not assigned default CoS or DSCP settings.
Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default TC (chip) | Default TC (chip) | Default TC (chip) |
| Untagged IP | Default TC (chip) | Default TC (chip) | DSCP (packet) |
| Tagged Non-I | Default TC (chip) | CoS (packet) | Default TC (chip) |
| Tagged IP | Default TC (chip) | CoS (packet) | DSCP (packet) |
Petra platform switches assign a default traffic class to the set of Ethernet interfaces controlled by individual PetraA chips. Default traffic class values are configurable for each PetraA chip, not individual interfaces.
The platform petraA traffic-class command specifies the default traffic class used by all ports controlled by a specified chip. The show platform petraA traffic-class command displays traffic class assignments.
switch(config)# platform petraA petra3/4 traffic-class 5
switch(config)# show platform petraA module 3 traffic-class
Petra3/0 traffic-class: 1
Petra3/1 traffic-class: 1
Petra3/2 traffic-class: 1
Petra3/3 traffic-class: 1
Petra3/4 traffic-class: 5
Petra3/5 traffic-class: 1
switch(config)#switch(config)# platform petraA module 6 traffic-class 6
switch(config)# show platform petraA module 6 traffic-class
Petra6/0 traffic-class: 6
Petra6/1 traffic-class: 6
Petra6/2 traffic-class: 6
Petra6/3 traffic-class: 6
Petra6/4 traffic-class: 6
Petra6/5 traffic-class: 6
switch(config)#The qos map cos command assigns a traffic class to a list of CoS settings. Multiple commands create a complete CoS–traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the port upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 4
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 4 2 4 4 4 6 4
switch(config)#| Inbound CoS | untagged | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 13 14 25 48 to traffic-class 3
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 3 3 3 0 2 2 2 2
2 : 2 2 2 2 3 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 5 5 5 5 5 5 5 3 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS rewrite function.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class-CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 2 2 2 4 2 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
DSCP rewrite is always disabled on Petra platform switches.
Transmit Queues and Port Shaping describes transmit queues and port shaping.
| High Priority Queue | Low Priority Queue | |
|---|---|---|
| Unicast Traffic | Transmit Queues 5 – 7 | Transmit Queues 0 – 4 |
| Multicast Traffic | Traffic Classes 5 – 7 | Traffic Classes 0 – 4 |
Multicast queue capacity that is available after multicast traffic is serviced is used for unicast traffic of a corresponding priority. Similarly, unicast queue capacity that is available after unicast traffic is serviced is used for overflow multicast traffic. Under conditions of unicast and multicast congestion, egress traffic is evenly split between unicast and multicast traffic.
Unicast Transmit Queues and Port Shaping describes unicast transmit queues and shaping. Multicast Egress Scheduling describes multicast priority and traffic classes.
A data stream’s traffic class determines the transmit queue it uses. The switch defines a single traffic class–transmit queue map for unicast traffic on all Ethernet interfaces. The show qos maps command displays the traffic class–transmit queue map. The following table displays the default traffic class to transmit queue map on Petra platform switches.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
Transmit queue parameters are configured in tx-queue configuration command mode.
The qos map traffic-class to tx-queue command assigns traffic classes to a transmit queue. Multiple commands complete the traffic class-transmit queue map. Traffic class 7 and transmit queue 7 are always mapped to each other. This association is not editable.
Example
switch(config)# qos map traffic-class 1 3 5 to tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to tx-queue 2
switch(config)# qos map traffic-class 0 to tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 1 2 1 2 7
switch(config)#The tx-queue (Petra) command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. Tx-queue 7not configurable. The show qos interfaces displays the transmit queue configuration for a specified port.
Example
switch(config)# interface ethernet 3/28
switch(config-if-Et3/28)# tx-queue 3
switch(config-if-Et3/28-txq-3)#Example
transmit queues 3, 4, and 5: 400 Mbps.
switch(config)# interface ethernet 3/28
switch(config-if-Et3/28)# shape rate 5000000
switch(config-if-Et3/28)# tx-queue 0
switch(config-if-Et3/28-txq-0)# shape rate 500000
switch(config-if-Et3/28-txq-0)# tx-queue 1
switch(config-if-Et3/28-txq-1)# shape rate 500000
switch(config-if-Et3/28-txq-1)# tx-queue 2
switch(config-if-Et3/28-txq-2)# shape rate 500000
switch(config-if-Et3/28-txq-5)# tx-queue 3
switch(config-if-Et3/28-txq-3)# shape rate 400000
switch(config-if-Et3/28-txq-3)# tx-queue 4
switch(config-if-Et3/28-txq-4)# shape rate 400000
switch(config-if-Et3/28-txq-4)# tx-queue 5
switch(config-if-Et3/28-txq-5)# shape rate 400000
switch(config-if-Et3/28-txq-5)# show qos interface ethernet 3/28
Ethernet3/28:
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A 400000 strict
4 N/A 400000 strict
3 N/A 400000 strict
2 N/A 500000 strict
1 N/A 500000 strict
0 N/A 500000 strict
switch(config-if-Et3/28-txq-5)#A queue’s configuration as round robin also applies to all lower priority queues regardless of other configuration statements.
The bandwidth percent (Petra) command configures a round robin queue’s bandwidth share. The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
switch(config-if-Et3/28)# tx-queue 3
switch(config-if-Et3/28-txq-3)# no priority
switch(config-if-Et3/28-txq-3)# bandwidth percent 40
switch(config-if-Et3/28-txq-3)# tx-queue 2
switch(config-if-Et3/28-txq-2)# bandwidth percent 30
switch(config-if-Et3/28-txq-2)# tx-queue 1
switch(config-if-Et3/28-txq-1)# bandwidth percent 20
switch(config-if-Et3/28-txq-1)# tx-queue 0
switch(config-if-Et3/28-txq-0)# bandwidth percent 10
switch(config-if-Et3/28-txq-0)# show qos interface ethernet 3/28
Ethernet3/28:
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A 400000 strict
4 N/A 400000 strict
3 40 400000 round-robin
2 30 500000 round-robin
1 20 500000 round-robin
0 10 500000 round-robin
switch(config-if-Et3/28-txq-0)#switch(config-if-Et3/28-txq-0)# tx-queue 3
switch(config-if-Et3/28-txq-3)# bandwidth percent 60
switch(config-if-Et3/28-txq-3)# show qos interface ethernet 3/28
Ethernet3/28:
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A 400000 strict
4 N/A 400000 strict
3 49 400000 round-robin
2 24 500000 round-robin
1 16 500000 round-robin
0 8 500000 round-robin
switch(config-if-Et3/28-txq-3)#Multicast traffic is not affected by traffic class assignment or port shaping statements. Multicast traffic is assigned to port egress queues based on traffic class and uses strict priority to schedule egress between the high and low queues.
The show qos interfaces trust command displays the trust mode of specified interfaces.
switch(config)# interface ethernet 15
switch(config-if-Et15)# qos trust dscp
switch(config-if-Et15)# interface ethernet 16
switch(config-if-Et16)# no qos trust
switch(config-if-Et16)# interface ethernet 17
switch(config-if-Et17)# qos trust cos
switch(config-if-Et17)# interface ethernet 18
switch(config-if-Et18)# switchport
switch(config-if-Et18)# default qos trust
switch(config-if-Et18)# interface ethernet 19
switch(config-if-Et19)# no switchport
switch(config-if-Et19)# default qos trust
switch(config-if-Et19)# show qos interface ethernet 15 - 19 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet15 DSCP DSCP
Ethernet16 UNTRUSTED UNTRUSTED
Ethernet17 COS COS
Ethernet18 COS DEFAULT
Ethernet19 DSCP DEFAULT
switch(config-if-Et19)#Example
switch(config)# interface ethernet 7
switch(config-if-Et7)# qos cos 4
switch(config-if-Et7)# qos dscp 44
switch(config-if-Et7)# show active
interface Ethernet7
qos cos 4
qos dscp 44
switch(config-if-Et7)# show qos interfaces ethernet 7
Ethernet7:
Trust Mode: COS
Default COS: 4
Default DSCP: 44
switch(config-if-Et7)#Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default CoS (port) | Default CoS (port) | Default DSCP (port) |
| Untagged IP | Default CoS (port) | Default CoS (port) | DSCP (packet) |
| Tagged Non-IP | Default CoS (port) | CoS (packet) | Default DSCP (port) |
| Tagged IP | Default CoS (port) | CoS (packet) | DSCP (packet) |
CoS and DSCP Port Settings – Trident and Tomahawk Platform Switches describes the default CoS and DSCP settings for each port.
The qos map cos command assigns a traffic class to a list of CoS settings. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the port upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 5 2 5 4 5 6 5
switch(config)#| Inboun CoS | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 24 41 44 45 46 47 to traffic-class 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 2 2 2 2 0 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 0 5 5 0 0 0 0 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS and DSCP rewrite functions.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class–CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 2 2 2 4 2 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The DSCP rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-DSCP rewrite map. The qos map traffic-class to dscp command assigns a DSCP rewrite value to a list of traffic classes. Multiple commands create the complete traffic class-DSCP rewrite map.
Example
switch(config)# qos map traffic-class 2 4 6 to dscp 29
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-dscp map:
tc: 0 1 2 3 4 5 6 7
-----------------------------
dscp: 8 0 29 24 29 40 29 56
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| DSCP | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
Transmit Queues and Port Shaping describes transmit queues and port shaping.
Trident and Tomahawk platform switches define 12 transmit queues: eight unicast (UC0 – UC7) and four multicast (MC0 – MC03). The traffic class–transmit queue maps are configured globally and apply to all Ethernet interfaces. The show qos maps command displays the traffic class–transmit queue maps.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Unicast Transmit Queue | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Multicast Transmit Queue | 0 | 0 | 1 | 1 | 2 | 2 | 3 | 3 |
Multiple commands create the complete maps.
Example
switch(config)# default interface ethernet 7
switch(config)# qos map traffic-class 1 3 5 to uc-tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to uc-tx-queue 5
switch(config)# qos map traffic-class 1 2 3 to mc-tx-queue 1
switch(config)# qos map traffic-class 4 5 6 to mc-tx-queue 3
switch(config)# qos map traffic-class 0 to uc-tx-queue 0
switch(config)# qos map traffic-class 0 to mc-tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 12
Tc - uc-tx-queue map:
tc: 0 1 2 3 4 5 6 7
------------------------------------
uc-tx-queue: 0 1 5 1 5 1 5 7
Tc - mc-tx-queue map:
tc: 0 1 2 3 4 5 6 7
------------------------------------
mc-tx-queue: 0 1 1 1 3 3 3 3
switch(config)#The show qos interfaces displays the transmit queue configuration for a specified port.
switch(config)# interface ethernet 5
switch(config-if-Et5)# uc-tx-queue 3
switch(config-if-Et5-uc-txq-3)#switch(config-if-Et5)# mc-tx-queue 2
switch(config-if-Et5-mc-txq-2)#Example
switch(config)# interface ethernet 7
switch(config-if-Et7)# shape rate 5000000
switch(config-if-Et7)# uc-tx-queue 0
switch(config-if-Et7-uc-txq-0)# shape rate 500000
switch(config-if-Et7-uc-txq-0)# uc-tx-queue 1
switch(config-if-Et7-uc-txq-1)# shape rate 500000
switch(config-if-Et7-uc-txq-1)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# shape rate 400000
switch(config-if-Et7-uc-txq-3)# uc-tx-queue 5
switch(config-if-Et7-uc-txq-5)# shape rate 400000
switch(config-if-Et7-uc-txq-5)# mc-tx-queue 0
switch(config-if-Et7-mc-txq-0)# shape rate 300000
switch(config-if-Et7-mc-txq-0)# mc-tx-queue 2
switch(config-if-Et7-mc-txq-2)# shape rate 300000
switch(config-if-Et7-mc-txq-2)# exit
switch(config-if-Et7)# show qos interface ethernet 7
Ethernet7:
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A 400000 strict 0
UC4 N/A disabled strict 0
MC2 N/A 300000 strict 0
UC3 N/A 400000 strict 0
UC2 N/A disabled strict 0
MC1 N/A disabled strict 0
UC1 N/A 500000 strict 0
UC0 N/A 500000 strict 0
MC0 N/A 300000 strict 0
switch(config-if-Et7)#A queue’s configuration as round robin also applies to all lower priority queues regardless of other configuration statements.
The bandwidth percent (Trident and Tomahawk) command configures a round robin queue’s bandwidth share. The cumulative operational bandwidth of all round robin queues is always 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
Priority Group 1 queues (UC7, UC6, MC3) are not configurable as round robin queues. The bandwidth percent command is not available for these queues.
switch(config)# interface ethernet 7
switch(config-if-Et7)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# no priority
switch(config-if-Et7-uc-txq-3)# bandwidth percent 5
switch(config-if-Et7-uc-txq-3)# uc-tx-queue 2
switch(config-if-Et7-uc-txq-2)# bandwidth percent 15
switch(config-if-Et7-uc-txq-2)# uc-tx-queue 1
switch(config-if-Et7-uc-txq-1)# bandwidth percent 25
switch(config-if-Et7-uc-txq-1)# uc-tx-queue 0
switch(config-if-Et7-uc-txq-0)# bandwidth percent 35
switch(config-if-Et7-uc-txq-0)# mc-tx-queue 1
switch(config-if-Et7-mc-txq-1)# bandwidth percent 12
switch(config-if-Et7-mc-txq-1)# mc-tx-queue 0
switch(config-if-Et7-mc-txq-0)# bandwidth percent 8
switch(config-if-Et7-mc-txq-0)# show qos interface ethernet 7
Ethernet7:
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 5 disabled round-robin 0
UC2 15 disabled round-robin 0
MC1 12 disabled round-robin 0
UC1 25 disabled round-robin 0
UC0 35 disabled round-robin 0
MC0 8 disabled round-robin 0
switch(config-if-Et7-mc-txq-0)#switch(config-if-Et7-uc-txq-0)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# bandwidth percent 30
switch(config-if-Et7-uc-txq-3)# show qos interface ethernet 7
Ethernet7:
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 24 disabled round-robin 0
UC2 12 disabled round-robin 0
MC1 9 disabled round-robin 0
UC1 20 disabled round-robin 0
UC0 28 disabled round-robin 0
MC0 6 disabled round-robin 0
switch(config-if-Et7-uc-txq-3)#ECN is independently configurable on all egress queues of each Ethernet interface. ECN settings for Port-Channels are applied on each of the channel’s member Ethernet interfaces. ECN is also globally configurable to mark packets from the shared pool used for dynamically allocating memory to the queues. Multicast packets contribute to the globally shared pool and can contribute to global level congestion that result in ECN marking of unicast packets queued after the multicast packets.
Average queue length is tracked for transmit queues and the global pool independently. When either entity reaches its maximum threshold, all subsequent packets are marked.
Although the switch does not limit the number of queues that can be configured for ECN, hardware table limitations restrict the number of queues (including the global shared pool) that can simultaneously implement ECN.
The qos random-detect ecn global-buffer (Trident and Tomahawk) command enables ECN marking for globally shared packet memory and specifies minimum and maximum queue threshold sizes.
switch(config)# qos random-detect ecn global-buffer minimum-threshold 20 segments
maximum-threshold 500 segments
switch(config)#switch(config)# no qos random-detect ecn global-buffer
switch(config)#The random-detect ecn (Trident and Tomahawk) command enables ECN marking for the configuration mode unicast transmit queue and specifies threshold queue sizes.
switch(config)# interface ethernet 15
switch(config-if-Et15)# uc-tx-queue 4
switch(config-if-Et15-uc-txq-4)# random-detect ecn minimum-threshold 10 segments
maximum-threshold 100 segments
switch(config-if-Et15-uc-txq-4)# show active
interface Ethernet15
uc-tx-queue 4
random-detect ecn minimum-threshold 10 segments maximum-threshold 100
segments
switch(config-if-Et15-uc-txq-4)# exit
switch(config-if-Et15)#switch(config-if-Et15-uc-txq-4)# no random-detect ecn
switch(config-if-Et15-uc-txq-4)# show active
interface Ethernet15
switch(config-if-Et15-uc-txq-4)# exit
switch(config-if-Et15)#The show qos interfaces trust command displays the trust mode of specified interfaces.
Example
switch(config)# interface ethernet 7/1
switch(config-if-Et7/1)# qos trust dscp
switch(config-if-Et7/1)# interface ethernet 7/2
switch(config-if-Et7/2)# no qos trust
switch(config-if-Et7/2)# interface ethernet 7/3
switch(config-if-Et7/3)# qos trust cos
switch(config-if-Et7/3)# interface ethernet 7/4
switch(config-if-Et7/4)# switchport
switch(config-if-Et7/4)# default qos trust
switch(config-if-Et7/4)# interface ethernet 8/1
switch(config-if-Et8/1)# no switchport
switch(config-if-Et8/1)# default qos trust
switch(config-if-Et8/1)# show qos interface ethernet 7/1 - 8/1 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet7/1 DSCP DSCP
Ethernet7/2 UNTRUSTED UNTRUSTED
Ethernet7/3 COS COS
Ethernet7/4 COS DEFAULT
Ethernet8/1 DSCP DEFAULT
switch(config-if-Et8/1)#Example
switch(config)# interface ethernet 7/3
switch(config-if-Et7/3)# qos cos 4
switch(config-if-Et7/3)# qos dscp 44
switch(config-if-Et7/3)# show active
interface Ethernet7/3
qos cos 4
qos dscp 44
switch(config-if-Et7/3)# show qos interfaces ethernet 7/3
Ethernet7/3:
Trust Mode: COS
Default COS: 4
Default DSCP: 44
switch(config-if-Et7/3)#Traffic Classes describes traffic classes.
| Untrusted | CoS Trusted | DSCP Trusted | |
|---|---|---|---|
| Untagged Non-IP | Default CoS (port) | Default CoS (port) | Default DSCP (port) |
| Untagged IP | Default CoS (port) | Default CoS (port) | DSCP (packet) |
| Tagged Non-IP | Default CoS (port) | CoS (packet) | Default DSCP (port) |
| Tagged IP | Default CoS (port) | CoS (packet) | DSCP (packet) |
CoS and DSCP Port Settings – Trident II and Helix Platform Switches describes the default CoS and DSCP settings for each port.
The qos map cos command assigns a traffic class to a list of CoS settings. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the port upon which it is received.
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 5 2 5 4 5 6 5
switch(config)#| Inbound CoS | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map dscp command assigns a traffic class to a set of DSCP values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
Example
switch(config)# qos map dscp 12 24 41 44 45 46 47 to traffic-class 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 2 2 2 2 0 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 0 5 5 0 0 0 0 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch(config)#| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Rewriting CoS and DSCP describes the CoS and DSCP rewrite functions.
The CoS rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-CoS rewrite map. The qos map traffic-class to cos command assigns a CoS rewrite value to a list of traffic classes. Multiple commands create the complete traffic class–CoS rewrite map.
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)#show qos map
Number of Traffic Classes supported: 8
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 2 2 2 4 2 6 7
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
The DSCP rewrite value is configurable and based on a data stream’s traffic class, as specified by the traffic class-DSCP rewrite map. The qos map traffic-class to dscp command assigns a DSCP rewrite value to a list of traffic classes. Multiple commands create the complete traffic class-DSCP rewrite map.
Example
switch(config)# qos map traffic-class 2 4 6 to dscp 29
switch(config)# show qos map
Number of Traffic Classes supported: 8
Tc-dscp map:
tc: 0 1 2 3 4 5 6 7
-----------------------------
dscp: 8 0 29 24 29 40 29 56
switch(config)#| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| DSCP | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
Transmit Queues and Port Shaping describes transmit queues and port shaping.
A data stream’s traffic class determines the transmit queue it uses. The switch defines a single traffic class-transmit queue map for all Ethernet interfaces and is used for unicast and multicast traffic. The traffic class to transmit queue maps are configured globally and apply to all Ethernet and port channel interfaces. The show qos maps command displays the traffic class to transmit queue map.
Trident II platform switches have eight unicast (UC0 – UC7) and eight multicast (MC0 – MC7) queues. Each UCx-MCx queue set is combined into a single queue group (L1.x), which is exposed to the CLI through this command.
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue Group | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
The qos map traffic-class to tx-queue command assigns traffic classes to a transmit queue. Multiple commands create the complete map.
Example
switch(config)# qos map traffic-class 1 3 5 to tx-queue 1
switch(config)# qos map traffic-class 2 4 6 to tx-queue 2
switch(config)# qos map traffic-class 0 to tx-queue 0
switch(config)# show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 1 2 1 2 7
switch(config)#Transmit queues are configurable on Ethernet ports and port channels. Queue parameters are configured in tx-queue configuration command mode, which is entered from the appropriate interface configuration mode. The tx-queue (Trident II) command places the switch in tx-queue configuration mode. The show qos interfaces displays the transmit queue configuration for a specified port.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# tx-queue 3
switch(config-if-Et5-txq-3)#Example
transmit queues 3, 4, and 5: 400 Mbps
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# shape rate 5000000
switch(config-if-Et17/3)# tx-queue 0
switch(config-if-Et17/3-txq-0)# shape rate 500000
switch(config-if-Et17/3-txq-0)# tx-queue 1
switch(config-if-Et17/3-txq-1)# shape rate 500000
switch(config-if-Et17/3-txq-1)# tx-queue 3
switch(config-if-Et17/3-txq-3)# shape rate 400000
switch(config-if-Et17/3-txq-3)# tx-queue 4
switch(config-if-Et17/3-txq-4)# shape rate 400000
switch(config-if-Et17/3-txq-4)# tx-queue 5
switch(config-if-Et17/3-txq-5)# shape rate 400000
switch(config-if-Et17/3-txq-5)# exit
switch(config-if-Et17/3)# show qos interface ethernet 17/3
Ethernet17/3:
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) 400 / 400 ( Mbps ) SP / SP
4 - / - ( - ) 400 / 400 ( Mbps ) SP / SP
3 - / - ( - ) 400 / 400 ( Mbps ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) 500 / 500 ( Mbps ) SP / SP
0 - / - ( - ) 500 / 500 ( Mbps ) SP / SP
switch(config-if-Et17/3)#Queue priority rank is denoted by the queue number; transmit queues with higher numbers have higher priority. Trident II supports strict priority queues; round robin queues are not supported.
The bandwidth guaranteed (Trident II) command configures specifies the minimum bandwidth for outbound traffic on the transmit queue.
Example
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)# show qos interface ethernet 17/3
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) 400 / 400 ( Mbps ) SP / SP
4 1 / 1 ( Mbps ) 400 / 400 ( Mbps ) SP / SP
3 - / - ( - ) 400 / 400 ( Mbps ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) 500 / 500 ( Mbps ) SP / SP
0 - / - ( - ) 500 / 500 ( Mbps ) SP / SP
switch(config-if-Et17/3-txq-4)#Ingress policing on a port-channel polices the matched traffic from all member interfaces combined, i.e. it provides aggregate policing and statistics (DCS-7050X, DCS-7010T, DCS-7250X, and DCS-7300X series). When a per-interface policer is attached to a port-channel, one set of TCAM entries is created for all member interfaces. The associated interface bitmap is updated, and aggregate policing is performed on all member interfaces.
switch(config)# policy-map policy-1
switch(config-pmap-qos-policy-1)# class class-1
switch(config-pmap-c-qos-policy-1-class-1)# police cir 512000 bps bc 96000
switch(config-pmap-c-qos-policy-1-class-1)# exit
switch(config-pmap-qos-policy-1)# exit
switch(config)# interface Et 4 / 5 / 4
switch(config-if-Et4/5/4)# channel-group 2 mode active
switch(config-if-Et4/5/4)# exit
switch(config)# interface po2
switch(config-if-Po2)# service-policy type qos input policy-1
switch(config-if-Po2)# exit
switch(config)#switch(config)# class-map type qos match-any class1
switch(config-cmap-qos-class1)# match ip access-group acl1
switch(config-cmap-qos-class1)# exit
switch(config)# policy-map type quality-of-service policy1
switch(config-pmap-qos-policy1)# class class1
switch(config-pmap-c-qos-policy1-class1)# police cir 512000 bc 96000
switch(config-pmap-c-qos-policy1-class1)# exit
switch(config-pmap-qos-policy1)# exit
switch(config)# show policy-map
Service-policy policy1
Class-map: class1 (match-any)
Match: ip access-group name acl1
police rate 512000 bps burst-size 96000 bytes
Class-map: class-default (match-any)
switch(config)#EOS is optimized to support QoS configuration on the Fabric interfaces on 7250x and 7300 series switches. Configuring QoS on the Fabric interfaces in addition to front panel ports allows user to have end-to-end control and helps to manage traffic better over these switches. By default, tx queues are configured as strict priority on 7250X and 7300X series.
Fabric QoS is configured using a QoS profiles which is then applied on fabric interfaces on 7250x and 7300x series. Following are the steps to configure Fabric QoS.
switch# show qos profile fabricProfile
qos profile fabricProfile
priority-flow-control priority 1 no-drop
priority-flow-control priority 6 no-drop dlb
tx-queue 0
bandwidth guaranteed 10000 kbps
random-detect ecn minimum-threshold 10 mbytes maximum-threshold 10 mbytesswitch# show qos interfaces fabric
qos profile fabricProfileEOS Release 4.23.1F introduces the ability to configure the color extended community in route-map set clauses and in an extcommunity-list for inbound and outbound policy application.
Use the color extended community for per-destination steering into Segment-Routing Traffic-Engineered (SR-TE) policies. If the next-hop and color of a BGP route match a particular policy (composed of an endpoint and color), any traffic bound to the destination can be steered according to the policy instead of forwarded via an IGP path or tunnel.
Configuring color extended communities is supported on all platforms.
Use the following command for color extended community expressions:
color COLOR-VALUE [color-only (exact-match | (endpoint-match (any | null)))]
| Configuring Color Extended Community in route-map mode | |
|---|---|
| Command (config-route-map mode) | [no | default] set extcommunity COLOR-EXPRESSION [additive | delete] |
| Action | Adds a color extended community to be applied to routes affected by the route-map. Multiple set clauses can be applied to a single route-map to configure multiple colors for routes. Additive adds the extended communities to those received, while delete deletes any matching extended color communities. Negating the command removes the entry from the route-map. |
| Default | None |
| Example |
|
| Configuring Color Extended Community in extcommunity-list | |
|---|---|
| Command (config mode) | [(no|default)] ip extcommunity-list WORD (permit|deny){COLOR-EXPRESSION} |
| Action | Adds a color extended community to an extcommunity-list. Multiple color extended communities can be added to the list. Negating the command removes the corresponding color extended community from the list. |
| Default | None |
| Example |
|
The color extended community is only supported in multi-agent mode. Enable Multi-agent mode via the following command:
service routing protocols mode multi-agent
The IPv4 ACL based QoS is enabled on switches through policy-map configuration. The ACL based QoS can be configured on front panel ports, port-channel interfaces on DCS-7160 series switches.
The ACL-based QoS policy applied on SVIs modify the QoS parameters for SVI traffic (L3 VLAN) based on ACL classification. EOS supports ACL-based QoS on Switched Virtual Interface (SVI) ports on the following platforms:
The QoS actions is applicable only to the routed traffic flowing through the members of the corresponding VLAN.
The steps to configure ACL based QoS is as follows:
The following are the limitations specific to DCS-7500E, DCS-7280E and DCS-7020TR:
When QoS service policies are applied to both SVI and its member interfaces and packets hit both policies, the behavior is indeterministic.
In addition to criteria like COS and DSCP, QoS decisions can be based on the IPv6 flow labels of packets. To use IPv6 flow labels as a criterion for QoS decisions, use the permit command to create ACL rules to select packets based on their IPv6 flow labels using an exact match and an optional mask, and then apply the access list to a class map in a QoS policy map, which can then be applied to individual interfaces. This requires a TCAM profile which must be installed explicitly.
hardware tcam
system profile qos-match-ipv6-flow-labelThere are approximately 130 lines.
Paste this into the CLI of the switch. Each command in the file will be executed in turn when you paste the file contents. When the paste completes, if the cursor is at the end of the last command, type enter to execute it.
Configure the TCAM with the hardware tcam command, and use the system profile command to confirm that the “qos-match-ipv6-flow-label” profile has been installed. If the profile is installed, the ? operator will show “qos-match-ipv6-flow-label” as an available profile.
Example
switch(config)# hardware tcam
switch(config-tcam)# system profile qos-match?
WORD qos-match-ipv6-flow-label
switch(config-tcam)# exit
switch(config)#If the profile "qos-match-ipv6-flow-label" is listed, use the system profile command to apply it. Confirm that the profile has been successfully applied with the show hardware tcam profile command.
Example
switch(config)# hardware tcam
switch(config-tcam)# system profile qos-match-ipv6-flow-label
!
WARNING!
Changing TCAM profile will cause forwarding agent(s) to exit and restart.
All traffic through the forwarding chip managed by the restarting
forwarding agent will be dropped.
Proceed [y/n] y
switch(config-tcam)# exit
switch(config)# show hardware tcam profile
Configuration Status
FixedSystem qos-match-ipv6-flow-label qos-match-ipv6-flow-label
switch(config)#Configure an access list with the ipv6 access-list command. Then create rules with the permit ipv6 command.
Example
switch(config)# ipv6 access-list L1
switch(config-ipv6-acl-L1)# permit ipv6 any any flow-label eq 23
switch(config-ipv6-acl-L1)# exit
switch(config)#Configure a QoS class map with the class-map command. Then add an access list to the class map with the match command.
Example
switch(config)# class-map type qos match-any C1
switch(config-cmap-qos-C1)# match ipv6 access-group L1
switch(config-cmap-qos-C1)# exit
switch(config)#Configure a QoS policy map, creating it if necessary, with the policy-map command. Then add a class map to the policy map and define the traffic class.
Example
switch(config)# policy-map type quality-of-service P1
switch(config-pmap-quality-of-service-P1)# class C1
switch(config-pmap-c-quality-of-service-P1-C1)# set traffic-class 4
switch(config-pmap-c-quality-of-service-P1-C1)# exit
switch(config-pmap-quality-of-service-P1)# exit
switch(config)#Configure an interface with the interface command. Apply the QoS policy to the interface with the service-policy command.
switch(config)# interface Ethernet 1/1
switch(config-if-Et1/1)# service-policy type qos input P1
switch(config-if-Et1/1)# exit
switch(config)#switch(config)# show policy-map P1
Service-policy input: P1
Hardware programming status: Successful
Class-map: C1 (match-any)
Match: ipv6 access-group name L1
set traffic-class 4
Class-map: class-default (match-any)
switch(config)# show ipv6 access-lists L1
IPV6 Access List L1
10 permit ipv6 any any flow-label eq 23
switch(config)#switch# show interface counters queue drop-precedence
intf 0 1 2
Et1/1 100 0 200
Et1/2 200 0 300
…When you enable this feature using the qos tx-queue shape rate percent percentage adaptive command, QoS calculates the txQueue shape rate based the available bandwidth and not the link speed. For instance, if the interface has a link speed of 100Gbps, and the subinterface configured to 50%, then the subinterface has a link speed of 50Gbps.
switch(config)# qos tx-queue shape rate percentage adaptive
! Change will take effect only after switch reboot.Reboot the switch.
Use the show qos tx-queue to display the status of the configuration. One of the following messages displays after entering the command:
switch# show qos tx-queue
Shape rate percent : Non-Adaptiveswitch# show qos tx-queue
Shape rate percent : Adaptiveswitch# show qos tx-queue
Shape rate percent : Non-Adaptive (reboot required for Adaptive)In Arista EOS, Tx Queue Precision Shaping addresses a fundamental hardware challenge by maintaining consistent traffic rates with the low configured bandwidth, typically in the kilobit or low megabit range.
EOS leverages the underlying switch ASIC high-precision timers to clock the egress of data. Instead of rounding the shape rate to the nearest hardware-supported increment, which might be 5–10% off at low speeds, precision shaping allows the switch to hit the target rate with much higher fidelity.
switch(config)# qos tx-queue shape rate precision 50Mbps
! Change will take effect only after switch reboot.The last parameter of the command indicates the minimum speed that requires precision. Currently, EOS only supports 50Mbps.
To disable precision shaping mode, use the [no | default] versions of the command.
switch# show qos tx-queue shape rate precision
Configured Operational
---------------- -----------
50 Mbps Noneswitch(config)# qos subinterface scheduling parent round-robin
! Change will only take effect after switch reboot.switch(config)# no qos subinterface scheduling parent round-robin
! Change will only take effect after switch reboot.switch# show platform sand subinterface capabilities
SubInterface:
------------------
Supported:
----------
Minimum port shape rate(kbps) : 1000
Maximum port shape rate(kbps) : 400000000
Number of voqs per subinterface when shaping is applied : 4
Traffic class to Voq mapping
TC0-1 : Voq0
TC2-3 : Voq1
TC4-5 : Voq2
TC6-7 : Voq3
Traffic class to scheduling mode
TC0-1 : WRR( weight 1 )
TC2-3 : WRR( weight 2 )
TC4-5 : WRR( weight 3 )
TC6-7 : SP
( Higher weight implies more credits )
Voq tail-drop threshold(MegaByte) : 12.500000
Voq tail-drop threshold(Buffer Descriptor) : 12500
Maximum number of subinterfaces with voq supported on the system: 512
Maximum number of subinterfaces with voq supported per core
System Core 0 : 512
System Core 1 : 512
Scheduling between parent and shaped subinterfaces: : Round RobinExplicit Congestion Notification (ECN) is an IP and TCP extension that facilitates end-to-end network congestion notification without dropping packets. ECN recognizes early congestion and sets flags that signal affected hosts. Trident and Tomahawk, Trident II, and Helix platform switches extend ECN support to non-TCP packets. LAG interfaces on Strata platforms support ECN counters.
ECN usage requires that it is supported and enabled by both endpoints. Although only unicast flows are modified by ECN markers, the multicast, broadcast, and unmarked unicast flows can affect network congestion and influence the indication of unicast packet congestion.
switch(config)# interface Ethernet 1/1
switch(config-if-Et1/1)# tx-queue 3
switch(config-if-Et1/1-txq-3)# random-detect ecn delay threshold 33 millisecondsConfigure a delay threshold as a value between 1 to 4294967 microseconds or a value between 1 to 4294 milliseconds.
switch(config)# show qos interfaces Ethernet 1/1 ecn
Ethernet1/1:
ECN ECN ECN ECN ECN
Minimum Maximum Delay Mark-Prob Weight
Tx-Queue Threshold Unit Threshold Threshold Threshold
-------- -------------- --------- --------- ------------------------- --------- ------
7 - - - - - / - -
6 - - - - - / - -
5 - - - - - / - -
4 - - - - - / - -
3 - - - 33000.000 / 33000.000 (L) - / - -
2 - - - - - / - -
1 - - - - - / - -
0 - - - - - / - -
Delay Threshold Type: G -> Global L -> Local
Note: Values are displayed as Configured/OperationalBoth types of notification result in the egress marking of the packet when experiencing the congestion beyond the configured threshold.
Configure ECN on a transmit queue of an interface, and only switches with front panel ports and port-channels support ECN.
Configuring a low latency transmit queue scheduler profile provides an alternative operating mode for queues with reduced latency. By default, the switch has a balanced profile focused on maintaining sustained throughput and avoiding excessive latency. In certain scenarios, this profile may not provide an optimal configuration for latency-sensitive scenarios with critical flow completion time. In this case, configure a responsive low latency scheduler profile validated against the hardware capabilities.
The responsive profile provides maximum benefits in scenarios with low fan-in and bursty flows and reduces the maximum latency from 40 microseconds to 8 microseconds when a flow starts or stops.
switch(config)# platform fap voq credit rates unifiedswitch(config)# qos tx-queue 0-7 scheduler profile responsiveConfigure up to eight (8) responsive profiles.
The bandwidth guaranteed command specifies the minimum bandwidth for outbound traffic on the transmit queue. By default, no bandwidth is guaranteed to any transmit queue.
The no bandwidth guaranteed and default bandwidth guaranteed commands remove the minimum bandwidth guarantee on the transmit queue by deleting the corresponding bandwidth guaranteed command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
bandwidth guaranteed rate DATA_MIN
no bandwidth guaranteed
default bandwidth guaranteed
Parameters
Related Command
tx-queue (Trident II) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)# bandwidth guaranteed 1000 kbps
switch(config-if-Et17/3-txq-4)# show qos interfaces ethernet 17/3
Ethernet17/3:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) - / - ( - ) SP / SP
4 1 / 1 ( Mbps ) - / - ( - ) SP / SP
3 - / - ( - ) - / - ( - ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) - / - ( - ) SP / SP
0 - / - ( - ) - / - ( - ) SP / SP
Note: Values are displayed as Operational/Configured
switch(config-if-Et17/3-txq-4)#The bandwidth guaranteed command specifies the minimum bandwidth for outbound traffic on the transmit queue. By default, no bandwidth is guaranteed to any transmit queue.
The no bandwidth guaranteed and default bandwidth guaranteed commands remove the minimum bandwidth guarantee on the transmit queue by deleting the corresponding bandwidth guaranteed command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
bandwidth guaranteed DATA_MIN
no bandwidth guaranteed
default bandwidth guaranteed
Parameters
Related Command
tx-queue (Helix) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 17
switch(config-if-Et17)# tx-queue 4
switch(config-if-Et17-txq-4)# bandwidth guaranteed 1000 kbps
switch(config-if-Et17-txq-4)# show qos interfaces ethernet 17
Ethernet17/3:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) - / - ( - ) SP / SP
4 1 / 1 ( Mbps ) - / - ( - ) SP / SP
3 - / - ( - ) - / - ( - ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) - / - ( - ) SP / SP
0 - / - ( - ) - / - ( - ) SP / SP
Note: Values are displayed as Operational/Configured
switch(config-if-Et17-txq-4)#The bandwidth percent command configures the bandwidth share of the transmit queue when configured for round robin priority. Bandwidth is allocated to all queues based on the cumulative configured bandwidth of all the port’s round robin queues.
The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
The no bandwidth percent and default bandwidth percent commands restore the default bandwidth share of the transmit queue by removing the corresponding bandwidth percent command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
bandwidth percent proportion
no bandwidth percent
default bandwidth percent
Parameter
proportion Bandwidth percentage assigned to queues. Values range from 1 to 100.
Related Command
tx-queue (Arad/Jericho) places the switch in tx-queue configuration mode.
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# no priority
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 10
switch(config-if-Et3/5/1-txq-3)# tx-queue 2
switch(config-if-Et3/5/1-txq-2)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-2)# tx-queue 1
switch(config-if-Et3/5/1-txq-1)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-1)# tx-queue 0
switch(config-if-Et3/5/1-txq-0)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-0)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 10 / 10 - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) RR / SP D
switch(config-if-Et3/5/1-txq-0)#switch(config-if-Et3/5/1-txq-0)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# bandwidth percent 30
switch(config-if-Et3/5/1-txq-3)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 24 / 30 - / - ( - ) RR / RR D
2 24 / 30 - / - ( - ) RR / SP D
1 24 / 30 - / - ( - ) RR / SP D
0 24 / 30 - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/5/1-txq-3)#switch(config-if-Et3/5/1-txq-3)# bandwidth percent 2
switch(config-if-Et3/5/1-txq-3)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 2 / 2 - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/5/1-txq-3)#The bandwidth percent command configures the bandwidth share of the transmit queue when configured for round robin priority. Bandwidth is allocated to all queues based on the cumulative configured bandwidth of all the port’s round robin queues.
The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
The no bandwidth percent and default bandwidth percent commands restore the default bandwidth share of the transmit queue by removing the corresponding bandwidth percent command running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
bandwidth percent proportion
no bandwidth percent
default bandwidth percent
Parameter
proportion Configured bandwidth percentage. Value ranges from 1 to 100. Default value is 0.
Related Command
tx-queue (FM6000) places the switch in tx-queue configuration mode.
switch(config)# interface Ethernet 19
switch(config-if-Et19)# tx-queue 3
switch(config-if-Et19-txq-3)# no priority
switch(config-if-Et19-txq-3)# bandwidth percent 10
switch(config-if-Et19-txq-3)# tx-queue 2
switch(config-if-Et19-txq-2)# bandwidth percent 30
switch(config-if-Et19-txq-2)# tx-queue 1
switch(config-if-Et19-txq-1)# bandwidth percent 30
switch(config-if-Et19-txq-1)# tx-queue 0
switch(config-if-Et19-txq-0)# bandwidth percent 30
switch(config-if-Et19-txq-0)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx Bandwidth Bandwidth Shape Rate Priority ECN/WRED
Queue (percent) Guaranteed (units) units)
-----------------------------------------------------------------------
7 - / - - / - ( - ) - / - ( - ) SP / SP D
6 - / - - / - ( - ) - / - ( - ) SP / SP D
5 - / - - / - ( - ) - / - ( - ) SP / SP D
4 - / - - / - ( - ) - / - ( - ) SP / SP D
3 10 / 10 - / - ( - ) - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
Legend:
RR -> Round Robin
SP -> Strict Priority
- -> Not Applicable / Not Configured
ECN/WRED: L -> Queue Length ECN Enabled W -> WRED Enabled D -> Disabledcp118.14:04:20# config
cp118.14:04:23(config)# interface ethernet 19
cp118.14:04:47(config-if-Et19-txq-0)# tx-queue 3
cp118.14:04:59(config-if-Et19-txq-3)# bandwidth percent 30
cp118.14:05:16(config-if-Et19-txq-3)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx Bandwidth Bandwidth Shape Rate Priority ECN/WRED
Queue (percent) Guaranteed (units) (units)
------------------------------------------------------------------------
7 - / - - / - ( - ) - / - ( - ) SP / SP D
6 - / - - / - ( - ) - / - ( - ) SP / SP D
5 - / - - / - ( - ) - / - ( - ) SP / SP D
4 - / - - / - ( - ) - / - ( - ) SP / SP D
3 24 / 30 - / - ( - ) - / - ( - ) RR / RR D
2 24 / 30 - / - ( - ) - / - ( - ) RR / SP D
1 24 / 30 - / - ( - ) - / - ( - ) RR / SP D
0 24 / 30 - / - ( - ) - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
Legend:
RR -> Round Robin
SP -> Strict Priority
- -> Not Applicable / Not Configured
ECN/WRED: L -> Queue Length ECN Enabled W -> WRED Enabled D -> Disabledcp118.14:09:37(config-if-Et19-txq-3)# bandwidth percent 2
cp118.14:12:56(config-if-Et19-txq-3)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx Bandwidth Bandwidth Shape Rate Priority ECN/WRED
Queue (percent) Guaranteed (units) (units)
----------------------------------------------------------------------
7 - / - - / - ( - ) - / - ( - ) SP / SP D
6 - / - - / - ( - ) - / - ( - ) SP / SP D
5 - / - - / - ( - ) - / - ( - ) SP / SP D
4 - / - - / - ( - ) - / - ( - ) SP / SP D
3 2 / 2 - / - ( - ) - / - ( - ) RR / RR D
2 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
1 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
0 30 / 30 - / - ( - ) - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
Legend:
RR -> Round Robin
SP -> Strict Priority
- -> Not Applicable / Not Configured
ECN/WRED: L -> Queue Length ECN Enabled W -> WRED Enabled D -> DisabledThe bandwidth percent command configures the bandwidth share of the transmit queue when configured for round robin priority. Bandwidth is allocated to all queues based on the cumulative configured bandwidth of all the port’s round robin queues.
The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
The no bandwidth percent and default bandwidth percent commands restore the default bandwidth share of the transmit queue by removing the corresponding bandwidth percent command running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
bandwidth percent proportion
no bandwidth percent
default bandwidth percent
Parameter
proportionBandwidth percentage assigned to queues. Values range from 1 to 100.
Related Command
tx-queue (Petra) places the switch in tx-queue configuration mode.
switch(config)# interface ethernet 3/28
switch(config-if-Et3/28)# tx-queue 3
switch(config-if-Et3/28-txq-3)# no priority
switch(config-if-Et3/28-txq-3)# bandwidth percent 10
switch(config-if-Et3/28-txq-3)# tx-queue 2
switch(config-if-Et3/28-txq-2)# bandwidth percent 30
switch(config-if-Et3/28-txq-2)# tx-queue 1
switch(config-if-Et3/28-txq-1)# bandwidth percent 30
switch(config-if-Et3/28-txq-1)# tx-queue 0
switch(config-if-Et3/28-txq-0)# bandwidth percent 30
switch(config-if-Et3/28-txq-0)# show qos interface ethernet 3/28
Ethernet3/28:
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 10 disabled round-robin
2 30 disabled round-robin
1 30 disabled round-robin
0 30 disabled round-robin
switch(config-if-Et3/28-txq-0)#switch(config-if-Et3/28-txq-0)# tx-queue 3
switch(config-if-Et3/28-txq-3)# bandwidth percent 30
switch(config-if-Et3/28-txq-3)# show qos interface ethernet 3/28
Ethernet3/28:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 24 disabled round-robin
2 24 disabled round-robin
1 24 disabled round-robin
0 24 disabled round-robin
switch(config-if-Et3/28-txq-3)#switch(config-if-Et3/28)# tx-queue 3
switch(config-if-Et3/28-txq-3)# bandwidth percent 2
switch(config-if-Et3/28-txq-3)# show qos interface ethernet 3/28
Ethernet3/28:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 2 disabled round-robin
2 30 disabled round-robin
1 30 disabled round-robin
0 30 disabled round-robin
switch(config-if-Et3/28-txq-3)#The bandwidth percent command configures the bandwidth share of the transmit queue when configured for round robin priority. Bandwidth is allocated to all queues based on the cumulative configured bandwidth of all the port’s round robin queues.
The cumulative operational bandwidth of all round robin queues is always less than or equal to 100%. If the cumulative configured bandwidth is greater than 100%, each port’s operational bandwidth is its configured bandwidth divided by the cumulative configured bandwidth.
The no bandwidth percent and default bandwidth percent commands restore the default bandwidth share of the transmit queue by removing the corresponding bandwidth percent command running-config.
Command Mode
Mc-Tx-Queue configuration
Uc-Tx-Queue configuration
Command Syntax
bandwidth percent proportion
no bandwidth percent
default bandwidth percent
Parameter
proportion Bandwidth percentage assigned to queues. Values range from 1 to 100.
switch(config)# interface ethernet 7
switch(config-if-Et7)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# no priority
switch(config-if-Et7-uc-txq-3)# bandwidth percent 30
switch(config-if-Et7-uc-txq-3)# uc-tx-queue 2
switch(config-if-Et7-uc-txq-2)# bandwidth percent 30
switch(config-if-Et7-uc-txq-2)# uc-tx-queue 1
switch(config-if-Et7-uc-txq-1)# bandwidth percent 30
switch(config-if-Et7-uc-txq-1)# mc-tx-queue 1
switch(config-if-Et7-mc-txq-1)# bandwidth percent 10
switch(config-if-Et7-mc-txq-1)# show qos interfaces ethernet 7
Ethernet7:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 30 disabled round-robin 0
UC2 30 disabled round-robin 0
MC1 10 disabled round-robin 0
UC1 30 disabled round-robin 0
UC0 0 disabled round-robin 0
MC0 0 disabled round-robin 0
switch(config-if-Et7-mc-txq-1)#switch(config-if-Et7-mc-txq-1)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# bandwidth percent 55
switch(config-if-Et7-uc-txq-3)# show qos interface ethernet 7
Ethernet7:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: disabled
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 44 disabled round-robin 0
UC2 24 disabled round-robin 0
MC1 8 disabled round-robin 0
UC1 24 disabled round-robin 0
UC0 0 disabled round-robin 0
MC0 0 disabled round-robin 0
switch(config-if-Et7-uc-txq-3)#Use the color command for the ability to configure the color extended community in route-map set clauses and in an extcommunity-list for inbound and outbound policy application.
Command Mode
Route-maps and extcommunity-lists
Command Syntax
color COLOR-VALUE [color-only [exact-match | [endpoint-match [any | null]]]]
switch(config)# route-map foo
switch(config0route-map-foo)# set community color 2 color-only endpoint-match any
The default dscp to traffic-class and no dscp to traffic-class commands restore the global map values for the given DSCP classes.
Command Mode
DSCP Map Configuration
Command Syntax
dscp dscp_classes to traffic-class traffic_class
default dscp dscp_classes to traffic-class
no dscp dscp_classes to traffic-class
Example
switch(config)# qos map dscp to traffic-class name map1
switch(config-dscp-map-map1)# dscp 35 to traffic-class 7
switch(config-dscp-map-map1)# dscp 20-25 to traffic-class 6The hardware access-list qos resource sharing vlan in command enables the ACL based QoS resources sharing on a VLAN interface.
The no hardware access-list qos resource sharing vlan in disables the ACL based QoS resources sharing on a VLAN interface. By default this function is disabled.
Command Mode
Global Configuration
Command Syntax
hardware access-list qos resource sharing vlan in
no hardware access-list qos resource sharing vlan in
Example
switch(config)# hardware access-list qos resource sharing vlan inThe interface fabric command places the switch in Fabric-interface configuration mode and allows the user to attach the QoS profile to the fabric interface of the switch.
Command Mode
Global Configuration
Command Syntax
interface fabric
Example
switch(config)# interface fabric
switch(config-if-fabric)# The ip extcommunity-list command adds a color extended community to an extcommunity-list. Multiple color extended communities can be added to the list. Negating the command removes the corresponding color extended community from the list.
Command Mode
Configuration mode
Command Syntax
ip extcommunity-list WORD [permit | deny][COLOR-EXPRESSION]
no ip extcommunity-list WORD [permit | deny] COLOR-EXPRESSION]
default ip extcommunity-list WORD [permit | deny][COLOR-EXPRESSION]
switch(config)# ip extcommunity-list foo permit color 1 color 2
switch(config)# ip extcommunity-list bar permit color 3 color-only endpoint-match null color 4 color-only endpoint-match anyThe mc-tx-queue command places the switch in mc-tx-queue configuration mode to configure a multicast transmit queue on the configuration mode interface. Mc-tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no mc-tx-queue and default mc-tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding mc-tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
mc-tx-queue queue_level
Parameterqueue_level The multicast transmit queue number. Values range from 0 to 3.
Related Command
uc-tx-queue Configures unicast transmit queues on Trident and Tomahawk platform switches.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# mc-tx-queue 3
switch(config-if-Et5-mc-txq-3)#The platform petraA traffic-class command configures the default traffic class used by all ports on a specified chip. The default traffic class is implemented by Petra platform switches to replace qos cos and qos dscp commands. Traffic class values range from 0 to 7. The default traffic class is 1.
The no platform petraA traffic-class and default platform petraA traffic-class commands restore the default traffic class of one for all ports on the specified chips by deleting the corresponding platform petraA traffic-class command from running-config.
Command Mode
Global Configuration
Command Syntax
platform petraA [CHIP_NAME] traffic-class tc_value
no platform petraA [CHIP_NAME] traffic-class
default platform petraA [CHIP_NAME] traffic-class
Parameters
7500 Series
Switches can contain up to eight linecards. CardX varies from 3 to 10.
7048 Series
Related Command
show platform petraA traffic-class displays the traffic class assignment on all specified Petra chips.
Example
switch(config)# platform petraA petra5/3 traffic-class 6
switch(config)#Tx-queue 7 is set to strict priority and is not configurable.
When a queue is configured as a round robin queue, all lower priority queues also function as round robin queues. A queue’s numerical label denotes its priority: higher labels denote higher priority. Tx-queue 6 has higher priority than Tx-queue 5, and Tx-queue 0 has the lowest priority.
The priority strict and default priority commands configure a transmit queue to function as a strict priority queue unless a higher priority queue is configured as a round robin queue.
The no priority command configures a transmit queue as a round robin queue. All lower priority queues also function as round robin queues regardless of their configuration.
Command Mode
Tx-Queue Configuration
Command Syntax
priority strict
no priority
default priority
Related Command
tx-queue (Arad/Jericho) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 3/4/1
switch(config-if-Et3/4/1)# show qos interfaces ethernet 3/4/1
Ethernet3/4/1:
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - 999 / 1000 ( Mbps ) SP / SP D
3 - / - 999 / 1000 ( Mbps ) SP / SP D
2 - / - - / - ( - ) SP / SP D
1 - / - - / - ( - ) SP / SP D
0 - / - - / - ( - ) SP / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/4/1)# tx-queue 3
switch(config-if-Et3/4/1-txq-3)# no priority
switch(config-if-Et3/4/1-txq-3)# show qos interfaces ethernet 3/4/1
Ethernet3/4/1:
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - 999 / 1000 ( Mbps ) SP / SP D
3 25 / - 999 / 1000 ( Mbps ) RR / RR D
2 25 / - - / - ( - ) RR / SP D
1 25 / - - / - ( - ) RR / SP D
0 25 / - - / - ( - ) RR / SP D
Note: Values are displayed as Operational/Configured
switch(config-if-Et3/4/1-txq-3)#When a queue is configured as a round robin queue, all lower priority queues also function as round robin queues. A queue’s numerical label denotes its priority: higher labels denote higher priority. Tx-queue 6 has higher priority than Tx-queue 5, and Tx-queue 0 has the lowest priority.
The priority strict and default priority commands configure a transmit queue to function as a strict priority queue unless a higher priority queue is configured as a round robin queue.
The no priority command configures a transmit queue as a round robin queue. All lower priority queues also function as round robin queues regardless of their configuration.
Command Mode
Tx-Queue Configuration
Command Syntax
priority strict
no priority
default priority
Related Command
tx-queue (FM6000) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 19
switch(config-if-Et19)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 N/A disabled strict
2 N/A disabled strict
1 N/A disabled strict
0 N/A disabled strict
switch(config-if-Et19)# tx-queue 3
switch(config-if-Et19-txq-3)# no priority
switch(config-if-Et19-txq-3)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 25 disabled round-robin
2 25 disabled round-robin
1 25 disabled round-robin
0 25 disabled round-robin
switch(config-if-Et19-txq-3)#Tx-queue 7 is set to strict priority and is not configurable.
When a queue is configured as a round robin queue, all lower priority queues also function as round robin queues. A queue’s numerical label denotes its priority: higher labels denote higher priority. Tx-queue 6 has higher priority than Tx-queue 5, and Tx-queue 0 has the lowest priority.
The priority strict and default priority commands configure a transmit queue to function as a strict priority queue unless a higher priority queue is configured as a round robin queue.
The no priority command configures a transmit queue as a round robin queue. All lower priority queues also function as round robin queues regardless of their configuration.
Command Mode
Tx-Queue Configuration
Command Syntax
priority strict
no priority
default priority
Related Command
tx-queue (Petra) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 3/28
switch(config-if-Et3/28)# show qos interface ethernet 3/28
Ethernet3/28:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 N/A disabled strict
2 N/A disabled strict
1 N/A disabled strict
0 N/A disabled strict
switch(config-if-Et3/28)# tx-queue 3
switch(config-if-Et3/28-txq-3)# no priority
switch(config-if-Et3/28-txq-3)# show qos interface ethernet 3/28
Ethernet3/28:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A disabled strict
3 25 disabled round-robin
2 25 disabled round-robin
1 25 disabled round-robin
0 25 disabled round-robin
switch(config-if-Et3/28-txq-3)#Priority group 1 queues are strict priority queues and are not configurable as round robin. Priority 0 queues are strict priority by default and are configurable as round robin. When a queue is configured as a round robin queue, all lower priority queues automatically function as round robin queues.
The priority strict and default priority commands configure a transmit queue to function as a strict priority queue unless a higher priority queue is configured as a round robin queue.
The no priority command configures a transmit queue as a round robin queue. All lower priority queues also function as round robin queues regardless of their configuration.
Command Mode
Mc-Tx-Queue configuration
Uc-Tx-Queue configuration
Command Syntax
priority strict
no priority
default priority
Example
switch(config) #interface ethernet 7
switch(config-if-Et7)# show qos interface ethernet 7
Ethernet7:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 N/A disabled strict 0
UC2 N/A disabled strict 0
MC1 N/A disabled strict 0
UC1 N/A disabled strict 0
UC0 N/A disabled strict 0
MC0 N/A disabled strict 0
switch(config-if-Et7)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# no priority
switch(config-if-Et7-uc-txq-3)# show qos interface ethernet 7
Ethernet7:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A disabled strict 0
UC3 20 disabled round-robin 0
UC2 16 disabled round-robin 0
MC1 16 disabled round-robin 0
UC1 16 disabled round-robin 0
UC0 16 disabled round-robin 0
MC0 16 disabled round-robin 0
switch(config-if-Et7-uc-txq-3)#The qos cos command specifies the default class of service (CoS) value of the configuration mode interface. CoS values range from 0 to 7. Default value is 0.
The no qos cos and default qos cos commands restore the port’s default CoS value to zero by deleting the corresponding qos cos command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
qos cos cos_value
no qos cos
default qos cos
Parameter
cos_valueCoS value assigned to port. Value ranges from 0 to 7. Default value is 0.
Example
switch(config-if-Et8)# qos cos 4
switch(config-if-Et8)#The no qos dscp and default qos dscp commands restore the port’s default DSCP value to zero by deleting the corresponding qos dscp command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
qos dscp dscp_value
no qos dscp
default qos dscp
Parameter
dscp_value DSCP value assigned to the port. Value ranges from 0 to 63. Default value is 0.
Example
switch(config)# interface ethernet 7
switch(config-if-Et7)# qos dscp 44
switch(config-if-Et7)The qos map cos command associates a traffic class to a list of class of service (CoS) settings. Multiple commands create a complete CoS to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s CoS field or the port upon which it is received. You can also configure a custom drop precedence for the QoS map.
The no qos map cos and default qos map cos commands restore the specified CoS values to the default traffic class setting by deleting the corresponding qos map cos statements from running-config.
Command Mode
Global Configuration
Command Syntax
qos map cos cos_value_1 [cos_value_2 ... cos_value_n] to traffic-class tc_value [drop-precedence dp_value]
no qos map cos cos_value_1 [cos_value_2 ... cos_value_n ]
default qos map cos cos_value_1 [cos_value_2 ... cos_value_n]
Default CoS to traffic class map varies by platform (Table 38 - Default CoS to Traffic Class Map).
Default Inbound CoS to Traffic Class Map
| Inbound CoS | untagged | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Arad /Jericho) | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (FM6000) | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Helix) | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Petra) | Assigned default traffic class | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Trident and Tomahawk) | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Trident II) | Derived: use default CoS as inbound CoS | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Example
switch(config)# qos map cos 1 3 5 7 to traffic-class 5
switch(config)#The qos map dscp command associates a traffic class to a set of Differentiated Services Code Point (DSCP) values. Multiple commands create a complete DSCP to traffic class map. The switch uses this map to assign a traffic class to data packets on the basis of the packet’s DSCP field or the chip upon which it is received.
This command configures the global DSCP to traffic-class map. To create additional named maps that can be attached to specific VRFs, use the qos map dscp to traffic-class command with the name option.
The no qos map dscp and default qos map dscp commands restore the specified DSCP values to their default traffic class settings by deleting corresponding qos map dscp statements from running-config.
Command Mode
Global Configuration
Command Syntax
qos map dscp dscpv_1 [dscpv_2...dscpv_n] to traffic-class tc_value
no qos map dscp dscpv_1 [dscpv_2...dscpv_n]
default qos map dscp dscpv_1 [dscpv_2...dscpv_n]
Default map varies by platform (Table 39 - Default DSCP to Traffic Class Map).
Default Inbound DSCP to Traffic Class Map
| Inbound DSCP | 0-7 | 8-15 | 16-23 | 24-31 | 32-39 | 40-47 | 48-55 | 56-63 |
| Traffic Class (Arad /Jericho) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (FM6000) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Helix) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Petra) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Trident and Tomahawk) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| Traffic Class (Trident II) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
switch(config)# qos map dscp 12 13 25 37 to traffic-class 3
switch(config)#
The no and default forms of the command remove the specified custom map.
Command Mode
Global Configuration
Command Syntax
qos map dscp to traffic-class name map_name
no qos map dscp to traffic-class name map_name
default qos map dscp to traffic-class name map_name
Parameters
map_name The name of the map to configure. If the map does not exist, it is created as a copy of the global DSCP-to-traffic-class map.
Example
switch(config)# qos map dscp to traffic-class name map1
switch(config-dscp-map-map1)#The qos map dscp to traffic-class command assigns a DSCP-to-traffic-class map to a VRF, replacing the global map or previous custom map. The switch uses this map to assign a traffic class to data packets routed to this VRF on the basis of the DSCP fields of these packets.
The no qos map dscp to traffic-class and default qos map dscp to traffic-map commands remove the assignment of a custom map from the VRF, restoring the global map. default traffic class settings by deleting corresponding qos map dscp statements from running-config.
Command Mode
MPLS Tunnel Termination VRF Configuration
Command Syntax
qos map dscp to traffic-class map_name
no qos map dscp to traffic-class map_name
default qos map dscp to traffic-class map_name
Parameter
map_name DSCP to traffic-class map name.
Example
switch(config)# mpls tunnel termination
switch(config-mpls-tunnel-termination)# vrf newVRF1
switch(config-tunnel-termination-vrf-newVRF1)# qos map dscp to traffic-class map1
switch(config-tunnel-termination-vrf-newVRF1)# exit
switch(config-mpls-tunnel-termination)# vrf newVRF2
switch(config-tunnel-termination-vrf-newVRF2)# qos map dscp to traffic-class map1
switch(config-tunnel-termination-vrf-newVRF2)# exit
switch(config-tunnel-termination)#The qos map traffic-class to cos command associates a class of service (CoS) to a list of traffic classes. Multiple commands create a complete traffic class to CoS map. The switch uses this map in CoS rewrite operations to fill the CoS field in outbound packets. This map is applicable to DSCP trusted ports and untrusted ports. CoS rewrite is disabled on CoS trusted ports. The show qos maps command displays the CoS to traffic class map.
The no qos traffic-class to cos and default qos traffic-class to cos commands restore the specified traffic class values to their default CoS settings by removing the corresponding qos map traffic-class to cos command from running-config.
Command Mode
Global Configuration
Command Syntax
qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to cos cos_value
no qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to cos
default qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to cos
Default Inbound Traffic Class to CoS Map
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (Arad and /Jericho) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (FM6000) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (Helix) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (Petra) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (Trident and Tomahawk) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
| CoS Rewrite Value (Trident II) | 1 | 0 | 2 | 3 | 4 | 5 | 6 | 7 |
Example
switch(config)# qos map traffic-class 1 3 5 to cos 2
switch(config)#The qos map traffic-class to dscp command associates a Differentiated Services Code Point (DSCP) value to a list of traffic classes. Multiple commands create a complete traffic class to DSCP map. The switch uses this map in DSCP rewrite operations to fill the DSCP field in outbound packets. This map is applicable to CoS trusted ports and untrusted ports but disabled by default on these ports. DSCP rewrite is disabled on DSCP trusted ports. The show qos maps command displays the traffic class to DSCP map.
The no qos traffic-class to dscp and default qos traffic-class to dscp commands restore the specified traffic class values to their default DSCP settings by removing the corresponding qos map traffic-class to dscp command from running-config.
Command Mode
Global Configuration
Command Syntax
qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to dscp dscp_value
no qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to dscp
default qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to dscp
Default Inbound Traffic Class to DSCP Map
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| DSCP Rewrite Value (FM6000) | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
| DSCP Rewrite Value (Helix) | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
| DSCP Rewrite Value (Trident and Tomahawk) | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
| DSCP Rewrite Value (Trident II) | 8 | 0 | 16 | 24 | 32 | 40 | 48 | 56 |
Example
switch(config)# qos map traffic-class 1 2 4 to dscp 17
switch(config)#The qos map traffic-class to mc-tx-queue command associates a multicast transmit queue to a list of traffic classes. Multiple commands create a complete traffic class to mc-tx-queue map. The switch uses this map to route outbound packets to transmit queues, which in turn schedules their transmission from the switch. The show qos maps command displays the traffic class to multicast transmit queue map.
The no qos traffic-class to mc-tx-queue and default qos traffic-class to mc-tx-queue commands restore the default traffic class to multicast transmit queue map for the specified traffic class values by removing the corresponding qos map traffic-class to mc-tx-queue command from running-config.
Command Mode
Global Configuration
Command Syntax
qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to mc-tx-queue mtq_value
no qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to mc-tx-queue
default qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to mc-tx-queue
Default Inbound Traffic Class to Multicast Transmit Queue Map
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Multicast Transmit Queue (Trident and Tomahawk) | 0 | 0 | 1 | 1 | 2 | 2 | 3 | 3 |
Example
switch(config)# qos map traffic-class 0 4 5 to mc-tx-queue 2
switch(config)#The qos map traffic-class to tx-queue command associates a transmit queue (tx-queue) to a list of traffic classes. Multiple commands create a complete traffic to tx-queue map. The switch uses this map to route outbound packets to transmit queues, which in turn schedules their transmission from the switch. The show qos maps command displays the transmit queue to traffic class map.
The no qos traffic-class to tx-queue and default qos traffic-class to tx-queue commands restore the specified traffic class values to their default transmit queue settings by removing the corresponding qos map traffic-class to tx-queue command from running-config.
Command Mode
Global Configuration
Command Syntax
qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to tx-queue txq_value
no qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to tx-queue
default qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to tx-queue
Restrictions
FM6000: When Priority Flow Control (PFC) is enabled, traffic classes are mapped to their corresponding transmit queues, regardless of existing qos map traffic-class to tx-queue statements.
Arad, Jericho, and Petra: Traffic class 7 always maps to transmit queue 7. This association is not editable.
Default Inbound Traffic Class to Transmit Queue Map
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue (Arad /Jericho) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue (FM6000) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue (Helix) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue (Petra) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Transmit Queue (Trident II) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
Example
switch(config)# qos map traffic-class 0 4 5 to tx-queue 4
switch(config)#The qos map traffic-class to uc-tx-queue command associates a unicast transmit queue to a list of traffic classes. Multiple commands create a complete traffic class to unicast transmit queue map. The switch uses this map to route outbound packets to transmit queues, which in turn schedules their transmission from the switch. The show qos maps command displays the traffic class to unicast transmit queue map.
The no qos traffic-class to uc-tx-queue and default qos traffic-class to uc-tx-queue commands restore the default traffic class to unicast transmit queue map for the specified traffic class values by removing the corresponding qos map traffic-class to uc-tx-queue command from running-config.
Command Mode
Global Configuration
Command Syntax
qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to uc-tx-queue utq_value
no qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to uc-tx-queue
default qos map traffic-class tc_num_1 [tc_num_2 ... tc_num_n] to uc-tx-queue
Default Inbound Traffic Class to Unicast Transmit Queue Map
| Traffic Class | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
| Unicast Transmit Queue (Trident and Tomahawk) | 0 | 1 | 2 | 3 | 4 | 5 | 6 | 7 |
Example
switch(config)# qos map traffic-class 0 4 5 to uc-tx-queue 4
switch(config)#The qos profile command places the switch in QoS profile configuration mode and for the specified profile and creates the profile if it does not already exist. QoS profiles are used to apply the same QoS configuration to multiple interfaces.
The no qos profile and default qos profile command deletes the QoS profile from the running configuration.
The exit command returns the switch to global configuration mode.
Command Mode
Global Configuration
Command Syntax
qos profile profile_name
no qos profile profile_name
default qos profile profile_name
Parameter
profile_name QoS profile name.
Example
switch(config)# qos profile TP
switch(config-qos-profile-TP)#The qos random-detect ecn allow non-ect chip-based enables per color queue thresholds using color based queue thresholds and drop-precedence values along with drop of non-ect traffic by allowing non-ect and set drop-precedence 1 in a policy map simultaneously.
The no qos random-detect ecn allow non-ect chip-based and default qos random-detect ecn allow non-ect chip-based commands disbales the use of non-ect and set drop-precedence 1 simultaneously in a policy map in the running-config.
Command Mode
Global Configuration
Command Syntax
qos random-detect ecn allow non-ect chip-based
no qos random-detect ecn allow non-ect chip-based
default qos random-detect ecn allow non-ect chip-based
Example
switch(config)# qos random-detect ecn allow non-ect chip-basedWhen transmitted packets are marked Non ECN Capable, congestion packets are dropped, not marked.
The no qos random-detect ecn global-buffer and default qos random-detect ecn global-buffer commands disables ECN marking for the shared buffer by removing the qos random-detect ecn global-buffer command from running-config.
Command Mode
Global Configuration
Command Syntax
qos random-detect ecn global-buffer minimum-threshold MIN maximum-threshold MAX
no qos random-detect ecn global-buffer
default qos random-detect ecn global-buffer
Parameters
Guidelines
Packet memory is divided into 46080 208-byte cells, whose allocation is managed by the memory management unit (MMU). The MMU tracks the cells that each entity uses and determines the number of cells that can be allocated to an entity.
Related Command
random-detect ecn (Helix) enables ECN marking for a unicast transmit queue.
switch(config)# qos random-detect ecn global-buffer minimum-threshold 20 segments
maximum-threshold 500 segments
switch(config)#switch(config)# no qos random-detect ecn global-buffer
switch(config)#When transmitted packets are marked Non ECN Capable, congestion packets are dropped, not marked.
The no qos random-detect ecn global-buffer and default qos random-detect ecn global-buffer commands disables ECN marking for the shared buffer by removing the qos random-detect ecn global-buffer command from running-config.
Command Mode
Global Configuration
Command Syntax
qos random-detect ecn global-buffer minimum-threshold MIN maximum-threshold MAX
no qos random-detect ecn global-buffer
default qos random-detect ecn global-buffer
Guidelines
Packet memory is divided into 46080 208-byte cells, whose allocation is managed by the memory management unit (MMU). The MMU tracks the cells that each entity uses and determines the number of cells that can be allocated to an entity.
Parameters
Related Command
random-detect ecn (Trident and Tomahawk) enables ECN marking for a unicast transmit queue.
switch(config)# qos random-detect ecn global-buffer minimum-threshold 20 segments maximum-threshold 500 segments
switch(config)#switch(config)# no qos random-detect ecn global-buffer
switch(config)#The qos rewrite cos command enables the rewriting of the CoS field for outbound tagged packets that were received on DSCP trusted ports and untrusted ports. CoS rewrite is always disabled on CoS trusted ports. The CoS value that is written into the packet is based on the data stream’s traffic class. CoS rewriting is active by default.
The no qos rewrite cos command disables CoS rewriting on the switch. The default qos rewrite cos command restores the default setting of enabling CoS rewriting by removing the no qos rewrite cos command from running-config.
Command Mode
Global Configuration
Command Syntax
qos rewrite cos
no qos rewrite cos
default qos rewrite cos
Related Command
qos map traffic-class to cos configures the traffic class to CoS rewrite map.
Example
switch(config)# qos rewrite cos
switch(config)#The qos rewrite dscp command enables the rewriting of the DSCP field for outbound tagged packets that were received on CoS trusted ports and untrusted ports. DSCP rewrite is always disabled on DSCP trusted ports. The DSCP value that is written into the packet is based on the data stream’s traffic class. DSCP rewriting is disabled by default.
The no qos rewrite dscp and default qos rewrite dscp commands disable DSCP rewriting on the switch by removing the no qos rewrite dscp command from running-config.
Command Mode
Global Configuration
Command Syntax
qos rewrite dscp
no qos rewrite dscp
default qos rewrite dscp
Related Command
qos map traffic-class to dscp configures the traffic class to DSCP rewrite map.
Example
switch(config)# qos rewrite dscp
switch(config)#The qos rewrite [ipv4-over-udp | ipv6-over-udp] command in the Global Configuration Mode enables rewriting the DSCP of the GUE encapsulated headers on IP-over-UDP tunnels while preserving the TOS value of the inner IP payload for IPv4 and IPv6.
The [no | default] versions of the command removes the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
qos rewrite [ipv4-over-udp | ipv6-over-udp] inner dscp disabled
Example
switch(config)# qos rewrite ipv4-over-udp inner dscp disabled
switch(config)#The qos tx-queue shape rate precision command in the Global Configuration Mode configures Tx Queue Precision Shaping on switches with a low configured rate. The [no | default] versions of the command disables the configuration.
Command Mode
Global Configuration
Command Syntax
qos tx-queue shape rate precision 50Mbps
no qos tx-queue shape rate precision
default qos tx-queue shape rate precision
Parameters
precision 50Mbps - Specifies the minimum speed that requires precision shaping. Currently, EOS only supports 50Mbps.
Example
switch(config)# qos tx-queue shape rate precision 50Mbps
! Change will take effect only after switch reboot.The qos subinterface command in the Global Configuration Mode configures subinterface behaviors for Quality of Service (QoS).
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
qos subinterface [port-channel [load-balancing | rebalancing]] [tx-queue [allocation always] [count [4 | 8]]
no qos subinterface
default qos subinterface
Example
switch(config)# qos subinterface port-channel load-balancing
switch(config)#The qos subinterface command in the Global Configuration Mode configures subinterface scheduling behaviors for Quality of Service (QoS).
The [no | default] versions of the command disable the feature and remove the configuration from the running-config.
Command Mode
Global Configuration
Command Syntax
qos subinterface scheduling [parent round-robin] [priority propagation]
no qos subinterface
default qos subinterface
Example
switch(config)# qos subinterface scheduling parent round-robin
switch(config)#The qos trust command configures the quality of service port trust mode for the configuration mode interface. Trust-enabled ports classify traffic by examining the traffic’s CoS or DSCP value. Port trust mode default setting is cos for switched interfaces and dscp for routed interfaces.
The default qos trust command restores the default trust mode on the configuration mode interface by removing the corresponding qos trust or no qos trust statement from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
qos trust [MODE]
no qos trust [MODE]
default qos trust
switch(config)# interface ethernet 7
switch(config-if-Et7)# qos trust dscp
switch(config-if-Et7)# show active
interface Ethernet7
qos trust dscp
switch(config-if-Et7)#switch(config)# interface port-channel 23
switch(config-if-Po23)# no qos trust
switch(config-if-Po23)# show active
interface Port-Channel23
no qos trust
switch(config-if-Po23)#When transmitted packets are marked Non ECN Capable, congestion packets are dropped, not marked.
The no random-detect ecn and default qos random-detect ecn commands disables ECN marking for the shared buffer by removing the qos random-detect ecn command from running-config.
Command Mode
Tx-Queue configuration
Command Syntax
random-detect ecn minimum-threshold [MIN | MAX]| maximum-threshold [MIN | MAX]
no random-detect ecn
default random-detect ecn
Parameters
Related Command
tx-queue (Arad/Jericho) places the switch in tx-queue configuration mode.
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 4
switch(config-if-Et3/5/1-txq-4)# random-detect ecn minimum-threshold 128 kbytes
maximum-threshold 1280 kbyte
switch(config-if-Et3/5/1-txq-4)# show active
interface Ethernet3/5/1
tx-queue 4
random-detect ecn minimum-threshold 128 kbytes maximum-threshold 1280 kbytes
switch(config-if-Et3/5/1-txq-4)#When transmitted packets are marked Non ECN Capable, congestion packets are dropped, not marked.
Average queue length is tracked for transmit queues and the global pool independently. When either entity reaches its maximum threshold, all subsequent packets are marked.
The no random-detect ecn and default random-detect ecn commands disable ECN marking on the configuration mode queue, deleting the corresponding random-detect ecn command from running-config.
Command Mode
Tx-Queue configuration
Command Syntax
random-detect ecn minimum-threshold [MIN | MAX] maximum-threshold [MIN | MAX]
no random-detect ecn
default random-detect ecn
Parameters
switch(config)# interface ethernet 15
switch(config-if-Et15)# uc-tx-queue 4
switch(config-if-Et15-txq-4)# random-detect ecn minimum-threshold 10 segments
maximum-threshold 100 segments
switch(config-if-Et15-txq-4)# show active
interface Ethernet15
tx-queue 4
random-detect ecn minimum-threshold 10 segments maximum-threshold 100
segments
switch(config-if-Et15-txq-4)# exit
switch(config-if-Et15)switch(config-if-Et15-txq-4)# no random-detect ecn
switch(config-if-Et15-txq-4)# show active
interface Ethernet15
switch(config-if-Et15-txq-4)# exit
switch(config-if-Et15)#When transmitted packets are marked Non ECN Capable, congestion packets are dropped, not marked.
Average queue length is tracked for transmit queues and the global pool independently. When either entity reaches its maximum threshold, all subsequent packets are marked.
The no random-detect ecn and default random-detect ecn commands disable ECN marking on the configuration mode queue, deleting the corresponding random-detect ecn command from running-config.
Command Mode
Uc-Tx-Queue configuration
Command Syntax
random-detect ecn minimum-threshold [MIN |MAX] maximum-threshold[MIN | MAX]
no random-detect ecn
default random-detect ecn
Parameters
switch(config)# interface ethernet 15
switch(config-if-Et15)# uc-tx-queue 4
switch(config-if-Et15-uc-txq-4)# random-detect ecn minimum-threshold 10 segments
maximum-threshold 100 segments
switch(config-if-Et15-uc-txq-4)#show active
interface Ethernet15
uc-tx-queue 4
random-detect ecn minimum-threshold 10 segments maximum-threshold 100
segments
switch(config-if-Et15-uc-txq-4)# exit
switch(config-if-Et15)#switch(config-if-Et15-uc-txq-4)# no random-detect ecn
switch(config-if-Et15-uc-txq-4)# show active
interface Ethernet15
switch(config-if-Et15-uc-txq-4)# exit
switch(config-if-Et15)#The random-detect ecn delay threshold command configures latency-based ECN on a per transmit queue basis.
The [no|default] version of the command disables the configuration and deletes the random-detect ecn delay threshold from the running-config.
Command Mode
Interface Configuration
Command Syntax
random-detect ecn delay threshold [microseconds | milliseconds ]
Example
switch(config)# interface Ethernet 1/1
switch(config-if-Et1/1)# tx-queue 3
switch(config-if-Et1/1-txq-3)# random-detect ecn delay threshold 33 millisecondsThe service-policy type qos input command applies the specified policy map to a QoS profile. The profile is then applied to an interface in interface configuration mode using the service-profile command.
The no service-policy type qos and default service-policy type qos command deletes the policy map from the profile.
The exit command returns the switch to global configuration mode.
Command Mode
QoS Profile Configuration
Command Syntax
service-policy type qos input policy_map_name
no service-policy type qos input policy_map_name
default service-policy type qos input policy_map_name
Parameter
policy_map_name - Specify a QoS policy map name.
Example
switch(config-qos-profile-TP)# service-policy type qos input PM-1
switch(config-qos-profile-TP)#The command applies the QoS profile to the configuration mode interface.
The no service-profile and the default service-profile command removes the QoS profile from the interface.
The exit command returns the switch to global configuration mode.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
service-profile profile_name
no service-profile profile_name
default service-profile profile_name
Parameter
profile_name QoS profile name.
Example
switch(config)# interface ethernet 13
switch(config-if-Et13)# service-profile TPThe set extcommunity command adds a color extended community to be applied to routes affected by the route-map. Multiple set clauses can be applied to a single route-map to configure multiple colors for routes.Negating the command removes the entry from the route-map.
Command Mode
Config-route-map mode
Command Syntax
set extcommunity COLOR-EXPRESSION [additive | delete]
no set extcommunity COLOR-EXPRESSION [additive | delete]
default set extcommunity COLOR-EXPRESSION [additive | delete]
switch(config)# route-map foo
switch(config-route-map foo)# set extcommunity color 1
switch(config-route-map foo)# set extcommunity color 2 color-only exact-match
switch(config-route-map foo)# set extcommunity color 3 color-only endpoint-match null
switch(config-route-map foo)# set extcommunity color 4 color-only endpoint-match anyThe shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Tx-queue – Arad/Jericho) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameters
byte_limit Shape rate applied to interface (Kbps). Value ranges from 162 to 100000000.
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# shape rate 5000000
switch(config-if-Et3/5/1)# show qos interfaces ethernet 3/5/1
Ethernet3/5/1:
Port shaping rate: 5000012 / 5000000 kbps
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - - / - ( - ) SP / SP D
3 - / - - / - ( - ) SP / SP D
2 - / - - / - ( - ) SP / SP D
1 - / - - / - ( - ) SP / SP D
0 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/5/1)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Tx-queue – FM6000) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameter
byte_limit Shape rate applied to interface (Kbps). Value ranges from 7000 to 10000000.
Guidelines
Enabling port shaping on an FM6000 interface disables queue shaping internally. Disabling port shaping restores queue shaping as specified in running-config.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# shape rate 5000000
switch(config-if-Et5)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Interface – Helix) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate DATA_LIMIT
no shape rate
default shape rate
Guidelines
Shaping rates of at least 8 kbps are supported. At shaping rates smaller than 1 Mbps, granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
Example
switch(config)# interface ethernet 17
switch(config-if-Et17)# shape rate 5000000 kbps
switch(config-if-Et17)# show qos interface ethernet 17/3
Ethernet17:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: 5000000 / 5000000 kbps
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
switch(config-if-Et17)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Tx-queue – Petra) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate data_limit [kbps]
no shape rate
default shape rate
Parameters
data_limit Shape rate applied to interface (Kbps). Value ranges from 100 to 10000000.
Guidelines
Commands that specify a smaller shape rate disable port shaping on the interface.
Example
switch(config)# interface ethernet 3/3
switch(config-if-Et3/3)# shape rate 5000000
switch(config-if-Et3/3)# show active
interface Ethernet3/3
shape rate 5000000
switch(config-if-Et3/3)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Tx-queue – Trident and Tomahawk) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate DATA_LIMIT
no shape rate
default shape rate
Guidelines
Shaping rates of at least 8 kbps are supported. At shaping rates smaller than 1 Mbps, granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# shape rate 5000000
switch(config-if-Et5)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode interface, also known as queue shaping. The shape rate for individual transmit queues is configured by the shape rate (Tx-queue – Trident II) command. By default, outbound transmission rate is not bounded by a shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode interface by deleting the corresponding shape rate command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
shape rate DATA_LIMIT
no shape rate
default shape rate
Parameters
8 to 60000000 pps 8 to 60000000 packets per second.
Guidelines
Shaping rates of at least 8 kbps are supported. At shaping rates smaller than 1 Mbps, granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# shape rate 5000000 kbps
switch(config-if-Et17/3)# show qos interface ethernet 17/3
Ethernet17/3:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: 5000000 / 5000000 kbps
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
switch(config-if-Et17/3)#The shape rate command specifies the maximum bandwidth for outbound traffic on the transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – Arad/Jericho) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
Shaping rates greater than 50000 kbps are supported. At lower shaping rates (less than 10 Mbps), granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode queue by deleting the corresponding shape rate command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameters
byte_limit Shape rate applied to interface (Kbps). Value ranges from 50000 to 100000000.
Related Command
tx-queue (Arad/Jericho) places the switch in tx-queue configuration mode.
Related Information
shape rate (Interface – Arad/Jericho)
Example
switch(config)# interface ethernet 3/4/1
switch(config-if-Et3/4/1)# tx-queue 4
switch(config-if-Et3/4/1-txq-4)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-4)# tx-queue 3
switch(config-if-Et3/4/1-txq-3)# shape rate 1000000 kbps
switch(config-if-Et3/4/1-txq-3)# show qos interface ethernet 3/4/1
Ethernet3/4/1:
Port shaping rate: disabled
Tx Bandwidth Shape Rate Priority ECN
Queue (percent) (units)
-----------------------------------------------------
7 - / - - / - ( - ) SP / SP D
6 - / - - / - ( - ) SP / SP D
5 - / - - / - ( - ) SP / SP D
4 - / - 999 / 1000 ( Mbps ) SP / SP D
3 - / - 999 / 1000 ( Mbps ) SP / SP D
2 - / - - / - ( - ) SP / SP D
1 - / - - / - ( - ) SP / SP D
0 - / - - / - ( - ) SP / SP D
switch(config-if-Et3/4/1-txq-3)#The shape ratecommand specifies the maximum bandwidth for outbound traffic on the transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – FM6000) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
Queue shaping on an FM6000 port is supported only when port shaping is not enabled on the interface. Enabling port shaping on a port disables queue shaping internally. Disabling port shaping restores queue shaping as specified by running-config.
Shaping rates greater than 460 kbps are supported. At lower shaping rates (less than 10 Mbps), granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the transmit queue by deleting the corresponding shape rate command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameters
byte_limit Shape rate applied to interface (Kbps). Value ranges from 464 to 10000000.
Example
switch(config)# interface ethernet 19
switch(config-if-Et19)# tx-queue 4
switch(config-if-Et19-txq-4)# shape rate 1000000
switch(config-if-Et19-txq-4)# tx-queue 3
switch(config-if-Et19-txq-3)# shape rate 1000000
switch(config-if-Et19-txq-3)# show qos interface ethernet 19
Ethernet19:
Trust Mode: COS
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
6 N/A disabled strict
5 N/A disabled strict
4 N/A 1000000 strict
3 25 1000000 round-robin
2 25 disabled round-robin
1 25 disabled round-robin
0 25 disabled round-robin
switch(config-if-Et19-txq-3)#The shape rate command specifies the maximum bandwidth for outbound traffic on the transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – Helix) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode transmit queue by deleting the corresponding shape rate command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameters
Restrictions
Queue shaping is not supported in cut-through mode.
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)# shape rate 1000000 kbps
switch(config-if-Et17/3-txq-4)# tx-queue 3
switch(config-if-Et17/3-txq-3)# shape rate 1000000 kbps
switch(config-if-Et17/3-txq-3)# show qos interface ethernet 17/3
Ethernet17/3:
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) - / - ( - ) SP / SP
4 - / - ( - ) 1 / 1 ( Gbps ) SP / SP
3 - / - ( - ) 1 / 1 ( Gbps ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) - / - ( - ) SP / SP
0 - / - ( - ) - / - ( - ) SP / SP
switch(config-if-Et17/3-txq-3)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – Petra) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
Queue shaping applies only to unicast traffic. Shaping rates of at least 162 Kbps are supported.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode queue by deleting the corresponding shape rate command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
shape rate DATA_LIMIT
no shape rate
default shape rate
Parameters
Shaping rates greater than 460 kbps are supported. At lower shaping rates (less than 10 Mbps), granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
Example
switch(config)# interface ethernet 3/28
switch(config-if-Et3/28)# tx-queue 4
switch(config-if-Et3/28-txq-4)# shape rate 1000000
switch(config-if-Et3/28-txq-4)# tx-queue 3
switch(config-if-Et3/28-txq-3)# shape rate 1000000
switch(config-if-Et3/28-txq-3)# show qos interface ethernet 3/28
Ethernet3/28:
Tx-Queue Bandwidth Shape Rate Priority
(percent) (Kbps)
-----------------------------------------------
7 N/A disabled strict
6 N/A disabled strict
5 N/A disabled strict
4 N/A 1000000 strict
3 25 1000000 round-robin
2 25 disabled round-robin
1 25 disabled round-robin
0 25 disabled round-robin
switch(config-if-Et3/28-txq-3)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – Trident and Tomahawk) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
The no shape rate and default shape rate commands remove the shape rate limit from the configuration mode transmit queue by deleting the corresponding shape rate command from running-config.
Command Mode
Mc-Tx-Queue configuration
Uc-Tx-Queue configuration
Command Syntax
shape rate DATA_LIMIT
no shape rate
default shape rate
Parameters
Guidelines
Shaping rates of at least 8 kbps are supported. At shaping rates smaller than 1 Mbps, granularity and rounding errors may skew the actual shaping rate by 20% from the specified rate.
When two queues source traffic from the same traffic class and the higher priority queue is shaped, that queue consumes all internal buffers, starving the lower priority queue even if bandwidth is available.
Example
switch(config)# interface ethernet 7
switch(config-if-Et7)# uc-tx-queue 3
switch(config-if-Et7-uc-txq-3)# shape rate 1000000
switch(config-if-Et7-uc-txq-3)# mc-tx-queue 2
switch(config-if-Et7-mc-txq-2)# shape rate 1000000
switch(config-if-Et7-mc-txq-2)# show qos interface ethernet 7
Ethernet7:
Tx-Queue Bandwidth Shape Rate Priority Priority Group
(percent) (Kbps)
----------------------------------------------------------------
UC7 N/A disabled strict 1
UC6 N/A disabled strict 1
MC3 N/A disabled strict 1
UC5 N/A disabled strict 0
UC4 N/A disabled strict 0
MC2 N/A 1000000 strict 0
UC3 20 1000000 round-robin 0
UC2 16 disabled round-robin 0
MC1 16 disabled round-robin 0
UC1 16 disabled round-robin 0
UC0 16 disabled round-robin 0
MC0 16 disabled round-robin 0
switch(config-if-Et7-mc-txq-2)#The shape rate command specifies the maximum bandwidth for outbound traffic on the configuration mode transmit queue, also known as queue shaping. The shape rate for interfaces is configured by the shape rate (Interface – Trident II) command. By default, the configured outbound transmission rate is not bounded by a transmit queue shape rate.
The no shape rate and default shape rate commands remove the shape rate bandwidth limit on the configuration mode transmit queue by deleting the corresponding shape rate command from running-config.
Command Mode
Tx-Queue Configuration
Command Syntax
shape rate byte_limit [kbps]
no shape rate
default shape rate
Parameters
Restrictions
Queue shaping is not supported in cut-through mode
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)# shape rate 1000000 kbps
switch(config-if-Et17/3-txq-4)# tx-queue 3
switch(config-if-Et17/3-txq-3)# shape rate 1000000 kbps
switch(config-if-Et17/3-txq-3)# show qos interface ethernet 17/3
Ethernet17/3:
Tx Bandwidth Shape Rate Priority
Queue Guaranteed (units) (units)
------------------------------------------------------------
7 - / - ( - ) - / - ( - ) SP / SP
6 - / - ( - ) - / - ( - ) SP / SP
5 - / - ( - ) - / - ( - ) SP / SP
4 - / - ( - ) 1 / 1 ( Gbps ) SP / SP
3 - / - ( - ) 1 / 1 ( Gbps ) SP / SP
2 - / - ( - ) - / - ( - ) SP / SP
1 - / - ( - ) - / - ( - ) SP / SP
0 - / - ( - ) - / - ( - ) SP / SP
switch(config-if-Et17/3-txq-3)#The show interface counters queue drop-precedence command displays the drop-precedence counters.
Command Mode
EXEC
Command Syntax
show interface counters queue drop-precedence
Example
switch# show interface counters queue drop-precedence
intf 0 1 2
Et1/1 100 0 200
Et1/2 200 0 300
switch#The show platform petraA traffic-class command displays the traffic class assignment on all specified Petra chips. Each chip controls eight Ethernet interfaces. The default traffic class of an interface is specified by the traffic class assigned to the chip that controls the interface.
Traffic class assignments are configured with the platform petraA traffic-class command.
Command Mode
EXEC
Command Syntax
show platform petraA traffic-class
show platform petraA CHIP_NAME traffic-class
show platform petraA MODULE_NAME traffic-class
7500 Series
Switches can contain up to eight linecards. cardX varies from 3 to 10.
7048 Series
Related Command
platform petraA traffic-class configures the default traffic class used by all ports on a specified chip.
Example
switch# show platform petraA module linecard 3 traffic-class
Petra3/0 traffic-class: 1
Petra3/1 traffic-class: 1
Petra3/2 traffic-class: 1
Petra3/3 traffic-class: 1
Petra3/4 traffic-class: 5
Petra3/5 traffic-class: 1
switch#The show platform trident tcam qos detail command displays the list of all the SVIs that are sharing the TCAM entries.
Command Mode
EXEC
Command Syntax
show platform trident tcam qos detail
Example
switch(config)# show platform trident tcam qos detail
=== Policy-map p01 type qos on switch Linecard0/0 ===
Interfaces : Vlan2 Vlan1
=-= Interface BitMap =-=
0x000000000000000001FFFFFEThe show platform trident tcam shared vlan interface-class-id command displays what SVIs are currently sharing the QoS policy-map in the below output under QoS PMAP Data.
Command Mode
EXEC
Command Syntax
show platform trident tcam shared vlan interface-class-id
Example
switch(config)# show platform trident tcam shared vlan interface-class-id
=== Shared RACL Data on switch Linecard0/0 ===
=== Shared QoS Policy-map Data on switch Linecard0/0 ===
Interface Class Id VLANs
1 1 2The show platform xp qos tcam hit command displays the TCAM entries programmed for each policy-map as well as the traffic hits. The hits option is used to see the TCAM entries with nonzero traffic hits.
Command Mode
EXEC
Command Syntax
show platform xp qos tcam hit
Example
switch# show platform xp qos tcam hit
=== Policy-map test type qos on switch 0 ===
Assigned to ports: Ethernet10/1
=-= Class-map test type qos =-=
=== ACL test
=========================================================================================
|Seq|AclId|Prot|Port|SPort|Ecn|FFlg|DPort|Vlan|Action|Hits|Src Ip|Dest Ip|hwId | | | | | | | |dscp|cos |tc|PolId| | | |
=========================================================================================
| 10| 0x01| | | | |0x04| | | 4 |- | - | - |91852787| | | | 0 | 0x00 | | | | |0xfb| | | | | |
-----------------------------------------------------------------------------------------The show policy-map interface command displays contents of the policy map applied to specified the interface.
Command Mode
EXEC
Command Syntax
show policy-map interface interface_name
Parameters
Example
switch# show policy-map interface ethernet 1
Service-policy input: p1
Hardware programming status: Successful
Class-map: c2001 (match-any)
Match: vlan 2001 0xfff
set dscp 4
Class-map: c2002 (match-any)
Match: vlan 2002 0xfff
set dscp 8
Class-map: c2003 (match-any)
Match: vlan 2003 0xfff
set dscp 12The show policy-map command displays the policy map information for the configured policy map.
Command Mode
EXEC
Command Syntax
show policy-map policy_map_name [counters][interface | summary]
switch# show policy-map policy1
Service-policy policy1
Class-map: class1 (match-any)
Match: ip access-group name acl1
Police cir 512000 bps bc 96000 bytes
Class-map: class-default (match-any)switch# show policy-map policy1 counters
Service-policy input: policy1
Hardware programming status: Successful
Class-map: class1 (match-any)
Match: vlan 20-40,1000-1250
police rate 100 mbps burst-size 100 kbytes
Interface: Ethernet16/1
Conformed 28621 packets, 7098008 bytes -------------- packet match count
Class-map: class-default (match-any)
Matched Packets: 19 -------------- packet match countThe show qos interfaces random-detect ecn command displays the Explicit Congestion Notification (ECN) configuration for each transmit queue on the specified interfaces.
Command Mode
EXEC
Command Syntax
show qos interfaces [INTERFACE_NAME] random-detect ecn
Parameters
Example
switch(config)# interface ethernet 3/5/1
switch(config-if-Et3/5/1)# tx-queue 0
switch(config-if-Et3/5/1-txq-0)# random-detect ecn minimum-threshold 2560 kbytes
maximum-threshold 256000 kbytes
switch(config-if-Et3/5/1-txq-0)# tx-queue 1
switch(config-if-Et3/5/1-txq-1)# random-detect ecn minimum-threshold 25600 kbytes
maximum-threshold 128000 kbytes
switch(config-if-Et3/5/1-txq-1)# tx-queue 2
switch(config-if-Et3/5/1-txq-2)# random-detect ecn minimum-threshold 25600 bytes
maximum-threshold 128000 bytes
switch(config-if-Et3/5/1-txq-2)# tx-queue 3
switch(config-if-Et3/5/1-txq-3)# random-detect ecn minimum-threshold 25 mbytes
maximum-threshold 128 mbytes
switch(config-if-Et3/5/1-txq-3)# show qos interfaces ethernet 3/5/1 random-detect
ecn
Ethernet3/5/1:
Tx-Queue Mininimum Threshold Maximum Threshold Threshold Unit
---------------------------------------------------------------------
7 - - -
6 - - -
5 - - -
4 - - -
3 25 128 mbytes
2 25600 128000 bytes
1 25600 128000 kbytes
0 2560 256000 kbytes
switch(config-if-Et3/5/1-txq-3)#The show qos interfaces trust command displays the configured and operational QoS trust mode of all specified interfaces.
Command Mode
EXEC
Command Syntax
show qos interfaces [INTERFACE_NAME] trust
Parameters
Example
switch(config)# interface ethernet 1/1
switch(config-if-Et1/1)# qos trust cos
switch(config-if-Et1/1)# interface ethernet 1/2
switch(config-if-Et1/2)# qos trust dscp
switch(config-if-Et1/2)# interface ethernet 1/3
switch(config-if-Et1/3)# no qos trust
switch(config-if-Et1/3)# interface ethernet 1/4
switch(config-if-Et1/4)# default qos trust
switch(config-if-Et1/4)# interface ethernet 2/1
switch(config-if-Et2/1)# no switchport
switch(config-if-Et2/1)# default qos trust
switch(config-if-Et2/1)# show qos interface ethernet 1/1 - 2/4 trust
Port Trust Mode
Operational Configured
---------------------------------------------------------------
Ethernet1/1 COS COS
Ethernet1/2 DSCP DSCP
Ethernet1/3 UNTRUSTED UNTRUSTED
Ethernet1/4 COS DEFAULT
Ethernet2/1 DSCP DEFAULT
Ethernet2/2 COS DEFAULT
Ethernet2/3 COS DEFAULT
Ethernet2/4 COS DEFAULT
switch(config-if-Et2/1)#The show qos interfaces command displays the QoS, DSCP, and transmit queue configuration on a specified interface. Information provided by this command includes the ports trust setting, the default CoS value, and the DSCP value.
Command Mode
EXEC
Command Syntax
show qos interfaces INTERFACE_NAME
Parameters
Example
switch> show qos interfaces ethernet 4
Ethernet4:
Trust Mode: COS
Default COS: 0
Default DSCP: 0
Port shaping rate: 5000000Kbps
Tx-Queue Bandwidth ShapeRate Priority
(percent) (Kbps)
-----------------------------------------------
0 50 disabled round-robin
1 50 disabled round-robin
2 N/A disabled strict
3 N/A 1000000 strict
4 N/A 1000000 strict
5 N/A 1500000 strict
6 N/A 2000000 strict
switch>The show qos interfaces latency maximum command displays the maximum latency tail-drop threshold active on each Tx queue for a specified interface.
Command Mode
EXEC
Command Syntax
show qos interfaces INTERFACE_NAME latency maximum
Parameters
INTERFACE_NAME Name of the interface.
Example
switch# show qos interfaces ethernet 23/1 latency maximum
Ethernet23/1:
Tx Queue Maximum Latency
-------- ---------------
7 -
6 -
5 -
4 -
3 10 ms
2 -
1 -
0 -
switch# show qos profile
qos profile latency
tx-queue 3
latency maximum 4000 microseconds
Tx-queue 4
latency maximum 30 millisecondsThe show qos maps command lists the number of traffic classes that the switch supports and displays the CoS-Traffic Class, DSCP-Traffic Class, Traffic Class-CoS, and Traffic Class-Transmit Queue maps.
Command Mode
EXEC
Command Syntax
show qos maps
Example
switch> show qos maps
Number of Traffic Classes supported: 8
Number of Transmit Queues supported: 8
Cos Rewrite: Disabled
Dscp Rewrite: Disabled
Cos-tc map:
cos: 0 1 2 3 4 5 6 7
----------------------------
tc: 1 0 2 3 4 5 6 7
Dscp-tc map:
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 2 2 2 2 3 3 3 3 3 3
3 : 3 3 4 4 4 4 4 4 4 4
4 : 5 5 5 5 5 5 5 5 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
Tc-cos map:
tc: 0 1 2 3 4 5 6 7
----------------------------
cos: 1 0 2 3 4 5 6 7
Tc-dscp map:
tc: 0 1 2 3 4 5 6 7
-----------------------------
dscp: 8 0 16 24 32 40 48 56
Tc - tx-queue map:
tc: 0 1 2 3 4 5 6 7
---------------------------------
tx-queue: 0 1 2 3 4 5 6 7
switch>
Command Mode
Privileged EXEC mode
Command Syntax
show qos map dscp to traffic-class [ map_name ]
Parameters
map_name The name of the DSCP to traffic-class map. If this is not specified, all DSCP to TC maps are shown.
Example
switch#show qos map dscp to traffic-class map1
DSCP to TC map: map1
d1 : d2 0 1 2 3 4 5 6 7 8 9
--------------------------------------
0 : 1 1 1 1 1 1 1 1 0 0
1 : 0 0 0 0 0 0 2 2 2 2
2 : 6 6 6 6 6 6 3 3 3 3
3 : 3 3 4 4 4 7 4 4 4 4
4 : 5 5 5 5 5 5 5 5 6 6
5 : 6 6 6 6 6 6 7 7 7 7
6 : 7 7 7 7
switch#The show qos profile summary command displays the QoS profile summary of those which are part of the running configuration.
Command Mode
EXEC
Command Syntax
show qos profile summary
Example
switch(config)# show qos profile summary
Qos Profile: p
Configured on: Et13,7
Fabric
Po12
Qos Profile: p2
Configured on: Et56The show qos profile command displays the contents of the specified QoS profile or of all QoS profiles in the running configuration.
Command Mode
EXEC
Command Syntax
show qos profile profile_name
Parameter
profile_name QoS profile name.
switch(config)# show qos profile
qos profile p
qos cos 1
no priority-flow-control pause watchdog
priority-flow-control priority 1 no-drop
priority-flow-control priority 2 no-drop
qos profile p2
qos cos 3
priority-flow-control priority 0 no-dropswitch# show qos profile p2
qos profile p2
qos cos 3
priority-flow-control priority 0 no-dropThe command displays the global Explicit Congestion Notification (ECN) configuration.
Command Mode
EXEC
Command Syntax
show qos random-detect ecn
Example
switch(config)# qos random-detect ecn global-buffer minimum-threshold 2 mbytes
maximum-threshold 5 mbytes
switch(config)# show qos random-detect ecn
Minimum Threshold: 2
Maximum Threshold: 5
Threshold Unit: mbytes
switch(config)#The show qos tx-queue shape rate precision command displays information about Tx Queue Precision Shaping on a switch.
Command Mode
EXEC
Command Syntax
show qos tx-queue shape rate precision
Example
switch# show qos tx-queue shape rate precision
Configured Operational
---------------- -----------
50 Mbps NoneTheshow run|grep sharing command displays whether the QoS policy-map sharing on SVIs is enabled or disabled.
Command Mode
EXEC
Command Syntax
show run|grep sharing
Example
switch# show run|grep sharing
hardware access-list qos resource sharing vlan in ---- If this message is displayed then QoS policy-map sharing on SVIs is enabled.
The tx-queue command places the switch in Tx-queue configuration mode to configure a transmit queue on the configuration mode interface. Tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
Arad and Jericho platform switches have eight queues, 0 through 7, and all queues are exposed through the CLI. However, queue 7 is not user-configurable. Queue 7 is always mapped to traffic class 7, which is reserved for control traffic.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no tx-queue and default tx-queue commands remove the configuration for the specified transmit queue by deleting all corresponding tx-queue mode statements from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
tx-queue queue_level
Parameters
queue_level The transmit queue. Values range from 0 to 7.
Guidelines
Arad and Jericho platform switch queues handle unicast traffic. Queues for multicast traffic are not supported.
Example
switch(config)# interface ethernet 3/3/3
switch(config-if-Et3/3/3)# tx-queue 4
switch(config-if-Et3/3/3-txq-4)#The tx-queue command places the switch in Tx-queue configuration mode to configure a transmit queue on the configuration mode interface. Tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
FM6000 platform switches have eight queues, 0 through 7. All queues are exposed through the CLI and are user configurable.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no tx-queue and default tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
tx-queue queue_level
Parameter
queue_level The transmit queue. Values range from 0 to 7.
Guidelines
FM6000 platform switch queues handle unicast and multicast traffic.
Example
switch(config)# interface ethernet 5
switch(config-if-Et5)# tx-queue 3
switch(config-if-Et5-txq-3)#The tx-queue command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. The tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
Helix platform switches have eight unicast (UC0 – UC7) and eight multicast (MC0 – MC7) queues. Each UCx-MCx queue set is combined into a single queue group (L1.x), which is exposed to the CLI through this command.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no tx-queue and default tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
tx-queue queue_level
Parameter
queue_level Transmit queue group number. Values range from 0 to 7.
Guidelines
Helix platform switch queues handle unicast and multicast traffic.
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)#The tx-queue command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. The tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
Petra platform switches have eight queues, 0 through 7, and all queues are exposed through the CLI. However, queue 7 is not user-configurable. Queue 7 is always mapped to traffic class 7, which is reserved for control traffic.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no tx-queue and default tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
tx-queue queue_level
Parameter
queue_level The transmit queue. Values range from 0 to 7.
Guidelines
Petra platform switch queues handle unicast traffic. Queues for multicast traffic are not supported.
Example
switch(config)# interface ethernet 3/3
switch(config-if-Et3/3)# tx-queue 3
switch(config-if-Et3/3-txq-3)#The tx-queue command places the switch in tx-queue configuration mode to configure a transmit queue on the configuration mode interface. The tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
Trident II platform switches have eight unicast (UC0 – UC7) and eight multicast (MC0 – MC7) queues. Each UCx-MCx queue set is combined into a single queue group (L1.x), which is exposed to the CLI through this command.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no tx-queue and default tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
tx-queue queue_level
Parameter
queue_level Transmit queue group number. Values range from 0 to 7.
Trident II platform switch queues handle unicast and multicast traffic.
Example
switch(config)# interface ethernet 17/3
switch(config-if-Et17/3)# tx-queue 4
switch(config-if-Et17/3-txq-4)#The uc-tx-queue command places the switch in the uc-tx-queue configuration mode to configure a unicast transmit queue on the configuration mode interface. The uc-tx-queue configuration mode is not a group change mode; running-config is changed immediately after commands are executed. The exit command does not affect the configuration.
The exit command returns the switch to the configuration mode for the base Ethernet or port channel interface.
The no uc-tx-queue and default uc-tx-queue commands remove the configuration for the specified transmit queue by deleting the all corresponding uc-tx-queue mode commands from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Command Syntax
uc-tx-queue queue_level
Parameter
queue_level The multicast transmit queue number. Values range from 0 to 7.
Related Command
mc-tx-queue: Configures multicast transmit queues on Trident and Tomahawk platform switches.
Exampleswitch(config)# interface ethernet 5
switch(config-if-Et5)# uc-tx-queue 4
switch(config-if-Et5-mc-txq-4)#| Model Number | Chipset Name |
|---|---|
| 710P | Trident3X1 |
| 720DF | Trident3X3 |
| 720DP | Trident3X1 |
| 720DP-48S | Trident3X2 |
| 720DT | Trident3X1 |
| 720DT-48S | Trident3X2 |
| 720XP | Trident3X3 |
| 722XPM | Trident3X2 |
| 7010T-48 | Helix4 |
| 7010T-48-DC | Helix4 |
| 7020SR-24C2 | QumranAX |
| 7020SR-32C2 | QumranAX |
| 7020SRG-24C2 | QumranAX |
| 7020TR-48 | QumranAX |
| 7020TRA-48 | QumranAX |
| 7048T-4S | Petra |
| 7048T-A | Petra |
| 7050CX3 | Trident3X7 |
| 7050DX4 | Trident4X11 |
| 7050Q-16 | Trident+ |
| 7050QX2-32S | Trident2+ |
| 7050QX-32 | Trident2 |
| 7050QX-32S | Trident2 |
| 7050S-52 | Trident+ |
| 7050S-64 | Trident+ |
| 7050SX-128 | Trident2 |
| 7050SX2-128 | Trident2+ |
| 7050SX2-72Q | Trident2+ |
| 7050SX3-48C8 | Trident3X5 |
| 7050SX3-48YC | Trident3X5 |
| 7050SX3-48YC12 | Trident3X7 |
| 7050SX3-48YC8 | Trident3X5 |
| 7050SX3-96YC8 | Trident3X7 |
| 7050SX-64 | Trident2 |
| 7050SX-72 | Trident2 |
| 7050SX-72Q | Trident2 |
| 7050SX-96 | Trident2 |
| 7050T-36 | Trident+ |
| 7050T-36 (HwRev4) | Trident+ |
| 7050T-52 | Trident+ |
| 7050T-52 (HwRev4) | Trident+ |
| 7050T-64 | Trident+ |
| 7050T-64 (HwRev4) | Trident+ |
| 7050TX-128 | Trident2 |
| 7050TX2-128 | Trident2+ |
| 7050TX3-48C8 | Trident3X5 |
| 7050TX-48 | Trident2 |
| 7050TX-64 | Trident2 |
| 7050TX-72 | Trident2 |
| 7050TX-72Q | Trident2 |
| 7050TX-96 | Trident2 |
| 7060CX2-32S | Tomahawk+ |
| 7060CX-32S | Tomahawk |
| 7060DX4-32 | Tomahawk3 |
| 7060PX4-32 | Tomahawk3 |
| 7060SX2-48YC6 | Tomahawk+ |
| 7120T-4S | Bali |
| 7124FX | Bali |
| 7124S | Bali |
| 7124SX | Bali |
| 7140T-8S | Bali |
| 7148S | Bali |
| 7148SX | Bali |
| 7150S-24 | Alta |
| 7150S-24-CL | Alta |
| 7150S-52-CL | Alta |
| 7150S-64-CL | Alta |
| 7150SC-24-CLD | Alta |
| 7150SC-64-CLD | Alta |
| 7160 | XP80 |
| 7170-32C | Tofino-32Q |
| 7170-32CD | Tofino-32D |
| 7170-64C | Tofino |
| 7250QX-64 | Trident2 |
| 7260CX3-64 | Tomahawk2 |
| 7260CX3-64E | Tomahawk2 |
| 7260CX-64 | Tomahawk |
| 7260QX-64 | Tomahawk |
| 7280CR-48 | Jericho |
| 7280CR2-60 | Jericho+ |
| 7280CR2A-60 | Jericho+ |
| 7280CR2AK-30 | Jericho+ |
| 7280CR2K-30 | Jericho+ |
| 7280CR2K-60 | Jericho+ |
| 7280CR2M-30 | Jericho+ |
| 7280CR3-32D4 | Jericho2 |
| 7280CR3-32P4 | Jericho2 |
| 7280CR3-36S | Jericho2C |
| 7280CR3-96 | Jericho2 |
| 7280CR3K-32D4 | Jericho2 |
| 7280CR3K-32D4A | Jericho2 |
| 7280CR3K-32P4 | Jericho2 |
| 7280CR3K-32P4A | Jericho2 |
| 7280CR3K-96 | Jericho2 |
| 7280CR3MK-32D4 | Jericho2 |
| 7280CR3MK-32P4 | Jericho2 |
| 7280CR-48 | Jericho |
| 7280DR3-24 | Jericho2 |
| 7280DR3K-24 | Jericho2 |
| 7280PR3-24 | Jericho2 |
| 7280PR3K-24 | Jericho2 |
| 7280QRA-C36S | Jericho |
| 7280QR-C36 | QumranMX |
| 7280QR-C72 | Jericho |
| 7280SE-64 | Arad+ |
| 7280SE-68 | Arad+ |
| 7280SE-72 | Arad+ |
| 7280SR2-48YC6 | Jericho+ |
| 7280SR2A-48YC6 | Jericho+ |
| 7280SR2K-48C6 | Jericho+ |
| 7280SR3-40YC6 | Jericho2C Q2A |
| 7280SR-48C6 | QumranMX |
| 7280SRA-48C6 | QumranMX |
| 7280SRAM-48C6 | QumranMX |
| 7280SRM-40CX2 | QumranMX |
| 7280TR3-40C6 | Jericho2C Q2A |
| 7280TR-48C6 | QumranMX |
| 7280TRA-48C6 | QumranMX |
| 7289 | Jericho2 |
| 7368X4 | Tomahawk 3 |
| DCS-7304 | Trident3 |
| DCS-7304 | Tomahawk |
| DCS-7304 | Trident2 |
| DCS-7308 | Trident3 |
| DCS-7308 | Tomahawk |
| DCS-7308 | Trident2 |
| DCS-7316 | Trident2 |
| DCS-7368X4 | Tomahawk3 |
| DCS-7504 | Petra |
| DCS-7504E | Arad/Arad+ |
| DCS-7504N | Jericho 2 |
| DCS-7504N | Jericho/Jericho+ |
| DCS-7508 | Petra |
| DCS-7508E | Arad/Arad+ |
| DCS-7508N | Jericho 2 |
| DCS-7508N | Jericho/Jericho+ |
| DCS-7512N | Jericho 2 |
| DCS-7512N | Jericho/Jericho+ |
| DCS-7516N | Jericho/Jericho+ |
| DCS-7804-CH | Jericho 2 |
| DCS-7808-CH | Jericho 2 |
Data packets that enter an entity to which a policy map is assigned are managed with traffic resolution commands of the first class that matches the packets.
The switch defines one control plane policy map named copp-system-policy. The copp-system-policy policy map always applies to the control plane and cannot be removed from the switch. Other control plane policy maps cannot be added. Copp-system-policy consists of preconfigured classes, each containing a static class map and traffic resolution commands. Preconfigured classes cannot be removed from copp-system-policy.
The switch provides static class maps and you cannot modify or delete them. The switch uses a naming convention of static class maps as copp-system- name, where name differentiates the class maps. Static class maps have pre-defined internal conditions, not based on ACLs, and only listed in running-config as components of copp-system-policy. The sequence of static class maps in the policy map is not significant. Traffic resolution commands define minimum (bandwidth) and maximum (shape) transmission rates for data streams matching the corresponding class map.
Create, edit, or delete dynamic class maps, and filter traffic with a single IPv4 ACL, and list in running-config.
QoS policy maps are user defined. The switch does not provide preconfigured QoS policy maps and in the default configuration, policy maps are not applied to any Ethernet or port channel interface. Policy maps and class maps are created and applied to interfaces through configuration commands.
A QoS policy map is composed of one or more classes. Each class contains an eponymous dynamic class map and traffic resolution commands. Dynamic class maps are user created, can be edited or deleted, filter traffic with a single IPv4 ACL, and are listed in running-config.
Data packets that enter an interface to which a policy map is assigned are managed with traffic resolution commands that correspond to the first class that matches the packet.
Segment Routing Traffic Engineering Policy (SR-TE) policy uses Segment Routing (SR) to enable a headend to steer traffic along any path without maintaining per flow state in every node based on the policy. Configuring SR policy for the MPLS dataplane (SR-MPLS) for Type-1 SR policy segments with BGP and locally configured policies as sources of SR policy is available on DCS-7500 and DCS-7280 family of switches.
Identity of a Candidate Path
State of an SID List (SL)
State of a Candidate Path
State of an SR Policy
EOS considers an SR policy as valid when at least one of its candidate paths is valid. Otherwise, the SR policy is invalid.
Resolution of an SL
An SL resolves if the top label (first SID) can be resolved in the system Labeled FIB (LFIB) to yield a nexthop and outgoing interface(s). The other labels in the SID-List do not play a part in resolution.
Best Candidate Path (Active Candidate Path) Selection Algorithm
switch# show traffic-engineering segment-routing policy endpoint <endpoint> color <color>Binding SID
BSID Conflict Handling
In both the cases, when the conflict no longer exists, the candidate paths re-evaluate and may become active.
SR Policies from a BGP peer (a controller, route reflector) received for installation at the headend by EOS. It does not propagate the received policies to BGP peers nor does it originate SR Policies for transmission to BGP peers.
Route-Target and NO_ADVERTISE Community in SR-TE SAFI Updates
EOS implements the Acceptance and Usability checks as defined in sections 4.2.1 and 4.2.2 of the IETF draft Advertising Segment Routing Policies in BGP. However EOS skips matching the Route-Target with the router-ID of the headend if the SR-TE NLRI is tagged with NO_ADVERTISE community.
ECMP does not support SR-TE SAFI Paths
EOS does not support ECMP for BGP SR-TE SAFI. The BGP path selects only one best candidate path and publishes it to SR-TE Policy Agent for candidate path selection.
Path Selection within BGP
The IETF draft Advertising Segment Routing Policies in BGP supports passing multiple candidate paths from a single protocol source for an SR-TE policy path selection. Therefore, it includes a field distinguisher in the NLRI which can be unique for each controller to make BGP pass through the policies. However when multiple sources use the same distinguisher, BGP performs a path selection for the tuple: Endpoint, Color and Distinguisher. The best path for that tuple publishes to the SR-TE Policy Agent for selecting an Active path. The best bgp-best-path selection applies to SR-TE SAFI as well.
Error Handling / Edge Cases
BGP-4-SRTE_IGNORED_SEGMENT_LIST_UNSUPPORTED_SEGMENTS
syslog. Such SID-Lists are not stored locally, and
show bgp sr-te command
does not display them. Steering Traffic into a Policy
Incoming label as BSID - Labelled Steering
At the headend when receiving a packet with a label stack with a BSID of an active CP of a valid SR Policy as the top label, the headend pops the label, and imposes the resolved label stack on the outgoing packet.
Example
For instance, an SR Policy with an active candidate path with BSID 965536 and SL with label stack [965540, 900001, 900002]. Assume that 965540 is an IS-IS SR Adjacency SID. An incoming packet has a label stack [965536, 100000] then the outgoing label stack consists of [900001, 900002, 100000].
Steering BGP learnt IP(v6) prefixes - IP Steering
Incoming label is BSID - Labelled Steering
At the headend, BGP IPv4 and IPv6 routes receive one or more extended color communities and recursively resolves them through any active SR Policy that matches the BGP routes’ nexthop and color. When receiving an IPv4 or IPv6 packet forwarded using this policy, the SL’s resolved label stack imposes on the outgoing packet.
For BGP routes received with color community to be steered via an SR policy, the route’s nexthop must already be resolvable through IGP. If no resolving route exists in IGP, the route is considered unresolvable and does not program in hardware even if a matching SR policy exists for the corresponding nexthop and color.
If no matching SR policy exists for the received BGP nexthop and color, the route resolves through the IGP route in IP RIB. If an active SR policy that matches the BGP nexthop and color gets instantiated at a later time, the BGP route changes from resolving through IGP to the new active SR policy.
Color only IP steering using CO bits
It is possible to relax the requirement of an exact match of the BGP route’s nexthop with the endpoint of the SR Policy using the “CO” (Color Only) bits in the color extended community. The “CO” bits are 2 reserved bits repurposed for color only steering as defined in section 3 of Advertising Segment Routing Policies in BGP. The exact match of the nexthop is done with the CO bits set to 00 or 11.
ECMP of IPv4/IPv6 Prefixes that Resolve over SR-TE Policies
When multiple BGP paths of BGP unicast prefixes resolve through active SR policies form ECMP, the resulting FIB entry for the BGP route has an ECMP of segment list paths which is a union of all the segments-list entries present in each of the resolving SR policies for the BGP paths.
Example
| Path | Nexthop | Color | Policy EP | Policy Color | Segment Lists | Per SL Traffic Distribution |
|---|---|---|---|---|---|---|
| 1 | 1.0.0.2 | CO(00):1000 | 1.0.0.2 | 1000 | [2500 500], Weight:
1 [2501 500], Weight: 2 |
8.33% 16.66% |
| 2 | 1.0.2.2 | CO(00):2000 | 1.0.2.2 | 2000 | [2502 500], Weight:
1 [2503 500], Weight: 1 |
12.5% 12.5% |
| 3 | 1.0.4.2 | CO(00):3000 | 1.0.4.2 | 3000 | [2504 500], Weight:
1 [2505 500], Weight: 1 |
12.5% 12.5% |
| 4 | 1.0.6.2 | CO(00):4000 | 1.0.6.2 | 4000 | [2506 500], Weight:
1 [2507 500], Weight: 1 |
12.5% 12.5% |
B I 192.1.0.0/31 [200/0] via SR-TE Policy 1.0.4.2, color 3000
via SR-TE tunnel index 6, weight 1
via 1.0.4.2, Ethernet1, label 2505 500
via SR-TE tunnel index 5, weight 1
via 1.0.4.2, Ethernet1, label 2504 500
via SR-TE Policy 1.0.0.2, color 1000
via SR-TE tunnel index 2, weight 1
via 1.0.0.2, Ethernet2, label 2501 500
via SR-TE tunnel index 1, weight 1
via 1.0.0.2, Ethernet2, label 2500 500
via SR-TE Policy 1.0.2.2, color 2000
via SR-TE tunnel index 4, weight 1
via 1.0.2.2, Ethernet3, label 2503 500
via SR-TE tunnel index 3, weight 1
via 1.0.2.2, Ethernet3, label 2502 500
via SR-TE Policy 1.0.6.2, color 4000
via SR-TE tunnel index 8, weight 1
via 1.0.6.2, Ethernet6, label 2507 500
via SR-TE tunnel index 7, weight 1
via 1.0.6.2, Ethernet6, label 2506 500The traffic distribution honors the weights of the SID-Lists. In the example, each of the four SR Policies will get 25% of the total traffic meant for prefix 192.1.0.0/31. Within each policy, the distribution is based on the weights of the SID-Lists.
ECMP Group when some BGP unicast paths resolve over SR Policies and some via non SR Policy IGP paths
B I 192.1.0.0/31 [200/0] via SR-TE Policy 1.0.4.2, color 3000
via SR-TE tunnel index 6, weight 1
via 1.0.4.2, Ethernet1, label 2505 500
via SR-TE tunnel index 5, weight 1
via 1.0.4.2, Ethernet1, label 2504 500
via SR-TE Policy 1.0.0.2, color 1000
via SR-TE tunnel index 2, weight 1
via 1.0.0.2, Ethernet2, label 2501 500
via SR-TE tunnel index 1, weight 1
via 1.0.0.2, Ethernet2, label 2500 500
via SR-TE Policy 1.0.2.2, color 2000
via SR-TE tunnel index 4, weight 1
via 1.0.2.2, Ethernet3, label 2503 500
via SR-TE tunnel index 3, weight 1
via 1.0.2.2, Ethernet3, label 2502 500UCMP of IPv4/IPv6 prefixes using LinkBandwidth (LBW) Extended Community that resolve over SR-TE policies not supported
When multiple BGP paths of BGP unicast prefixes resolve through active SR policies form ECMP, and the unicast paths also contain the LBW extended community, EOS does not form UCMP amongst the unicast paths. Only ECMP is formed at the unicast prefix level. The LBW is ignored the behavior is identical to the behavior explained in the previous section.
Resolution of BGP unicast prefixes that resolve over other BGP unicast prefixes resolved via SR Policies
A BGP unicast prefix P1, that is recursively resolved via another BGP prefix P2, such that P2 resolves via an SR Policy, then in the FIB, P1 is programmed with the resolved nexthop pointing to the non SR Policy resolution of P2. P1 does not use P2s SR Policy for forwarding.
Explicit Null Label Imposition
When the address family of the BGP unicast prefix is not the same as the address family of the endpoint of the SR Policy that the unicast prefixes resolves via, an explicit null label is automatically imposed in the outgoing label stack.
Example
If an IPv4 unicast prefix P1 resolves over a policy whose endpoint EP1 is an IPv6 address (this can happen due to color only CO=01/10 steering with P1 having an IPv4 nexthop) and the SR Policy had a SID-List whose resolved label stack is [1001, 1002, 1003], the outgoing packet is imposed with [1001, 1002, 1003, 2] where 0 is the IPv4 explicit null label.
If an IPv6 prefix P2, resolves over a policy whose endpoint EP2 is an IPv4 address (this can happen with color only CO=01/10 steering with P2 having a IPv6 nexthop) and the SR Policy had a SID-List whose resolved label stack is [1001, 1002, 1003], the outgoing packet is imposed with [1001, 1002, 1003, 2] where 2 is the IPv6 explicit null label.
| ENLP configuration for the resolving SR Policy | IPv4 Prefixes | IPv6 Prefixes |
|---|---|---|
| None | - | - |
| IPv4 | IPv4 explicit null appended to the end of label stack | - |
| IPv6 | - | IPv6 explicit null appended to the end of label stack |
| Both | IPv4 explicit null appended to the end of label stack | IPv6 explicit null appended to the end of label stack |
| No/Default config (incase of BGP learnt policies ENLP Sub-TLV is not received) | Resolving SR Policy has IPv4 Endpoint
address: No explicit-null |
Resolving SR Policy has IPv4 Endpoint
address: IPv6 explicit null appended to the end of label stack |
| Resolving SR Policy has IPv6 Endpoint
address: IPv4 explicit null appended to the end of label stack |
Resolving SR Policy has IPv6 Endpoint
address: No explicit-null |
switch(config)# router traffic-engineering
switch(config-te)# segment-routingswitch(config-te-sr)# policy endpoint v4Address|v6Address color color-value
switch(config-te-sr-policy)# binding-sid mpls-label
switch(config-te-sr-policy)# path-group preference valueswitch(config-te-sr-policy)# path-group preference value
switch(config-te-sr-policy-path)# segment-list label-stack label1 label2 … weight valueswitch(config-te-sr-policy-path)# explicit-null [none|ipv4|ipv6|both]BGP configuration for SR-TE SAFI
switch(config)# router bgp <as>
switch(config-router-bgp)# address-family ipv4|ipv6 sr-te
switch(config-router-bgp-af-srte)# neighbor neighbor activateswitch(config-router-bgp-af-srte)# neighbor neighbor route-map routeMapName inswitch(config)# hardware counter feature mpls tunnelswitch# show hardware counter feature
Feature Direction Counter Resource (Engine)
------------------ ---------------- --------------------------
ACL-IPv4 out Jericho: 2, 3
ACL in Jericho: 4, 5, 6, 7
MPLS tunnel out Jericho: 8, 9switch(config)# no hardware counter feature mpls tunnelswitch# show bgp sr-te summary
BGP summary information for VRF default
Router identifier 100.1.1.2, local AS number 100
Neighbor Status Codes: m - Under maintenance
Neighbor V AS MsgRcvd MsgSent InQ OutQ Up/Down State PfxRcd PfxAcc
100.1.1.1 4 100 407 413 0 0 00:18:57 Estab 1 1
1000::1 4 100 407 413 0 0 00:18:57 Estab 1 1switch# show bgp sr-te ipv4 summary
BGP summary information for VRF default
Router identifier 100.1.1.2, local AS number 100
Neighbor Status Codes: m - Under maintenance
Neighbor V AS MsgRcvd MsgSent InQ OutQ Up/Down State PfxRcd PfxAcc
100.1.1.1 4 100 407 413 0 0 00:18:57 Estab 0 0switch# show bgp sr-te ipv6 summary
BGP summary information for VRF default
Router identifier 100.1.1.2, local AS number 100
Neighbor Status Codes: m - Under maintenance
Neighbor V AS MsgRcvd MsgSent InQ OutQ Up/Down State PfxRcd PfxAcc
1000::1 4 100 407 413 0 0 00:18:57 Estab 0 0switch# show bgp sr-te
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
Policy status codes: * - valid, > - active, E - ECMP head, e - ECMP
c - Contributing to ECMP
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop - Link Local Nexthop
Endpoint Color Distinguisher Next Hop Metric LocPref Weight Path
*> 133.1.1.1 0 1 130.1.1.3 0 100 0 ?
*> 133.1.1.1 0 2 130.1.1.3 0 100 0 ?
*> 1330::1 0 1 1300::3 0 100 0 ?
*> 1330::1 0 2 1300::3 0 100 0 ?switch# show bgp sr-te ipv4
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
Policy status codes: * - valid, > - active, E - ECMP head, e - ECMP
c - Contributing to ECMP
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop - Link Local Nexthop
Endpoint Color Distinguisher Next Hop Metric LocPref Weight Path
*> 133.1.1.1 0 1 130.1.1.3 0 100 0 ?
*> 133.1.1.1 0 2 130.1.1.3 0 100 0 ?switch# show bgp sr-te ipv6
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
Policy status codes: * - valid, > - active, E - ECMP head, e - ECMP
c - Contributing to ECMP
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop - Link Local Nexthop
Endpoint Color Distinguisher Next Hop Metric LocPref Weight Path
*> 1330::1 0 1 1300::3 0 100 0 ?
*> 1330::1 0 2 1300::3 0 100 0 ?switch# show bgp sr-te endpoint 133.1.1.1 color 0 distinguisher 1
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
BGP routing table entry for Endpoint: 133.1.1.1 Color: 0 Distinguisher: 1
Paths: 1 available
Local
130.1.1.3 from 100.1.1.2 (100.1.1.2)
Origin INCOMPLETE, metric 0, localpref 100, IGP metric 0, weight 0,
received 00:01:29 ago, valid, internal, best
Community: no-advertise
Rx SAFI: SR TE Policyswitch# show bgp sr-te endpoint 133.1.1.1 color 0 distinguisher 1 detail
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
BGP routing table entry for Endpoint: 133.1.1.1 Color: 0 Distinguisher: 1
Paths: 1 available
Local
130.1.1.3 from 100.1.1.2 (100.1.1.2)
Origin INCOMPLETE, metric 0, localpref 100, IGP metric 0, weight 0,
received 00:01:29 ago, valid, internal, best
Community: no-advertise
Rx SAFI: SR TE Policy
Tunnel encapsulation attribute: SR Policy
Preference: 200
Binding SID: 965536
Explicit null label policy: IPv4
Segment-List: Label Stack: [ 16004 16003 ], Weight: 10
Segment-List: Label Stack: [ 2000 3000 ]switch# show bgp neighbors 100.1.1.2 ipv4 sr-te policies
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
Policy status codes: * - valid, > - active
Origin codes: i - IGP, e - EGP, ? - incomplete
AS Path Attributes: Or-ID - Originator ID, C-LST - Cluster List, LL Nexthop - Link Local Nexthop
Endpoint Color Distinguisher Next Hop Metric LocPref Weight Path
*> 133.1.1.1 0 1 133.1.1.3 0 100 0 ?
*> 133.1.1.1 0 2 133.1.1.3 0 100 0 ?switch# show bgp neighbors 100.1.1.2 ipv4 sr-te policies detail
BGP routing table information for VRF default
Router identifier 100.1.1.1, local AS number 100
BGP routing table entry for Endpoint: 133.1.1.1 Color: 0 Distinguisher: 2
Paths: 1 available
Local
130.1.1.3 from 100.1.1.2 (100.1.1.2)
Origin INCOMPLETE, metric 0, localpref 100, IGP metric 0, weight 0,
received 00:01:29 ago, invalid, internal
Rx SAFI: SR TE Policy
Tunnel encapsulation attribute: SR Policy
Preference: 200
Binding SID: 965536
Explicit null label policy: IPv4
Segment-List: Label Stack: [ 16004 16003 ], Weight: 10
Segment-List: Label Stack: [ 2000 3000 ]Policy-Based Routing (PBR) allows the operator to specify the next hop for selected incoming packets on an L3 interface, overriding the routing table. Incoming packets are filtered through a policy map referencing one or more ACLs, and matching packets are routed to the next hop specified.
A PBR policy map is composed of one or more classes and can include next-hop information for each class. It can also include single-line raw match statements, which have the appearance and function of a single line from an ACL. Each class contains an eponymous class map. Class maps are user-created, can be edited or deleted, filter traffic using IPv4 ACLs, and are listed in running-config.
Traffic policies are implemented by policy maps, which are applied to the control plane, or to L3 interfaces for Policy-Based Routing (PBR). Policy maps contain classes, which are composed of class maps and traffic resolution commands.
Traffic Management Conceptual Overview describes traffic policies.
EOS implements default control plane traffic policies automatically without user intervention, and modified by associating traffic resolution commands with static classes that comprise the control plane policy map.
Control plane traffic policies utilize static class maps, provided by the switch, not editable, and cannot be deleted.
You cannot delete the control plane policy map, copp-system-policy. In its default form, copp-system-policy consists of the classes listed in class (policy-map (control-plane) Arad). Although you cannot edit the underlying class map of each class , you can adjust the traffic resolution commands. The default classes cannot be removed from the policy map and their sequence within the policy map is not editable.
Policy maps are modified in the Policy-Map Configuration mode. The policy-map type copp command enters the Policy-Map Configuration mode mode.
Examples
copp-system-policy.switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#The class (policy-map (control-plane) Arad) command enters the Policy-Map Configuration mode, where you modify traffic resolution commands for the configuration mode class.
Example
copp-system-lacp static
class.switch(config-pmap-copp-system-policy)# class copp-system-lacp
switch(config-pmap-c-copp-system-policy-copp-system-lacp)#Example
copp-system-lacp class
map:switch(config-pmap-c-copp-system-policy-copp-system-lacp)# bandwidth kbps 2000
switch(config-pmap-c-copp-system-policy-copp-system-lacp)# shape kbps 4000
switch(config-pmap-c-copp-system-policy-copp-system-lacp)#Policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the saved version of policy map. The show pending command displays the modified policy map.
Example
switch(config-pmap-c-copp-system-policy-copp-system-lacp)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class copp-system-bpdu
class copp-system-lldp
class copp-system-lacp
shape kbps 4000
bandwidth kbps 2000
class copp-system-l3ttl1
class copp-system-l3slowpath
switch(config-pmap-copp-system-policy)# exit
switch(config)#EOS always applies the copp-system-policy policy map to the control plane. No commands can add or remove this assignment.
The show policy-map interface type qos command displays the configured values of the policy maps classes and the number of packets filtered and dropped as a result of the class maps.
Example
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Hardware programming status: InProgress
Class-map: copp-system-mlag (match-any)
shape : 10000001 kbps
bandwidth : 10000001 kbps
Out Packets : 0
Drop Packets : 0
Class-map: copp-system-bpdu (match-any)
shape : 2604 kbps
bandwidth : 1302 kbps
Out Packets : 0
Drop Packets : 0
Class-map: copp-system-lacp (match-any)
shape : 4230 kbps
bandwidth : 2115 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#
switch(config-pmap-c-copp-system-policy-copp-system-lacp)# exitEOS implements QoS traffic policies to create class maps and policy maps, then apply the policy maps to Ethernet and port channel interfaces.
QoS traffic policies utilize dynamic class maps created and modified in the Class-Map Configuration mode. The class-map type qos command enters class-map configuration mode.
Example
switch(config)# class-map type qos match-any Q-CMap_1
switch(config-cmap-Q-CMap_1)#A class map contains one IPv4 access control list (ACL). The match ip access-group command assigns an ACL to the class map. Subsequent match commands replace the existing match command. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded.
Example
switch(config-cmap-Q-CMap_1)# match ip access-group ACL_1
switch(config-cmap-Q-CMap_1)#The Class-Map Configuration mode is a group-change mode. Save the changes made in a group-change mode by exiting the mode. The show active command displays the saved version of class map. The show pending command displays the unsaved class map.
Example
switch(config-cmap-Q-CMap_1)# show active
switch(config-cmap-Q-CMap_1)# show pending
class-map type qos match-any Q-CMap_1
match ip access-group ACL_1
switch(config-cmap-Q-CMap_1)#The exit command returns the switch to Global Configuration mode and saves pending class map changes. The abort command returns the switch to global configuration mode and discards pending changes.
Example
switch(config-cmap-CP-CMAP_1)# exit
switch(config)# show class-map type control-plane CP-CMAP_1
Class-map: CP-CMAP_1 (match-any)
Match: ip access-group name ACLv4_1
switch(config)#Policy maps are created and modified in policy-map configuration mode. The policy-map type quality-of-service command enters policy-map configuration mode.
Example
switch(config)# policy-map type quality-of-service Q-PMAP_1
switch(config-pmap-Q-PMAP_1)#Policy map are edited by adding or removing classes. A class automatically contains its eponymous class map; traffic resolution commands are added or edited in policy-map-class configuration mode. The below command adds a class to the configuration mode policy map and places the switch in policy-map-class configuration mode, where traffic resolution commands are added to the class.
Example
switch(config-pmap-Q-PMAP_1)# class Q-CMap_1
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set cos 7
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set traffic-class 4
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#Policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active and show pending commands display the saved and modified policy map versions, respectively.
Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# exit
switch(config-pmap-Q-PMAP_1)# show pending
policy-map type quality-of-service Q-PMAP_1
class Q-CMap_1
set cos 7
set traffic-class 4
class class-default
switch(config-pmap-Q-PMAP_1)# exit
switch(config)#The last class in all QoS policy maps is class-default. The class-default class map matches all traffic except IPv4 or IPv6 traffic and provides no traffic resolution commands. The class-default class map is not editable; traffic resolution commands can be added to the class-default class.
To modify traffic resolution commands for the class-default class, enter policy-map-class configuration mode for the class, then enter the desired set commands.
Example
switch(config)# policy-map type quality-of-service Q-PMap_1
switch(config-pmap-Q-PMap_1)# class class-default
switch(config-pmap-c-Q-PMap_1-class-default)# set traffic-class 2
switch(config-pmap-c-Q-PMap_1-class-default)# exit
switch(config-pmap-Q-PMap_1)# exit
switch(config)# show policy-map type qos Q-PMap_1
Service-policy Q-PMap_1
Class-map: Q-CMap_1 (match-any)
Match: ipv6 access-group name ACLv6_1
set cos 7
set traffic-class 4
Class-map: class-default (match-any)
set traffic-class 2
switch(config)#The service-policy type qos (Interface mode) command applies a specified policy map to the configuration mode interface.
switch(config)# interface ethernet 8
switch(config-if-Et8)# show active
switch(config-if-Et8)# service-policy input PMAP-1
switch(config-if-Et8)# show active
interface Ethernet8
service-policy type qos input PMAP-1
switch(config-if-Et8)#Policy-Based Routing (PBR) is implemented by creating class maps and policy maps, then applying the policy maps to Ethernet interfaces, port channel interfaces or switch virtual interfaces (SVIs).
PBR policies utilize class maps that are created and modified in the class-map configuration mode. The class-map type pbr command enters the class-map configuration mode.
Example
switch(config)# class-map type pbr match-any CMAP1
switch(config-cmap-PBR-CMAP1)#A class map contains one or more access control lists (ACLs). The match (policy-map (pbr)) command assigns an ACL to the class map. Subsequent match commands add additional ACLs to the class map. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded; if a class map includes ACLs with deny rules, the configuration reverts to its previous state.
Example
switch(config-cmap-PBR-CMAP1)# match ip access-group ACL1
switch(config-cmap-PBR-CMAP1)#The class-map configuration mode is a group-change mode. Changes made in a group-change mode are saved by exiting the mode. The show active command displays the saved version of class map.
switch(config-cmap-PBR-CMAP1)# show active
switch(config-cmap-PBR-CMAP1)#The exit command returns the switch to the global configuration mode and saves pending class map changes. The abort command returns the switch to the global configuration mode and discards pending changes.
Example
switch(config-cmap-PBR-CMAP1)# exit
switch(config)# show class-map type pbr CMAP1
class-map type pbr match-any CMAP1
10 match ip access-group ACL1
switch(config)#Policy maps are created and modified in policy-map configuration mode. The policy-map type pbr command enters the policy-map configuration mode.
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)#Policy map are edited by adding or removing classes. A class automatically contains its eponymous class map; next-hop commands are added or edited in the policy-map-class configuration mode. The class (policy-map (pbr)) command adds a class to the configuration mode policy map and places the switch in the policy-map-class configuration mode, where next-hop commands are added to the class.
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)#The set nexthop (policy-map-class pbr) command configures the next hop for data that passes the class map.
switch(config-pmap-c-PMAP1-CMAP1)# set nexthop 10.12.0.5
switch(config-pmap-c-PMAP1-CMAP1)#The set nexthop-group (policy-map-class(pbr) Arad) command configures a nexthop group as the next hop for data that passes the class map.
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)# set nexthop-group GROUP1
switch(config-pmap-c-PMAP1-CMAP1)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the currently saved map version.
switch(config-pmap-c-PMAP1-CMAP1)# exit
switch(config-pmap-PMAP1)# exit
switch(config)#The service-policy type pbr (Interface mode) command applies the specified PBR policy map to the configuration mode interface. Only one PBR service policy is supported per interface.
switch(config)# interface ethernet 8
switch(config-if-Et8)# service-policy type pbr input PMAP1
switch(config-if-Et8)#When hardware decapsulation takes place, PBR policy maps on Arad platform switches match on outer packet headers (i.e., they match based on the attributes of the packet before it is decapsulated).
Traffic policies are implemented by policy maps, which are applied to the control plane or an interface. Policy maps contain classes, which are composed of class maps and traffic resolution commands. Traffic Management Conceptual Overview describes traffic policies.
Default control plane traffic policies are implemented automatically without user intervention. These policies are modified by associating traffic resolution commands with static classes that comprise the control plane policy map.
Control plane traffic policies utilize static class maps, which are provided by the switch, are not editable, and cannot be deleted.
| Class Name | shape (pps) | bandwidth (pps) |
|---|---|---|
| copp-system-arp | 10000 | 1000 |
| copp-system-default | 8000 | 1000 |
| copp-system-ipmcrsvd | 10000 | 1000 |
| copp-system-ipmcmiss | 10000 | 1000 |
| copp-system-igmp | 10000 | 1000 |
| copp-system-l2rsvd | 10000 | 10000 |
| copp-system-l3slowpath | 10000 | 1000 |
| copp-system-pim-ptp | 10000 | 1000 |
| copp-system-ospf-isis | 10000 | 1000 |
| copp-system-selfip | 5000 | 5000 |
| copp-system-selfip-tc6to7 | 5000 | 5000 |
| copp-system-sflow | 25000 | 1000 |
Policy maps are modified in the policy-map configuration mode. The policy-map type copp command enters the policy-map configuration mode.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#The class (policy-map (control-plane) FM6000) command enters the policy-map-class configuration mode, where traffic resolution commands are modified for the configuration mode class.
Example
switch(config-pmap-copp-system-policy)# class copp-system-arp
switch(config-pmap-c-copp-system-policy-copp-system-arp)#Example
switch(config-pmap-c-copp-system-policy-copp-system-arp)# bandwidth pps 2000
switch(config-pmap-c-copp-system-policy-copp-system-arp)# shape pps 4000
switch(config-pmap-c-copp-system-policy-copp-system-arp)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the saved version of policy map. The show pending command displays the modified policy map.
Example
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class CP-CMAP_1
shape pps 4000
bandwidth pps 2000
class copp-system-bpdu
class copp-system-lldp
class copp-system-lacp
class copp-system-arp
class copp-system-arpresolver
class copp-system-default
switch(config-pmap-copp-system-policy)#exit
switch(config)#The copp-system-policy policy map is always applied to the control plane. No commands are available to add or remove this assignment.
QoS traffic policies are implemented by creating class maps and policy maps, then applying the policy maps to Ethernet and port channel interfaces.
QoS traffic policies utilize dynamic class maps that are created and modified in the class-map configuration mode. The class-map type qos command enters the class-map configuration mode.
Example
switch(config)# class-map type qos match-any Q-CMap_1
switch(config-cmap-Q-CMap_1)#A class map contains one IPv4 access control list (ACL). The match (class-map (qos) FM6000) command assigns an ACL to the class map. Subsequent match commands replace the existing match command. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded.
Example
switch(config-cmap-Q-CMap_1)# match ip access-group ACL_1
switch(config-cmap-Q-CMap_1)#The class-map configuration mode is a group-change mode. Changes made in a group-change mode are saved by exiting the mode. The show active command displays the saved version of class map. The show pending command displays the unsaved class map.
Example
switch(config-cmap-Q-CMap_1)# show active
switch(config-cmap-Q-CMap_1)# show pending
class-map type qos match-any Q-CMap_1
match ip access-group ACL_1
switch(config-cmap-Q-CMap_1)#The exit command returns the switch to the global configuration mode and saves pending class map changes. The abort command returns the switch to the global configuration mode and discards pending changes.
Example
switch(config-cmap-CP-CMAP_1)# exit
switch(config)# show class-map type control-plane CP-CMAP_1
Class-map: CP-CMAP_1 (match-any)
Match: ip access-group name ACLv4_1
switch(config)#Policy maps are created and modified in the policy-map configuration mode. The policy-map type quality-of-service command enters the policy-map configuration mode.
Example
switch(config)# policy-map type quality-of-service Q-PMAP_1
switch(config-pmap-Q-PMAP_1)#Policy map are edited by adding or removing classes. A class automatically contains its eponymous class map; traffic resolution commands are added or edited in the policy-map-class configuration mode. The class (policy-map (qos) FM6000) command adds a class to the configuration mode policy map and places the switch in the policy-map-class configuration mode, where traffic resolution commands are added to the class.
Example
switch(config-pmap-Q-PMAP_1)# class Q-CMap_1
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set cos 7
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set traffic-class 4
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active and show pending commands display the saved and modified policy map versions, respectively.
Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# exit
switch(config-pmap-Q-PMAP_1)# show pending
policy-map type quality-of-service Q-PMAP_1
class Q-CMap_1
set cos 7
set traffic-class 4
class class-default
switch(config-pmap-Q-PMAP_1)# exit
switch(config)#The last class in all QoS policy maps is class-default. The class-default class map matches all traffic except IPv4 or IPv6 traffic and provides no traffic resolution commands. The class-default class map is not editable; traffic resolution commands can be added to the class-default class.
To modify traffic resolution commands for the class-default class, enter the policy-map-class configuration mode for the class, then enter the desired set commands.
Example
switch(config)# policy-map type quality-of-service Q-PMap_1
switch(config-pmap-Q-PMap_1) #class class-default
switch(config-pmap-c-Q-PMap_1-class-default)# set traffic-class 2
switch(config-pmap-c-Q-PMap_1-class-default)# exit
switch(config-pmap-Q-PMap_1)# exit
switch(config)# show policy-map type qos Q-PMap_1
Service-policy Q-PMap_1
Class-map: Q-CMap_1 (match-any)
Match: ipv6 access-group name ACLv6_1
set cos 7
set traffic-class 4
Class-map: class-default (match-any)
set traffic-class 2
switch(config)#The service-policy type qos (Interface mode) command applies a specified policy map to the configuration mode interface.
These commands apply PMAP-1 policy map to interface ethernet 8.switch(config)# interface ethernet 8
switch(config-if-Et8)# show active
switch(config-if-Et8)# service-policy input PMAP-1
switch(config-if-Et8)# show active
interface Ethernet8
service-policy type qos input PMAP-1
switch(config-if-Et8)#Policy-Based Routing (PBR) is implemented by creating class maps and policy maps, then applying the policy maps to Ethernet interfaces, port channel interfaces or Switch Virtual Interfaces (SVIs).
PBR policies utilize class maps that are created and modified in the class-map configuration mode. The class-map type pbr command enters the class-map configuration mode.
Example
switch(config)# class-map type pbr match-any CMAP1
switch(config-cmap-PBR-CMAP1)#A class map contains one or more IPv4 access control lists (ACLs). The match (policy-map (pbr)) command assigns an ACL to the class map. Subsequent match commands add additional ACLs to the class map. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded; if a class map includes ACLs with deny rules, the configuration reverts to its previous state.
On FM6000 platform switches, counters are not supported, so a counters per-entry (ACL configuration modes) command in an ACL is ignored.
Example
switch(config-cmap-PBR-CMAP1)# match ip access-group ACL1
switch(config-cmap-PBR-CMAP1)#The class-map configuration mode is a group-change mode. Changes made in a group-change mode are saved by exiting the mode. The show active command displays the saved version of class map.
switch(config-cmap-PBR-CMAP1)# show active
switch(config-cmap-PBR-CMAP1)#The exit command returns the switch to global configuration mode and saves pending class map changes. The abort command returns the switch to global configuration mode and discards pending changes.
Example
switch(config-cmap-PBR-CMAP1)# exit
switch(config)# show class-map type pbr CMAP1
class-map type pbr match-any CMAP1
10 match ip access-group ACL1
switch(config)#Policy maps are created and modified in the policy-map configuration mode. The policy-map type pbr command enters the policy-map configuration mode.
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)#Policy map are edited by adding or removing classes. A class automatically contains its eponymous class map; next-hop commands are added or edited in the policy-map-class configuration mode. The class (policy-map (pbr)) command adds a class to the configuration mode policy map and places the switch in the policy-map-class configuration mode, where next-hop commands are added to the class.
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)#The set nexthop (policy-map-class pbr) command configures the next hop for data that passes the class map.
switch(config-pmap-c-PMAP1-CMAP1)# set nexthop 10.12.0.5
switch(config-pmap-c-PMAP1-CMAP1)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the currently saved map version.
Example
switch(config-pmap-c-PMAP1-CMAP1)# exit
switch(config-pmap-PMAP1)# exit
switch(config)#The service-policy type pbr (Interface mode) command applies the specified PBR policy map to the configuration mode interface. Only one PBR service policy is supported per interface.
switch(config)# interface ethernet 8
switch(config-if-Et8)# service-policy type pbr input PMAP1
switch(config-if-Et8)#When hardware decapsulation takes place, PBR policy maps on FM6000 platform switches match on outer packet headers (i.e., they match based on the attributes of the packet before it is decapsulated).
Traffic policies are implemented by policy maps, which are applied to the control plane. Policy maps contain classes, which are composed of class maps and traffic resolution commands. QoS traffic policies are not supported on 7500 Series switches.
Traffic Management Conceptual Overview describes traffic policies.
Default control plane traffic policies are implemented automatically without user intervention. These policies are modified by associating traffic resolution commands with static classes that comprise the control plane policy map.
Control plane traffic policies utilize static class maps, which are provided by the switch, are not editable, and cannot be deleted.
| Class Name | shape (kbps) | bandwidth (kbps) |
|---|---|---|
| copp-system-bpdu | 2500 | 1250 |
| copp-system-default | 2500 | 250 |
| copp-system-igmp | 2500 | 250 |
| copp-system-ipbroadcast | 2500 | 250 |
| copp-system-ipmc | 2500 | 250 |
| copp-system-ipmcmiss | 2500 | 250 |
| copp-system-ipmcrsvd | 2500 | 250 |
| copp-system-ipunicast | NO LIMIT | 250 |
| copp-system-l3destmiss | 2500 | 250 |
| copp-system-l3slowpath | 2500 | 250 |
| copp-system-l3ttl0 | 2500 | 250 |
| copp-system-l3ttl1 | 2500 | 250 |
| copp-system-lacp | 2500 | 1250 |
| copp-system-lldp | 2500 | 250 |
| copp-system-unicast-arp | 2500 | 250 |
Policy maps are modified in the policy-map configuration mode. The policy-map type copp command enters the policy-map configuration mode.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#The class (policy-map (control-plane) Petra) command enters the policy-map-class configuration mode, where traffic resolution commands are modified for the configuration mode class.
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#switch(config-pmap-c-copp-system-policy-copp-system-lldp)# bandwidth kbps 2000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# shape kbps 4000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the saved version of policy map. The show pending command displays the configured policy map.
Petra platform switches do not support all discrete rate values. When a bandwidth or shape command specifies a value that is not supported, the switch converts the rate to the next highest discrete value that it supports. The show policy-map interface type qos command displays the converted rate and not the user configured rate.
Example
switch(config-pmap-c-copp-system-policy-copp-system-lacp)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class copp-system-bpdu
class copp-system-lldp
shape kbps 4000
bandwidth kbps 2000
class copp-system-lacp
switch(config-pmap-copp-system-policy)# exit
switch(config)#Changes are saved with the exit command or discarded with the abort command. The show active command displays the saved version of policy map. The show pending command displays the modified policy map.
The show policy-map interface type qos command displays the traffic resolution rates of the policy maps classes and the number of packets filtered and dropped as a result of the class maps. The shape and bandwidth rates may differ from configured values, because the switch does not support all discrete rate values.
Example
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Hardware programming status: InProgress
Class-map: copp-system-mlag (match-any)
shape : 10000001 kbps
bandwidth : 10000001 kbps
Out Packets : 0
Drop Packets : 0
Class-map: copp-system-lacp (match-any)
shape : 2604 kbps
bandwidth : 1302 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#The copp-system-policy policy map is always applied to the control plane. No commands are available to add or remove this assignment.
QoS traffic policies are not supported on Petra platform switches.
PBR policies are not supported on Petra platform switches.
EOS implements traffic policies using policy maps applied to the control plane or an interface. Policy maps contain classes, composed of class maps and traffic resolution commands. Traffic Management Conceptual Overview describes traffic policies.
Default control plane traffic policies are implemented automatically without user intervention. These policies are modified by creating class maps and editing the policy map to include the new class maps.
Control plane traffic policies utilize static and dynamic class maps. Static class maps are provided by the switch, are not editable, and cannot be deleted. Dynamic class maps are created and modified in the class-map configuration mode. The class-map type copp command enters the class-map configuration mode.
Example
switch(config)# class-map type copp match-any CP-CMAP_1
switch(config-cmap-CP-CMAP_1)#Class maps contain one IPv4 or IPv6 access control list (ACL). The match (class-map (control-plane) Trident) command assigns an ACL to the class map. Subsequent match commands replace the existing match command. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded.
Example
switch(config-cmap-CP-CMAP_1)# match ip access-group ACLv4_1
switch(config-cmap-CP-CMAP_1)#The class-map configuration mode is a group-change mode. Changes are saved by exiting the mode. The show active command displays the saved version of class map. The show pending command displays the unsaved class map.
Example
switch(config-cmap-CP-CMAP_1)# show active
switch(config-cmap-CP-CMAP_1)# show pending
class-map type copp match-any CP-CMAP_1
match ip access-group ACLv4_1
switch(config-cmap-CP-CMAP_1)#The exit command returns the switch to the global configuration mode and saves pending class map changes. The abort command returns the switch to the global configuration mode and discards pending class map changes.
Example
switch(config-cmap-CP-CMAP_1)# exit
switch(config)# show class-map type control-plane CP-CMAP_1
Class-map: CP-CMAP_1 (match-any)
Match: ip access-group name ACLv4_1
switch(config)#| Class Name | shape (pps) | bandwidth (pps) |
|---|---|---|
| copp-system-bpdu | 5000 | 5000 |
| copp-system-lacp | 5000 | 5000 |
| copp-system-selfip-tc6to7 | 5000 | 5000 |
| copp-system-selfip | 5000 | 5000 |
| copp-system-tc6to7 | 10000 | 1000 |
| copp-system-lldp | 10000 | 1000 |
| copp-system-ipmcrsvd | 10000 | 1000 |
| copp-system-igmp | 10000 | 1000 |
| copp-system-ipmcmiss | 10000 | 1000 |
| copp-system-glean | 10000 | 1000 |
| copp-system-tc3to5 | 10000 | 1000 |
| copp-system-arp | 10000 | 1000 |
| copp-system-arpresolver | 10000 | 1000 |
| copp-system-l3destmiss | 10000 | 1000 |
| copp-system-l3slowpath | 10000 | 1000 |
| copp-system-l3ttl1 | 10000 | 1000 |
| copp-system-default | 8000 | 1000 |
| copp-system-acllog | 10000 | 1000 |
| copp-system-sflow | 25000 | 0 |
Policy maps are modified in the policy-map configuration mode. The policy-map type copp command enters the policy-map configuration mode.
Example
switch(config)#policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#Dynamic classes are inserted in front of the static classes. Classes automatically contain their eponymous class map; traffic resolution commands are created or edited in the policy-map-class configuration mode. The class (policy-map (control-plane) Trident) command adds a class to the policy map and places the switch in the policy-map-class configuration mode, where traffic resolution commands are added to the class.
Example
switch(config-pmap-copp-system-policy)# class CP-CMAP_1
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)#Example
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)# bandwidth pps 2000
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)# shape pps 4000
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active command displays the saved version of policy map. The show pending command displays the modified policy map.
Example
switch(config-pmap-c-copp-system-policy-CP-CMAP_1)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class CP-CMAP_1
shape pps 4000
bandwidth pps 2000
class copp-system-bpdu
class copp-system-lldp
class copp-system-lacp
class copp-system-arp
class copp-system-arpresolver
class copp-system-default
switch(config-pmap-copp-system-policy)# exit
switch(config)#To modify traffic resolution commands for a static class, enter the policy-map-class configuration mode for the class, then enter the desired bandwidth and shape commands.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-bpdu
switch(config-pmap-c-copp-system-policy-copp-system-bpdu)# shape pps 200
switch(config-pmap-c-copp-system-policy-copp-system-bpdu)# bandwidth pps 100
switch(config-pmap-c-copp-system-policy-copp-system-bpdu)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class CP-CMAP_1
shape pps 4000
bandwidth pps 2000
class copp-system-bpdu
shape pps 200
bandwidth pps 100
class copp-system-lldp
switch(config-pmap-copp-system-policy)# exit
switch(config)#The copp-system-policy policy map is always applied to the control plane. No commands are available to add or remove this assignment.
QoS traffic policies are implemented by creating class maps and policy maps, then applying the policy maps to Ethernet and port channel interfaces.
QoS traffic policies utilize dynamic class maps that are created and modified in the class-map configuration mode. The class-map type qos command enters the class-map configuration mode.
Example
switch(config)# class-map type qos match-any Q-CMap_1
switch(config-cmap-Q-CMap_1)#A class map contains one IPv4 or IPv6 Access Control List (ACL). The match (class-map (qos) Trident) command assigns an ACL to the class map. Subsequent match commands replace the existing match command. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded.
Example
switch(config-cmap-Q-CMap_1)# match ipv6 access-group ACLv6_1
switch(config-cmap-Q-CMap_1)#The class-map configuration mode is a group-change mode. Changes made in a group-change mode are saved by exiting the mode. The show active command displays the saved version of class map. The show pending command displays the unsaved class map.
Example
switch(config-cmap-Q-CMap_1)# show active
switch(config-cmap-Q-CMap_1)# show pending
class-map type qos match-any Q-CMap_1
match ipv6 access-group ACLv6_1
switch(config-cmap-Q-CMap_1)#The exit command returns the switch to global configuration mode and saves pending class map changes. The abort command returns the switch to global configuration mode and discards pending class map changes.
Example
switch(config-cmap-CP-CMAP_1)# exit
switch(config)# show class-map type control-plane CP-CMAP_1
Class-map: CP-CMAP_1 (match-any)
Match: ip access-group name ACLv4_1
switch(config)#Policy maps are created and modified in the policy-map configuration mode. The policy-map type quality-of-service command enters the policy-map configuration mode.
Example
switch(config)# policy-map type quality-of-service Q-PMAP_1
switch(config-pmap-Q-PMAP_1)#Policy maps are edited by adding or removing classes. A class automatically contains its eponymous class map; traffic resolution commands are added or edited in the policy-map-class configuration mode. The class (policy-map (qos) Trident) command adds a class to the configuration mode policy map and places the switch in the policy-map-class configuration mode, where traffic resolution commands are added to the class.
Example
switch(config-pmap-Q-PMAP_1)# class Q-CMap_1
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set cos 7
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# set traffic-class 4
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)#The policy-map and policy-map-class configuration modes are group-change modes. Changes are saved with the exit command or discarded with the abort command. The show active and show pending commands display the saved and modified policy map versions, respectively.
Example
switch(config-pmap-c-Q-PMAP_1-Q-CMap_1)# exit
switch(config-pmap-Q-PMAP_1)# show pending
policy-map type quality-of-service Q-PMAP_1
class Q-CMap_1
set cos 7
set traffic-class 4
class class-default
switch(config-pmap-Q-PMAP_1)# exit
switch(config)#The last class in all QoS policy maps is class-default. The class-default class map matches all traffic except IPv4 or IPv6 traffic and provides no traffic resolution commands. The class-default class map is not editable; traffic resolution commands can be added to the class-default class.
To modify traffic resolution commands for the class-default class, enter the policy-map-class configuration mode for the class, then enter the desired set commands.
Example
switch(config)# policy-map type quality-of-service Q-PMap_1
switch(config-pmap-Q-PMap_1)# class class-default
switch(config-pmap-c-Q-PMap_1-class-default)# set traffic-class 2
switch(config-pmap-c-Q-PMap_1-class-default)# exit
switch(config-pmap-Q-PMap_1)# exit
switch(config)# show policy-map type qos Q-PMap_1
Service-policy Q-PMap_1
Class-map: Q-CMap_1 (match-any)
Match: ipv6 access-group name ACLv6_1
set cos 7
set traffic-class 4
Class-map: class-default (match-any)
set traffic-class 2
switch(config)#The service-policy type qos (Interface mode) command applies a specified policy map to the configuration mode interface.
Example
switch(config)# interface ethernet 8
switch(config-if-Et8)# show active
switch(config-if-Et8)# service-policy input PMAP-1
switch(config-if-Et8)# show active
interface Ethernet8
service-policy type qos input PMAP-1
switch(config-if-Et8)#Policy-Based Routing (PBR) is implemented by creating class maps and policy maps, then applying the policy maps to Ethernet interfaces, port channel interfaces or Switch Virtual Interfaces (SVIs).
PBR policies utilize class maps that are created and modified in the class-map configuration mode. The class-map type pbr command enters the class-map configuration mode.
Example
switch(config)# class-map type pbr match-any CMAP1
switch(config-cmap-PBR-CMAP1)#A class map contains one or more Access Control Lists (ACLs). The match (policy-map (pbr)) command assigns an ACL to the class map. Subsequent match commands add additional ACLs to the class map. Class maps filter traffic only on ACL permit rules. Deny ACL rules are disregarded; if a class map includes ACLs with deny rules, the configuration reverts to its previous state.
switch(config-cmap-PBR-CMAP1)# match ip access-group ACL1
switch(config-cmap-PBR-CMAP1)#The class-map configuration mode is a group-change mode. Changes made in a group-change mode are saved by exiting the mode. The show active command displays the saved version of class map.
switch(config-cmap-PBR-CMAP1)# show active
switch(config-cmap-PBR-CMAP1)#switch(config-cmap-PBR-CMAP1)# exit
switch(config)# show class-map type pbr CMAP1
class-map type pbr match-any CMAP1
10 match ip access-group ACL1
switch(config)#Policy maps are created and modified in the policy-map configuration mode. The policy-map type pbr command enters policy-map configuration mode.
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)#Policy map are edited by adding or removing classes. A class automatically contains its eponymous class map; next-hop commands are added or edited in the policy-map-class configuration mode. The class (policy-map (pbr)) command adds a class to the configuration mode policy map and places the switch in the policy-map-class configuration mode, where next-hop commands are added to the class.
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)#switch(config-pmap-c-PMAP1-CMAP1)# set nexthop 10.12.0.5
switch(config-pmap-c-PMAP1-CMAP1)#switch(config-pmap-c-PMAP1-CMAP1)# exit
switch(config-pmap-PMAP1)# exit
switch(config)#switch(config)# interface ethernet 8
switch(config-if-Et8)# service-policy type pbr input PMAP1
switch(config-if-Et8)#When hardware decapsulation takes place, PBR policy maps on Trident platform switches match on inner packet headers (i.e., they match based on the attributes of the decapsulated packet).
Traffic policies are implemented by policy maps, which are applied to the control plane or an interface. Policy maps contain classes, which are composed of class maps and traffic resolution commands. Traffic Management Conceptual Overview describes traffic policies.
Default control plane traffic policies are implemented automatically without user intervention. These policies are modified by associating traffic resolution commands with static classes that comprise the control plane policy map.
Control plane traffic policies utilize static class maps, which are provided by the switch, are not editable, and cannot be deleted.
| Class Name | shape (pps) | bandwidth (pps) |
|---|---|---|
| copp-system-acllog | 1000 | 10000 |
| copp-system-arp | 1000 | 10000 |
| copp-system-arpresolver | 1000 | 10000 |
| copp-system-bfd | 5000 | 10000 |
| copp-system-bgp | 5000 | 5000 |
| copp-system-bpdu | 5000 | 5000 |
| copp-system-default | 1000 | 8000 |
| copp-system-glean | 1000 | 10000 |
| copp-system-igmp | 1000 | 10000 |
| copp-system-ipmcmiss | 1000 | 10000 |
| copp-system-ipmcrsvd | 1000 | 10000 |
| copp-system-l3destmiss | 1000 | 10000 |
| copp-system-l3slowpath | 1000 | 10000 |
| copp-system-l3ttl1 | 1000 | 10000 |
| copp-system-lacp | 5000 | 5000 |
| copp-system-lldp | 1000 | 10000 |
| copp-system-mlag | 5000 | 5000 |
| copp-system-selfip | 5000 | 5000 |
| copp-system-selfip-tc6to7 | 5000 | 5000 |
| copp-system-sflow | 0 | 25024 |
| copp-system-tc3to5 | 1000 | 10000 |
| copp-system-tc6to7 | 1000 | 10000 |
| copp-system-urm | 1000 | 10000 |
Policy maps are modified in the policy-map configuration mode. The policy-map type copp command enters the policy-map configuration mode.
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#switch(config-pmap-copp-system-policy)# class copp-system-lacp
switch(config-pmap-c-copp-system-policy-copp-system-lacp)#switch(config-pmap-c-copp-system-policy-copp-system-lacp)# bandwidth pps 2000
switch(config-pmap-c-copp-system-policy-copp-system-lacp)# shape pps 4000
switch(config-pmap-c-copp-system-policy-copp-system-lacp)#switch(config-pmap-c-copp-system-policy-copp-system-lacp)# exit
switch(config-pmap-copp-system-policy)# show pending
policy-map type copp copp-system-policy
class copp-system-bpdu
class copp-system-lldp
class copp-system-lacp
shape pps 4000
bandwidth pps 2000
class copp-system-arp
switch(config-pmap-copp-system-policy)# exit
switch(config)#The copp-system-policy policy map is always applied to the control plane. No commands are available to add or remove this assignment.
The TTL action is effective only when it is configured along with a set nexthop or nexthop-group action. The TCAM profile has the set-ttl-3b or set-ttl action in the pbr ip and pbr ipv6 features, such as in the tc-counters system profile.
Command Mode
For IP
TCAM feature PBR IP configuration mode.
For IPv6
TCAM feature PBR IPv6 configuration mode.
Command Syntax
action set-time [set-ttl | set-ttl-3b]
no action set-time [set-ttl | set-ttl-3b]
default action set-time [set-ttl | set-ttl-3b]
Examples
(config)# hardware tcam
(config-tcam)# profile pbr-set-ttl copy default
(config-tcam-profile-pbr-set-ttl)# feature pbr ip
(config-tcam-feature-pbr-ip)# action set-ttlconfig)# hardware tcam
(config-tcam)# profile pbr-set-ttl copy default
(config-tcam-profile-pbr-set-ttl)# feature pbr ip
(config-tcam-feature-pbr-ip)# feature pbr ipv6
(config-tcam-feature-pbr-ipv6)# action set-ttlThe bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) Arad)
Command Syntax
bandwidth kbps kilobits
no bandwidth
default bandwidth
Parameters
kilobits Minimum data rate in kilobits per second. Value ranges from 1 to 10000000.
Static Classes Default Bandwidth
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# bandwidth kbps 500
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Hardware programming status: InProgress
Class-map: copp-system-lldp (match-any)
shape : 2500 kbps
bandwidth : 500 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#The bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) FM6000)
Command Syntax
bandwidth pps packets
no bandwidth
default bandwidth
Parameters
packets Minimum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Bandwidth
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class PMAP-1
switch(config-pmap-c-copp-system-policy-PMAP-1)# bandwidth pps 1000
switch(config-pmap-c-copp-system-policy-PMAP-1)#The bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) Helix)
Command Syntax
bandwidth pps packets
no bandwidth
default bandwidth
Parameter
packets Minimum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Bandwidth
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# bandwidth pps 500
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map interface control-plan copp-system-policy
Service-policy input: copp-system-policy
Number of units programmed: 4
Hardware programming status: Successful
Class-map: copp-system-lldp (match-any)
shape : 10000 pps
bandwidth : 500 pps
Out Packets : 304996
Drop Packets : 0
switch(config)#The bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) Petra)
Command Syntax
bandwidth kbps kilobits
no bandwidth
default bandwidth
Parameter
kbits Minimum data rate in kilobits per second. Value ranges from 1 to 10000000.
Static Classes Default Bandwidth
Guidelines
Petra does not support all discrete rate values. When a specified discrete value is not supported, the switch converts the rate to the next highest discrete value that it supports. The show command displays the converted rate and not the user-configured rate.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# bandwidth kbps 500
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Hardware programming status: InProgress
Class-map: copp-system-lldp (match-any)
shape : 2766 kbps
bandwidth : 651 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#The bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) Trident II).
Command Syntax
bandwidth pps packets
no bandwidth
default bandwidth
Parameter
packets Minimum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Bandwidth
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# bandwidth pps 500
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map interface control-plan copp-system-policy
Service-policy input: copp-system-policy
Number of units programmed: 4
Hardware programming status: Successful
Class-map: copp-system-lldp (match-any)
shape : 10000 pps
bandwidth : 500 pps
Out Packets : 304996
Drop Packets : 0
switch(config)#The bandwidth command specifies the minimum bandwidth for traffic filtered by the configuration mode policy map class.
The no bandwidth and default bandwidth commands remove the minimum bandwidth guarantee for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration
accessed through class (policy-map (control-plane) Trident).
Command Syntax
bandwidth pps packets
no bandwidth
default bandwidth
Parameter
packets Minimum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Bandwidth
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class PMAP-1
switch(config-pmap-c-copp-system-policy-PMAP-1)# bandwidth pps 1000
switch(config-pmap-c-copp-system-policy-PMAP-1)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. All changes in a group change mode edit session are pending until the end of the session.
Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content. Dynamic classes are not supported for control plane policing on Arad platform switches.
Each class corresponds to a transmission queue. Queue scheduling is round-robin until bandwidth rate for a queue is exceeded. Scheduling becomes strict-priority with CPU queue number determining priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to policy-map configuration mode. Saving policy-map-class changes also require an exit from policy-map mode, which saves pending policy-map-class and policy-map changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove policy-map-class commands for the specified class assignment from the policy map.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntax
class class_name
no class class_name
default class class_name
Parameter
class_name name of the class.Static Classes
Related Commands
policy-map type copp places switch in policy-map (control plane) configuration mode.Example
These commands enters policy-map-class configuration mode to modify the shape, bandwidth parameters associated with the static class named copp-system-lldp.switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. All changes in a group change mode edit session are pending until the end of the session.
Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content. Dynamic classes are not supported for control plane policing on FM6000 platform switches.
Each class corresponds to a transmission queue. Queue scheduling is round-robin until bandwidth rate for a queue is exceeded. Scheduling becomes strict-priority with CPU queue number determining priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to policy-map configuration mode. Saving policy-map-class changes also require an exit from policy-map mode, which saves pending policy-map-class and policy-map changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove policy-map-class commands for the specified class assignment from the policy map. The class is removed from the policy map if it is a dynamic class.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntax
class class_name
no class class_name
default class class_name
Parameter
class_name name of the class.Static Classes
Related Commands
policy-map type copp places switch in policy-map (control plane) configuration mode.Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-arp
switch(config-pmap-c-copp-system-policy-copp-system-arp)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. All changes in a group change mode edit session are pending until the end of the session.
Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content. Dynamic classes are not supported for control plane policing on Helix platform switches.
Each class corresponds to a transmission queue. Queue scheduling is strict-priority; CPU queue number determines priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to policy-map configuration mode. Saving policy-map-class changes also require an exit from policy-map mode, which saves the pending policy-map-class and policy-map changes to running-config and returns the switch to global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the policy-map-class commands for the specified class assignment from the policy map.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntax
class class_name
no class class_name
default class class_name
Parameter
class_name name of the class.Static Classes
Related Commands
policy-map type copp places switch in policy-map (control plane) configuration mode.Example
switch(config)# policy-map
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. All changes in a group change mode edit session are pending until the end of the session.
Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content. Dynamic classes are not supported for control plane policing on Petra platform switches.
Each class corresponds to a transmission queue. Queue scheduling is round-robin until bandwidth rate for a queue is exceeded. Scheduling becomes strict-priority with CPU queue number determining priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to policy-map configuration mode. Saving the policy-map-class changes also require an exit from policy-map mode, which saves the pending policy-map-class and policy-map changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the policy-map-class commands for the specified class assignment from the policy map.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntax
class class_name
no class class_name
default class class_name
Parameter
class_name name of the class.
Static Classes
Related Commands
policy-map type copp places switch in policy-map (control plane) configuration mode.
Example
switch(config)# policy-map
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. All changes in a group change mode edit session are pending until the end of the session.
Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content. Dynamic classes are not supported for control plane policing on Trident II platform switches.
Each class corresponds to a transmission queue. Queue scheduling is strict-priority; CPU queue number determines priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to the policy-map configuration mode. Saving the policy-map-class changes also require an exit from the policy-map mode, which saves the pending policy-map-class and policy-map changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the policy-map-class commands for the specified class assignment from the policy map.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntax
class class_name
no class class_name
default class class_name
Parameter
class_name name of the class.Static Classes
Related Commands
policy-map type copp places switch in policy-map (control plane) configuration mode.Example
switch(config)# policy-map
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)#The class command places the switch in policy-map-class (control plane) configuration mode, which is a group change mode for changing bandwidth and shape parameters associated with a specified class. The command adds the specified class to the policy map if it was not previously included. All changes in a group change mode edit session are pending until the end of the session.
Dynamic class maps identify a data stream with an ACL assigned by match (class-map (control-plane) Trident). Static class maps identify a data stream by definition. Each data packet is managed by commands of the first class whose map matches the packets content.
Static classes are provided with the switch and cannot be removed from the policy map or modified by the class command. Dynamic classes are user defined and added to the policy map by this command. Dynamic classes are always placed in front of the static classes. Bandwidth and shape parameters are editable for all classes.
Each class corresponds to a transmission queue. Queue scheduling is round-robin until bandwidth rate for a queue is exceeded. Scheduling becomes strict-priority with CPU queue number determining priority until the shape rate is reached. Packets are dropped after the shape rate is exceeded.
The exit command returns the switch to policy-map configuration mode. Saving the policy-map-class changes also require an exit from policy-map mode, which saves the pending policy-map-class and policy-map changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the policy-map-class commands for the specified class assignment from the policy map. The class is removed from the policy map if it is a dynamic class.
Command Mode
Policy-Map (control plane) configuration accessed through policy-map type copp command.
Command Syntaxclass class_name [PLACEMENT]
no class class_name [PLACEMENT]
default class class_name [PLACEMENT]
Static Classes
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class CM-1
switch(config-pmap-c-copp-system-policy-CM-1)#The class (policy-map (pbr) command places the switch in policy-map-class (pbr) configuration mode, which is a group change mode that modifies the specified class of the configuration mode Policy-Based Routing (PBR) policy map. The command adds the class to the policy map if it was not previously included in the policy map. All changes in a group change mode edit session are pending until the mode is exited, and can be canceled by using the abort command.
PBR policy maps can also contain one or more raw match statements which filter incoming traffic without using ACLs. Data packets are managed by commands of the first class or raw match statement matching the packets contents.
The exit command returns the switch to the policy-map (pbr) configuration mode. However, saving the policy-map-class changes also requires an exit from policy-map (pbr) configuration mode. This saves all the pending policy map and policy-map-class changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the class assignment from the configuration mode policy map by deleting the corresponding class configuration from running-config.
Command Mode
Policy-Map (pbr) Configuration accessed through policy-map type pbr.
Command Syntax
[sequence_number] class class_name
no [sequence_number] class class_name
default [sequence_number] class class_name
no [sequence_number]
default [sequence_number]
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)#The class command places the switch in policy-map-class (qos) configuration mode, which is a group change mode that modifies the specified class of the configuration mode policy map. The command adds the class to the policy map if it was not previously included in the policy map. All changes in a group change mode edit session are pending until the end of the session.
Data packets are managed by commands of the first class whose map matches the packets content.
The exit command returns the switch to the policy-map configuration mode. However, saving policy-map-class changes also require an exit from the policy-map mode. This saves all pending policy map and policy-map-class changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the class assignment from the configuration mode policy map by deleting the corresponding class configuration from running-config.
Command Mode
Policy-Map (qos) Configuration accessed through policy-map type quality-of-service.
Command Syntax
class class_name [PLACEMENT]
no class class_name [PLACEMENT]
default class class_name [PLACEMENT]
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)#The class command places the switch in the policy-map-class (QoS) configuration mode, which is a group change mode that modifies the specified class of the configuration mode policy map. The command adds the class to the policy map if it was not previously included in the policy map. All changes in a group change mode edit session are pending until the end of the session.
Data packets are managed by commands of the first class whose map matches the packets content.
The exit command returns the switch to the policy-map configuration mode. However, saving policy-map-class changes also require an exit from the policy-map mode. This saves all the pending policy map and policy-map-class changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the class assignment from the configuration mode policy map by deleting the corresponding class configuration from running-config.
Command Mode
Policy-Map (qos) Configuration accessed through policy-map type quality-of-service command.
Command Syntax
class class_name [PLACEMENT]
no class class_name [PLACEMENT]
default class class_name [PLACEMENT]
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)#The class command places the switch in the policy-map-class (QoS) configuration mode, which is a group change mode that modifies the specified class of the configuration mode policy map. The command adds the class to the policy map if it was not previously included in the policy map. All changes in a group change mode edit session are pending until the end of the session.
Data packets are managed by commands of the first class whose map matches the packets content.
The exit command returns the switch to the policy-map configuration mode. However, saving the policy-map-class changes also require an exit from the policy-map mode. This saves all the pending policy map and policy-map-class changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the class assignment from the configuration mode policy map by deleting the corresponding class configuration from running-config.
Command Mode
Policy-Map (qos) Configuration accessed through policy-map type quality-of-service command.
Command Syntax
class class_name [PLACEMENT]
no class class_name [PLACEMENT]
default class class_name [PLACEMENT]
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)# The class command places the switch in policy-map-class (qos) configuration mode, which is a group change mode that modifies the specified class of the configuration mode policy map. The command adds the class to the policy map if it was not previously included in the policy map. All changes in a group change mode edit session are pending until the end of the session.
Data packets are managed by commands of the first class whose map matches the packets content.
The exit command returns the switch to policy-map configuration mode. However, saving policy-map-class changes also require an exit from policy-map mode. This saves all the pending policy map and policy-map-class changes to running-config and returns the switch to the global configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no class and default class commands remove the class assignment from the configuration mode policy map by deleting the corresponding class configuration from running-config.
Command Mode
Policy-Map (qos) Configuration accessed through policy-map type quality-of-service command.
Command Syntax
class class_name [PLACEMENT]
no class class_name [PLACEMENT]
default class class_name [PLACEMENT]
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)#The class-map type copp command places the switch in Class-Map (control plane) configuration mode, which is a group change mode that modifies a control-plane dynamic class map. A dynamic class map is a data structure that uses Access Control Lists (ACLs) to define a data stream by specifying characteristics of data packets that comprise that stream. Control-plane policy maps use class maps to specify which control plane traffic is controlled by policy map criteria.
The exit command saves pending class map changes to running-config and returns the switch to the global configuration mode. Class map changes are also saved by entering a different configuration mode. The abort command discards pending changes and returns the switch to the global configuration mode.
The no class-map type copp and default class-map type copp commands delete the specified class map by removing the corresponding class-map type copp command and its associated configuration.
Command Mode
Global Configuration
Command Syntax
class-map type copp match-any class_name
no class-map type copp [match-any] class_name
default class-map type copp [match-any] class_name
Parameter
class_name Name of class map.Commands Available in Class-Map (Control Plane) Configuration Mode
match (class-map (control-plane) Trident)
Example
switch(config)# class-map type copp match-any CP-CMAP-1
switch(config-cmap-CP-CMAP-1)#The class-map type pbr command places the switch in the class-map (pbr) configuration mode for the specified class map, and creates the class map if one does not already exist. The class-map (PBR) configuration mode is a group change mode that modifies a class map for Policy-Based Routing (PBR). PBR class maps contain one or more match statements which filter incoming traffic using ACLs. PBRs can then use these class maps to set next-hop IP addresses for the traffic that matches them. (Classes without set commands translate to no action being performed on that class of packets.)
The exit command saves pending class map changes to running-config, then returns the switch to the global configuration mode. Class map changes are also saved by directly entering a different configuration mode. The abort command discards pending changes and returns the switch to the global configuration mode.
The no class-map type pbr and default class-map type pbr commands delete the specified class map by removing the corresponding class-map type pbr command and its associated configuration.
Command Mode
Global Configuration
Command Syntax
class-map type pbr match-any map_name
no class-map type pbr match-any map_name
default class-map type pbr match-any map_name
Parameter
map_name Name of class map.Example
switch(config)# class-map type pbrmatch-any MAP1
switch(config-cmap-MAP1)#The class-map type qos command places the switch in the class-map (QoS) configuration mode, which is a group change mode that modifies a QoS dynamic class map. A dynamic class map is a data structure that uses Access Control Lists (ACLs) to define a data stream by specifying characteristics of data packets that comprise that stream. QoS policy maps use class maps to specify the traffic (to which the policy map is assigned) that is transformed by policy map criteria.
The exit command saves pending class map changes to running-config, then returns the switch to the global configuration mode. Class map changes are also saved by entering a different configuration mode. The abort command discards pending changes and returns the switch to the global configuration mode.
The no class-map type qos and default class-map type qos commands delete the specified class map by removing the corresponding class-map type qos command and its associated configuration. The class-map and class-map type qos commands are equivalent.
Command Mode
Global Configuration
Command Syntax
class-map type qos match-any class_name
no class-map type qos match-any class_name
default class-map type qos match-any class_name
Parameters
class_name Name of class map.
class-map map_name and class-map type qos map_name are identical commands.
Example
switch(config)# class-map type qos match-any MAP-1
switch(config-cmap-MAP-1)#The clear policy-map command resets the specified policy map counters to zero. Policy map counters record the quantity of packets that are filtered by the ACLs that comprise a specified policy map.
Command Mode
Privileged EXEC
Command Syntax
clear policy-map INTERFACE_NAME counters MAP_NAME
Policy-Based Routing (PBR) is a feature that is applied on IPv4 or IPv6 routable ports, to preferentially route packets. Forwarding is based on a policy that is enforced at the ingress of the applied interface and overrides normal routing decisions. In addition to matches on regular ACLs, PBR policy-maps can also include “raw match” statements that look like a single entry of an ACL as a convenience for users.
Configuration Mode
For IP:
TCAM PBR profile set TTL configuration mode.
For IPv6:
TCAM feature PBR IP configuration mode.
Command Syntax
For IP:
feature pbr ip [copy]
no feature pbr ip [copy]
default feature pbr ip [copy]
For IPv6:
feature pbr ipv6 [copy | bank]
no feature pbr ipv6 [copy | bank]
default featue pbr ipv6 [copy | bank]
Parameters
For IP:
copy Copy a feature from a TCAM profile.
For IPv6:
(config)# hardware tcam
(config-tcam)# profile pbr-set-ttl copy default
(config-tcam-profile-pbr-set-ttl)# feature pbr ip(config)# hardware tcam
(config-tcam)# profile pbr-set-ttl copy default
(config-tcam-profile-pbr-set-ttl)# feature pbr ip
(config-tcam-feature-pbr-ip)# feature pbr ipv6The feature traffic-policy cpu command configures the CPU traffic policy features for the IPv4 and IPv6 traffic in user-defined TCAM profile.
The no feature traffic-policy cpu and default feature traffic-policy cpu commands remove the CPU policy configurations from running-config.
Command Mode
Hardware TCAM
Command Syntax
feature traffic-policy cpu [ipv4 | ipv6]
no feature traffic-policy cpu [ipv4 | ipv6]
default feature traffic-policy cpu [ipv4 | ipv6]
Example
switch(config)# hardware tcam
switch(config-hw-tcam)# profile test
switch(config-hw-tcam-profile-test)# feature traffic-policy cpu ipv4The feature traffic-policy port command configures the port-related traffic policy features for the IPv4 and IPv6 traffic in user-defined TCAM profile.
The no feature traffic-policy port and default feature traffic-policy port commands remove the CPU policy configurations from running-config.
Command Mode
Hardware TCAM
Command Syntax
feature traffic-policy port [ipv4 | ipv6]
no feature traffic-policy port [ipv4 | ipv6]
default feature traffic-policy port [ipv4 | ipv6]
Example
switch(config)# hardware tcam
switch(config-hw-tcam)# profile test
switch(config-hw-tcam-profile-test)# feature traffic-policy port ipv4The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4 and IPv4 standard ACLs.
A class map is assigned to a policy map by the class (policy-map (control-plane) Helix) command.
The class map (control plane) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-Map (control plane) configuration accessed through class-map type copp command.
Command Syntax
match ip access-group list_name
no match ip access-group list_name
default match ip access-group list_name
Parameters
list_name name of ACL assigned to class map.Guidelines
Static class maps cannot be modified by this command.
Match statements are saved to running-config only upon exiting class-map (control plane) configuration mode.
Example
switch(config)# class-map type copp map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4 and IPv4 standard ACLs.
A class map is assigned to a policy map by the class (policy-map (control-plane) Trident II) command.
The class map (control plane) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-Map (control plane) configuration accessed through class-map type copp command.
Command Syntax
list_name
list_name
list_name
Parameter
list_name name of ACL assigned to class map.Guidelines
Static class maps cannot be modified by this command.
Match statements are saved to running-config only upon exiting class-map (control plane) configuration mode.
Example
switch(config)# class-map type copp map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4, IPv6, IPv4 standard, and IPv6 standard ACLs.
A class map is assigned to a policy map by the class (policy-map (control-plane) Trident) command.
Class map (control plane) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-Map (control plane) configuration accessed through class-map type copp command
Command Syntax
match IP_VERSION access-group list_name
no match IP_VERSION access-group list_name
default match IP_VERSION access-group list_name
Guidelines
Static class maps cannot be modified by this command.
Match statements are saved to running-config only upon exiting class-map (control plane) configuration mode.
Example
switch(config)# class-map type copp map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns ACLs to the configuration mode Policy-Based Routing (PBR) class map. The command accepts IPv4, IPv4 standard, IPv6 and IPv6 standard ACLs.
Class map (pbr) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-map (pbr) configuration accessed through class-map type pbr command.
Command Syntax
[sequence_number] match [ip | ipv6] access-group list_name
no [sequence_number] match [ip | ipv6] access-group list_name
default [sequence_number] [ip | ipv6] access-group list_name
no [sequence_number]
default [sequence_number]
Example
switch(config)# class-map type pbr map1
switch(config-cmap-map1)# match ip access-group list1
switch(config-cmap-map1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4 and IPv4 standard ACLs.
The class map (qos) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-map (qos) configuration accessed through class-map type qos command.
Command Syntax
match IP_VERSION access-group list_name
no match IP_VERSION access-group list_name
default match IP_VERSION access-group list_name
Example
switch(config)# class-map type qos map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4, IPv4 standard, IPv6, and IPv6 standard ACLs.
the class map (QoS) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-Map (QoS) configuration accessed through class-map type qos command.
Command Syntax
match IP_VERSION access-group list_name
no match IP_VERSION access-group list_name
default match IP_VERSION access-group list_name
Example
switch(config)# class-map type qos map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4, IPv4 standard, IPv6, and IPv6 standard ACLs.
The class map (QoS) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
The class-map (qos) configuration accessed through class-map type qos command.
Command Syntax
IP_VERSION list_name
IP_VERSION list_name
IP_VERSION list_name
Example
switch(config)# class-map type qos map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command assigns an ACL to the configuration mode class map. A class map can contain only one ACL. Class maps only use permit rules to filter data; deny rules are ignored. The command accepts IPv4, IPv4 standard, IPv6, and IPv6 standard ACLs.
Class map (QoS) configuration mode is a group change mode. Match statements are not saved to running-config until the edit session is completed by exiting the mode.
The no match and default match commands remove the match statement from the configuration mode class map by deleting the corresponding command from running-config.
Command Mode
Class-Map (qos) configuration accessed through class-map type qos command.
Command Syntax
match IP_VERSION access-group list_name
no match IP_VERSION access-group list_name
default match IP_VERSION access-group list_name
Example
switch(config)# class-map type qos map_1
switch(config-cmap-map_1)# match ip access-group list_1
switch(config-cmap-map_1)# exit
switch(config)#The match command creates a policy map clause entry that specifies one filtering condition. When a packet matches the filtering criteria, its next hop is set as specified. When a packets properties do not equal the statement parameters, the packet is evaluated against the next clause or class map in the policy map, as determined by sequence number. If all clauses fail to set a next hop for the packet, the packet is routed according to the FIB.
The no match and default match commands remove the match statement from the configuration mode policy map by deleting the corresponding command from running-config.
Command Mode
Policy-Map (pbr) Configuration accessed through policy-map type pbr command.
Command Syntax
[sequence_number] match ip SOURCE_ADDR DEST_ADDR [set nexthop [recursive] NH-addr_1 [NH-addr_2] ... [NH-addr_n]]
no match ip SOURCE_ADDR DEST_ADDR [set nexthop [recursive] NH-addr_1 [NH-addr_2] ... [NH-addr_n]]
default match match ip SOURCE_ADDR DEST_ADDR [set nexthop [recursive] NH-addr_1 [NH-addr_2] ... [NH-addr_n]]
no SEQ_NUM
default SEQ_NUM
Source and destination subnet addresses support discontiguous masks.
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# match ip 172.16.0.0/12 any set nexthop 192.163.3.5
switch(config-pmap-PMAP1)# exit
switch(config)#The platform arad tcam counters feature command enables incrementing PBR hardware counters corresponding to ACL. If counters for PBR are enabled, then counters for ACL will be automatically disabled in all cases. If counters for ACL are enabled, then counters for PBR will be automatically disabled in all cases.
The no platform arad tcam counters feature command disables PBR/ACL counters selection. The default platform arad tcam counters feature commands resets the default behavior.
Command Mode
Global Configuration
Command Syntax
platform arad tcam counters feature [OPTIONS]
no platform arad tcam counters feature [OPTIONS]
default platform arad tcam counters feature [OPTIONS]
Parameters
switch(config)# platform arad tcam counters feature acl
switch(config)#switch(config)# no platform arad tcam counters feature acl
switch(config)#The policy-map type copp command places the switch in the policy-map (control plane) configuration mode, which is a group change mode that modifies a control-plane policy map. A policy map is a data structure that consists of class maps that identify a specific data stream and specify bandwidth and shaping parameters that controls its transmission. Control plane policy maps are applied to the control plane to manage traffic.
The copp-system-policy policy map is supplied with the switch and is always applied to the control plane. The copp-system-policy is the only valid control plane policy map.
The exit command saves pending policy map changes to running-config and returns the switch to the global configuration mode. Policy map changes are also saved by entering a different configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no policy-map type copp and default policy-map type copp commands delete the specified policy map by removing the corresponding policy-map type copp command and its associated configuration.
Command Mode
Global Configuration
Command Syntax
policy-map type copp copp-system-policy
no policy-map type copp copp-system-policy
default policy-map type copp copp-system-policy
The copp-system-policy is supplied with the switch and is the only valid control plane policy map.
Related Commands
class-map type copp enters the control-plane class-map configuration mode for modifying a control-plane dynamic class map.
Only Helix and Trident platform switches support dynamic classes for control plane policing.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)#The policy-map type pbr command places the switch in policy-map (pbr) configuration mode, which is a group change mode that modifies a Policy-Based Routing (PBR) policy map. The command also creates the specified policy map if it does not already exist. A PBR policy map is a data structure that consists of class maps that identify specific packets and the next hops for those packets. Policy maps are applied to Ethernet or port channel interfaces to manage traffic.
The exit command saves pending policy map changes to running-config and returns the switch to the global configuration mode. Policy map changes are also saved by entering a different configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no policy-map type pbr and default policy-map type pbr commands delete the specified policy map by removing the corresponding policy-map type pbr command and its associated configuration.
Command Mode
Global Configuration
Command Syntax
policy-map type pbr map_name
no policy-map type pbr map_name
default policy-map type pbr map_name
Parameter
map_name Name of policy map.Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)#The policy-map type quality-of-service command places the switch in the policy-map (QoS) configuration mode, which is a group change mode that modifies a QoS policy map. A policy map is a data structure that consists of class maps that identify a specific data stream and shaping parameters that controls its transmission. Policy maps are applied to Ethernet or port channel interfaces to manage traffic.
The exit command saves pending policy map changes to running-config and returns the switch to the global configuration mode. Policy map changes are also saved by entering a different configuration mode. The abort command discards pending changes, returning the switch to the global configuration mode.
The no policy-map type quality-of-service and default policy-map type quality-of-service commands delete the specified policy map by removing the corresponding policy-map type quality-of-service command and its associated configuration. The policy-map and policy-map type quality-of-service commands are equivalent.
Command Mode
Global Configuration
Command Syntax
policy-map type quality-of-service map_name
no policy-map type quality-of-service map_name
default policy-map type quality-of-service map_name
Parameter
map_name Name of policy map.Conditions
policy-map map_name and policy-map type quality-of-service map_name are identical commands.
Example
switch(config)# policy-map PMAP-1
switch(config-pmap-PMAP-1)#The policy-map type quality-of-service counter command in the Global Configuration Mode configures per interface counters for policy map and class map matches.
The no | default versions of the command disables the feature and removes it from the running-config.
Command Mode
Global Configuration
Command Syntax
policy-map type quality-of-service counter per-interface
no policy-map type quality-of-service counter per-interface
default policy-map type quality-of-service counter per-interface
Example
switch(config)# policy-map type quality-of-service counter per-interfaceThe policy-map type quality-of-service policer copy command is used to copy an existing QoS policy map to the policy map policer.
The policy-map type quality-of-service policer drop counter command is used to enable drop counters for the QoS policy map policer.
The no policy-map type quality-of-service policer and default policy-map type quality-of-service policer commands delete the policy map policer by removing the corresponding policy-map type quality-of-service policer command and its associated configuration.
The no policy-map type quality-of-service policer drop counter and default policy-map type quality-of-service policer drop counter commands disable drop counters for the policy map policer.
Command Mode
Global Configuration
Command Syntax
policy-map type quality-of-service policer copy map_name
policy-map type quality-of-service policer drop counter
no policy-map type quality-of-service policer
default policy-map type quality-of-service policer
Parameter
map_name Name of policy map to copy.Examples
switch(config)#policy-map type quality-of-service policer copy PMAP-1
switch(config-pmap-PMAP-1)#switch(config)#policy-map type quality-of-service policer drop counter
switch(config)#The resequence command assigns sequence numbers to rules in the configuration mode class map. Command parameters specify the number of the first rule and the numeric interval between consecutive rules. Once changed, rule numbers persist unless changed again using the resequence command, but the interval used for numbering new rules reverts to 10 on the exiting class-map (pbr) configuration mode.
Maximum rule sequence number is 4294967295.
Command Mode
Class-Map (PBR) Configuration accessed through class-map type pbr command.
Command Syntax
resequence [start_num [inc_num]]
Example
switch(config)# class-map type pbr match-any CMAP1
switch(config-cmap-CMAP1)# show active
class-map type pbr match-any CMAP1
10 match ip access-group group1
20 match ip access-group group2
30 match ip access-group group3
switch(config-cmap-CMAP1)# resequence 100 20
switch(config-cmap-CMAP1)# exit
switch(config)# class-map type pbr match-any CMAP1
switch(config-cmap-CMAP1)# show active
class-map type pbr match-any CMAP1
100 match ip access-group group1
120 match ip access-group group2
140 match ip access-group group3The resequence command assigns sequence numbers to rules in the configuration mode policy map. Command parameters specify the number of the first rule and the numeric interval between consecutive rules. Once changed, rule numbers persist unless changed again using the resequence command, but the interval used for numbering new rules reverts to 10 on the exiting policy-map (pbr) configuration mode.
Maximum rule sequence number is 4294967295.
Command Mode
Policy-Map (PBR) Configuration accessed through policy-map type pbr command
Command Syntax
resequence [start_num [inc_num]]
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# show active
policy-map type pbr PMAP1
10 class CMAP1
set nexthop 172.16.1.1
20 class CMAP2
set nexthop 172.16.2.2
30 class CMAP3
set nexthop 172.16.3.3
switch(config-pmap-PMAP1)# resequence 100 20
switch(config-pmap-PMAP1)# exit
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# show active
class-map type pbr PMAP1
100 class CMAP1
set nexthop 172.16.1.1
120 class CMAP2
set nexthop 172.16.2.2
140 class CMAP3
set nexthop 172.16.3.3
switch(config-pmap-PMAP1)#The service-policy pbr command applies the specified Policy-Based Routing (PBR) policy map to the configuration mode interface. A PBR policy map is a data structure that consists of class maps that identify specific packets and the next hops for those packets. Policy maps are applied to Ethernet or port channel interfaces to manage traffic. Only one service policy is supported per interface.
The no service-policy pbr and default service-policy pbr commands remove the service policy assignment from the configuration mode interface by deleting the corresponding service-policy pbr command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
service-policy type pbr TRAFFIC_DIRECTION map_name
no service-policy type pbr TRAFFIC_DIRECTION map_name
default service-policy type pbr TRAFFIC_DIRECTION map_name
Guidelines
A policy map that is attached to a port channel interface takes precedence for member interfaces of the port channel over their individual interface Ethernet configuration. Members that are removed from a port channel revert to the policy map implementation specified by its interface Ethernet configuration.
Related Commands
policy-map type pbrExample
switch# config
switch(config)# interface ethernet 8
switch(config-if-Et8)# service-policy type pbr input PMAP1
switch(config-if-Et8)#The service-policy command applies a specified policy map to the configuration mode interface. A policy map is a data structure that identifies data traffic through class maps, then specifies actions to classify the traffic (by setting the traffic class), mark the traffic (by setting the cos and dscp values), and police the traffic (by setting the police rate) through data packet field modifications.
The no service-policy and default service-policy commands remove the service policy assignment from the configuration mode interface by deleting the corresponding service-policy command from running-config.
Command Mode
Interface-Ethernet Configuration
Interface-Port-Channel Configuration
Interface-VLAN Configuration
Command Syntax
service-policy [type qos] TRAFFIC_DIRECTION map_name
no service-policy [type qos] TRAFFIC_DIRECTION map_name
default service-policy [type qos] TRAFFIC_DIRECTION map_name
Guidelines
A policy map that is attached to a port channel interface takes precedence for member interfaces of the port channel over their individual interface Ethernet configuration. Members that are removed from a port channel revert to the policy map implementation specified by its interface Ethernet configuration.
Related Cmmands
policy-map type quality-of-serviceExample
switch# config
switch(config)# interface ethernet 8
switch(config-if-Et8)# show active
switch(config-if-Et8)# service-policy input PMAP-1
switch(config-if-Et8)# show active
interface Ethernet8
service-policy type qos input PMAP-1
switch(config-if-Et8)#Each type of set command can be assigned to a class, allowing for the simultaneous modification of both (cos, dscp) fields and assignment to a traffic class.
The no set and default set commands remove the specified data action from the class map by deleting the associated set command from running-config.
Command Mode
Policy-map-class (qos) configuration
accessed through class (policy-map (qos) FM6000) command.
Command Syntax
set QOS_TYPE value
no set QOS_TYPE
default set QOS_TYPE
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)# set cos 7
switch(config-pmap-c-PMAP-1-CMAP-1)# set traffic-class 4
switch(config-pmap-c-PMAP-1-CMAP-1)#Each type of set command can be assigned to a class, allowing for the simultaneous modification of both (cos, dscp) fields and assignment to a traffic class.
The no set and default set commands remove the specified data action from the class map by deleting the associated set command from running-config.
Command Mode
Policy-map-class (qos) configuration accessed through class (policy-map (qos) Helix) command.
Command Syntax
set QOS_TYPE value
no set QOS_TYPE
default set QOS_TYPE
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)# set cos 7
switch(config-pmap-c-PMAP-1-CMAP-1)# set traffic-class 4
switch(config-pmap-c-PMAP-1-CMAP-1)#Each type of set command can be assigned to a class, allowing for the simultaneous modification of both (cos, dscp) fields and assignment to a traffic class.
The no set and default set commands remove the specified data action from the class map by deleting the associated set command from running-config.
Command Mode
Policy-map-class (qos) configuration accessed through class (policy-map (qos) Trident) command.
Command Syntax
set QOS_TYPE value
no set QOS_TYPE
default set QOS_TYPE
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)# set cos 7
switch(config-pmap-c-PMAP-1-CMAP-1)# set traffic-class 4
switch(config-pmap-c-PMAP-1-CMAP-1)#Each type of set command can be assigned to a class, allowing for the simultaneous modification of both (cos, dscp) fields and assignment to a traffic class.
The no set and default set commands remove the specified data action from the class map by deleting the associated set command from running-config.
Command Mode
Policy-map-class (qos) configuration accessed through class (policy-map (qos) Trident) command.
Command Syntax
set QOS_TYPE value
no set QOS_TYPE
default set QOS_TYPE
Example
switch(config)# policy-map type quality-of-service PMAP-1
switch(config-pmap-PMAP-1)# class CMAP-1
switch(config-pmap-c-PMAP-1-CMAP-1)# set cos 7
switch(config-pmap-c-PMAP-1-CMAP-1)# set traffic-class 4
switch(config-pmap-c-PMAP-1-CMAP-1)#The set nexthop command specifies the next hop for traffic defined by its associated class map in its configuration mode policy map class.
The no set nexthop and default set nexthop commands remove the specified action from the class map by deleting the associated set nexthop command from running-config.
Command Mode
Policy-map-class (pbr) configuration accessed through class (policy-map (pbr)) command.
Command Syntax
set nexthop [recursive] NH-addr_1 [NH-addr_2] ... [NH-addr_n]
no set nexthop [recursive]
default set nexthop [recursive]
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)# set nexthop 192.168.5.3
switch(config-pmap-c-PMAP1-CMAP1)#The set nexthop-group command specifies a nexthop group as the next hop for traffic defined by its associated class map in its configuration mode policy map class.
The no set nexthop-group and default set nexthop-group commands remove the specified action from the class map by deleting the associated set nexthop-group command from running-config.
Command Mode
Policy-map-class (pbr) configuration accessed through class (policy-map (pbr)) command.
Command Syntax
set nexthop-group group_name
no set nexthop-group group_name
default set nexthop-group group_name
Parameters
group_name name of ECMP group to use as next hop.
Example
switch(config)# policy-map type pbr PMAP1
switch(config-pmap-PMAP1)# class CMAP1
switch(config-pmap-c-PMAP1-CMAP1)# set nexthop-group GROUP1
switch(config-pmap-c-PMAP1-CMAP1)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) Arad)
Command Syntax
Parameter
kilobits Maximum data rate in kilobits per second. Value ranges from 1 to 10000000.
Static Classes Default Shape
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# shape kbps 2000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Class-map: copp-system-lldp (match-any)
shape : 2000 kbps
bandwidth : 250 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) FM6000).
Command Syntax
shape pps packets
no shape
default shape
Parameters
packets Maximum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Shape
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class PMAP-1
switch(config-pmap-c-copp-system-policy-PMAP-1)# shape pps 5000
switch(config-pmap-c-copp-system-policy-PMAP-1)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) Helix).
Command Syntax
shape pps packets
no shape
default shape
Parameters
packets Maximum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Shape
Example
switch(config)# policy-map type control-plan copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# shape pps 5000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Class-map: copp-system-lldp (match-any)
shape : 5000 pps
bandwidth : 500 pps
Out Packets : 305961
Drop Packets : 0
switch(config)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) Petra)
Command Syntax
shape kbps kilobits
no shape
default shape
Parameter
kilobits Maximum data rate in kilobits per second. Value ranges from 1 to 10000000.
Static Classes Default Shape
Guidelines
Petra does not support all discrete rate values. When a specified discrete value is not supported, the switch converts the rate to the next highest discrete value that it supports. The show command displays the converted rate and not the user-configured rate.
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# shape kbps 2000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Class-map: copp-system-lldp (match-any)
shape : 2115 kbps
bandwidth : 325 kbps
Out Packets : 0
Drop Packets : 0
switch(config)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) Trident II).
Command Syntax
shape pps packets
no shape
default shape
Parameter
packets Maximum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Shape
Example
switch(config)# policy-map type control-plan copp-system-policy
switch(config-pmap-copp-system-policy)# class copp-system-lldp
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# shape pps 5000
switch(config-pmap-c-copp-system-policy-copp-system-lldp)# exit
switch(config-pmap-copp-system-policy)# exit
switch(config)# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Class-map: copp-system-lldp (match-any)
shape : 5000 pps
bandwidth : 500 pps
Out Packets : 305961
Drop Packets : 0
switch(config)#The shape command specifies the maximum bandwidth for traffic filtered by the configuration mode policy map class.
The no shape and default shape commands remove the maximum bandwidth restriction for the configuration mode class by deleting the corresponding bandwidth command from running-config.
Command Mode
Policy-map-class (control plane) configuration accessed through class (policy-map (control-plane) Trident).
Command Syntax
shape pps packets
no shape
default shape
Parameters
packets Maximum data rate in packets per second. Value ranges from 1 to 100000.
Static Classes Default Shape
Example
switch(config)# policy-map type copp copp-system-policy
switch(config-pmap-copp-system-policy)# class PMAP-1
switch(config-pmap-c-copp-system-policy-PMAP-1)# shape pps 5000
switch(config-pmap-c-copp-system-policy-PMAP-1)The show class-map command displays contents of available control-plane class maps. Control-plane class maps can be added to the copp-system-policy policy map. Control-plane class maps can be static class maps defined by the system or dynamic maps created in class-map configuration mode.
Dynamic class maps are composed of statements that match IPv4 access control lists. Static class maps are defined by the switch and cannot be altered.
Command Mode
EXEC
Command Syntax
show class-map type control-plane [MAP_NAME]
Parameters
Example
switch# show class-map type control-plane
Class-map: CM-CP1 (match-any)
Match: ip access-group name LIST-CP1
Class-map: copp-system-acllog (match-any)
Class-map: copp-system-arp (match-any)
Class-map: copp-system-arpresolver (match-any)
Class-map: copp-system-bpdu (match-any)
Class-map: copp-system-glean (match-any)
Class-map: copp-system-igmp (match-any)
Class-map: copp-system-ipmcmiss (match-any)
Class-map: copp-system-ipmcrsvd (match-any)
Class-map: copp-system-l3destmiss (match-any)
Class-map: copp-system-l3slowpath (match-any)
Class-map: copp-system-l3ttl1 (match-any)
Class-map: copp-system-lacp (match-any)
Class-map: copp-system-lldp (match-any)
Class-map: copp-system-selfip (match-any)
Class-map: copp-system-selfip-tc6to7 (match-any)
Class-map: copp-system-sflow (match-any)
Class-map: copp-system-tc3to5 (match-any)
Class-map: copp-system-tc6to7 (match-any)
switch>The show class-map command displays contents of all available Policy-Based Routing (PBR) class maps, or of a specified PBR class map. PBR class maps are used by PBR policy maps. PBR class maps are dynamic maps that are created in class-map-configuration mode. Dynamic class maps are composed of statements that match IPv4 or IPv6 access control lists.
Command Mode
EXEC
Command Syntax
show class-map type pbr [map_name]
Parameters
map_name Name of class map displayed by the command. If no parameter is entered, command show all available PBR class maps.
Related Command
show policy-map type pbr displays PBR policy maps.
Example
switch# show class-map type pbr CMAP1
Class-map: CMAP1 (match-any)
Match: 10 ip access-group PBRgroup1
Match: 20 ip access-group PBRgroup2
Match: 30 ip access-group PBRgroup3
switch>The show class-mapcommand displays contents of all available QoS class maps. QoS class maps are used by QoS policy maps. QoS class maps are dynamic maps that are created in class-map configuration mode. Dynamic class maps are composed of statements that match IPv4 or IPv6 access control lists.
Command Mode
EXEC
Command Syntax
show class-map type qos [MAP_NAME]
Parameters
show class-map and show class-map type qos are identical commands.
Related Command
show class-map type control-plane displays control plane class maps.
Example
switch# show class-map type qos
Class-map: CM-Q1 (match-any)
Match: ipv6 access-group name LIST-1
Class-map: CM-Q2 (match-any)
Match: ip access-group name LIST-2The show policy-map copp command displays contents of the control-plane policy map. Control-plane policy maps are applied to the control plane, and copp-system-policy is the only supported policy map.
Command Mode
EXEC
Command Syntax
show policy-map copp copp-system-policy
Example
switch# show policy-map copp copp-system-policy
Service-policy input: copp-system-policy
Number of units programmed: 1
Hardware programming status: Successful
Class-map: copp-system-bpdu (match-any)
shape : 5000 pps
bandwidth : 5000 pps
Out Packets : 2
Drop Packets : 0
Class-map: copp-system-lacp (match-any)
shape : 5000 pps
bandwidth : 5000 pps
Out Packets : 0
Drop Packets : 0
switch>The show policy-map interface command displays the quantity of packets that are filtered by ACLs applied to a interface.
Command Mode
EXEC
Command Syntax
show policy-map [INTERFACE_NAME][type qos][TRAFFIC] counters
Example
switch# show policy-map interface ethernet 7-8
Service-policy input: PMAP-1
Hardware programming status: Successful
Class-map: cmap-1 (match-any)
Match: ip access-group name LIST-2
set cos 6
Class-map: class-default (match-any)
Service-policy input: PMAP-2
Hardware programming status: Successful
Class-map: cmap-2 (match-any)
Match: ip access-group name LIST-2
set dscp 10
Class-map: class-default (match-any)The show policy-map interface command displays contents of the policy maps applied to specified interfaces or to the control plane.
Command Mode
EXEC
Command Syntax
show policy-map interface INTERFACE_NAME [type qos] [TRAFFIC]
Example
switch# show policy-map interface ethernet 7-8
Service-policy input: PMAP-1
Hardware programming status: Successful
Class-map: cmap-1 (match-any)
Match: ip access-group name LIST-2
set cos 6
Class-map: class-default (match-any)
Service-policy input: PMAP-2
Hardware programming status: Successful
Class-map: cmap-2 (match-any)
Match: ip access-group name LIST-2
set dscp 10
Class-map: class-default (match-any)The show policy-map type copp command displays contents of control plane policy maps. Control-plane policy maps are applied to the control plane; copp-system-policy is the only supported policy map.
Command options filter the output to display contents of all policy maps, contents of a specified policy map, or contents of a single class map within a specified policy map.
Command Mode
EXEC
Command Syntax
show policy-map type copp copp-system-policy [CMAP_NAME]
Parameters
Example
switch# show policy-map type copp copp-system-policy class copp-system-bpdu
Class-map: copp-system-bpdu (match-any)
shape : 5000 pps
bandwidth : 5000 ppsThe show policy-map pbr command displays contents of Policy-Based Routing (PBR) policy maps. PBR policy maps are applied to Ethernet interfaces, port channel interfaces or switch virtual interfaces (SVIs).
Command options filter the output to either display contents of all policy maps, contents of a specified policy map, or summary contents of all or a specified policy map.
Command Mode
EXEC
Command Syntax
show policy-map type pbr [PMAP_NAME][DATA_LEVEL]
Example
switch# show policy-map type pbr
Service policy PMAP1
Configured on:
Applied on:
10: Class-map: CMAP1 (match-any)
Match: 10 ip access-group PBRgroup1
Match: 20 ip access-group PBRgroup2
Match: 30 ip access-group PBRgroup3
Configured actions: set nexthop 172.16.10.12
20: Class-map: CMAP2 (match-any)
Match: 10 ip access-group PBRgroup1
Match: 10 ip access-group PBRgroup4
Match: 20 ip access-group PBRgroup5
Configured actions: set nexthop 192.168.15.15The show policy-map counters command displays the quantity of packets that are filtered by the ACLs that comprise a specified QoS policy map.
Command Mode
EXEC
Command Syntax
show policy-map type qos pmap_name [TRAFFIC] counters [INFO_LEVEL]
Example
switch# show policy-map p1 counters
Service-policy input: p1
Hardware programming status: Successful
Class-map: c1 (match-any)
Match: vlan 100 0xfff
set dscp 7
Matched Packets: 7
Interface: Ethernet1/1
Matched Packets: 1
Interface: Ethernet2/1
Matched Packets: 2
Interface: Ethernet3/1
Matched Packets: 4
Class-map: c2 (match-any)
Match: ip access-group name acl1
set cos 6
Matched Packets: 6
Interface: Ethernet1/1
Matched Packets: 2
Interface: Ethernet2/1
Matched Packets: 0
Interface: Ethernet3/1
Matched Packets: 4
Class-map: class-default (match-any)
Matched Packets: 0
Interface: Ethernet1/1
Matched Packets: 0
Interface: Ethernet2/1
Matched Packets: 0
Interface: Ethernet3/1
Matched Packets: 0The show policy-map qos command displays contents of QoS policy maps. QoS policy maps are applied to Ethernet or port channel interfaces.
Command options filter the output to either display contents of all policy maps, contents of a specified policy map, or contents of a single class map within a specified policy map.
Command Mode
EXEC
Command Syntax
show policy-map [type qos][PMAP_NAME [CMAP_NAME]]
Example
switch# show policy-map type qos
Service-policy input: PMAP-1
Hardware programming status: Successful
Class-map: xeter (match-any)
Match: ip access-group name LIST-1
set cos 6
Class-map: class-default (match-any)
Service-policy PMAP-2
Class-map: class-default (match-any)The show traffic-policy command displays traffic policy information on the interface.
Command Mode
EXEC
Command Syntax
show traffic-policy NAME interface
show traffic-policy interface [DETAILS]
Parameters
switch(config-traffic-policies)# show traffic-policy interface summary
Traffic policy samplePolicy
Configured on interfaces: Ethernet1/1, Ethernet2/1, Ethernet3/1, ...
Applied on interfaces for IPv4 traffic: Ethernet1/1, Ethernet2/1, Ethernet3/1, ...
Applied on interfaces for IPv6 traffic:
Total number of rules configured: 3
match SIMPLE ipv4
match ipv4-all-default ipv4
match ipv6-all-default ipv6switch(config-traffic-policies)# show traffic-policy samplePolicy interface
Traffic policy samplePolicy
Configured on interfaces: Ethernet1/1, Ethernet2/1, Ethernet3/1, ...
Applied on interfaces for IPv4 traffic: Ethernet1/1, Ethernet2/1, Ethernet3/1, ...
Applied on interfaces for IPv6 traffic:
Total number of rules configured: 3
match SIMPLE ipv4
Source prefix: 192.0.2.0/24
198.51.100.0/24
Destination prefix: 203.0.113.0/24
Protocol: tcp
Source port: 50-100
110-200
Actions: Drop
match ipv4-all-default ipv4
match ipv6-all-default ipv6switch(config-traffic-policies)# show traffic-policy interface detail
Traffic policy samplePolicy
Configured on interfaces: Ethernet1/1, Ethernet2/1, Ethernet3/1, Ethernet4/1
Applied on interfaces for IPv4 traffic: Ethernet1/1, Ethernet2/1, Ethernet3/1, Ethernet4/1
Applied on interfaces for IPv6 traffic:
Total number of rules configured: 3
match SIMPLE ipv4
Source prefix: 192.0.2.0/24
198.51.100.0/24
Destination prefix: 203.0.113.0/24
Protocol: tcp
Source port: 50-100
110-200
Actions: Drop
match ipv4-all-default ipv4
match ipv6-all-default ipv6switch(config-traffic-policies)# show traffic-policy interface errors
Traffic policy samplePolicy
Failed on interface for IPv4 traffic:
Failed on interface for IPv6 traffic:The switch chassis, fans, power supplies, line cards, and supervisors also provide LEDs that signal status and conditions that require attention. The Quick Start Guide for the individual switches provides information about their LEDs.
Arista switching platforms are designed to work reliably in common data center environments.
To ensure their reliable operation and to monitor or diagnose the switch's health, Arista provides a set of monitoring capabilities available through the CLI or SNMP entity MIBs to monitor and diagnose potential problems with the switching platform.